Providing Out-of-Band Connectivity to Mission-Critical IT Resources

SASE & Zero Trust: How They Come Together to Improve Network Security
shutterstock_1908952546

How do secure access service edge (SASE) and zero trust work together to improve network security? Simply put, SASE works by deploying security via the cloud, and zero trust deploys security in the least privileged access method.

Networking trends have heavily shifted in favor of SASE following the shift to remote work. Gartner predicts that 60% of businesses will adopt or begin to adopt a SASE-oriented model for their company by 2025. Let’s discover more about how SASE and zero trust work together to benefit large enterprise networks.

SASE and zero trust defined

The rise of SASE has made it one of the most talked-about terms in the world of networking, but defining it in simple terms has proved challenging for some. Palo Alto Networks defines SASE as a convergence of several protocols into a cloud-based interface, including wide area networking (WAN), cloud access security broker (CASB), firewall as a service (FWaaS), data loss protection (DLP), and zero trust. 

SASE uses edge computing to solve the inherent bandwidth issues caused by the in-and-out traffic of proxy connections to SaaS programs via the company data center. SASE allows companies to apply their security measures to these programs, preventing possible security leaks and mitigating them when they do happen.

SASE’s emphasis on applied proxy security is due to zero trust architecture, which has recently gained popularity. Traditional models have used a “castle & moat” approach, installing firewall protection around a business’s network perimeter. These models assume, however, that devices within the network are inherently trustworthy. Zero trust architecture never changes these protocols to make such an assumption, demanding that the user or device provide credentials regardless of circumstance. Learn more about the SASE model’s key use cases and benefits and the zero trust security benefits for large companies. 

How SASE and zero trust work together

The new focus on proxy connections is what truly defines both SASE and zero trust. Whereas the company data center used to act as the nerve cluster of business operations, that role has now been fundamentally decentralized and relegated to many smaller data paths coming from remote locations. 
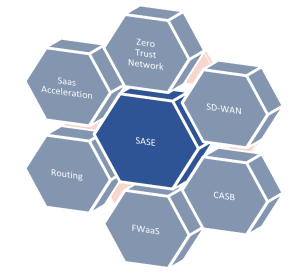
SASE: Zero Trust, SD-WAN, CASB, FWaaS, Routing, and SaaS Acceleration.This decentralization means an increased reliance on programs found in the cloud, as it offers the most convenient access for employees working from home. This is the ultimate goal of SASE; the use of edge computing to redirect traffic from the data center to the cloud, easing the traffic flow.

2020 saw a rise in cybercrime due to an increased dependency on unprotected (or poorly protected) cloud and remote access programs during the pandemic—the FBI reported a 75% increase in daily cybercrimes by June. This exposed a dire need for protocols that offer security rules. Zero trust architecture provided precisely this opportunity, using SASE’s emphasis on edge computing to issue company protections from proxy locations onto cloud-based services.

However, zero trust security doesn’t just provide multiple checkpoints for potential users in a network; it also restricts user access once checkpoints have been cleared. Think of your enterprise network like a concert—the ticket gets you into the venue, but if you want to access the VIP or backstage areas, you need to clear additional checkpoints with an ID badge or backstage pass. With zero trust security, users and devices only gain access to the specific resources they’ve authenticated to—they’ll need to prove their identity and verify their privileges if they want to move to any other area of your network.

These security protocols are critical to successful SASE implementation, as it allows companies to implement their security protocols for SaaS programs and mitigate potential leaks when they do happen. Together, they provide the best of both worlds, allowing for a decentralized network model that still provides the security needed for such a model to exist. It is precisely this balance between access and safety that makes SASE and zero trust what you need to shield your business as you continue to accommodate remote work and distributed users.

Why does my company need both SASE and zero trust?

A SASE network implementation lacking zero trust principles is left drastically exposed to potential cyberattacks. For example, the lack of internal protection ensures that a more extensive information leak could happen.

Consider what would happen if you implemented SASE without zero trust, and a hacker used a compromised account to connect to one of your cloud applications. In addition to stealing the data available in that cloud app, they could potentially jump to other edge resources using the same username and password, or even find an access point to your primary enterprise network. The more lateral movement that account has on your network, the more sensitive data they could exfiltrate. Additionally, the absence of intensive logs ensures that these leaks will consume a great deal of time and energy as network managers attempt to locate and neutralize threats when they arise.

On the other hand, while it’s never a bad idea to put extra measures in place to secure your data, the purpose of zero trust is to handle edge computing access to cloud-based SaaS applications. Zero trust is a welcome addition to your existing security stack and removes the necessity of having a centralized model.

Talking about SASE and zero trust individually makes the two of them sound as though they are mutually exclusive; they aren’t. Zero trust security is one of many programs integral to the successful implementation of SASE. This listing of the key SASE components gives more context regarding how these systems work together.  

Implementing SASE and zero trust protocols

The advantages these two protocols offer companies stem from the way they are used together. When combined, SASE and zero trust allow companies to recenter their business models around a proxy structure. This new model gives employees the flexibility of working from home while ensuring that sensitive information remains safeguarded against ransomware and cyber attacks. Palo Alto Networks cites that the advantages of combining SASE & zero trust are: 

  • Stronger network security
  • Streamlined network management
  • Reduced costs of deploying security at scale
  • A single, holistic view of the whole network

The final benefit listed above is worth further consideration. Instead of viewing your company’s systems as individual pieces, conversion to the SASE model allows you to view your company’s network through a single lens. This helps to streamline your business model even further, making you that much more competitive in the workplace of tomorrow.

We encourage you to read Gartner’s roadmap for SASE convergence for more information. 

Ready to begin your conversion to SASE?

Our products page boasts several options to get you started. Contact us for further questions and get started today! 
Contact Us

SASE vs Security Service Edge: What’s the difference?

Employee tapping into cloud services such as security service edge

Security Service Edge. Is it just another fancy networking term? After all, we’ve already got SASE (Secure Access Service Edge), so why throw another buzzword into the mix?

The truth is, there’s a big difference between Security Service Edge (SSE) and SASE. SSE is a foundational element of SASE, but there’s another necessary component you need to be aware of. In this article, we’ll break down the differences between these two acronyms so you can understand how to achieve better security for your distributed users and devices.

But first, let’s quickly recap why networking and security have become decentralized.

Security Service Edge: An evolving need

The modern workforce is increasingly distributed. In fact, Gartner research shows that demand for remote work will increase 30% by 2030, as Gen Z fully enters the workforce. Another factor is the ongoing coronavirus pandemic, which has forced companies worldwide to accommodate off-site staff.

But the need for distributed networking goes back much earlier than the previous 18 months.

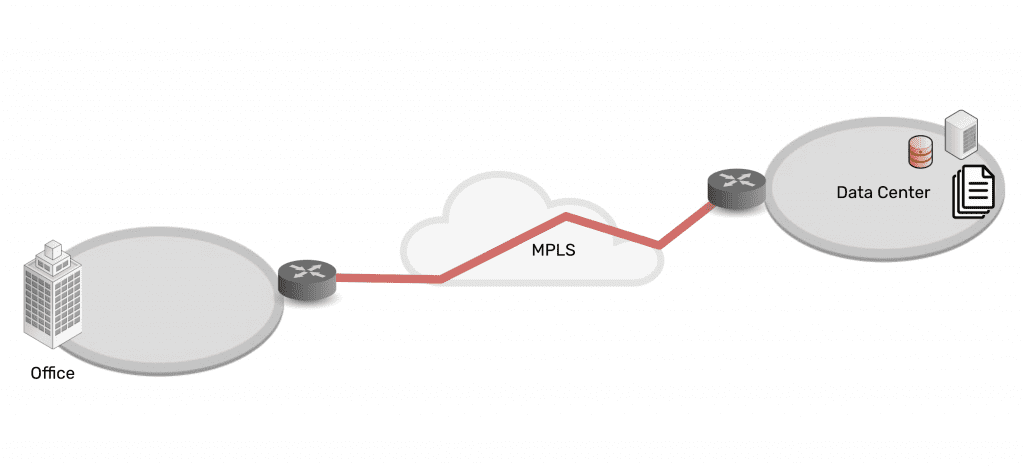
Connectivity and network architectures used to be simple. In the 1990s and 2000s, companies centralized data in the data center, connected branch offices to the data center, and set up simple security measures in between. Most staff worked from the office, which made it easy to provide secure access to and from these enterprise locations and resources.

Network architecture showing simplicity of data center connected via MPLS to branch office

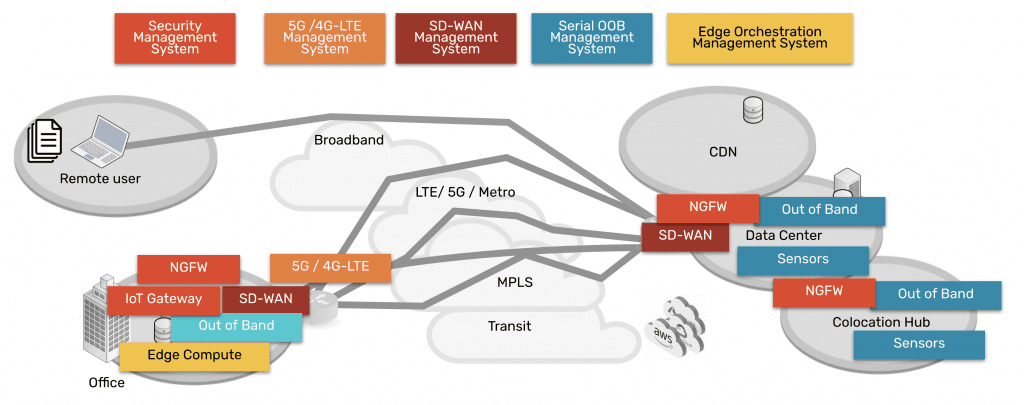
As technologies advanced, companies and their employees discovered that it was becoming easier to work outside of the office. Cloud, SaaS, and edge offerings emerged to create a hybrid infrastructure, as everything moved from being centralized to highly distributed. Now data, security, networking, and computing are everywhere and comprise a complex web of services — owned by enterprises themselves as well as third parties. Securing it all has been an impossible feat for more than a decade.

Network architecture showing complexity of data center, CDN, remote user, branch office, all connected via many paths

Fortunately, Security Service Edge and SASE are models that can address this challenge.

SASE vs Security Service Edge (SSE)

Security Service Edge is a main component of SASE. In the simplest terms, SASE is the architecture that organizations strive to build. It involves delivering networking and security via the cloud, directly to the end user, device, office, etc. instead of having to backhaul through the company’s data center. Aside from SSE, the other main component of SASE is the access portion, which allows the edge services to be deployed and managed. This access portion includes the physical hardware required to connect ‘network’ the edges and services.

Therefore, SASE breaks down into two main components:

  • Security Service Edge, and
  • Access

Keep reading for a detailed explanation of each and why they have been separated out into two pieces now.

Security Service Edge

Security Service Edge (SSE) is the security component of SASE. As Gartner states, SSE ensures secure access to the web, cloud services, and applications. SSE is delivered via the cloud and offers several capabilities, including threat protection, security monitoring, and data security.

Security Service Edge capabilities are available from companies who provide NGFWs (next generation firewalls), SWGs (secure web gateways), and CASBs (cloud access security brokers).

  • NGFWs: Next generation firewalls are implemented to not only secure networking components and services, but also to protect against modern threats that exploit weaknesses in applications.  This type of service secures all the traffic even traffic that’s UDP and also non web based applications including malware exploits.
  • SWGs: Secure web gateways are self explanatory. They are placed between the user and the web, serving as a gateway that provides secure access to the web. Basic functions of SWGs include blocking access to certain websites, preventing unauthorized transfers of data, and inspecting for malicious content.  As its name implies this type of service is limited to web traffic and is used in specific use cases.
  • CASBs: Cloud access security brokers are software that sit between cloud users and cloud applications, to monitor activity and enforce security policies. This software keeps a close eye on data as it moves between cloud environments, SaaS, and users, and enforces security policies to block malware, protect sensitive data, and maintain compliance.  This type of service also has a specific use case of only examining specific cloud applications as its name suggests.

Access for Security Service Edge

In order to use the capabilities of Security Service Edge, you need the physical hardware to deploy services at your locations. This hardware is the access component, and includes SD-WAN capabilities. When deployed, it connects your location to a variety of services (NGFWs, SWGs, CASBs mentioned above) in order to make those services available to your location.

SASE = Security Service Edge + Access

A simple way to think about the SASE concept and its components is to imagine a skyscraper.

Imagine SSE capabilities live in the clouds, and you’d like to bring them down to your enterprise. You’ve got the blueprints to build a skyscraper (SASE) that can connect you to these cloud-based capabilities. But before you can do any of that, you need a sturdy foundation (the access portion) on which to build it all. In other words, your investment in cloud services needs a solid access onramp to those services.

With the right access component, your employees can shuffle in and out of your skyscraper, and easily perform their job functions using SSE capabilities in the cloud. And if you deploy a more robust access solution such as ZPE Systems’ Nodegrid, you’ll be able to maintain your SASE architecture no matter how the clouds change.

How to implement SASE: Focus on Access

When you’re considering implementing SASE architecture, you might be inclined to go to a SASE company to buy everything. But Gartner states that companies that offer the two segments have more mature offerings. 

Therefore, you should focus on purchasing the right solution for the access portion, since it serves as the foundation of your infrastructure at the edge, and then marry this to the right SSE solution for your company. This separation of vendors gives you flexibility to manage several IT systems, and eliminates vendor tie in.

Nodegrid puts the Access in SASE

The Nodegrid SR family of edge routers serves as the access portion in your SASE architecture. A single Nodegrid SR device is a powerful, cost-effective solution to connecting sites to Security Service Edge providers.

The onboard Intel CPU and Linux-based Nodegrid OS offer speed and flexibility. Orchestrate freely across vendors to activate service licenses, spin up VMs, and get your SSE solutions up and running automatically. Additional RAM and storage also help you deploy edge computing for data thinning, de-duplication, monitoring, and other edge workloads.

On top of this, Nodegrid gives you out-of-band management capabilities so you can remotely manage your SASE architecture from anywhere. If you need to optimize bandwidth, investigate data logs for security, or simply power cycle an edge device, you don’t have to get out of your pajamas. Nodegrid gives you secure access to everything via your web browser.

To summarize, the reason SSE has been separated from SASE is that many SD-WAN vendors began to confuse the market by advertising that they offered SASE. This prompted Gartner to point out that there are security-savvy companies that give you more mature security solutions, and to consider such solutions from vendors like zScaler, Netskope, and Acreto, for example. Regarding the Access component, vendors like ZPE Systems provide more capable and robust solutions for connectivity to cloud services, when compared to SD-WAN companies that claim to offer SASE.

Don’t miss out on valuable SSE content. Make sure to sign up for our newsletter using the form below.

If you have questions or would like to speak with an expert, feel free to contact us.


SASE Implementation: A Step-by-Step Guide for Businesses

shutterstock_1902760141

SASE—which stands for secure access service edge—is a relatively new framework that converges wide-area networking with security into one cloud-based service stack. SASE uses software-defined wide area network (SD-WAN) technology to directly connect branch offices and remote users to the cloud and software-as-a-service (SaaS) resources without backhauling traffic through the primary firewall. 

SD-WAN traffic can bypass a firewall because SASE enables the application of enterprise security policies, traffic filtering, and other controls to that remote traffic. By using cloud-based security features like firewall-as-a-service (FWaaS), cloud access security brokers (CASBs), and zero trust network access (ZTNA).

SASE provides numerous benefits to businesses to simplify, optimize, and secure their network edge, including:

  • SASE reduces network latency for both enterprise and remote traffic. SASE separates remote, cloud-destined traffic from the rest of your SD-WAN traffic, so a branch office user doesn’t need to go through an HQ firewall just to access a web service like Office 365. SASE increases the security of the network edge by allowing you to implement the same enterprise security policies and controls to all remote traffic.
  • SASE simplifies and optimizes network administration by consolidating SD-WAN management and edge security controls into one unified platform.

A successful SASE implementation requires a lot of planning, as well as a comprehensive understanding of your existing infrastructure, requirements, and pain points.

SASE implementation: A step-by-step guide for businesses

Each SASE implementation is unique to the business it serves. However, there are six basic steps that most successful SASE deployments follow:

Step 1: Define SASE goals and requirements

During the planning phase of the SASE implementation, the first step is defining the project’s business goals. Identify SASE use cases: What problems need a solution, and what benefits does your organization hope to gain? These use cases will inform how to conduct the following steps—once the goals are clear, developing plans for reaching them is what follows.

For example, you may want to use SASE to secure and optimize SD-WAN traffic. In this case, you already have SD-WAN technology, so the primary goal is to add SASE’s cloud-based network security stack to protect that traffic. 

The following steps determine whether the existing SD-WAN architecture can support SASE and ensure preferred SASE vendors integrate with your existing infrastructure. Once you know why SASE is essential, decide what technologies, processes, and training to implement to reach those goals.

Step 2: Assess the environment and identify gaps

Next is to conduct a thorough assessment of your existing network infrastructure and resources to identify any gaps in the ability to achieve your SASE goals. Use the following questions as a checklist:

  • Do the critical staff members have the knowledge and skills to implement and manage a SASE deployment?
  • Do you need an access on-ramp to the SASE service provider (e.g., an SD-WAN backbone)?
  • Can any existing infrastructure be used with SASE implementation, or do you need to purchase new hardware for your edge?

Review technical documentation and network diagrams, interview key staff about their requirements and training, and examine the security and network configurations to assemble a complete picture of your current environment. Choosing this before defining SASE requirements is vital because a thorough understanding of existing infrastructure can make it much easier to identify pain points and business goals.

With a clear picture of where you are now and what you hope to achieve with SASE in the future, you can start choosing SASE vendors and solutions.

Step 3: Choose SASE vendors and solutions

There aren’t any fully mature, single-solution SASE providers yet. Some vendors provide access via SD-WAN and related technologies, while others offer security service edge via cloud-based network security features. If you have an existing SD-WAN backbone that provides all networking functionality, then a single vendor for a cloud-based security stack is only needed. Otherwise, combine a security service edge solution with an SD-WAN solution to complete SASE implementation.

SD-WAN and cloud security solutions need to work well together. Security service edge providers often partner with SD-WAN vendors to create fully integrated solutions managed from one unified platform. For example, ZPE Systems partners with Palo Alto Networks to provide an SD-WAN on-ramp to the Prisma Access security service edge solution. Enterprises should prioritize integration when evaluating potential vendors.

Step 4: Stage and test SASE deployment

The exact steps to configure services will vary depending on the provider, environment, and requirements.

We recommend creating a staging and testing environment separate from the production environment, so you can perform thorough integration and user acceptance testing before going live with SASE deployment. Test how cloud security stack integrates with an SD-WAN solution, as well as other applications and tools like security information and event management (SIEM), role-based access control (RBAC), and security orchestration, automation, and response (SOAR).

Additionally, perform user acceptance testing with real users and workloads to accurately picture how these changes will affect the people using your systems every day. This will help identify bugs and issues, determine what kind of user training is needed at the cutover time, and optimize the overall user experience to make the transition to SASE easier for your organization as a whole.

Step 5: Cutover, troubleshoot, and support

Even the most meticulously planned deployments can go awry, so companies should have support staff ready to handle any user complaints and technical staff on hand to troubleshoot any configuration or deployment errors. After cutover, your support staff also needs to provide training and documentation for the user base to ensure they know how their daily processes will change and what to do if they encounter any problems.

Step 6: Continuously optimize SASE implementation

Once your SASE implementation is live, you should constantly monitor it and look for ways to improve and optimize. Infrastructures will evolve, as will the technology offered by SASE vendors. As adding new cloud infrastructure, SaaS platforms, branch offices, and other edge computing requirements, you should evaluate the SASE technology to see if additional functionality is needed or desired.

You should plan and implement a SASE deployment that addresses a unique environment, requirements, and business goals by practicing these six steps.

Discover more on how to simplify SASE implementation

A successful SASE implementation requires in-depth planning and preparation, robust testing, comprehensive training and support, and continuous monitoring and optimization. You can make this process easier by investing in SASE solutions that integrate and consolidate management tasks behind one pane of glass. 

For example, you can use Nodegrid’s innovative SD-WAN and remote branch management solutions as your on-ramp to secure service edge technologies. We partner with trusted SASE providers to deliver an integrated platform that consolidates and simplifies your SASE management and optimization.

Want to learn more about how ZPE Systems’ Nodegrid can help your business with SASE implementation?

Call 1-844-4ZPE-SYS or schedule a free demo.

Watch A Demo

Detecting Ransomware on a Network: 3 Critical Steps to Ensure Network Security

shutterstock_1612695883

Ransomware is one of the biggest threats to enterprise network security. Recent findings show that 37% of organizations were affected by ransomware attacks in 2020 alone. These attacks can be financially devastating, costing companies an average of $1.85 million in payouts and damages.

To minimize the impact of a ransomware attack, it is critical to detect and mitigate the infection as early as possible. Still, traditional signature-based firewalls and antivirus software may not be able to detect novel malware (new viruses that haven’t been seen before) and zero-day exploits that hackers frequently use to deploy ransomware on a network. For example, in early 2021, Microsoft detected multiple zero-day exploits that hackers used to attack on-premises Exchange servers. That is why it is essential to have a comprehensive network monitoring solution for preventing, detecting, and removing ransomware on a network. However, it’s essential to understand what ransomware is and how it works before diving into the best strategies for detecting ransomware on a network.

What is ransomware, and how does it work?

Ransomware is malware (malicious software) that takes systems or data hostage until you pay a ransom to the hacker. Usually, hackers will encrypt your files, and after you pay the ransom, they’ll provide an encryption key. On some occasions, the hacker will just take your money and run; other times, they’ll decrypt your files but leave malware on your system so they can attack in the future.

Even in the best-case scenario, where access to your files is fully restored, and the malware is completely removed, you’re likely to face significant business interruptions both during and after the breach. One notable example would be Colonial Pipeline, which faced a ransomware attack in May of 2021. Even after paying the ransom, they had to shut down operations for several days while removing all traces of malware from their network, causing President Biden to declare a state of emergency. 

So, not only do you pay a steep cost for the ransom, but you’ll also pay the cost of lost business, lost consumer trust, and even potential legal fines if regulated data was exposed during the attack.

Detecting ransomware on a network

Detecting ransomware on a network is notoriously difficult until it has fully infected the network and activated its encryption. That’s because traditional security solutions rely on signature-based detection, which means they keep a database of known virus types to compare potential infections. If a piece of malware doesn’t match anything in the signature database, or if that database isn’t kept up-to-date, it could get through firewall and antivirus software.

Since ransomware attacks frequently use novel malware, you may need to instead look for signs of that infection interacting with systems and files on your network. This requires a comprehensive network that gives complete visibility on enterprise infrastructure, including edge networks and remote and branch locations. For example, a SIEM (security information and event management) solution offers a holistic view of your network by collecting logs and event data from all your systems and applications.

Collecting data is only the first step—you also need to know what to look for. Here are some of the signs of a ransomware infection that you can detect through network monitoring:

  • New processes and code. Any unfamiliar processes and programs launching on your systems could be a sign of ransomware taking hold.
  • Registry changes. Unexpected changes to the Windows registry on servers and other devices are also early warning signs of ransomware.
  • Unusual internal and external traffic. Traffic to and from an unknown external source could be a sign of hackers controlling their ransomware or exfiltrating data. Unusual traffic between systems on your network that don’t usually communicate could be a sign of ransomware spreading between devices.
  • Elevated PowerShell scripts. Hackers frequently use elevated PowerShell scripts to propagate ransomware throughout a network.
  • Unexpected file modifications. Ransomware typically works by encrypting your files so that anomalous file modification activity could be a late-stage sign of a ransomware infection.
  • Data exfiltration. Hackers can remove valuable data from your network to use in their ransom requests. If you notice any large-scale data transfers of your network, it’s another late-stage warning of a ransomware attack.

If you catch a ransomware infection on your network before it has encrypted any of your files, then you may be able to remove it the same way you’d remove other kinds of malware. You should isolate infected devices, run malware removal programs, and thoroughly scrub for any lingering trace of ransomware. It may be necessary to reinstall the operating system from scratch to clean the system entirely. 

However, if the ransomware infection has begun encrypting files already, none of these removal methods will reverse that process or restore access to your files. That’s why it’s so essential to prevent a ransomware infection in the first place.

Three critical steps to ensure network security against ransomware

Though there aren’t any security solutions or strategies that provide 100% protection against malware, there are still some best practices to follow to decrease the risk of infection:

1. Simplify your security and infrastructure management.

Often, large enterprises end up with a patchwork of security solutions and infrastructure configurations spread out across many geographic locations and cloud providers. Maintaining security standards, patch management schedules, and monitoring dashboards across many different platforms increases the chances of mistakes leading to a ransomware attack. That’s why you should look for opportunities to consolidate your security and infrastructure management to reduce the number of physical devices you’re responsible for configuring and securing. You should also avoid vendor lock-in by choosing a vendor-neutral infrastructure management solution,  so your security teams can provide the best possible care and attention across your entire enterprise network from one unified control panel.

2. Establish a robust and secure backup strategy.

You need to backup all your critical data systems and fully secure backups. Backups need to be isolated from the enterprise network so ransomware can’t access them from any other infected systems. It is also important to test backups frequently and ensure teams know how to execute disaster recovery plans. If a solid backup and recovery strategy is in place, many of the expenses involved in a ransomware attack may be avoided.

3. Create a culture of security.

Hackers frequently use social engineering tactics (such as phishing) to get their ransomware onto a network. Educating staff on recognizing social engineering attempts, avoiding clicking on suspicious links, and reporting potential security incidents to IT can go a long way towards preventing a ransomware infection. Every member of an organization should feel responsible for enterprise network security and know how to spot and respond to a potential infection.

Detect and prevent ransomware attacks with the right solutions

Ransomware is a major threat to enterprise network security, but you can detect or even prevent an attack with the right tools and plans in place. By utilizing SIEM or other comprehensive network monitoring solutions, you can spot the signs of ransomware moving throughout your network. 

Even better, you can prevent a ransomware attack from occurring at all by implementing a robust backup strategy, educating staff at every level of your organization, and consolidating your security and infrastructure management tools with a solution like Nodegrid. ZPE Systems’ Nodegrid simplifies network management by reducing remote and edge infrastructure into one centralized control panel.

Learn more about detecting ransomware on a network and preventing infections with the Nodegrid infrastructure management solution.

Contact ZPE Systems today.

Contact Us

Understanding Key SASE Components & Benefits

Vector,Of,Men,And,Women,Using,Mobile,Devices,,Computers,Uploading

SASE—secure access service edge—combines SD-WAN technology with network security functionality into a single cloud-native solution. SASE uses SD-WAN’s intelligent routing to connect remote and branch users directly to cloud services, improving network and application performance for end-users. In addition, it is combined with security features like CASB, FWaaS, and ZTNA to provide a secure and scalable network architecture.

Outstanding right? Still, there’s one unanswered question: What are all these key SASE components, and how do they work? In this article, we will dive deeper into the key SASE components and benefits. 


The four key SASE components and benefits

SASE combines SD-WAN networking with advanced security functionality, including cloud access security brokers, firewall as a service, and zero trust network access. Let’s examine each of these features in detail.

1. SD-WAN: Intelligent routing of your WAN traffic

Software-defined wide area network, or SD-WAN, is the critical component of SASE’s networking stack. SD-WAN is a virtualized service that securely and intelligently routes traffic across the WAN. This gives your users a secure and reliable connection to enterprise and cloud-based applications from anywhere in the world.

In a traditional WAN, all remote traffic—even traffic destined for the cloud—gets backhauled to a firewall in a hub or headquarters data center. This causes bottlenecks and delays, impacting network and application performance. 

SD-WAN solves this problem using intelligent and application-aware routing to directly and securely connect remote and branch office users to your cloud and software as a service (SaaS) resources. This increases the performance of both your enterprise and cloud applications and improves the end-user experience.

SD-WAN works by separating the control and management processes from the underlying WAN hardware, making them available as software—that’s why it’s called software-defined WAN. If you’ve already implemented an SD-WAN architecture, you can layer SASE’s security stack on top of your SD-WAN backbone. However, SASE simplifies the security aspects of SD-WAN management, so some organizations prefer to implement them simultaneously.

That’s because, in a typical SD-WAN architecture, you still need to install security appliances and solutions at each branch office and data center to keep that traffic secure. SASE takes SD-WAN functionality and rolls it up with network security features into one unified solution, saving you the time and money of deploying security controls at each remote site. Let’s take a deeper look at SASE’s network security functionality.

2. CASB: Extending your security to the cloud

Cloud access security brokers, or CASBs, are software gatekeepers that sit between your on-premises infrastructure and your cloud-based infrastructure and services. A CASB ensures that network traffic between your enterprise network and your cloud provider complies with your organizational security policies. 

CASBs typically include the following five components:

User  User and Entity Behavior Analytics (UEBA)
A CASB uses UEBA to detect unusual behavioral patterns and enforce security policies on traffic between your enterprise and the cloud traffic.
Cloud Application Discovery
A CASB uses UEBA to detect unusual behavioral patterns and enforce security policies on traffic between your enterprise and the cloud traffic.
Data Loss Prevention (DLP)
CASBs prevent the exfiltration of sensitive and proprietary data according to your data governance policies.
Adaptive Access Control
A CASB analyzes the context of access requests to determine risk, looking at factors such as user location and the time/date of the request.
Malware Detection
CASBs use firewall technology to identify and block malware from entering the enterprise network


A cloud access security broker provides cross-platform security policy management and enforcement from one control panel. When CASB functionality is combined with SASE’s other network security features, you gain even more control over your cloud and edge network security.

3. FWaaS: Unlimited scaling of advanced firewall functionality

Firewall as a service, or FWaaS, is pretty much exactly what it sounds like—a firewall solution delivered as a cloud-based service. FWaaS provides next-generation firewall capabilities such as web filtering, advanced threat protection (ATP), domain name system (DNS) security, and intrusion prevention. Since FWaaS is cloud-based, you can quickly and easily scale it up as your network edge expands to include new branch offices and cloud infrastructure.

In addition to typical stateful firewall features like packet filtering, network monitoring, and IP mapping, FWaaS also uses deep packet inspection (DPI) to identify malware and other threats. DPI analyzes the information contained in the header of each data packet and the content of the packet itself to determine whether the packet is malicious. 

FWaaS also uses machine-learning tools to analyze network traffic for abnormal behavior, which means it can detect novel and zero-day threats that have never been encountered before. This improves upon traditional signature-based threat detection that relies on a database of previously-encountered threats to determine whether to block a connection.

Since FWaaS is a cloud-based service, your provider is responsible for maintaining and upgrading the hardware infrastructure needed to power your solution. This gives you the freedom to scale up your services on-demand without worrying about provisioning new hardware. For example, FWaaS solutions are typically highly customizable, meaning you can add or subtract some security features as your business requirements change. You can also add new data centers, branch offices, and cloud services to your FWaaS solution with the click of a button.

Essentially, firewall as a service provides all the functionality of a next-generation firewall, without the hassle of deploying and managing any hardware. Plus, all of these features are contained within a single unified control panel, which is why FWaaS integrates so well with SASE architectures.

4. ZTNA: Remote access without sacrificing security

Zero trust network access, or ZTNA, is a cloud-based service that applies the principles of zero trust security (“never trust, always verify”) to your remote traffic. Whenever a remote user, device, application, or service attempts to access a resource within your enterprise or cloud infrastructure, ZTNA verifies their identity and gives them only the specific access they need to perform their function. This enables you to provide remote users a reliable connection to enterprise and cloud resources without sacrificing the security of your network.

Traditionally, remote users connect to enterprise networks using a VPN, which creates a secure tunnel to your LAN. Once a remote user authenticates with your VPN, they gain full access to all the resources on your LAN that they’d have if they were on premises. ZTNA, by comparison, only grants access to the specific applications, services, or resources that the remote user needs to complete their task.

ZTNA prevents remote users from seeing any network resources they haven’t been permitted to access. This decreases your attack surface if a hacker uses a compromised account to access your network remotely. The damage done by such an attack will be limited to the few systems they were granted access to during their remote ZTNA session.

Like CASB, ZTNA can also use context-based access control policies to determine the active risk of allowing a remote user or device to connect. For example, you can implement location-based policies that prevent remote devices from accessing your network if they leave a specific geographic area. Or, you could create device-specific policies that require remote devices to upgrade to a particular firmware or OS version to patch vulnerabilities before they can connect.

ZTNA replaces VPNs by giving your remote users access to the enterprise and cloud resources they need while keeping them isolated from your main LAN. Zero trust network access, cloud access security brokers, and firewall as a service are the key components of the SASE security stack, though individual SASE solutions and offerings may use additional or varying technologies as well.


Implementing the key SASE components for your enterprise

SASE combines SD-WAN and network security into one solution that you can manage from a single pane of glass. In addition to SD-WAN, SASE’s key components include cloud access security broker (CASB), firewall as a service (FWaaS), and zero trust network access (ZTNA). Together, this cloud-based functionality gives you greater control over your network, improves your overall network security, and enables easy scaling so your SASE solution can grow with your business.

Putting these key SASE components to work for your enterprise requires a robust and flexible branch edge security and management solution like Nodegrid. ZPE Systems’ Nodegrid is a vendor-neutral platform of hardware and software tools that support SASE deployment and management, including console servers for remote out of band management and zero touch provisioning to automate device setup and configuration.


Learn more about how Nodegrid can help your enterprise put these key SASE components to work.

Schedule a free demo or get in touch with ZPE Systems today.

Contact Us

ZPE Systems announces Nodegrid Data Lake, app marketplace, and sensors to help organizations uncover valuable data for edge operations

CloudApps
Fremont, CA, August 10, 2021 – ZPE Systems launches a new applications marketplace, along with a portfolio of USB-type environmental sensors, meant to help organizations leverage valuable data generated by their IT components. As networks and users become more distributed, it’s imperative that organizations uncover hidden data to optimize availability and user experiences. Nodegrid sensors allow organizations to collect critical data points, for deep insights into their infrastructures, systems, and security logs, among other categories.

Enterprises in telco, content delivery, manufacturing, and other industries can benefit from Nodegrid Data Lake. This application gathers previously uncollected data points to give network admins and engineers visibility into key performance indicators (KPIs). Nodegrid Data Lake helps inspect and visualize data points for:

  • Infrastructure components, such as power, cooling, relay, dry contact
  • Environmental conditions, such as temperature, humidity, air flow
  • System utilization, such as disk usage, processes, memory
  • User experience applications, such as Office365, Zoom, point of sale
  • Security, such as system logs, data logs, GPS data
  • Networking, such as data traffic, application profiling, antenna/tower traffic
  • Previously hidden server and switch logs from IPMI and RS232 serial console

Gartner considers Nodegrid Data Lake a killer app, as it’s indispensable to maximizing business continuity and avoiding downtime.

ZPE Cloud’s additional applications help enterprises and resellers gain further insights and convenience. These applications include:

  • Extended Storage — Save time with centralized file management and add disk space via the cloud
  • Generic Forwarder — Secure distributed users with software-defined perimeter gateways on-prem or cloud-delivered
  • Reports — Drive smart decision making with comprehensive reports on device availability and other metrics
  • Palo Alto Prisma Access — Easily manage Palo Alto security solutions using centralized access
  • ZPE Cloud mobile — Never lose sight of network performance using the ZPE Cloud mobile app, available free on App Store and Google Play

These applications begin an extended product roadmap designed to optimize the configuration, access, and management capabilities offered via ZPE Cloud.

ZPE Systems also launches USB-type environmental sensors, to help ensure optimal utilization of critical physical infrastructure components. These sensors can be managed independently via Nodegrid devices, or via Nodegrid Data Lake for complex event processing. Nodegrid sensors support alert triggers and tracking, and integrate seamlessly with ZPE Cloud’s management interface. Available sensors include:

  • Temperature and humidity
  • Airflow and temperature
  • Smoke
  • Particulate
  • GPIO
  • Relay
  • Proximity
  • Beacon (no alarm)
  • Beacon (with alarm)
  • Door lock with RFID tag

“IT staff struggle with downtime, yet their infrastructure generates so much valuable data that goes to waste,” says Arnaldo Zimmermann, CEO and Cofounder of ZPE Systems. “Our apps and sensors help capture this information. They can use it to prevent device failures, adjust cooling systems, or pinpoint why their Zoom app is suddenly lagging, for example.”

Nodegrid Data Lake and ZPE Cloud apps are now available. Get a free 90-day trial by visiting the ZPE Cloud Apps page.

Nodegrid sensors are also available. Learn more on the Nodegrid Environmental Sensors page.

About ZPE Systems, Inc.

ZPE Systems frees enterprises from today’s networking challenges.

Nodegrid’s Intel-based serial consoles & modular services routers deliver power to datacenter & branch applications, while the Linux-based Nodegrid OS replaces vendor lock-in with limitless flexibility. With ZPE Cloud for fast & secure provisioning, this platform streamlines networking using virtualization, prevents downtime using automation, and offers convenience via remote management capabilities.

Intel-based serial consoles & modular services routers deliver unparalleled power to datacenter & branch applications, while the Linux-based Nodegrid OS replaces vendor lock-in with limitless flexibility. With ZPE Cloud for fast & secure provisioning, it’s the only networking platform to streamline the stack using virtualization, prevent downtime using automation, and offer convenience using in-depth remote management capabilities.

ZPE collaborates with best-in-class technology partners, to add value by integrating with SD-WAN, firewall, IoT, and other solutions. The world’s top companies trust ZPE Systems to provide advanced out-of-band management, Secure Access Service Edge (SASE) platforms, and SD-Branch networking.

Top companies trust ZPE Systems to provide advanced out-of-band management, Secure Access Service Edge (SASE) platforms, and SD-Branch networking.

ZPE Systems is based in Fremont, California with offices worldwide. Visit ZPE Systems website at
www.zpesystems.com.