Providing Out-of-Band Connectivity to Mission-Critical IT Resources

The SASE Model: Key Use Cases & Benefits
shutterstock_1748437547

Secure access service edge (SASE) is the recommended architecture for security and connectivity.  SASE combines wide area network (WAN) technology for robust onramp to cloud and network security services into one cloud-delivered connectivity and security software stack. This allows enterprises to connect geographically diverse workforces securely while reducing network latency and performance issues. 

Though SASE is a relatively new concept, it’s taking the IT world by storm, partially due to the pandemic forcing companies to adopt or improve their remote work capabilities. In addition, SASE addresses the security challenges of using WAN and SD-WAN (software-defined wide area network) technology for remote and branch office (ROBO) network management. 

Let’s examine two essential SASE model use cases and discuss the benefits of integrating SASE into your enterprise network management and security strategy.

SASE model key use cases and benefits

SASE offers numerous benefits for remote and branch office security, performance, and network management, which may be why Gartner predicts that at least 40% of enterprises will have explicit plans for SASE adoption by 2024. Consider these use cases as you decide whether adopting the SASE model aligns with your business goals and network management and security requirements.


SASE use case #1: Replacing VPNs for remote work
 

shutterstock_1687381003

The need to pivot to a remote workforce in 2020 has driven many organizations to prioritize SASE adoption. Enterprises use VPNs (virtual private networks) to handle their limited work-from-home traffic. But scaling up a VPN solution with enough licenses and VPN concentrators to meet an entirely remote workforce’s increased demand can be more expensive. 

Additionally, not all VPN services include centralized remote management to deploy, monitor, and manage remote connections. This could be a minor issue if you only have a handful of remote employees at any given time, but a substantial logistical challenge when your entire workforce must suddenly pivot to work from home. 

If you were relying on a VPN solution for all remote work, you likely found yourself overwhelmed by the need to deploy and troubleshoot hundreds or thousands of new VPN client installations, keep those connections secure without crippling your network performance, and ensure that all your enterprise and cloud applications were tested and supported for VPN access.


SASE model benefits of replacing VPNs for remote work

SASE implementations can solve a lot of these remote work challenges. Instead of creating an encrypted tunnel between each remote workstation and your primary network, like a VPN, SASE connects remote users to nearby points of presence (PoPs) to access enterprise applications and resources in the cloud or the data center. 

All traffic to and from a PoP is encrypted, with other security technologies—such as secure web gateways (SWGs), remote browser isolation, and cloud firewalls—layered to monitor and protect system use. SASE provides additional security by using cloud access security brokers (CASBs) to apply enterprise access control policies to resources outside of the data center, such as Software as a Service (SaaS) tools or other cloud applications.

Despite these robust security controls, SASE still reduces network latency and improves application performance for remote workers compared to a VPN. Instead of relying on a limited number of VPN gateways to handle all your remote traffic, SASE uses a wide network of PoPs to connect remote users to the services and applications they need. 

If a remote user needs to access a cloud application, a PoP can connect them directly to that service, bypassing your data centers and reducing the load on your network. In addition, many SASE providers house their PoPs in the same facilities as major SaaS providers—Microsoft 365 and Salesforce, for example—optimizing the routing paths to these applications and improving performance for remote workers.

IT teams may find SASE easier to manage than VPNs as well. One of SASE’s big selling points for engineers and security teams is reduced network complexity—SASE seeks to replace the physical and virtual VPN appliances you use for remote traffic with a single cloud-native solution. One main advantage is that the end user experience is at its best since the traffic can reach the destination quickly without tromboning (hairpinning) through the datacenter and competing for bandwidth with increased latency. 

This also reduces the amount of time and resources spent on updates and patching, device maintenance, and configuration management for your VPN appliances and other remote and branch network infrastructure. SASE also provides one centralized management platform to control identity management and security policies for the entire enterprise and monitor and manage remote network traffic.

Replacing VPNs with SASE for your remote workforce improves the security of your remote traffic and systems, reduces network latency, increases SaaS and cloud application performance, and simplifies remote network and security management.


SASE use case #2: Optimizing SD-WAN security and performance
 

shutterstock_1097989835

Many enterprises have already jumped from VPN and traditional WAN technology to SD-WAN or software-defined vast area networks. SD-WAN improves upon WAN technology—often using existing public and private WAN connections as a backbone or underlay network—to connect remote workers and branch offices to enterprise services and applications. 

SD-WAN separates the control and management processes from the underlying WAN hardware and makes those functions available as software (hence the name “software-defined” WAN). This virtualized overlay network creates a private, encrypted WAN to connect branch locations, prioritize and route ROBO traffic, and manage and monitor network performance.

SD-WAN does present some security challenges, however. An SD-WAN implementation requires the use of firewalls, intrusion prevention, and web filtering at each branch office, which could mean installing and configuring hundreds or thousands of security appliances. Cyberattacks are becoming a more significant threat each year, reportedly costing businesses up to $4 billion in 2020, so many enterprises are looking to a security-centric solution like SASE to protect their network edge. SASE essentially combines SD-WAN functionality with network security features and bundles them together as a single solution.


SASE model benefits of optimizing SD-WAN security and performance

SASE allows teams to manage both SD-WAN traffic and security from a single pane of glass. SASE solutions roll up security features like CASB, firewall as a service (FWaaS), and zero trust network access (ZTNA) into a single cloud-native service to prevent, detect and mitigate network attacks without the need to deploy multiple security appliances and solutions for all your branch sites. 

For existing SD-WAN implementations, you can layer SASE’s network security features into the WAN appliances at each branch office to provide next generation firewall, intrusion protection, analytics, and unified threat management functionality without purchasing new infrastructure. This means you can manage the security of all your branch locations without needing to install firewalls and other security appliances at each site, reducing network complexity by combining SD-WAN and security into one centrally managed solution.

Plus, since the SASE model connects remote and branch users with SaaS and cloud applications via PoPs, you won’t need to backhaul your branch office traffic through your leading network’s firewall. This means your external-to-external traffic (from branch sites to cloud services and vice versa) bypasses your primary network entirely, reducing bottlenecks and delays and improving network and application performance.

You can use SASE to integrate cloud-based security functionality like CASB, FWaaS, and ZTNA with your existing SD-WAN infrastructure, or you can use SASE’s combined security and SD-WAN service stack to upgrade a traditional WAN architecture. Either way, you’ll reduce network complexity and provide a centralized solution for managing ROBO network traffic and security, all while reducing network bottlenecks and application performance issues.

Take complete advantage of all SASE model benefits

Two of the biggest use cases driving enterprises to adopt SASE include the recent pivot to a remote, home-based workforce and the need to improve the security and management of WAN and SD-WAN technology for branch offices.

The SASE model combines SD-WAN technology with network security features into a unified, cloud-native service stack to provide enterprises with many benefits, including increased security, improved application, network performance, and simplified management for remote and branch office connections.  

To realize a SASE architecture organizations need a robust and extensible branch edge device that can be the ‘Access’ on-ramp to the cloud delivered ‘Secure Service Edge’ (SSE.)

ZPE Systems’ Nodegrid family of hardware and software is a modular, vendor-neutral solution that provides innovative features such as 4G/LTE failover to maintain business continuity, remote out-of-band management (OOBM) for greater device visibility, and zero touch provisioning (ZTP) to automate deployment.  And our SR family can be the on-ramp to SSE vendors such as zScaler, Netscope, Acreto or similar.  Contact us for a deep dive video demo of our solution providing the Access onramp for SSE to flexibly realize the SASE architecture. 

ZPE Systems’ Nodegrid platform is a comprehensive branch networking solution that supports a comprehensive SASE model platform. 

To learn more about how Nodegrid’s built-in automation and ROBO management features can streamline your SASE deployment, get in touch with ZPE Systems today.
Contact Us

4 Things to Avoid When Choosing a VPN

Do you know what to avoid when choosing a VPN? These virtual private networks are commonly promoted as the key to online privacy and security, as they employ dedicated point-to-point connections, tunneling protocols, and encryption. With the sharp increase in distributed workforces and Ransomware outbreaks during 2020, it’s no wonder why consumers and enterprises alike showed significantly more interest in VPNs last year.

But before we dive into what you should avoid when choosing a VPN, here’s a brief refresher on this decades-old technology.

What is a VPN, and what is it used for?

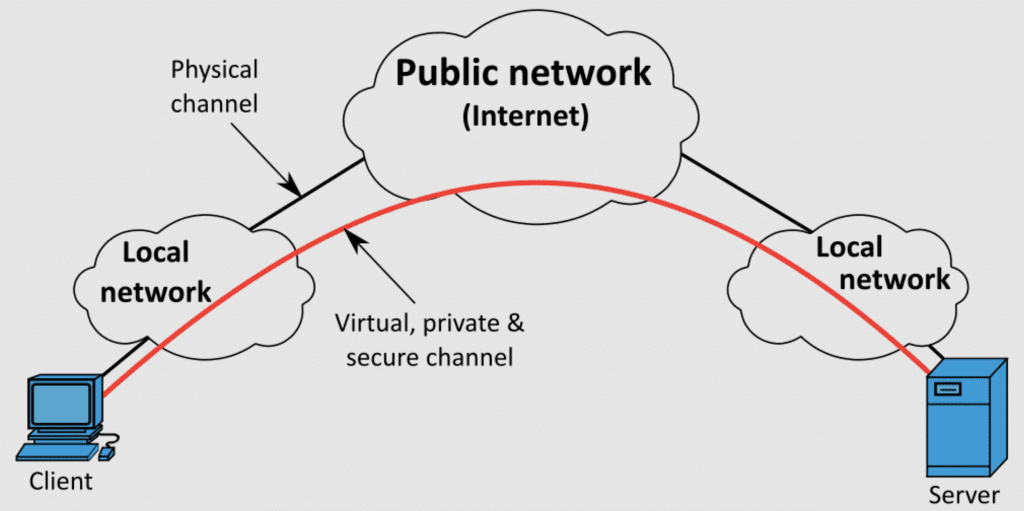
A VPN, or virtual private network, is a private network that allows users to send and receive data over a public or shared network, without having to establish a physical connection with the private network. Essentially, a VPN uses a dedicated tunnel that connects through the Internet and to a private network, such as a company’s intranet.

A remote computer using a secure VPN tunnel to connect through the Internet and to its private office network.

Here’s an example:

The year is 2020, and you’ve just been sent home to work remotely. On your personal computer, you open a browser tab and try to access your everyday business applications, but to no avail. Then you remember the VPN instructions sitting in your inbox. You use them to set up your computer with a VPN configuration, which includes selecting the appropriate protocol and entering your authentication credentials. Once you finish, you turn on the VPN connection, and suddenly you gain access to your applications as if you were sitting at the office.

Of course, there’s more work involved when setting up on the business side, such as selecting the right services and/or components. But once you have these in place, you can start configuring and using your VPN for access to the resources you need.

Enterprises commonly use VPNs to allow their workers to remotely access their private networks and their connected resources, as in the example above. For enterprise IT staff, such as a data center network technician, a VPN gives them access to important data center management tools without exposing their actions or data to the unsecured public internet.

Enterprises also use VPNs to connect multiple networks or offices to each other and/or to a data center location. This is called a site-to-site configuration. Site-to-site configurations can involve multiple sites owned by one organization, called intranet site-to-site; or multiple sites owned by multiple organizations, called extranet site-to-site.

Enterprises are drawn to using VPNs because they can provide several advantages. They offer a convenient way for staff to remotely access resources, but also hide users’ IP addresses and can encrypt sensitive data for added security.

However you should be aware that not all VPN services are created equal. It’s really quite the opposite, so whether you already use one or are ready to shop around, keep in mind these four things to avoid when choosing a VPN.

4 things to avoid when choosing a VPN

False sense of security

Aside from providing remote access capabilities, a VPN’s purpose is to help you communicate securely without exposing your data to public or shared networks. However, VPN (as its name implies) is about privacy, not security. Many VPN service providers give you a false sense of security when in fact your data can still contain malware and spread to your peers. Many VPN vendors also leak and log your data. Aside from connection logs, which typically contain usage data used for optimizing the provider’s operations, there are IP address and traffic logs that some providers employ. Data like your IP address, browsing history, and even recent online purchases can be stored in these logs, which means they could potentially be sold to advertisers, or worse — attackers. When you’re considering a VPN provider, be sure to read the fine print in their service agreement and see whether they log IP addresses, usage, traffic, or other sensitive information.

Slow speeds

Imagine your data center technician is trying to resolve a critical issue and uphold your stringent service level agreement (SLA). Recent social distancing guidelines restrict the technician from resolving the issue on site, so they must connect via VPN for remote troubleshooting. The problem is, it’s peak usage time and the public network is overloaded. What would have been a five-minute job turns into an hour-long waiting game punctuated by unresponsive experiences.

Slow speeds are common with VPNs. That’s because data packets need to be re-routed and encrypted through a VPN server. The farther this server is located from your users, the longer it will take for your data to reach this server. This slowness is exacerbated when you opt for a free VPN service or plan, as these likely don’t offer or prioritize high-speed connections. When considering a VPN, be sure to get a free trial that will enable you to check your speeds.

Potential abuse

If instead of setting up your own VPN architecture, you opt to use a VPN service, keep in mind that there are many providers on the market. And if you choose a provider whose services are operated and maintained in a country where regulation is minimal, such as in China or Russia, you need to understand that your data is vulnerable to abuse. Providers who offer bulletproof hosting (BPH) services in foreign countries, for example, often serve as safe havens for criminals and cyberattackers. Because these operations are typically well insulated against judicial action from governing bodies in the U.S. and other western nations, there’s no legal remedy for customers who suffer from abuse. When considering a VPN service, always choose a trusted provider who operates in a well-regulated country, so you can have the confidence that your data won’t be abused.

Potential abuse

If instead of setting up your own VPN architecture, you opt to use a VPN service, keep in mind that there are many providers on the market. And if you choose a provider whose services are operated and maintained in a country where regulation is minimal, such as in China or Russia, you need to understand that your data is vulnerable to abuse. Providers who offer bulletproof hosting (BPH) services in foreign countries, for example, often serve as safe havens for criminals and cyberattackers. Because these operations are typically well insulated against judicial action from governing bodies in the U.S. and other western nations, there’s no legal remedy for customers who suffer from abuse. When considering a VPN service, always choose a trusted provider who operates in a well-regulated country, so you can have the confidence that your data won’t be abused.

All for the money

This somewhat reiterates the first point above, but can’t be understated. The fact is that with thousands of VPN providers to choose from, many exist solely to make money.

Trusted providers may use RAM-based servers that don’t have the ability to log any of your data. To further protect you, they typically encrypt your traffic using 256-bit encryption or higher, which makes it impossible to hack your sensitive information. These are just a couple features that reliable VPN services provide in order to keep your data private and secure, but unfortunately there are many providers who lack these basic components.

Some providers turn on logs temporarily to identify suspicious users. This can be beneficial in preventing abuse, cybercrime, and illegal activities, but also puts the average user’s data at risk, especially if the provider retains all logged data. Some of the worst VPN providers don’t even employ VPN servers, and instead use peer-to-peer connections, which forces users to share bandwidth and use each other’s IP addresses. Insecure practices like these show that companies don’t truly have their customers’ best interests in mind, and are instead focused mostly on minimizing infrastructure costs in order to make more money.

When choosing a VPN, opt for a trusted provider who can provide secure service to your remote users as well as your branch office employees. Or simply deploy ZPE Systems’ Nodegrid portfolio of flexible branch routers, which serve as your on-ramp to VPN-as-a-service. These make it easy to secure your connections, because you can deploy virtual machines directly on Nodegrid devices and run apps from security leaders like Palo Alto Networks or Fortinet. You could also use Nodegrid routers simply as your access to Secure Service Edge (SSE) providers like Zscaler or CloudFlare, and easily build your Secure Access Service Edge architecture.

Don’t fall into VPN traps

Your IT infrastructure’s integrity is a top priority, especially with cybercrime on the rise and expected to cost $10.5 trillion by 2025. Your staff need secure remote connectivity to maintain network and business operations. But with so many options available, it can be difficult to choose the best approach — VPN or otherwise.

To make sure you don’t expose your staff or your business to unsafe services, contact one of our experts today. We can show you the most secure way to gain remote access to your IT infrastructure, with or without using a VPN! You can take a free tour of ZPE Cloud, which gives you VPN-less access to your distributed infrastructure, and provides completely secure, end-to-end encryption to and from the cloud. Get in touch for a first-hand look.

3 Ways Your Critical Remote Infrastructure Is Costing You

It’s easy to imagine all the ways that downtime can throw a wrench into your critical remote infrastructure operations. Things like scaling, service outages, and tedious management are just part of the job. No matter how much these stand in the way of business, there’s not much that you can do about them, right?

Not quite. In this post, we’ll explore three reasons your complex critical remote infrastructure is costing you, and how Nodegrid is the simple solution that helps you save.

If you’re short on time, here’s a two-minute video explaining how you can cut through the complexity of managing your network.

Deploying critical remote infrastructure

You’re probably familiar with long deployment times for your critical remote infrastructure. Manually provisioning and setting up networks consumes a lot of time and resources. The obvious costs here are the staff wages and device shipping expenses; however, the not-so-obvious cost is the business opportunity that you miss. The longer it takes you to deploy, the longer your location goes without meeting demand or generating revenue.

How can you minimize this cost? By using zero touch provisioning.

Zero touch provisioning uses automation to automatically configure and build your networks. Instead of putting staff on site to manually set up each device in your stack, you can instruct even unskilled staff to simply plug in and boot your devices. Zero touch provisioning does the rest of the work and can bring you online in hours.

Not all zero touch provisioning is the same, though. Most vendors only allow you to use it for their devices or products, which means unless you standardize on their offerings, you’re going to be limited in terms of what systems and services you can automatically deploy. On top of this, you still need to pre-configure devices and put sensitive info at risk, as well as perform manual orchestration and firmware updates.

This is where Nodegrid sets itself apart. Because it features the vendor-neutral Nodegrid OS, it allows you to use your choice of automation tools as well as build custom scripts to orchestrate across devices and environments. This means you can use true zero touch provisioning that extends to every part of your infrastructure — from configuring end devices from different vendors, to bootstrapping VMs, activating service licenses, and setting up your entire network. It offers airtight security as well, because you can completely provision bare-metal devices via ZPE Cloud.

When it comes to your critical remote infrastructure, Nodegrid is your go-to solution for fast, complete, and secure network deployments.

Keeping critical remote infrastructure online

How often does your critical remote infrastructure go offline? When it does, you can suffer losses at a rate of $5,000 or more per minute, according to Gartner. And this only covers the monetary portion. You also need to consider the reputation damage, degradation of trust, and decreased customer satisfaction that result from sudden outages.

If you’re familiar with redundant solutions, you know that these can be a life saver — but on the other hand, they come with two times the number of solutions that you need to purchase, deploy, and manage.

You typically need to deploy two boxes for each function you wish to add redundancy to, and connect them in a high availability configuration. In other words, two firewalls, two routers, two SD-WAN boxes, etc. All this means the initial and ongoing burden of redundancy can be…off-putting.

However, Nodegrid devices feature a powerful hypervisor that allows you to deploy virtualized network functions (VNFs). The onboard, multi-core Intel CPU and Linux-based Nodegrid OS provide you with enough resources to spin up VMs, guest operating systems, applications, and Docker containers directly on Nodegrid appliances. Instead of spending tons of money on more devices that clutter your infrastructure and management efforts, you can host firewalls, virtual routers, SD-WAN solutions, and custom and third-party solutions on one box. You can easily shrink a redundant setup of six devices into two Nodegrid boxes.

Beyond covering your network services with redundancy, Nodegrid also gives you built-in 5G/4G LTE connectivity available via two and four SIM cards, respectively. You don’t have to worry about a main line outage taking down an entire office or store location. Nodegrid automatically switches to your backup cellular connections, so you can keep critical remote infrastructure online and operations running.

Responding to critical remote infrastructure problems

It can be difficult to manage critical remote infrastructure because it’s, well, remote. You may have store locations that are very far away from any skilled IT staff. Or you may operate in an industry such as utilities or oil and gas, where you have critical components distributed across power grids or offshore drilling platforms.

Unless you have a robust remote management tool in place, you’re losing time and money responding to problems. This also means the user experience suffers and is difficult to optimize.

For your business, the losses can start to pile up even before an issue is reported. Your efforts are pulled into managing and dispatching IT teams for on-site support, while users and customers put up with poor network performance or even complete outages.

But when you use Nodegrid and ZPE Cloud, you gain in-depth management capabilities that allow you to fully support your network from a distance. You can save significantly on operational costs by reducing or eliminating the need to roll support trucks. That’s because ZPE Cloud gives you a complete view of your distributed infrastructure, and gives you convenient remote access to manage all your solutions. Use your browser to securely connect without a VPN. You can instantly troubleshoot issues and even reboot devices from thousands of miles away.

Want more tactics to help you reduce downtime?

Watch our free webinar to see how you can cut downtime 50% or more using a Fortune 500 strategy.

Zero Trust Architecture: What to Know About the Latest Cybersecurity Executive Order and How to Implement It

Without a zero trust architecture in place, your business might suffer a setback of $4 million or more due to cybercrime. That’s how much the Colonial Pipeline recently paid out after hackers shut down their oil delivery infrastructure and held its restoration for ransom (reference at bottom). The reality is, this is just a drop in the bucket when it comes to risks and losses overall, but it’s why cybersecurity and zero trust are again in the national spotlight.

On May 12, the President acknowledged the importance of protecting public and private sectors from incidents like these, by signing an executive order to improve the nation’s cybersecurity. One of the order’s main callings is for organizations to adopt a zero trust architecture.

Zero Trust Architecture

 In this post, we’ll examine some goals of this executive order and how it seeks to improve cybersecurity for both public and private entities.

But first, let’s recap zero trust and why it’s critical to protecting more than just sensitive data.

What is zero trust architecture?

A zero trust architecture is made up of systems that verify every user, device, application, etc. that tries to access a business’ IT resources. In networking, this involves creating micro-segments or perimeters within each network, and continuously verifying who and what is granted access.

The philosophy behind zero trust architecture is fundamentally this: trust nothing, because threats are everywhere, always.

Here’s a brief rundown of zero trust’s guiding principles:

  • Always verify — Treat every user, device, application, etc. as untrusted, and always verify to determine access.
  • Deny by default — Assume that your environment is already under attack, and continuously monitor for anomalies and malicious activities.
  • Grant least-privilege access — Allow users, devices, applications, etc. access to only the minimum resources needed to perform their jobs.

Zero trust isn’t a turnkey solution, nor does it rely on a single technology. Instead, it involves transforming network security by taking a holistic approach to safeguard every network interaction. This includes implementing hardware, software, and virtual solutions built with security in mind — from Trusted Platform Modules (TPMs), to multi-factor authentication and user access rights — as well as transforming security processes in your organization.

For a closer look at zero trust architecture and its origins, read our previous post.

Does zero trust architecture matter that much?

Zero trust architecture is key to protecting both public and private sector organizations. Though it can be more difficult to measure how attacks impact less tangible things like public safety or brand reputation, the cybersecurity risks are apparent just by looking at monetary losses.

In 2020, cybercrime cost businesses and consumers billions of dollars in the United States alone. In California for example, total financial losses reported as a result of cybercrime totaled more than $621 million, with leading types of crime including phishing, extortion, data breach, identity theft, and misrepresentation, among others. Other states including Colorado, Ohio, and New York ranked with staggeringly high losses as well, which ranged from $100 million to over $400 million.

Aside from causing financial damages, cyberattacks can open the door to allowing very sensitive info to fall into the wrong hands, which can jeopardize public safety and economic stability. Just imagine what malicious actors could do with classified government information or access to public or private infrastructure.

  • In early 2020, the major IT firm SolarWinds was attacked by hackers using malicious code. They successfully created a backdoor to access information and systems belonging to 18,000 SolarWinds customers, which include Fortune 500 companies and government agencies. The attackers were able to spy on customers and infect even more with malware.
  • In early 2021, hackers attacked on-prem versions of Microsoft Exchange Server using zero day exploits (flaws that haven’t yet been patched by the vendor). They were able to access email accounts and install web shell malware that gave them ongoing admin access to victims’ servers. It’s reported that more than 250,000 organizations have been affected worldwide.
  • In May 2021, hackers gained access to the Colonial Pipeline and shut down oil delivery. For six days, the 5,500-mile-long pipeline was offline. Because it carries 45% of the fuel used on the U.S. East Coast, fuel prices skyrocketed before a $4.4 million ransom payment was made to unlock the compromised systems and restore fuel flow.

These attacks and others could have been prevented — or at least dramatically reduced through better containment — with zero trust architecture in place.

For example, if a hacker attempted to embed malicious code into a device, this device would already be trusted in a traditional network security model. This implicit trust would allow the malicious code to go unnoticed, giving the hacker remote access to sensitive information and systems. But with zero trust architecture, implicit trust is eliminated. In this example, the hacker might still be able to remotely access the device, but micro-segmentation would deny access to other devices, and continuous monitoring and analytics would alert company staff to the anomalous activity. In essence, zero trust would contain the threat and help the organization pinpoint the system that requires attention, without having to suffer potentially catastrophic losses.

For all of these reasons, comprehensive cybersecurity is a must-have for organizations. The President’s executive order aims to help catalyze the rapid adoption of better cyber protection methods such as zero trust.

What does the cybersecurity executive order do?

The Executive Order on Improving the Nation’s Cybersecurity seeks to improve protection for federal government networks, and in turn encourage private entities to do the same for their own networks. To achieve these goals, the executive order focuses on three major areas:

  • Removing barriers to threat information sharing Until now, contractual barriers often prevented companies from sharing information with the government about cyber threats that compromised their security. The executive order removes these barriers, and also requires companies to share information regarding security breaches that could impact government networks.
  • Bringing stronger cybersecurity standards to the federal government
    Systems have historically become compromised due to outdated security models and best practices. The executive order seeks to modernize cybersecurity for the federal government, through the adoption of secure cloud services, zero trust architecture, and multi-factor authentication and encryption. The order attaches a specific time period (see below) by which federal agencies must develop plans for implementing these approaches.
  • Improving software supply chain security
    Software is inevitably shipped with vulnerabilities that can pose significant danger of being exploited. The executive order combats this by establishing baseline security standards for software developed and sold to the government. The order calls for the creation of a pilot program for an ‘energy star’ type of label that will allow organizations to easily determine whether software has been created securely. Additionally, the order creates a concurrent public-private process to foster secure software development; incentivizes the market with federal procurement; and requires developers to maintain greater software visibility and make security data publicly available.

Specifically regarding zero trust, the order states that within 60 days, the head of each federal agency must develop a plan to implement zero trust architecture. The order also states that within 90 days, the Cybersecurity and Infrastructure Security Agency (CISA) must assist the Secretary of Homeland Security and the Administrator of General Services to develop a federal cloud-security strategy and issue appropriate guidance to government-wide agencies. In all, these efforts will modernize the federal government’s cybersecurity as agencies move to cloud services and require more comprehensive network protection.

With the federal government leading the charge, the President hopes that private sector organizations will follow by implementing their own zero trust architectures and best practices. The executive order encourages these efforts through additional steps and resources, which include:

  • Creating a review board— The order calls for the creation of a cybersecurity safety review board. This board will be responsible for analyzing cyber incidents and making concrete recommendations that will improve security.
  • Creating a playbook — The order requires the creation of a standard playbook for responding to cyber incidents. This playbook will ensure government agencies can take uniform steps to identify and mitigate threats, and will also serve as a template for private sector entities to create their own playbooks.
  • Enabling better detection — The order calls for enabling government-wide endpoint detection, response systems, and information sharing to improve detection of cybersecurity incidents on government networks.
  • Creating log requirements— The order calls for improving investigative and remediation capabilities, through the creation of cybersecurity event log requirements for federal departments and agencies.

How can you implement zero trust?

Remember that implementing a zero trust architecture isn’t as simple as deploying a piece of hardware or software. Because the threat landscape is constantly evolving, you need to take a holistic approach in transforming your security from the inside out. Despite the risks that seem to loom larger with every passing day and make you anxious to fortify your networks, keep in mind that achieving zero trust is a gradual process. Here are some tips to help you overcome common challenges:

Think processes

  • Implement gradually — Zero trust is a reimagining of your network security model, so you need to implement it gradually at the process level. This will help you identify what needs urgent attention while also preventing you from making widespread changes that can create security gaps.
  • Perform routine maintenance — From a security standpoint, your requirements are constantly changing (adding customers, adjusting user access rights, etc.). Routine maintenance ensures that you don’t leave vulnerabilities on your network when, say, a new customer requires user group access, or one of your employees moves to a different department.
  • Consider employee productivity — If you’re a little too ambitious to implement zero trust, you could end up causing issues that affect your employees’ ability to do their jobs. Again, take time to gradually implement your zero trust architecture, so that you don’t inadvertently lock out an entire department or blacklist the wrong mail server.
Think technologies

  • Zero trust equipment and applications — Without the right infrastructure components in place, zero trust is only an idea. Bring it to life by deploying equipment and applications that can enforce multi-factor authentication, verify identities, and allow access only as needed.
  • Identity and access management for all equipment — A critical component of zero trust is being able to determine who needs access to your infrastructure. Because you need to limit admission on a need-to-know basis, your design and security teams need the appropriate tools that will allow them to map user access, and also precisely identify users and applications.
  • Complete and cloud-enabled security stack — Gone are the days of simply plugging into firewall devices for total security. With cloud models and distributed networks and staff, you need end-to-end security offered by segmentation capabilities, and also solutions such as Secure Access Service Edge (SASE). These give you the ability to provide secure, least-privilege access, whether users try to connect from HQ or using airport Wi-Fi on another continent.
  • Infrastructure edge platform to isolate, and connect it all — In order to bring everything together and remain in control of your solutions, you need a robust and secure edge platform. Not only will this help you securely fuse together your zero trust architecture components, but it will provide you with protected out-of-band management of your infrastructure. A truly powerful edge platform will also accommodate additional workloads to help detect, analyze, and automatically respond to threats.

Get serious about these zero trust technologies

With cyberattacks on the rise, tomorrow is too late to start thinking about zero trust architecture. Recent executive action means it’s time to get serious about fortifying networks and the sensitive data they handle. Read our next post for a deeper dive into the technologies that can save you from crippling ransomware and malicious attacks.

ZeroTrust-1

Questions? Contact us with your concerns about zero trust or to see a free demo.

What Is the Network Edge, and How Do You Manage It? Watch Our Webinar

What is the network edge?

The network edge consists of systems that are not part of the data center. Think of a typical enterprise network: the data center is at the core, and then there are locations distributed across a market, area, or region, or even across the globe. These distributed locations are considered to be at the network edge, because they require infrastructure that connects them back to the data center and to the rest of the enterprise.

The network edge can cover everything from branch office locations, retail shops, and university campuses, to smart city infrastructures, factories, and faraway mining locations.

The network edge includes critical remote infrastructure

At the business-need level, the network edge must provide its customers with the appropriate experience. This can mean authenticating account info for ATM users, processing in-store transactions for shoppers, or providing real-time sensor readings to drilling crews. All of these require critical remote infrastructure to be in place.

Critical remote infrastructure includes the systems that can communicate with the data center, cloud, and/or other edge locations in order to provide the intended user experience.

Why is network edge infrastructure so important?

The network edge is part of the backbone of distributed enterprise. It’s what allows operations to happen quickly and efficiently outside of the data center. Having the right edge infrastructure in place means the difference between smooth operations that keep customers happy, and constant slowdowns and outages that hamper business growth or even lead to severe losses.

As an example, consider what can happen at a popular retailer’s newly-opened branch location. By using solutions that aren’t optimized for the edge, such as MPLS lines and many disparate devices, the customer experience can be very unresponsive. When it takes 20 minutes or more to check product availability, or several minutes just to process a purchase, the simple logistics slow down business and limit the amount of revenue that the day can bring. Even if shoppers don’t abandon their carts, slow infrastructure means slow business.

But with the right edge infrastructure in place, business changes dramatically. Processing tasks can be performed quickly at the edge instead of having to rely on slow MPLS lines to communicate back to HQ. Customers can get product updates in real time, and transactions can be completed in seconds. Optimized infrastructure is the key to meeting demand at the network edge.

Why you need the best edge network management tools

Just as critical as edge network infrastructure are the tools you use to manage it.

Having distributed locations poses challenges because of physical and geographic limitations. These challenges are only compounded as you deploy your edge farther away and in more remote locations. And with typical management solutions, you’re forced to spend monumental sums of time and money performing on-site support — for even the smallest troubleshooting tasks.

Consider this real-world example: an offshore drilling company requires strong connectivity, which means each rig needs a networking stack. Managing these stacks used to require on-site support, which came with extreme costs and risks. On-call IT teams had to be dispatched via helicopter, sometimes traveling more than 100 miles out to sea to simply cycle device power or install a firmware upgrade.

Luckily, the company deployed out-of-band management, which allowed them to gain remote control of their networking infrastructure. They no longer needed to spend thousands on support or put employees at risk. Their out-of-band solution let them perform even complex troubleshooting and recovery tasks from thousands of miles away.

Want to learn more about this customer and how you can save at the edge?

Watch our free webinar, Managing the Network Edge.

How to Overcome 5 Challenges of Zero Trust Security

How to Overcome 5 Challenges of Zero Trust Security

Zero Trust Security protects your enterprise inside and out. By safeguarding connections with approaches like traffic segmentation and multi-factor authentication, you can ensure total network security. But implementing and maintaining a zero trust posture poses unique challenges that you must be ready to address.

In this post, we’ll cover five challenges of zero trust security and how to help your enterprise stay protected.

But first, here’s a recap about zero trust security.

Zero Trust Security: What is it, and why use it?

Zero trust security is a relatively new approach to protecting enterprise networks and data. Traditional methods follow a castle-and-moat structure, in which the enterprise is the castle and network security is the moat. When a user or device is granted access to the enterprise network (the castle), it is considered trusted and allowed past security (the moat). The problem with this is that it assumes everything that has access to the castle can be trusted, and also that threats only come from the outside.

It’s no secret that attacks are constantly evolving and can come from within an organization. Zero trust security was conceptualized to address vulnerabilities no matter where they may come from. It takes an ‘always verify, never trust’ approach to network security. This means that every user and device is always verified, regardless of whether they’ve had previously been granted access.

Because business is becoming more distributed, organizations are moving away from the castle-and-moat approach. Zero trust security is a potent and thorough security solution that addresses the need for total protection of global networks. For more about its advantages, read our other post about zero trust security.

Now let’s take a look at some major challenges that come with implementing this approach.

5 Challenges of Zero Trust Security

Zero Trust Security is not a turnkey solution

Implementing zero trust security does not mean deploying a single technology or solution. Instead, it’s a reimagining of your enterprise’s approach to network security. In order to achieve a zero trust environment, you need to take a holistic approach and start from the ground up. The biggest obstacle here is that you can be left with hidden gaps in your protection — especially if you’re replacing legacy security solutions.

It would be great if locking down your network was as simple as flipping a Zero Trust Security switch. But the reality is, you need to usher in a new security model. This means identifying users & devices, deploying monitoring tools, setting up access controls, and more. On top of this, you need secure hardware & software that keep your deployment and management efforts secure.

To overcome this obstacle, implement zero trust gradually. This helps you identify key areas that need immediate attention, and also helps you prevent gaps from going unnoticed or becoming significant vulnerabilities. This makes it easier to see and address issues as they arise, especially if you’re rolling back legacy solutions.

Zero Trust Security requires ongoing management

Some security solutions can be configured and deployed, and then left unmanaged for long periods of time. But because zero trust security is an approach (a mindset, if you will), it requires ongoing management to ensure ongoing protection.

Though it does provide hardened security across your distributed networks, zero trust security is not a ‘set it and forget it’ approach. Your business is constantly changing inside and out, whether it’s employees gaining different responsibilities, or adding new sites, staff, and customer accounts. Your network security requires ongoing administration to ensure that all of these activities are kept safe.

Imagine you recently adopted a zero trust model, but your newest deployment includes hardware with outdated & vulnerable firmware onboard. Or, one of your customers suffered a data breach and you suddenly need to protect their accounts from hackers. With zero trust, you need to make sure your devices are properly patched & secure, and you need to have monitoring tools in place to catch malicious activities.

To help with this challenge, it’s beneficial to implement routine maintenance tasks & checkups into your processes. This is where automation tools can come in handy to consistently check for firmware upgrades, or assist with security configuration changes. You can also use monitoring tools, alerts, and notifications to help you stay ahead of attacks.

Zero Trust Security can impact staff performance

Another challenge of zero trust security is the potential for losing productivity. In a way, this obstacle arises alongside the challenge of requiring ongoing management.

As you implement your zero trust posture and continue to manage it, you may unknowingly create issues with security settings. Imagine you adjust your firewall incorrectly or enter a typo into the CLI, which then inadvertently locks out an entire department of employees. Solving this problem may involve a quick fix, or it could take days. Meanwhile, your workers get set back and can’t perform optimally.

The best way to overcome this is, again, by gradually implementing your zero trust posture and routinely managing your solutions. As you make the transition away from your legacy systems, you can address setbacks like these as they come to you. You won’t have to deal with an array of issues all at once, and you can instead pinpoint specific areas that cause disruptions.

Zero Trust Security calls for secure hardware

Many purpose-built appliances come with some form of built-in safeguards. However, part of implementing a zero trust security framework involves securing your hardware. This means patching and updating your existing boxes, or deploying new devices altogether. Remember that if you don’t lock down your assets, including the physical appliances that make up your infrastructure, you remain open to attack.

When you deploy your hardware, there’s always a chance that it might get lost or stolen during shipment. Once it gets installed and set up, attacks could also come from on site, via additional hardware/software integrations, or over your network. The bottom line: you need devices that are secure inside & out.

Combat these vulnerabilities by choosing hardware with trusted CPUs, like those from Intel®, which make it easy to maintain system integrity. This means features like secure boot, signed OS, and trusted platform module that protect you at the lowest levels. Also, look out for features like GPS tracking and geofencing. These help you keep an eye on your devices during shipment, and allow only you to boot & provision once safely under your control.

Zero Trust Security requires flexible software

With security solutions spread across your networks, you run into challenges trying to manage it all. Every vendor has their unique tools and UIs, and there are different limitations in terms of features, capabilities, and integrations. Comprehensive management software goes a long way in giving you control of certain solutions. But you also need software that is flexible and can pull everything together under a simplified UI.

Consider everything that you need to manage, like user roles, access rights, firewall settings, device firmware, etc. Zero trust security is an all-encompassing approach that gives you more protection, but also more work. This is why it’s important to use software that is flexible and can accommodate third-party solutions, regardless of vendor.

One way to overcome this challenge is by using a complete tool like ZPE Cloud. This vendor-neutral cloud platform gives you secure remote access to both your solutions layer and your infrastructure layer — no matter which vendor solutions you deploy on your network. It also helps you connect seamlessly to third-party integrations like Palo Alto Panorama and Prisma Access. ZPE Cloud serves as a single gateway to keeping your network secure, whether you need to manage your next-gen virtual firewalls, or update device firmware with the latest security patches.

If you’d like to learn more, visit our Zero Trust Security page and see how you can deploy a secure network platform.