Providing Out-of-Band Connectivity to Mission-Critical IT Resources

Enterprise Network Management Trends to Expect in 2023 and Beyond
2023 enterprise network management trends visualized as the number 2023 composed of a glowing network of interconnected nodes (2)
With remote working gaining popularity over the last few years, supply chain issues affecting hardware purchasing decisions, and ongoing economic uncertainty forcing staffing squeezes, enterprise network management has grown very challenging in the year 2023. Companies are experiencing complete restructuring of their network operations, from how systems are supported and where they’re housed to how SLAs are met. These changes have also impacted network security, with the overall cost of data breaches rising to $4.35 million in 2022.

Consequently, organizations are now looking for ways to improve the security and resilience of their networks despite staffing shortages and budget squeezes. This article will dive deep into these network management trends and how you should expect to see them develop over the next year.

Enterprise network management trends to expect in 2023 and beyond

SASE (secure access service edge)

Over the course of the COVID-19 pandemic, the mass transition to SASE delivered access to cloud services to remote staff outside of the company’s internal network. In addition, the model allows for network managers to apply their company’s security protocols directly onto SaaS applications used by their employees, allowing for greater security while solving pressing bandwidth issues caused by the initial move to remote work.

SASE is a relatively new resource in the network manager’s toolbox; however, it has quickly become a mainstay of the workforce moving into the 2020s. Gartner predicts that at least 60% of enterprises will move towards a SASE-based model by 2025. As the workforce becomes increasingly remote, we expect these edge-oriented frameworks will become an integral part of the new paradigm shift.

SASE is essentially security and networking delivered via the cloud, which is ideal for accommodating modern distributed workforces. To learn more, read this beginner’s guide to SASE network security.

SD-WAN technologies

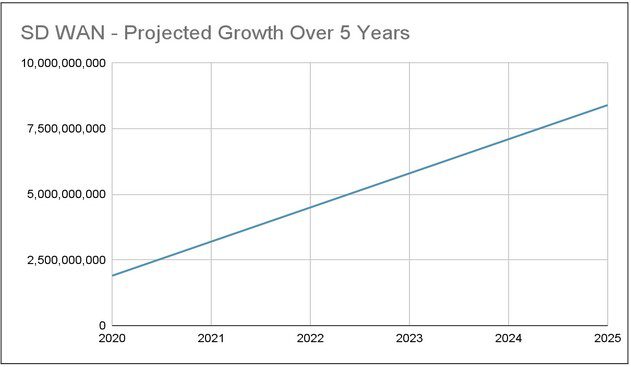
Software-defined wide area networking (SD-WAN) is not a new technology. Still, since the move towards remote work over recent years, it has become the standard for remote workers accessing their company’s network. This boost in popularity is mainly due to the structural emphasis on using software to access software, allowing remote users to access company-wide area networks (WAN) using only software-based entry points. Markets and Markets predicts the industry will grow to $8.4 billion in 2025, representing a 34.5% compound annual growth rate over five years.
SDWAN projectedGrowth
For example, staff working at home no longer need company-issued laptops in order to access their critical applications. SD-WAN similarly revolutionizes the hiring process for companies, eliminating the need to deliver company hardware to an employee so they can begin work. Because of their inherent adaptability, SD-WAN systems constitute a significant boon for companies switching to remote models.

As the next evolution of networking expands and transforms, we expect to see a new level of customizability to remote connections through composable networks, which use modular network components to streamline their business via shared services.

Read more about the benefits of SD-WAN, and see how ZPE is actively working to refine and hone your SD-WAN connection for the future.

Zero trust architecture

It’s no secret that cyberattacks have increased in recent years, taking advantage of security systems that traditionally had not focused on such a software-based model. In response, network management trends have increasingly moved away from the traditional “castle & moat” model used by companies in the past and towards security systems that no longer assume that devices within their network are trustworthy. These models insist that users always verify their credentials to access a company’s SaaS applications.

The advent of these “zero trust” networks has dominated the security industry in recent years and offers various benefits not previously available for remote work. Forbes cites that, when followed correctly, zero trust systems provide:

  • Microsegmentation: Installation of multiple security checkpoints to access applications
  • Universal Enforcement: Integration with unsupported applications
  • Identity & Access Management (IAM): Enforcement of application-level network rules
  • Visibility & Automation: Granular logs and orchestration tools to search for anomalies and suspicious activity

The article also notes that problems within the zero trust architecture exist primarily on the human level, citing that “organizations do not rely on zero trust data solutions” even when the programs are installed. This means that the next generation of zero trust models will have to adequately grapple with their front end, encouraging employees to use them by making them more user-friendly. For more information, we recommend reading about how to implement zero trust policies successfully.

Automation & AIOps

The shift to remote work has put a considerable strain on network managers due to the vast increase in connection points it has created. In the past, network managers had to manually dig through each point’s log to track instances of signing into a network, using an application, sending a file, etc. These procedures are often tedious and consume a great deal of time and energy that would otherwise be spent tackling more specific problems.

New network management trends regulate these granular protocols to automated procedures, which scan for user credentials and other significant information (device, location, application, time, metadata, etc.). These automated systems free up network managers and their teams to handle more focused issues requiring specialized knowledge and skill. In the coming years, we expect to see an even bigger focus on automation with the development of AIOps and machine learning programs that will handle even larger workloads.

A full-blown AI security system is still a ways off. However, the new emphasis on active data management is likely to become the industry standard. Gartner predicts that automation technologies will help lower operational costs by as much as 30% by 2024. As a result, we expect a greater emphasis on automation and AIOps to manage enterprise networks more effectively in the coming years.

Want more information on how to apply automation principles to your network? Read about the key automation infrastructure components that enable end-to-end network automation.

Platform engineering

Enterprise network management involves many different toolkits and workflows, which are often spread across a variety of different vendor solutions. Integrating these services together is challenging since vendors typically operate within closed ecosystems. It’s also difficult to use custom-built tools unless they’re written in a vendor’s chosen programming language. That often means organizations end up with a loosely-connected patchwork of tools to manage various parts of their network. As enterprise networks grow more complex, it’s more important than ever to give admins a centralized, holistic network management platform from which to orchestrate all their workflows.

Platform engineering is an emerging software trend that gives users the ability to “self serve” the tools they need. Essentially, the platform is designed with a set of common, reusable tools and features that you can use to create custom applications to handle network management workflows. These applications are easily integrated together through the platform, so teams can build a single, unified control center from which to monitor and orchestrate the entire enterprise network.

Learn more about the platform approach to network management by reading The Benefits of Vendor Agnostic Platforms in Network Management.

Implementing network management trends for your enterprise   

The most significant challenges facing enterprises in 2023 include remote work, tech talent shortages, network complexity, and the ever-increasing threat of cyberattacks. Recent network management trends show that organizations are adopting technologies like SASE, SD-WAN, zero trust, automation, and platform engineering to help overcome these difficulties.

To learn more about how to build a resilient network infrastructure based on network management trends like automation and zero trust, download the Network Automation Blueprint

Want to learn how to capitalize on these network management trends?

Contact us today or visit our products page to discuss how ZPE Systems Nodegrid can simplify your enterprise networking needs.
Contact Us

What Is a Zero Trust Gateway?

What Is a Zero Trust Gateway(2)
The constant threat of cyberattacks has made network security a top priority for companies in every sector, with Gartner predicting that global cybersecurity spending will reach $188 billion in 2023. However, security continues to get more challenging due to factors like a rise in remote work, an increasing reliance on touchless internet of things (IoT) devices, and the overall decentralization of enterprise networks. It’s hard to create a secure perimeter around the enterprise when its users, devices, applications, and data could be anywhere in the world.

The zero trust security methodology addresses this challenge by shrinking the focus from one large security perimeter and instead creating smaller “micro-perimeters” around each individual resource that needs defending. It’s called zero trust because it follows the principle of “never trust, always verify.” That means each user and device needs to verify its identity and prove its trustworthiness before it can penetrate the micro-perimeter. So, for example, if a cybercriminal uses stolen credentials to log into the enterprise network, they have to pass through many different security checkpoints to see or access any sensitive resources, which increases the likelihood they’ll get caught before excessive damage is done.

One way to implement micro-perimeters and apply zero trust security policies is with a device called a zero trust gateway. This post discusses the technologies that make up a zero trust gateway and explains how they work together to defend enterprise networks.

What is a zero trust gateway?

A zero trust gateway is a device that sits at the edge of the network – or at the top of the rack – and applies zero trust security policies and controls to traffic flowing in either direction. The gateway can be a dedicated security appliance, but it’s often more cost- and space-effective to use a multi-functional device that combines security, networking, and infrastructure management in a single box.

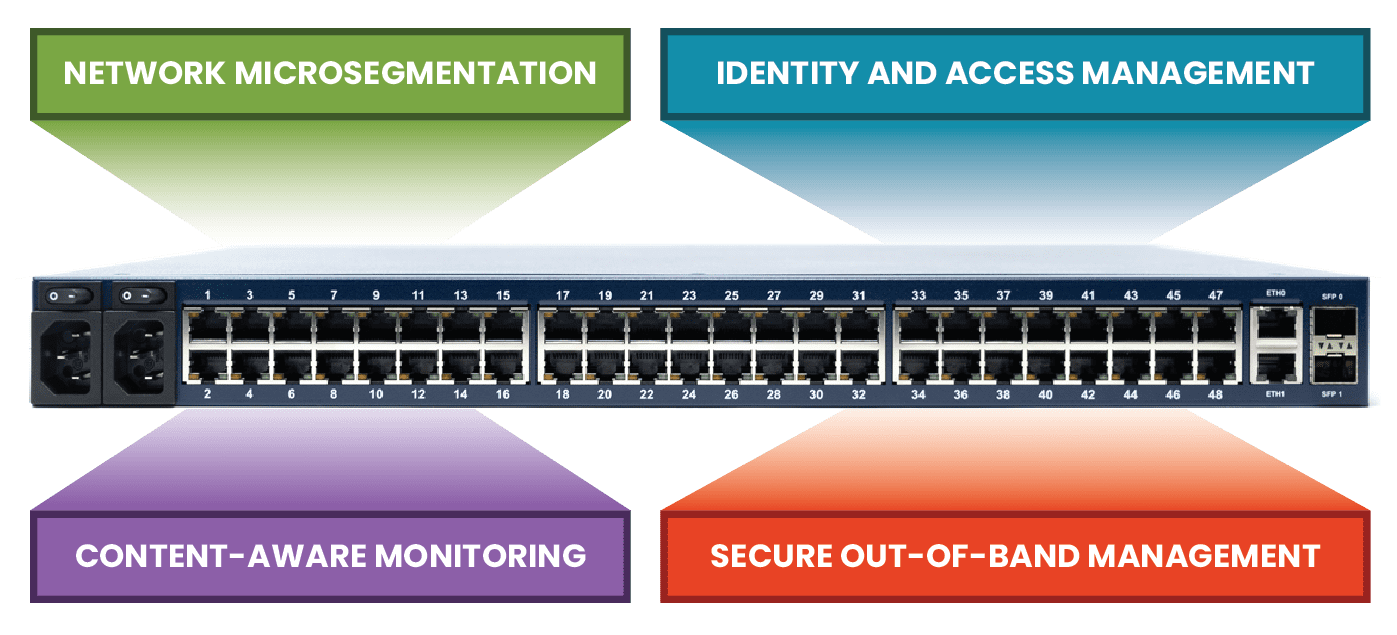
Some of the key features used in an all-in-one zero trust gateway include network micro-segmentation, identity and access management, context-aware monitoring, and secure out-of-band management. There are a small number of mature solutions that deliver all of these features off-the-shelf, but they lock you into their small solution ecosystem and limited feature roadmap. A better approach is to start with a vendor-neutral platform that lets you host and integrate your choice of security applications to create a fully customized zero trust gateway. Let’s walk through how each of these security technologies works and how to combine them into a bespoke zero trust gateway solution.

To see an example of a vendor-neutral zero trust gateway at work, request a demo of the Nodegrid solution from ZPE Systems.

Request a Demo

Network micro-segmentation

A zero trust micro-perimeter is made up of granular access control policies and security controls that are custom-tailored to the specific vulnerabilities and requirements of resources they’re defending. For example, an on-premises database containing sensitive financial records needs different policies than a cloud-based application that doesn’t process any personal information. To implement micro-perimeters, resources first need to be logically organized based on their sensitivity level, who needs access to them, and what their interdependencies are.

Network micro-segmentation is used to separate resources based on these criteria so that micro-perimeters can then be applied. For a device to be considered a zero trust gateway, it must support VLAN micro-segmentation and be able to apply access control rules consistently across all micro-segments.

Identity and access management

In a zero trust architecture, user and device permissions should be limited to only what’s necessary to perform their job role. For example, an HR account used to manage employee records shouldn’t have access to customer financial data, and vice versa. Access policies should be specific to individual micro-segments and resources and need to be applied to all users and devices consistently, no matter where they’re logging in from. That means a remote user should follow the same authentication steps and have the same permissions as they would if they logged in at the office.

For a large enterprise network, this is only achievable with a centralized identity and access management (IAM) solution. An IAM provides a single platform from which to create, manage, and apply security policies. A zero trust IAM also enables best practices like single sign-on (SSO) and two-factor authentication (2FA).

A zero trust gateway needs to integrate with your chosen IAM provider to ensure that policies are applied to both production traffic and management traffic. Some vendor-neutral gateway solutions can even directly host and run third-party IAM solutions, providing a more integrated experience and saving rack space.

Context-aware monitoring

Many successful cyberattacks use stolen credentials gained through phishing schemes and other social engineering tactics. For example, Mailchimp was recently attacked by malicious actors using credentials stolen from employees through social engineering. It’s difficult to detect and contain such an attack because the criminal looks like an authorized user. However, careful monitoring often reveals suspicious behavior, such as logging in from an unusual IP address or time zone, making multiple access requests to areas of the network they don’t usually visit, or transferring abnormally large quantities of data.

User and entity behavior analytics, or UEBA, uses machine learning technology to monitor and analyze account activity on the enterprise network. UEBA creates a baseline of “normal” behavior for individual accounts so it can detect any anomalous activity. UEBA integrates with other security and monitoring solutions, such as IAM and firewalls, so it can compare data from various sources to make more informed decisions. This is one of the ways that zero trust security verifies the trustworthiness of accounts trying to access sensitive resources, making UEBA a critical component of zero trust gateways.

Secure out-of-band (OOB) management

Admins need a fast and reliable way to access remote infrastructure for management, troubleshooting, and recovery. For example, it’s common for a single data center management team to be responsible for customer equipment in multiple DCs distributed around the world for redundancy. These admins can’t physically go on-site every time a firmware update fails or a device loses its IP address. That’s why they rely on remote out-of-band (OOB) management; remote OOB management creates a separate network just for management traffic that doesn’t rely on the production LAN. Admins access the OOB network using a dedicated management device, like a jump box or a serial console server.

This management device is a tempting target for cybercriminals, as gaining control of that device will give them complete control over the connected infrastructure. One way to protect the OOB network is by using a zero trust gateway with integrated management ports. For example, the Nodegrid Net Services Router (NSR) is a modular zero trust gateway that can be customized to connect to any type of device that needs to be managed or secured. The NSR comes with gateway routing and switching capabilities, an embedded firewall, and hardware security features like secure boot and a self-encrypted disk. Nodegrid is also completely vendor-neutral, which means it can directly host or integrate with your choice of third-party security solutions, including next-generation firewalls (NGFWs) and zero trust technologies like identity and access management and UEBA.

The NSR is a modular, open platform upon which to build a fully customized zero trust gateway for large data center deployments. The Nodegrid product line from ZPE Systems also includes a variety of serial console solutions and integrated all-in-one gateway routers to support other use cases, such as edge computing sites, branches, and automated IoT deployments.

A zero trust gateway helps organizations implement micro-perimeters of specific policies and controls to defend sensitive data and other valuable resources. A vendor-neutral, integrated solution like the Nodegrid Serial Console Plus from ZPE Systems makes it possible to combine zero trust security with networking and management functionality to create a streamlined, cost-effective zero trust gateway deployment.

Ready to learn more about Zero Trust Gateway?

To learn more about deploying Nodegrid as a zero trust gateway in your enterprise, contact ZPE Systems today.

Contact Us

ZPE Systems’ Services Delivery Platform accelerates time-to-market

Zero Pain Ecosystemedit

ZPE Systems’ Services Delivery Platform accelerates time-to-market with any app, anytime, anywhere

IT teams can deliver instant business value with the on-demand services delivery architecture

Fremont, CA, April 25, 2023 — ZPE Systems’ Services Delivery Platform is IT’s ‘easy’ button for delivering instant business value. Instead of deploying dedicated NGFW hardware and Intel® NUCs, ZPE’s Intel-based platform runs 3rd party apps at remote locations delivered via ZPE Cloud app marketplace. This speed and flexibility simplify global service delivery and fleet management for manufacturing, healthcare, finance, and other industries, where any app can be automatically deployed from the cloud.

Why is this important?

Private-cloud and on-prem services must run on dedicated systems, which causes infrastructure sprawl. This complexity pulls IT teams away from generating revenue, recovering from outages, and stopping ransomware attacks. Their job becomes managing low-level infrastructure and inefficient delivery pipelines. The Services Delivery Platform alleviates this by giving them the speed and flexibility to:

  • Secure remote locations with cloud-deployed pen test agents & other services
  • Segment edge networks regardless of interface type
  • Eliminate supply chain risks with hardened devices
  • Shrink attack surfaces with swift centralized patch management
  • Collapse device stacks into 1RU or less using virtual services

Services Delivery Platform apps and services

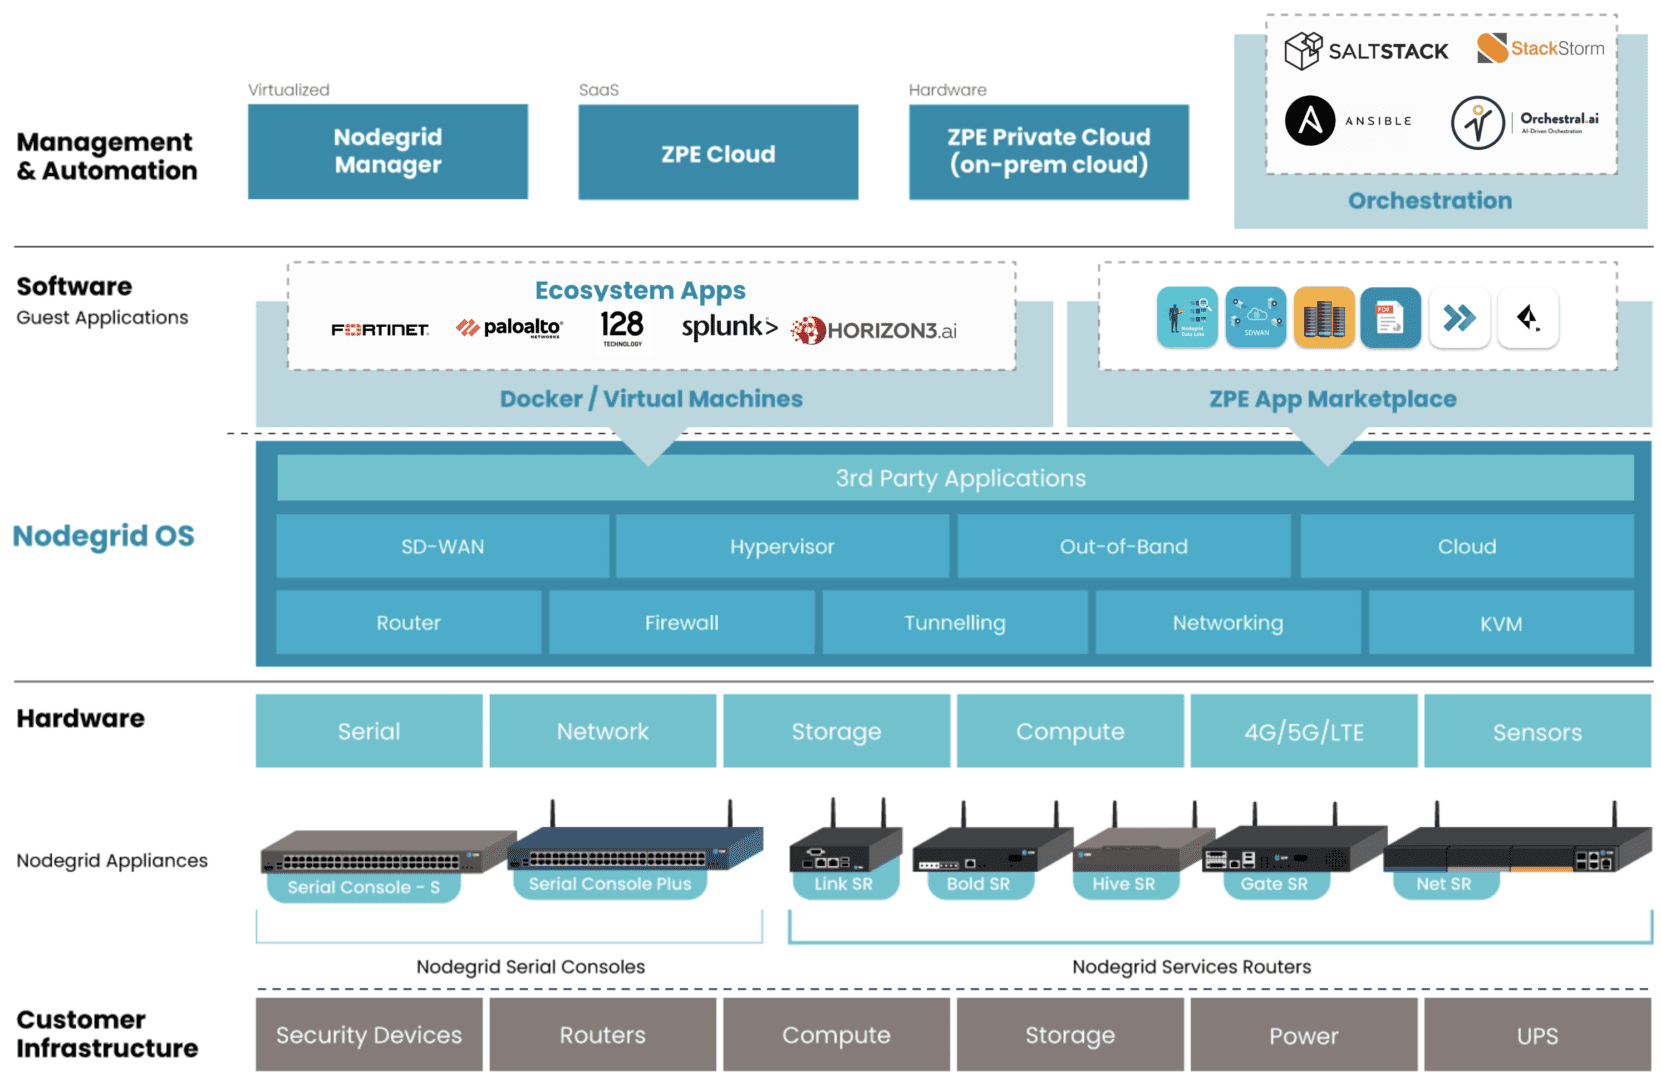
Graphic: ZPE’s Services Delivery Platform is represented as blue blocks. Examples of 3rd-party hosted apps are represented in white blocks under Ecosystem Apps.

The Services Delivery Platform brings to life Gartner’s concept of platform engineering. This platform-as-a-service model allows admins to tailor environments with the right apps for SD-WAN, NGFW, pen testing, and other functions, without battling vendor lock-in or changes in security posture. They also gain a consistent management experience across private-cloud and on-prem solutions.

Teams typically avoid platform engineering because there are no best practices for creating the proper control plane management network on secure devices.

ZPE Systems worked with Big Tech to define these best practices, which enterprises can now apply to private-cloud colo and edge deployments using the Services Delivery Platform. This establishes the resilient control plane management network and platform engineering component, both on a single, multi-function device connected to the cloud.

Enterprises accelerate revenue generation, reduce outage costs, and stop ransomware attacks using this architecture.

How does it work?

Nodegrid edge routers bring dedicated LAN and WAN links through multiple interface types (serial, ethernet, USB, IPMI). These create a secure control plane — a Double-RingTM management architecture — while eliminating the hardware attack surface with security features including TPM 2.0, encrypted disk, geofencing, and fully-signed Nodegrid OS.

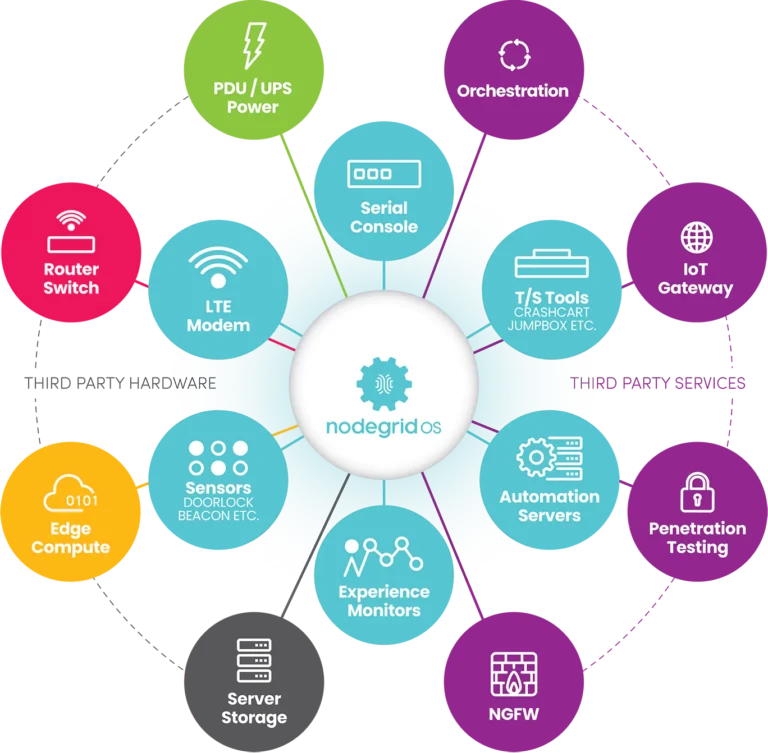
This network is the foundation of the Services Delivery Platform. Along with hosting the management network, Nodegrid devices directly run VMs, containers, and any choice of app using the onboard multi-core Intel CPU and Linux-based Nodegrid OS. This OS also extends automation across environments and devices to give teams end-to-end activation and chaining of SASE, NGFWs, SD-WAN, and any cloud or on-prem solution.

“I’ve been in ops for a long time. Most of your day is spent just figuring out how to get your environments to work right,” says James Cabe, Director, Technical Alliances at ZPE Systems. “The Services Delivery Platform is a game-changer. The whole thing sits right on the Nodegrid box and you can switch or swap out services whenever you need to. Just choose what you want to deploy and go. It’s all done via separate control plane with no attack surface and no exposure to the Internet.”

Where can I find more information?

Go to zpesystems.com/services-delivery-platform to learn more about the Services Delivery Platform.

If you’re attending RSA Conference April 24-27, visit ZPE Systems at booth 4125 between north and south halls and ask for a demo.  Use this code for free RSA expo pass: 52EZPESYSXP

Zero Touch Deployment Cheat Sheet

A zero touch deployment cheat sheet is visualized as a literal cheat sheet used by a student during an exam

Zero touch deployment is meant to make admins’ lives easier by automatically provisioning new devices. However, many teams find the reality of zero touch deployment much more frustrating than manual device configurations. For example, zero touch deployment isn’t always compatible with legacy systems, can be difficult to scale, and is often error-prone and difficult to remotely troubleshoot. This post provides a “cheat sheet” of solutions to the most common zero touch deployment challenges to help organizations streamline their automatic device provisioning.

Zero touch deployment cheat sheet

Zero touch deployment – also known as zero touch provisioning (ZTP) – uses software scripts or definition files to automatically configure new devices. The goal is for a team to be able to ship a new-in-box device to a remote branch where a non-technical user can plug in the device’s power and network cables, at which point the device automatically downloads its configuration from a centralized repository via the branch DHCP server.

In practice, however, there are a variety of common issues that force admins to intervene in the “zero touch” deployment. This guide discusses these challenges and advises how to overcome them to achieve truly zero touch deployments.

Zero touch deployment challenge: The solution:
Legacy systems don’t have native support for zero touch Extending zero touch to legacy systems using a vendor-neutral platform
Deployment errors result in costly truck-rolls Recovering from errors remotely with Gen 3 out-of-band (OOB) management
Securing remote deployments causes firewall bottlenecks Moving security to the edge with Zero trust gateways and Secure Access Service Edge (SASE)
Automating deployments at scale increases management complexity Maintaining control through centralized, vendor-neutral orchestration with version control

Extend zero touch to legacy systems with a vendor-neutral platform

Challenge Solution

While many new systems and networking solutions support zero touch deployment, sometimes there’s still a need to repurpose or reconfigure legacy systems that don’t come with native ZTP support.

Pre-staging these devices before shipping them to the branch is a security risk because the system could be intercepted in transit; plus, they’re likely already deployed at remote sites and need to be reconfigured in place. Without a way to extend zero touch deployment capabilities to those legacy systems, companies often have to pay for admins to travel to remote branches, negating any cost savings they were hoping to gain from reusing older devices.

One way to extend zero touch to legacy systems is with a vendor-neutral management platform. For example, a vendor-neutral serial console switch with auto-sensing ports can connect to modern and legacy infrastructure solutions in a heterogeneous branch deployment so they can all be managed from a single place.

From that unified management platform, admins can write and deploy configuration scripts to connected devices, including legacy systems that don’t support zero touch. Technically, this isn’t zero touch deployment because the system doesn’t automatically download and run its configuration file, but it’s still a way to turn an on-site, manual process into one that’s remotely activated and mostly automated.

Recover from deployment errors with Gen 3 OOB management

Challenge Solution

A new branch deployment almost never goes completely according to plan, and this is especially true when teams are using zero touch for the first time, or aren’t completely comfortable with software-defined infrastructure and networking. In the best-case scenario, when there’s a configuration error, the zero touch deployment aborts, and an admin is able to correct the problem and restart the process.

However, sometimes the deployment hiccup causes the device to hang, freeze, or get stuck in a reboot cycle. Or, even worse, an unnoticed error in the configuration could allow the deployment to finish successfully but then go on to affect other production dependencies and bring the entire branch network down. Either way, organizations must again deal with the expenses involved in sending a tech out to troubleshoot and fix the problem.

The best way to ensure continuous access to remote infrastructure is with out-of-band (OOB) management. An OOB solution, such as a serial console or all-in-one branch gateway, connects to the management ports on infrastructure devices so admins can remotely monitor and control every device from a single place without IP addresses.

This creates a separate (out-of-band) network that’s dedicated to management and troubleshooting, making it possible for teams to remotely recover devices that have failed the zero touch deployment process or brought down production LAN dependencies. Plus, the OOB gateway uses independent, redundant network interfaces to ensure admins still have remote access even if the production WAN or ISP link goes down.

To ensure full OOB management coverage of a heterogenous, mixed-vendor environment, the out-of-band solution should be completely vendor-neutral. An open OOB device also supports integrations with third-party solutions for automation, orchestration, and security. This kind of out-of-band platform is known as Gen 3 OOB. Gen 3 OOB management ensures that teams can remotely recover from zero touch deployment errors no matter what device is affected or how the production network is impacted.

Secure remote deployments with zero trust gateways and SASE

Challenge Solution

Organizations need to secure all devices at all remote sites using consistent policies and security controls. However, for smaller branches and IoT sites, it usually isn’t cost-effective to deploy a security appliance in each location.

Plus, adding more firewalls also adds more management complexity. That means traffic is usually backhauled through the main data center firewall, creating bottlenecks and causing network latency for the entire enterprise.

Using zero trust gateways and cloud-based security services, companies can move security to the branch without the cost and complexity of additional firewalls. An all-in-one, zero trust gateway solution combines SD-WAN, gateway routing, and OOB management in a single device. It also supports zero trust authentication technologies like SAML 2.0 and 2FA. A zero trust gateway also needs to support network micro-segmentation, which will allow the use of highly specific security policies and targeted security controls. Plus, by enabling software-defined wide area networking (SD-WAN), a zero trust gateway facilitates the use of SASE.

Secure Access Service Edge (SASE) is a cloud-based service that combines several enterprise security solutions into a single platform. Zero trust gateways use SD-WAN’s intelligent routing capabilities to detect branch traffic that’s destined for the cloud or web. This traffic is directed through the SASE stack for firewall inspection and security policy application, allowing it to bypass the main security appliance entirely. SASE helps reduce the load on the enterprise firewall, reducing bottlenecks and improving performance without sacrificing security.

Scale zero touch deployments with centralized orchestration

Challenge Solution
Zero touch deployments occur (at least in theory) without any admin intervention, but they still need to be monitored for failures. Keeping track of a handful of automatic deployments may seem easy enough, but as the number and frequency increases, it becomes more challenging. This is especially true when companies kick off large-scale expansions, deploying dozens of devices at once, all of which could be plugged in at any time to begin the automated provisioning process. Plus, different devices need different configuration files, and admins need a way to work together without overwriting each other’s code or duplicating each other’s efforts. A vendor-neutral orchestration platform provides a central hub for network and infrastructure automation across the entire enterprise. This platform uses the serial consoles and OOB gateways in each remote location to gain control over all the connected devices, so network teams can monitor and deploy all their zero touch configurations from one place. An orchestration platform is the single source of truth for all automation, so it needs to support version control. This ensures that admins can see who created or changed a configuration file and revert to a previous version when there’s a mistake.

Simplifying zero touch deployment with Nodegrid

Zero touch deployment can be a hassle, but using vendor-neutral management systems, Gen 3 OOB management, zero trust gateways, and centralized orchestration can help organizations overcome the most common hurdles. For example, a vendor-neutral Nodegrid branch gateway deployed at each remote site helps you extend automation to legacy systems, provides fast and reliable out-of-band access to recover from issues, enables zero trust security & SASE, and gives you unified orchestration through the Nodegrid Manager (on premises) and ZPE Cloud software.

Ready to learn more about zero touch deployment?

Nodegrid has a solution for every zero touch deployment challenge. Schedule a demo to see how Nodegrid’s vendor-neutral platform can simplify zero touch deployment for your enterprise.

Contact Us

ZPE Systems Partners with Atsign to Add Zero Attack Surface Technology

ZPE & Atsign

ZPE Systems Partners with Atsign to Add Zero Attack Surface Technology to Industry-Leading Infrastructure Management Solutions

ZPE Systems and Atsign to demonstrate solution at RSA Conference (booth 4125) April 24 – 27, 2023

FREMONT, Calif. and SAN JOSE, Calif., April 19, 2023 (GLOBE NEWSWIRE) — ZPE Systems, the leading provider of open infrastructure management solutions, and Atsign, a leading provider of privacy and security solutions, have announced a strategic partnership. This partnership combines ZPE’s award-winning networking solutions with Atsign’s cutting-edge security technology, to help customers achieve zero attack surface.

This joint solution enables organizations to manage network infrastructure from anywhere in the world, and with zero open TCP/UDP ports or static IP addresses. Attackers cannot identify or fingerprint the device or services. This stops adversaries from persisting or moving inside your organization. Pairing ZPE with Atsign enhances efficiency and security, giving customers access to comprehensive network management and security features that include advanced authentication and access control, centralized management of user accounts, and real-time monitoring and alerting.

“We are thrilled to partner with Atsign and help customers address the growing complexity of network management and security,” said James Cabe, Director Global Alliances and Strategic Sales at ZPE Systems. “Atsign’s advanced security technology allows organizations to easily deploy our joint solution and implement the highest level of security possible, while streamlining network management.”

“We are excited to partner with ZPE Systems to deliver world-class security to their world-class network infrastructure solution,” said Kevin Nickels, CPO of Atsign. “Our network security solution will enable customers to take advantage of ZPE’s network routing and administration tools with peace of mind knowing their systems are completely secure.”

The joint solution will be shown at the RSA conference (ZPE booth 4125) in San Francisco April 24 – 27, 2023. More information can be found at https://zpesystems.com/company/events/rsa-conference-2023/

About Atsign

Atsign is an award-winning technology company that believes the privacy and security of every person, organization, and device is a fundamental right, and they’re working towards making it a reality. They won the 2022 IoTSF Champion award and the 2023 IoT Global Award for Securing IoT. For more information, visit www.atsign.com.

About ZPE Systems

ZPE Systems provides the best, most resilient, and secure solutions that support infrastructure reliability and holistic security for medium to large enterprises and digital service providers. 6 of the top 10 global tech giants trust ZPE Systems’ Cybersecurity Delivery Platform for Automated Zero-day Infrastructure Patching and Ransomware Recovery & Remediation for Datacenter, Edge, OT, and MSPs. ZPE Systems solutions eliminate human error and allow IT to easily manage, secure, and scale a resilient infrastructure with Intel-based serial consoles, services routers, sensors, zero-touch zero-trust provisioning and cloud-managed out-of-band automation. For more information, visit www.zpesystems.com.