Providing Out-of-Band Connectivity to Mission-Critical IT Resources

Better Application Hosting & Guest OS

Better Application Hosting & Guest OS

As your business continues to expand, your infrastructure needs to adapt and grow to keep up with increases in demand. Rack space in your data centers comes at a premium with little to no additional room for unnecessary equipment. Cooling and power costs must also be considered whenever any additional equipment is needed. This creates a delicate balancing act between function, need, and cost that requires decision makers to think carefully before approving any new deployments.
Branch Locations

Branch locations also add to the puzzle as most will need at least some hardware to be located on site in order to support basic business operations. The more branch locations you have, the more hardware is required, along with all of the cost associated with maintaining it. In some situations, your new branch location may not even have a pre-built server room. This can lead to additional construction costs to create one, or you may need to make use of a storage room that does not have independent cooling available. In this case, you may be greatly limited to how much hardware you can reasonably accommodate without worrying about overheating. 


Virtualization Technology

Fortunately, virtualization technology is growing rapidly and can address many of the issues that companies are facing in today’s ever evolving market. With virtualization, you are able to run more applications using substantially less hardware. This leads to a significant reduction in capital spending on hardware, as well reduced power consumption and cooling costs. For branch locations without dedicated server rooms, you can now worry less about rack space and overheating issues and focus more on critical tasks.

While virtualization can offer great solutions to many key issues that companies today are facing, it is not without its own set of challenges. Even if several virtual instances are running on a single piece or hardware, that hardware must still be managed. With remote branch locations, this may offer an additional challenge as there may not be a dedicated team on site. On top of this, virtual machines are managed differently than physical hardware which can add an additional layer of complexity to the entire infrastructure.  There is also an increased need for managing network infrastructure like switches, routers, firewalls or even storage hardware. System admins are forced to use multiple methods of managing a growing proliferation of device types, protocols and brands.


Choice Matters

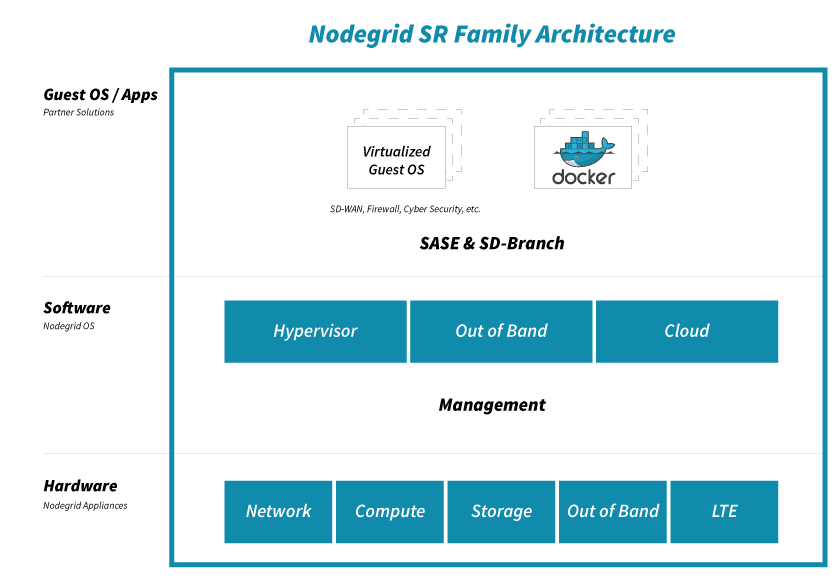
Selecting the proper solution to suit your business needs is critical. ZPE Systems Nodegrid solution offers a best in class “Open Infrastructure Management Solution™” for in-band and out-of-band access and control of Network, Compute, Storage and Power Devices in both physical and virtual IT Infrastructures. The NodeGrid® platform easily consolidates, organizes, and simplifies the need for a complete and highly secure remote access and control solution.

ZPE’s Nodegrid SR family of Open Infrastructure Management Solutions have been tested to work with a full suite of Virtualized Network Function (VNF) Applications including Darktrace, 128 Technology, Palo Alto Networks, Ubuntu, HP, SAP, Fortinet, and more. You can see the full list of prevalidated virtual applications here.


Ready to Learn More?

For more information on ZPE’s full product line, please visit our products page.

Have a specific question or want to experience a live demonstration for yourself? Reach out to us via our contact page. We’re here for you!
ZPE Systems Announces Integration with Palo Alto Networks to Provide Enhanced Network Security


ZPE Systems + Palo Alto Networks

Fremont, CA, August 21, 2020 – Today, ZPE Systems, Inc., a leading solutions provider for network infrastructure management solutions, announced an integration with Palo Alto Networks to provide enhanced networking, out-of-band management and security capabilities to branch locations for customers, including those with very remote locations.

The integration combines ZPE Systems’ Nodegrid hardware and management software with Palo Alto Networks VM-Series virtual firewalls. ZPE Systems’ Nodegrid platform with Palo Alto Networks VM-Series allows enterprises to consolidate and customize their network infrastructure, while safeguarding their traffic with the advanced security of a virtual firewall. Customers benefit from flexible, reliable network management and connectivity, along with proven protection for in-band and out-of-band paths. 

ZPE Systems’ Nodegrid Services Router (NSR) solutions come in a variety of form factors for various applications, resulting in a network stack that’s easy to deploy, scale and manage even in isolated and obscure locations. These NSR solutions provide additional value thanks to reliable backup connections via 4G LTE cellular failover, which give redundancy to connected devices while improving rapid response and Mean Time to Innocence (MTI).

According to ZPE Systems’ CEO and Co-Founder Arnaldo Zimmermann, “Together, Palo Alto Networks virtual’ firewalls and our Nodegrid SR solutions give customers a secure and streamlined infrastructure, with centralized management that puts everything in one place — firewalls, servers, routers and even power controls.”

“With this integration, customers can extend their network security with VM-Series and add our SD-WAN and IoT Security subscriptions that can be managed from a single interface, plus deploy Wi-Fi with ZPE Systems’ NSR solution,” said Mukesh Gupta, Vice President of Product Management, VM Series at Palo Alto Networks. “This enables organizations to have universal customer premises equipment capabilities, known as uCPE, to help protect their branch locations.”

About ZPE Systems, Inc.

ZPE Systems is rethinking the way networks are built and managed by providing software-defined, vendor-neutral infrastructure management and networking solutions.

ZPE Systems’ Nodegrid® platform consolidates, organizes, and simplifies the need for a complete remote access and control solution; Nodegrid solutions address the OOB management needs of the data center, unifies edge networking environments, manages converged infrastructure and provides intelligent automation. ZPE’s smart, consolidated IT management solutions reduce downtime, deliver OPEX savings, and extend the reach of IT workforces.

ZPE’s global headquarters is located in Fremont, California with offices throughout the US and globally in Ireland, India, Brazil and Japan.

ZPE Systems, the ZPE logo and Nodegrid are registered trademarks of ZPE Systems, Inc.

To learn more, visit www.zpesystems.com

Transform Enterprise Network Operations With Application Hosting & Guest OS

Application hosting and guest OS are transforming enterprise network operations. With the ability to globally distribute software via the cloud and take advantage of applications regardless of operating system requirements, application hosting and guest OS deliver major benefits to NetOps teams. Here’s a more detailed look at what they are, how they help business, and how they’re made better by Nodegrid.

Application Hosting and Guest OS

What Are Application Hosting and Guest OS?

Application hosting is essentially putting your apps in the cloud (think SaaS). Instead of having applications installed locally on each device, you can host them on a server. This way, you can virtualize your enterprise applications and have them delivered to clients throughout your organization.

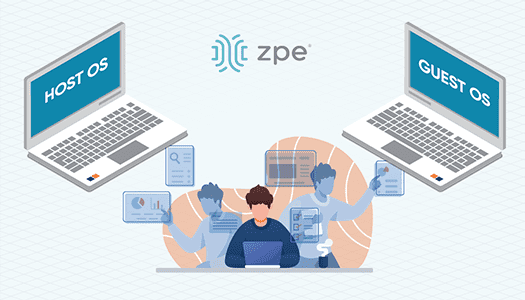
Because virtualization requires virtual machines (VMs) to run in your environment, guest OS becomes a key component in application hosting. Guest OS is the software that is installed and running on a VM, and it’s this software that dictates what applications can run on that VM.

Here’s another way to look at it using an example: you want to use three separate applications on a device, but your device’s operating system, or host OS, is compatible with only one of the applications. The two others require Windows Server 2012. You don’t have to do without, because on the device you can deploy a VM using Windows Server 2012 as the guest OS, which then allows you to take advantage of the remaining applications.


What Issues Do They Address?

You’re probably used to juggling network infrastructure solutions throughout your organization. It takes time and resources to deploy, manage, and maintain physical devices at each location. The same goes for all of your applications – installing, updating or rolling back, and troubleshooting can add to your management headaches.

  • It can take days or weeks to get a new service up and running
  • Having localized applications bogs you down with on-site support
  • Your edge network suffers from inconsistencies, leaving you open to security threats and disruptions

Application hosting and guest OS drastically uncomplicate how you manage your infrastructure, by eliminating these issues.

  • You can deploy and distribute applications on demand
  • You can make applications available globally and manage them remotely
  • Your edge network is standardized, with the latest application updates and fixes keeping you safe

You don’t have to worry about the problems or interruptions that can occur from, say, having different software versions across your network. Application hosting and guest OS let you deliver a consistent experience no matter how distributed your infrastructure might be.


How Do Application Hosting & Guest OS Help Business?

The business benefits of application hosting and guest OS can be summed up with one word: savings.

For starters, you save space and resources at each location, which helps you slash CAPEX and OPEX costs. When deploying, you no longer need to spend time and money on many pieces of hardware, or put together a hodgepodge stack that sacrifices on capabilities. You can instead deploy consolidated devices running all the OSes and applications you need, for a network that’s flexible and adaptable. And because ongoing maintenance can be performed remotely, you don’t need to put support staff on-site.

You also increase uptime, because having a virtual presence allows you to respond fast from anywhere.

Your network staff benefit from easier deployment and maintenance. To bring a site online, they don’t have to manually install and configure every device and app. Instead, they can take advantage of zero touch provisioning, which builds the network itself and helps make applications available quickly. To maintain and manage the network environment, your staff have a virtual presence that lets them update apps, install patches, or troubleshoot as needed — without having to commute to the location and physically connect to devices. Application hosting and guest OS also simplify integrations within your network, and they boost security by centralizing your authentication processes.


How Does Nodegrid Make Them Better?

ZPE’s Nodegrid hardware and software allow you to host applications and guest OSes, putting both layers in one place for simplified management. Not only can you easily perform app installations and maintenance, but you can also troubleshoot any issues should you have problems with the guest OS layer.

Nodegrid also makes it easier to deploy your own tools and utilities. If you’ve developed custom applications, whether for added security, better traffic routing, or faster kickoff configuring, you can deploy them directly on Nodegrid devices. You don’t have to find third-party hosting providers, and can instead use Nodegrid to get your private cloud and applications running in no time.

Consolidated appliances support automation and containerization using common tools like Puppet, Chef, Docker, and Kubernetes. These devices and capabilities deliver a vendor-agnostic system to help you free up rack space and streamline your NetOps workload. Since your network functions can also be hosted on a single Nodegrid device, you no longer need to separately maintain additional IP addresses, either.

For the ultimate in uptime and accessibility, Nodegrid provides you with a secure out-of-band management path. This allows you to remotely manage guest OSes and applications across your network, without having to put teams on-site. This secure OOB network is also accessible via 4G/LTE cellular failover. Should any main-line outages or disruptions occur, you can keep your network running and continue to manage your applications no matter where you are.

Keep up with the latest in application hosting, zero touch provisioning, and more networking innovations from ZPE. Visit our blog page for tons of free resources to help turn your network into a powerful asset.

3 Ways Docker Improves Network Management

Docker is the best way to deploy applications. There are several ways Docker improves network management. From being compatible with almost any programming language and machine, to its ability to run multiple containers in the same infrastructure, Docker has a lot to offer when it comes to automation and out-of-band management (OOB). But before we dive into the benefits of implementing it into your strategy, let’s take a closer look at what Docker is.


What is Docker?

Virtualization using virtual machines (VMs) was a game changer when first introduced. It allowed businesses to take full advantage of their network resources by giving them the ability to efficiently run multiple OSs and apps on the same host. When deploying new hardware, VMs significantly cut down the time it took to set up devices, allowing teams to configure resources in minutes instead of days.

But VMs have limitations. Aside from having to boot up an OS, each new addition requires virtual resources to be allocated (such as RAM), which can quickly strain your system when running multiple VMs. When porting, VMs typically cause compatibility issues, too, and they can’t share data volumes.

Docker is equally as revolutionary as VMs, and has been rapidly adopted by organizations since its initial release in 2013.

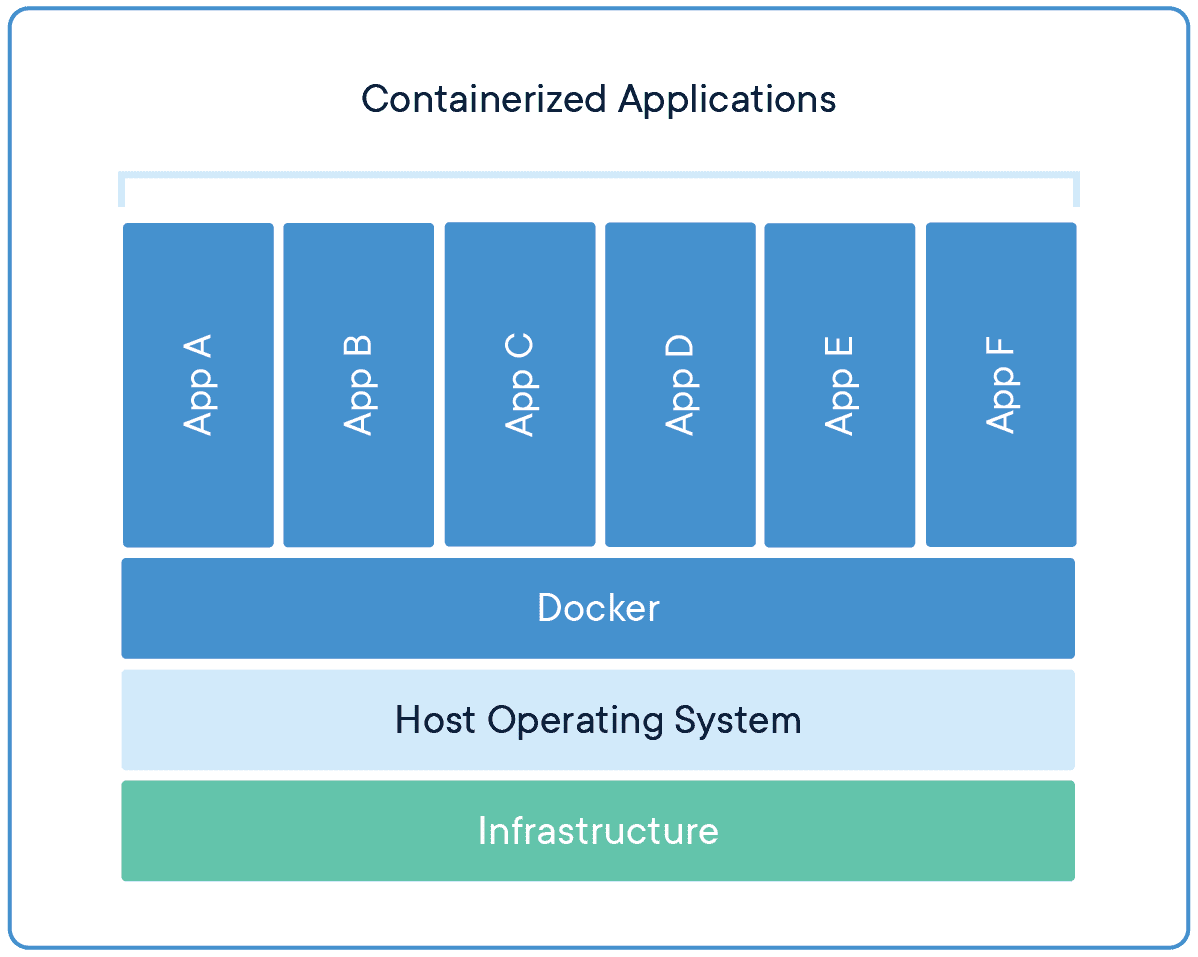
Docker takes virtualization in a different route, using something called containerization. Docker containers are lightweight and automate deployment of applications so they can work in different environments (i.e. on different machines). Each container is essentially its own software package that contains the dependencies to run an application, such as code, configuration files, processes, networking info, and sometimes even pieces of an OS.

So instead of running separate desktop environments, as with resource-hungry VMs, Docker containers run on a single system kernel and allow you to maintain isolated applications that work properly — regardless of what machine they’re running on.


How Docker Improves Network Management

Modern OOB networks employ an array of sophisticated tools, like those that support monitoring, management, and automation. Using Docker containers means that you can deploy applications and know that they’ll work on any resource, because Docker works on the client side. Docker can also act as a service and be deployed onto any server. And because all application dependencies are contained directly on the image, management is easier as well.

On a high level, using Docker containers brings these advantages to OOB:

  • You save on resource allocation, because containers require only a small amount of server space.
  • You can gather info and monitor your system by easily deploying lightweight apps.
  • Because containers are highly portable, you can use them for diagnostics, even when devices go offline.
  • Adding to the previous point, you can use containers for quick deployments, as well as for maintenance and backup.
  • With regards to things that require safeguarding, such as temporary configuration data or emergency recovery data, containers allow you to add them quickly on-demand.

On top of all these advantages, Docker improves network management by giving you three major benefits.


Docker Simplifies Virtualization

VMs allow you to run any platform — along with its unique configuration — on your infrastructure. However, VMs come with drawbacks because they require significant resources in order to work properly. Essentially, running a VM means running a separate, virtual desktop environment on your hardware. And with each VM you run, your device must allocate RAM and other resources, which can be expensive and lead to unstable performance.

Docker containers are much more lightweight, and you can run multiple containers using only a single OS kernel. Containers use less memory than VMs, they boot faster (because they don’t have to spool up an OS), and they can share and reuse data volumes. In a nutshell, containers make virtualization simple, highly efficient, and easy to configure, which significantly reduces the overhead associated with virtualization when compared to using VMs.

Docker Makes Deployment Fast

Before VMs, setting up new hardware took days because of the tedious, manual configuration that was required. With VMs, devices could be configured in minutes (and remotely), but IT teams still lost time due to the need to boot up an OS for each VM.

Using Docker containers, fresh resources can be configured in seconds because there’s no need to boot up an OS. Multiple containers running on the same hardware can run isolated applications, such as those containing configuration data and automation scripts, to help you rapidly deploy resources to your network. Simply create a container for the appropriate job.

Docker Helps With Disaster Recovery

When it comes to business continuity, traditional approaches call for assigning a single purpose site to disaster recovery efforts. This means that resources sit idle at this site, because most of the time your organization is not focused on recovering from disaster. In essence, a traditional approach leaves disaster recovery as an afterthought, which means that managing and maintaining its infrastructure is costly and complex.

However, by using Docker containers, you can transform disaster recovery to be just another stage in the integration and development pipeline. This means that your recovery infrastructure is expanded from a single site to an entire region (or your entire organization), because containers allow you to utilize more resources more frequently. And should disaster strike, containers offer accurate automation for fast and reproducible deployments, so you can recover quickly and continue with your business continuity efforts.

Remember that a robust OOB solution takes advantage of the latest tools to give you more visibility & control of your network. Docker is one of those tools. It allows you to automate and take full advantage of your network resources, and you can focus on running only your necessary applications (not entire VMs). It introduces more efficiency with highly portable containers that work across platforms, and saves your system from the strain of deploying many resource-hungry VMs.

To get the latest network tips and out-of-band management advice, sign up for tips and updates.

How One Unified Platform Gives You More Control Over Branch Networking,

Branch networking comes with its own set of challenges that can get in the way of normal operations. As a network engineer, you’re tasked with preventing business disruptions while simultaneously scaling, troubleshooting, and managing network connections. This can be a daunting challenge that may lead to slow deployments, inevitable downtime, and unoptimized connectivity.

The good news is, Nodegrid was built from the ground up to address these major concerns with branch networking. Read on to see how our branch-in-a-box solution helps you scale, troubleshoot, and manage with one innovative system.


Make Branch Networking Easy to Secure and Scale

Consider the common challenges of scaling and adding branch locations to your enterprise network. You’re typically left to ship preconfigured devices to each site, which not only adds more time and cost, but more risk as well. What if these preconfigured devices get lost or end up in the wrong hands? Because they contain user accounts, passwords, and other sensitive information, having these devices get lost or stolen puts your network at greater risk of attack.

Once your devices successfully reach their destination, the real work begins. You need to manually set up all appliances at the location, which involves logging into each individually and making appropriate configurations. This takes even more of your time and money, and leaves you open to potential setbacks that can occur due to human error. What if your compliance documentation contains a mistake, or your IT personnel unknowingly repeat an error while deploying 10, 20, or even 50 new sites?

Nodegrid was made to address these concerns of security and scalability. Nodegrid appliances consolidate network functions, sport Linux OS for third-party application hosting, and feature ZPE Cloud connectivity.

When adding a new branch location, you don’t need to ship anything preconfigured. Ship bare-metal Nodegrid devices, which eliminates the threat of having your data lost or stolen, and simply plug them in. Zero touch provisioning means all configuration data can be automatically downloaded from ZPE Cloud, only when your devices are safely at their destination. This capability is even extended to devices that you connect to Nodegrid appliances.

Suddenly, backdoor security threats are no longer an issue, and neither is costly human error, since all your branch locations can be deployed consistently via the cloud.


Pinpoint Problems for Better Troubleshooting

Face it — troubleshooting issues could be a much more intuitive undertaking. But it’s difficult, mostly because of the sheer number of devices you deploy at each location. When something goes wrong, you probably refer to your spreadsheet that shows specific device information for each branch. From there, you might run through troubleshooting protocols to narrow the list of potentially problematic devices and what the issue might be, and then you can finally work toward a solution.

Nodegrid does away with all the hassle, because it uses consolidated devices and Nodegrid Manager software that pinpoints problems for you.

Nodegrid devices are powerful, featuring x86 64-bit architecture that accommodates third-party application hosting for cyber security, SD-WAN, firewalls, and more. For switching, routing, and computing, you need only a single Nodegrid device. This reduces potential points of failure so you can solve issues easier. On top of this, Nodegrid Manager is software that gives you a complete view of all your network-connected devices. It features alerts and notifications that let you know of problems before they occur. Together, Nodegrid’s hardware and software make it simple to pinpoint issues and prevent downtime.

Manage Using one Intuitive Platform

With many devices at each branch location, it’s likely that your hardware stack includes multiple vendors. This is part of achieving a right-fit solution for your enterprise, which can serve you well when looking at the bigger business picture.

But when you get down to the details of managing branch networking, this mishmash of vendors can be a nightmare. Each device has its own OS and interface, which can exhaust your staff. You need to spend time and money training them to become proficient with each. Still, even your best experts can become quickly fatigued when they’re forced to transition from device to device, interface to interface, protocol to protocol, and so on.

One of the best parts about Nodegrid is that it answers the question, “What if it could all be done using one tool?” That tool is Nodegrid Manager.

Nodegrid Manager shows you every device connected to your Nodegrid appliances, and features Guest OS that gives you total out-of-band control regardless of vendor. With one intuitive interface, you can control your entire infrastructure, get deeper visibility and insight into your network, and even extend features to bridge gaps between devices. It can all be done remotely as well, so you can manage and optimize your branch networking no matter where you are.

If you want a first hand look at all these benefits and more, schedule your Nodegrid demo today!


Free Yourself from Vendor Lock-in!

Back in the early and mid-2000’s the race was on to implement an out-of-band infrastructure (OOBI) to provide access and control to all your IT assets in the data center via a separate management network. Isolating device management to a separate management network was, and still is a great practice. Having the ability to remotely connect to a device in the data center via an isolated network, allows users to perform various tasks such as Reboot, Power off, Power on, run a specific script, provision, test, etc. of specific devices, without impacting the production network processing. Another benefit (among many) is being able to connect to a failed production network device and bring it back in service via remote access and management. Reduces recovery time. Minutes can mean millions when it comes to a production IT outage. The faster you can respond, the less it costs.
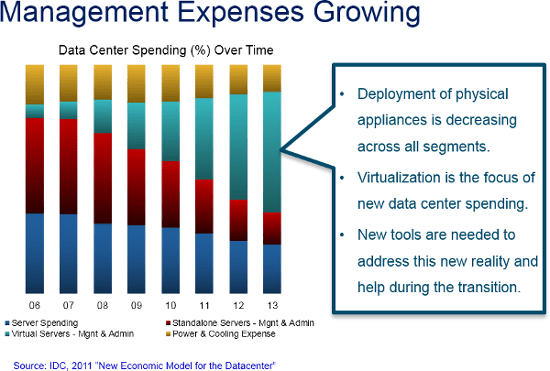
Currently, and some 10 years ago, implementing an OOBI required various hardware appliances to be installed in your network to provide access to the device. Serial Console Servers, KVM/IP Switches, Intelligent and Controllable Rack PDU’s, etc… which you need to purchase and install in your data center. 1000’s of dollars were, and still are being spent on the purchase and implementation of these appliances. Why? Because that’s how you do it. Buy more management appliances and add them to your existing infrastructure as you grow. In an attempt to keep up with new technologies like Service Processors (IPMI, ILO, Drac, CIMC, etc) and the explosion of Virtualization, the manufactures have addressed this by creating another appliance for you to buy, add to your rack and network, just to facilitate the access and control to the Service processors and Virtual Machines. These solutions also require periodic updates or upgrades to the vendor specific management software, which was developed (for what was available at the time) over 10 years ago, and based on the use of appliances (sell you more hardware). Not what’s available now.


Today, Virtualization and Service processors are aggressively being adopted in data centers. This greatly reduces the need for expensive, rack cluttering, and heat generating KVM/IP Switches, and perhaps, in some cases, reduced the need for expensive rack PDU’s. Quite a cost savings. But still not enough. Most all OOBI management solutions require additional hardware appliances in order to consolidate and provide access to the Service Processor or Virtual Machine infrastructure. Again, this method of implementing an OOBI came about 10 years ago and required hardware components (KVM/IP, Serial Console, Intelligent Rack PDU’s, Service Processor, and virtual Machine consolidators) in order for it work. And let’s not forget the vendor specific management tools that are useless without the presence of vendor specific appliances and don’t integrate with equivalent competitor products. For example, Console Servers from different vendors. As a result, you, the users are locked in to a specific vendor technology and method of OOBI management. To frame this differently, suppose your company purchases a company which standardized on an OOBI from vendor A. You’re standardized on vendor B. How do you handle this? Maintain both solutions until you can replace one with the other. Buy more hardware from your preferred OOBI manufacturer to replace the hardware from the other manufacturer. Either way, it’s costly and locking you into a specific vendor OOBI technology and method.

So, what can you do? Continue to expand your OOBI infrastructure from a specific vendor with outdated methods and solutions, OR, you could implement a vendor neutral OOBI software-only management solution that provides the same, if not better, secure access and control to devices from both Vendor A and B without having to add additional hardware appliances. Now you can have OOB connectivity and management of your Physical and Virtual infrastructures as it grows, and expands via whatever vendor/s products you decide to use. In fact, you could use a combination of Vendor A, B, C, and D’s OOB appliances to rebuild a best of breed OOBI. Let Freedom Ring. No more OOBI vendor lock-in.

From the team that gave us the Linux Break Safe Console Server, Managed Rack PDU’s, and put IPMI in Service processors, comes the world’s first Software-Only, Vendor Neutral Access and Control solution for the management of both Physical and Virtual (VMware and Kernel Virtualization) IT device Infrastructures, regardless of manufacturer. “NodeGrid Manager” is the first software-only solution for Access and Control that doesn’t require any additional hardware components to provide access and control to your existing OOBI, regardless of manufacturer. NodeGrid Manager’s agnostic approach to device management allows you to take advantage of your existing hardware OOBI without regard for manufacturer, or the addition of expensive KVM/IP, or service processor and virtual machine consolidator hardware appliances. As a byproduct, NodeGrid Manager frees you from vendor lock-in. NodeGrid provides the same user experience regardless of device and manufacturer via a common UI and standardized feature and command stack across the entire infrastructure. User experience is the same for Server, Storage, Network, Power, and Virtual Machine (VMware and Kernel Virtualization) infrastructure regardless of manufacturer.

If it hasn’t already happened, there will come a time when your existing OOBI starts letting you down. When that happens, turn to ZPE Systems NodeGrid Manager for relief. NodeGrid Manager Delivers a true vendor-neutral experience in OOBI management. Oh, and did we mention you don’t have to add expensive vendor specific proprietary appliances to manage your physical and virtual IT infrastructure.


Free your OOBI now from vendor lock-in. Stay ahead of technology changes and growth with NodeGrid Manager. The world’s first, Software-Only, Vendor-Neutral Access and Control Solution for both Physical and Virtual IT Infrastructures, that simply and easily works, and scales to meet your needs.

See for yourself.

The fastest way to learn more – Email us at sales@zpesystems.com (or call +1 510 298 3022) to schedule a chat or request a demo.