Providing Out-of-Band Connectivity to Mission-Critical IT Resources

Optimize Edge Networking With This Free Guide to Out-of-Band, SD-Branch, & More
GG2 – branch and edge networking

Edge networking continues to grow as a vital component to business. With more people working remotely, whether from home, in the field, or on the road, it’s now critical to have a network that goes wherever your people go. And achieving that kind of connectivity is becoming easier by the day, as companies like ZPE Systems carry on innovating new technologies to accommodate secure, on-the-go networking.

Traditional network architectures are becoming obsolete, simply because they can’t offer flexibility at the edge. Their rigid systems and protocols restrict both IT and non-IT staff from accessing the resources they need, when they need them. This has only spurred the evolution of better edge networking, and now many companies operate remotely 100-percent of the time.

Even if your goal isn’t to fully migrate your workforce out of the office, you can reap major benefits from strengthening your edge networking capabilities. That’s why you need to get our free Gorilla Guide to Deploying, Maintaining, and Maximizing Branch & Edge Networking. Keep reading to learn more.

What are some crucial edge networking capabilities & their benefits?

Think of a few ideal capabilities you’d like your business network to have.

  • Do you want to give full remote access to IT and network staff?
  • Do you want to gain in-depth visibility & control of branch networks?
  • Do you want to deliver safe, reliable connectivity where your workers go?
The good news is, you can get all these and more when you use an open, cloud-enabled edge networking platform like Nodegrid. Here’s how you can benefit:

  • You can make easy work of every deployment thanks to cloud-based provisioning. If you need to set up a new branch network, even at a very isolated location such as an offshore drilling platform, the cloud gives you push-button simplicity. You don’t have to preconfigure devices or put staff on-site to manually provision the stack. You can ship boxes that are 100% unconfigured, which gives you complete security, and then simply boot your devices. The cloud does everything for you using zero touch provisioning, so you can sit back and watch your network build itself.
  • You don’t have to put IT staff on-site in order to troubleshoot network issues, fix configuration errors, and restore uptime. You can take advantage of remote out-of-band management and cloud-based provisioning. These allow you to fulfill all of your network administration duties from afar. When a router goes offline or a software version needs to be rolled back, you can respond quickly and remediate the problem — even from thousands of miles away. These technologies work together so you can maintain branch networks without breaking a sweat.
  • You can optimize your branch networks by taking advantage of software-defined branch (SD-Branch) capabilities. Traditionally, SD-WAN gives you control of only what goes to and from your branch networks. But with SD-Branch, you can see and control WANs and LANs, with comprehensive capabilities that let you access what goes on inside each location. SD-Branch lets you manage at a granular level. Not only can you adjust traffic priorities and specific device settings, but you can also manage all the clients connected to your network. This means that you don’t need to dispatch support teams for troubleshooting or management, so you can save time & money on operations.
  • You can deliver pick-up-and-go networking by using Secure Access Service Edge. SASE is a new model that combines networking and security in the cloud, and delivers them to users wherever they need secure network access. It’s also identity driven to provide even more flexibility. For remote and on-the-go workers, you no longer need to allocate resources to configure company laptops or other devices. Because SASE ties network access to a user’s identity, you can let them connect from anywhere using any device. With SASE, business can continue seamlessly no matter what change you need to adapt to.

Why download our free guide?

For details about how you can improve your edge networking abilities, get our free Gorilla Guide to Deploying, Maintaining, and Maximizing Branch & Edge Networking. It shows you:

  • Why you need cloud provisioning — Discover how a cloud-based approach to provisioning gives you valuable benefits, such as hardened security and effortless deployments.
  • How the cloud makes out-of-band better — See how to easily maintain branch locations with the cloud on your side, from remote troubleshooting to configuration management.
  • Best practices for optimizing branch networks — Learn how to deploy and optimize your distributed networks, and take advantage of in-depth SD-Branch for total network control.
  • Why you need to get SASE — Explore Secure Access Service Edge and how it transforms the edge with nimble networking & security, for business that goes wherever your employees go.

It’s never been more critical to give your edge networking capabilities a boost. Now’s your chance to improve business agility with a free download, the Gorilla Guide to Deploying, Maintaining, and Maximizing Branch & Edge Networking.
7 Reasons Why We Put Intel CPUs in the Nodegrid Serial Console

Intel® CPUs power many of the computers we use today. These include everything from personal desktops and laptops, to high performance computing clusters that aggregate power to solve major global issues. So when choosing a suitable processor to build into our Nodegrid Serial Console, Intel was the obvious choice. In this post, we’ll go over 7 reasons why we put Intel CPUs in the NSC.

But before we get into the details, let’s review some basics.

Besides Intel CPUs, What Else is Available?

There are mainly two types of CPUs, or processors, available today: x86 (such as Intel’s offerings) and ARM. Though they serve a variety of purposes and can have some overlapping applications, x86 processors are typically deployed when speed & power are main concerns. Meanwhile, ARM processors are used in implementations geared toward minimizing power consumption and maximizing battery life.

The way these types of processors work is based on their underlying instruction set. x86 CPUs take advantage of the Complex Instruction Set Computer (CISC), which is able to process complex instructions that are crammed into a single line. ARM-based CPUs, on the other hand, use the Reduced Instruction Set Computer (RISC), which processes simple instructions over a span of multiple lines.

As for the advantages, x86 processors are able to perform more tasks rapidly, while ARM processors are able to consume less power and maximize energy efficiency. The main drawbacks include more power consumption for the x86 CPU, and slower speeds for the ARM CPU.

This is why purpose-built appliances, such as modems & routers, typically employ an ARM-based processor, while highly demanding devices such as desktops & servers use an x86 CPU.

In a nutshell, this is why we chose the multi-core Intel CPU for the Nodegrid Serial Console. But here’s a more detailed breakdown of the reasons for our choice.

Performance is Key

The Nodegrid Serial Console is designed to maximize speed and capabilities. Using x86 Intel CPUs, we created the world’s fastest 1U serial console that doesn’t compromise on performance. This processor allows for more simultaneous operations, more users, and more input/output than ARM-based CPUs. In terms of real-world benefits, this blazing fast processor means quicker CPU cycles that help customers complete more tasks, reduce MTTR, and increase their ROI.

Commonality Helps Users and Developers

Many existing servers use x86-based CPUs. Naturally, we wanted Nodegrid to integrate seamlessly for both users and developers. The Intel-based processor promises a common platform that these users are already accustomed to. They don’t have to worry about application incompatibilities or slowdowns, nor do they have to spend time learning new systems. The x86 CPU provides a management and maintenance experience that users are familiar with, so they can maintain OS & application availability.

Customization Through a Common Dev Environment

Our Intel-based devices are a perfect platform to deploy custom solutions. The x86 CPU allows developers to benefit from a variety of readily-downloadable SDKs and environments. The Nodegrid Serial Console’s SDK comes with Yocto, which means customers always have the latest updates, packages, and DIY customization capabilities. No more waiting for third-party fixes or workarounds, because customers can create solutions that meet their unique requirements.

Docker

Because the x86 platform is capable of robust performance, Nodegrid allows users to leverage Docker containers and deploy virtualized solutions. With regards to Docker, the Nodegrid Serial Console is optimizable right out of the box so customers can get the most functionality out of a single device.

Availability of Security

When it comes to open networking, the Intel CPU is the industry standard, which means customers get security patches as soon as they’re available. They don’t have to be left vulnerable waiting for third-party kernel patches from other chip makers. With an x86-based device, customers remain safe with up-to-date security, and in some cases can even apply patches before official updates are available.

Peripheral Support Via Multiple Interfaces

Part of designing a more powerful serial console was having the ability to support a variety of peripherals. The Nodegrid Serial Console features USB 3.0 and USB 2.0 ports, allowing customers to connect an array of add-on devices. They’re no longer limited by a single-purpose appliance that comes with minimal additional ports. With the NSC, customers can extend the box’s functionality by adding cellular, Wi-Fi, storage, and other peripherals.

Greater Storage

With power and speed at the core of the Nodegrid Serial Console, we needed to incorporate enough drive space. We built the NSC with 32GB of storage, along with 4GB of RAM. Not only can it store plenty of data, but it also has a healthy amount of memory to accommodate running more apps and functions. And if 32GB isn’t enough, customers can connect external drives via USB for even more local storage capacity.

This list is made up of 7 compelling reasons why we chose x86 Intel CPUs for our devices. However, there’s an 8th reason that we love to share…

Cost Savings That We Pass to Customers

By choosing the readily-available x86 CPU, we pass powerful processing along with cost savings to customers every day. Because we think having the world’s best serial console shouldn’t be prohibitively expensive.

ZPE Systems is an Intel Network Builders Winners’ Circle Partner

Intel

Driving digital innovations and network transformation are visions we closely share with Intel. That’s why ZPE Systems has been recognized as a Winners’ Circle Member and Solution Plus Partner. Together, we offer go-to-market solutions that cultivate customer success and enrich our partner ecosystem with innovative networking technologies.

We partner with Intel to transform networking. See how we do the same with our other partners by visiting our Strategic Alliances page.

4 Critical Things to Know About Zero Trust Security

Zero trust security is not a new concept, however it has gained popularity in recent years. As companies become increasingly distributed, they must offer network access that’s flexible, without putting sensitive data at risk. This is where zero trust security comes in.

In this post, we’ll cover 4 critical things you should know about zero trust security, such as what it is, why companies use it, how it works, and more.

What is Zero Trust Security?

Zero trust security can be boiled down to a simple concept: always verify every user and device trying to access the network.

Traditional networking safeguards are based on the castle-and-moat architecture. This means that all users and devices within the network are deemed trustworthy and can access the resources they need. Those outside of the network (or moat) must be verified and trusted before gaining access to the network. One of the glaring problems with this approach is that it doesn’t consider the possibility of attacks coming from a trusted user/device within the network. This means that an attacker simply needs to hack into the network, and then there are few (if any) obstacles remaining in their way.

Zero trust reimagines security with the concept that organizations should not automatically trust anyone/anything trying to connect to their network. Instead, they should verify everyone and everything that tries to connect, including users/devices outside and inside of its perimeter. In other words, trust no one.

Where Did Zero Trust Security Come From?

The zero trust concept was first prototyped in the early 2000s. In 2010, John Kindervag coined the term ‘zero trust’ for the concept, and its adoption by Google a few years later increased the industry’s interest in the zero trust model.

This new security architecture came from the realization that the traditional castle-and-moat configuration was becoming increasingly vulnerable. Years ago, a typical organization’s data and sensitive information were kept in a central location. This made the network and its resources easy to protect, and also easy for IT staff to monitor for threats and address attacks.

Now, organizations are adopting technologies that offer greater networking capabilities for distributed access. These technologies include public and private clouds, third-party services, virtualized SD-WAN & firewall solutions, and more. Securing an entire network means putting in place multiple safeguards. The traditional architecture is now being replaced by the more robust yet nimble security setup of zero trust.

Why Are Companies Using Zero Trust Security?

One of the canonical goals of networking is to allow information to flow between computers, people, and organizations. Yet with information becoming more and more decentralized and relayed through various channels, risk is on the rise. And because traditional security architectures simply can’t provide omnipresent protection for data and communications, zero trust security is being adopted by organizations across the globe.

A major benefit of zero trust is that it provides hardened security, regardless of how distributed the network is. Whether a company serves a single contained network, or hundreds of branch locations distributed around the world, zero trust security offers peace of mind for every interaction. This means more thorough protection from outside and inside threats, because verification is needed — always.

This complements Secure Access Service Edge and SD-Perimeter implementations (more on those below), which companies use to offer more flexible networking and define least-privilege access rights. Used in conjunction with these configurations, zero trust security also eliminates the need for companies to backhaul traffic through their main security controls. This translates to fewer slowdowns and more availability, so companies can meet their business goals without their networks holding them back.

Real-world examples include scaling, working from home, and even securing data at HQ.

  • Setting up new locations comes with its own set of security risks. However, companies using a zero trust model can get granular control of who & what can access their network. This can help eliminate attacks from stolen equipment, devices, and credentials.
  • When setting up a Secure Access Service Edge (SASE) implementation, whether for faraway locations or remote & on-the-go workers, zero trust keeps networks & resources secure. It requires user identities and devices to be verified, eliminating many methods of attack.
  • When defining access rights using an SD-Perimeter approach, zero trust enables companies to make sure that access to resources is given only to appropriate personnel. This ensures data stays secure from malicious intent by actors outside or inside of the organization.
  • How Does Zero Trust Security Work?

    Zero trust security assumes that threats can come from anywhere, including from inside the organization. The big takeaway, however, is that zero trust is not a single new tool or technology. Instead, it uses a combination of existing tech and methodologies such as micro-segmentation, multi-factor authentication, and least-privilege access.

    A zero trust model works by segmenting parts of the network into small sections, each with their own security controls. In order to gain access to a segment, a user must verify their identity using multi-factor authentication (MFA). Once a user is verified, least-privilege access means they can use only the resources they need to perform their job. This is essentially a perimeter around what the user is allowed to access.

    Here’s a basic example: One segment contains SD-WAN and firewall controls. If Ryan is an admin responsible for SD-WAN management, and Priya is an admin responsible for firewall management, the company must define these perimeters respectively. Then, Ryan can be verified and granted access only to the SD-WAN tools, while Priya can be verified and granted access only to the firewall tools. If either user tries to gain access outside of their perimeter, they will be denied by their company’s zero trust security measures.

    Though it’s not a quick fix or turnkey solution, zero trust is transforming the ways organizations secure their networks. What’s more, the market is expanding with new solutions that offer increased granular control over access, using technologies like IP tracking, geo-fencing, and others. And using an open platform like Nodegrid, the possibilities are endless for organizations wishing to evolve their security and block threats from across the globe.

    Check out ZPE Systems’ full list of security partners that can help you achieve a zero trust model.

    6 IT Solutions to Implement Right Now for More Effective Remote Work

    ZPE Systems Blog Photo- Header

    Many companies have found it difficult to adjust to remote work. In the face of drastic changes brought on by pandemics, natural disasters, and other challenges, untethering your workforce from the office can be a big ask. Your success relies on one crucial component: your network.

    Keeping your enterprise connected – both internally and to customers – is the only way to maintain business continuity and customer satisfaction. Unfortunately, traditional networking solutions were built for the office. Not only does this slow down your transition to working remotely, but also makes everyday operations anything but efficient.

    The good news is, our experts have pinpointed six IT solutions that will make your company more effective at remote work, using a network that accommodates distributed business better than ever.

    ZPE Systems Blog Photo- Body Image

    1. Give Network Staff Convenient Access With Advanced Out-of-Band

    Out-of-band (OOB) management is not a new technology. But taking advantage of this tool has traditionally proven cumbersome and inefficient.

    It’s not uncommon for businesses to treat their OOB network as an afterthought, something they might use once in a while when an update or fix is needed. Phone lines, modems, and dedicated OOB devices make management a chore, even for tasks like resetting passwords, rebooting devices, and other routine work.

    Remote access via DSL or dial-up is too slow, which takes time, puts your security at risk, and forces you to juggle delicate admin protocols. Putting staff on site is another option, but also eats up time and binds specialized IT personnel to specific locations.

    Fortunately, you can take advantage of advanced out-of-band, which lets you perform network management tasks from anywhere.

    An advanced out-of-band solution gives you a secure management path that’s completely separate from all other networks. Not only do you stay protected from unwanted traffic and attacks, but you can also get blazing fast access to your management network via broadband connection.

    This means that for issues large and small, you can slash response times and put your best people on the job – even if they’re across the globe. And if your main connection suffers an outage, you can remote-in to your out-of-band network via cellular failover backup.

    Advanced out-of-band makes network management convenient and efficient.

    2. Protect Business From Costly Downtime Thanks to Cellular Failover

    If one of your critical locations suddenly goes offline, your business could lose up to thousands of dollars per hour. Restoring your main connection can take hours or days, while your employee and customer interactions come to a standstill. Business stops, and your reputation plummets alongside customer satisfaction.

    However, cellular failover is a simple solution that can prevent all of this, so you can leave downtime in the past. When your main connection drops, your failover-equipped network automatically switches to 3G, 4G, or even 5G cellular to give employees and customers a seamless experience.

    Capable cellular solutions give you freedom of choice, allowing you to determine which wireless carriers you use, as well as letting you take advantage of multiple backups. It’s like an insurance policy for your connectivity, with most cellular providers sporting over 99% reliability.

    When you need to deploy a new location, cellular failover can even help you bring critical systems online – before your main connection is established. It’s a wireless solution that lets you scale on demand and helps you increase your business’ agility.

    3. Keep Staff Connected Using Secure Access Service Edge

    Accommodating remote work usually involves a slow, stringent process. You need to purchase and configure laptops and other equipment, create users and groups, and adjust other hardware- and network-specific settings. All of this just to allow staff to work away from the office.

    ZPE Systems - SASE Image

    On top of this, all traffic likely gets routed through your main enterprise firewall. This degrades performance and speed for every user, and can bring business operations to a grinding halt.

    But Secure Access Service Edge, or SASE, is a transformative technology that does away with the traditional hassles of setting up for remote work, and instead puts networking and security into the cloud. This allows safe connectivity to be delivered close to users no matter where they are. And because SASE uses an identity-driven model, your employees don’t have to rely on special hardware. They can access your network using their smartphone, tablet, desktop, or other device.

    SASE gives your employees flexible network access, and also frees your main enterprise connection for more business-critical traffic. You can deploy your SASE solution and get a network that keeps your staff connected.

    4. Fully Optimize Using a Vendor-Neutral System

    Typical networking solutions cause vendor lock-in. This is when you’re limited to choosing specific hardware and software products that are compatible only with each other. Vendor lock-in forces you to make sacrifices during implementation, so you end up with a solution that doesn’t entirely satisfy your requirements.

    But with a vendor-neutral management platform, you can boost efficiency even on your existing network.

    A vendor-neutral system means you don’t have to worry about over-buying or under-serving, and can instead connect the physical and virtual assets of your choice. You can optimize your network with SD-WAN, firewall, routing, and other solutions that perfectly suit your needs.

    Some providers even offer a unified management tool that consolidates control of your network solutions, regardless of which vendors they’re from. Your IT staff no longer need to jump from one unique UI to another, because everything can be controlled under a simple management umbrella. You can update firmware, change traffic priorities, monitor devices, and more from one clean interface.

    With a vendor-neutral system in place, you can turn your network into a powerful asset that supports your global enterprise.

    5. Streamline with virtualization

    You’re probably used to having dedicated, single-purpose devices for your network functions. Even if these deliver all the capabilities you need, you’ll inevitably find it difficult to scale and manage due to large stacks of hardware & software solutions.

    But you can significantly reduce your physical stack and your management efforts by using virtualization.

    With the right devices, you can consolidate and virtualize your network functions to streamline every part of infrastructure management.

    And the more guest operating systems you can run, the better. With virtualization, you can host custom or third-party applications, so instead of deploying separate appliances for SD-WAN, routing, failover, and firewall functions, you can use fewer devices capable of handling it all. This means smaller stacks, tighter solution integrations, and easier management of network functions.

    6. Use Automation to Take Work off Your Hands

    You spend a lot of time and money just to keep your network running. Routine tasks and configuration management are some of your biggest challenges, simply because they pull critical resources away from more urgent business needs. Moreover, you’re left vulnerable to human error that can cause interruptions and downtime.

     This is where automation comes into play, which helps by doing some (or all) of the work for you.

    For everything from routine fixes, to provisioning, to configuration updates and rollbacks, automation helps you achieve autonomous networking. Use your favorite tools like Ansible, Chef, and Python to create workflows that carry out themselves, and set up zero touch provisioning for push-button deployments. Automation is the only solution that helps you replicate and scale with consistency, so you can avoid costly errors while keeping specialized staff focused on the core of your business.

    Take advantage of automation capabilities for more efficient and productive enterprise networking.

    Remote work can be difficult to accommodate, especially when your business is distributed across the globe. But you can help your entire organization operate more effectively through networking.

    At ZPE Systems, we’re leading the remote-work initiative with comprehensive offerings for all six of these IT solutions. From advanced out-of-band, to virtualized, vendor-neutral infrastructure and management, our hardware & software help your business work better from anywhere.

    To take advantage of these solutions, get in touch today!

    Secure Access Service Edge For an Oil & Gas Provider

    Secure Access Service Edge is a new concept that’s transforming the edge network. SASE delivers more flexible and secure network access, so your business can adapt to drastic changes and accommodate a distributed workforce.

    Want to see it in action? Here’s a 90-second explainer video to help you visualize business with SASE.

    In a nutshell, SASE delivers a ton of benefits:

    • SASE combines networking and security in a cloud environment. This means you don’t have to backhaul traffic through your main enterprise firewall, which causes slowdowns and degraded performance. Instead, you can deliver safe network access directly to users, which makes it easy to connect from anywhere. At the same time, this lets your main network breathe so business can continue without interruptions or lagging network speeds.
    • SASE is identity-driven. This means network connectivity is tied to users instead of to specific devices or access points. So when changes force you to accommodate remote work or distributed staff, your IT teams don’t have to be burdened configuring countless laptops, smartphones, tablets, etc. Your workers can simply pick up and go, and connect to your network even using their own devices or public access points.
    • SASE converges network functions for secure and easy management. Accommodating a more agile edge network used to require adding purpose-built solutions to your stack. This made a nightmare out of deploying and scaling, and management became more complex because each solution came with its own UI, architecture, requirements, etc. With SASE, you can virtualize all your essential functions. This helps reduce your stack to make scaling simple, and centralizes functions so IT staff can manage your network in one place.

    Why is SASE better with Nodegrid?

    Nodegrid provides a SASE platform that’s unlike other solutions on the market. This owes to all-in-one devices and the 64-bit, Linux-based Nodegrid OS. With more speed and compute power, Nodegrid offers even more flexibility through virtualization, capable of running multiple guest operating systems (guest OS) and directly hosting your choice of applications.

    Nodegrid also supports automation and zero touch provisioning. In order to deploy new locations, just install your Nodegrid devices, and then provisioning can be executed automatically. This significantly increases security, since you can ship 100% unconfigured devices and then provision only when they’re under your control. This also saves on deployment resources, because you don’t have to send specialized IT staff to each site for time-consuming, manual setup tasks.

    How does Nodegrid deliver SASE in the real world?

    A global oil & gas provider needed to streamline their edge networking solutions.

    Their hardware stack consisted of many devices that were difficult to deploy and manage. This was a major hurdle for the company, considering their remote sites were very limited by physical space constraints. Additionally, support costs continued to rise and IT staff were dispatched to fix even minor issues.

    The company needed a streamlined solution that was more space- and energy-efficient, and that could also maintain a high availability environment. Nodegrid was the only platform that could meet all their needs.

    Want to learn how the company cut their stack in half, maintained a secure & highly-available environment, and saved on support?

    ZPE Systems and 128 Technology Announce Strategic Partnership

    Fremont, CA, September 17, 2020 – Today, ZPE Systems, Inc., a leading provider of network infrastructure management solutions, and 128 Technology, Inc. (128T), a leading provider of software-defined networking solutions, announced a strategic partnership to offer combined networking and out-of-band management capabilities. As a result of the agreement, customers will experience faster and smarter designs, deployments, and support for their networking solutions.

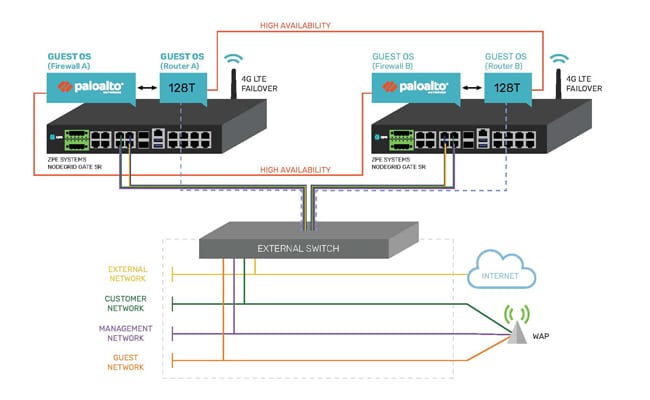
    ZPE Systems’ Nodegrid hardware and software directly host 128T’s SD-WAN offerings, such as their Session Smart™ routing application, for an all-in-one platform that vastly improves branch networking. Nodegrid’s strong capabilities are enhanced by this tight integration with 128T, to deliver a powerful combined solution that’s easier to deploy and support.

    “ZPE has a very strong communications channel with 128T,” says ZPE Systems’ CEO and Cofounder Arnaldo Zimmermann. “With this partnership, our customers can benefit from an always-ready OOB platform with SD-WAN and cellular failover. In addition, they no longer need to worry about the handoff during support — they get direct assistance with both their Nodegrid appliances and their 128T solution.”

    “The evolution to software-defined networking is delivering breakthroughs across several quantifiable areas and giving enterprises newfound freedom and business agility.  However, because most networks today are a heterogenous mix of solutions from several vendors, the complexity of managing today’s enterprise networks has increased significantly as well,” said Ritesh Mukherjee, Vice President of Product Management, 128 Technology.  “ZPE Systems has established itself as an innovator in the area of network management. Through this partnership we are taking steps to ensure our customers can experience the benefits of software-defined routing, while also maintaining the highest levels of visibility, management and control of their networks.”

    Both companies are intimately familiar with each other’s products, which makes for an ideal offering for customers looking to consolidate their infrastructure, cut costs, and meet the demands of their branch networks. This all-in-one solution is further improved by Nodegrid’s remote out-of-band capabilities. Nodegrid’s out-of-band is supported through separate WAN links as well as through major cellular networks. This gives customers reliable access to their critical systems and high-availability environments, even during outages and service disruptions.

    Together, ZPE Systems and 128T pledge to deliver the highest quality support, and have already demonstrated their strong partnership for a top utilities provider. When this customer required help with their proof-of-concept (POC), ZPE and 128T came together to assist with creating a streamlined and efficient design for the customer’s required implementation.

    Read the official press release here.

    About ZPE Systems, Inc.

    ZPE Systems is rethinking the way networks are built and managed by providing software-defined, vendor-neutral infrastructure management and networking solutions.

    ZPE Systems’ Nodegrid® platform consolidates, organizes, and simplifies the need for a complete remote access and control solution; Nodegrid solutions address the OOB management needs of the data center, unifies edge networking environments, manages converged infrastructure and provides intelligent automation. ZPE’s smart, consolidated IT management solutions reduce downtime, deliver OPEX savings, and extend the reach of IT workforces.

    ZPE’s global headquarters is located in Fremont, California with offices throughout the US and globally in Ireland, India, Brazil and Japan.

    ZPE Systems, the ZPE logo and Nodegrid are registered trademarks of ZPE Systems, Inc.

    To learn more, visit www.zpesystems.com.

    About 128 Technology

    We’re relentless in our commitment to creating a world where the network is no longer following changes in the computing environment—it’s leading.

    We are serial entrepreneurs, die-hard technologists, and principled pragmatists. But most of all, we’re purists—when there’s an important problem to solve, we do it right, or we don’t do it at all. The world needs more than yet another temporary solution. It needs a radical redesign of the core network building block—the router—and that’s what we’ve done. We took our innovation down to the IP layer to solve for every connected session because when the underlay works, the overlay goes away—and so does the accumulation of technical debt.

    To learn more, visit www.128technology.com.