Providing Out-of-Band Connectivity to Mission-Critical IT Resources

What is FIPS 140-3, and Why Does it Matter?
A lock representing cybersecurity, with the title What is FIPS 140-3 and why does it matter?

Handling sensitive information is a responsibility shared by so many organizations. Ensuring the security of data, whether in transit or at rest, is not only critical for maintaining the trust of end users and customers, but is often a regulatory requirement. One of the most reliable ways to secure data within network infrastructure is by implementing FIPS 140-3-certified cryptographic solutions. This certification, which was developed by the National Institute of Standards and Technology (NIST), serves as a benchmark for robust encryption practices, enabling organizations to meet high security standards and ensure regulatory compliance.

Let’s explore what it means to have FIPS 140-3 certification, why it matters, and its key applications in network infrastructure.

What is FIPS 140-3 Certification?

The Federal Information Processing Standard (FIPS) 140-3 certification is a stringent, government-endorsed security standard that sets guidelines for cryptographic modules used to protect sensitive data. It includes requirements for securing cryptographic functions within hardware, software, and firmware. The certification process rigorously tests cryptographic solutions for security and reliability, ensuring that they meet specific criteria in data encryption, access control, and physical security.

There are four levels of FIPS 140-3 certification, each adding layers of protection to help secure information in various environments:

  • Level 1: Ensures basic encryption standards.
  • Level 2: Adds tamper-evident protection and role-based authentication.
  • Level 3: Provides advanced tamper-resistance and strong user authentication.
  • Level 4: Offers the highest level of security, including physical defenses against tampering.

FIPS 140-3 certification ensures that an organization’s network infrastructure meets high standards for cryptographic security. This is important for protecting sensitive information against cyber threats as well as fulfilling regulatory requirements.

Why FIPS 140-3 Certification Matters

1. Meeting Regulatory Compliance Requirements

FIPS 140-3 certification is often required by regulatory bodies, especially in sectors like government/defense, healthcare, and finance, where sensitive data must be protected by law. Here are a few industry-specific regulations that FIPS 140-3-certified modules help with:

  • Defense: DFARS, NIST SP 800-171
  • Healthcare: HIPAA
  • Finance: PCI-DSS
  • Energy: NERC CIP
  • Education: FERPA

Compliance with FIPS 140-3 also makes it easier for organizations to meet audit requirements, reducing the risk of fines or penalties for security lapses.

2. Strengthening Customer Trust

End users and customers expect that their data is handled with care and protected against breaches. By using FIPS 140-3-certified solutions, organizations can demonstrate their commitment to securing customer data with recognized, government-endorsed security standards. FIPS certification is a valuable trust signal, showing customers that their information is being managed with the highest level of protection available.

3. Protecting Against Emerging Cyber Threats

Relying on uncertified or outdated cryptographic solutions increases the risk of data breaches. FIPS 140-3-certified solutions are tested to withstand advanced attacks and tampering, which is an important safeguard against threats that continue to evolve in complexity. Certified modules help prevent unauthorized access to sensitive data, whether through intercepted communications, phishing, or other cyber threats.

FIPS 140-3 certification gives assurance, especially for organizations that handle high volumes of data, that they have adequate encryption to protect against sophisticated attacks.

4. Ensuring Business Continuity and Operational Resilience

According to IBM’s Cost of a Data Breach Report 2024, data breaches now cost $4.88 million (global average), with healthcare being the most costly at $9.8 million per breach. The financial impact is staggering, but the ongoing operational disruption and recovery efforts determine whether an organization can fully bounce back from a breach. With FIPS 140-3 certification, there’s an added layer of resilience to an organization’s infrastructure, which reduces the likelihood of breaches and ensures a secure base for maintaining continuity (such as through an Isolated Recovery Environment). By implementing FIPS-certified encryption, businesses can minimize downtime, maintain access to encrypted systems, and recover more smoothly from potential incidents.

5. Gaining a Competitive Advantage in Security-Conscious Markets

Organizations that follow rigorous data security standards are more likely to gain the trust of clients, stakeholders, and customers, especially in industries where security is non-negotiable. Organizations that adopt FIPS 140-3-certified infrastructure can differentiate themselves as having a reputation for security, which can be a competitive advantage that attracts customers and partners who value data protection.

Key Applications of FIPS 140-3 in Network Infrastructure

For organizations managing large amounts of customer data, FIPS 140-3-certified solutions can be applied to several critical areas within network infrastructure:

  • Network Firewalls and VPNs: FIPS-certified encryption ensures that data moving across networks remains private, protecting it from interception by unauthorized users.
  • Access Control Systems: Identity-based access controls with FIPS-certified modules add another layer of security to protect against unauthorized access to sensitive data.
  • Out-of-Band Management: Using FIPS 140-3-certified encryption in OOB management ensures the same stringent security level for OOB traffic as for in-band network traffic.
  • Data Storage and Backup: FIPS-certified encryption secures data at rest, protecting stored customer information from unauthorized access or tampering.
  • Cloud and Hybrid Environments: For companies using cloud or hybrid environments, FIPS-certified encryption helps protect data across multiple infrastructure layers, ensuring consistent security whether data resides on-premises or in the cloud.

Discuss FIPS 140-3 With Our Network Infrastructure Experts

FIPS 140-3 certification gives organizations the ability to reassure customers, meet compliance requirements, and protect critical data across every layer of the network. Get in touch with our network infrastructure experts to discuss FIPS 140-3, isolated management infrastructure, and other resilience best practices.

Explore FIPS 140-3 for Out-of-Band Management

Read about 7 benefits of implementing FIPS 140-3 across your out-of-band management infrastructure. This article discusses the benefits it brings to remotely accessing devices, protecting against physical attacks, and securing edge infrastructure.

7 Security Benefits of Implementing FIPS 140-3 for Out-of-Band Management

ZPE Systems -FIPS 140-3

Out-of-band (OOB) management is essential for maintaining control over critical network infrastructure, especially during outages or cyberattacks. This separate management network enables administrators to remotely access, troubleshoot, and recover production equipment. However, managing network devices outside the main data path also brings unique security challenges, as these channels often carry sensitive control data and system access credentials.

Implementing FIPS 140-3-certified encryption within OOB systems can help organizations secure this vital access path to ensure that management data can’t be intercepted or manipulated by unauthorized actors. Here’s how FIPS 140-3 certification can enhance the security, reliability, and compliance of your out-of-band management.

What is FIPS 140-3 Certification?

FIPS (Federal Information Processing Standard) 140-3 is a high-level security standard developed by the National Institute of Standards and Technology (NIST). It specifies rigorous requirements for cryptographic modules used to protect sensitive data. FIPS 140-3 certification covers everything from data encryption to user authentication and physical security. For out-of-band management, FIPS 140-3 certification ensures that cryptographic components in hardware, software, and firmware meet stringent data security standards.

By implementing FIPS-certified solutions, organizations can ensure their OOB management is resilient against modern cyber threats, protecting both the control channels and the sensitive data they carry. Here are seven security benefits of implementing FIPS 140-3 for out-of-band management.

7 Security Benefits of Implementing FIPS 140-3 for Out-of-Band Management

1. Secure Encryption of Management Traffic

OOB management often involves remote access to routers, switches, servers and other critical devices. FIPS 140-3 certification guarantees that all cryptographic modules used in these systems have been rigorously tested to secure data in transit. Encrypting management traffic is crucial to prevent interception or manipulation by unauthorized users, particularly for tasks such as command execution, configuration updates, and device monitoring.

With FIPS-certified encryption, companies can protect OOB traffic between management devices and network components, so that only authorized administrators have access to sensitive system commands and device settings.

2. Enhanced Authentication and Access Control

OOB management solutions typically support different user roles, each with its own access privileges. FIPS 140-3-certified modules, like ZPE Systems’ Nodegrid, feature multi-factor authentication (MFA) to control who can initiate OOB management sessions. Certified solutions also include secure key management practices that prevent unauthorized access, ensuring that only verified users can control and modify network devices.

These protections mean FIPS-certified solutions help mitigate the risk of unauthorized users accessing high-value assets. This is especially important during ransomware recovery efforts, when teams need to launch a secure, Isolated Recovery Environment to combat an active attack in a compromised environment.

3. Protection Against Tampering and Physical Attacks

Many organizations deploy IT infrastructure in locations where physical device security is lacking. For example, remote colocations, unmonitored drilling sites, or rural health clinics can easily expose network infrastructure to device tampering. FIPS 140-3 certification mandates tamper-evident and tamper-resistant features to protect the cryptographic modules used in OOB systems. OOB solutions like ZPE Systems’ Nodegrid provide robust protection against tampering, with features including:

  • UEFI secure boot: Prevents the execution of unauthorized software during the boot process.
  • TPM 2.0: Ensures secure key generation and storage, so only authorized software can run.
  • Secure erase: Allows for deletion of all data from storage, so no data can be recovered from devices that have been tampered with.

These features prevent unauthorized individuals from physically accessing OOB equipment to intercept or modify management traffic. In remote and edge locations, FIPS-certified cryptographic modules provide robust protection against physical attacks, making it harder for adversaries to compromise OOB management pathways.

4. Compliant and Secure Logging of Access Activities

Because OOB management systems provide access to critical equipment, organizations need transparency into OOB users and their management activities. This means logging and auditing are essential to maintaining security and compliance. FIPS 140-3-certified modules support secure logging of all management activities, creating a clear audit trail of access attempts and security events. These logs are stored securely to prevent unauthorized users from altering or erasing them, providing valuable insights for security monitoring and incident response.

Secure logging is not only critical for monitoring access but also necessary for meeting regulatory compliance. FIPS 140-3 ensures that OOB management systems can satisfy audit requirements, making compliance easier and protecting organizations from potential regulatory penalties.

5. Meeting Regulatory Requirements in Sensitive Environments

Many industries handle sensitive data, especially government, healthcare, and finance. For organizations in these industries, it’s often mandatory to use FIPS-certified cryptographic solutions. FIPS 140-3 certification helps OOB management systems align with federal security regulations and standards like HIPAA and PCI-DSS. By deploying FIPS-certified encryption, organizations can comply with these standards, streamline audits, reduce the risk of regulatory penalties, and reinforce trust with customers.

6. Consistent Security Across Main and OOB Networks

It’s easy for organizations to focus mostly on securing the main network, while overlooking the security protections that they employ on their out-of-band network. FIPS-certified solutions help establish consistent security standards across both paths. This is especially important in protecting against lateral attacks, where hackers infiltrate one network and are then able to jump to the other. In cases where attackers gain access to one segment of the network, matching security protocols across the main and OOB networks prevents them from moving laterally into sensitive management channels.

Using FIPS 140-3-certified encryption across both networks also strengthens the organization’s ability to monitor, manage, and control devices, even when the primary network is under threat.

7. Securing Remote and Edge Devices

For organizations with remote infrastructure, such as telecom and retail, OOB management is critical for managing network devices in distant locations. However, these environments often lack the physical security of centralized data centers, making them vulnerable to tampering. FIPS-certified solutions ensure that all communication with remote OOB devices is encrypted, which protects management data from unauthorized access.

FIPS 140-3 certification also supports the resilience of IoT and edge devices, which often require OOB management for secure monitoring, patching, and configuration.

Implement the Most Secure Out-of-Band Management with ZPE Systems

Security in Layers

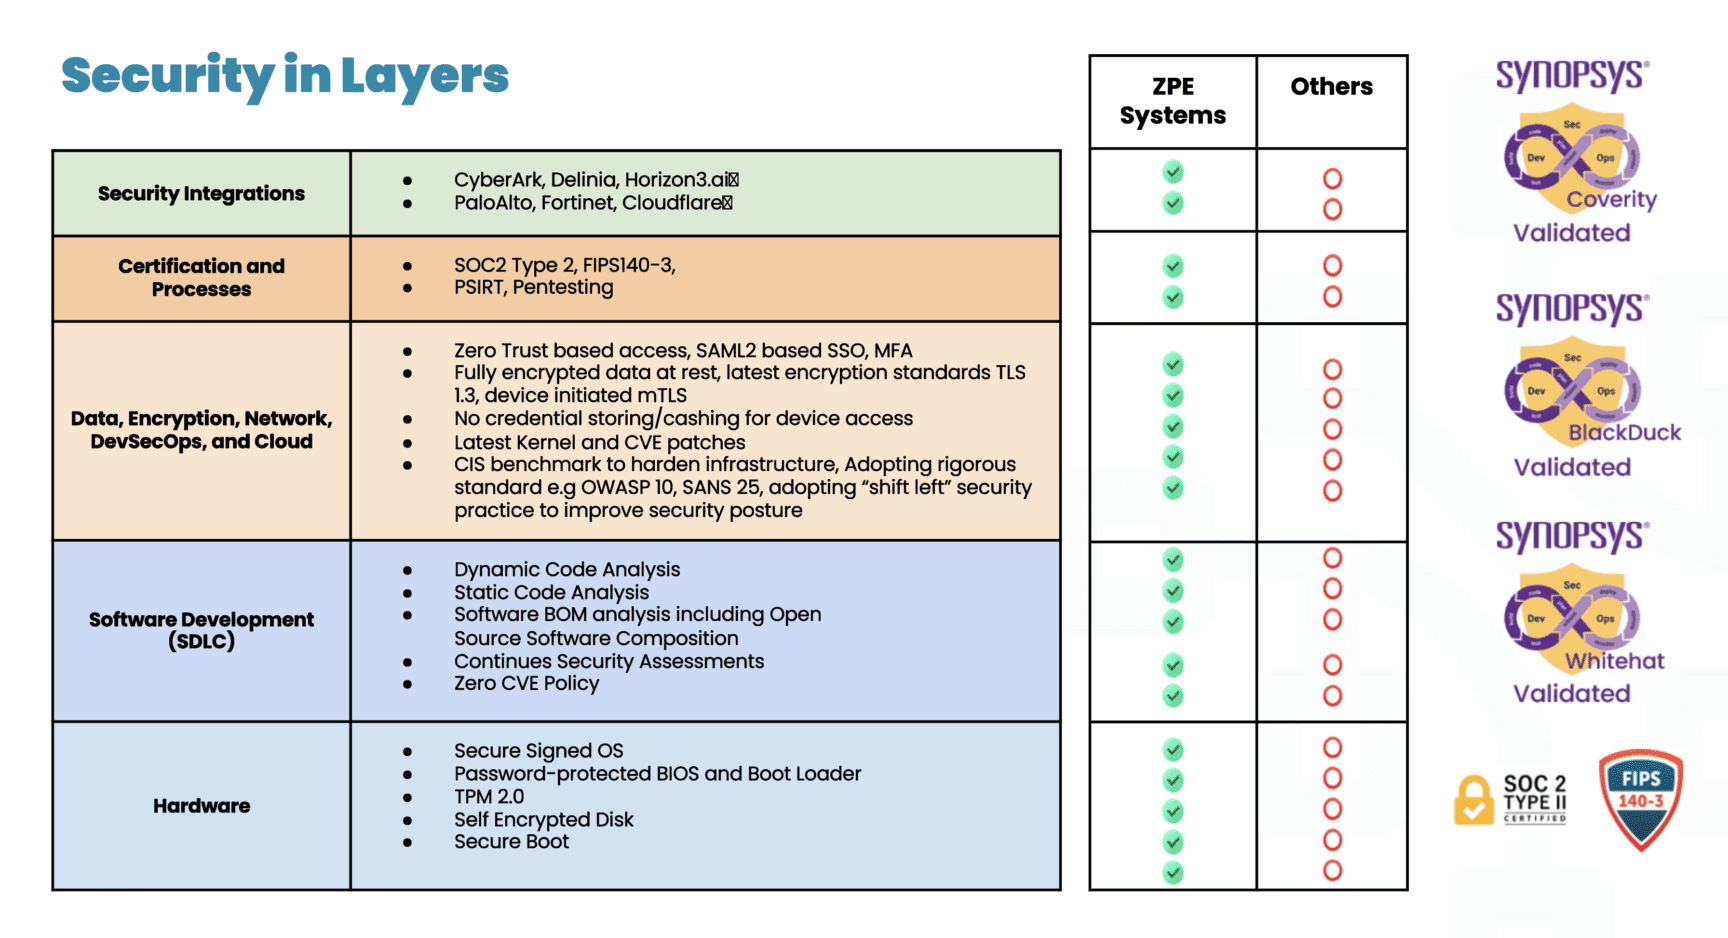
ZPE Systems’ Nodegrid is the industry’s most secure out-of-band management solution. Not only do we carry FIPS 140-3, SOC 2 Type 2, and ISO27001 certifications, but we also feature a Synopsys-validated codebase and dozens of security features across the hardware, software, and cloud layers. These are all part of a multi-layered, secure-by-design approach that ensures the strongest physical and cyber safeguards.

Download our pdf to explore more of our security assurance.

See FIPS-Certified Out-of-Band in Action

Our engineers are ready to walk you through our industry-leading out-of-band management. Use the button below to set up a 15-minute demo and explore FIPS 140-3 security features first-hand.

Terminal Server Alternative for Simple Break/Fix Use Cases


The Nodegrid Serial Console Core Edition terminal server alternative.

A terminal server is a device that provides consolidated remote management access to routers, switches, and other network infrastructure in data centers. There are numerous reasons to consider replacing an existing terminal server solution. Many of these devices are old and unpatched, leaving them vulnerable to exploits. Older solutions may not integrate well with newer hardware and software or lack the ability to unify management for all deployed terminal servers across a distributed enterprise network, creating a lot of management complexity and potential human error.

On the other hand, some newer terminal server solutions (also known as serial consoles or console servers) include advanced features or beefed-up hardware that increase both costs and complexity. It’s important to find the right balance between security, functionality, and ease-of-use for your particular use case. This guide compares five terminal server alternatives that are optimized for simple break/fix deployments, giving teams reliable remote management access without unnecessary complications.

Key takeaways


Pros

Cons

ZPE Nodegrid NSCP-Core Edition

  • Up to 48 managed serial ports in a 1U appliance
  • Extends OOB management and ZTP to legacy and mixed-vendor infrastructure
  • Analog modem and 5G/4G LTE options available
  • Robust on-board security features like BIOS protection and TPM
  • Integrates with third-party software
  • Supports a wide range of USB environmental monitoring sensors
  • Supports automation only via ZPE Cloud

Opengear CM8100

  • 2U model can manage up to 96 devices 
  • Extensible operating system
  • Automatic port discovery
  • No cellular, Wi-Fi, or analog modem
  • Doesn’t support 2FA or SAML 2.0 security
  • Most automation requires Lighthouse Enterprise software upgrade

WTI DSM Series

  • Can manage up to 50 devices
  • Optional analog modem or 4G cellular
  • Integrates with select third-party vendors
  • OS is not extensible
  • Lacks an embedded firewall
  • No environmental sensor ports

Vertiv Avocent ACS8000

  • Includes 8 managed USB ports for 56 total serial connections
  • 4G LTE WAN, OOB, and failover support
  • Environmental sensor port
  • Doesn’t support any third-party integrations 
  • Lacks advanced authentication features
  • No embedded firewall or VPN

Perle IOLAN SDSC

  • Simple, easy-to-manage solution
  • Includes an analog modem for OOB
  • Robust security features
  • OOB is only available over an analog connection
  • Doesn’t integrate with any third-party software
  • Barebones internal hardware can’t support modern software

Comparing terminal server alternatives for break/fix use cases

Read our in-depth reviews of the best terminal server alternatives below, or click here to compare tech specs.

ZPE Nodegrid NSCP-Core Edition

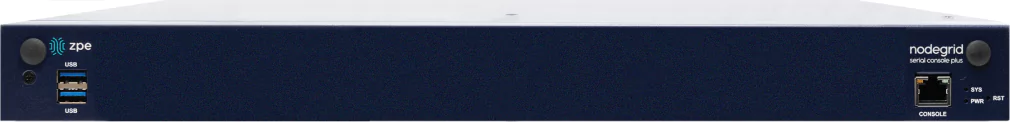
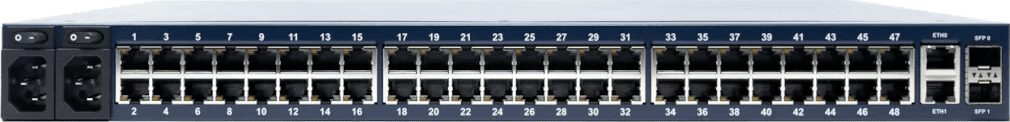
The Nodegrid Serial Console Core Edition (NSCP-CE) from ZPE Systems provides out-of-band (OOB) serial console management for up to 48 devices. It’s vendor-neutral, which means it can extend OOB control and zero-touch provisioning (ZTP) to legacy and mixed-vendor infrastructure. It has dual SFP+ and dual Ethernet ports as well as 5G/4G LTE, Wi-Fi, and analog modem options for both network failover and OOB management.

Nodegrid’s management software is available either on-premises or in the cloud so you can choose the best option for your use case. ZPE frequently patches the NSCP-CE’s software, firmware, and modern, Linux-based operating system to prevent known exploits. Plus, the device itself comes backed with security features like BIOS protection, UEFI Secure Boot, self-encrypted disk (SED), Trusted Platform Module (TPM) 2.0, and multi-site VPN using IPSec, WireGuard, and OpenSSL protocols.

The NSCP-CE’s vendor-neutral architecture integrates with third-party 2FA and SAML 2.0 authentication providers as well as other software for security, automation, and troubleshooting. It also supports a wide range of USB environmental monitoring sensors to help remote teams control conditions in the data center.

Pros:

  • Up to 48 managed serial ports in a 1U appliance
  • Extends OOB management and ZTP to legacy and mixed-vendor infrastructure
  • Analog modem and 5G/4G LTE options available
  • Robust on-board security features like BIOS protection and TPM
  • Integrates with third-party software
  • Supports a wide range of USB environmental monitoring sensors

Cons:

  •  Supports automation only via ZPE Cloud

Opengear CM8100

The Opengear CM8100 console server provides remote terminal server management for up to 48 devices in a 1U form-factor, or up to 96 devices in a 2U form-factor. It comes with dual ETH ports or dual switchable ETH/SFP ports for in-band, out-of-band, and failover, without any alternative network interfaces like cellular or analog modem. It supports some automation, such as ZTP and Python scripts, but only with an upgraded version of the Opengear Lighthouse management software.

The CM8100 includes some advanced security features like IPsec & OpenVPN, SSL tunnels, and Secure Shell (SSHv2) as well as a stateful firewall with IP filtering and port forwarding. While its embedded Linux operating system is programmable and extensible with third-party integrations, it does not support 2FA, SAML 2.0, or multi-site IPsec VPN.

Pros:

  • 2U model can manage up to 96 devices
  • Extensible operating system
  • Automatic port discovery

Cons:

  • No cellular, Wi-Fi, or analog modem
  • Doesn’t support 2FA or SAML 2.0 security
  • Most automation requires Lighthouse Enterprise software upgrade

WTI DSM Series

The WTI DSM series provides out-of-band terminal server management for up to 50 devices. It comes with options for single or dual Ethernet interfaces as well as an optional analog modem or cellular interface. The WTI centralized management software integrates with some third-party software like PRTG and Splunk, and it provides ZTP and RESTful API support for automation. However, only a small handful of providers are supported, and the device’s OS is not extensible.

DSM console servers come with robust security features including advanced authentication, port-specific password protection, and invalid access lockout and alarm. It also integrates with Duo, RSA, Okta, and Azure for 2FA. It lacks an embedded firewall, however, as well as an environmental sensor port.

Pros:

  • Can manage up to 50 devices
  • Optional analog modem or 4G cellular
  • Integrates with select third-party vendors

Cons:

  • OS is not extensible
  • Lacks an embedded firewall
  • No environmental sensor ports

Vertiv Avocent ACS8000

The Vertiv Avocent ACS800 can manage up to 48 devices over RS-232 serial and up to 8 devices over USB for a total of 56 managed ports. In addition to dual Ethernet and dual SFP ports, you can add 4G LTE connectivity for WAN, OOB, and failover. The on-premises DSView management software provides ZTP as well as event logging and notifications, but it doesn’t support any third-party integrations.

The ACS8000 doesn’t support 2FA, SAML 2.0, or advanced authentication features, though it does support FIPS 410-2 cryptography. It also lacks an embedded firewall and VPN functionality. It does, however, have an environmental sensor port.

Pros:

  • Includes 8 managed USB ports for 56 total serial connections
  • 4G LTE WAN, OOB, and failover support
  • Environmental sensor port

Cons:

  • Doesn’t support any third-party integrations
  • Lacks advanced authentication features
  • No embedded firewall or VPN

Perle IOLAN SDSC

The Perle IOLAN SDSC is a simple break/fix terminal server that can manage up to 32 devices. It has dual Ethernet ports for WAN and failover, but OOB is only available via the included analog modem, so it’ll be a much slower experience for remote administrators. Perle’s management software provides ZTP but does not offer any automation capabilities or integrate with any third-party solutions. Additionally, the SDSC’s barebones CPU, RAM, and storage hardware may make the software itself slow and frustrating to use, even over the in-band Ethernet connection.

The IOLAN SDSC comes with an embedded firewall and advanced security features like 2FA, IPsec VPN/OpenVPN, and remote RADIUS, TACACS+, and LDAP authentication.

Pros:

  • Simple, easy-to-manage solution
  • Includes an analog modem for OOB
  • Robust security features

Cons:

  • OOB is only available over an analog connection
  • Doesn’t integrate with any third-party software
  • Barebones internal hardware can’t support modern software

Tech Specs: Terminal server alternatives for break/fix use cases


Nodegrid NSCP-CE

Opengear CM8100

WTI OOB Rescue

Vertiv Avocent ACS8000

Perle IOLAN SDSC

Serial Ports

16 / 32 / 48x RS-232

16 / 32 / 48 / 96x RS-232

8 / 24 / 40x RS-232 

8 / 16 / 32 / 48x RS-232

8 / 16 / 32x RS-232

Network Interfaces

2x SFP & 2x ETH

1x Analog modem (optional)

2x 5G/4G LTE (optional)

2x ETH

1x ETH

or

2x ETH

1x Analog modem (optional)

1x 4G Cellular (optional)

2x SFP & 2x ETH

2x ETH

Additional Interfaces

1x RS-232 console

2x USB 3.0 Type A

1x RS-232 console

2x USB 3.0

1x RS-232 console

1x USB Mini Set-up Port

1x RS-232 console

8x USB 2.0 Type A

–

CPU

Intel x86_64 Dual-Core

ARM Cortex-A9 1.6 GHz Dual-Core

–

ARM Cortex-A9 Dual-Core

MPC8349E 400 MHz

Storage

16GB Flash (upgrades available)

32GB eMMC Flash

–

16GB eMMC Flash

16MB Flash

RAM

4GB DDR4 (upgrades available)

2GB DDR4

–

1GB DDR3L

64MB

Environmental Monitoring

Any USB sensors

–

–

4 digital-in ports

–

Wi-Fi

Optional

No

No

No

No

Cellular

Optional

No

Optional

Optional

No

Power

Dual AC

or

Dual DC

Dual AC

or

Dual DC

Single AC

or

Single DC

Single or Dual AC

or

Single or Dual DC

Single AC

Form Factor

1U Rack Mounted

1U Rack Mounted (up to 48 ports)

2U Rack Mounted (96 ports)

1U Rack Mounted

1U Rack Mounted

1U Rack Mounted

Experience the convenience of a vendor-neutral management platform

The Nodegrid Serial Console Core Edition is a vendor-neutral terminal server alternative that strikes the perfect balance between simplicity, functionality, and security. With flexible OOB and networking options, extensible cloud-based software, and industry-leading security features, Nodegrid can streamline and protect any environment.

Schedule a demo to see the Nodegrid terminal server alternative in action.

End of Row vs Top of Rack Deployments

End of Row vs Top of Rack Deployments

The terms end-of-row and top-of-rack refer to two different approaches to data center architecture design. Both approaches have advantages and disadvantages that make them suited to different use cases or teams, with neither being the clear “winner” overall. This blog compares end-of-row vs. top-of-rack deployments based on crucial factors like cost, management complexity, scalability, and resilience to help organizations choose the right approach for their environment.


What is an end-of-row (EoR) deployment?

ZPE Graphic Request IR Nov 4
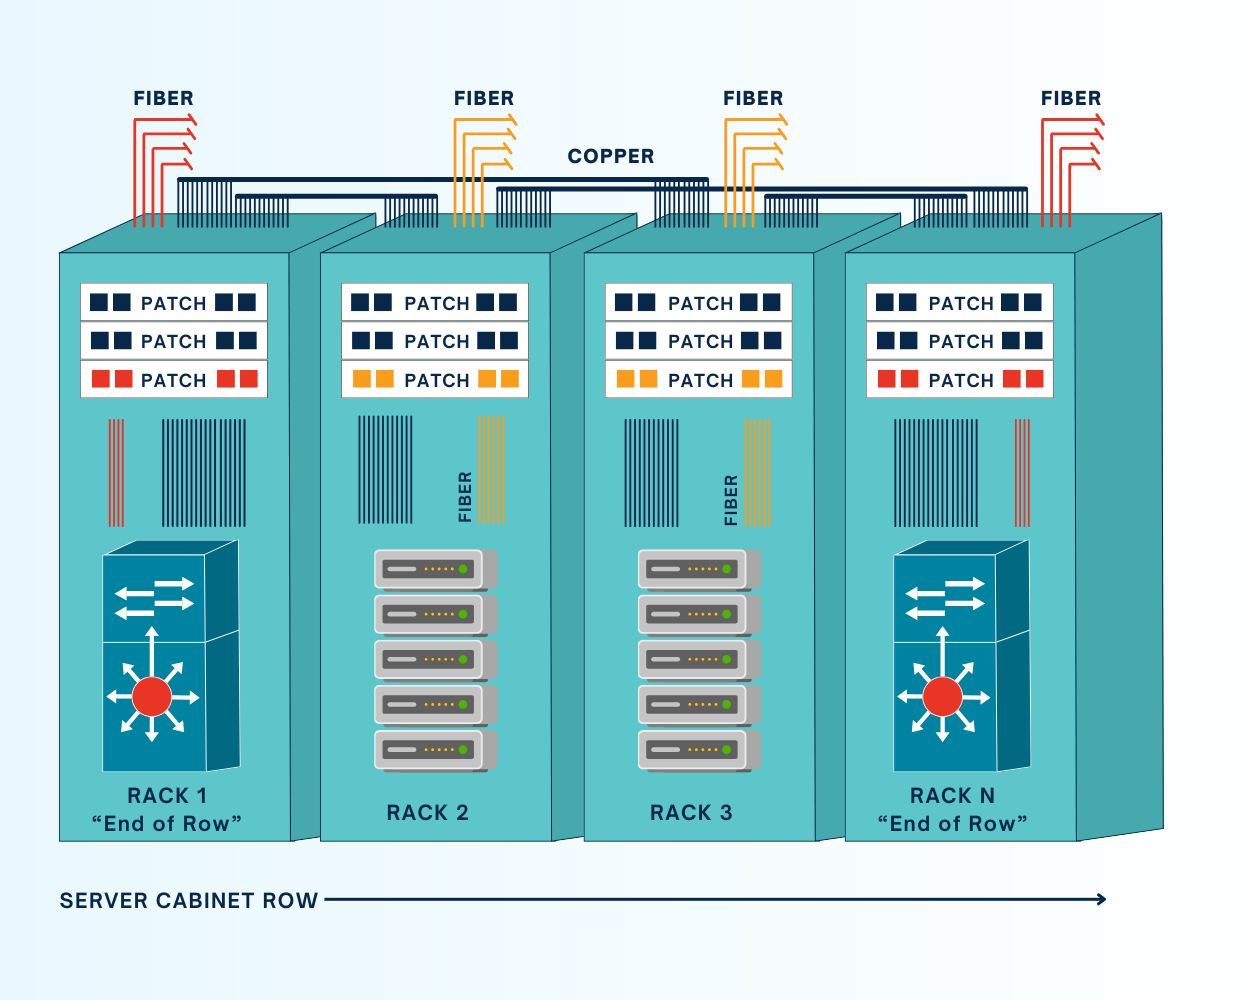
In data center deployments consisting of multiple rows of racks or cabinets, it’s common for teams to consolidate all the networking for each row in one physical location, rather than deploying switches in every single rack. All patch cables for the devices in a particular row are run to the dedicated networking cabinet, which is typically (but not always) at the end of the row. An end-of-row (or EoR) architecture requires fewer switches than a ToR deployment, which helps reduce costs and management complexity while enabling easier scaling.

One of the main drawbacks of this architecture is that the EoR switch is a single point of failure for the entire row. If that switch fails due to a botched update, ransomware attack, or other adverse event, the whole row loses network access. Running cables from each cabinet to the EoR can also get messy very quickly, especially at scale. In the long run, it’s also a less flexible architecture that forces teams to consider an entire row of infrastructure every time they want to change or upgrade networking components.


What is a top-of-rack (ToR) deployment?

ZPE Graphic Request IR Nov 4 (1)
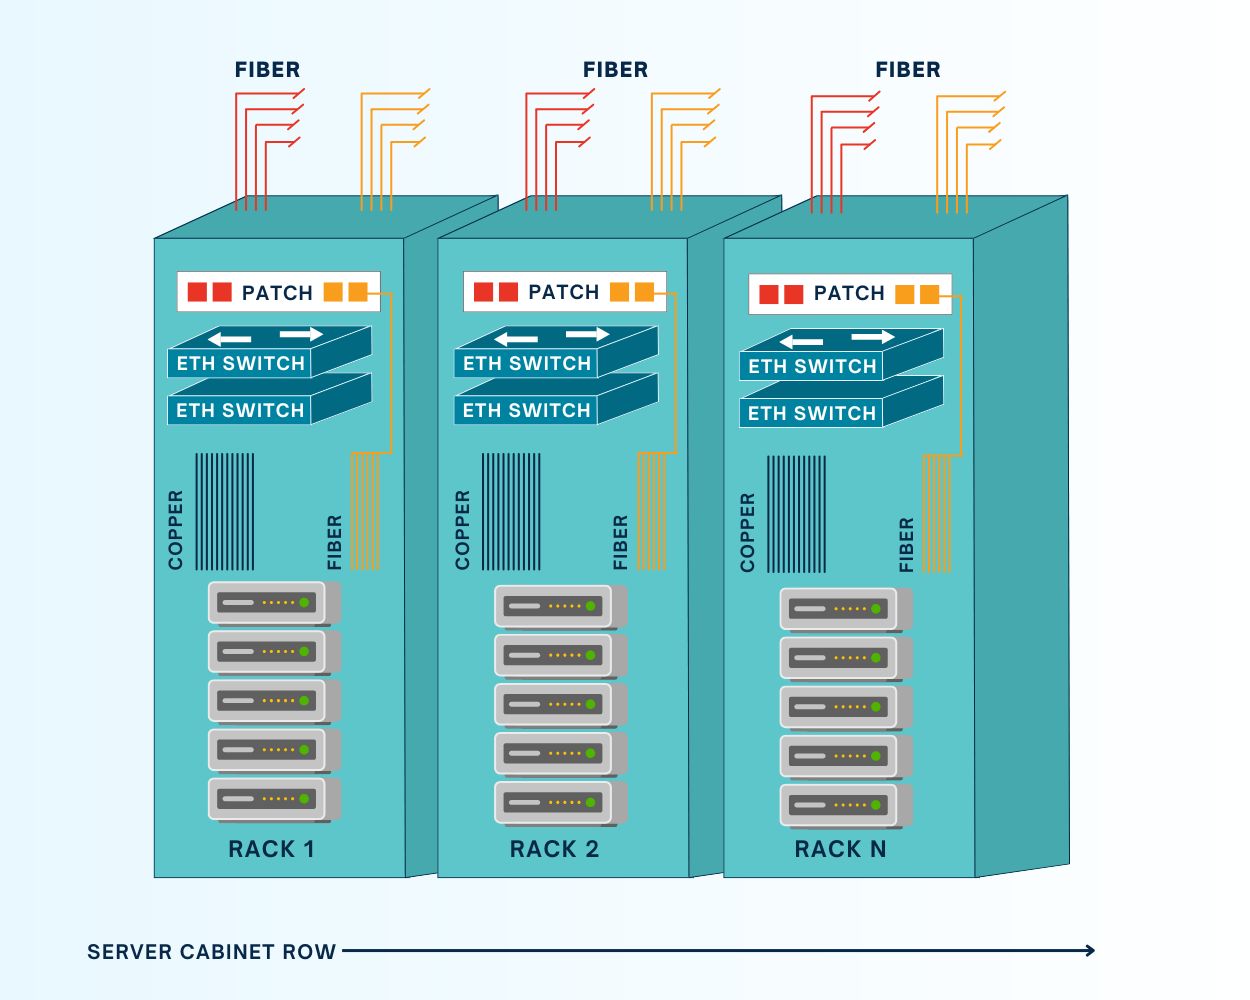
In a top-of-rack data center architecture, DC teams install one or more switches in every rack of their deployment; despite the name, the switch doesn’t need to actually be at the very top of the rack. A ToR deployment keeps copper/Ethernet patch cables inside the rack, which helps with cable management. It also eliminates the single-point-of-failure that an EoR switch represents – if one ToR switch goes down for some reason, only the devices within that rack are affected, vs. the entire row. Another major benefit of EoR deployments is that each rack becomes a modular unit that DC teams can modify, upgrade, or scale without necessarily affecting other racks in the row.

On the other hand, a ToR deployment requires more switches than an EoR deployment, which can increase costs and complexity. More switches equate to more power draw, and they add an extra network hop to local traffic that could possibly affect throughput. Each switch must also be monitored, secured, and regularly patched, potentially creating more work for infrastructure teams. As a result, ToR deployments are also more challenging to scale, as each new rack added to the data center requires an additional ToR switch.

Comparing end-of-row vs top-of-rack deployments: Which should you choose?


End-of-Row Top-of-Rack
Number of switches One or more per row One or more per rack
Cable management Requires patch cables running along the entire row Keeps patch cables within the rack or cabinet
Cost Fewer switches and lower power draw keeps costs down More switches and higher power draw gets more expensive
Complexity Fewer switches to secure, manage, and troubleshoot More devices to manage
Ease of scaling Can deploy an entire new row with only one networking cabinet Each new rack requires one or more switches
Flexibility Inflexible; networking changes affect entire row Each rack is a modular unit that can be changed without affecting others
Resilience EoR switch is a single point of failure for the entire row One rack’s switch can go down without affecting any other racks


Both EoR and ToR architectures have advantages and disadvantages, with neither being the clear-cut winner for every possible use case.

End-of-row deployments are more cost-effective and easier to manage and scale, so they’re often favored by smaller, leaner IT teams or, on the opposite end of the spectrum, very large (or hyperscale) data centers. For example, a large cloud provider might prefer EoR to cut down on the number of switches to purchase, deploy, and manage at their hubs.

Top-of-rack deployments are modular, flexible, and resilient, which makes them a great choice for DevOps teams that need the ability to add or change components at any time without affecting the entire architecture. For example, managed service providers might prefer ToR so they can easily customize or update one customer’s rack without worrying about how the changes will impact others.

How Nodegrid improves resilience for EoR and ToR deployments

Nodegrid serial console switches can be deployed top-of-rack or end-of-row to improve the resilience of either architecture. Nodegrid switches connect to the serial port on data center devices to provide out-of-band (OOB) management, allowing teams to remotely manage and troubleshoot DC equipment even when the primary network is down. They isolate the management interfaces for data center infrastructure, making them inaccessible to malware or malicious actors on the production network. Plus, Nodegrid also provides network failover to keep business-critical services running during adverse events.

Nodegrid serial consoles have an open architecture that can integrate and host other vendors’ software and virtualized network functions. That means a single Nodegrid box could theoretically replace an entire rack of networking hardware, streamlining EoR deployments and making ToR architectures more feasible for lean, budget-strapped IT teams. Plus, Nodegrid switches and all connected devices can be remotely managed from a single, on-premises or cloud-based software platform, significantly reducing management complexity for either deployment.

Reach out to ZPE Systems for more help comparing end-of-row vs. top-of-rack deployments or to see a demo of the Nodegrid platform in action.

Zombie Servers: The Hidden Energy Drainers in Data Centers

Zombies in the data center
As enterprises adopt AI, cloud computing, and data analytics, one thing lurks in the shadows of their data centers: zombie servers. These inactive or severely underutilized servers take a big bite out of operations, drawing power and resources without contributing meaningful work. Research from the Uptime Institute indicates that as much as 30% of servers may be idle at any given time, suggesting enterprises could save millions each year by identifying and eliminating these “zombies.”

The Cost of Zombie Servers

When it comes to cost, zombie servers can devour more than their fair share. Each idle server can consume approximately 200 to 400 watts per hour, resulting in annual power costs of $400 to $600 per server. In large data centers housing thousands of servers, wasted energy expenses can easily scale into the millions. Currently, U.S. data centers account for over 4% of the nation’s total electricity consumption, a figure projected to rise to 6% by 2026 due to growing demands from AI and cloud computing applications.

How ZPE Systems’ Nodegrid Fights Zombie Servers

Out-of-band management (OOBM) solutions, like ZPE Systems’ Nodegrid, provide an effective way to monitor, manage, and optimize data center infrastructure, even when the primary network is down. When combined with ServerTech Intelligent PDUs, data center admins can remote-in to identify and address zombie servers, so they can ensure their operations run at peak efficiency.

Key Features of Nodegrid’s Out-of-Band Management for Zombie Server Management

  • 24/7 Monitoring and Real-Time Insights: Nodegrid allows IT teams to continuously monitor server performance, making it easy to detect underutilized or idle servers. Real-time metrics show server activity, power usage, and health, so teams can pinpoint servers that may need to be repurposed or removed.
  • Detailed Power Usage Data: The combined Nodegrid and ServerTech solution provides comprehensive energy usage data, so teams can see inefficiencies and where power is consumed most. This is essential for high-density data centers, where wasting even a little bit of power adds up to substantial costs. These insights help data center operators pinpoint zombie servers, reducing energy costs and freeing up space.
  • Enhanced Automation and Management Control: With automation features, Nodegrid simplifies the complex task of managing server lifecycles. For instance, automated alerts can notify teams when a server reaches a specific threshold of low utilization, enabling quicker action to reassign or shut down the server.
  • Increased Security and Resilience: Nodegrid enhances security by providing direct access to infrastructure via isolated management. Teams can access critical systems even during network failures, to ensure servers remain compliant, functional, and secure.

Benefits of Removing Zombie Servers

AI and other resource-intensive applications mean data centers need to be as efficient as possible. Zombie servers are not just an energy problem; they impact a data center’s ability to scale and meet demand for high-performance computing. Here are some benefits of removing or repurposing zombie servers:

  • Energy Efficiency: Data centers can significantly lower energy costs and reduce environmental impact by shutting down idle servers.
  • Cost Savings: Operating more efficiently by removing zombie servers can lead to substantial annual savings, freeing up resources for necessary expansions.
  • Optimized AI-Ready Infrastructure: Freeing up resources allows data centers to repurpose space and energy toward servers that can support AI and other high-density applications.

Get Help Fighting Zombie Servers

Set up a call with one of ZPE Systems’ engineers, and we’ll show you how to get zombie servers out of your data center. Click the button below to schedule your call.

Watch a Walkthrough Demo

Watch this 20-minute video where Marcel van Zwienen (Senior Sales Engineer) demonstrates the remote management capabilities of Nodegrid and ZPE Cloud.

Marcel van Zwienen gives a walkthrough of ZPE Cloud for remote device management.

More Valuable Resources for Remote Monitoring

Check out these resources to help fight zombie servers and other inefficiencies lurking in your data center:

Data Center Environmental Sensors: Everything You Need to Know

According to a recent Uptime Institute survey, severe outages can cost more than $1 million USD and lead to reputational loss as well as business and customer disruption. Humidity, air particulates, and other problems could shorten the lifetime of critical equipment or cause outages. Unfortunately, much of a business’s critical digital infrastructure and services are housed in remote data centers, making it difficult for busy IT teams to keep eyes on the environmental conditions.

Data center environmental sensors can help teams prevent downtime by monitoring conditions in remote infrastructure deployments and alerting administrators to any problems before they lead to equipment failure. This blog explains how environmental sensors work and describes the ideal environmental monitoring solution for minimizing outages.

How data center environmental sensors reduce downtime

Data center environmental sensors are deployed around the rack, cabinet, or cage to collect information about various conditions that could negatively affect equipment like routers, servers, and switches. 

Mitigating environmental risks with data center environmental sensors

Environmental Risk Description How Environmental Sensors Help
Temperature All data center equipment has an optimal operating temperature range, as well as a max temp threshold above which devices may overheat. Environmental sensors monitor ambient temperatures and trigger automated alerts when it gets too hot or too cold in the data center.
Humidity If the air in the data center gets too humid, moisture may collect on the internal components of devices and cause corrosion, shorts, or other failures. Environmental sensors monitor the relative humidity in the DC and alert administrators when there’s a danger of moisture accumulation.
Fire A fire in the data center could burn equipment, raise the ambient temperature beyond acceptable limits, or activate automatic fire suppression controls that damage devices. Environmental sensors detect the heat and smoke from fires, giving DC teams time to shut down systems before they’re damaged.
Tampering A malicious actor who’s able to get past data center security (such as an inside threat) could potentially tamper with equipment to damage or breach it. Tamper detection sensors alert remote teams when data center cabinet doors are opened or a device is physically moved.
Air Particulates Smoke, ozone, and other air particulates could potentially damage data center infrastructure by oxidizing components or clogging vents. Environmental sensors monitor air quality and automatically alert teams when particulates are detected.

These sensors report back to monitoring software that’s either deployed on-premises in the data center or hosted in the cloud. Administrators use this software to view real-time conditions or to configure automated alerts.

Environmental monitoring sensors help reduce outages by giving remote IT teams advance warning that something is wrong with conditions in the data center, enabling them to potentially fix the problem before any systems go down. However, traditional monitoring solutions suffer from a number of limitations.

  1. They need a stable internet connection to allow remote access, so if there’s an ISP outage or unknown failure, teams lose their ability to monitor the situation.
  2. Many of them use on-premises software that requires administrators to connect via VPN to monitor or manage the solution, creating security risks and management hurdles.
  3. Most environmental monitoring systems don’t easily integrate with other remote management tools, leaving administrators with a disjointed patchwork of platforms to wrestle with.

The ideal data center environmental monitoring solution

The Nodegrid data center environmental monitoring platform overcomes these challenges with a combination of out-of-band management, cloud-based software, and a vendor-agnostic architecture.

Nodegrid environmental sensors work with Nodegrid serial consoles to provide remote teams with a virtual presence in the data center. These devices create an instant out-of-band network that uses a dedicated internet connection to provide continuous remote access to all connected sensors and infrastructure. This network doesn’t rely on the primary ISP or production network resources, giving administrators a lifeline to monitor and recover remote data center devices during an outage. The addition of Nodegrid Data Lake also allows teams to collect environmental monitoring data, discover trends and insights, and create better automation to address issues.

Nodegrid’s data center environmental monitoring and infrastructure management software is available on-premises or in the cloud, allowing teams to access critical equipment and respond to alerts from anywhere in the world. Plus, all Nodegrid hardware and software is vendor-neutral, supporting seamless integrations with third-party tools for automation, security, and more.

Schedule a free Nodegrid demo to see our data center environmental sensors and vendor-neutral management platform in action!