Providing Out-of-Band Connectivity to Mission-Critical IT Resources

What Is a Zero Trust Gateway?
What Is a Zero Trust Gateway(2)
The constant threat of cyberattacks has made network security a top priority for companies in every sector, with Gartner predicting that global cybersecurity spending will reach $188 billion in 2023. However, security continues to get more challenging due to factors like a rise in remote work, an increasing reliance on touchless internet of things (IoT) devices, and the overall decentralization of enterprise networks. It’s hard to create a secure perimeter around the enterprise when its users, devices, applications, and data could be anywhere in the world.

The zero trust security methodology addresses this challenge by shrinking the focus from one large security perimeter and instead creating smaller “micro-perimeters” around each individual resource that needs defending. It’s called zero trust because it follows the principle of “never trust, always verify.” That means each user and device needs to verify its identity and prove its trustworthiness before it can penetrate the micro-perimeter. So, for example, if a cybercriminal uses stolen credentials to log into the enterprise network, they have to pass through many different security checkpoints to see or access any sensitive resources, which increases the likelihood they’ll get caught before excessive damage is done.

One way to implement micro-perimeters and apply zero trust security policies is with a device called a zero trust gateway. This post discusses the technologies that make up a zero trust gateway and explains how they work together to defend enterprise networks.

What is a zero trust gateway?

A zero trust gateway is a device that sits at the edge of the network – or at the top of the rack – and applies zero trust security policies and controls to traffic flowing in either direction. The gateway can be a dedicated security appliance, but it’s often more cost- and space-effective to use a multi-functional device that combines security, networking, and infrastructure management in a single box.

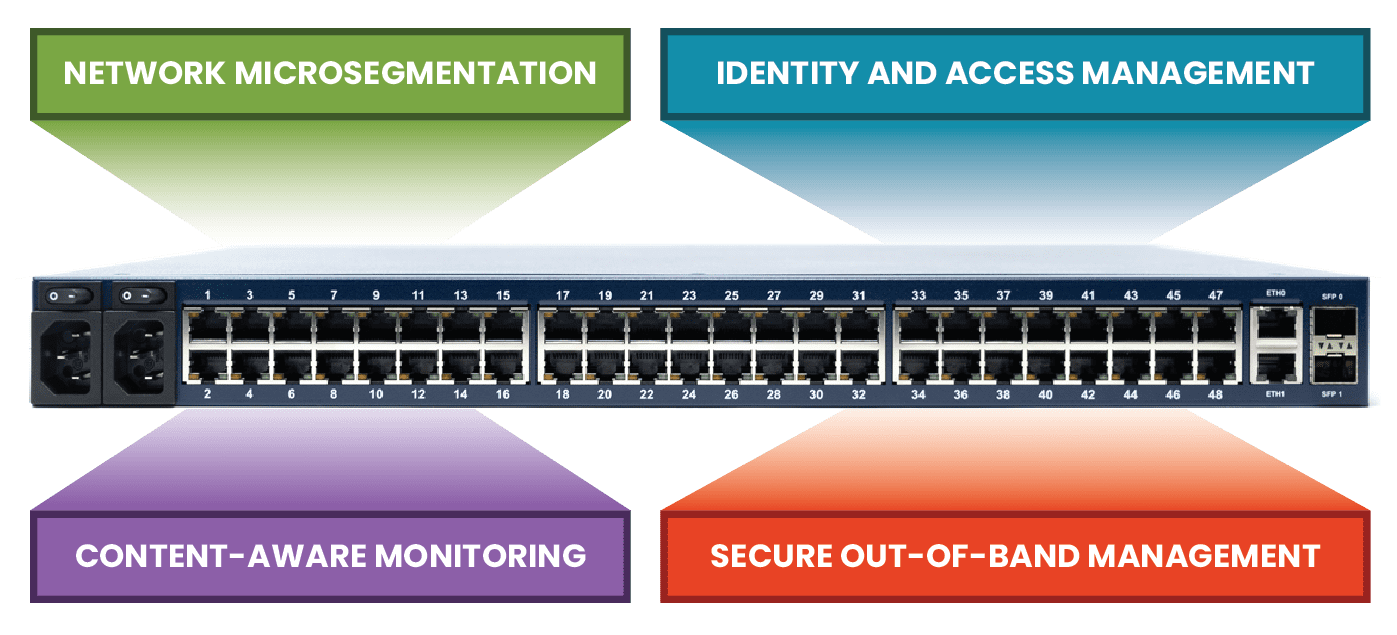
Some of the key features used in an all-in-one zero trust gateway include network micro-segmentation, identity and access management, context-aware monitoring, and secure out-of-band management. There are a small number of mature solutions that deliver all of these features off-the-shelf, but they lock you into their small solution ecosystem and limited feature roadmap. A better approach is to start with a vendor-neutral platform that lets you host and integrate your choice of security applications to create a fully customized zero trust gateway. Let’s walk through how each of these security technologies works and how to combine them into a bespoke zero trust gateway solution.

To see an example of a vendor-neutral zero trust gateway at work, request a demo of the Nodegrid solution from ZPE Systems.

Request a Demo

Network micro-segmentation

A zero trust micro-perimeter is made up of granular access control policies and security controls that are custom-tailored to the specific vulnerabilities and requirements of resources they’re defending. For example, an on-premises database containing sensitive financial records needs different policies than a cloud-based application that doesn’t process any personal information. To implement micro-perimeters, resources first need to be logically organized based on their sensitivity level, who needs access to them, and what their interdependencies are.

Network micro-segmentation is used to separate resources based on these criteria so that micro-perimeters can then be applied. For a device to be considered a zero trust gateway, it must support VLAN micro-segmentation and be able to apply access control rules consistently across all micro-segments.

Identity and access management

In a zero trust architecture, user and device permissions should be limited to only what’s necessary to perform their job role. For example, an HR account used to manage employee records shouldn’t have access to customer financial data, and vice versa. Access policies should be specific to individual micro-segments and resources and need to be applied to all users and devices consistently, no matter where they’re logging in from. That means a remote user should follow the same authentication steps and have the same permissions as they would if they logged in at the office.

For a large enterprise network, this is only achievable with a centralized identity and access management (IAM) solution. An IAM provides a single platform from which to create, manage, and apply security policies. A zero trust IAM also enables best practices like single sign-on (SSO) and two-factor authentication (2FA).

A zero trust gateway needs to integrate with your chosen IAM provider to ensure that policies are applied to both production traffic and management traffic. Some vendor-neutral gateway solutions can even directly host and run third-party IAM solutions, providing a more integrated experience and saving rack space.

Context-aware monitoring

Many successful cyberattacks use stolen credentials gained through phishing schemes and other social engineering tactics. For example, Mailchimp was recently attacked by malicious actors using credentials stolen from employees through social engineering. It’s difficult to detect and contain such an attack because the criminal looks like an authorized user. However, careful monitoring often reveals suspicious behavior, such as logging in from an unusual IP address or time zone, making multiple access requests to areas of the network they don’t usually visit, or transferring abnormally large quantities of data.

User and entity behavior analytics, or UEBA, uses machine learning technology to monitor and analyze account activity on the enterprise network. UEBA creates a baseline of “normal” behavior for individual accounts so it can detect any anomalous activity. UEBA integrates with other security and monitoring solutions, such as IAM and firewalls, so it can compare data from various sources to make more informed decisions. This is one of the ways that zero trust security verifies the trustworthiness of accounts trying to access sensitive resources, making UEBA a critical component of zero trust gateways.

Secure out-of-band (OOB) management

Admins need a fast and reliable way to access remote infrastructure for management, troubleshooting, and recovery. For example, it’s common for a single data center management team to be responsible for customer equipment in multiple DCs distributed around the world for redundancy. These admins can’t physically go on-site every time a firmware update fails or a device loses its IP address. That’s why they rely on remote out-of-band (OOB) management; remote OOB management creates a separate network just for management traffic that doesn’t rely on the production LAN. Admins access the OOB network using a dedicated management device, like a jump box or a serial console server.

This management device is a tempting target for cybercriminals, as gaining control of that device will give them complete control over the connected infrastructure. One way to protect the OOB network is by using a zero trust gateway with integrated management ports. For example, the Nodegrid Net Services Router (NSR) is a modular zero trust gateway that can be customized to connect to any type of device that needs to be managed or secured. The NSR comes with gateway routing and switching capabilities, an embedded firewall, and hardware security features like secure boot and a self-encrypted disk. Nodegrid is also completely vendor-neutral, which means it can directly host or integrate with your choice of third-party security solutions, including next-generation firewalls (NGFWs) and zero trust technologies like identity and access management and UEBA.

The NSR is a modular, open platform upon which to build a fully customized zero trust gateway for large data center deployments. The Nodegrid product line from ZPE Systems also includes a variety of serial console solutions and integrated all-in-one gateway routers to support other use cases, such as edge computing sites, branches, and automated IoT deployments.

A zero trust gateway helps organizations implement micro-perimeters of specific policies and controls to defend sensitive data and other valuable resources. A vendor-neutral, integrated solution like the Nodegrid Serial Console Plus from ZPE Systems makes it possible to combine zero trust security with networking and management functionality to create a streamlined, cost-effective zero trust gateway deployment.

Ready to learn more about Zero Trust Gateway?

To learn more about deploying Nodegrid as a zero trust gateway in your enterprise, contact ZPE Systems today.
Contact Us

ZPE Systems’ Services Delivery Platform accelerates time-to-market

Zero Pain Ecosystemedit

ZPE Systems’ Services Delivery Platform accelerates time-to-market with any app, anytime, anywhere

IT teams can deliver instant business value with the on-demand services delivery architecture

Fremont, CA, April 25, 2023 — ZPE Systems’ Services Delivery Platform is IT’s ‘easy’ button for delivering instant business value. Instead of deploying dedicated NGFW hardware and Intel® NUCs, ZPE’s Intel-based platform runs 3rd party apps at remote locations delivered via ZPE Cloud app marketplace. This speed and flexibility simplify global service delivery and fleet management for manufacturing, healthcare, finance, and other industries, where any app can be automatically deployed from the cloud.

Why is this important?

Private-cloud and on-prem services must run on dedicated systems, which causes infrastructure sprawl. This complexity pulls IT teams away from generating revenue, recovering from outages, and stopping ransomware attacks. Their job becomes managing low-level infrastructure and inefficient delivery pipelines. The Services Delivery Platform alleviates this by giving them the speed and flexibility to:

  • Secure remote locations with cloud-deployed pen test agents & other services
  • Segment edge networks regardless of interface type
  • Eliminate supply chain risks with hardened devices
  • Shrink attack surfaces with swift centralized patch management
  • Collapse device stacks into 1RU or less using virtual services

Services Delivery Platform apps and services

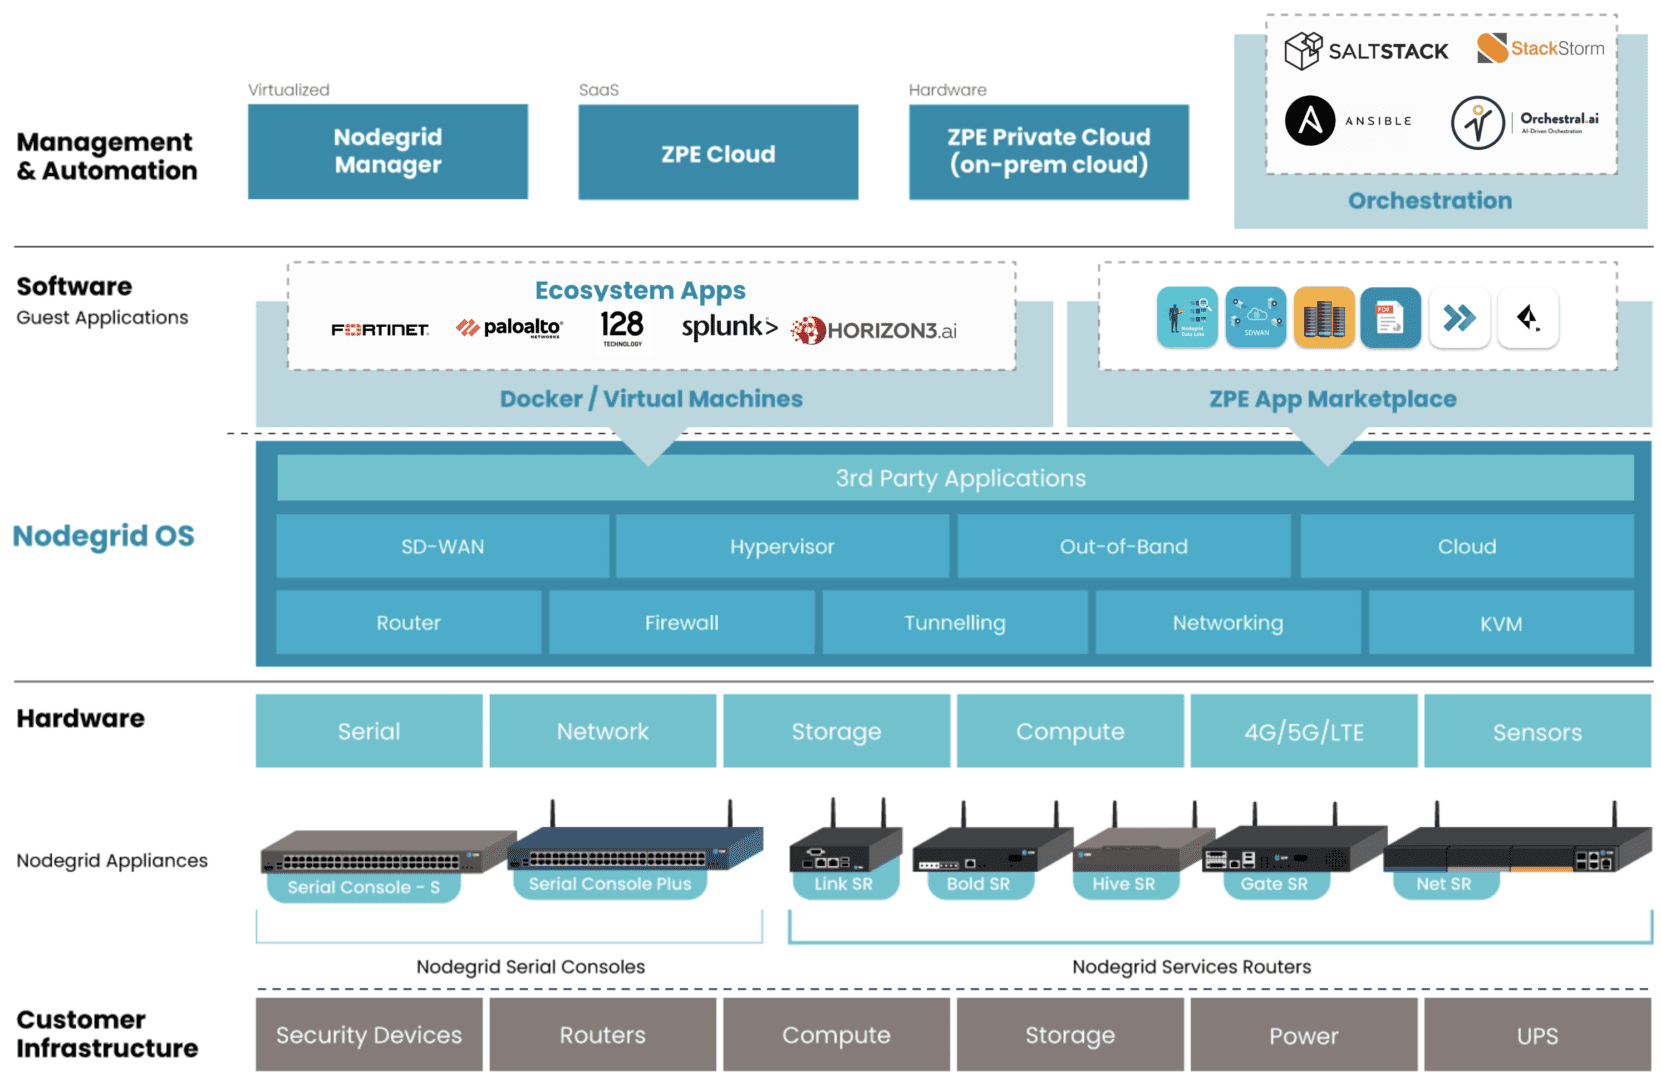
Graphic: ZPE’s Services Delivery Platform is represented as blue blocks. Examples of 3rd-party hosted apps are represented in white blocks under Ecosystem Apps.

The Services Delivery Platform brings to life Gartner’s concept of platform engineering. This platform-as-a-service model allows admins to tailor environments with the right apps for SD-WAN, NGFW, pen testing, and other functions, without battling vendor lock-in or changes in security posture. They also gain a consistent management experience across private-cloud and on-prem solutions.

Teams typically avoid platform engineering because there are no best practices for creating the proper control plane management network on secure devices.

ZPE Systems worked with Big Tech to define these best practices, which enterprises can now apply to private-cloud colo and edge deployments using the Services Delivery Platform. This establishes the resilient control plane management network and platform engineering component, both on a single, multi-function device connected to the cloud.

Enterprises accelerate revenue generation, reduce outage costs, and stop ransomware attacks using this architecture.

How does it work?

Nodegrid edge routers bring dedicated LAN and WAN links through multiple interface types (serial, ethernet, USB, IPMI). These create a secure control plane — a Double-RingTM management architecture — while eliminating the hardware attack surface with security features including TPM 2.0, encrypted disk, geofencing, and fully-signed Nodegrid OS.

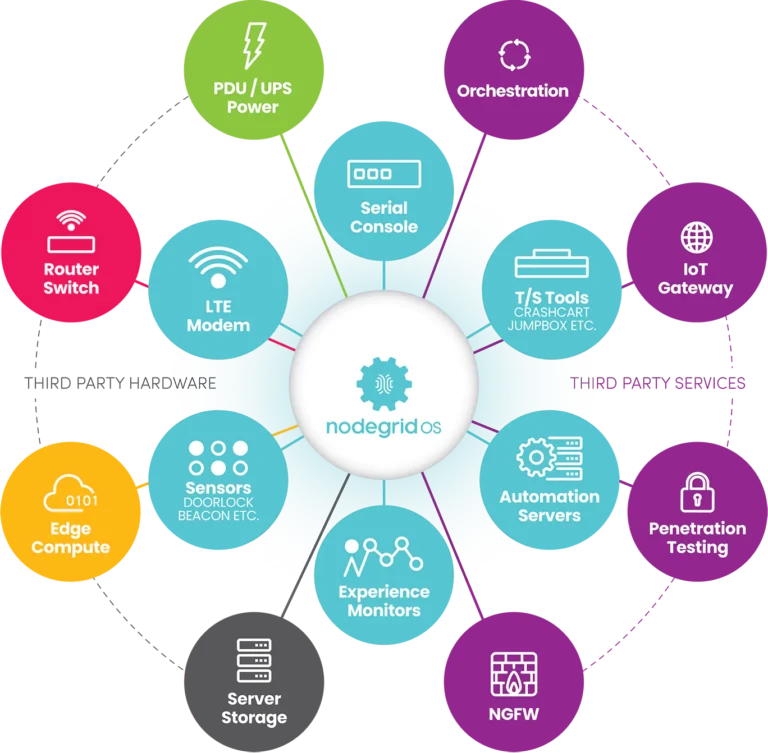
This network is the foundation of the Services Delivery Platform. Along with hosting the management network, Nodegrid devices directly run VMs, containers, and any choice of app using the onboard multi-core Intel CPU and Linux-based Nodegrid OS. This OS also extends automation across environments and devices to give teams end-to-end activation and chaining of SASE, NGFWs, SD-WAN, and any cloud or on-prem solution.

“I’ve been in ops for a long time. Most of your day is spent just figuring out how to get your environments to work right,” says James Cabe, Director, Technical Alliances at ZPE Systems. “The Services Delivery Platform is a game-changer. The whole thing sits right on the Nodegrid box and you can switch or swap out services whenever you need to. Just choose what you want to deploy and go. It’s all done via separate control plane with no attack surface and no exposure to the Internet.”

Where can I find more information?

Go to zpesystems.com/services-delivery-platform to learn more about the Services Delivery Platform.

If you’re attending RSA Conference April 24-27, visit ZPE Systems at booth 4125 between north and south halls and ask for a demo.  Use this code for free RSA expo pass: 52EZPESYSXP

Zero Touch Deployment Cheat Sheet

A zero touch deployment cheat sheet is visualized as a literal cheat sheet used by a student during an exam

Zero touch deployment is meant to make admins’ lives easier by automatically provisioning new devices. However, many teams find the reality of zero touch deployment much more frustrating than manual device configurations. For example, zero touch deployment isn’t always compatible with legacy systems, can be difficult to scale, and is often error-prone and difficult to remotely troubleshoot. This post provides a “cheat sheet” of solutions to the most common zero touch deployment challenges to help organizations streamline their automatic device provisioning.

Zero touch deployment cheat sheet

Zero touch deployment – also known as zero touch provisioning (ZTP) – uses software scripts or definition files to automatically configure new devices. The goal is for a team to be able to ship a new-in-box device to a remote branch where a non-technical user can plug in the device’s power and network cables, at which point the device automatically downloads its configuration from a centralized repository via the branch DHCP server.

In practice, however, there are a variety of common issues that force admins to intervene in the “zero touch” deployment. This guide discusses these challenges and advises how to overcome them to achieve truly zero touch deployments.

Zero touch deployment challenge: The solution:
Legacy systems don’t have native support for zero touch Extending zero touch to legacy systems using a vendor-neutral platform
Deployment errors result in costly truck-rolls Recovering from errors remotely with Gen 3 out-of-band (OOB) management
Securing remote deployments causes firewall bottlenecks Moving security to the edge with Zero trust gateways and Secure Access Service Edge (SASE)
Automating deployments at scale increases management complexity Maintaining control through centralized, vendor-neutral orchestration with version control

Extend zero touch to legacy systems with a vendor-neutral platform

Challenge Solution

While many new systems and networking solutions support zero touch deployment, sometimes there’s still a need to repurpose or reconfigure legacy systems that don’t come with native ZTP support.

Pre-staging these devices before shipping them to the branch is a security risk because the system could be intercepted in transit; plus, they’re likely already deployed at remote sites and need to be reconfigured in place. Without a way to extend zero touch deployment capabilities to those legacy systems, companies often have to pay for admins to travel to remote branches, negating any cost savings they were hoping to gain from reusing older devices.

One way to extend zero touch to legacy systems is with a vendor-neutral management platform. For example, a vendor-neutral serial console switch with auto-sensing ports can connect to modern and legacy infrastructure solutions in a heterogeneous branch deployment so they can all be managed from a single place.

From that unified management platform, admins can write and deploy configuration scripts to connected devices, including legacy systems that don’t support zero touch. Technically, this isn’t zero touch deployment because the system doesn’t automatically download and run its configuration file, but it’s still a way to turn an on-site, manual process into one that’s remotely activated and mostly automated.

Recover from deployment errors with Gen 3 OOB management

Challenge Solution

A new branch deployment almost never goes completely according to plan, and this is especially true when teams are using zero touch for the first time, or aren’t completely comfortable with software-defined infrastructure and networking. In the best-case scenario, when there’s a configuration error, the zero touch deployment aborts, and an admin is able to correct the problem and restart the process.

However, sometimes the deployment hiccup causes the device to hang, freeze, or get stuck in a reboot cycle. Or, even worse, an unnoticed error in the configuration could allow the deployment to finish successfully but then go on to affect other production dependencies and bring the entire branch network down. Either way, organizations must again deal with the expenses involved in sending a tech out to troubleshoot and fix the problem.

The best way to ensure continuous access to remote infrastructure is with out-of-band (OOB) management. An OOB solution, such as a serial console or all-in-one branch gateway, connects to the management ports on infrastructure devices so admins can remotely monitor and control every device from a single place without IP addresses.

This creates a separate (out-of-band) network that’s dedicated to management and troubleshooting, making it possible for teams to remotely recover devices that have failed the zero touch deployment process or brought down production LAN dependencies. Plus, the OOB gateway uses independent, redundant network interfaces to ensure admins still have remote access even if the production WAN or ISP link goes down.

To ensure full OOB management coverage of a heterogenous, mixed-vendor environment, the out-of-band solution should be completely vendor-neutral. An open OOB device also supports integrations with third-party solutions for automation, orchestration, and security. This kind of out-of-band platform is known as Gen 3 OOB. Gen 3 OOB management ensures that teams can remotely recover from zero touch deployment errors no matter what device is affected or how the production network is impacted.

Secure remote deployments with zero trust gateways and SASE

Challenge Solution

Organizations need to secure all devices at all remote sites using consistent policies and security controls. However, for smaller branches and IoT sites, it usually isn’t cost-effective to deploy a security appliance in each location.

Plus, adding more firewalls also adds more management complexity. That means traffic is usually backhauled through the main data center firewall, creating bottlenecks and causing network latency for the entire enterprise.

Using zero trust gateways and cloud-based security services, companies can move security to the branch without the cost and complexity of additional firewalls. An all-in-one, zero trust gateway solution combines SD-WAN, gateway routing, and OOB management in a single device. It also supports zero trust authentication technologies like SAML 2.0 and 2FA. A zero trust gateway also needs to support network micro-segmentation, which will allow the use of highly specific security policies and targeted security controls. Plus, by enabling software-defined wide area networking (SD-WAN), a zero trust gateway facilitates the use of SASE.

Secure Access Service Edge (SASE) is a cloud-based service that combines several enterprise security solutions into a single platform. Zero trust gateways use SD-WAN’s intelligent routing capabilities to detect branch traffic that’s destined for the cloud or web. This traffic is directed through the SASE stack for firewall inspection and security policy application, allowing it to bypass the main security appliance entirely. SASE helps reduce the load on the enterprise firewall, reducing bottlenecks and improving performance without sacrificing security.

Scale zero touch deployments with centralized orchestration

Challenge Solution
Zero touch deployments occur (at least in theory) without any admin intervention, but they still need to be monitored for failures. Keeping track of a handful of automatic deployments may seem easy enough, but as the number and frequency increases, it becomes more challenging. This is especially true when companies kick off large-scale expansions, deploying dozens of devices at once, all of which could be plugged in at any time to begin the automated provisioning process. Plus, different devices need different configuration files, and admins need a way to work together without overwriting each other’s code or duplicating each other’s efforts. A vendor-neutral orchestration platform provides a central hub for network and infrastructure automation across the entire enterprise. This platform uses the serial consoles and OOB gateways in each remote location to gain control over all the connected devices, so network teams can monitor and deploy all their zero touch configurations from one place. An orchestration platform is the single source of truth for all automation, so it needs to support version control. This ensures that admins can see who created or changed a configuration file and revert to a previous version when there’s a mistake.

Simplifying zero touch deployment with Nodegrid

Zero touch deployment can be a hassle, but using vendor-neutral management systems, Gen 3 OOB management, zero trust gateways, and centralized orchestration can help organizations overcome the most common hurdles. For example, a vendor-neutral Nodegrid branch gateway deployed at each remote site helps you extend automation to legacy systems, provides fast and reliable out-of-band access to recover from issues, enables zero trust security & SASE, and gives you unified orchestration through the Nodegrid Manager (on premises) and ZPE Cloud software.

Ready to learn more about zero touch deployment?

Nodegrid has a solution for every zero touch deployment challenge. Schedule a demo to see how Nodegrid’s vendor-neutral platform can simplify zero touch deployment for your enterprise.

Contact Us

3 Gaps That Will Leave IT Teams Scrambling

Today’s IT teams must maintain a growing infrastructure of on-prem and cloud solutions. These range from physical routers, out-of-band devices, and firewalls, to Zero Trust Security solutions, micro-segmentation tools, and network automation integrations. Despite an abundance of physical and virtual solutions meant to help keep digital services online, many organizations face an overwhelming number of tasks just to sustain everyday operations. 

With the rising risk of recession, organizations will be forced to cut back on resources including staff, training, and tools. This will only worsen the existing challenges teams face in their efforts to maintain their distributed infrastructure. 

In this blog, we’ll explore three gaps that will leave IT teams scrambling and show you several practical approaches to cope during recession. 

Gap 1: Lack of staff

IT teams have been historically understaffed, and most people can remember at least one significant tech worker hiring campaign from the past decade. Today’s CIOs may in fact be facing the biggest talent gap since 2008. For example, in the cybersecurity sector alone, the 2021 (ISC)2 Cybersecurity Workforce Study reported that despite adding 700,000 cybersecurity professionals to the workforce in 2021, there’s still a gap of more than 2.7 million workers globally, 377,000 of which are needed in the United States. 

Trained staff are a must for managing an organization’s distributed sites, especially as team silos disappear and workers are required to have a breadth of skills. Business leaders increasingly need people who are proficient in networking and programming, so they can maintain normal operations while progressing their digital transformation initiatives such as hyperautomation. It’s a challenge that often comes down to hiring new talent or increasing the skills of existing employees, and both of these approaches require plenty of time and money. 

This issue will only worsen with the coming recession as companies begin to tighten their belts and slash budgets. Major brands have already shed thousands of workers this year, leaving IT teams to make due with existing staff numbers or even reduced headcounts. In the simplest terms, the coming recession will leave companies much less willing or able to invest in staff. 

Gap 2: Lack of tools to reduce workloads

Today’s infrastructure incorporates solutions from many different vendors, but the problem is these often come with their own unique tools that are meant to serve only a specific function. Managing SD-WAN, SASE, ZTNA, orchestration, and out-of-band solutions means jumping between disparate tools, many of which lack integration with one another. This complexity leaves operational teams stuck in a reactionary break/fix posture trying to climb mountains of never-ending support tickets. 

To address this challenge, many Big Tech companies empower their IT teams through digital transformation initiatives, such as using automation to achieve a proactive approach. But this requires additional investments in upskilling staff and acquiring adequate automation infrastructure/tools. For many organizations, a lack of money and resources makes this difficult during normal economic conditions, and will only become exacerbated with the coming recession. IT teams will continue scrambling with their inflated workloads.

Gap 3: Lack of trust in automation

Automation can greatly reduce the risk of human error (and subsequent outages) by handling simple workloads, such as device provisioning and firmware updates. However, companies that do have the resources to implement automation also recognize its limitations. Automation solutions that aren’t optimized leave IT teams with mundane tasks like managing, scheduling, and restarting bots. But to even reach this level of automation requires training staff who typically don’t have a background in programming or development. 

These teams will be unfamiliar with NetOps/DevOps concepts. In order to develop essential automation practices, these employees will need to learn through trial and error. This is a problem because most organizations lack the proper automation infrastructure and tools that allow their IT teams to recover from mistakes. Operational teams in charge of keeping infrastructure running often fear automation for this exact reason — if they make one error, there’s the potential that it will bring down the network, lead to unhappy customers, and cost them their job. 


BlueprintPDF

Close these gaps with the Network Automation Blueprint

You can close these gaps for good using out-of-band, jump boxes, and tools you already have. After years of working directly with tech giants, we’ve created a best practice reference architecture any company can use to automate their network. This Network Automation Blueprint has been proven by global enterprises to increase capabilities and reduce workloads through trustworthy automation.

Simplifying Retail Network Management

Retail network management is visualized with interconnecting icons of networked retail services displayed in front of a retail warehouse

Fast and reliable networks are critical to the success of retail operations. Without network access, stores can’t process payments, handle customer data, or update inventory, which makes outages highly disruptive. According to a recent study, downtime could cost over $300,000 per hour in lost business, which is why it’s crucial that admins have the necessary tools to effectively monitor, manage, and optimize retail networks. This blog discusses some of the specific challenges involved in retail network management and how the right edge gateway solution can help overcome these difficulties.

Retail network management challenges

Managing a retail network comes with unique challenges, especially as the size and geographical distribution of the organization grows. Examples of these challenges include:

  1. Extending fast, reliable connectivity to the entire store for payment processing machines, inventory scanners, and other crucial devices. This is especially challenging in big box stores and other locations with large footprints as well as service-based chains with mechanics’ bays, drive-thrus, and other outdoor or semi-outdoor devices.
    .
  2. Maintaining optimal environmental conditions for networking equipment that’s often installed in closets, storage rooms, warehouses, and other out-of-the-way locations. The priority is typically to keep these devices hidden from customers, so they’re kept in areas that may not be climate controlled and may not have staff physically checking them every day. This increases the risk of environmental issues (like heat and humidity) causing a device failure and means no one is likely to notice the issue until it’s too late.
    .
  3. Remotely troubleshooting and recovering from issues without any on-site technicians. If the ISP connection, WAN, or LAN go down, there’s often no way to remotely access on-site equipment to diagnose and fix the problem. That means network outages require truck rolls to solve, with stores losing money waiting for technicians to travel on-site.
    .
  4. Efficiently monitoring and managing a distributed retail network architecture made up of many different network solutions and platforms. The lack of centralized management increases the risk of human error and makes it difficult to preemptively address potential problems or optimize the speed and performance of the network.

Retail network management teams need a robust solution that addresses these particular challenges. For example, they need small and powerful network devices that use centralized management to reduce management complexity. They also need a way to monitor environmental conditions and recover from outages without having to be on-site.

Simplifying retail network management

Now, let’s discuss how a robust branch gateway solution can help organizations address these challenges.

Compact, all-in-one networking

The layout of a retail store is carefully planned to ensure an optimal experience for customers, which means networking devices need to be as unobtrusive as possible. The ideal branch gateway for retail is compact and combines multiple networking functions, reducing the number of devices that need to be installed. Retail notoriously operates on a small profit margin, so the branch gateway also needs to be affordable without sacrificing performance.

Environmental monitoring

Environmental monitoring sensors collect data on conditions like temperature, humidity, and air quality in the location where networking equipment is installed. These sensors typically connect to the retail branch gateway via USB and report back to the management platform, giving admins the ability to remotely monitor the environment. This is crucial when most retail networks are managed by admins in a centralized office which may be hundreds or thousands of miles away from the stores themselves. Environmental monitoring allows them to identify and resolve potential problems before they cause device failures and outages. For example, if environmental sensors detect high temperatures, admins can get on-site personnel to turn up the air conditioning or call in an HVAC repair before devices overheat and bring down the network.

Out-of-band (OOB) management

Out-of-band (OOB) management uses redundant network interfaces (often cellular) to provide an alternative path to remote infrastructure. A branch gateway with OOB allows admins to remotely connect to devices in the store without relying on an IP address from the LAN, which means they’ll always have access even if the production network goes down. Without OOB management, the retail location goes offline for hours or even days waiting for a technician to arrive on-site, diagnose, and repair the issue. With OOB, admins can remotely access the infrastructure to restore services, often so fast that customers don’t even notice. That means they can remotely recover from more outages without truck rolls, saving time and money.

Vendor-neutral orchestration

A vendor-neutral branch gateway can interface with all the other devices in a retail network infrastructure, even if they’re from a different vendor’s ecosystem. This gives admins a single platform from which to monitor and manage every device in the store. Even better is when all of the branch gateways in the entire retail network architecture hook into a single, centralized, cloud-based orchestration platform. Admins can then monitor, control, and optimize network infrastructure for all the retail locations from one place for ultimate efficiency.

In addition, a vendor-neutral retail network management platform enables the use of third-party automation solutions. Automation reduces the risk of human error and makes it easier for teams to effectively manage and optimize even complex retail network architectures.

Retail network management with Nodegrid

Compact, all-in-one branch gateways like Nodegrid use environmental monitoring, OOB management, and vendor-neutral platforms to simplify retail network management. The Nodegrid Mini SR, for example, is an inexpensive retail branch gateway that’s roughly the size of an iPhone, so you can easily deploy them anywhere in your store without disrupting the customer experience. Despite its small size and low price point, the MSR still delivers Gen 3 OOB management capabilities while supporting Nodegrid environmental monitoring sensors and third-party automation. The Nodegrid platform is also completely vendor-neutral, giving retail network admins a single pane of glass from which to monitor, orchestrate, and optimize the entire distributed network architecture.

Ready to learn more about Nodegrid?

To learn more about about simplifying retail network management with Nodegrid, click here to download the Mini SR datasheet, or contact ZPE Systems today.

Contact Us

Network Automation Tools To Offset the Tech Talent Shortage

network automation tools
As enterprise networks grow more complex, there’s a rising need for highly-specialized engineers to implement and maintain these complicated architectures. However, due to the Covid-19 pandemic, a global recession, and other world events beyond an organization’s control, it can be very difficult to recruit and retain these specialists. In fact, many companies are currently relying on smaller IT teams than usual to manage their vital network infrastructure. According to Gartner research, the tech talent shortage is one of the biggest barriers to the adoption of emerging technology like network automation.

However, network automation tools can actually help understaffed organizations ensure the continued availability and performance of enterprise networks by streamlining workflows and reducing manual intervention. In this blog, we’ll discuss how four different types of network automation tools can be used to solve major problems caused by the tech talent shortage.

Problem Solution
You lack the staff required to efficiently deploy, monitor, and manage network configurations. Automated network configuration management solutions like SolarWinds Network Configuration Manager (NCM) and Micro Focus Network Automation Software.
You need to extend DevOps automation to networking without purchasing additional solutions or hiring network automation experts. DevOps configuration management solutions that can be used for server and network automation like RedHat Ansible and Puppet.
You want to improve network reliability and performance while reducing management complexity. Software-defined networking (SDN) and software-defined wide area networking (SD-WAN) solutions like Palo Alto Prisma and Cisco Meraki.
You lack full-coverage network security, so you’re unsure where your vulnerabilities are or how efficiently you can respond to incidents. Network security automation solutions like Palo Alto’s Next-Generation Firewall (NGFW) and Datadog AIOps security and monitoring.


To learn more about using automation technology to ensure network resilience, click here to download the Network Automation Blueprint from ZPE Systems.


Network automation tools to offset the tech talent shortage

The following categories of network automation tools are designed to simplify network management workflows to ensure optimal performance and 24/7 availability.

Automated network configuration management

Network configuration management refers to the ongoing process of creating, deploying, and maintaining configurations for network devices and logic. Some of the tasks involved in network configuration management include device discovery, provisioning, and software and firmware updates. In addition, network configurations are monitored to ensure they don’t drift away from documented standards (configuration shift), and if needed, unauthorized changes are rolled back. This reduces the risk that an undocumented configuration tweak will introduce an unnoticed security vulnerability (such as the recent Fortinet authentication bypass exploit) and ensures consistent quality across the entire network architecture.

However, manual network configuration management is complicated and time-consuming, especially when so many network operations teams are overworked and understaffed. An automated network configuration management solution handles many of these tasks without the need for human intervention. Admins can create network configuration policies and playbooks which are used to automatically deploy new devices and update network dependencies, saving time and reducing human error. In addition, automated configuration management uses these policies to continuously monitor for and correct configuration drift. In the case of the Fortinet CVE, for example, automatic configuration management could have helped teams instantly roll back to the last known good config to close the vulnerability.

Examples of network automation tools for network configuration management include SolarWinds Network Configuration Manager and Micro Focus Network Automation.

DevOps IaC configuration management

Many organizations have adopted the DevOps methodology, which seeks to dissolve the barriers between the software development and IT operations teams to improve efficiency. On the Ops side, this often involves a practice called IaC, or Infrastructure as Code. IaC uses software code and machine-readable definition files to automatically provision servers and manage configurations. IaC enables Ops teams to spin up resources at the velocity required for fast-paced DevOps software projects. It also means that infrastructure configuration code can be stored, managed, and deployed from the same platform as software code, facilitating easy collaboration between developers and sysadmins.

With the recession forcing many IT teams to downsize, organizations are looking for ways to extend the efficiency provided by DevOps automation tools to the networking side of the house without purchasing additional solutions. Plus, many network admins lack the expertise required to operate network automation solutions, and the tech talent shortage makes recruiting such specialized engineers difficult. Luckily, some IaC configuration management tools like RedHat Ansible and Puppet can also be used for network configurations, which helps teams automate without any special programming skills.

That also means admins can deploy, monitor, and manage configurations for network devices and systems across the entire architecture from a single platform, saving money and reducing operational complexity. This convergence of DevOps and network management is known as NetDevOps or NetOps, and it’s empowering organizations to improve efficiency even during the recession and talent shortage.

Software-defined networking and SD-WAN

Enterprise networks are typically highly distributed and very complex. An organization could have 500 branch offices around the world, each of which uses slightly different networking hardware and software solutions. Each of these vendor solutions might have its own management platform for admins to configure, manage, and continuously monitor. Things grow more challenging when an organization uses a hybrid cloud infrastructure, which requires WAN (wide area networking) orchestration across multiple public and private clouds. This complexity makes it challenging for overworked network administrators to maintain optimal performance and 24/7 availability.

Software-defined networking (SDN) and software-defined wide area networking (SD-WAN) help to reduce the complexity of enterprise networks by abstracting network configurations and workflows as software code that’s decoupled from the underlying hardware. Codifying network configurations makes it easier to use technology like automated configuration management, which reduces the burden on overworked admins and reduces human error. SDN and SD-WAN also facilitate the use of centralized network orchestration platforms, which give admins a single pane of glass from which to control the entire network architecture.

This holistic coverage makes it possible for small teams to efficiently monitor and manage large, complex networks, reducing the risk of fatigue, human error, or negligence affecting performance. Plus, SDN and SD-WAN solutions employ automation to continuously monitor and adjust routing configurations as needed to ensure optimal performance. That means these solutions are often able to detect and remediate issues with latency and site availability much faster than a human admin could, ensuring optimal performance and reliability.

Examples of SDN and SD-WAN solutions include Cisco Meraki SDN and Palo Alto Prisma SD-WAN.

Network security automation

With the quantity, sophistication, and cost of cybersecurity attacks rising every year, network security is more important than ever. According to the Sophos State of Ransomware 2022 survey, 66% of organizations were hit by ransomware, a massive increase from 2020 in which only 37% of organizations were attacked.

However, the tech talent shortage and ongoing recession have left many organizations with gaps that increase both the risk that a breach will occur and the time it will take to recover. For example, IBM estimated in 2021 that unpatched vulnerabilities accounted for at least one-third of all data breaches. However, staying on top of patch management for large, diverse, and distributed network infrastructures is difficult when teams are overworked and understaffed.

Plus, when networking and security teams are spread so thin, it can take them much longer to detect a breach that has already occurred, even if the hacker is actively exfiltrating data or changing system configurations. Remediation is also slowed down by the need to manually investigate logs, isolate affected systems, and implement fixes.

Network security automation can help bridge these gaps by reducing the need for human analysts to perform the more tedious and repetitive – but highly vital – tasks involved in ongoing cybersecurity management. Automated security solutions use technology like AIOps and machine learning to manage software and firmware updates, analyze network traffic for threats, and even perform remediation steps like quarantining infected systems and blocking compromised accounts.

Popular examples of network security automation tools include Palo Alto Network’s Next Generation Firewall (NGFW) and Datadog AIOps Security and Monitoring.

Using a vendor-neutral platform to deploy network automation tools

The goal of automation is to make it easier for network admins to maintain and optimize the enterprise network. However, if admins need to learn, configure, deploy, and manage a bunch of additional automation solutions, you could end up increasing the complexity of their jobs rather than reducing it.

The Nodegrid platform can help by directly hosting all of the network automation tools listed above, reducing the need for additional hardware to manage. Deploying Nodegrid boxes in all your data centers and remote sites gives you the ability to extend automation to every corner of your network and manage it all from behind a single pane of glass. Hosting your network automation on a vendor-neutral platform like Nodegrid gives your team an easy way to orchestrate automated workflows across your entire enterprise architecture.

Network automation tools help to bridge the gaps caused by the tech talent shortage, ensuring the reliability and resilience of enterprise networks. To get step-by-step instructions for how to implement the network automation solutions mentioned above, click here to download the Network Automation Blueprint from ZPE Systems.

Ready to learn more?

To learn more about deploying network automation tools with Nodegrid, contact ZPE Systems today.

Contact Us