Providing Out-of-Band Connectivity to Mission-Critical IT Resources

Why You Need an Out-of-Band Cybersecurity Platform
out of band cyber security
As enterprise networks continue to grow in size and complexity, many organizations struggle to defend their expanding attack surface. The cost of failure also continues to grow – according to IBM’s 2022 Cost of a Data Breach report, the average cost of a successful ransomware attack reached $4.54 million. Koroush Saraf, VP of Product Management at ZPE Systems, identified the top five cybersecurity gaps that must be closed to achieve holistic cybersecurity, which include:

  • Unnecessary exposure of management ports
  • Credential theft
  • Unpatched infrastructure
  • Inability to deploy the right security tools
  • Human error

Closing these gaps requires a three-pronged approach – out-of-band infrastructure, an open platform from which to deploy and manage security tools, and end-to-end automation (aka, hyperautomation). In this blog, we’ll explain how an out-of-band cybersecurity platform combines these three key features into a single, holistic network security solution. Want to see an out-of-band cybersecurity platform in action? Request a free demo of the Nodegrid solution.

Why you need an out-of-band cybersecurity platform

An out-of-band (OOB) cybersecurity platform provides a single, unified interface from which to:

  • View and manage network infrastructure
  • Deploy and control all of the various security policies and applications needed to protect that infrastructure, and
  • Orchestrate network, infrastructure, and security automation.

This platform resides and operates on an out-of-band network running parallel to the production network, which ensures 24/7 availability even if there’s a LAN failure or ISP outage. All network, infrastructure, and security management occur OOB, which prevents resource-intensive orchestration workflows from negatively impacting performance. This vendor-neutral, automation-friendly, out-of-band approach to cybersecurity helps you in several areas.

Reduce your attack surface

The management ports on devices like servers and switches are frequently targeted by cybercriminals because they can be used to gain access to valuable data and resources on the production network. With an out-of-band cybersecurity platform, all infrastructure and network management occurs on the OOB network, which means you no longer need to expose management ports on the production network. Isolating management and orchestration workflows to the OOB network helps reduce the attack surface by making it much more difficult for attackers to find and access those open management ports. Vendor-neutral OOB cybersecurity platforms can also help companies reduce the number of individual devices and solutions on their network, which decreases the attack surface even more. An open OOB serial console like the Nodegrid Serial Console Plus (NSCP) can host other vendors’ applications and solutions and seamlessly integrate them into the cybersecurity platform, so there are fewer devices to patch and defend, and fewer vectors through which cybercriminals can attack.

Understand your attack surface

A centralized, vendor-neutral cybersecurity platform is able to dig its hooks into every component of an enterprise network, providing a complete overview of the entire architecture. With this holistic view, security analysts gain a better understanding of the attack surface and what’s needed to protect each vulnerability. For example, a cybersecurity platform can provide information about software versioning to help with security patch management or help identify which ports are open in various applications and why. Armed with this knowledge, an organization can then deploy granular policies, tools, and controls that are custom-tailored to provide the best defense.

Mitigate human error

Even the best network engineer, working in the ideal environment, will occasionally make mistakes. For example, a recent FAA outage that delayed thousands of flights was caused by a contractor mistakenly deleting some files. And unfortunately, the combination of a tech industry recession and a tech talent gap has meant that many IT teams are overworked and understaffed – far from an ideal situation. Human error is a leading cause of successful breaches, so network automation can reduce human error by letting scripts and playbooks handle many of the tedious and repetitive workflows involved in network management. An out-of-band cybersecurity platform can host or integrate with all the leading automation solutions and scripting languages, giving overworked admins the freedom to use the tools they’re most comfortable with. The centralized platform consolidates automated workflows in a single place for streamlined deployments and efficient management. Organizations can even achieve hyperautomation – automating every task and workflow across the network and security architecture – using the cybersecurity platform as an orchestration hub. This empowers understaffed teams to optimize network performance and security while reducing manual interventions, mitigating the risk of human error.

Ensure 24/7 coverage and availability

An out-of-band cybersecurity platform uses a dedicated network interface – such as a 5G cellular modem – to ensure continuous management access even when there’s an outage on the production network. That means admins have 24/7 access to the cybersecurity platform itself, as well as the devices and systems being protected by that platform. And, crucially, all of the security policies and tools will continue to protect production network infrastructure during that downtime. This continuous availability makes it possible for IT teams to remotely recover from device and network failures without the need for costly and time-consuming truck rolls. Or, in the event of a successful attack such as ransomware, admins can conduct recovery operations on the OOB network, creating an isolated recovery environment (IRE) that’s inaccessible to attackers.

Why choose Nodegrid as your OOB cybersecurity platform

An out-of-band cybersecurity platform uses OOB infrastructure, vendor-neutral management software, and end-to-end automation to provide holistic network security. The Nodegrid platform from ZPE Systems delivers all of this functionality in a single package. Using Gen 3 out-of-band serial consoles and integrated services routers, Nodegrid can dig its orchestration hooks into every system, device, and solution in your infrastructure for complete control. Nodegrid can host or integrate with your choice of automation tools (such as Chef, Ansible, and Puppet) and security applications (such as NGFWs and SSE) for seamless and unified network security management. Plus, with fast and reliable OOB network interface options – including 5G cellular and Wi-Fi – you can maintain 24/7 security coverage and management availability.

Ready to learn more?

To learn more about the Nodegrid out-of-band cybersecurity platform, contact ZPE Systems today. Contact Us
Building an IoT Device Management System

shutterstock_1350962531(1)(1)

Internet of Things (IoT) devices are integral components of many modern businesses. In 2020, there were almost 9 billion active IoT devices—that number is predicted to exceed 25 billion by 2030. Effectively deploying, monitoring, and managing all of these devices in an enterprise environment requires powerful, centralized orchestration using an IoT device management system. This post discusses the best practices and key considerations to keep in mind when planning, designing, and building your IoT device management system.

What is an IoT device management system?

An IoT device management system provides a unified platform from which to manage all of the IoT devices in use by an organization. Many of these devices operate with little-to-no human interaction, in remote sites that may be difficult or even dangerous to access for routine maintenance. For example, IoT sensors are used inside oil pipelines to monitor crucial metrics like flow, pressure, and temperature. In addition, one organization may need to employ dozens or hundreds of different IoT devices to handle specific functions. These devices often come from different vendors, with separate management platforms, patch schedules, and configuration schemes. This results in a lot of management complexity for the IT teams responsible for provisioning, maintaining, and troubleshooting all of these devices, creating the need for an IoT device management system. The goal of such a solution is to bring all of the tasks involved in IoT device management under one roof, including:


  • → Onboarding:
    Bringing new IoT devices onto the network with the proper credentials and security policies
  • → Configuration: Provisioning new IoT devices with the necessary settings
  • → Maintenance: Updating firmware and applying security patches in a timely manner
  • → Security: Applying enterprise security policies to all IoT devices on the network
  • → Diagnostics: Collecting and analyzing logs to help identify and fix IoT device issues
  • → End-of-life management: Decommissioning EOL devices so they don’t create a security risk by remaining online and unpatched
Nodegrid is a vendor-agnostic IoT device management system that enables end-to-end automation and reliable OOB management access. To see Nodegrid in action, schedule a free demo.

Best practices for building an IoT device management system

Here are some best practices and key considerations to keep in mind when planning, designing, and building your IoT device management system.

Avoid closed ecosystems

There are off-the-shelf software solutions for IoT device management that are designed to work within a single vendor’s ecosystem. While they may offer some support for third-party devices, they generally work best if you’re already operating within that vendor’s environment. For example, AWS IoT Device Management works with third-party IoT devices but requires an existing AWS infrastructure to use it effectively. These types of solutions will usually include a library of features and supported integrations, but you may not be able to integrate your preferred scripting languages, open-source tools, or other third-party components. A vendor-neutral, or vendor-agnostic, IoT device management system does not suffer from these limitations. In addition to the ability to hook into multi-vendor IoT devices, these platforms also allow you to use your choice of third-party software and scripts. A vendor-neutral solution gives you the freedom to build a truly bespoke IoT device management system that makes use of your team’s existing skills, preferred tools, and custom innovations.

Ensure 24/7 remote management access

One of the benefits of IoT devices is they can be deployed anywhere. However, maintaining continuous access to devices in remote and hard-to-reach environments can prove challenging. Natural disasters, LAN failures, ISP outages, political instability, and global pandemics can all occur with little-to-no warning, leaving organizations cut off from their critical remote IoT devices and infrastructure. Out-of-band (OOB) management solves this problem by providing an alternative path to remote network infrastructure. For example, an IoT device management system can use OOB serial consoles to create a management network that’s dedicated to the orchestration, maintenance, and troubleshooting of production network equipment. These serial consoles have multiple redundant network interfaces (e.g., 5G cellular, Fiber, and Wi-Fi) so admins can remotely access the IoT device management system even when the remote site loses its main internet connection. This ensures that organizations can recover from remote network failures faster, continue internal operations during ISP outages, and maintain continuous access to their IoT devices.

Protect IoT infrastructure with Zero Trust Security

IoT device management systems help ensure the security of remote IoT devices by simplifying tasks like firmware updates and vulnerability patch deployment. However, the IoT device management platform itself is a potential target for malicious actors hoping to gain complete control over an organization’s IoT infrastructure. That’s why organizations must protect their IoT device management system using Zero Trust Security. Zero Trust Security follows the principle of “never trust, always verify” by requiring all users, systems, and devices to continuously prove their trustworthiness as they access the network and enterprise resources. It also requires the consistent application of enterprise security policies and controls to every system and application that connects to the network, including the IoT device management system. That means, for example, that you should use technology such as two-factor authentication (2FA) and identity and access management (IAM) to control access and prevent compromised accounts from gaining control.

  • ☆ Bonus tip: Zero Trust Security is easier to apply if you use a vendor-neutral IoT device management system that supports integrations with third-party security solutions like next-generation firewalls (NGFWs) and Secure Access Service Edge (SASE). This will also ensure that Zero Trust controls are in place to protect the OOB management network from unauthorized access.

However, it’s important to acknowledge that there’s currently no way to completely prevent a breach from occurring. According to the Sophos State of Ransomware 2022 survey, 66% of organizations were hit by ransomware in 2021 alone, and that number is only expected to trend upwards over time. That’s why another critical aspect of Zero Trust Security for IoT device management is building a resilient network architecture with automation tools that reduce the MTTR (mean time to recovery) when—and not if—a breach occurs. Learn more about how to implement such an architecture with ZPE’s network automation blueprint.

Building an IoT device management system with Nodegrid

An IoT device management system is meant to simplify and streamline the management of remote, hard-to-reach, and complex IoT devices and infrastructure. Vendor-neutral systems allow you to customize your platform with the third-party tools and solutions that work best for your team and your organization’s use case. Out-of-band (OOB) management ensures that IT teams have reliable, 24/7 access to remote IoT systems. Finally, Zero Trust Security protects the IoT device management system and all connected devices from malicious attacks. The Nodegrid platform from ZPE Systems is a completely vendor-agnostic IoT device management system supported by Gen 3 OOB serial consoles like the Nodegrid Serial Console Plus (NSCP) and all-in-one edge gateway routers like the Mini Services Router (MSR). Nodegrid supports integrations with your choice of custom scripts, automation tools, and security solutions so you can build a bespoke IoT device management system that addresses your organization’s unique challenges and use cases.

Ready to learn more about the Nodegrid IoT device management system?

Contact ZPE Systems today to learn more about the Nodegrid IoT device management system, contact ZPE Systems today. Contact Us
What To Look for In a Cloud Edge Gateway Solution

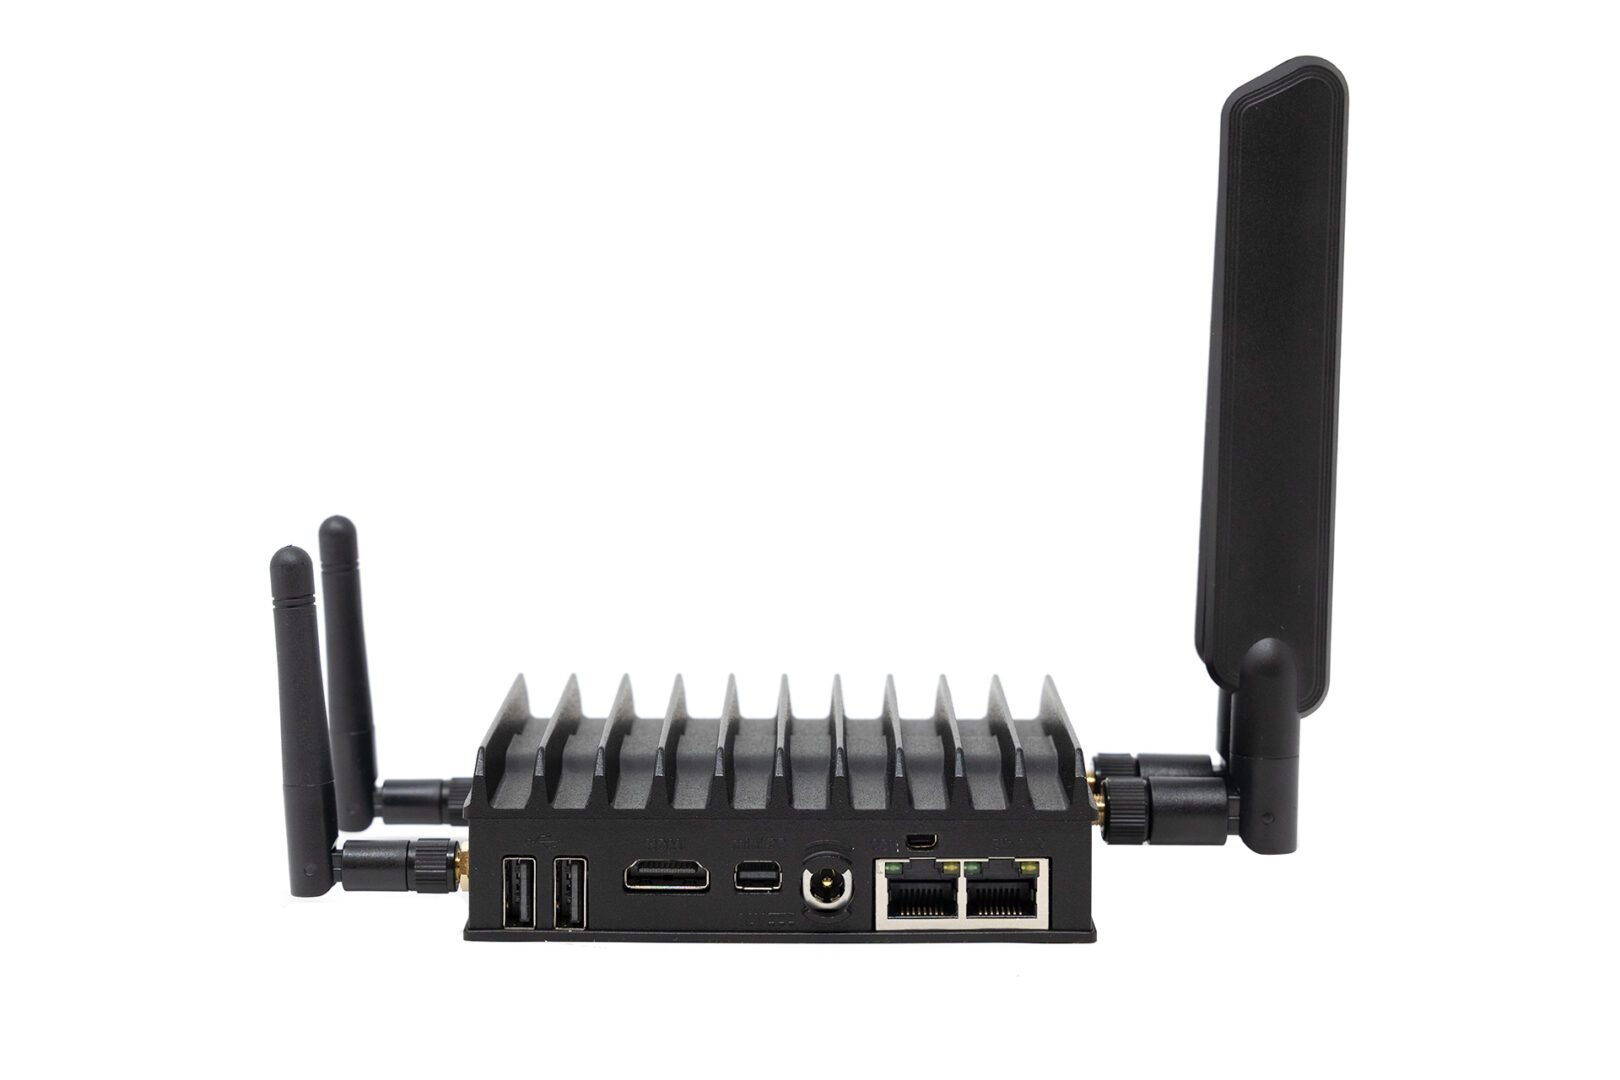
Mini-SR-Rear
Gartner predicts that by 2029 more than 15 billion IoT devices will connect to enterprise infrastructure. Many of these devices will operate outside of the centralized enterprise network, in satellite offices, manufacturing facilities, retail stores, and other remote locations. These remote – or edge – IoT devices need a secure and reliable way to connect to cloud resources and applications.

A cloud edge gateway is a hardware or software solution used to connect edge devices to the cloud. Some edge gateways are also routers that connect the edge location’s network to the WAN (wide area network) or SD-WAN (software-defined wide area network). In addition, many cloud edge gateway solutions also provide management access to connected devices, so administrators can remotely monitor and control edge infrastructure.

Some popular use cases for cloud edge gateways include:

  • Retail stores: Cloud edge gateways give retail stores a fast and secure connection for POS (point of sale) terminals, credit card readers, and security cameras.
  • Remote health facilities: Hospitals and clinics in remote areas use cloud edge gateways to securely and reliably transmit health data from IoT medical devices.
  • Police/emergency response vehicles: Cloud edge gateways enable secure data transmission from police, fire, and EMS vehicles to cloud applications.

In this blog post, we’ll discuss the key characteristics and components of a robust, secure, and reliable cloud edge gateway solution.

What to look for in a cloud edge gateway

Vendor neutrality

In a decentralized network with many remote locations, network solutions like edge gateways are often chosen based on which vendor offered the best deal or had the most compelling sales pitch at the time a new site was opening. This creates a heterogeneous network architecture, with each vendor offering their own platform from which to monitor and manage their solutions. With so many platforms to learn and keep track of, it becomes very challenging for admins to keep networks operating at peak efficiency.

A vendor-neutral cloud edge gateway solution reduces management complexity by seamlessly integrating with the existing edge infrastructure. For example, Nodegrid Services Routers can run other vendors’ software, so admins can keep using the management platform they’re most comfortable with. Or, admins can use the ZPE Cloud network orchestration platform to manage any other vendor solution that’s connected to a Nodegrid device.

Vendor-neutral cloud edge gateways give organizations the freedom to continue expanding to new locations without worrying about integration issues. Vendor neutrality also reduces headaches for network administrators so they can focus on improving efficiency and optimizing performance.

High-speed cellular failover and out-of-band management

Edge IoT devices are used for critical operations, which means they need 24/7 connectivity. Cellular failover provides a secondary internet connection that’s independent of wired network infrastructure. A cloud edge gateway with cellular failover ensures that IoT devices have uninterrupted access to the cloud even if the primary ISP connection goes down. The best solution supports high-speed 4G/5G cellular to reduce the performance impact of failover, as well as providing dual-SIM slots for redundancy.

In addition, admins need management access to edge infrastructure and IoT devices that are independent of both the WAN and the LAN (local area network), so if something like a firmware update causes the local network to go down, they can repair the issue without needing to dispatch an expensive truck roll. Out-of-band (OOB) management uses a secondary network interface (like a 5G cellular SIM) to create an OOB network that’s dedicated to management and troubleshooting. An edge gateway with OOB management ensures that admins have 24/7 high-speed access to remote infrastructure so they can recover from problems faster and reduce downtime.

Secure hardware and software

The security threats to enterprise networks are ceaseless and growing more sophisticated by the day. Many IoT devices and edge locations operate with little-to-no human intervention, which means breaches could go undetected for a long time. In addition, it can be difficult to stay on top of patch schedules or remotely install security updates on so many devices in so many locations, which can leave edge networks vulnerable to attack.

The right cloud edge gateway comes with robust hardware security features like BIOS protection, encrypted disks, and geofencing that prevent malicious actors from using a stolen gateway to hijack edge networks. Its management software should also include Zero Trust security features like SAML 2.0 integration, selectable cryptographic protocols and cipher suite levels, and two-factor authentication (2FA). With a vendor-neutral solution like Nodegrid, admins can even use the cloud edge gateway to push out security updates to connected devices using the ZPE Cloud management platform.

Automation support

It’s growing more difficult for people to simultaneously manage the complex network infrastructures required for modern business operations while ensuring peak performance and 24/7 availability. Network automation solutions help decrease the burden on overworked admins and can improve the performance and reliability of edge networks.

Many edge gateways include some automation features as part of their management software. However, these tend to be limited to baked-in workflows, meaning admins may not be able to use custom scripts or third-party playbooks. The best cloud edge gateway has vendor-neutral automation support so admins can use their choice of automation solutions. For example, Nodegrid edge gateways can directly host automation playbooks from all the major platforms including Ansible and Puppet. Nodegrid also supports custom scripting and third-party integrations for even greater flexibility.

The best cloud edge gateway solution is vendor-neutral, uses high-speed cellular for failover and OOB management, follows Zero Trust best practices to keep the infrastructure secure, and supports all of the major automation tools and scripting languages. With the edge gateway market still being somewhat new, there’s really only one solution that checks all these boxes: the Nodegrid family of cloud edge gateway routers.

Why choose the Nodegrid cloud edge gateway solution?

There are six Nodegrid Services Router models to choose from based on your deployment size, networking requirements, and use case. For example, the Mini SR delivers versatile edge networking capabilities in a device approximately the size of an iPhone, which is perfect for mobile emergency response units or retail branches where space is at a premium.

For larger deployments, such as an edge compute data center or Smart Building system, the Net SR provides a modular solution with options for additional serial console ports, disk space, compute, PoE, and more.

Nodegrid’s vendor-neutral platform is extensible and capable of directly hosting other vendor solutions for automation, security, and other networking functions. Cellular failover and high-speed OOB are delivered via dual- or quad-SIM cellular slots with 5G/4G LTE support. Nodegrid devices are protected by secure hardware features, SAML 2.0 and 2FA support, and advanced authentication, plus the OS is kept up-to-date with frequent patches. Nodegrid is also the only cloud edge gateway with full support for all the top automation and IaC (infrastructure as code) solutions, including Ansible, Chef, and Puppet.

Ready to learn more about the Nodegrid cloud edge gateway solution?

Contact ZPE Systems today to learn more about the Nodegrid cloud edge gateway solution.

Contact Us

Key Automation Infrastructure Components That Enable End-to-End Network Automation

A resilient network containing automation infrastructure components and concepts overlays a busy industrial plant that uses OT automation.

As inflation rises, new business declines, and another COVID-19 surge looms on the horizon, many organizations are bracing for a recession. CIOs and IT managers are having to do more with less—less staff, less budget for upgrades and repairs, and less access to on-site infrastructure. Despite these restrictions, they still need to ensure the 24/7 availability and optimal performance of enterprise network resources as any amount of downtime could severely impact business revenue.

The ability to continue providing digital services in less-than-ideal situations is known as network resiliency. Network automation is a key tool for ensuring resiliency during staffing shortages and lockdowns, and a network automation framework provides the tools and methodologies needed to create a fully-automated network infrastructure.

The four building blocks of a resilient network automation framework include:

  1. IT/OT production infrastructure
  2. Automation infrastructure
  3. Orchestration infrastructure
  4. AIOps

We’ve previously discussed the role of IT/OT production infrastructure in network automation and how an IT/OT convergence strategy accelerates network automation. In this post, we’ll describe the automation infrastructure components that enable end-to-end network automation. Future blogs will explain how the orchestration infrastructure layer and AIOps layer build upon these components to ensure business resiliency.

What is automation infrastructure?

Automation infrastructure is composed of all the hardware and software solutions that enable automation to occur. These solutions target the IT and OT production infrastructure and automate some or all of their workflows.

Key automation infrastructure components

There are a variety of hardware and software solutions that provide automation capabilities for specific workflows, use cases, and deployment models. As part of a resilient network automation framework, the most important automation infrastructure components include:

Gen 3 OOB serial consoles

Serial consoles are typically installed in data centers and used to manage other devices over a serial cable connection. They create an out-of-band management (OOBM) network that’s dedicated to troubleshooting, management, and orchestration traffic, and which is accessible via a secondary internet connection (often using cellular). This secondary connection ensures administrators always have remote management access to critical data center infrastructure even when the primary ISP, WAN link, or production LAN goes down. That means businesses can recover from outages faster and without dispatching expensive truck rolls.

The latest generation of serial consoles, Gen 3, gives administrators the ability to automate workflows on all data center infrastructure. Gen 3 serial consoles are vendor-neutral, which means they can extend their automated management capabilities to any vendor’s device. That vendor neutrality also means that Gen 3 serial consoles support custom scripts and third-party automation tools in addition to whatever automation capabilities are built-in.

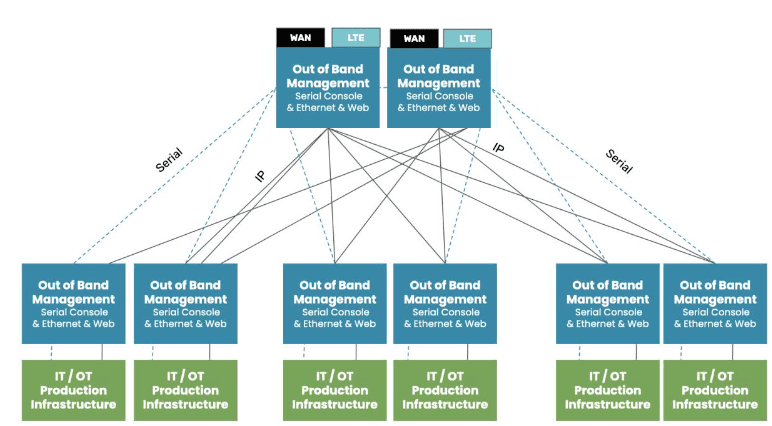
For peak resiliency, data center deployments should follow a two-tier OOB architecture. That means each rack of IT/OT production infrastructure should connect to its own Gen 3 serial console, which provides OOB management access and automation. These top-of-rack serial consoles should then connect to an OOB appliance in the middle or end of the row. This ensures OOBM access for the top-of-rack appliances and creates an additional layer of redundancy and resiliency.

Screenshot 2022-12-05 202130
Another important aspect of Gen 3 serial consoles is security. Since serial consoles provide comprehensive management access to critical infrastructure, they’re a tempting target for cybercriminals. A secure Gen 3 OOBM solution includes:

  • → Integration support for third-party security solutions like next-generation firewalls (NGFWs), security service edge (SSE), and SAML 2.0
  • → An up-to-date operating system (OS) kernel that’s frequently patched by the vendor when vulnerabilities are identified
  • → Onboard firewall functionality to inspect traffic on both the OOB network and the production network
  • → Hardware security features like encrypted boot sequences and BIOS protection to prevent unauthorized access on stolen serial consoles

Gen 3 OOB serial consoles are the automation infrastructure components that enable automation and resiliency for data center deployments at the core of enterprise networks.

SD-WAN gateway routers

A gateway router is used to connect a LAN infrastructure to the internet and the enterprise WAN architecture. As part of a resilient network automation framework, all gateway routers should support SD-WAN (software-defined wide area networking).

SD-WAN separates the control and management processes from underlying WAN hardware and virtualizes them as software. SD-WAN uses features like application awareness and guaranteed minimum bandwidth to automatically optimize network performance. An SD-WAN solution can also use automatic load balancing and failover to ensure continuous availability in the event of a localized failure or data center outage.

SD-WAN is usually a cloud-based service that delivers centralized management and orchestration of automated workflows. This service runs on top of the gateway routers deployed at each site.

An SD-WAN gateway router is a key automation infrastructure component for the main office, data center, branch, and edge deployments because it enables automated WAN management and orchestration. An all-in-one cloud-managed gateway router is particularly useful for OT automation in remote facilities like warehouses and factories because it provides SD-WAN capabilities, OOBM, and routing in one multi-function device.

Monitoring, visibility, and analytics

Monitoring and visibility solutions give administrators virtual eyes and ears on remote network infrastructure. As part of a resilient network automation framework, a visibility solution should be vendor neutral so it can dig its probes into any device in a mixed vendor environment. It should also include environmental monitoring sensors that collect data on conditions in the rack.

Device monitoring and environmental sensors give administrators the ability to detect potential issues and respond quickly to prevent outages. Monitoring and visibility solutions also collect valuable data that can feed into the AIOps building block of the network automation framework.

Infrastructure as Code

Infrastructure as Code, or IaC, uses software abstraction to decouple infrastructure configurations from the underlying hardware. Configurations are written as scripts or definition files that automatically provision virtual machines (VMs), containers, or software-defined networking (SDN) devices. An IaC definition file can be deployed repeatedly, which means many identical resources can be spun up quickly while ensuring consistent configurations. An IaC config can also undergo automatic security testing before it’s deployed to any devices to prevent vulnerabilities from affecting production.

Another important aspect of IaC is automatic configuration management. Configuration management solutions like RedHat Ansible allow administrators to define the desired state of a system or network resource. The configuration management tool continuously monitors the resource to detect unauthorized changes, which might be made by a careless sysadmin or could be a sign of a malware infection. As soon as the change is detected, the configuration management solution uses a programmatic playbook to take whatever actions are needed to restore the system to its proper state.

IaC helps ensure network resiliency by reducing human error in device configurations and updates, as well as by enabling the use of pre-production automated security vulnerability scanning and configuration management. Infrastructure as Code also facilitates another key automation infrastructure component—immutable infrastructure.

Immutable infrastructure

In-place system and device updates are a common cause of hangs or failures which can be challenging to resolve remotely. Immutable infrastructure resolves this problem by eliminating updates and configuration changes altogether. Immutable infrastructure refers to virtual systems and network resources that are never changed in place. If an immutable resource has an issue or vulnerability, or if its OS is out of date, an entirely new resource is spun up and the old one is simply deleted.

IaC is an immutable infrastructure best practice because it gives administrators the ability to provision many devices very quickly and with identical configurations. Immutable infrastructure is secure, easy to deploy, and resilient to failure, making it an important part of the network automation framework.

Why Nodegrid is a key automation infrastructure component

The automation infrastructure building block of the network automation framework relies on vendor-neutral OOBM devices like gateway routers and Gen 3 serial consoles that extend automation to converged IT/OT production infrastructure. These devices must also support monitoring and visibility solutions, Infrastructure as Code with configuration management, and immutable infrastructure.

For example, the Nodegrid platform from ZPE Systems includes OOB management hardware for a variety of data centers, branch, and edge deployments. Nodegrid serial consoles, such as the NSCP, can dig their hooks into any device in your data center to enable end-to-end network automation. A Nodegrid Gen 3 OOB serial console can even extend IaC and immutable practices to legacy devices to ensure resiliency without expensive forklift upgrades.

Nodegrid services routers, such as the Mini SR, are compact edge gateways that deliver SD-WAN support, OOBM, and cloud management capabilities to IT/OT infrastructure in smaller branch office and edge data center deployments. Nodegrid SRs can help you consolidate an entire rack of branch infrastructure into a single device to reduce management complexity, CapEx, and OpEx.

Nodegrid out-of-band is delivered via WiFi, Ethernet, or 5G/4G LTE to ensure administrators have fast and reliable access to remote infrastructure. All Nodegrid OOB devices are protected by robust hardware security features like BIOS protection, UEFI Secure Boot, geofencing, disk encryption, and TPM 2.0. Plus, Nodegrid supports integrations with Zero Trust Security solutions like identity and access management (IAM) and SAML 2.0, as well as providing an on-ramp to SSE.

Nodegrid serial consoles and services routers also include interfaces for environmental monitoring sensors to collect crucial data about conditions in your rack. These sensors, as well as any other connected devices, can all be observed and managed from a single, centralized monitoring and reporting platform.

What makes Nodegrid a crucial element of automation infrastructure is its ability to directly host Infrastructure as Code and automated configuration solutions, including Ansible, Chef, Puppet, SaltStack, Monit, and Docker. Nodegrid appliances can then extend the capabilities of the IaC solution to any of the modern, legacy, and mixed-vendor devices it manages.

ZPE’s Network Automation Blueprint

Automation infrastructure works together with IT/OT production infrastructure, orchestration, and AIOps to ensure network resiliency during uncertain times. The Network Automation Blueprint from ZPE Systems provides a reference architecture for achieving Gartner’s definition of hyperautomation as well as meeting the Open Networking User Group (ONUG) Orchestration and Automation recommendations.

In future blog posts, we’ll discuss the remaining two building blocks of the Network Automation Blueprint in depth. In the meantime, you can read about IT/OT production infrastructure or click here to get a sneak peek of the blueprint, which includes a 10-step checklist to get started with automation now.

Want to learn more about key automation infrastructure?

To learn more about Nodegrid as a key automation infrastructure component, contact ZPE Systems today.

Contact Us
How an IT/OT Convergence Strategy Accelerates Network Automation

An ITOT convergence strategy visualized with many digital services organized together in a data center.
In the face of a looming recession, Covid-19 uncertainty, global political instability, and an increasing frequency of natural disasters, network resiliency should be on every organization’s mind. Network resiliency is the ability to continue providing services and connectivity even during disruptions, such as when buildings are locked down or layoffs reduce the number of staff available to maintain or operate the technology. Network automation is the key to ensuring continuous, consistent, and streamlined management during tumultuous times.

A network automation framework provides all the tools and processes needed to create an efficient, resilient, fully automated network infrastructure. The four building blocks of a resilient network automation framework include:

  1. IT/OT production infrastructure
  2. Automation infrastructure
  3. Orchestration infrastructure
  4. AIOps

In this blog, we’ll discuss why an IT/OT convergence strategy is critical for forming the foundation of a network automation framework. Future posts will discuss the other three building blocks and how they work together to ensure business resiliency.

What is IT/OT convergence?

IT/OT convergence is exactly what it sounds like—bringing your information technology (IT) and operational technology together under unified management.

Operational technology, or OT, controls equipment interacting with the physical world, such as industrial machinery or HVAC systems. OT automation runs on specialized industrial computers, such as programmable logic controllers (PLCs) and supervisory control and data acquisition systems (SCADAs). Those computers are usually completely isolated from IT networks, which means operators have no way to access them remotely. If operators can’t get onsite, whether due to a Covid-19 lockdown or natural disaster, they lose the ability to manage OT.

For example, Southern California is home to many high tech manufacturing plants, especially in the aerospace and defense industries. Due to the effects of climate change, there’s been an increase in the frequency and severity of wildfires in this region, leading to more frequent evacuation orders and plant closures. That means operators can’t access their computer systems to control and monitor OT devices, forcing these businesses to pause their operations.

In addition, OT control systems aren’t usually within the purview of IT management because they use specialized computers and automation software that needs to be operated and supported by OT experts. That means IT infrastructure automation and OT infrastructure automation are siloed, which can lead to cost and management inefficiencies. With recession anxieties running high, many organizations are looking for ways to reduce such inefficiencies by converging their IT and OT infrastructure.

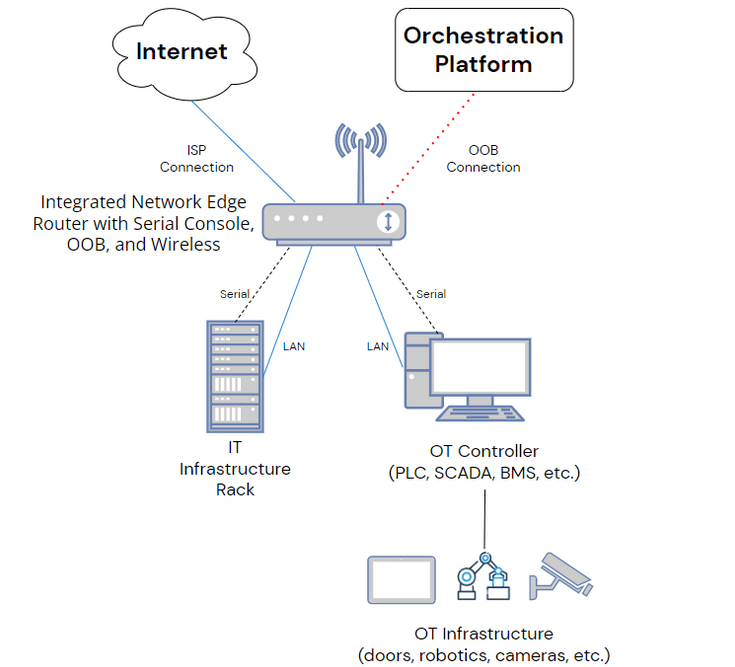
IT/OT convergence involves bringing your operational technology under the same management and automation umbrella as your IT network infrastructure. In a converged IT/OT infrastructure, OT control systems like PLCs and SCADAs connect to the same management hardware (e.g., serial consoles or cloud-managed gateway routers) as IT servers and network devices. This gives administrators a single platform from which to orchestrate automation across both IT and OT infrastructure.

What does IT/OT convergence look like?

IT and OT equipment being managed
First, you have the IT and OT equipment being managed. On the IT side, this includes things like servers, storage, security appliances, and SD-WAN devices. On the OT side, you have devices like environmental sensors, cameras, and power distribution units, as well as industrial computers used to monitor and control physical equipment. Some examples of those industrial systems include:

  • Programmable logic controllers (PLCs), which control industrial machines, robotic devices, and other manufacturing processes.
  • Supervisory control and data acquisition (SCADA), which is a control system for high-level supervision of industrial processes, including PLCs.
  • Building management systems (BMSs) which manage building equipment such as HVAC, fire suppression, lighting, and automatic doors.

These IT devices and OT computers all connect to common management hardware. For large deployments, these might be high-density serial consoles; in smaller deployments, these might be network edge routers with integrated serial console management functionality. This management hardware then connects to an orchestration platform that’s used to monitor, deploy, and manage automation across the converged IT/OT infrastructure.

How an IT/OT convergence strategy accelerates network automation

Bringing operational technology onto IT networks makes it possible for operators to remotely access their OT systems when they’re unable to come onsite. That means that your business can continue to function even during pandemic lockdowns, extreme weather events, or wars that prevent your staff from entering the building.

IT/OT convergence also allows you to bring operational technology under the same management umbrella as IT, so you can use the automation tools you’re already familiar with on the IT side to automate your OT. This reduces the overall management complexity of the IT/OT infrastructure and facilitates holistic orchestration of a fully automated—or even hyperautomated—enterprise network. This level of automation can help organizations reduce wasteful processes, eliminate redundancies, and increase operational efficiency so they can weather recessions and other economic difficulties.

Building IT/OT convergence into a resilient network automation framework

Your IT and OT infrastructure represent the target devices that are automated as part of a network automation framework. For maximum resiliency, your IT/OT convergence strategy should include:

Out-of-band (OOB) connectivity

Out-of-band (OOB) connectivity provides an alternative path to remote IT and OT infrastructure when the primary ISP connection goes down. In addition, OOB management devices (like serial consoles) directly connect to IT/OT devices, so administrators can manage them without an IP address or LAN connectivity. While OOB is not itself a component of IT/OT infrastructure, it’s a crucial element of the management devices and orchestration solution you’ll use to converge your IT and OT infrastructure.

Wired and wireless connectivity

Your converged IT/OT management solution also needs to support a variety of wired and wireless connectivity options to ensure resilience and flexibility. For example, if the ISP’s wired network infrastructure is disrupted due to extreme weather or warfare, you should be able to fail over to a 5G or 4G cellular connection. Or you may have some devices that lack RJ-45 ports, which means you need a management solution that supports USB. The goal is for your management solution to be adaptable to any scenario so that sudden changes or unforeseen issues don’t cripple your network operations.

Power control with UPS backup

As a remote network infrastructure, one of the most frustrating issues to deal with is a device that locks up after a system crash or failed firmware update. Often, a power cycle is all that’s needed to fix the problem, but that requires an on-site technician, which means an expensive and time-consuming truck roll. To ensure network resiliency while reducing the incidence of truck rolls, you need an IT/OT management solution that includes rack PDUs and IPMI options to facilitate remote power control of all connected devices.

In addition, an uninterruptible power supply (UPS) improves resiliency by providing backup power in case of an outage. This gives network teams time to investigate the problem and (hopefully) implement a fix before losing power. As part of the network resilience framework, all UPS units should hook into the management solution to allow for automated monitoring, optimization, and troubleshooting.

Environmental Sensors

Environmental sensors are used to monitor conditions in the location where IT and OT infrastructure is deployed. Traditionally, these sensors monitor racks in remote data centers, but they’re especially critical for IT/OT infrastructure that resides in less-ideal locations. For example, environmental sensors can provide data on the temperature and humidity levels in remote warehouses, offshore oil rigs, outdoor “smart city” deployments, and other locations when environmental conditions can’t be controlled.

Environmental sensors alert administrators when conditions grow too extreme for IT/OT equipment to function optimally. That means that teams can respond quickly and prevent equipment failures from bringing down critical resources. In addition, your infrastructure orchestration solution can analyze the data from these sensors to predict future issues or recommend optimizations to improve efficiency and resiliency.

How Nodegrid accelerates IT/OT convergence

The most successful IT/OT convergence strategy relies on vendor-agnostic platforms that can connect to both IT and OT infrastructure. For example, the Nodegrid solution includes management hardware that can connect to modern and legacy devices in a mixed vendor IT/OT infrastructure, such as the Nodegrid Serial Console Plus (NSCP) for large and hyperscale data center deployments and the Nodegrid Net Services Router (NSR) for flexible edge and branch deployments. These devices allow you to use the ZPE Cloud management platform to extend automation and orchestration to all your IT and OT targets to create a unified, efficient, and resilient converged network infrastructure.

ZPE’s Network Automation Blueprint

IT/OT production infrastructure works together with automation infrastructure, orchestration, and AIOps to ensure network resiliency during uncertain times. The Network Automation Blueprint from ZPE Systems provides a reference architecture for achieving Gartner’s definition of hyperautomation as well as meeting the Open Networking User Group (ONUG) Orchestration and Automation recommendations.

In future blog posts, we’ll discuss the remaining three building blocks of the Network Automation Blueprint in depth. In the meantime, click here to get a sneak peek of the blueprint, which includes a 10-step checklist to get started with automation now.

Ready to learn more about implementing an IT/OT convergence strategy?

To learn more about implementing an IT/OT convergence strategy with Nodegrid, contact ZPE Systems today.

Contact Us
What Is Edge Computing for Machine Learning?

Edge computing for machine learning is visualized as an artificial brain on the monitor of a remote industrial machine
Edge computing and machine learning technologies are helping organizations use their data more efficiently and effectively. In this blog, we’ll explain what edge computing is and discuss how it’s used with machine learning to improve performance and keep data secure. We’ll also explore two different edge computing deployment models for machine learning and provide advice on how to manage them.

What is edge computing?

For many modern enterprises, most of their data is no longer generated in a centralized data center or office building. These days, that data comes from IoT devices, “smart” industrial systems, and other remote locations around the globe. Transferring all that data to and from a central data center for processing can introduce latency and negatively impact performance. Transmitting sensitive data over the internet also increases the risk of interception by hackers.

Edge computing moves computational power closer to the source of data so that data doesn’t need to be sent to a separate location for processing. The benefit of edge computing is that data doesn’t need to travel as far, which translates to less latency and improved application performance. Plus, the data stays behind the firewall on the local network, reducing security risks.

What is edge computing for machine learning?

Machine learning (ML) is powered by data, and with data moving to the edge of enterprise networks, machine learning needs to decentralize as well. Edge computing for machine learning places ML applications closer to remote sources of data. The benefits of edge computing for machine learning are the same for edge computing in general, just supercharged.

Machine learning requires data to make intelligent predictions and decisions. In many cases, that data originates from the edge of the network. For example, the healthcare industry uses ML algorithms to analyze health data from smart devices in hospitals and clinics around the world, sometimes in hard-to-reach and politically unstable regions.

Getting patient health data from these remote facilities back to a centralized data center for machine learning processing can be very challenging, especially if the internet infrastructure is outdated or inconsistent. In addition, this data is personal and sensitive, and healthcare organizations are obligated to ensure its protection, so transferring it over uncertain internet connections is too risky.

Instead, organizations can install the ML algorithm on servers in each remote facility, or even on the smart devices themselves. This drastically reduces their reliance on outside network infrastructure for running machine learning workloads, which improves performance and ensures patient health data stays private.

How to deploy edge computing for machine learning

There are two basic deployment models for machine learning at the edge.

A traditional edge machine learning deployment uses one or more racks of heavy-duty servers with high-performance machine learning processing units. This deployment model is best suited to large ML workloads that process massive amounts of edge data.

A “thin” or “nano” edge machine learning deployment runs on smaller servers or multi-purpose devices that share rack space with other edge infrastructure. This deployment model is more cost-effective and works best for smaller ML workloads in buildings where space is limited.

For either deployment model, you need a solution in place for remote management so administrators can maintain and troubleshoot edge infrastructure without traveling on-site. The best way to ensure reliable management access is through out-of-band (OOB) management. OOB management creates a separate network dedicated to remote management and troubleshooting, and that  provides an alternative path to remote infrastructure (typically via cellular LTE) in case the primary ISP or WAN link goes down.

Through that OOB management network, you can orchestrate workloads, push out security patches, and monitor the health and performance of edge infrastructure.

Deploy and manage edge computing machine learning infrastructure with Nodegrid

The Nodegrid Net Services Router (NSR) from ZPE Systems supports both traditional and nano edge computing machine learning deployment models. The NSR is a modular and customizable solution that delivers OOB management, cellular failover, edge routing and switching, and automation in a single device.

You can use the NSR’s serial console modules to monitor, manage, and orchestrate an entire rack of edge machine learning servers. For less intensive workloads, you can use the edge compute module to host ML applications, virtual machines, and Docker images.

Either way, you can take advantage of 5G/4G LTE to ensure fast and reliable OOB access and cellular failover. The NSR is also secured by Zero Trust features like SAML 2.0 integration and BIOS protection to keep edge machine learning data protected.

Ready to learn more about 5G/4G LTE to ensure fast and reliable OOB access?

To learn more about edge computing for machine learning with Nodegrid, contact ZPE Systems today.

Contact Us