Providing Out-of-Band Connectivity to Mission-Critical IT Resources

Atsign: Why Choose ZPE Systems to Host IoT Security?

Colin

A Conversation with Atsign CTO & Co-Founder, Colin Constable

This is a guest post composed by Atsign, creators of zero-attack-surface solutions including atProtocol.

We recently sat down with our CTO and Mariposa Rotary Club extraordinaire, Colin Constable, to discuss our partnership with our friends over at ZPE Systems. Let’s explore the driving force behind this powerful partnership, and how together we’re securing IoT devices and the data shared between them.

Why is this partnership strategically important?

We are a software company that helps people connect beyond the edge of the Internet. And as a software company, we need to have hardware to run our software on. After looking at a number of hardware platforms, ZPE stood out as an organization that provides a strong array of network connectivity options. Our software running on ZPE’s hardware serves as an edge platform that gives customers reliable access to edge-generated data.

What are some of the synergies between Atsign and ZPE?

First and foremost, ZPE’s hardware was designed from scratch to provide the openness and flexibility that we were looking for in a hardware platform. If I were going to design something like this myself, it would look very much like a ZPE box! It is incredibly easy to drop our Docker containers straight onto the platform, and they just simply work, which is quite a joy. To have a Docker container environment on an edge box is really the thing that makes ZPE stand out as a platform. Combine that with the fact that ZPE boxes are running x86, which makes things easy–plus actually having dual SIM cards–we can work with our MVNO partners to provide constant connectivity; even if hardlines go down, there’s cellular backup. The thing we can offer ZPE and their customers is if the box can see the Internet, then you’ll be able to address it, get data to and from it, and actually even log into it, and get hold of the built-in UI on the box.

Tell us about ZPE’s Docker Container support

Our docker containers literally just ran perfectly on the ZPE hardware. I went into the UI, selected my docker container, and it just ran. It doesn’t get much easier than that. Plus, there’s the promise of being able to have the docker container talk to connected devices like V.24 cables to provide connectivity to IoT devices.

Once IoT devices become directly addressable, then it opens up all kinds of opportunities for more efficient delivery or sharing of information that can save customers tons of money by eliminating a lot of the current infrastructure they currently use to do that job.

What are some real-world use cases for Atsign and ZPE Systems?

Because ZPE boxes have lots of connectivity options (e.g. serial ports, 4/5G backhaul, and ethernet–with more coming!) for connecting IoT devices, then you can have always-on devices at the edge, and be able to address and get data to and from them. For example, a radio station that has DSL connectivity, and cellular backup would be able to just automatically move over to cellular backup, notify the radio station that it’s on cellular backup, but use that connectivity until the ADSL line comes back online and at all times be able to get information from the equipment at the radio station. This is critical for radio stations, as it eliminates “dead air,” that moment when the transmitter is not transmitting. Sponsors rely on radio stations to put out notifications for what their businesses are doing, so having constant, uninterrupted connectivity is essential.

Do Atsign & ZPE Systems improve sustainability?

Traditional solutions would have you installing many different boxes. What we really like about the ZPE platform is that although the hardware provides lots of connectivity options–that reduces the footprint for starters–there’s no need to have different modems and firewalls, and any other services can be added via docker containers, so you actually have an environment where you have a single box, and it can do multiple functions at the edge.

What are your final thoughts on the partnership between Atsign and ZPE Systems?

As a software company, we need hardware to deploy on. We especially need hardware that can sit on the edge with all the right connectivity points. Atsign and ZPE Systems is really a perfect combination of great software and great hardware at the edge.

Bonus: What is Colin’s favorite firewall configuration for a ZPE box?

My favorite firewall rule is the one that costs the least money, and is ultimately the most secure firewall ruleset: Deny All. If you’ve got Deny All, that means that you don’t have to deal with the pain and complexities of firewall rules in order to address devices, which is what the real cost of networking is these days; it’s not necessarily the hardware, it’s actually having people to administer firewall rulesets. Having zero network attack surfaces, having a Deny All ruleset, just means you don’t have to have people changing rulesets all the time, which is a good thing.

99.999% Uptime for a Top-10 Engineering School

Providing low-level remote access and automation saves hundreds of hours per month for the university’s small IT team

One of the largest universities in the United States fosters academics and research for nearly 40,000 students, staff, and researchers. The university sits among the top 10 schools for engineering, and heavily integrates technology into all disciplines, including engineering, computer sciences, and agricultural studies.

The university received a grant to expand, update, and connect their network of campuses, while enhancing infrastructure and mobility, resiliency, and campus amenities.  But having more than 200 on-campus buildings presents a challenge. The campus is home to academic facilities as well as a hospital, airport, 60,000-seat sports stadium, and dozens of leased spaces for local businesses. This makes the university equivalent to a small city, and its network infrastructure is what keeps it all connected.

Their small IT team was responsible for maintaining more than 10,000 management devices, most of which were long past EOL and frequently failing. They needed a refresh, but with a solution that could also reduce the hundreds of hours they spent every month on travel and on-site work. To maximize their day-to-day efficiency, they required a solution that could overcome these operational gaps:

  • Reducing the 100-150 hours of monthly travel times, by giving engineers the ability to fully access their stack remotely
  • Reducing the 80-120 hours of monthly on-site work required to maintain the 99.999% SLA, by automating manual jobs such as patching and firmware upgrades
  • Expanding their management headroom and use-case adaptability, by migrating to IPv6 and reducing the existing 6RU device stack

Download the full case study to see how ZPE’s Nodegrid hardware and software solved these problems.

EngineeringSchoolCover

Download the full case study

Problems and Gaps

The university is one of the largest in the United States. It sits among the nation’s top 50 schools for research expenditures, and heavily integrates technology into all disciplines, including engineering. Its main campus is home to more than 200 buildings that sit on over 2,500 acres of land. The campus is essentially a small city, and the university’s network infrastructure keeps it all connected.

This network infrastructure, however, was well beyond EOL and in disrepair. But rather than simply upgrade to newer devices, the university’s small IT team wanted to improve the overall quality of life well into the future. This meant addressing three gaps:

  • Inefficient management at scale — Each engineer spent an average of ten hours per month on travel alone, just to traverse the campus’ wide footprint and get to each MDF/IDF closet.
  • Too much focus on ops — The aging infrastructure was on the brink of collapse and required each engineer to spend eight hours per month in on-site work, just to keep devices running.
  • Too many devices — The infrastructure includes roughly 10,000 devices to manage, which was exhausting IP on their limited IPv4 network and too rigid to fit in tight spaces, like their remote farm closets and research labs.

Solution

The university deployed the full lineup of Nodegrid devices, including the Nodegrid Serial Console, Nodegrid Services Routers, and Nodegrid Manager. These allowed them to overcome all three gaps using remote management, automation, and consolidated functionality, to save engineers hundreds of hours every month. Download the full case study to see the complete solution and benefits.

Need Help Replacing End-of-Life Gear?

Check out our complete products and services package to make your EOL transition seamless. Choose from a variety of Synopsys-validated devices, get a generous trade-in discount, and let our engineers install and configure into your environment. Click below to explore this offer and more customer case studies.

Network Automation Cost Savings Calculator

automation cost savings calculator
Many organizations feel continuous financial pressure to cut costs and streamline operations due to economic factors like the ongoing threat of a recession and global supply chain interruptions. Network automation can help companies across all industries save money during lean financial times. A recent Cisco and ACG Research study found that network automation can reduce OPEX by 55% by streamlining workflows such as device provisioning and service ticket management. Though they aren’t mentioned in the study, additional savings are generated by using automation to avoid outages and accelerate recovery efforts.

This post discusses how to save money through automation and provides a network automation cost savings calculator for a more customized estimate of your potential ROI.


Table of contents

How network automation provides cost savings

Network automation reduces costs by streamlining operations, preventing outages, and aiding in backup and recovery workflows.

Network automation saves money by solving problems

Problem: High OPEX

Solution: Automation tackles repetitive tasks like new installs and ticketing operations, which helps you generate revenue sooner and reduce the time and resources spent on maintaining operations.

Problem: Too many outages

Solution: Automation allows teams to be proactive by leveraging critical data to identify potential problems before they cause outages, freeing them from the typical break/fix approach.

Problem: Slow recovery

Solution: Automation speeds up processes like backups, snapshotting, and device re-imaging, which makes networks more resilient by accelerating recovery from outages and ransomware.

Reduces OPEX

The focus of the Cisco/ACG study was the economic benefits of streamlining network operations through automation. For example, the OPEX (operational expenditure) involved in spinning up a new branch is too high because deployments require so much work, time, and staff. Using automation to provision and deploy new resources can significantly reduce the time it takes to spin up a new branch, which means the site could start generating revenue much sooner. Using automation to monitor device health and environmental conditions could extend the life expectancy of critical (and expensive) equipment while reducing the number of on-site staff needed to maintain that equipment.

Network automation reduces OPEX by increasing the efficiency of repetitive or tedious tasks like new installs, incident management, and device monitoring. Crucially, automation does so without reducing the quality of service for end users and often only improves the speed, reliability, and overall experience.

Prevents outages

Network downtime is an expense that cash-strapped businesses can’t afford to bear. According to a recent ITIC survey, a single hour of downtime costs most organizations (91%) over $300,000 in lost business, with 44% of enterprises reporting outage costs exceeding $1 million. However, preventing downtime is difficult when most network teams are caught in a reactive break/fix cycle because they lack the staffing, resources, and technology required to maintain visibility and identify issues before they occur.

Network automation solves this problem using advanced machine learning algorithms to analyze monitoring data and identify potential issues before they cause outages. For example, AIOps (artificial intelligence for IT operations) solutions provide real-time analysis of infrastructure, network, and security logs. AIOps is adept at recognizing patterns and detecting anomalies in data so that it can identify issues before they affect the performance or reliability of the network.

Accelerates recovery

While network automation helps to reduce downtime, it can’t eliminate outages altogether. When outages do occur, recovery is often a long, drawn-out process involving a lot of manual work, during which time revenue and customer faith may be lost. Network resilience is the ability to quickly recover from ransomware, equipment failures, and other causes of downtime with as little impact as possible on end users and business revenue. Automation speeds up recovery efforts in a few critical ways:

  • Streamlined backups – Automation makes performing regular backups and snapshots easier, reducing the risk of gaps or inaccuracies.
  • Reduced imaging delays – Automatic provisioning ensures that clean systems are spun up quickly so that business can resume as soon as possible.
  • Faster failover – Automatic network failover and routing technologies can reroute traffic around downed nodes before a human admin has time to respond, providing a more seamless end-user experience.

Network automation is a direct source of cost savings because it reduces OPEX without negatively impacting the business or customer experience. Automation also indirectly saves money by helping organizations avoid outages through proactive monitoring and maintenance. In addition, network automation technologies make businesses more resilient by speeding up recovery efforts when breaches and failures do occur.

Network automation cost savings calculator

ZPE Systems provides network and infrastructure automation solutions for any use case, pain point, or technological need. ZPE’s vendor-neutral platform allows you to extend automation to every device on your network, including legacy and mixed-vendor solutions, so that you can achieve true end-to-end automation (a.k.a. hyperautomation). For a customized estimation of how much money you can save by automating your network operations with ZPE Systems, check out our network automation cost savings calculator.

Ready to Learn More?

For help with the network automation cost savings calculator or to learn more about automating your network operations, contact ZPE Systems today.

Contact Us

What Is a Zero Trust Gateway?

What Is a Zero Trust Gateway(2)
The constant threat of cyberattacks has made network security a top priority for companies in every sector, with Gartner predicting that global cybersecurity spending will reach $188 billion in 2023. However, security continues to get more challenging due to factors like a rise in remote work, an increasing reliance on touchless internet of things (IoT) devices, and the overall decentralization of enterprise networks. It’s hard to create a secure perimeter around the enterprise when its users, devices, applications, and data could be anywhere in the world.

The zero trust security methodology addresses this challenge by shrinking the focus from one large security perimeter and instead creating smaller “micro-perimeters” around each individual resource that needs defending. It’s called zero trust because it follows the principle of “never trust, always verify.” That means each user and device needs to verify its identity and prove its trustworthiness before it can penetrate the micro-perimeter. So, for example, if a cybercriminal uses stolen credentials to log into the enterprise network, they have to pass through many different security checkpoints to see or access any sensitive resources, which increases the likelihood they’ll get caught before excessive damage is done.

One way to implement micro-perimeters and apply zero trust security policies is with a device called a zero trust gateway. This post discusses the technologies that make up a zero trust gateway and explains how they work together to defend enterprise networks.

What is a zero trust gateway?

A zero trust gateway is a device that sits at the edge of the network – or at the top of the rack – and applies zero trust security policies and controls to traffic flowing in either direction. The gateway can be a dedicated security appliance, but it’s often more cost- and space-effective to use a multi-functional device that combines security, networking, and infrastructure management in a single box.

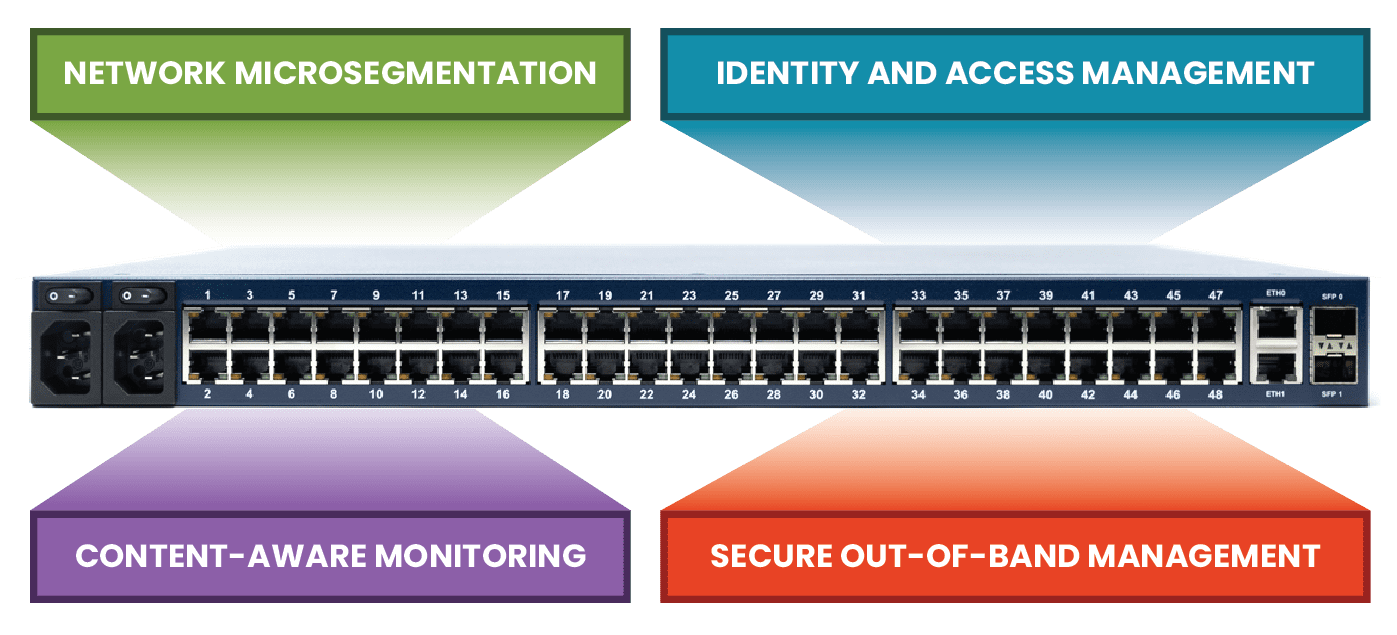
Some of the key features used in an all-in-one zero trust gateway include network micro-segmentation, identity and access management, context-aware monitoring, and secure out-of-band management. There are a small number of mature solutions that deliver all of these features off-the-shelf, but they lock you into their small solution ecosystem and limited feature roadmap. A better approach is to start with a vendor-neutral platform that lets you host and integrate your choice of security applications to create a fully customized zero trust gateway. Let’s walk through how each of these security technologies works and how to combine them into a bespoke zero trust gateway solution.

To see an example of a vendor-neutral zero trust gateway at work, request a demo of the Nodegrid solution from ZPE Systems.

Request a Demo

Network micro-segmentation

A zero trust micro-perimeter is made up of granular access control policies and security controls that are custom-tailored to the specific vulnerabilities and requirements of resources they’re defending. For example, an on-premises database containing sensitive financial records needs different policies than a cloud-based application that doesn’t process any personal information. To implement micro-perimeters, resources first need to be logically organized based on their sensitivity level, who needs access to them, and what their interdependencies are.

Network micro-segmentation is used to separate resources based on these criteria so that micro-perimeters can then be applied. For a device to be considered a zero trust gateway, it must support VLAN micro-segmentation and be able to apply access control rules consistently across all micro-segments.

Identity and access management

In a zero trust architecture, user and device permissions should be limited to only what’s necessary to perform their job role. For example, an HR account used to manage employee records shouldn’t have access to customer financial data, and vice versa. Access policies should be specific to individual micro-segments and resources and need to be applied to all users and devices consistently, no matter where they’re logging in from. That means a remote user should follow the same authentication steps and have the same permissions as they would if they logged in at the office.

For a large enterprise network, this is only achievable with a centralized identity and access management (IAM) solution. An IAM provides a single platform from which to create, manage, and apply security policies. A zero trust IAM also enables best practices like single sign-on (SSO) and two-factor authentication (2FA).

A zero trust gateway needs to integrate with your chosen IAM provider to ensure that policies are applied to both production traffic and management traffic. Some vendor-neutral gateway solutions can even directly host and run third-party IAM solutions, providing a more integrated experience and saving rack space.

Context-aware monitoring

Many successful cyberattacks use stolen credentials gained through phishing schemes and other social engineering tactics. For example, Mailchimp was recently attacked by malicious actors using credentials stolen from employees through social engineering. It’s difficult to detect and contain such an attack because the criminal looks like an authorized user. However, careful monitoring often reveals suspicious behavior, such as logging in from an unusual IP address or time zone, making multiple access requests to areas of the network they don’t usually visit, or transferring abnormally large quantities of data.

User and entity behavior analytics, or UEBA, uses machine learning technology to monitor and analyze account activity on the enterprise network. UEBA creates a baseline of “normal” behavior for individual accounts so it can detect any anomalous activity. UEBA integrates with other security and monitoring solutions, such as IAM and firewalls, so it can compare data from various sources to make more informed decisions. This is one of the ways that zero trust security verifies the trustworthiness of accounts trying to access sensitive resources, making UEBA a critical component of zero trust gateways.

Secure out-of-band (OOB) management

Admins need a fast and reliable way to access remote infrastructure for management, troubleshooting, and recovery. For example, it’s common for a single data center management team to be responsible for customer equipment in multiple DCs distributed around the world for redundancy. These admins can’t physically go on-site every time a firmware update fails or a device loses its IP address. That’s why they rely on remote out-of-band (OOB) management; remote OOB management creates a separate network just for management traffic that doesn’t rely on the production LAN. Admins access the OOB network using a dedicated management device, like a jump box or a serial console server.

This management device is a tempting target for cybercriminals, as gaining control of that device will give them complete control over the connected infrastructure. One way to protect the OOB network is by using a zero trust gateway with integrated management ports. For example, the Nodegrid Net Services Router (NSR) is a modular zero trust gateway that can be customized to connect to any type of device that needs to be managed or secured. The NSR comes with gateway routing and switching capabilities, an embedded firewall, and hardware security features like secure boot and a self-encrypted disk. Nodegrid is also completely vendor-neutral, which means it can directly host or integrate with your choice of third-party security solutions, including next-generation firewalls (NGFWs) and zero trust technologies like identity and access management and UEBA.

The NSR is a modular, open platform upon which to build a fully customized zero trust gateway for large data center deployments. The Nodegrid product line from ZPE Systems also includes a variety of serial console solutions and integrated all-in-one gateway routers to support other use cases, such as edge computing sites, branches, and automated IoT deployments.

A zero trust gateway helps organizations implement micro-perimeters of specific policies and controls to defend sensitive data and other valuable resources. A vendor-neutral, integrated solution like the Nodegrid Serial Console Plus from ZPE Systems makes it possible to combine zero trust security with networking and management functionality to create a streamlined, cost-effective zero trust gateway deployment.

Ready to learn more about Zero Trust Gateway?

To learn more about deploying Nodegrid as a zero trust gateway in your enterprise, contact ZPE Systems today.

Contact Us

Zero Touch Deployment Cheat Sheet

A zero touch deployment cheat sheet is visualized as a literal cheat sheet used by a student during an exam

Zero touch deployment is meant to make admins’ lives easier by automatically provisioning new devices. However, many teams find the reality of zero touch deployment much more frustrating than manual device configurations. For example, zero touch deployment isn’t always compatible with legacy systems, can be difficult to scale, and is often error-prone and difficult to remotely troubleshoot. This post provides a “cheat sheet” of solutions to the most common zero touch deployment challenges to help organizations streamline their automatic device provisioning.

Zero touch deployment cheat sheet

Zero touch deployment – also known as zero touch provisioning (ZTP) – uses software scripts or definition files to automatically configure new devices. The goal is for a team to be able to ship a new-in-box device to a remote branch where a non-technical user can plug in the device’s power and network cables, at which point the device automatically downloads its configuration from a centralized repository via the branch DHCP server.

In practice, however, there are a variety of common issues that force admins to intervene in the “zero touch” deployment. This guide discusses these challenges and advises how to overcome them to achieve truly zero touch deployments.

Zero touch deployment challenge: The solution:
Legacy systems don’t have native support for zero touch Extending zero touch to legacy systems using a vendor-neutral platform
Deployment errors result in costly truck-rolls Recovering from errors remotely with Gen 3 out-of-band (OOB) management
Securing remote deployments causes firewall bottlenecks Moving security to the edge with Zero trust gateways and Secure Access Service Edge (SASE)
Automating deployments at scale increases management complexity Maintaining control through centralized, vendor-neutral orchestration with version control

Extend zero touch to legacy systems with a vendor-neutral platform

Challenge Solution

While many new systems and networking solutions support zero touch deployment, sometimes there’s still a need to repurpose or reconfigure legacy systems that don’t come with native ZTP support.

Pre-staging these devices before shipping them to the branch is a security risk because the system could be intercepted in transit; plus, they’re likely already deployed at remote sites and need to be reconfigured in place. Without a way to extend zero touch deployment capabilities to those legacy systems, companies often have to pay for admins to travel to remote branches, negating any cost savings they were hoping to gain from reusing older devices.

One way to extend zero touch to legacy systems is with a vendor-neutral management platform. For example, a vendor-neutral serial console switch with auto-sensing ports can connect to modern and legacy infrastructure solutions in a heterogeneous branch deployment so they can all be managed from a single place.

From that unified management platform, admins can write and deploy configuration scripts to connected devices, including legacy systems that don’t support zero touch. Technically, this isn’t zero touch deployment because the system doesn’t automatically download and run its configuration file, but it’s still a way to turn an on-site, manual process into one that’s remotely activated and mostly automated.

Recover from deployment errors with Gen 3 OOB management

Challenge Solution

A new branch deployment almost never goes completely according to plan, and this is especially true when teams are using zero touch for the first time, or aren’t completely comfortable with software-defined infrastructure and networking. In the best-case scenario, when there’s a configuration error, the zero touch deployment aborts, and an admin is able to correct the problem and restart the process.

However, sometimes the deployment hiccup causes the device to hang, freeze, or get stuck in a reboot cycle. Or, even worse, an unnoticed error in the configuration could allow the deployment to finish successfully but then go on to affect other production dependencies and bring the entire branch network down. Either way, organizations must again deal with the expenses involved in sending a tech out to troubleshoot and fix the problem.

The best way to ensure continuous access to remote infrastructure is with out-of-band (OOB) management. An OOB solution, such as a serial console or all-in-one branch gateway, connects to the management ports on infrastructure devices so admins can remotely monitor and control every device from a single place without IP addresses.

This creates a separate (out-of-band) network that’s dedicated to management and troubleshooting, making it possible for teams to remotely recover devices that have failed the zero touch deployment process or brought down production LAN dependencies. Plus, the OOB gateway uses independent, redundant network interfaces to ensure admins still have remote access even if the production WAN or ISP link goes down.

To ensure full OOB management coverage of a heterogenous, mixed-vendor environment, the out-of-band solution should be completely vendor-neutral. An open OOB device also supports integrations with third-party solutions for automation, orchestration, and security. This kind of out-of-band platform is known as Gen 3 OOB. Gen 3 OOB management ensures that teams can remotely recover from zero touch deployment errors no matter what device is affected or how the production network is impacted.

Secure remote deployments with zero trust gateways and SASE

Challenge Solution

Organizations need to secure all devices at all remote sites using consistent policies and security controls. However, for smaller branches and IoT sites, it usually isn’t cost-effective to deploy a security appliance in each location.

Plus, adding more firewalls also adds more management complexity. That means traffic is usually backhauled through the main data center firewall, creating bottlenecks and causing network latency for the entire enterprise.

Using zero trust gateways and cloud-based security services, companies can move security to the branch without the cost and complexity of additional firewalls. An all-in-one, zero trust gateway solution combines SD-WAN, gateway routing, and OOB management in a single device. It also supports zero trust authentication technologies like SAML 2.0 and 2FA. A zero trust gateway also needs to support network micro-segmentation, which will allow the use of highly specific security policies and targeted security controls. Plus, by enabling software-defined wide area networking (SD-WAN), a zero trust gateway facilitates the use of SASE.

Secure Access Service Edge (SASE) is a cloud-based service that combines several enterprise security solutions into a single platform. Zero trust gateways use SD-WAN’s intelligent routing capabilities to detect branch traffic that’s destined for the cloud or web. This traffic is directed through the SASE stack for firewall inspection and security policy application, allowing it to bypass the main security appliance entirely. SASE helps reduce the load on the enterprise firewall, reducing bottlenecks and improving performance without sacrificing security.

Scale zero touch deployments with centralized orchestration

Challenge Solution
Zero touch deployments occur (at least in theory) without any admin intervention, but they still need to be monitored for failures. Keeping track of a handful of automatic deployments may seem easy enough, but as the number and frequency increases, it becomes more challenging. This is especially true when companies kick off large-scale expansions, deploying dozens of devices at once, all of which could be plugged in at any time to begin the automated provisioning process. Plus, different devices need different configuration files, and admins need a way to work together without overwriting each other’s code or duplicating each other’s efforts. A vendor-neutral orchestration platform provides a central hub for network and infrastructure automation across the entire enterprise. This platform uses the serial consoles and OOB gateways in each remote location to gain control over all the connected devices, so network teams can monitor and deploy all their zero touch configurations from one place. An orchestration platform is the single source of truth for all automation, so it needs to support version control. This ensures that admins can see who created or changed a configuration file and revert to a previous version when there’s a mistake.

Simplifying zero touch deployment with Nodegrid

Zero touch deployment can be a hassle, but using vendor-neutral management systems, Gen 3 OOB management, zero trust gateways, and centralized orchestration can help organizations overcome the most common hurdles. For example, a vendor-neutral Nodegrid branch gateway deployed at each remote site helps you extend automation to legacy systems, provides fast and reliable out-of-band access to recover from issues, enables zero trust security & SASE, and gives you unified orchestration through the Nodegrid Manager (on premises) and ZPE Cloud software.

Ready to learn more about zero touch deployment?

Nodegrid has a solution for every zero touch deployment challenge. Schedule a demo to see how Nodegrid’s vendor-neutral platform can simplify zero touch deployment for your enterprise.

Contact Us

Network Automation Tools To Offset the Tech Talent Shortage

network automation tools
As enterprise networks grow more complex, there’s a rising need for highly-specialized engineers to implement and maintain these complicated architectures. However, due to the Covid-19 pandemic, a global recession, and other world events beyond an organization’s control, it can be very difficult to recruit and retain these specialists. In fact, many companies are currently relying on smaller IT teams than usual to manage their vital network infrastructure. According to Gartner research, the tech talent shortage is one of the biggest barriers to the adoption of emerging technology like network automation.

However, network automation tools can actually help understaffed organizations ensure the continued availability and performance of enterprise networks by streamlining workflows and reducing manual intervention. In this blog, we’ll discuss how four different types of network automation tools can be used to solve major problems caused by the tech talent shortage.

Problem Solution
You lack the staff required to efficiently deploy, monitor, and manage network configurations. Automated network configuration management solutions like SolarWinds Network Configuration Manager (NCM) and Micro Focus Network Automation Software.
You need to extend DevOps automation to networking without purchasing additional solutions or hiring network automation experts. DevOps configuration management solutions that can be used for server and network automation like RedHat Ansible and Puppet.
You want to improve network reliability and performance while reducing management complexity. Software-defined networking (SDN) and software-defined wide area networking (SD-WAN) solutions like Palo Alto Prisma and Cisco Meraki.
You lack full-coverage network security, so you’re unsure where your vulnerabilities are or how efficiently you can respond to incidents. Network security automation solutions like Palo Alto’s Next-Generation Firewall (NGFW) and Datadog AIOps security and monitoring.


To learn more about using automation technology to ensure network resilience, click here to download the Network Automation Blueprint from ZPE Systems.


Network automation tools to offset the tech talent shortage

The following categories of network automation tools are designed to simplify network management workflows to ensure optimal performance and 24/7 availability.

Automated network configuration management

Network configuration management refers to the ongoing process of creating, deploying, and maintaining configurations for network devices and logic. Some of the tasks involved in network configuration management include device discovery, provisioning, and software and firmware updates. In addition, network configurations are monitored to ensure they don’t drift away from documented standards (configuration shift), and if needed, unauthorized changes are rolled back. This reduces the risk that an undocumented configuration tweak will introduce an unnoticed security vulnerability (such as the recent Fortinet authentication bypass exploit) and ensures consistent quality across the entire network architecture.

However, manual network configuration management is complicated and time-consuming, especially when so many network operations teams are overworked and understaffed. An automated network configuration management solution handles many of these tasks without the need for human intervention. Admins can create network configuration policies and playbooks which are used to automatically deploy new devices and update network dependencies, saving time and reducing human error. In addition, automated configuration management uses these policies to continuously monitor for and correct configuration drift. In the case of the Fortinet CVE, for example, automatic configuration management could have helped teams instantly roll back to the last known good config to close the vulnerability.

Examples of network automation tools for network configuration management include SolarWinds Network Configuration Manager and Micro Focus Network Automation.

DevOps IaC configuration management

Many organizations have adopted the DevOps methodology, which seeks to dissolve the barriers between the software development and IT operations teams to improve efficiency. On the Ops side, this often involves a practice called IaC, or Infrastructure as Code. IaC uses software code and machine-readable definition files to automatically provision servers and manage configurations. IaC enables Ops teams to spin up resources at the velocity required for fast-paced DevOps software projects. It also means that infrastructure configuration code can be stored, managed, and deployed from the same platform as software code, facilitating easy collaboration between developers and sysadmins.

With the recession forcing many IT teams to downsize, organizations are looking for ways to extend the efficiency provided by DevOps automation tools to the networking side of the house without purchasing additional solutions. Plus, many network admins lack the expertise required to operate network automation solutions, and the tech talent shortage makes recruiting such specialized engineers difficult. Luckily, some IaC configuration management tools like RedHat Ansible and Puppet can also be used for network configurations, which helps teams automate without any special programming skills.

That also means admins can deploy, monitor, and manage configurations for network devices and systems across the entire architecture from a single platform, saving money and reducing operational complexity. This convergence of DevOps and network management is known as NetDevOps or NetOps, and it’s empowering organizations to improve efficiency even during the recession and talent shortage.

Software-defined networking and SD-WAN

Enterprise networks are typically highly distributed and very complex. An organization could have 500 branch offices around the world, each of which uses slightly different networking hardware and software solutions. Each of these vendor solutions might have its own management platform for admins to configure, manage, and continuously monitor. Things grow more challenging when an organization uses a hybrid cloud infrastructure, which requires WAN (wide area networking) orchestration across multiple public and private clouds. This complexity makes it challenging for overworked network administrators to maintain optimal performance and 24/7 availability.

Software-defined networking (SDN) and software-defined wide area networking (SD-WAN) help to reduce the complexity of enterprise networks by abstracting network configurations and workflows as software code that’s decoupled from the underlying hardware. Codifying network configurations makes it easier to use technology like automated configuration management, which reduces the burden on overworked admins and reduces human error. SDN and SD-WAN also facilitate the use of centralized network orchestration platforms, which give admins a single pane of glass from which to control the entire network architecture.

This holistic coverage makes it possible for small teams to efficiently monitor and manage large, complex networks, reducing the risk of fatigue, human error, or negligence affecting performance. Plus, SDN and SD-WAN solutions employ automation to continuously monitor and adjust routing configurations as needed to ensure optimal performance. That means these solutions are often able to detect and remediate issues with latency and site availability much faster than a human admin could, ensuring optimal performance and reliability.

Examples of SDN and SD-WAN solutions include Cisco Meraki SDN and Palo Alto Prisma SD-WAN.

Network security automation

With the quantity, sophistication, and cost of cybersecurity attacks rising every year, network security is more important than ever. According to the Sophos State of Ransomware 2022 survey, 66% of organizations were hit by ransomware, a massive increase from 2020 in which only 37% of organizations were attacked.

However, the tech talent shortage and ongoing recession have left many organizations with gaps that increase both the risk that a breach will occur and the time it will take to recover. For example, IBM estimated in 2021 that unpatched vulnerabilities accounted for at least one-third of all data breaches. However, staying on top of patch management for large, diverse, and distributed network infrastructures is difficult when teams are overworked and understaffed.

Plus, when networking and security teams are spread so thin, it can take them much longer to detect a breach that has already occurred, even if the hacker is actively exfiltrating data or changing system configurations. Remediation is also slowed down by the need to manually investigate logs, isolate affected systems, and implement fixes.

Network security automation can help bridge these gaps by reducing the need for human analysts to perform the more tedious and repetitive – but highly vital – tasks involved in ongoing cybersecurity management. Automated security solutions use technology like AIOps and machine learning to manage software and firmware updates, analyze network traffic for threats, and even perform remediation steps like quarantining infected systems and blocking compromised accounts.

Popular examples of network security automation tools include Palo Alto Network’s Next Generation Firewall (NGFW) and Datadog AIOps Security and Monitoring.

Using a vendor-neutral platform to deploy network automation tools

The goal of automation is to make it easier for network admins to maintain and optimize the enterprise network. However, if admins need to learn, configure, deploy, and manage a bunch of additional automation solutions, you could end up increasing the complexity of their jobs rather than reducing it.

The Nodegrid platform can help by directly hosting all of the network automation tools listed above, reducing the need for additional hardware to manage. Deploying Nodegrid boxes in all your data centers and remote sites gives you the ability to extend automation to every corner of your network and manage it all from behind a single pane of glass. Hosting your network automation on a vendor-neutral platform like Nodegrid gives your team an easy way to orchestrate automated workflows across your entire enterprise architecture.

Network automation tools help to bridge the gaps caused by the tech talent shortage, ensuring the reliability and resilience of enterprise networks. To get step-by-step instructions for how to implement the network automation solutions mentioned above, click here to download the Network Automation Blueprint from ZPE Systems.

Ready to learn more?

To learn more about deploying network automation tools with Nodegrid, contact ZPE Systems today.

Contact Us