Providing Out-of-Band Connectivity to Mission-Critical IT Resources

SD-WAN Leaders Analysis Report
Logos for the six SD-WAN leaders with a vs. in the middle
Gartner’s most recent Magic Quadrant for SD-WAN identified six vendors as leaders in the market. These vendors qualify as leaders due to numerous factors, including their influence in the market, a demonstrated ability to adapt to changing customer requirements and innovate to anticipate future needs, and solid SD-WAN product offerings that serve most use cases and verticals. This report uses Gartner’s Magic Quadrant and independent analysis to compare the six SD-WAN leaders based on their features, security, versatility, and other key factors.

Comparing SD-WAN leaders

Leading SD-WAN Vendor

Key Takeaways

Cisco

    • Cisco Catalyst SD-WAN (formerly Viptela) and Cisco Meraki SD-WAN products include SD-WAN appliances, integrated security, and centralized management and orchestration

    • Cisco has a proven track record of aligning its SD-WAN feature roadmap with the ever-changing needs of enterprise customers

    • Catalyst and Meraki are different products with entirely separate management platforms, reducing scalability and versatility

Fortinet

    • Fortinet Secure SD-WAN includes physical and virtual NGFW appliances, multi-cloud on-ramp access, and centralized orchestration

    • Fortinet’s SD-WAN offering is extensible with the addition of AI-powered security bundles for a single-vendor SASE solution

    • Fortinet’s limited support for third-party integrations creates vendor lock-in and prevents companies from deploying a unified, multi-vendor SASE solution

HPE (Aruba)

    • HPE’s Aruba EdgeConnect SD-WAN and Aruba EdgeConnect SD-Branch products include physical and virtual appliances with centralized management and orchestration

    • Aruba SD-WAN offerings include performance optimization, cloud on-ramping, and enhanced operational capabilities

    • SD-WAN and SD-Branch offerings target different use cases, which could cause confusion, though both are managed by the same Aruba Central platform

Palo Alto Networks

    • Palo Alto Network’s Prisma SD-WAN includes Instant-On Network (ION) edge appliances and centralized orchestration, while the PAN-OS branch firewall can be upgraded with limited SD-WAN capabilities

    • Prisma provides robust SD-WAN features like cloud on-ramp access and autonomous digital experience management

    • Each product is managed separately and comes with limitations to either security or SD-WAN functionality

Versa Networks

    • Versa Networks offers the on-premises Secure SD-WAN and cloud-based Versa Titan products, which include physical or virtual appliances and centralized orchestration

    • Versa Networks offers a robust SD-WAN feature set, including strong routing and application steering, cloud on-ramping, and integrated security

    • Versa’s high price point and limited geographic presence make it unsuitable for customers in certain regions

VMware

    • VMware VeloCloud SD-WAN includes edge appliances, optional gateway points of presence (POPs), and a cloud-based orchestrator

    • VeloCloud SD-WAN integrates with VMware’s SASE platform as well as other products for cloud security and AIOps

    • VMware SD-WAN lacks native SD-Branch functionality and offers fewer integrated security features for the standalone SD-WAN product

Cisco

Cisco offers two different SD-WAN products: Cisco Catalyst SD-WAN (formerly Viptela), which targets enterprise customers, and Cisco Meraki SD-WAN, which targets mid-size organizations with lean IT operations. Each product is an entirely separate offering managed by different software platforms, making it difficult for a customer to mix-and-match products to adapt to new use cases or start with Meraki and then scale up to Catalyst during an aggressive growth period.

Catalyst SD-WAN is an advanced solution with integrated security, support for cloud on-ramp access, and integrations with ThousandEyes for monitoring and analytics as well as Cisco SSE products for a single-vendor SASE solution. Meraki SD-WAN is a more streamlined option, offering unified management of Meraki infrastructure with integrated security, zero-touch provisioning, and support for machine learning analytics.

Cisco SD-WAN - Pro's
  • Catalyst SD-WAN offers advanced features like multi-cloud on-ramp access and SSE integrations
  • Meraki SD-WAN provides a more streamlined experience with features like zero-touch provisioning to simplify lean IT operations
  • Cisco’s SD-WAN feature roadmap typically aligns with the current and future needs of enterprise customers
  • Cisco SD-WAN - Con's
    • Catalyst and Meraki are separate products with different management platforms, making it more challenging to use both
    • Based on Gartner’s reported client interactions, Cisco’s customer experience rating is lower than other vendors in this category
    • Fortinet

      Fortinet’s Secure SD-WAN solutions run on FortiGate physical and virtual NGFW (next-generation firewall) appliances, tightly integrating networking and security in a consolidated platform. In addition to a centralized orchestrator, Fortinet SD-WAN includes zero-touch provisioning and multi-cloud on-ramp access. It also enables single-vendor SASE with the addition of optional, AI-powered security bundles. However, Fortinet’s limited third-party integrations create vendor lock-in and prevent customers from building a unified, customized, multi-vendor SASE solution.

      Fortinet SD-WAN - Pro's
      • Fortinet combines SD-WAN functionality with NGFW appliances for a tightly integrated, consolidated experience
      • Fortinet offers zero-touch provisioning and multi-cloud on-ramp access to further streamline SD-WAN operations
      • Fortinet enables single-vendor SASE with options for AI-powered security bundles
      • Fortineet SD-WAN - Con's
        • Fortinet has limited integrations with third-party SSE vendors, preventing customers from unifying their multi-vendor SASE deployment
        • Gartner reports that Fortinet’s customer experience rating is below average compared to other SD-WAN vendors in the Magic Quadrant
        • HPE (Aruba)

          HPE (Aruba) has two SD-WAN offerings: EdgeConnect SD-WAN, which is a standalone SD-WAN product, and EdgeConnect SD-Branch, which builds upon the SD-WAN platform by adding software-defined management for wired and wireless branch LANs. Both products run on physical and virtual NGFW appliances for integrated security functionality, and both are managed by the same central orchestrator. Additional features include multi-cloud on-ramp access, unified management of Aruba networking solutions, and integrations with Aruba SSE products for single-vendor SASE.

          It’s notable that HPE (Aruba) is one of only two vendors named as Gartner SD-WAN leaders for all six years of the SD-WAN Magic Quadrant’s existence – the other is VMware.

          HPE (Aruba) SD-WAN - Pro's
          • Aruba offers two tightly integrated products combining SD-WAN and NGFW functionality for converged networking
          • Aruba’s SD-Branch solution extends software-defined control and zero-trust security to wired and wireless branch LANs
          • Aruba’s products include multi-cloud on-ramp access and integrations with Aruba SSE for single-vendor SASE
          • HPE (Aruba) SD-WAN - Con's
            • Aruba’s two different SD-WAN offerings may confuse customers who are unfamiliar with SD-Branch technology
            • Gartner noted that Aruba’s geographic strategy lacked details, so it may not reach customers in all locations
            • Palo Alto Networks

              Palo Alto Networks offers a dedicated SD-WAN product called Prisma SD-WAN, as well as an SD-WAN upgrade for its PAN-OS branch NGFW solution.

              Prisma SD-WAN is part of Palo Alto’s Prisma SASE platform, which was one of the industry’s first complete, single-vendor SASE solutions. The SD-WAN component uses Palo Alto’s Instant-On Network (ION) edge appliances that include integrated, cloud-delivered security, AIOps, SD-Branch, cloud on-ramp access, and autonomous digital experience management (ADEM).

              Palo Alto’s SD-WAN plugin integrates with PAN-OS branch firewalls to provide an SD-WAN overlay with centralized orchestration. It uses separate management software (called Panorama) from the Prisma platform. Essentially, each SD-WAN product targets different use cases and has different limitations. Prisma offers more advanced SD-WAN functionality but weaker on-premises security features (though this can be addressed by hosting Prisma on hardened third-party devices), whereas the PAN-OS platform offers strong branch security features but a more basic SD-WAN overlay.

              Palo Alto Networks SD-WAN Pros
              • Prisma SD-WAN offers advanced features like cloud-delivered security, AIOps, SD-Branch, cloud on-ramp access, and ADEM
              • Palo Alto’s SD-WAN plugin for PAN-OS provides a simpler upgrade path for existing NGFW customers
              • Based on Gartner’s reporting client interactions and Peer Insights data, Palo Alto has an above-average customer experience rating
              • Palo Alto Networks SD-WAN Cons
                • Palo Alto customers must choose between robust SD-WAN with limited branch security or advanced on-premises security functionality with limited SD-WAN
                • Gartner clients reported that Palo Alto Prisma SD-WAN has higher pricing compared to other vendors
                • Versa Networks

                  Versa Networks provides two SD-WAN options, Versa Secure SD-WAN and Versa Titan, which are entirely separate platforms with different orchestrators. Versa Secure SD-WAN offers a fully-featured SD-WAN overlay including advanced features such as multi-cloud on-ramp access, AIOps, a wide range of integrated security functionality like CASB and NGFW, and automated zero-touch provisioning.

                  Versa Titan is a cloud-managed, single-vendor SASE platform for leaner IT operations, providing a basic SD-WAN overlay that’s tightly integrated with cloud-based security features. Titan is an entirely separate product offering and platform targeting an entirely different use case. It offers a more streamlined experience, and it’s more affordable than Versa Secure SD-WAN, according to Gartner analyst assessment and Peer Insights data.

                  Versa Networks SD-WAN Pros
                  • Versa Secure SD-WAN is packed with advanced networking and security features like multi-cloud on-ramp access, AIOps, integrated security, and application steering
                  • Versa Titan offers a streamlined, unified SASE platform with a basic SD-WAN overlay for lean IT operations
                  • Gartner is optimistic about Versa Networks’ product roadmap and ability to meet changing customer requirements
                  • Versa Networks SD-WAN Cons
                    • Based on information from Gartner analysts and Peer Insights data, Versa Secure SD-WAN has a higher-then-average price point in the industry
                    • Versa Networks lacks a strong global presence and may not reach customers in all regions or countries
                    • VMware

                      VMware offers the VeloCloud SD-WAN product, which includes edge networking appliances (physical and virtual), optional gateway points of presence (POPs), and a centralized, cloud-based orchestrator. The VMware Edge Cloud Orchestrator software also integrates with other VMware products like VeloCloud Web Security and the VMware Edge Intelligence AIOps platform. VMware’s SD-WAN offering is also part of VMware’s VeloCloud SASE solution, which uses security functionality from Symantec (owned by Broadcom, the same parent company as VMware).

                      However, the VeloCloud SD-WAN product itself lacks many of the advanced features natively available in competing solutions, such as integrated security and SD-Branch. Despite these limitations, VMware is the only other vendor besides HPE (Aruba) to achieve Gartner SD-WAN leader status for six consecutive years.

                      VMware SD-WAN Pros
                      • VMware VeloCloud SD-WAN includes optional features like gateway POPs and integrations with other VMware products for security and AIOps
                      • VeloCloud SD-WAN is part of VMware’s VeloCloud SASE solution that uses Symantec security features to deliver unified SASE
                      • VMware has a strong customer experience rating based on Gartner client interactions and Peer Insights data
                      • VMware SD-WAN Cons
                        • VMware VeloCloud SD-WAN lacks many of the advanced features natively offered by competing vendors, such as multi-cloud on-ramp access and SD-Branch
                        • The standalone VeloCloud SD-WAN product has limited integrated security functionality unless expanded with additional services
                        • A peek into the future of SD-WAN

                          Gartner’s SD-WAN Magic Quadrant predicted that by 2026, 60% of new SD-WAN purchases will be part of a single-vendor SASE solution, an increase of 45% from 2023. However, extensibility and vendor choice still factored into Gartner’s ratings of current SD-WAN leaders. Closed ecosystems with limited integrations prevent organizations from adapting to new use cases and changing requirements with the speed and agility needed to stay competitive.

                          Companies can avoid vendor lock-in by deploying vendor-neutral edge infrastructure that supports third-party SD-WAN and SASE solutions. For example, the Nodegrid platform from ZPE Systems provides powerful, consolidated branch networking functionality that integrates (or even directly runs) other vendors’ software for SD-WAN, security, AIOps, and more. Plus, Nodegrid provides out-of-band (OOB) management to ensure 24/7 remote management access and network resilience.

                          Deploy SD-WAN leaders with Nodegrid

                          Nodegrid provides a powerful, vendor-neutral foundation to simplify SD-WAN deployment and enable unlimited extensibility, future-proofing branch network operations. Request a free Nodegrid demo to see how it works with your chosen SD-WAN solution.
                          Get a Demo

                          Opengear ACM7000 Resilience Gateway Alternative Options

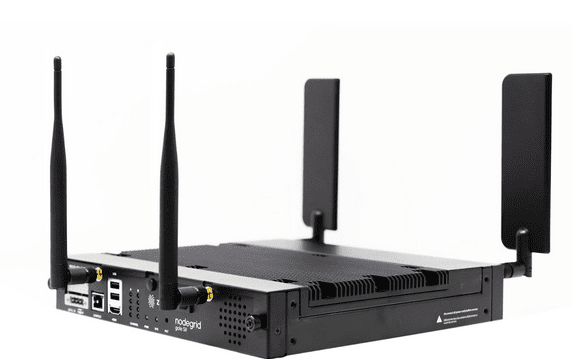
                          An angled view of the Nodegrid Gate SR, which is an alternative to the Opengear Resilience Gateway.
                          The Opengear ACM7000 Resilience Gateway provides gateway routing and out-of-band (OOB) management for small IT deployments in branch and edge locations. As the name implies, the ACM7000 improves network resilience by helping organizations maintain network uptime and deliver core business services without interruption. However, as a second-generation, or Gen 2, device, the ACM7000 lacks certain features that prevent it from being a complete resilience solution. This blog provides more information about the Opengear ACM7000 Resilience Gateway and its limitations before discussing alternative options from ZPE Systems that cover these gaps for greater resilience and control.

                          Executive summary:

                          • The Opengear ACM7000 Resilience Gateway offers branch gateway routing and out-of-band management access, along with some automation capabilities for individual tasks and workflows.
                          • As a Gen 2 solution, the ACM7000 has limited third-party integrations, so your automation capabilities are restricted to built-in playbooks and add-on NetOps modules, with Zero Touch Provisioning locked behind a Lighthouse account upgrade. 
                          • The ACM7000 also can’t run third-party software for additional edge networking and resilience solutions like AI/machine learning, next-generation firewalls (NGFWs), and Secure Access Service Edge (SASE). 
                          • The Nodegrid Services Router (SR) product line from ZPE Systems addresses many of these limitations with Gen 3 OOB on a vendor-neutral platform.
                          • Nodegrid’s modern, open-architecture Linux kernel supports virtualization and containers to directly host third-party software for automation, monitoring, security, recovery, and more. 
                          • Nodegrid’s centralized management software is available as an on-premises or cloud-based, as-a-service solution, and it’s easily extensible with third-party solutions to provide consolidated, 360-degree control, visibility, and resilience.

                          Opengear ACM7000 Key Features

                          Nodegrid Services Routers Key Features

                          • Gen 2 out-of-band management

                          • Centralized management through on-premises Lighthouse software

                          • Integrations with Nagios NSCA & NRPE

                          • Failover to embedded 4G LTE cellular modem

                          • Built-in automation for monitoring, detection, and recovery from equipment faults

                          • Additional automation capabilities require Lighthouse account upgrades or NetOps modules

                          • Gen 3 out-of-band supporting 3rd party automation and orchestration over OOB

                          • Centralized, vendor-neutral management through ZPE Cloud and Nodegrid Manager solutions

                          • Extensible applications with virtualization and containers

                          • Modular devices that are adaptable to any use case

                          • Integrations with your choice of 3rd party monitoring, security, automation, and more

                          • Failover to 5G/4G/LTE and Wi-Fi

                          • Zero Touch Provisioning (ZTP) for fast and easy remote setup

                          • Power control and monitoring to get alerts on device health and solve problems automatically

                          • Automation support via Puppet, Ansible, RESTful, and more

                          Why replace the Opengear ACM7000 Resilience Gateway?

                          The Opengear ACM7000 Resilience Gateway combines branch gateway routing features with serial console out-of-band (OOB) management, consolidating networking and remote management functionality in a single device.Opengear’s Smart OOBTM allows the creation of a dedicated control plane with isolated management infrastructure (IMI). This OOB solution supports automation via scripts and add-on NetOps modules, but Zero Touch Provisioning (ZTP) and automation over IP-based management interfaces require an upgraded “Automation” edition of Opengear’s Lighthouse management software.

                          Opengear ACM7000 Resilience Gateway alternative options

                          ZPE Systems offers a full suite of vendor-neutral branch and edge networking solutions that serve as direct replacements for – or alternatives to – the ACM7000. Nodegrid Services Routers, or SRs, are all-in-one devices delivering Gen 3 OOB management, 5G/4G cellular failover, branch gateway routing and networking, virtualization and container hosting, and edge computing capabilities. Nodegrid’s open, x86-64bit Linux-based Nodegrid OS allows easy integrations with third-party automation and orchestration software like Ansible, Puppet, and RESTful APIs. Nodegrid can even extend ZTP and other automation capabilities to legacy and mixed-vendor end devices over the out-of-band connection. Nodegrid also supports Guest OS and containers, so you can host everything needed to manage, troubleshoot, and recover remote deployments on the OOB network. Nodegrid provides the perfect foundation for a resilience system that enables companies to continue delivering core services during ransomware attacks, network outages, and other adverse events. Nodegrid’s extensible, open platform streamlines branch management, scaling, and resilience.

                          Comparing Nodegrid replacement options for the ACM7000 Resilience Gateway

                          Nodegrid Link SR

                          Nodegrid Bold SR

                          Nodegrid Hive SR

                          Nodegrid Gate SR

                          Nodegrid Net SR

                          Nodegrid Mini SR

                          Potential Use Cases

                          Branch, IoT, and M2M (Machine-to-Machine) deployments

                          Branch and edge deployments like telecom, retail, and oil & gas

                          Distributed branch and edge sites like manufacturing plants 

                          uCPE (universal customer premises equipment) and branch service delivery

                          Edge data centers, large branch deployments

                          Edge IoT, OT, and IoMD (Internet of Medical Devices) deployments

                          CPU

                          x86-64bit Intel Processor

                          x86-64bit Intel Processor

                          x86-64bit Intel Processor

                          x86-64bit Intel Processor

                          x86-64bit Intel Processor

                          x86-64bit Intel Processor

                          Guest OS

                          1

                          1

                          1-2

                          1-3

                          1-6

                          1

                          Docker Apps

                          1-2

                          1-2

                          1-3

                          1-4

                          1-4

                          1-2

                          Storage

                          16GB - 128GB

                          32GB - 128GB

                          16GB - 128GB

                          32GB - 128GB

                          32GB - 128GB

                          16GB SED

                          Secondary Additional Storage

                          Up to 4TB

                          Up to 4TB

                          Up to 4TB

                          Up to 4TB

                          Up to 4TB

                          -

                          PoE+ Output

                          -

                          -

                          -

                          Yes

                          Yes

                          -

                          Wi-Fi

                          Yes

                          Yes

                          Yes

                          Yes

                          Yes

                          Yes

                          ZPE Cloud Support

                          Yes

                          Yes

                          Yes

                          Yes

                          Yes

                          Yes

                          Cellular (Dual-SIM)

                          1

                          1-2

                          1-2

                          1-2

                          1-4

                          1

                          Serial

                          1

                          8

                          8

                          8

                          16-80

                          Via USB

                          Network

                          1 x Gb ETH 1 x SFP

                          5 x Gb ETH

                          2x GbE ETH, 2x 10 Gbps, 4x 10/100/1000/2.5 Gbps RJ-45

                          2 x SFP+, 5 x Gb ETH, 4 x 1Gb ETH PoE+

                          2 1Gb ETH, 2 SFP+, Multiple Cards

                          2 x 1Gb ETH

                          GPIO

                          2 DIO, 2 OUT

                          -

                          -

                          2 DIO, 1 OUT, 1 Relay

                          -

                          -

                          Power

                          Single

                          Single

                          Single

                          Single or Redundant

                          Single or Redundant

                          Single

                          Data Sheet

                          Download

                          Download

                          Download

                          Download

                          Download

                          Download

                          Improve branch resilience and efficiency with Nodegrid

                          Nodegrid Services Routers address the limitations of the Opengear ACM7000 Resilience Gateways with a vendor-neutral platform that enables unlimited automation over a Gen 3 out-of-band management connection for ultimate network resilience. Get a free demo to see a Nodegrid SR in action. Get a Demo

                          Opengear ACM7000 Resilience Gateway replacement SKUs

                          The following table provides a list of ZPE’s Nodegrid SR product SKUs that serve as the best direct replacements for the corresponding Opengear ACM7000 products. Depending on your specific requirements, you may find that other Nodegrid products work better for your use case. Contact ZPE Systems for more assistance finding alternative solutions.

                          ACM7000 Product SKUs

                          Nodegrid Replacement Product SKUs

                          ACM7004-2-L


                          4 serial Cisco Straight pinout, ext power, dual 1 GbE ETH, Global 4G LTE-A Pro cellular

                          ZPE-BSR-24-4G


                          ZPE Nodegrid Bold SR. 8 RJ45 serial rolled, ext power, 5 GbE ETH including 4 GbE switch, dual sim 4G LTE (CAT12), 2 USB 3.0, 2 USB 2.0

                          ACM7004-2-LMP


                          4 serial Cisco Straight pinout, ext power, dual 1 GbE ETH, 4G LTE-A Pro cellular

                          ZPE-BSR-24-4G


                          ZPE Nodegrid Bold SR. 8 RJ45 serial rolled, ext power, 5 GbE ETH including 4 GbE switch, dual sim 4G LTE (CAT12), 2 USB 3.0, 2 USB 2.0

                          ACM7004-5-L


                          4 serial Cisco Straight pinout, ext power, dual 1 GbE ETH or fiber SFP, 4 GbE switch, dual SIM Global 4G LTE-A Pro cellular

                          ZPE-GSR-48-4G


                          ZPE Nodegrid Gate SR. 8 RJ45 serial rolled, dual ext power, 5 GbE ETH including 4 GbE switch, 2 fiber SFP, 4 PoE+ GbE ETH including switch, dual sim 4G LTE (CAT12), 2 USB 3.0, 2 USB 2.0


                          ZPE-GSR-48-5G


                          ZPE Nodegrid Gate SR. 8 RJ45 serial rolled, dual ext power, 5 GbE ETH including 4 GbE switch, 2 fiber SFP, 4 PoE+ GbE ETH including switch, 5G LTE (Sub 6 with 4G/LTE CAT20), 2 USB 3.0, 2 USB 2.0

                          ACM7004-5-LMP


                          4 serial Cisco Straight pinout, ext power, dual 1 GbE ETH or fiber SFP, 4 GbE switch, dual SIM 4G LTE-A Pro cellular

                          ZPE-GSR-48-4G


                          ZPE Nodegrid Gate SR. 8 RJ45 serial rolled, dual ext power, 5 GbE ETH including 4 GbE switch, 2 fiber SFP, 4 PoE+ GbE ETH including switch, dual sim 4G LTE (CAT12), 2 USB 3.0, 2 USB 2.0


                          ZPE-GSR-48-5G


                          ZPE Nodegrid Gate SR. 8 RJ45 serial rolled, dual ext power, 5 GbE ETH including 4 GbE switch, 2 fiber SFP, 4 PoE+ GbE ETH including switch, 5G LTE (Sub 6 with 4G/LTE CAT20), 2 USB 3.0, 2 USB 2.0

                          ACM7004-2


                          4 serial Cisco Straight pinout, ext power, dual 1 GbE ETH, 4 USB console

                          ZPE-BSR-24-Base


                          ZPE Nodegrid Bold SR. 8 RJ45 serial rolled, ext power, 5 GbE ETH including 4 GbE switch, dual sim 4G LTE (CAT12), 2 USB 3.0, 2 USB 2.0

                          ACM7004-5


                          4 serial Cisco Straight pinout, ext power, dual 1 GbE ETH or fiber SFP, 4 GbE switch

                          ZPE-BSR-24-Base


                          ZPE Nodegrid Bold SR. 8 RJ45 serial rolled, ext power, 5 GbE ETH including 4 GbE switch, dual sim 4G LTE (CAT12), 2 USB 3.0, 2 USB 2.0


                          ZPE-GSR-48-Base


                          ZPE Nodegrid Gate SR. 8 RJ45 serial rolled, dual ext power, 5 GbE ETH including 4 GbE switch, 2 fiber SFP, 4 PoE+ GbE ETH including switch, 2 USB 3.0, 2 USB 2.0

                          ACM7008-2-L


                          8 serial Cisco Straight pinout, ext power, dual 1 GbE ETH, Global 4G LTE-A Pro cellular

                          ZPE-BSR-24-4G


                          ZPE Nodegrid Bold SR. 8 RJ45 serial rolled, ext power, 5 GbE ETH including 4 GbE switch, dual sim 4G LTE (CAT12), 2 USB 3.0, 2 USB 2.0

                          ACM7008-2-LMP


                          8 serial Cisco Straight pinout, ext power, dual 1 GbE ETH, dual sim 4G LTE-A Pro cellular

                          ZPE-BSR-24-4G


                          ZPE Nodegrid Bold SR. 8 RJ45 serial rolled, ext power, 5 GbE ETH including 4 GbE switch, dual sim 4G LTE (CAT12), 2 USB 3.0, 2 USB 2.0

                          ACM7008-2


                          8 serial Cisco Straight pinout, ext power, dual 1 GbE ETH, 4 USB console

                          ZPE-BSR-24-Base


                          ZPE Nodegrid Bold SR. 8 RJ45 serial rolled, ext power, 5 GbE ETH including 4 GbE switch, dual sim 4G LTE (CAT12), 2 USB 3.0, 2 USB 2.0

                          Network Resilience vs Redundancy vs Backups

                          Network Resilience vs Redundancy vs Backups
                          Network resilience is an organization’s ability to continue delivering critical business services during adverse events, service degradation, and complete outages. Resilience is vitally important to a company’s revenue and reputation, and failure has serious consequences. For example, a popular file transfer appliance was recently hit with CL0P ransomware, resulting in the theft of more than 4 million healthcare patients’ sensitive data. SolarWinds’ high-profile breach resulted in legal action from the SEC due to a potential lack of resilience infrastructure and practices.

                          Many organizations already use redundant and backup systems for disaster recovery and assume this makes them resilient. However, these measures aren’t able to withstand many major events like ransomware attacks, supply chain failures, and WAN outages. This article compares network resilience vs. redundancy and backups and describes some of the tools and best practices for ensuring resilience.

                          Network resilience vs. redundancy vs. backups

                          Backups

                          Copies of data, configurations, and application code used in a hot or cold restore of a failed production system.

                          Redundancy

                          The duplication of critical systems, services, and applications so organizations can “failover” during an outage.

                          Network Resilience

                          The ability to continue delivering critical business services during adverse events, service degradation, and complete outages.

                          What are backups?

                          Backups are extra copies of critical data, configurations, and application code that are made in case the originals are lost or compromised. Backups are usually stored off-site so that they’ll be available if the primary data center or business location suffers an outage. The backup site communicates with the primary systems to download data on a scheduled or continuous basis to maintain a secondary copy of data at its most current state. This connection, while necessary, also allows ransomware and other malware to infect backups, which limits their usefulness in recovery operations. Additionally, if that connection is interrupted by an outage or configuration error, backups may be incomplete or inaccessible.

                          What is redundancy?

                          Redundancy involves duplicating the most critical systems, services, and applications so organizations can “failover” to them if the primary systems go down or become inaccessible. Typically, a company will have redundant systems in one or more disaster recovery sites in different locations to prevent a regional ISP outage or weather event from affecting them all at the same time. If one site goes down, teams reroute traffic to a redundant site to continue delivering services. However, each redundant site is susceptible to the same risks as the primary site, and cybercriminals and malware could potentially jump from one site to another.

                          What is network resilience?

                          Network resilience is the ability to continue operating and delivering core services – if in a degraded state – during adverse events. Backups and redundancy contribute to resilience, but there are additional pieces to the puzzle. Teams also need the ability to recover data, rebuild systems, and perform security testing without worrying about ransomware reinfection or access disruption. Additionally, organizations must be able to protect management interfaces from cybercriminals on the network, or they could become completely cut off from vital systems and services.

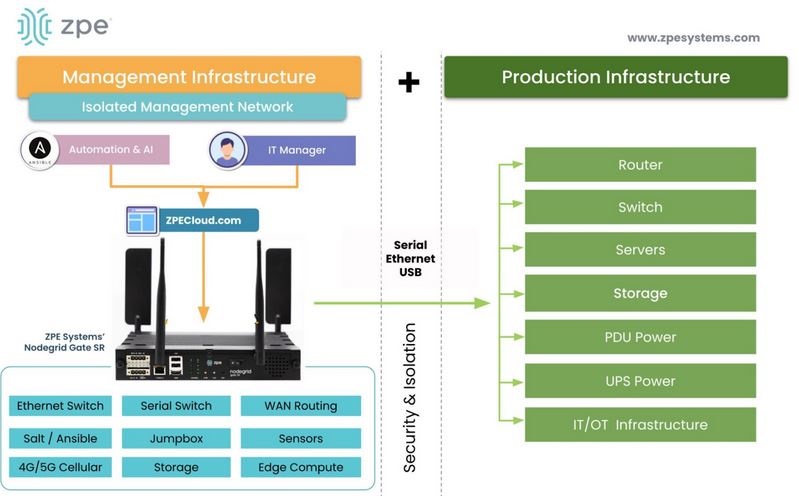
                          The best way to improve resilience is by building a resilience system containing all the infrastructure, tools, and services needed to continue delivering services and recover failed or compromised systems. It must be isolated from the production network using isolated management infrastructure (IMI) to prevent malicious actors from compromising it and ensure teams have continuous remote access even if the primary network goes down.

                          Read more about ransomware resilience with IMI:

                          Resilience systems use the following tools, technologies, and best practices to provide network resilience.


                          Network Resilience Tools, Technologies, and Best Practices

                          Alternative Networking

                          Routing, switching, Wi-Fi, VoIP, virtualization, and software-defined network overlays for SDN & SD-WAN

                          Alternative Compute

                          CPU/GPU compute, containers, virtual machines, and any other resources needed to run applications and deliver services during an outage

                          Storage & Storage Recovery

                          Enough storage to recover systems and applications, rebuild new systems, and support content delivery

                          Automation

                          Tools like zero-touch provisioning (ZTP) to facilitate speedy recovery while minimizing human error

                          Out-of-Band (OOB) Management

                          A separate, isolated management plane that ensures continuous remote access to troubleshoot and recover infrastructure during production network outages and attacks

                          Redundancy and backups are crucial for disaster recovery and contribute to your ability to continue operating during adverse events. But, because these rely on the underlying infrastructure, achieving network resilience requires a more comprehensive strategy. A resilience system using IMI allows you to continuously deliver critical services and provides teams with everything they need to safely recover.
                          A diagram showing how to use ZPE to follow Gartner’s best practices for an isolated management infrastructure.
                          The Nodegrid platform from ZPE Systems streamlines network resilience by providing a vendor-neutral foundation for a resilience system. Nodegrid’s out-of-band management solutions enable redundancy while creating an isolated management plane capable of running your choice of third-party tools for troubleshooting, recovery, security validation, and more. You can even use Nodegrid’s powerful x86 compute architecture to host and deliver services while your primary systems are down.

                          Download the Blueprint for Network Resilience

                          Want to see how these principles fit together? Download the Network Resilience Blueprint to learn a practical framework for designing an infrastructure that’s easy to manage and quick to recover.

                          The Network Resilience Blueprint

                          The Future of Edge Computing

                          The Future of Edge Computing
                          Edge computing moves computing resources and data processing applications out of the centralized data center or cloud, deploying them at the edges of the network and allowing companies to use their edge data in real-time. An explosion in edge data generated by Internet of Things (IoT) sensors, automated operational technology (OT), and other remote devices has created a high demand for edge computing solutions. A recent report from Grand View Research valued the edge computing market size at $16.45 billion in 2023 and predicted it to grow at a compound annual growth rate (CAGR) of 37.9% by 2030.

                          The current edge computing landscape comprises solutions focused on individual use cases,  lacking interoperability and central orchestration. The future of edge computing, as described by leading analysts at Gartner, depends on unifying the edge computing ecosystem with comprehensive strategies and centralized, vendor-neutral management and orchestration. This future relies on edge-native applications that integrate seamlessly with upstream resources, remote management, and orchestration while still being able to operate independently.

                          Where is edge computing now?

                          Many organizations already use edge computing technology to solve individual problems or handle specific workloads. For example, a manufacturing department may deploy an edge computing application to analyze log data and provide predictive maintenance recommendations for a single type of machine or assembly line. A single company may have a dozen or more disjointed edge computing solutions in use throughout the network, creating visibility and management headaches for IT teams. This piecemeal approach to edge computing results in what Gartner calls “edge sprawl”: many disparate solutions deployed without centralized control, security, or visibility. Edge sprawl increases management complexity and risk while decreasing operational efficiency, creating significant roadblocks for digital transformation initiatives.

                          Additionally, many organizations misunderstand edge computing by thinking it’s just about moving computing resources as close to the edge as possible to collect data. In reality, the true potential of the edge involves using edge data in real-time, gaining “cloud-in-a-box” capability that works in concert with the network’s upstream resources.

                          Anticipating the future of edge computing

                          At Gartner’s 2023 IT Infrastructure Operations & Cloud Strategies Conference, edge technology experts predicted that, by 2025, enterprises will create and process more than 50% of their data outside the centralized data center or cloud. Surging edge data volume will accelerate the challenges caused by a lack of strategy or orchestration.

                          Gartner’s 6 Edge Computing Challenges

                          Lack of extensibility

                          Many purpose-built edge computing solutions can’t adapt as use cases change or expand as the business scales, limiting agility and preventing efficient growth.

                          Inability to extract value from edge data

                          Much of the valuable data generated by edge sensors and devices gets left on the table, so to speak, because companies lack the resources needed to run all their data analytics and AI apps at the edge and are stuck simply collecting data rather than being able to do much with it.

                          Data storage constraints

                          Edge computing deployments are often smaller and have more data storage constraints than large data centers and cloud deployments, but quickly distinguishing between valuable data and destroyable junk is difficult with edge resources.

                          Knowledge debt from edge-native apps

                          Edge-native applications are designed for edge computing architectures from the ground up. Edge containers are similar to cloud-native apps, but clustering and cluster management work much differently, creating what’s known as “knowledge debt” and straining IT teams.

                          Lack of security controls, policies, & visibility

                          Edge deployments often lack many of the security features used in data centers, and sometimes other departments install edge computing solutions without onboarding them with IT for the application of security policies and monitoring agents, adding risk and increasing the attack surface.

                          Inability to remotely orchestrate, monitor, & troubleshoot

                          When equipment failures, configuration errors, or breaches take down edge networks, remote teams are often cut-off and unable to troubleshoot or recover without traveling on-site or paying for managed services, increasing the duration and cost of the outage. Current edge solutions are novel and don’t connect to or integrate with the full networking stack.

                          At the Gartner conference, analyst Thomas Bittman gave multiple presentations echoing his advice from the Building an Edge Computing Strategy report published earlier in the year. In preparing for the future of edge computing, Bittman urges companies to proactively develop a comprehensive edge computing strategy encompassing all potential use cases and addressing the challenges described above. His recommendations include:

                          • Enabling extensibility by utilizing vendor-neutral platforms that allow for expansion and integration, which supports growth and agility at the edge.
                          • Looking for opportunities to deploy artificial intelligence, data analytics, and machine learning alongside edge computing units, for example, with system-on-chip technology or all-in-one edge networking and computing devices.
                          • Anticipating data storage and governance challenges at the edge by defining clear policies and deploying AI/ML data management solutions that dynamically determine data value.
                          • Reducing knowledge debt by utilizing vendor-neutral platforms that support familiar container and cluster management technologies (like Docker and Kubernetes).
                          • Securing the edge with a multi-layered defense, including hardware security, frequent patches, zero-trust policies, strong authentication, network micro-segmentation, and comprehensive security monitoring.
                          • Centralizing edge management and orchestration (EMO) with a vendor-neutral platform that unifies control, supports environmental monitoring, and uses out-of-band (OOB) management while interoperating with automated edge management workflows (such as zero-touch provisioning and infrastructure configuration management).

                          Bittman’s recommended edge computing strategy uses the central EMO as a hub for all the technologies, processes, and workflows involved in operating and supporting the edge. This strategy will prepare companies for the future of edge computing and support efficient, agile growth and innovation.

                          Enter the future of edge computing with Nodegrid

                          Nodegrid is a vendor-neutral edge management and orchestration platform from ZPE Systems. Nodegrid easily interoperates with your choice of edge solutions and can directly run third-party AI, ML, data analytics, and data governance applications to help you extract more value from your edge data. The open, Linux-based Nodegrid OS can also host Docker containers and edge-native applications to reduce hardware overhead and knowledge debt.

                          Nodegrid devices protect your edge management interfaces with hardware security features like TPM and geofencing, support for strong authentication like 2FA, and integrations with leading zero-trust providers like Okta and PING. The Nodegrid OS and ZPE Cloud are Synopsys-validated to address security at every stage of the SDLC. Plus, you can run third-party security solutions for SASE, next-generation firewalls, and more.

                          Nodegrid edge networking solutions use out-of-band technology to give teams 24/7 remote visibility, management, and troubleshooting access to edge deployments. It freely interoperates with third-party solutions for infrastructure automation, monitoring, and recovery to support network resilience and operational efficiency. Nodegrid is like a cloud-in-a-box solution, incorporating edge computing and the full networking stack. Nodegrid’s edge management and orchestration platform provides single-pane-of-glass visibility, control, and resilience while supporting future edge growth.

                          Use Nodegrid for your Gartner-approved edge computing strategy

                          The Nodegrid EMO platform helps you anticipate the future of edge computing with vendor-neutral, single-pane-of-glass visibility and control. Watch a free Nodegrid demo to learn more.

                          Request a Demo

                          Distributed Edge Computing Use Cases

                          An industrial worker selecting an illustration of distributed edge computing concepts surrounding the word edge computing
                          Across every industry, networks are decentralizing as organizations expand with remote business sites, Internet of Things (IoT) deployments, and mobile technologies. Distributed edge computing involves moving data processing systems and applications out of the centralized cloud or data center and distributing them around the network’s edges, where much of the data is generated. As defined by The Open Glossary of Edge Computing, edge native computing integrates with centralized cloud computing resources, local workloads, remote management, and orchestration while having the ability to operate independently.

                          Edge computing supports secure, real-time data analysis by reducing off-site data transmission. Edge native computing also enables the transition to digital transformation 2.0 by allowing companies to do something with their edge data in real-time, not just collect it. This post discusses six different use cases that could benefit from distributed edge computing, including healthcare, finance, energy, manufacturing, utilities/public services, and AI & machine learning.

                          Jump to the executive summary.

                          Distributed edge computing use cases

                          Use cases for distributed edge computing include:

                          Healthcare

                          • Mitigate security, privacy, and compliance concerns with local data processing, AI, and Zero Touch Provisioned Virtual Network Functions

                          • Improve patient health outcomes with real-time alerts that don’t require Internet access

                          • Enable emergency mobile medical intervention while reducing mistakes

                          Finance

                          • Support distributed financial networks while reducing security and regulatory risks by managing scope through isolation and built-in change management.

                          • Get fast, localized business insights to improve revenue and customer service

                          • Deploy AI-powered surveillance and security solutions without network bottlenecks

                          Energy

                          • Enable real-time data processing and ensure network access for air-gapped and isolated environments with IT and OT operations. without network access

                          • Improve efficiency with predictive maintenance recommendations and other insights

                          • Proactively identify and remediate safety, quality, and compliance issues

                          Manufacturing

                          • Get real-time, data-driven insights to improve manufacturing efficiency and product quality

                          • Reduce the risk of confidential production data falling into the wrong hands during transit

                          • Ensure continuous communications and operations during network outages and other adverse events

                          Utilities/Public Services

                          • Use IoT technology to deliver better services, improve public safety, and keep communities connected

                          • Reduce the fleet management challenges involved in difficult deployment environments

                          • Provide IT with reliable remote access to install critical security patches and maintain devices

                          • Aid in Disaster Recovery and resilience

                          AI & Machine Learning

                          • Get enhanced data analytics capabilities for any distributed edge computing use case

                          • Improve AI/ML efficiency by eliminating network bottlenecks and reducing security risks

                          • Use edge devices with a built-in networking stack to improve the agility, cost-effectiveness, and scalability of edge AI/ML

                          Migration from On Premises to Edge Computing

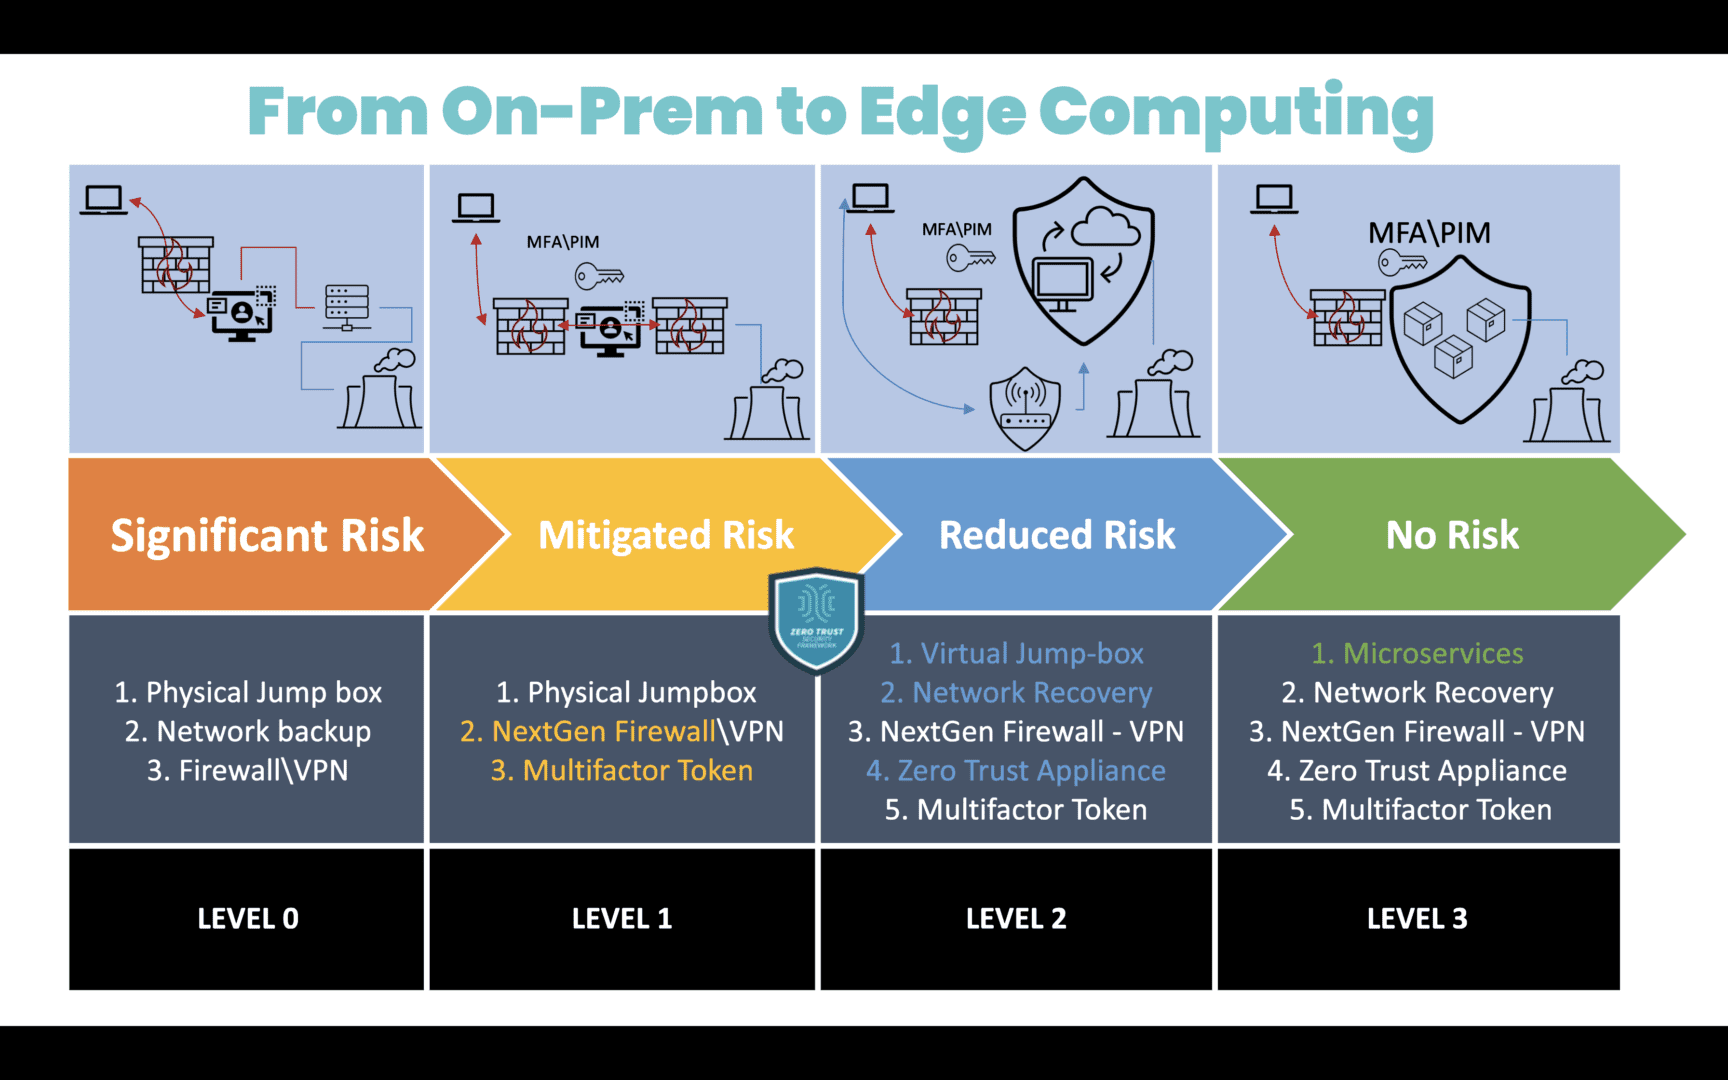
                          Image: Concrete use case that can work across all industries, showing the migration from on-prem computing to microservices at the edge, along with the associated level of security risk.

                          Healthcare

                          The healthcare industry quickly and enthusiastically adopted IoT technology for medical equipment like insulin pumps, pacemakers, and imaging devices to improve patient health monitoring and outcomes. These sensors generate massive quantities of data that healthcare organizations must transmit to applications in central data centers or the cloud for processing. This data can’t be transferred over the open Internet for security and compliance reasons, so it’s usually funneled through a central firewall via MPLS (for branches, clinics, and other physical sites), overlay networks, or SD-WAN (for wearable sensors and mobile EMS devices). The firewall becomes a bottleneck that increases latency and prevents real-time data processing, introducing potentially lethal delays in health monitoring and response.

                          Distributed edge computing for healthcare involves installing medical data processing applications closer to the sensors and devices generating most of the data. Edge computing occurs on the same local network or even the same onboard chip (using system-on-chip or SoC technology), which reduces security risks and latency. For example, software running on an implanted heart-rate monitor can analyze patient data in real time without a network connection. If it detects any concerning activity that falls outside of an established baseline, it uses multiple cellular and ATT FirstNet connections to send alerts to the cardiologist without exposing any private patient data. Even if the application can’t establish a network connection at all, the device itself can alert the patient that there’s a problem so they can take immediate action.

                          Another healthcare use case is mobile EMS units processing patient health data en route to the hospital using edge compute resources built into cellular edge routers. Edge native applications can help medics prevent allergic reactions and harmful medication interactions when administering treatment.

                          Finance

                          Finance industry networks are typically highly decentralized, using branches, web and mobile applications, and self-service ATMs to make their services accessible to customers around the world. Banks and other institutions know that edge data has value beyond the financial transactions being conducted, so they use data analytics software (often powered by AI & machine learning) to gain insights into how to improve their services and generate more revenue. However, there are enormous security, regulatory, and reputational risks involved in transmitting sensitive financial data, making it challenging to leverage cloud- or data center-based analytics software.

                          Distributed edge computing moves financial data processing applications to branches and 26remote PoPs (points of presence) to help mitigate the risks of transmitting data off-site. For example, financial institutions can install all-in-one branch gateway services routers with built-in edge compute functionality in networking closets, drive-up kiosks, or even inside an ATM’s housing. Running data analytics software from this device enables real-time data processing for business insights, surveillance, customer service improvements, and more. These routers should also include out-of-band (OOB) management technology to support infrastructure isolation and simplify compliance with PCI DSS 4.0 and other regulations.

                          Energy

                          Edge data in the oil and gas industry comes from IoT sensors and automated equipment deployed in remote sites, drilling rigs, and offshore platforms all over the world. Analyzing that data is crucial for productivity, safety, and compliance, but it’s often difficult to maintain a fast and reliable network connection with applications in data centers or the cloud.

                          Distributed edge computing allows oil and gas companies to effectively harness their data in challenging deployment environments, such as the middle of the ocean. For example, companies can tuck compact, cellular-enabled edge computing devices into maintenance closets or other small compartments to deploy software that analyzes equipment monitoring data, well logs, and borehole logs. This software can provide predictive maintenance recommendations, alert technicians to potential quality or safety issues, and deliver productivity forecasts and insights without requiring an Internet connection.

                          Manufacturing

                          Companies across nearly every industry are increasingly automating their manufacturing to improve productivity, lower costs, and reduce errors. To further reduce human involvement, they use software to monitor equipment health, track production costs, schedule preventative maintenance, and perform quality assurance (QA) tasks. This software, which typically runs from the cloud or a centralized data center, relies on data generated by automated operational technology (OT) and other manufacturing machinery. As in the above use cases, transmitting OT back and forth creates latency and security issues. There are additional risks associated with manufacturing operations located overseas, where political instability, disasters, and other external forces could interrupt communications.

                          Distributed edge computing enables real-time, data-driven insights to improve manufacturing efficiency and elevate product quality. Plus, some edge computing solutions, like the Nodegrid integrated branch services router, provide out-of-band (OOB) management access to remote equipment. OOB management creates a dedicated management network that’s completely isolated from the production network, ensuring continuous remote access to operational technology, monitoring systems, and edge native applications during Internet outages and other adverse events.

                          Utilities / public services

                          Many forward-thinking cities are deploying Internet of Things (IoT) devices to improve their utilities and public services and better connect their communities. These “smart cities” collect data from Internet-connected thermostats, parking meters, traffic lights, security cameras, and other devices deployed outdoors, in public facilities, and in citizens’ homes. However, local governments often find it challenging to keep up with fleet management, ensuring all these devices are connected, patched, and up-to-date to prevent breaches and failures.

                          Distributed edge computing reduces the networking and bandwidth requirements for IoT-enabled utilities, public services, and smart cities. Edge native applications can analyze data on the same sensor or device that generates it, reporting back to a centralized cloud or data center as needed to provide alerts, reports, and visualizations. All-in-one edge networking solutions combine connectivity with compute capabilities and are small enough to fit in utility cabinets, under public benches, or on top of street lights. They provide remote IT teams with easy access to monitor devices, deploy updates, and troubleshoot issues over a reliable, cellular OOB connection. An edge native networking solution should also enable automatic, zero-touch operations to streamline digital fleet management at scale.

                          AI & machine learning

                          Artificial intelligence (AI) and machine learning (ML) applications ingest data to train, operate, and make decisions. Much of that data originates at the network’s edges – in fact, there are AI & ML applications for every edge use case and industry listed above. Transmitting vast quantities of data to the cloud or a data center introduces network bottlenecks, latency, and security risks that can prevent organizations from getting the full value out of their AI investment.

                          Because artificial intelligence is very resource-hungry, edge native computing for AI/ML sometimes looks a little different than in other use cases. A typical edge computing deployment for AI & ML involves racks of high-performance machine learning processing units deployed in edge data centers on the same site as (or very nearby) the devices generating data. This approach works well for large machine-learning workloads occurring in a limited number of deployment sites. A more flexible approach involves using smaller graphics processing units (GPUs) or multi-purpose edge devices to handle individual AI/ML workloads in smaller and more distributed edge deployment sites. These “thin” or “nano” deployments are agile and cost-effective, scaling easily as organizations grow in size and geographic distribution.

                          Executive summary

                          • Distributed edge computing for healthcare improves patient health outcomes and data privacy with SoC applications on wearable medical devices and cellular edge routers in mobile EMS units.
                          • Distributed edge computing for the finance industry provides insights into how to improve services and revenue while helping to mitigate security and regulatory risks with on-site data processing and infrastructure isolation.
                          • Distributed edge computing helps the energy sector effectively harness critical data from sensors and equipment in challenging deployment environments to improve quality, safety, and productivity.
                          • Distributed edge computing for manufacturing helps companies process data from automated machinery and operational technology to improve manufacturing efficiency and elevate product quality.
                          • Distributed edge computing for utilities/public services reduces the networking and fleet management challenges for IoT-enabled utilities, public services, and smart cities with all-in-one edge networking solutions, OOB, and zero-touch operations.
                          • Distributed edge computing for AI & machine learning uses multi-purpose edge devices to handle individual workloads, improving the agility, scalability, and cost-effectiveness of edge AI/ML.

                          Distributed edge computing with Nodegrid

                          Nodegrid is a line of all-in-one edge networking solutions from ZPE Systems. Nodegrid’s vendor-neutral, integrated branch services routers combine edge gateway networking functionality with Gen 3 out-of-band management and edge computing capabilities. The Nodegrid platform streamlines distributed edge computing for any use case with consolidated hardware and software that reduce deployment costs and management headaches while improving efficiency.

                          See Nodegrid’s edge solutions in action

                          Nodegrid delivers streamlined, cost-effective solutions for distributed edge computing in healthcare, EMS, financial services, local governments, and more. To see how Nodegrid works for your edge computing use case, request a free demo.

                          Request a Demo

                          Edge Computing Ecosystem Design

                          A person in a suit taps a glowing edge computing ecosystem with many network connections and glowing icons of edge computing concepts
                          Edge computing allows companies with highly distributed networks to efficiently process data from remote devices like Internet of Things (IoT) sensors and automated industrial systems. Teams deploy computing resources and data handling applications closer to data sources at the network’s edges, eliminating transmission latency and preventing data from leaving the local security perimeter. The current edge computing ecosystem consists mainly of solutions designed around individual use cases that lack interoperability with each other or a centralized management platform. That means most organizations end up with a disjointed edge computing architecture without any organized strategy.

                          According to Gartner, companies that deploy edge computing non-strategically are less efficient and lack the agility and scalability to meet their digital transformation goals. This post discusses the challenges created by a fragmented edge computing market before providing edge computing ecosystem design best practices to overcome these hurdles.

                          Edge computing ecosystem challenges

                          Most edge computing vendors offer products designed around a single use case or workload, such as analyzing machine logs to provide predictive maintenance recommendations for a specialized robotic manufacturing arm. These solutions don’t interoperate with each other or integrate with centralized orchestration platforms from other vendors, so each one is managed independently, often by the individual departments that use them. This fragmented architecture creates three major problems that prevent organizations from operating securely and efficiently: shadow IT, edge sprawl, and a lack of edge resilience.

                          Edge Computing Ecosystem Challenges

                          Shadow IT

                          Shadow IT occurs when individual departments or users purchase technology solutions without the knowledge, approval, or support of IT. Shadow IT is dangerous because these solutions aren’t onboarded with security controls and monitoring tools, so they are vulnerable to cybercriminals. Organizations also might purchase edge computing solutions with overlapping capabilities without realizing it, needlessly increasing operational costs.

                          Edge Sprawl

                          Edge sprawl occurs when there are so many different edge computing solutions that an organization can’t effectively manage them all. Teams often struggle to stay on top of patch schedules, leaving vulnerabilities in edge devices critically exposed. They also lack the ability to monitor and optimize performance, reducing the efficiency of edge computing operations. 

                          Poor Resilience

                          Edge computing deployments typically lack the climate control, physical security, and technical oversight of centralized data centers, increasing the likelihood of environmental issues and limiting IT’s ability to respond to them. Complex edge deployments are also at high risk of human error, and network outages prevent remote teams from quickly troubleshooting and recovering.

                          Gartner’s best practices for overcoming these challenges is a vendor-neutral edge management and orchestration (EMO) platform that unifies edge computing solutions and gives teams a complete, 360-degree overview of edge operations. This EMO should use out-of-band (OOB) management technology to ensure 24/7 accessibility during production network outages and breaches. Additionally, the platform should integrate with edge automation solutions like zero-touch provisioning and AIOps to improve efficiency and reduce the risk of human error.
                          A diagram showing how to use ZPE to follow Gartner’s best practices for an isolated management infrastructure.
                          Additionally, exposed management interfaces represent a major threat to edge resilience because attackers who breach the network could take complete control over infrastructure and “crown jewels” assets. Gartner’s recommendation is to move management interfaces to an isolated management infrastructure (IMI) that’s completely separate from the production network. Download our blueprint to learn more.

                          Edge computing ecosystem design with Nodegrid

                          The Nodegrid solution from ZPE Systems helps organizations overcome their biggest edge computing challenges with a unified, vendor-neutral platform. With compact, all-in-one edge networking solutions like the Bold SR, you can consolidate your edge infrastructure for streamlined, cost-effective deployments. For challenging outdoor or mobile deployments, the Mini SR delivers networking, automation, and OOB in a smartphone-sized device that fits anywhere.

                          Nodegrid’s vendor-neutral, out-of-band management platform gives teams a lifeline to monitor, troubleshoot, and recover edge infrastructure during cyber attacks and outages, improving edge resilience and reducing business disruption. Plus, our environmental sensors provide crucial data about temperature, humidity, and other conditions so teams can proactively address issues before a failure occurs.

                          Nodegrid’s management platform, available as an on-premises or cloud-based application, unifies all your edge computing solutions under one roof. Teams can view monitoring dashboards, deploy patches, perform device maintenance, orchestrate automated workflows, and more from one centralized, vendor-neutral portal.

                          Maximize edge computing efficiency, security, and resilience

                          Using the Nodegrid edge management and orchestration platform as the foundation for your edge computing ecosystem design helps maximize the efficiency, security, and resilience of edge deployments. Contact ZPE Systems to learn more.

                          Contact Us