Providing Out-of-Band Connectivity to Mission-Critical IT Resources

Applications of Edge Computing
A healthcare worker presents various edge computing concepts to highlight some of the applications of edge computing

The edge computing market is huge and continuing to grow. A recent study projected that spending on edge computing will reach $232 billion in 2024. Organizations across nearly every industry are taking advantage of edge computing’s real-time data processing capabilities to get immediate business insights, respond to issues at remote sites before they impact operations, and much more. This blog discusses some of the applications of edge computing for industries like finance, retail, and manufacturing, and provides advice on how to get started.

What is edge computing?

Edge computing involves decentralizing computing capabilities and moving them to the network’s edges. Doing so reduces the number of network hops between data sources and the applications that process and use that data, which mitigates latency, bandwidth, and security concerns compared to cloud or on-premises computing.

Learn more about edge computing vs cloud computing or edge computing vs on-premises computing.

Edge computing often uses edge-native applications that are built from the ground up to harness edge computing’s unique capabilities and overcome its limitations. Edge-native applications leverage some cloud-native principles, such as containers, microservices, and CI/CD. However, unlike cloud-native apps, they’re designed to process transient, ephemeral data in real time with limited computational resources. Edge-native applications integrate seamlessly with the cloud, upstream resources, remote management, and centralized orchestration, but can also operate independently as needed.
.

Applications of edge computing

Industry

Applications

Financial services

  • Mitigate security and compliance risks of off-site data transmission

  • Gain real-time customer and productivity insights

  • Analyze surveillance footage in real-time

Industrial manufacturing

  • Monitor and respond to OT equipment issues in real-time

  • Create more efficient maintenance schedules

  • Prevent network outages from impacting production

Retail operations

  • Enhance the in-store customer experience

  • Improve inventory management and ordering

  • Aid loss prevention with live surveillance analysis

Healthcare

  • Monitor and respond to patient health issues in real-time

  • Mitigate security and compliance risks by keeping data on-site

  • Reduce networking requirements for wearable sensors

Oil, gas, & mining

  • Ensure continuous monitoring even during network disruptions

  • Gain real-time safety, maintenance, and production recommendations

  • Enable remote troubleshooting and recovery of IT systems

AI & machine learning

  • Reduce the costs and risks of high-volume data transmissions

  • Unlock near-instantaneous AI insights at the edge

  • Improve AIOps efficiency and resilience at branches

Financial services

The financial services industry collects a lot of edge data from bank branches, web and mobile apps, self-service ATMs, and surveillance systems. Many firms feed this data into AI/ML-powered data analytics software to gain insights into how to improve their services and generate more revenue. Some also use AI-powered video surveillance systems to analyze video feeds and detect suspicious activity. However, there are enormous security, regulatory, and reputational risks involved in transmitting this sensitive data to the cloud or an off-site data center.

Financial institutions can use edge computing to move data analytics applications to branches and remote PoPs (points of presence) to help mitigate the risks of transmitting data off-site. Additionally, edge computing enables real-time data analysis for more immediate and targeted insights into customer behavior, branch productivity, and security. For example, AI surveillance software deployed at the edge can analyze live video feeds and alert on-site security personnel about potential crimes in progress.

Industrial manufacturing

Many industrial manufacturing processes are mostly (if not completely) automated and overseen by operational technology (OT), such as supervisory control and data acquisition systems (SCADA). Logs from automated machinery and control systems are analyzed by software to monitor equipment health, track production costs, schedule preventative maintenance, and perform quality assurance (QA) on components and products. However, transferring that data to the cloud or centralized data center increases latency and creates security risks.

Manufacturers can use edge computing to analyze OT data in real time, gaining faster insights and catching potential issues before they affect product quality or delivery schedules. Edge computing also allows industrial automation and monitoring processes to continue uninterrupted even if the site loses Internet access due to an ISP outage, natural disaster, or other adverse event in the region. Edge resilience can be further improved by deploying an out-of-band (OOB) management solution like Nodegrid that enables control plane/data plane isolation (also known as isolated management infrastructure), as this will give remote teams a lifeline to access and recover OT systems.

Retail operations

In the age of one-click online shopping, the retail industry has been innovating with technology to enhance the in-store experience, improve employee productivity, and keep operating costs down. Retailers have a brief window of time to meet a customer’s needs before they look elsewhere, and edge computing’s ability to leverage data in real time is helping address that challenge. For example, some stores place QR codes on shelves that customers can scan if a product is out of stock, alerting a nearby representative to provide immediate assistance.

Another retail application of edge computing is enhanced inventory management. An edge computing solution can make ordering recommendations based on continuous analysis of purchasing patterns over time combined with real-time updates as products are purchased or returned. Retail companies, like financial institutions, can also use edge AI/ML solutions to analyze surveillance data and aid in loss prevention.

Healthcare

The healthcare industry processes massive amounts of data generated by medical equipment like insulin pumps, pacemakers, and imaging devices. Patient health data can’t be transferred over the open Internet, so getting it to the cloud or data center for analysis requires funneling it through a central firewall via MPLS (for hospitals, clinics, and other physical sites), overlay networks, or SD-WAN (for wearable sensors and mobile EMS devices). This increases the number of network hops and creates a traffic bottleneck that prevents real-time patient monitoring and delays responses to potential health crises.

Edge computing for healthcare allows organizations to process medical data on the same local network, or even the same onboard chip, as the sensors and devices that generate most of the data. This significantly reduces latency and mitigates many of the security and compliance challenges involved in transmitting regulated health data offsite. For example, an edge-native application running on an implanted heart-rate monitor can operate without a network connection much of the time, providing the patient with real-time alerts so they can modify their behavior as needed to stay healthy. If the app detects any concerning activity, it can use multiple cellular and ATT FirstNet connections to alert the cardiologist without exposing any private patient data.

Oil, gas, & mining

Oil, gas, and other mining operations use IoT sensors to monitor flow rates, detect leaks, and gather other critical information about equipment deployed in remote sites, drilling rigs, and offshore platforms all over the world. Drilling rigs are often located in extremely remote or even human-inaccessible locations, so ensuring reliable communications with monitoring applications in the cloud or data center can be difficult. Additionally, when networks or systems fail, it can be time-consuming and expensive – not to mention risky – to deploy IT teams to fix the issue on-site.

The energy and mining industries can use edge computing to analyze data in real time even in challenging deployment environments. For example, companies can deploy monitoring software on cellular-enabled edge computing devices to gain immediate insights into equipment status, well logs, borehole logs, and more. This software can help establish more effective maintenance schedules, uncover production inefficiencies, and identify potential safety issues or equipment failures before they cause larger problems. Edge solutions with OOB management also allow IT teams to fix many issues remotely, using alternative cellular interfaces to provide continuous access for troubleshooting and recovery.

AI & machine learning

Artificial intelligence (AI) and machine learning (ML) have broad applications across many industries and use cases, but they’re all powered by data. That data often originates at the network’s edges from IoT devices, equipment sensors, surveillance systems, and customer purchases. Securely transmitting, storing, and preparing edge data for AI/ML ingestion in the cloud or centralized data center is time-consuming, logistically challenging, and expensive. Decentralizing AI/ML’s computational resources and deploying them at the edge can significantly reduce these hurdles and unlock real-time capabilities.

For example, instead of deploying AI on a whole rack of GPUs (graphics processing units) in a central data center to analyze equipment monitoring data for all locations, a manufacturing company could use small edge computing devices to provide AI-powered analysis for each individual site. This would reduce bandwidth costs and network latency, enabling near-instant insights and providing an accelerated return on the investment into artificial intelligence technology.

AIOps can also be improved by edge computing. AIOps solutions analyze monitoring data from IT devices, network infrastructure, and security solutions and provide automated incident management, root-cause analysis, and simple issue remediation. Deploying AIOps on edge computing devices enables real-time issue detection and response. It also ensures continuous operation even if an ISP outage or network failure cuts off access to the cloud or central data center, helping to reduce business disruptions at vital branches and other remote sites.

Getting started with edge computing

The edge computing market has focused primarily on single-use-case solutions designed to solve specific business problems, forcing businesses to deploy many individual applications across the network. This piecemeal approach to edge computing increases management complexity and risk while decreasing operational efficiency.

The recommended approach is to use a centralized edge management and orchestration (EMO) platform to monitor and control edge computing operations. The EMO should be vendor-agnostic and interoperate with all the edge computing devices and edge-native applications in use across the organization. The easiest way to ensure interoperability is to use vendor-neutral edge computing platforms to run edge-native apps and AI/ML workflows.

For example, the Nodegrid platform from ZPE Systems provides the perfect vendor-neutral foundation for edge operations. Nodegrid integrated branch services routers like the Gate SR with integrated Nvidia Jetson Nano use the open, Linux-based Nodegrid OS, which can host Docker containers and edge-native applications for third-party AI, ML, data analytics, and more. These devices use out-of-band management to provide 24/7 remote visibility, management, and troubleshooting access to edge deployments, even in challenging environments like offshore oil rigs. Nodegrid’s cloud-based or on-premises software provides a single pane of glass to orchestrate operations at all edge computing sites.

Streamline your edge computing deployment with Nodegrid

The vendor-neutral Nodegrid platform can simplify all applications of edge computing with easy interoperability, reduced hardware overhead, and centralized edge management and orchestration. Schedule a Nodegrid demo to learn more.
Schedule a Demo
Edge Computing Examples

Interlocking cogwheels containing icons of various edge computing examples are displayed in front of racks of servers

The edge computing market is growing fast, with experts predicting edge computing spending to reach almost $350 billion in 2027. Companies use edge computing to leverage data from Internet of Things (IoT) sensors and other devices at the periphery of the network in real-time, unlocking faster insights, accelerating ROIs for artificial intelligence and machine learning investments, and much more. This blog highlights 7 edge computing examples from across many different industries and provides tips and best practices for each use case.

What is edge computing?

Edge computing involves moving compute capabilities – processing units, RAM, storage, data analysis software, etc. – to the network’s edges. This allows companies to analyze or otherwise use edge data in real-time, without transmitting it to a central data center or the cloud.

Edge Computing Learning Center

Edge computing shortens the physical and logical distance between data-generating devices and the applications that use that data, which reduces bandwidth costs and network latency while simplifying many aspects of data security and compliance.

7 Edge computing examples

Below are 7 examples of how organizations use edge computing, along with best practices for overcoming the typical challenges involved in each use case. Click the links in the table for more information about each example.

Examples Best Practices
Monitoring inaccessible equipment in the oil & gas industry Use a vendor-neutral edge computing & networking platform to reduce the tech stack at each site.
Remotely managing and securing automated Smart buildings Isolate the management interfaces for automated building management systems from production to reduce risk.
Analyzing patient health data generated by mobile devices Protect patient privacy with strong hardware roots-of-trust, Zero Trust Edge integrations, and control plane/data plane separation.
Reducing latency for live streaming events and online gaming Use all-in-one, vendor-neutral devices to minimize hardware overhead and enable cost-effective scaling.
Improving performance and business outcomes for AI/ML Streamline operations by using a vendor-neutral platform to remotely monitor and orchestrate edge AI/ML deployments.
Enhancing remote surveillance capabilities at banks and ATMs Isolate the management interfaces for all surveillance systems using Gen 3 OOB to prevent compromise.
Extending data analysis to agriculture sites with limited Internet access Deploy edge gateway routers with environmental sensors to monitor operating conditions and prevent equipment failures.

1. Monitoring and managing inaccessible equipment in the oil and gas industry

The oil and gas industry uses IoT sensors to monitor flow rates, detect leaks, and gather other critical information about human-inaccessible equipment and operations. With drilling rigs located offshore and in extremely remote locations, ensuring reliable internet access to communicate with cloud-based or on-premises monitoring applications can be tricky. Dispatching IT teams to diagnose and repair issues is also costly, time-consuming, and risky. Edge computing allows oil and gas companies to process data on-site and in real-time, so safety issues and potential equipment failures are caught and remediated as soon as possible, even when Internet access is spotty.

Best practice: Use a vendor-neutral edge computing & networking platform like the Nodegrid Gate SR to reduce the tech stack at each site. The Gate SR can host other vendors’ software for SD-WAN, Secure Access Service Edge (SASE), equipment monitoring, and more. It also provides out-of-band (OOB) management and built-in cellular failover to improve network availability and resilience. Read this case study to learn more.

2. Remotely managing and securing fully automated Smart buildings

Smart buildings use IoT sensors to monitor and control building functions such as HVAC, lighting, power, and security. Property management companies and facilities departments use data analysis software to automatically determine optimal conditions, respond to issues, and alert technicians when emergencies occur. Edge computing allows these automated processes to respond to changing conditions in real-time, reducing the need for on-site personnel and improving operational efficiency.

Best practice: Keep the management interfaces for automated building management systems isolated from the production environment to reduce the risk of compromise or ransomware infection. Use edge computing platforms with Gen 3 out-of-band (OOB) management for control plane/data plane separation to improve resilience and ensure continuous remote access for troubleshooting and recovery. 

3. Analyzing patient health data generated by mobile devices in the healthcare industry

Healthcare organizations use data analysis software, including AI and machine learning, to analyze patient health data generated by insulin pumps, pacemakers, imaging devices, and other IoT medical technology. Keeping that data secure is critical for regulatory compliance, so it must be funneled through a firewall on its way to cloud-based or data center applications, increasing latency and preventing real-time response to potentially life-threatening health issues. Edge computing for healthcare moves patient monitoring and data analysis applications to the same local network (or even the same onboard chip) as the sensors generating most of the data, reducing security risks and latency. Some edge computing applications for healthcare can operate without a network connection most of the time, using built-in cellular interfaces and ATT FirstNet connections to send emergency alerts as needed without exposing any private patient data.

Best practice: Protect patient privacy by deploying healthcare edge computing solutions like Nodegrid with strong hardware roots-of-trust, Zero Trust Edge integrations, and control plane/data plane separation. Nodegrid secures management interfaces with the Trusted Platform Module 2.0 (TPM 2.0), multi-factor authentication (MFA), secure boot, built-in firewall intrusion prevention, and more.

4. Reducing latency for live streaming events and online gaming

Streaming live content requires low-latency processing for every user regardless of their geographic location, which is hard to deliver from a few large, strategically placed data centers. Edge computing decentralizes computing resources, using relatively small deployments in many different locations to bring services closer to audience members and gamers. Edge computing reduces latency for streaming sports games, concerts, and other live events, as well as online multiplayer games where real-time responses are critical to the customer experience.

Best practice: Use all-in-one, vendor-neutral devices like the Nodegrid Gate SR to combine SD-WAN, OOB management, edge security, service delivery, and more. Nodegrid services routers reduce the tech stack at each edge computing site, allowing companies to scale out as needed while minimizing hardware overhead.

5. Improving performance and business outcomes for artificial intelligence/machine learning

Artificial intelligence and machine learning applications provide enhanced data analysis capabilities for essentially any use case, but they must ingest vast amounts of data to do so. Securely transmitting and storing edge and IoT data and preparing it for ingestion in data lakes or data warehouses located in the cloud or data center takes significant time and effort, which may prevent companies from getting the most out of their AI investment. Edge computing for AI/ML eliminates transmission and storage concerns by processing data directly from the sources. Edge computing lets companies leverage their edge data for AI/ML much faster, enabling near-real-time insights, improving application performance, and providing accelerated business value from AI investments.

Best practice: Use a vendor-neutral OOB management platform like Nodegrid to remotely monitor and orchestrate edge AI/ML deployments. Nodegrid OOB ensures 24/7 remote management access to AI infrastructure even during network outages. It also supports third-party automation for mixed-vendor devices to help streamline edge operations. 

6. Enhancing remote surveillance capabilities at banks and ATMs

Constantly monitoring video surveillance feeds from banks and ATMs is very tedious for people, but machines excel at it. AI-powered video surveillance systems use advanced machine-learning algorithms to analyze video feeds and detect suspicious activity with far greater vigilance and accuracy than human security teams. With edge computing, these solutions can analyze surveillance data in real-time, so they could potentially catch a crime as it’s occurring. Edge computing also keeps surveillance data on-site, reducing bandwidth costs, network latency, and the risk of interception.

Best practice: Isolate the management interfaces for all surveillance systems using a Gen 3 OOB solution like Nodegrid to keep malicious actors from hijacking the security feeds. OOB control plane/data plane separation also makes it easier to establish a secure environment for regulated financial data, simplifying PCI DSS 4.0 and DORA compliance.

7. Extending data analysis to agriculture sites with limited Internet access

The agricultural sector uses IoT technology to monitor growing conditions, equipment performance, crop yield, and much more. Many of these devices use cellular connections to transmit data to the cloud for analysis which, as we’ve already discussed ad nauseam, introduces latency, increases bandwidth costs, and creates security risks. Edge computing moves this data processing on-site to reduce delays in critical applications like livestock monitoring and irrigation control. It also allows farms to process data on a local network, reducing their reliance on cellular networks that aren’t always reliable in remote and rural areas.

Best practice: Deploy all-in-one edge gateway routers with environmental sensors, like the Nodegrid Mini SR, to monitor operating conditions where your critical infrastructure is deployed. Nodegrid’s environmental sensors alert remote teams when the temperature, humidity, or airflow falls outside of established baselines to prevent equipment failure. 

Edge computing for any use case

The potential uses for edge computing are nearly limitless. A shift toward distributed, real-time data analysis allows companies in any industry to get faster insights, reduce inefficiencies, and see more value from AI initiatives.

Simplify your edge deployment with Nodegrid

The Nodegrid line of integrated services routers delivers all-in-one edge networking, computing, security, and more. For more edge computing examples using Nodegrid, reach out to ZPE Systems today. Contact Us

Edge Computing vs Cloud Computing

A factory floor with digital overlays showing edge computing data analysis dashboards

Both edge computing and cloud computing involve moving computational resources – such as CPUs (central processing units), GPUs (graphics processing units), RAM (random access memory), and data storage – out of the centralized, on-premises data center. As such, both represent massive shifts in enterprise network designs and how companies deploy, manage, secure, and use computing resources. Edge and cloud computing also create new opportunities for data processing, which is sorely needed as companies generate more data than ever before, thanks in no small part to an explosion in Internet of Things (IoT) and artificial intelligence (AI) adoption. This year, IoT devices alone are predicted to generate 80 zettabytes of data, much of it decentralized around the edges of the network. AI, machine learning, and other data analytics applications, meanwhile, require vast quantities of data (and highly scalable infrastructure) to provide accurate insights. This guide compares edge computing vs cloud computing to help organizations choose the right deployment model for their use case.

 Table of Contents

Defining edge computing vs cloud computing

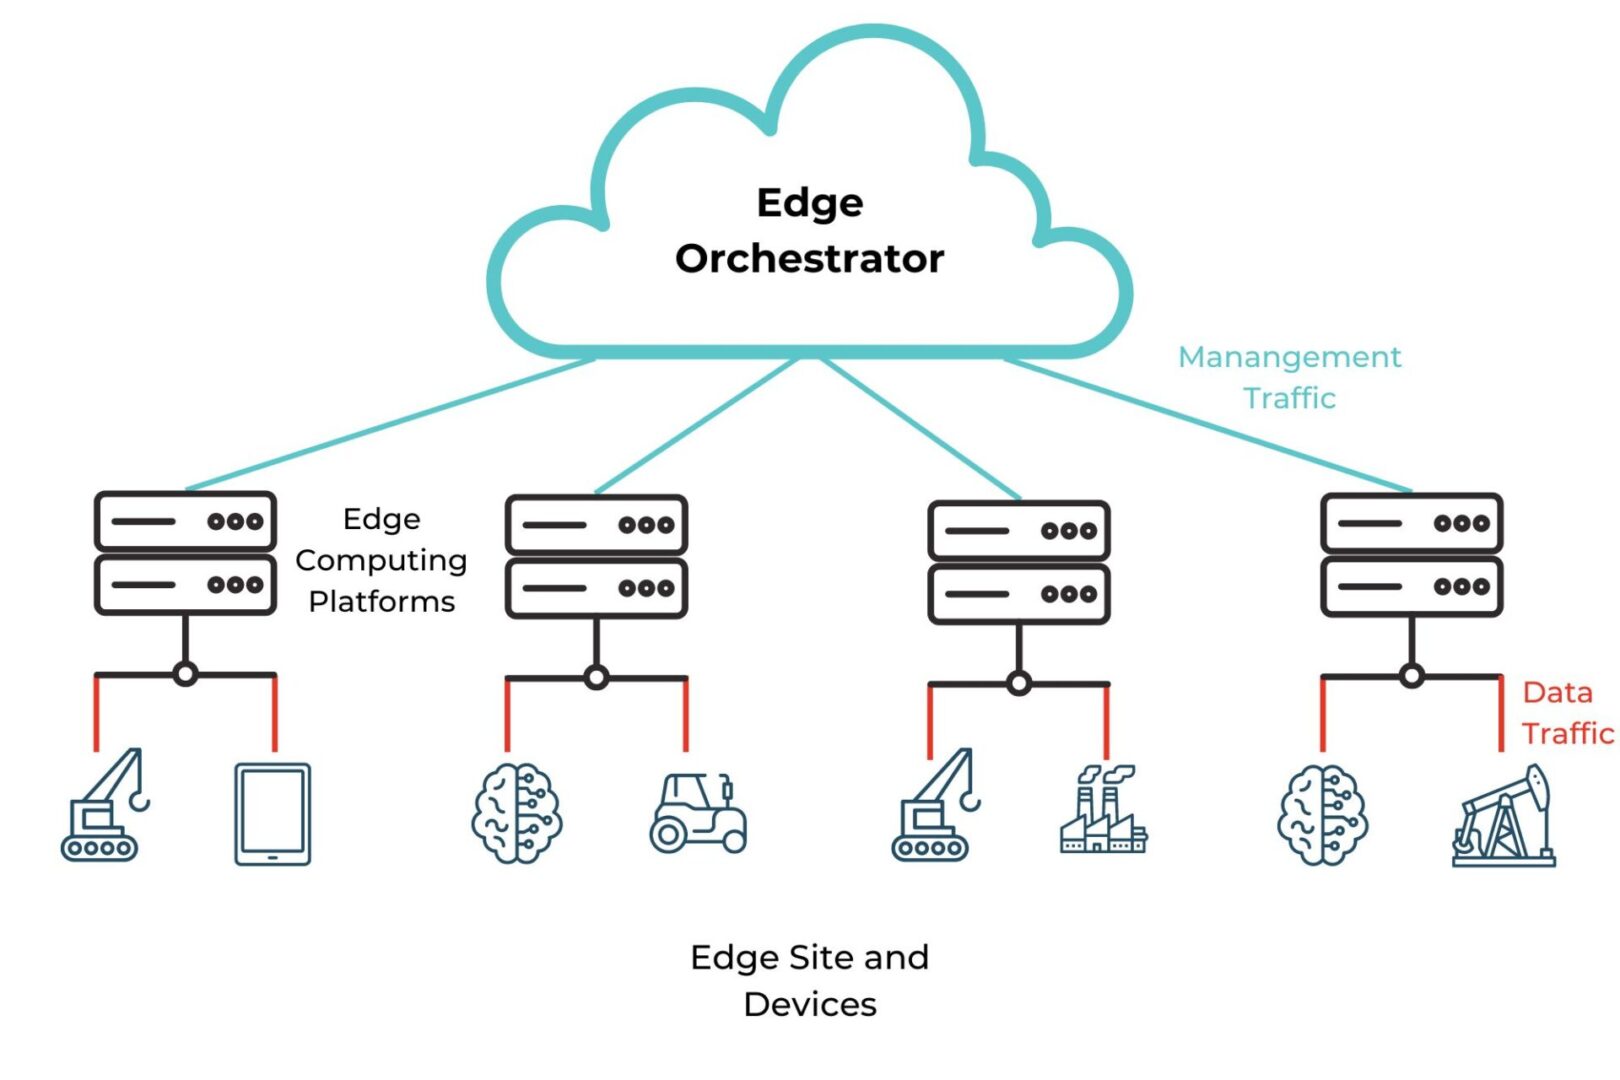
Edge computing involves deploying computing capabilities to the network’s edges to enable on-site data processing for Internet of Things (IoT) sensors, operational technology (OT), automated infrastructure, and other edge devices and services. Edge computing deployments are highly distributed across remote sites far from the network core, such as oil & gas rigs, automated manufacturing plants, and shipping warehouses. Ideally, organizations use a centralized (usually cloud-based) orchestrator to oversee and conduct operations across the distributed edge computing architecture.

Diagram showing an example edge computing architecture controlled by a cloud-based edge orchestrator.

Reducing the number of network hops between edge devices and the applications that process and use edge data enables real-time data processing, reduces MPLS bandwidth costs, improves performance, and keeps private data within the security micro-perimeter. Cloud computing involves using remote computing resources over the Internet to run applications, process and store data, and more. Cloud service providers manage the physical infrastructure and allow companies to easily scale their virtual computing resources with the click of a button, significantly reducing operational costs and complexity over on-premises and edge computing deployments.

Examples of edge computing vs cloud computing

Edge computing works best for workloads requiring real-time data processing using fairly lightweight applications, especially in locations with inconsistent or unreliable Internet access or where privacy/compliance is a major concern. Example edge computing use cases include:

Cloud computing is well-suited to workloads requiring extensive computational resources that can scale on-demand, but that aren’t time-sensitive. Example use cases include:

The advantages of edge computing over cloud computing

Using cloud-based applications to process edge device data involves transmitting that data from the network’s edges to the cloud provider’s data center, and vice versa. Transmitting data over the open Internet is too risky, so most organizations route the traffic through a security appliance such as a firewall to encrypt and protect the data. Often these security solutions are off-site, in the company’s central data center, or, best-case scenario, a SASE point-of-presence (PoP), adding more network hops between edge devices and the cloud applications that service them.  This process increases bandwidth usage and introduces latency, preventing real-time data processing and negatively affecting performance, which is one of the main reasons why organizations are repatriating workloads from the cloud to on-prem.

Edge computing moves data processing resources closer to the source, eliminating the need to transmit this data over the Internet. This improves performance by reducing (or even removing) network hops and preventing network bottlenecks at the centralized firewall. Edge computing also lets companies use their valuable edge data in real time, enabling faster insights and greater operational efficiencies.

Edge computing mitigates the risk involved in storing and processing sensitive or highly regulated data in a third-party computing environment, giving companies complete control over their data infrastructure. It can also help reduce bandwidth costs by eliminating the need to route edge data through VPNs or MPLS links to apply security controls.

Edge computing advantages:

  • Improves network and application performance
  • Enables real-time data processing and insights
  • Simplifies security and compliance
  • Reduces MPLS bandwidth costs

The disadvantages of edge computing compared to cloud computing

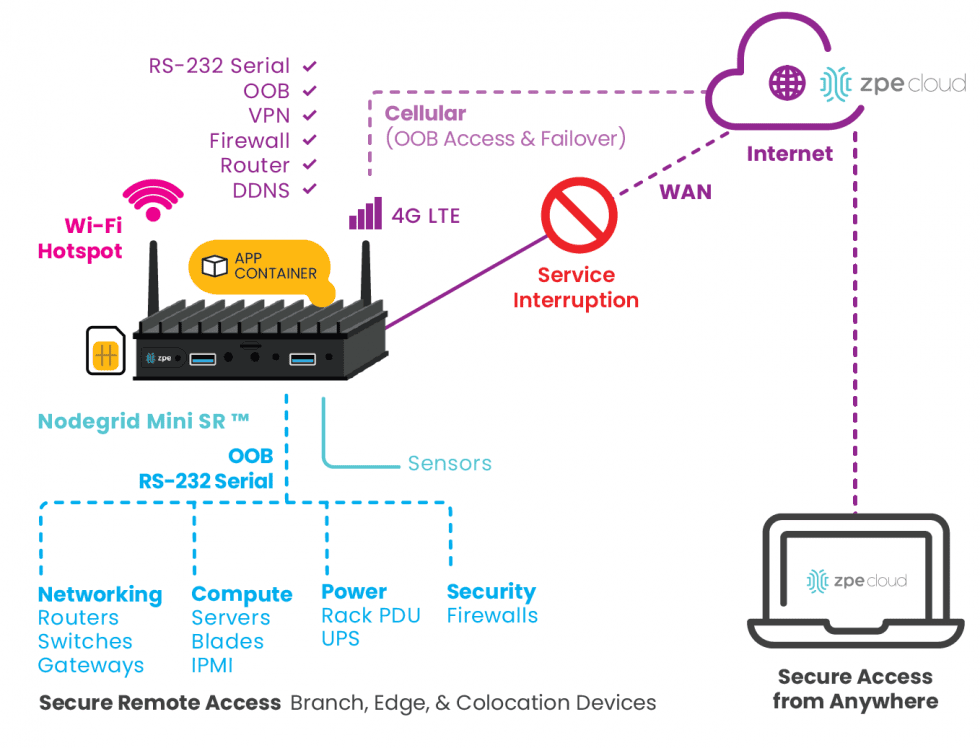
Cloud computing resources are highly scalable, allowing organizations to meet rapidly changing requirements without the hassle of purchasing, installing, and maintaining additional hardware and software licenses. Edge computing still involves physical, on-premises infrastructure, making it far less scalable than the cloud. However, it’s possible to improve edge agility and flexibility by using vendor-neutral platforms to run and manage edge resources. An open platform like Nodegrid allows teams to run multiple edge computing applications from different vendors on the same box, swap out services as business needs evolve, and deploy automation to streamline multi-vendor edge device provisioning from a single orchestrator. A diagram showing how the Nodegrid Mini SR combines edge computing and networking capabilities on a small, affordable, flexible platform.

Diagram showing how the Nodegrid Mini SR combines edge computing and networking capabilities on a small, affordable, flexible platform.

Organizations often deploy edge computing in less-than-ideal operating environments, such as closets and other cramped spaces that lack the strict HVAC controls that maintain temperature and humidity in cloud data centers. These environments also typically lack the physical security controls that prevent unauthorized individuals from tampering with equipment, such as guarded entryways, security cameras, and biometric locks. The best way to mitigate this disadvantage is with an environmental monitoring system that uses sensors to detect temperature and humidity changes that could cause equipment failures as well as proximity alarms to notify administrators when someone gets too close. It’s also advisable to use hermetically sealed edge computing devices capable of operating in extreme temperatures and with built-in security features making them tamper-proof.

Cloud computing is often more resilient than edge computing because cloud service providers must maintain a certain level of continuous uptime to meet service level agreements (SLAs). Edge computing operations could be disrupted by network equipment failures, ISP outages, ransomware attacks, and other adverse events, so it’s essential to implement resilience measures that keep services running (if in a degraded state) and allow remote teams to fix problems without having to be on site. Edge resilience measures include Gen 3 out-of-band management, control plane/data plane separation (also known as isolated management infrastructure or IMI), and isolated recovery environments (IRE).

Edge computing disadvantages:

  • Less scalable than cloud infrastructure
  • Lack of environmental and security controls
  • Requires additional resilience measures

Edge-native applications vs cloud-native applications

Edge-native applications and cloud-native applications are similar in that they use containers and microservices architectures, as well as CI/CD (continuous integration/continuous delivery) and other DevOps principles.

Cloud-native applications leverage centralized, scalable resources to perform deep analysis of long-lived data in long-term hot storage environments. Edge-native applications are built to leverage limited resources distributed around the network’s edges to perform real-time analysis of ephemeral data that’s constantly moving. Typically, edge-native applications are highly contextualized for a specific use case, whereas cloud-native applications offer broader, standardized capabilities. Another defining characteristic of edge-native applications is the ability to operate independently when needed while still integrating seamlessly with the cloud, upstream resources, remote management, and centralized orchestration.

Choosing edge computing vs cloud computing

Both edge computing and cloud computing have unique advantages and disadvantages that make them well-suited for different workloads and use cases. Factors like increasing data privacy regulations, newsworthy cloud provider outages, greater reliance on human-free IoT and OT deployments, and an overall trend toward decentralizing business operations are pushing organizations to adopt edge computing. However, most companies still rely heavily on cloud resources and will continue to do so, making it crucial to ensure seamless interoperability between the edge and the cloud.

The best way to ensure integration is by using vendor-neutral platforms. For example, Nodegrid integrated services routers like the Gate SR provide multi-vendor out-of-band serial console management for edge infrastructure and devices, using an embedded Jetson Nano card to support edge computing and AI workloads. The ZPE Cloud management platform unifies orchestration for the entire Nodegrid-connected architecture, delivering 360-degree control over complex and highly distributed networks. Plus, Nodegrid easily integrates – or even directly hosts – other vendors’ solutions for edge data processing, IT automation, SASE, and more, making edge operations more cost-effective. Nodegrid also provides the complete control plane/data plane separation needed to ensure edge resilience.

Get edge efficiency and resilience with Nodegrid

The Nodegrid platform from ZPE Systems helps companies across all industries streamline their edge operations with resilient, vendor-neutral, Gen 3 out-of-band management. Request a free Nodegrid demo to learn more. REQUEST A DEMO

Edge Computing Architecture Guide

Edge-computing-architecture-concept-icons-arranged-around-the-word-edge-computing
Edge computing is rapidly gaining popularity as more  organizations see the benefits of decentralizing data processing for Internet of Things (IoT) deployments, machine learning applications, operational technology (OT), AI and machine learning, and other edge use cases. This guide defines edge computing and edge-native applications, highlights a few key use cases, describes the typical components of an edge deployment, and provides additional resources for building your own edge computing architecture.

Table of Contents

What is edge computing?

The Open Glossary of Edge Computing defines it as deploying computing capabilities to the edges of a network to improve performance, reduce operating costs, and increase resilience. Edge computing reduces the number of network hops between data-generating devices and the applications that process and use that data, mitigating latency, bandwidth, and security concerns compared to cloud or on-premises computing.

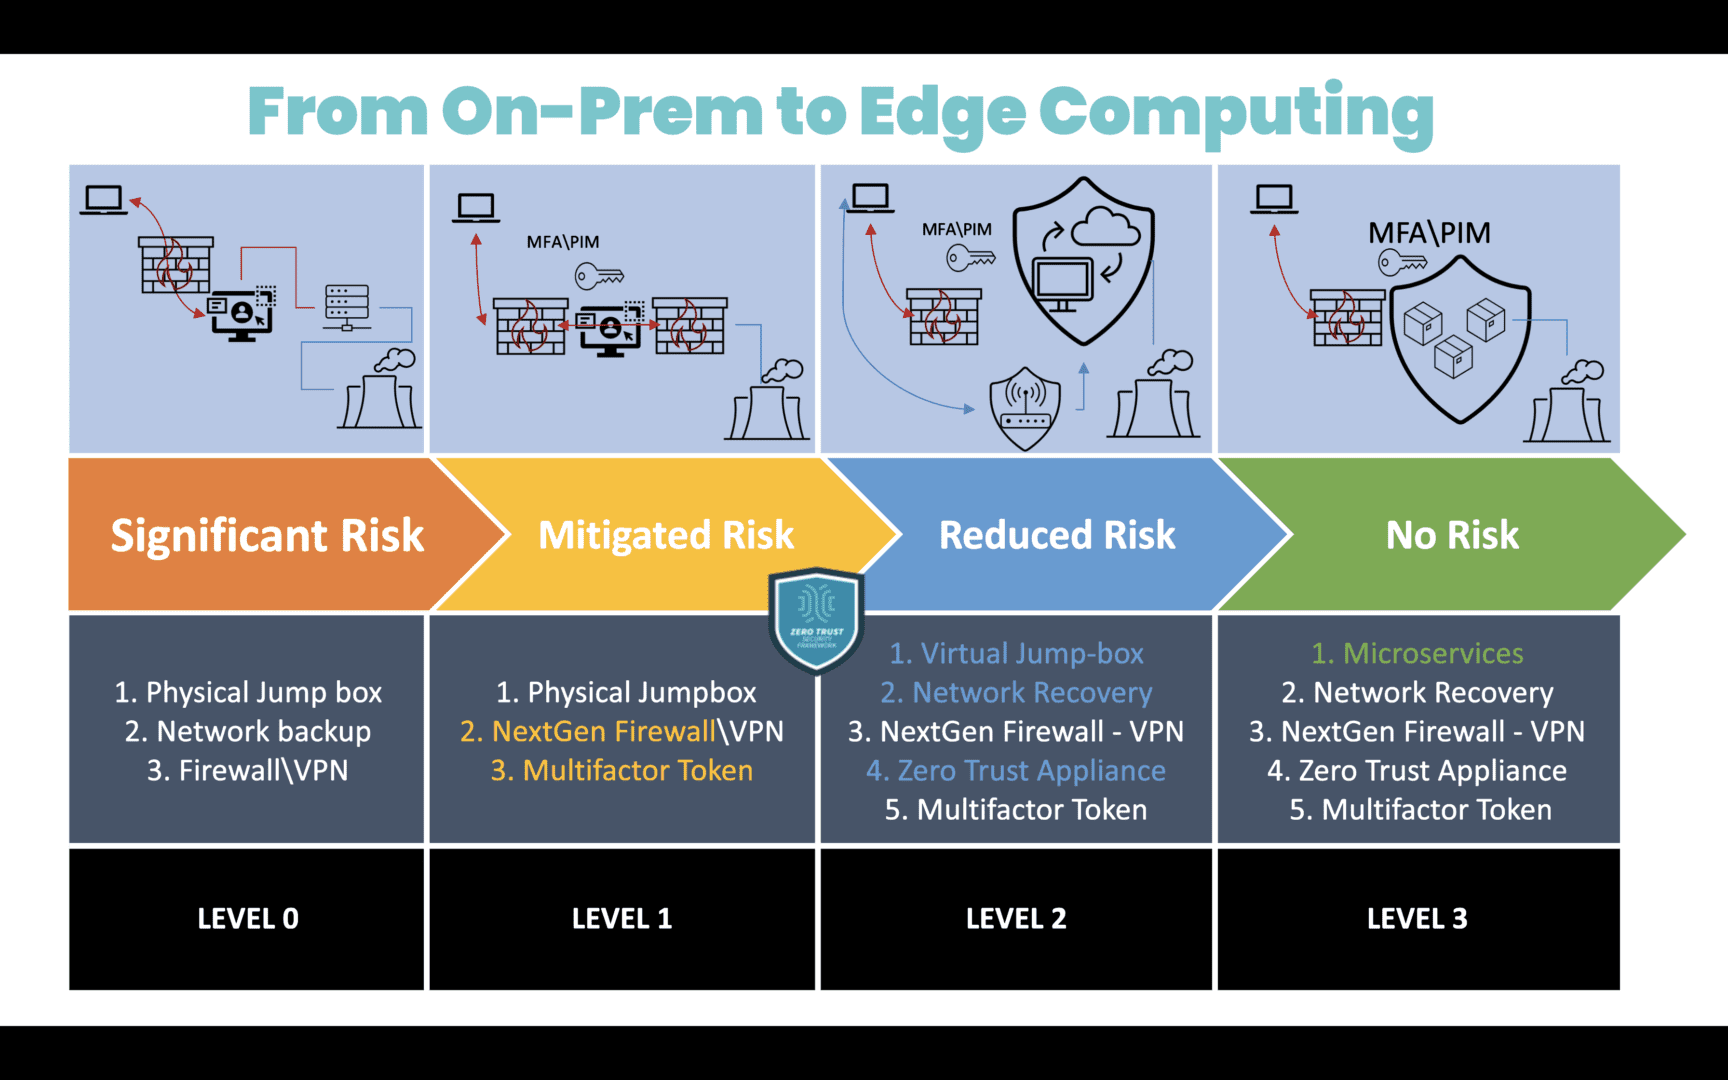
A diagram showing the migration path from on-premises computing to edge computing, along with the associated level of security risk.

Image: A diagram showing the migration path from on-premises computing to edge computing, along with the associated level of security risk.

Edge-native applications

Edge-native applications are built from the ground up to harness edge computing’s unique capabilities while mitigating the limitations. They leverage some cloud-native principles, such as containers, microservices, and CI/CD (continuous integration/continuous delivery), with several key differences.

Edge-Native vs. Cloud-Native Applications

Edge-Native Cloud-Native
Topology Distributed Centralized
Compute Real-time processing with limited resources Deep processing with scalable resources
Data Constantly changing and moving Long-lived and at rest in a centralized location
Capabilities Contextualized Standardized
Location Anywhere Cloud data center

Source: Gartner

Edge-native applications integrate seamlessly with the cloud, upstream resources, remote management, and centralized orchestration, but can also operate independently as needed. Crucially, they allow organizations to actually leverage their edge data in real-time, rather than just collecting it for later processing.

Edge computing use cases

Nearly every industry has potential use cases for edge computing, including:

Industry Edge Computing Use Cases
Healthcare
  • Mitigating security, privacy, and HIPAA compliance concerns with local data processing
  • Improving patient health outcomes with real-time alerts that don’t require Internet access
  • Enabling emergency mobile medical intervention while reducing mistakes
Finance
  • Reducing security and regulatory risks through local computing and edge infrastructure isolation
  • Getting fast, localized business insights to improve revenue and customer service
  • Deploying AI-powered surveillance and security solutions without network bottlenecks
Energy
  • Enabling network access and real-time data processing for airgapped and isolated environments
  • Improving efficiency with predictive maintenance recommendations and other insights
  • Proactively identifying and remediating safety, quality, and compliance issues
Manufacturing
  • Getting real-time, data-driven insights to improve manufacturing efficiency and product quality
  • Reducing the risk of confidential production data falling into the wrong hands in transit
  • Ensuring continuous operations during network outages and other adverse events
  • Using AI with computer vision to ensure worker safety and quality control of fabricated components/products
Utilities/Public Services
  • Using IoT technology to deliver better services, improve public safety, and keep communities connected
  • Reducing the fleet management challenges involved in difficult deployment environments
  • Aiding in disaster recovery and resilience with distributed redundant edge resources

To learn more about the specific benefits and uses of edge computing for each industry, read Distributed Edge Computing Use Cases.

Edge computing architecture design

An edge computing architecture consists of six major components:

Edge Computing Components Description Best Practices
Devices generating edge data IoT devices, sensors, controllers, smartphones, and other devices that generate data at the edge Use automated patch management to keep devices up-to-date and protect against known vulnerabilities
Edge software applications Analytics, machine learning, and other software deployed at the edge to use edge data Look for edge-native applications that easily integrate with other tools to prevent edge sprawl
Edge computing infrastructure CPUs, GPUs, memory, and storage used to process data and run edge applications Use vendor-neutral, multi-purpose hardware to reduce overhead and management complexity
Edge network infrastructure and logic Wired and wireless connectivity, routing, switching, and other network functions Deploy virtualized network functions and edge computing on common, vendor-neutral hardware
Edge security perimeter Firewalls, endpoint security, web filtering, and other enterprise security functionality Implement edge-centric security solutions like SASE and SSE to prevent network bottlenecks while protecting edge data
Centralized management and orchestration An EMO (edge management and orchestration) platform used to oversee and conduct all edge operations Use a cloud-based, Gen 3 out-of-band (OOB) management platform to ensure edge resilience and enable end-to-end automation

Click here to learn more about the infrastructure, networking, management, and security components of an edge computing architecture.

How to build an edge computing architecture with Nodegrid

Nodegrid is a Gen 3 out-of-band management platform that streamlines edge computing with vendor-neutral solutions and a centralized, cloud-based orchestrator.

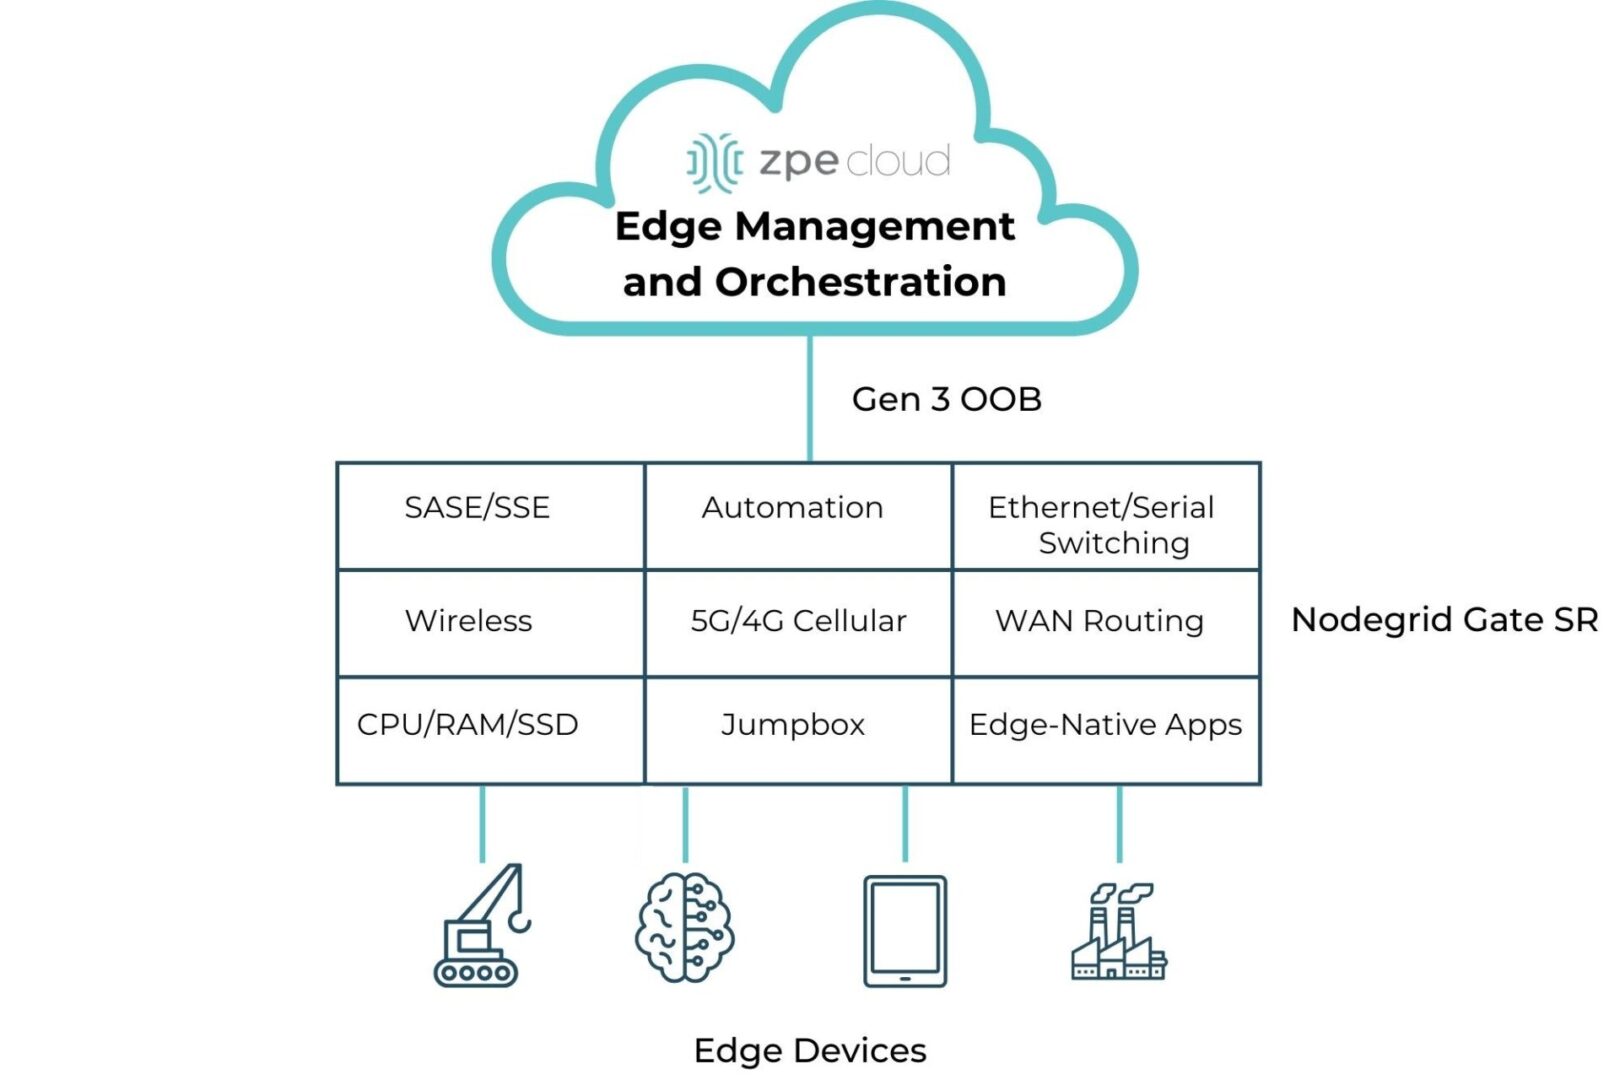
A diagram showing all the edge computing and networking capabilities provided by the Nodegrid Gate SR

Image: A diagram showing all the edge computing and networking capabilities provided by the Nodegrid Gate SR.

Nodegrid integrated services routers deliver all-in-one edge computing and networking functionality while taking up 1RU or less. A Nodegrid box like the Gate SR provides Ethernet and Serial switching, serial console/jumpbox management, WAN routing, wireless networking, and 5G/4G cellular for network failover or out-of-band management. It includes enough CPU, memory, and encrypted SSD storage to run edge computing workflows, and the x86-64bit Linux-based Nodegrid OS supports virtualized network functions, VMs, and containers for edge-native applications, even those from other vendors. The new Gate SR also comes with an embedded NVIDIA Jetson Orin NanoTM module featuring dual CPUs for EMO of AI workloads and infrastructure isolation.

Nodegrid SRs can also host SASE, SSE, and other security solutions, as well as third-party automation from top vendors like Redhat and Salt. Remote teams use the centralized, vendor-neutral ZPE Cloud platform (an on-premises version is available) to deploy, monitor, and orchestrate the entire edge architecture. Management, automation, and orchestration workflows occur over the Gen 3 OOB control plane, which is separated and isolated from the production network. Nodegrid OOB uses fast, reliable network interfaces like 5G cellular to enable end-to-end automation and ensure 24/7 remote access even during major outages, significantly improving edge resilience.

Streamline your edge deployment

The Nodegrid platform from ZPE Systems reduces the cost and complexity of building an edge computing architecture with vendor-neutral, all-in-one devices and centralized EMO. Request a free Nodegrid demo to learn more.

Click here to learn more!

NIS2 Compliance & Requirements

NIS2 Compliance

NIS2 – an update of the EU’s Network and Information Security Directive – seeks to enhance the cybersecurity level and resilience of EU member states. Compared to the original NIS, it significantly increases risk management, corporate accountability, business continuity, and reporting requirements. NIS2 became law in all EU member states on 17 October 2024, so affected organizations must take action to avoid fines and other penalties. This guide describes the 10 minimum cybersecurity requirements mandated by NIS2 and provides tips to simplify NIS2 compliance. Citation: Directive (EU) 2022/2555 of the European Parliament and of the Council of 14 December 2022 on measures for a high common level of cybersecurity across the Union, amending Regulation (EU) No 910/2014 and Directive (EU) 2018/1972, and repealing Directive (EU) 2016/1148 (NIS 2 Directive)

Who does NIS2 apply to, and what are the consequences for noncompliance?

NIS2 applies to organizations providing services deemed “essential” or “important” to the European economy and society. Essential Entities (EE) generally have at least 250 employees, annual turnover of €50 million, or balance sheets of €43 million. Essential sectors include:

Important Entities (IE) generally have at least 50 employees, annual turnover of €10 million, or balance sheets of €10 million. Important sectors include:

  • Postal services
  • Waste management
  • Chemicals
  • Research
  • Food
  • Manufacturing (e.g., medical devices and other equipment)
  • Digital providers (e.g., social networks, online marketplaces)

The NIS2 Directive outlines three types of penalties for noncompliance: non-monetary remedies, administrative fines, and criminal sanctions. Non-monetary remedies include things like compliance orders, binding instructions, security audit orders, and customer threat notification orders. Financial penalties for Essential Entities max out at €10 million or 2% of the global annual revenue, whichever is higher; for Important Entities, the maximum is €7 million or 1.4% of the global annual revenue, whichever is higher. NIS2 also directs member states to hold top management personally responsible for gross negligence in a cybersecurity incident, which could involve:

  • Ordering organizations to notify the public of compliance violations
  • Publicly identifying the people and/or entities responsible for the violation
  • Temporarily banning an individual from holding management positions (EEs only)

Even the nonfinancial penalties of NIS2 noncompliance can affect revenue by causing reputational damage and potential lost business, so it’s crucial for IEs and EEs to be prepared when this directive takes effect in their state.

10 Minimum requirements for NIS2 compliance

The NIS2 directive requires essential and important entities to take “appropriate and proportional” measures to manage security and resilience risks and minimize the impact of incidents. It mandates an “all-hazards approach,” which means creating a comprehensive business continuity framework that accounts for any potential disruptions, whether they be natural disasters, ransomware attacks, or anything in between. Organizations must implement “at least” the following requirements as a baseline for NIS2 compliance (click links for more info):

10 NIS2 Compliance Requirements

NIS2 Minimum Requirement

Implementation Tip

Maintain comprehensive risk analysis and information system security policies

Keep policies in a centralized repository with version control to track changes and prevent unauthorized modifications.

Implement robust security incident handling measures

Use AIOps to accelerate incident creation, triage, and root-cause analysis (RCA).

Establish business continuity and crisis management strategies

Use out-of-band (OOB) management and isolated recovery environments (IREs) to minimize downtime and improve resilience.

Mitigate supply chain security risks

Implement User and Entity Behavior Analytics (UEBA) to monitor third parties on the network.

Ensure network and IT system security throughout acquisition, development, and maintenance

Use automated provisioning, vulnerability scanning, and patch management to reduce risks.

Perform regular cybersecurity and risk-management assessments

Use artificial intelligence technology like large language models (LLMs) to streamline assessments.

Enforce cybersecurity training requirements for all personnel

Simulate phishing emails and other social engineering attacks to prepare users for the real thing.

Implement cryptography and, when necessary, encryption

Ensure all physical systems are protected by strong hardware roots of trust like TPM 2.0.

Establish secure user access control and asset management practices 

Use zero-trust policies and controls to restrict privileges and limit lateral movement.

Use multi-factor authentication (MFA) and encrypted communications 

Extend MFA to management interfaces and recovery systems to prevent compromise.

1. Risk analysis and information system security policies

Organizations must create and update comprehensive policies covering cybersecurity risk analysis and overall IT system security practices. These policies should cover all the topics listed below and include specific consequences and/or corrective measures for failing to follow the outlined processes.

Tip: Keeping all company policies in a centralized, version-controlled repository will help track updates over time and prevent anyone from making unauthorized changes.

2. Security incident handling

Entities must implement incident-handling tools and practices to help accelerate resolution and minimize the impact on end users and other essential or important services. This includes mechanisms for identifying problems, triaging according to severity, remediating issues, and notifying relevant parties. NIS2 outlines a specific timeline for reporting significant security incidents to the relevant authorities:

  • Within 24 hours – Entities must provide an early warning indicating whether they suspect an unlawful or malicious attack or whether it could have a cross-border impact.
  • Within 72 hours – Entities must update the relevant authorities with an assessment of the attack, including its severity, impact, and indicators of compromise.
  • Within one month – Organisations must submit a final report including a detailed description of the incident, the most likely root cause or type of threat, what mitigation measures were taken, and, if applicable, the cross-border impact. If the incident is still ongoing, entities must submit an additional report within one month of resolution.
Tip: AIOps (artificial intelligence for IT operations) analyzes monitoring logs using machine learning to identify threat indicators and other potential issues that less sophisticated tools might miss. It can also generate, triage, and assign incidents, perform root-cause analysis (RCA) and other automated troubleshooting, and take other actions to streamline security incident handling.

3. Business continuity and crisis management

Essential and important entities must establish comprehensive business continuity and crisis management strategies to minimize service disruptions. These strategies should include redundancies and backups as part of a resilience system that can keep operations running, if in a degraded state, during major cybersecurity incidents. It’s also crucial to maintain continuous access to management, troubleshooting, and recovery infrastructure during an attack.

Tip: Serial consoles with out-of-band (OOB) management provide an alternative path to systems and infrastructure that doesn’t rely on the production network, ensuring 24/7 management and recovery access during outages and other major incidents. OOB serial consoles can also be used to create an isolated recovery environment (IRE) where teams can safely restore and rebuild critical services without risking ransomware reinfection.

4. Supply chain security

Organizations must implement supply chain security risk management measures to limit the risk of working with third-party suppliers. These include performing regular risk assessments based on the supplier’s security and compliance history, applying zero-trust access control policies to third-party accounts, and keeping third-party software and dependencies up-to-date.

Tip: User and entity behavior analytics (UEBA) software uses machine learning to analyze account activity on the network and detect unusual behavior that could indicate compromise. It establishes baselines for normal behavior based on real user activity, reducing false positives and increasing detection accuracy even with vendors and contractors who operate outside of normal business hours and locations.

5. Secure network and IT system acquisition, development, and maintenance

Entities must ensure the security of network and IT systems during acquisition, development, and maintenance. This involves, among other things, inspecting hardware for signs of tampering before deployment, changing default settings and passwords on initial startup, performing code reviews on in-house software to check for vulnerabilities, and applying security patches as soon as vulnerabilities are discovered.

Tip: Automation can streamline many of these practices while reducing the risk of human error. For example, zero-touch provisioning automatically configures devices as soon as they come online, reducing the risk of attackers compromising a system-default admin account. Automated vulnerability scanning tools can help detect security flaws in software and systems; automated patch management ensures third-party updates are applied as soon as possible.

6. Cybersecurity and risk-management assessments

Organizations must have a way to objectively assess their cybersecurity and risk-management practices and remediate any identified weaknesses. These assessments involve identifying all the physical and logical assets used by the company, scanning for potential threats, determining the severity or potential impact of any identified threats, taking the necessary mitigation steps, and thoroughly documenting everything to streamline any reporting requirements.

Tip: An AI-powered cybersecurity risk assessment tool uses large language models (LLMs) and other machine learning technology to automate assessments with greater accuracy than older solutions. These tools are often better at identifying novel threats than human assessors or signature-based detection methods, and they typically provide automated reporting to aid in NIS2 compliance.

7. Cybersecurity training

Essential and important entities must enforce cybersecurity training and basic security hygiene policies for all staff. This training should include information about the most common social engineering attacks, such as email phishing or vishing (voice phishing), compliant data handling practices, and how to securely create and manage account credentials.

Tip: Some cybersecurity training programs include attack simulations – such as fake phishing emails – to test trainees’ knowledge and give them practice identifying social engineering attempts. These programs help companies identify users who need additional education and periodically reinforce what they have learned.

8. Cryptography and encryption

NIS2 requires organizations to use cryptography to protect systems and data from tampering. This includes encrypting sensitive data and communications when necessary.

Tip: Roots of Trust (RoTs) are hardware security mechanisms providing cryptographic functions, key management, and other important security features. RoTs are inherently trusted, so it’s important to choose up-to-date solutions offering strong cryptographic algorithms, such as Trusted Platform Module (TPM) 2.0.

9. User access control and asset management

Entities must establish policies and procedures for employees accessing sensitive data, including least-privilege access control and secure asset management. This also includes mechanisms for revoking access and locking down physical assets when users violate safe data handling policies, or malicious outsiders compromise privileged credentials.

Tip: Zero trust security uses network micro-segmentation and highly specific security policies to protect sensitive resources. MFA and continuous authentication controls seek to re-establish trust each time a user requests access to a new resource, making it easier to catch malicious actors and preventing lateral movement on the network.

10. Multi-factor authentication (MFA) and encrypted communications

The final minimum requirement for NIS2 compliance is using multi-factor authentication (MFA) and continuous authentication solutions to verify identities, as described above. Additionally, entities must be able to encrypt voice, video, text, and internal emergency communications when needed.

Tip: MFA, continuous authentication, and other zero-trust controls should also extend to management interfaces, resilience systems, and isolated recovery environments to prevent malicious actors from compromising these critical resources. The best practice is to isolate management interfaces and resilience systems using OOB serial consoles to prevent lateral movement from the production network.

How ZPE streamlines NIS2 compliance

EU-based entities classified as essential or important have limited time to implement all the security policies, practices, and tools required for NIS2 compliance. Using vendor-neutral, multi-purpose hardware platforms to deploy new security controls can help reduce the hassle and expense, making it easier to meet the October deadline. For example, a Nodegrid serial console from ZPE Systems combines out-of-band management, routing, switching, cellular failover, SSL VPN and secure tunnel capabilities, and environmental monitoring in a single device. The vendor-neutral Nodegrid OS supports GuestOS and containers for any third-party software, including next-generation firewalls (NGFWs), Secure Access Service Edge (SASE), automation tools like Puppet and Ansible, and UEBA. Nodegrid devices have strong hardware Roots of Trust with TPM 2.0, selectable encrypted cryptographic protocols and cipher suite levels, and configuration checksumTM. Plus, Nodegrid’s Gen 3 OOB creates the perfect foundation for infrastructure isolation, resilience systems, and isolated recovery environments.

Looking to Upgrade to a Nodegrid serial console?

Looking to replace your discontinued, EOL serial console with a Gen 3 out-of-band solution? Nodegrid can expand your capabilities and manage your existing solutions from other vendors. Click here to learn more!

ZPE Systems Unveils IT Resilience Products at Cisco Live, Including Solution to Protect AI Investments

NSC Core Edition and Gate SR with Jetson module

Budget-friendly console server product and dual-CPU NVIDIA platform help organizations protect their infrastructure and AI investments.

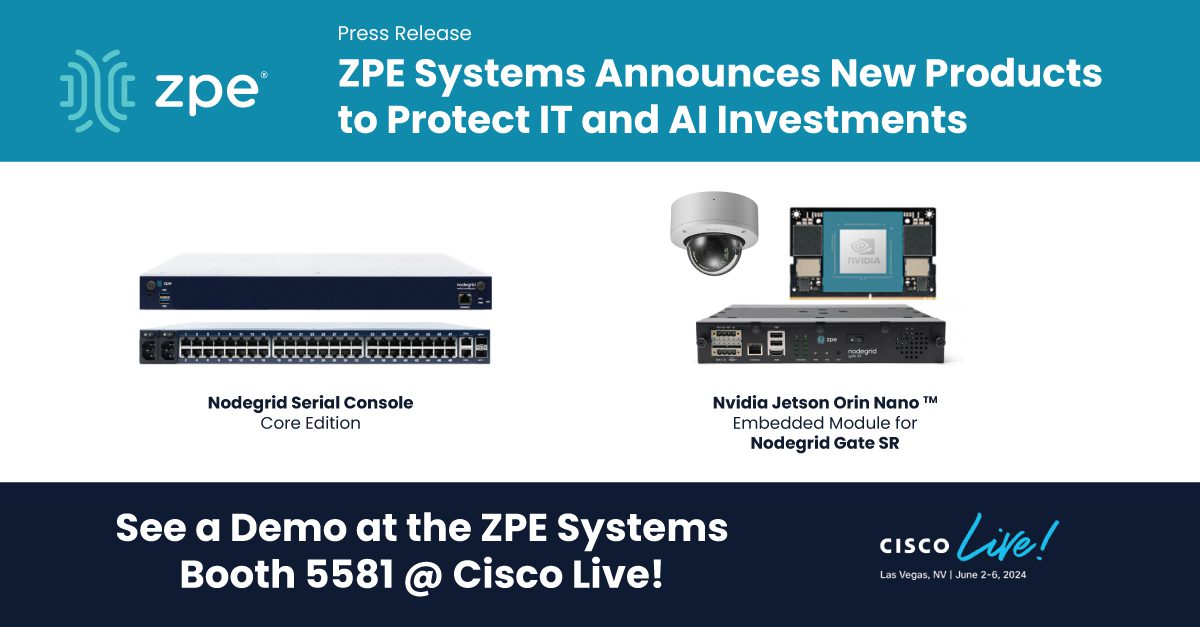
Fremont, CA — May 28, 2024 — ZPE Systems, a leader in network infrastructure and management solutions that is now part of Legrand, launches two new products at Cisco Live Las Vegas: the Nodegrid Serial Console Core Edition and the Nodegrid Gate SR platform with embedded NVIDIA Jetson Orin Nano™ module. These innovative products will empower organizations to better protect their vital IT infrastructure and NVIDIA AI investments from the growing risks of cyber-attacks.

The Nodegrid Serial Console Core Edition is a cost-effective third generation console server that resolves the vulnerabilities left by legacy console servers. It leverages drop-in Isolated Management Infrastructure (IMI) to fully separate management traffic from production networks. The creation of a separate management network provides physical and logical isolation from unauthorized users and cyber threats.  

“The first step in cybersecurity resiliency is proper IT hygiene, starting with the right architecture to remove anxiety from automated patching and recovery,” said Koroush Saraf, VP of Products and Marketing at ZPE Systems. “The Core Edition simplifies IMI, providing secure, isolated management access from any branch office or remote location via any LAN or WAN link type, including cellular connections. This gives customers a safe environment for patching or configuration rollback even during an outage or cyberattack.” 

Though IMI has been used primarily by hyperscalers and big tech brands, the Core Edition enables businesses of all sizes to build their own IMI networks and reap the benefits of a layered security approach at an affordable price. 

“With the NSCP Core Edition, our goal is to make big tech’s resilience practices accessible and affordable for all organizations,” emphasizes Arnaldo Zimmermann, Cofounder of ZPE and VP/GM at Legrand. “Now, anyone can drop in our Gen 3 console server, create their IMI, and close those vulnerabilities created by their outdated devices.” 

ZPE is also releasing the Nodegrid Gate SR with embedded Jetson module. This new platform internally hosts the NVIDIA Jetson Orin Nano™ module, serving as an out-of-band device for initial bring-up, patching, and upgrading when running NVIDIA workloads. ZPE’s Gate SR with embedded Jetson module offers a dual-CPU platform that uses the same IMI concept for provisioning AI workloads via out-of-band path and allows customers to deploy, manage, and upgrade remotely via ZPE Cloud. This new Nodegrid platform enables organizations to improve industrial floor safety, campus security, and manufacturing quality control, by deploying 3rd party computer vision software at the edge. Organizations can now add resilience and recovery to the fleet of their NVIDIA AI workloads with ZPE embedded or external AI hardware devices.

To learn more, visit the Core Edition page or meet us in booth 5581 at Cisco Live.