Providing Out-of-Band Connectivity to Mission-Critical IT Resources

Uplogix 5000 Local Manager EOL Best Replacement Options
A businessman considers two different options, such as which model to replace the Uplogix 5000 Local Manager EOL with
The Uplogix 5000 Local Manager line of serial console servers will go end-of-life (EOL) on December 31, 2025, with software support ending on December 31, 2023. Uplogix recommends the LM83X as a replacement model, but there are some concerns and limitations to be aware of before you make this switch. In this blog, we’ll compare the new LM83X to the Uplogix 5000 Local Manager and discuss an alternative replacement option.

About the Uplogix 5000 Local Manager

The 5000 Local Manager is Uplogix’s flagship serial console, providing out-of-band (OOB) management for up to 38 devices. Management access is delivered via two 10/100/1000 Mbps Base-T Ethernet interfaces, with a slot available for an optional v.92 modem, cellular SIM, RS-232 card, or fiber module.

All Uplogix serial console servers use the Local Manager software platform for monitoring and management. This software includes automation capabilities for routine management, maintenance, and recovery tasks. However, the Local Manager platform does not support the use of third-party automation tools or custom scripts. In addition, while the 5000 Local Manager hardware can access and manage devices from other vendors, the management software is not easily extensible by the customer. That means users are locked into the vendor’s feature roadmap and automation capabilities.

Uplogix 5000 Local Manager tech specs:

System
CPU Intel 1.3 GHz Atom
RAM 1 GB
Storage 40 GB 2.5″ SSD
Local interfaces – Up to 38 x RS-232 Serial ports

– Up to 8 x dedicated 10/100/1000 Mbps Ethernet ports

– 1 x RS-232 Power management port

– 1 x RJ-11 Modem port

– 2 x USB ports

Management interfaces – 2 x 10/100/1000 Mbps Base Ethernet interfaces

– 1 x RS-232 Console port

Option slots 1 available for field installable internal modems (v.92, cellular, or RS232) or a fiber module
Expansion slots 2 available for:

– 8 Port Serial card

– 16 Port Serial card

– 8 Port Ethernet card (10/100/1000 Mbps)

Power Dual AC or Dual DC
Features
Vendor-neutral Heterogeneous device access and management
Security – Secure Shell (SSHv2)

– TACACS and Radius authentication

– IP and caller ID filtering

– FIPS 140-2 Level 2

– Automatic session management to prevent unauthorized access

– Enforces RBAC, command-level authorization

– Logging of user access, device changes, and session activity

OOB/Failover – POTS lines

– Cellular modems

– Fiber

– DSL

– Satellite

Device monitoring In-band or out-of-band data collection every 5 to 30 seconds
Environmental monitoring – Temperature

– Humidity

Remote access – SSHv2

– Secure access to web-only management interfaces

Automation Rule-based engine for automation of routine management tasks

– No third-party automation

– cannot be easily expanded by customer

Remote power management Monitors and controls power, can remotely restart a managed device

Uplogix ended the sale of the 5000 Local Manager at the end of 2020, with the EOL date set at 12/31/2022. The EOL Uplogix 5000 product SKUs are listed below.

Uplogix 5000 EOL replacement option: The Uplogix LM83X

Uplogix released a new Local Manager serial console to replace the 5000: the LM83X. This model can manage up to 104 devices through the use of three expansion bays for additional serial and Ethernet ports. In addition to two 10/100/1000 Base-T Ethernet interfaces, the new Local Manager has a 1-Gbps SFP port for faster management access.

The LM83X runs on the same Local Manager software platform as its predecessor, which means it also suffers from vendor lock-in and limited automation capabilities. In addition, the Uplogix platform has some advanced security features like FIPS 140-2 Level 2 certification and support for Radius authentication, but it doesn’t support SAML 2.0 for cross-domain single sign-on. That makes it difficult to extend Zero Trust Security best practices to the out-of-band management network, which can leave the entire enterprise vulnerable to an attack.

Another crucial consideration is that Uplogix was just bought by Lantronix, one of its biggest competitors. It’s still unknown how Uplogix will be integrated, leaving existing customers uncertain about the future of their hardware and software support contracts.

Uplogix 5000 Local Manager vs. LM83X tech specs:

Uplogix 5000 Uplogix LM83X
System
CPU Intel 1.3 GHz Atom Not listed
RAM 1 GB Not listed
Storage 40 GB 2.5″ SSD 256 GB NVMe
Local interfaces – Up to 38 x RS-232 Serial ports

– Up to 8 x dedicated 10/100/1000 Mbps Ethernet ports

– 1 x RS-232 Power management port

– 1 x RJ-11 Modem port

– 2 x USB ports

– Up to 104 x RS-232 Serial ports

– 1 x USB-A port

– 1 x USB-C port

Management interfaces – 2 x 10/100/1000 Mbps BaseT Ethernet interfaces

– 1 x RS-232 Console port

– 2 x 10/100/1000 BaseT Ethernet ports

– 1 x 1-Gbps SFP port

Option slots 1 available for field installable internal modems (v.92, cellular, or RS232) or a fiber module 1 available for field installable internal modems (v.92, cellular, or RS232) or a fiber module
Expansion slots 2 available for:

– 8 Port Serial card

– 16 Port Serial card

– 8 Port Ethernet card (10/100/1000 Mbps)

3 available for:

– 8 Port, 16 Port, or 32 Port Serial cards

– 8 Port Ethernet card (10/100/1000 Mbps)

– LCD keypad

Power Dual AC or Dual DC Redundant internal universal power
Features
Vendor-neutral Heterogeneous device access and management Heterogeneous device access and management
Security – Secure Shell (SSHv2)

– TACACS and Radius authentication

– IP and caller ID filtering

– FIPS 140-2 Level 2

– Automatic session management to prevent unauthorized access

– Enforces RBAC, command-level authorization

– Logging of user access, device changes, and session activity

– Secure Shell (SSHv2)

– TACACS and Radius authentication

– IP and caller ID filtering

– FIPS 140-2 Level 2

– Automatic session management to prevent unauthorized access

– Enforces RBAC, command-level authorization

– Logging of user access, device changes, and session activity

OOB/Failover – POTS lines

– Cellular modems

– Fiber

– DSL

– Satellite

– POTS lines

– Cellular modems

– Fiber

– DSL

– Satellite

Device monitoring In-band or out-of-band data collection every 5 to 30 seconds In-band or out-of-band data collection every 5 to 30 seconds
Environmental monitoring – Temperature

– Humidity

– Temperature

– Humidity

Remote access – SSHv2

– Secure access to web-only management interfaces

– SSHv2

– Secure access to web-only management interfaces

Automation Rule-based engine for automation of routine management tasks

– No third-party automation

– Not easily expandable

Rule-based engine for automation of routine management tasks

– No third-party automation

– Not easily expandable

Remote power management Monitors and controls power, can remotely restart a managed device Monitors and controls power, can remotely restart a managed device

Alternative Uplogix 5000 EOL replacement options from ZPE Systems

The Uplogix Local Manager solutions are what’s known as second generation, or Gen 2, out-of-band serial consoles. That means they provide heterogeneous device management, built-in security features, and some automation capabilities. However, they fall short of true vendor neutrality, which makes it impossible to achieve end-to-end network automation. In addition, without SAML 2.0 support, Uplogix devices are vulnerable to compromise by malicious actors who could use them to gain control over the production network.

To get secure and extensible OOB management access with end-to-end automation capabilities, you need a Gen 3 out-of-band serial console solution like the Nodegrid platform from ZPE Systems.

About the Nodegrid Serial Console Plus (NSCP)

The Nodegrid Serial Console Plus (NSCP) provides Gen 3 OOB management for up to 96 devices, including support for Cisco and legacy pinouts. Management access is delivered via two Gigabit Ethernet ports, two SFP+ ports, or v.92 modem, with out-of-band and network failover to dual SIM 5G/4G LTE cellular, WiFi, or v.92 modem.

All Nodegrid devices can be managed with one of two offerings: the on-premises Nodegrid Manager software or the ZPE Cloud application. Both solutions are easily extensible with your choice of third-party applications for infrastructure automation and orchestration, security, big data analytics, and more. Nodegrid hardware can even directly host other vendors’ software, giving you a convenient platform for Docker containers, Infrastructure as Code (IaC) playbooks, Security Service Edge (SSE) applications, and SD-WAN solutions.

The Gen 3 NSCP protects your infrastructure using Zero Trust best practices like SAML 2.0 support, disk encryption, and secure boot. ZPE Systems is also the only serial console vendor with a FIPS 140-3 pre-certification, making them the most secure OOB solution on the market.

Head-to-head: Uplogix 5000 vs. Uplogix LM83X vs. NSCP tech specs

Uplogix 5000 Uplogix LM83X Nodegrid Serial Console Plus (NSCP)
System
CPU Intel 1.3 GHz Atom Not listed Intel x 86, 64 bit
RAM 1 GB Not listed 4 GB / 8 GB
Storage 40 GB 2.5″ SSD 256 GB NVMe 32 GB FLASH
Local interfaces – Up to 38 x RS-232 Serial ports

– Up to 8 x dedicated 10/100/1000 Mbps Ethernet ports

– 1 x RS-232 Power management port

– 1 x RJ-11 Modem port

– 2 x USB ports

– Up to 104 x RS-232 Serial ports

– 1 x USB-A port

– 1 x USB-C port

– Up to 96 x RS-232 Serial ports

– 2 x 1-GbE Ethernet

– 2 x SFP+

– 2 x USB 3.0 ports

– 1 x HDMI port

– 1 x Console port

– can manage devices RS-232, USB, IPMI, SSH,Telenet, WebUI, RESTAPI

– can manage over 500 devices (mix of serial and IP) on a single appliance

Management interfaces – 2 x 10/100/1000 Mbps BaseT Ethernet interfaces

– 1 x RS-232 Console port

– 2 x 10/100/1000 BaseT Ethernet ports

– 1 x 1-Gbps SFP port

– 2 x 1-GbE Ethernet

– 2 x SFP+

– 1 x v.92 Modem

Option slots 1 available for field installable internal modems (v.92, cellular, or RS232) or a fiber module 1 available for field installable internal modems (v.92, cellular, or RS232) or a fiber module – Wi-Fi

– Dual SIM 5G/4G LTE cellular

– v.92 modem

Expansion slots 2 available for:

– 8 Port Serial card

– 16 Port Serial card

– 8 Port Ethernet card (10/100/1000 Mbps)

3 available for:

– 8 Port, 16 Port, or 32 Port Serial cards

– 8 Port Ethernet card (10/100/1000 Mbps)

– LCD keypad

Power Dual AC or Dual DC Redundant internal universal power Single or Dual AC, Dual DC
Features
Vendor-neutral Heterogeneous device access and management Heterogeneous device access and management – Vendor-neutral device access and management

– Can directly host third-party apps for security, automation, etc.

– Platform integrates with third-party solutions not hosted on Nodegrid hardware

– Can extend Zero Touch Provisioning to other vendor devices

Security – Secure Shell (SSHv2)

– TACACS and Radius authentication

– IP and caller ID filtering

– FIPS 140-2 Level 2

– Automatic session management to prevent unauthorized access

– Enforces RBAC, command-level authorization

– Logging of user access, device changes, and session activity

– Secure Shell (SSHv2)

– TACACS and Radius authentication

– IP and caller ID filtering

– FIPS 140-2 Level 2

– Automatic session management to prevent unauthorized access

– Enforces RBAC, command-level authorization

– Logging of user access, device changes, and session activity

Hardware Security:

– TPM 2.0

– Encrypted solid-state disk

– UEFI BIOS with protection

– Secure boot (signed OS)

– Geofencing

Authentication:

– Local

– RADIUS

– TACACS+

– LDAP/AD

– NIS and Kerberos

– SAML 2.0 (Okta, Duo, PingID, ADFS)

OOB/Failover – POTS lines

– Cellular modems

– Fiber

– DSL

– Satellite

– POTS lines

– Cellular modems

– Fiber

– DSL

– Satellite

– 5G/4G/LTE

– V.92 modem

– Wi-Fi

Device monitoring In-band or out-of-band data collection every 5 to 30 seconds In-band or out-of-band data collection every 5 to 30 seconds – Keystroke logging

– Logging to ZPE Cloud, NFS, Local

– Alert on cable disconnects

Environmental monitoring – Temperature

– Humidity

– Temperature

– Humidity

– Particulate

– Smoke

– Airflow & temperature

– Proximity/door lock

– Temp & humidity

– 7-port USB hub

– 8-port GPIO

– 4-port Relay

Remote access – SSHv2

– Secure access to web-only management interfaces

– SSHv2

– Secure access to web-only management interfaces

– SSH direct to consoles

– ZPE Cloud (web) or Nodegrid Manager (local)

Automation Rule-based engine for automation of routine management tasks

– No third-party automation

– cannot be easily expanded by customer

Rule-based engine for automation of routine management tasks

– No third-party automation

– cannot be easily expanded by customer

– ZPE Cloud

– Chef

– Docker

– KVM Hypervisor

– Puppet

– Python

– RedHat Ansible

– Ruby

– ShellScript

– Node.js JavaScript

Remote power management Monitors and controls power, can remotely restart a managed device Monitors and controls power, can remotely restart a managed device – Support major power strip manufacturers

– Power management integrated with serial session (escape sequence in the serial session or power buttons in web serial session)

– Power control of VMs

– Access rights for users and user groups

The Uplogix LM83X is the direct replacement for the EOL Uplogix 5000 Local Manager, which means it provides the same base capabilities with some upgraded hardware features. However, this also means the LM83X suffers from the same limitations as its predecessor, namely a lack of SAML 2.0 integration and a closed management platform that doesn’t support third-party automation. To achieve end-to-end network automation, you need a Gen 3 OOB serial console solution like the Nodegrid Serial Console Plus.

Uplogix 5000 Local Manager EOL product SKUs

Product SKU Description End of Hardware Support End of Software Support End of Life End of Sale
71-1321-10 FIPS Uplogix 5000 Local manager, 14 Serial, V.92 modem 12/31/2023 12/31/2025 12/31/2025 12/31/2020
61-5001-01 Uplogix 5000 8 Port Serial Expansion Module w/LMS-FIPS 12/31/2023 12/31/2025 12/31/2025 12/31/2020
61-5500-30 Uplogix 5000 Local Manager 12/31/2023 12/31/2025 12/31/2025 12/31/2020
61-5500-33 FIPS Uplogix 5000 Local Manager 12/31/2023 12/31/2025 12/31/2025 12/31/2020

Ready to replace your Uplogix 5000​?

To replace your Uplogix 5000 Local Manager EOL serial console server with the Gen 3 Nodegrid Serial Console Plus, Contact ZPE Systems today!
Request a Demo Today

The Growing Role of Hybrid Cloud in Digital Transformation

cloud in digital transformation

Digital transformation is a broad term for the act of changing and improving your business processes through the implementation of new technologies. The cloud plays a major role in digital transformation because it provides a flexible, scalable, and accessible environment that’s ideal for a wide range of business applications. However, there are still many processes that are better suited for a traditional, on-prem data center or colocation infrastructure due to cost, security, or performance concerns.

Combining public cloud platforms with private infrastructure is known as hybrid cloud infrastructure, and it allows organizations to map their business processes and applications to the environments best suited to run them. In this post, we’ll discuss the role of hybrid cloud in digital transformation and provide tips for managing and orchestrating a hybrid infrastructure.

The importance of hybrid cloud in digital transformation

While the public cloud offers many advantages, there are a variety of reasons why an organization would want or need to keep some services private.

For example, a company doing business in an industry that’s subject to strict data privacy regulations—like finance, defense, or healthcare—may want to keep sensitive data in an on-premises data center so they can maintain complete control over the security and access control measures. At the same time, they might have other processes and applications that aren’t as high-risk and could benefit from the flexibility of cloud infrastructure.

Sometimes, an organization will migrate a workload to the cloud, only to bring it back in-house later. For instance, cloud services can reduce costs for certain applications but can increase costs for others. Most public cloud providers charge extra for data egress—transferring data of their systems and to another cloud or on-premises. That means applications that require a lot of data egress can be much more expensive to run in the cloud. That cost increase may be worthwhile in the long run to achieve optimal scalability and flexibility, but with a recession looming, many organizations are sacrificing those big picture goals to cut costs for short-term survival.

One of the biggest use cases for hybrid cloud in digital transformation is a gradual cloud migration. Digital transformation is a journey, and along the way, many organizations end up in a hybrid state because they’ve successfully moved some of their processes to the cloud but have others that still live in the data center. For example, a business may send some of their data analysis workflows to a business intelligence application in the cloud but then have an on-premises DCIM tool analyzing the same data in the data center. They eventually transition from hybrid cloud to a pure cloud or multi-cloud environment once they’ve finished migrating all their workloads to the cloud.

Hybrid cloud is one of the most popular enterprise infrastructure models because it’s flexible and affordable, allowing organizations to make the digital transformation journey at their own pace and in their own way.

Tips for managing hybrid cloud infrastructure

The most effective hybrid cloud deployment provides a single, seamless digital environment for business applications and resources, with centralized workload and infrastructure orchestration that works across all platforms and data centers. Let’s discuss how to achieve this ideal hybrid cloud deployment.

Vendor-agnostic platforms

To create a seamless environment in which workflows move effortlessly between the cloud and the data center to deliver a simple and unified experience to end-users, you need all your public cloud, private cloud, and data center solutions to work together. The best way to ensure this is by only using vendor-agnostic (vendor-neutral) hardware and software from the very beginning, but for most organizations that ship has already sailed. The next best option is to use a vendor-agnostic management platform that’s able to hook into all those closed solutions and control them equally. These solutions allow you to orchestrate workloads across public cloud, private cloud, and legacy environments without needing to replace all the systems and software already in place.

SD-WAN

A hybrid cloud deployment can create some networking challenges because of the need to orchestrate WAN (wide area networking) connections across multiple clouds and data centers, each of which may have a different networking infrastructure in place. Software-defined wide area networking, or SD-WAN, helps to reduce the complexity of hybrid cloud networking by separating the control and management processes from the underlying WAN hardware.

SD-WAN virtualizes network management functions as software or script-based configurations, which enables centralized and automated deployment. With the aid of a vendor-agnostic management platform, SD-WAN benefits hybrid cloud infrastructure by consolidating control behind a single pane of glass. This gives administrators the ability to easily orchestrate, optimize, and secure the entire distributed network.

Automation

Automation plays a key role in digital transformation because it can speed up workflows while reducing the risk of human error. For example, using automation to deploy new infrastructure means administrators can provision many resources in a short amount of time while ensuring consistent configurations.

Automation also improves security, both by reducing the rate of misconfigurations and by ensuring all infrastructure is patched as soon as possible. Unpatched infrastructure leaves you vulnerable to hacks and ransomware, but keeping track of updates for so many vendor solutions in so many different places can be challenging. Automation can help by ensuring patches are pushed out to hybrid cloud infrastructure solutions as soon as they become available. 

Vendor agnostic platforms, SD-WAN, and automation are key tools that help organizations more effectively utilize a hybrid cloud in their digital transformation journey.

The role of ZPE Systems in digital transformation

ZPE Systems offers a range of vendor-agnostic network management solutions to help your organization achieve digital transformation. The Nodegrid platform can dig its hooks into your legacy and mixed-vendor infrastructure to provide a common interface from which to manage and orchestrate your entire network architecture. Plus, Nodegrid can host or integrate with your choice of SD-WAN solutions to help you consolidate your tech stack while delivering optimized performance and security.

Contact ZPE Systems today

To learn more about the role of hybrid cloud in digital transformation.

Contact Us

What Is uCPE, and How Does It Benefit Enterprise Customers?

ucpe

uCPE stands for universal Customer Premises Equipment. A uCPE box is a general purpose networking device used to run virtual network functions, or VNFs. VNFs are essentially software versions of network devices such as routers, switches, and firewalls. That means you can consolidate an entire networking tech stack into a single uCPE box, saving money and reducing management complexity.

Despite the promise of uCPE, the technology has been slow to catch on. In this article, we’ll explore the reasons for the lack of popularity of early uCPE before discussing how newer generations overcome these issues to deliver cost savings, simplified management, and other benefits to enterprise customers.

The shortcomings of gen 1 uCPE

Early uCPE devices were generally provided by telecoms and ISPs to host their specific networking software. Customers didn’t get to choose the software or virtualization solutions—they had to use whatever the vendor gave them. That meant enterprises didn’t have the flexibility to swap out VNFs and software to get the specific features or pricing they wanted, and they couldn’t continue using existing solutions that they really liked.

However, the larger issue was that the virtualization technology itself was ahead of its time. Many organizations still didn’t have use cases that justified the business disruption and expense of swapping out networking infrastructure with virtualized solutions. Plus, software-based networking was so new that many network administrators and engineers didn’t have the skills and experience needed to configure, deploy, and manage fully virtualized tech stacks.

Due to these limitations, enterprises showed minimal interest in uCPE for a long time, leading many to believe that the technology would die out entirely. Instead, forward-thinking hardware and software vendors continued to improve uCPE technology to overcome these shortcomings. In addition, enterprises have been pushing their computing and business operations out to remote locations at the network edge, resulting in the rapid adoption of SD-WAN (software-based wide-area networking) solutions for distributed network management. A greater interest in software-based networking technology, and a need for hardware capable of running that software, has led to a renewed enthusiasm for uCPE.

The next evolution of uCPE

The current generation of uCPE focuses on delivering a truly universal, vendor-neutral platform from which to host, manage, and troubleshoot an entire consolidated tech stack. This is provided in two parts:

  1. The device itself, which runs on an open, Linux-based operating system and supports multiple pinout standards.
  2. An orchestration platform which consolidates the monitoring and management of all uCPE solutions behind a single pane of glass.

Through its a vendor-agnostic hardware, software, and orchestration platform, uCPE benefits enterprise customers in numerous ways, including:

Vendor freedom

Next-gen uCPE devices are capable of hosting any software or virtualization solution from any vendor. This gives enterprise customers the ability to shop around for the best features and pricing for their particular use case. If customers already have a software-based networking solution that works well for them, they can simply migrate it to the uCPE with minimal hassle.

Tech consolidation

A single uCPE box can take the place of an entire rack of networking equipment, reducing the number of devices to install, license, and maintain. This is especially vital for organizations that want to expand their operations to branch offices, edge data centers, and even hard-to-reach locations like oil rigs and research stations. Tech consolidation reduces the time and expense required to deploy remote infrastructure.

Centralized management

The current generation of uCPE includes an orchestration platform capable of observing and controlling the entire distributed network of uCPE boxes and connected infrastructure. Enterprises can deploy hundreds or even thousands of uCPE boxes to locations all over the globe, but they only need to log in to one platform to manage them all. uCPE gives organizations the ability to orchestrate network functions, monitor remote infrastructure, and troubleshoot and respond to issues from behind a single pane of glass, which results in simplified and optimized network management.

SD-WAN capabilities

As organizations have sped up their SD-WAN adoption plans in response to the rise of remote work, edge computing, and distributed network management, the need for universal networking hardware has also quickly increased. Next-gen uCPE devices are the perfect hosts for SD-WAN software solutions because they allow for easy integration with the underlying WAN infrastructure, which run as VNFs on the same box. That means enterprises don’t need to invest in new SD-WAN-capable routers and gateways for each remote site. Plus, with a uCPE orchestration platform, it is easier to view and control the entire SD-WAN architecture. 

To take advantage of the benefits promised by uCPE technology, you need to ensure that you choose a platform that’s truly vendor-neutral to support your choice of SD-WAN and VNF solutions. The hardware also needs to be powerful enough to run your entire edge networking stack from a single box.

Universal network management with Nodegrid

Nodegrid is a next-gen uCPE platform that delivers universal infrastructure orchestration for enterprise customers. Nodegrid’s flexible hardware and open OS give you the freedom to bring your choice of networking devices, SD-WAN solutions, and VNFs. Nodegrid devices are built with CPU and memory headroom and expansive storage options so you can run your entire branch from a single box. Plus, the ZPE Cloud infrastructure orchestration platform gives you complete control over your distributed network, including third-party automation playbooks and workflows.

Ready to learn more?

To learn more about Nodegrid next-gen uCPE, contact ZPE Systems today.

Contact Us

Network Engineers: 5 Must-Have Tools During a Slow Economy

Network Engineers: 5 Must-Have Tools During a Slow Economy

Network engineers need powerful tools to keep digital services online and customers happy. This is especially true during economic downturn, when organizations must freeze hiring and put more strain on existing staff. Revenue relies on network availability, and with experts predicting a recession this winter, significant operational challenges are inevitable for most organizations.

The burden of overcoming these challenges falls on network engineers. Success means maintaining reliable services and reaping any professional benefits (salary increases, promotions, etc.). Failure, on the other hand, means the very realistic possibility of major business losses and job cuts, including yours.

In order to make sure you don’t fall into the latter scenario, here are five must-have tools and techniques to help network engineers overcome these challenges.

Tool 1. OOBI-LAN™

Out-of-band (OOB) management is an essential part of a network engineer’s toolkit. At the conceptual level, out-of-band is meant to provide management access to production equipment, even if the production equipment is offline.

One major problem is that many organizations invest a lot of time and money into their production infrastructure, but not into any dedicated OOB infrastructure. In other words, they deploy OOB solutions that rely in part on their production equipment, such as OOB VLANs connected to in-band switches. All it takes is a mistake, misconfiguration, or attack to bring down the production and management networks, leaving network engineers to rebuild the entire system from scratch while their services remain offline to customers. This is simply not acceptable in a slow economy, where the business’ resources and revenue are already too thin.

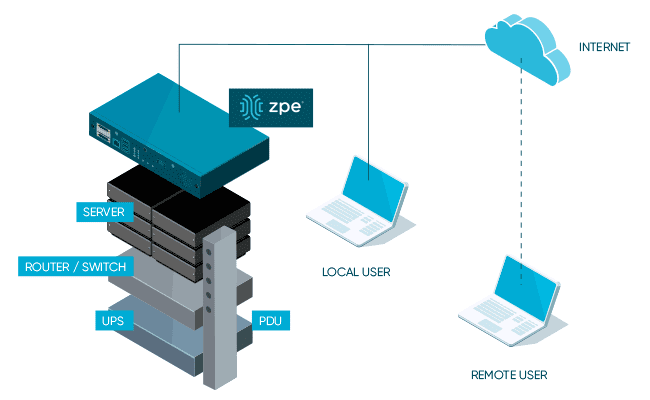
From the pandemic lockdowns, organizations have learned that they need a way to more quickly recover their network locations. According to the Uptime Institute’s 2022 Outage Analysis, outages lasting longer than 24 hours increased to nearly 30% in 2021. This has led many to build dedicated OOB infrastructure for the LAN (OOBI-LAN). They deploy a serial console locally to establish connectivity to the management ports of their sensitive equipment. Network engineers must use this serial console to access their production infrastructure. This serial console minimizes the attack surface since it’s the only device connected to the Internet, and allows network engineers to restore services even if production equipment is down.

Tool 2. OOBI-WAN™

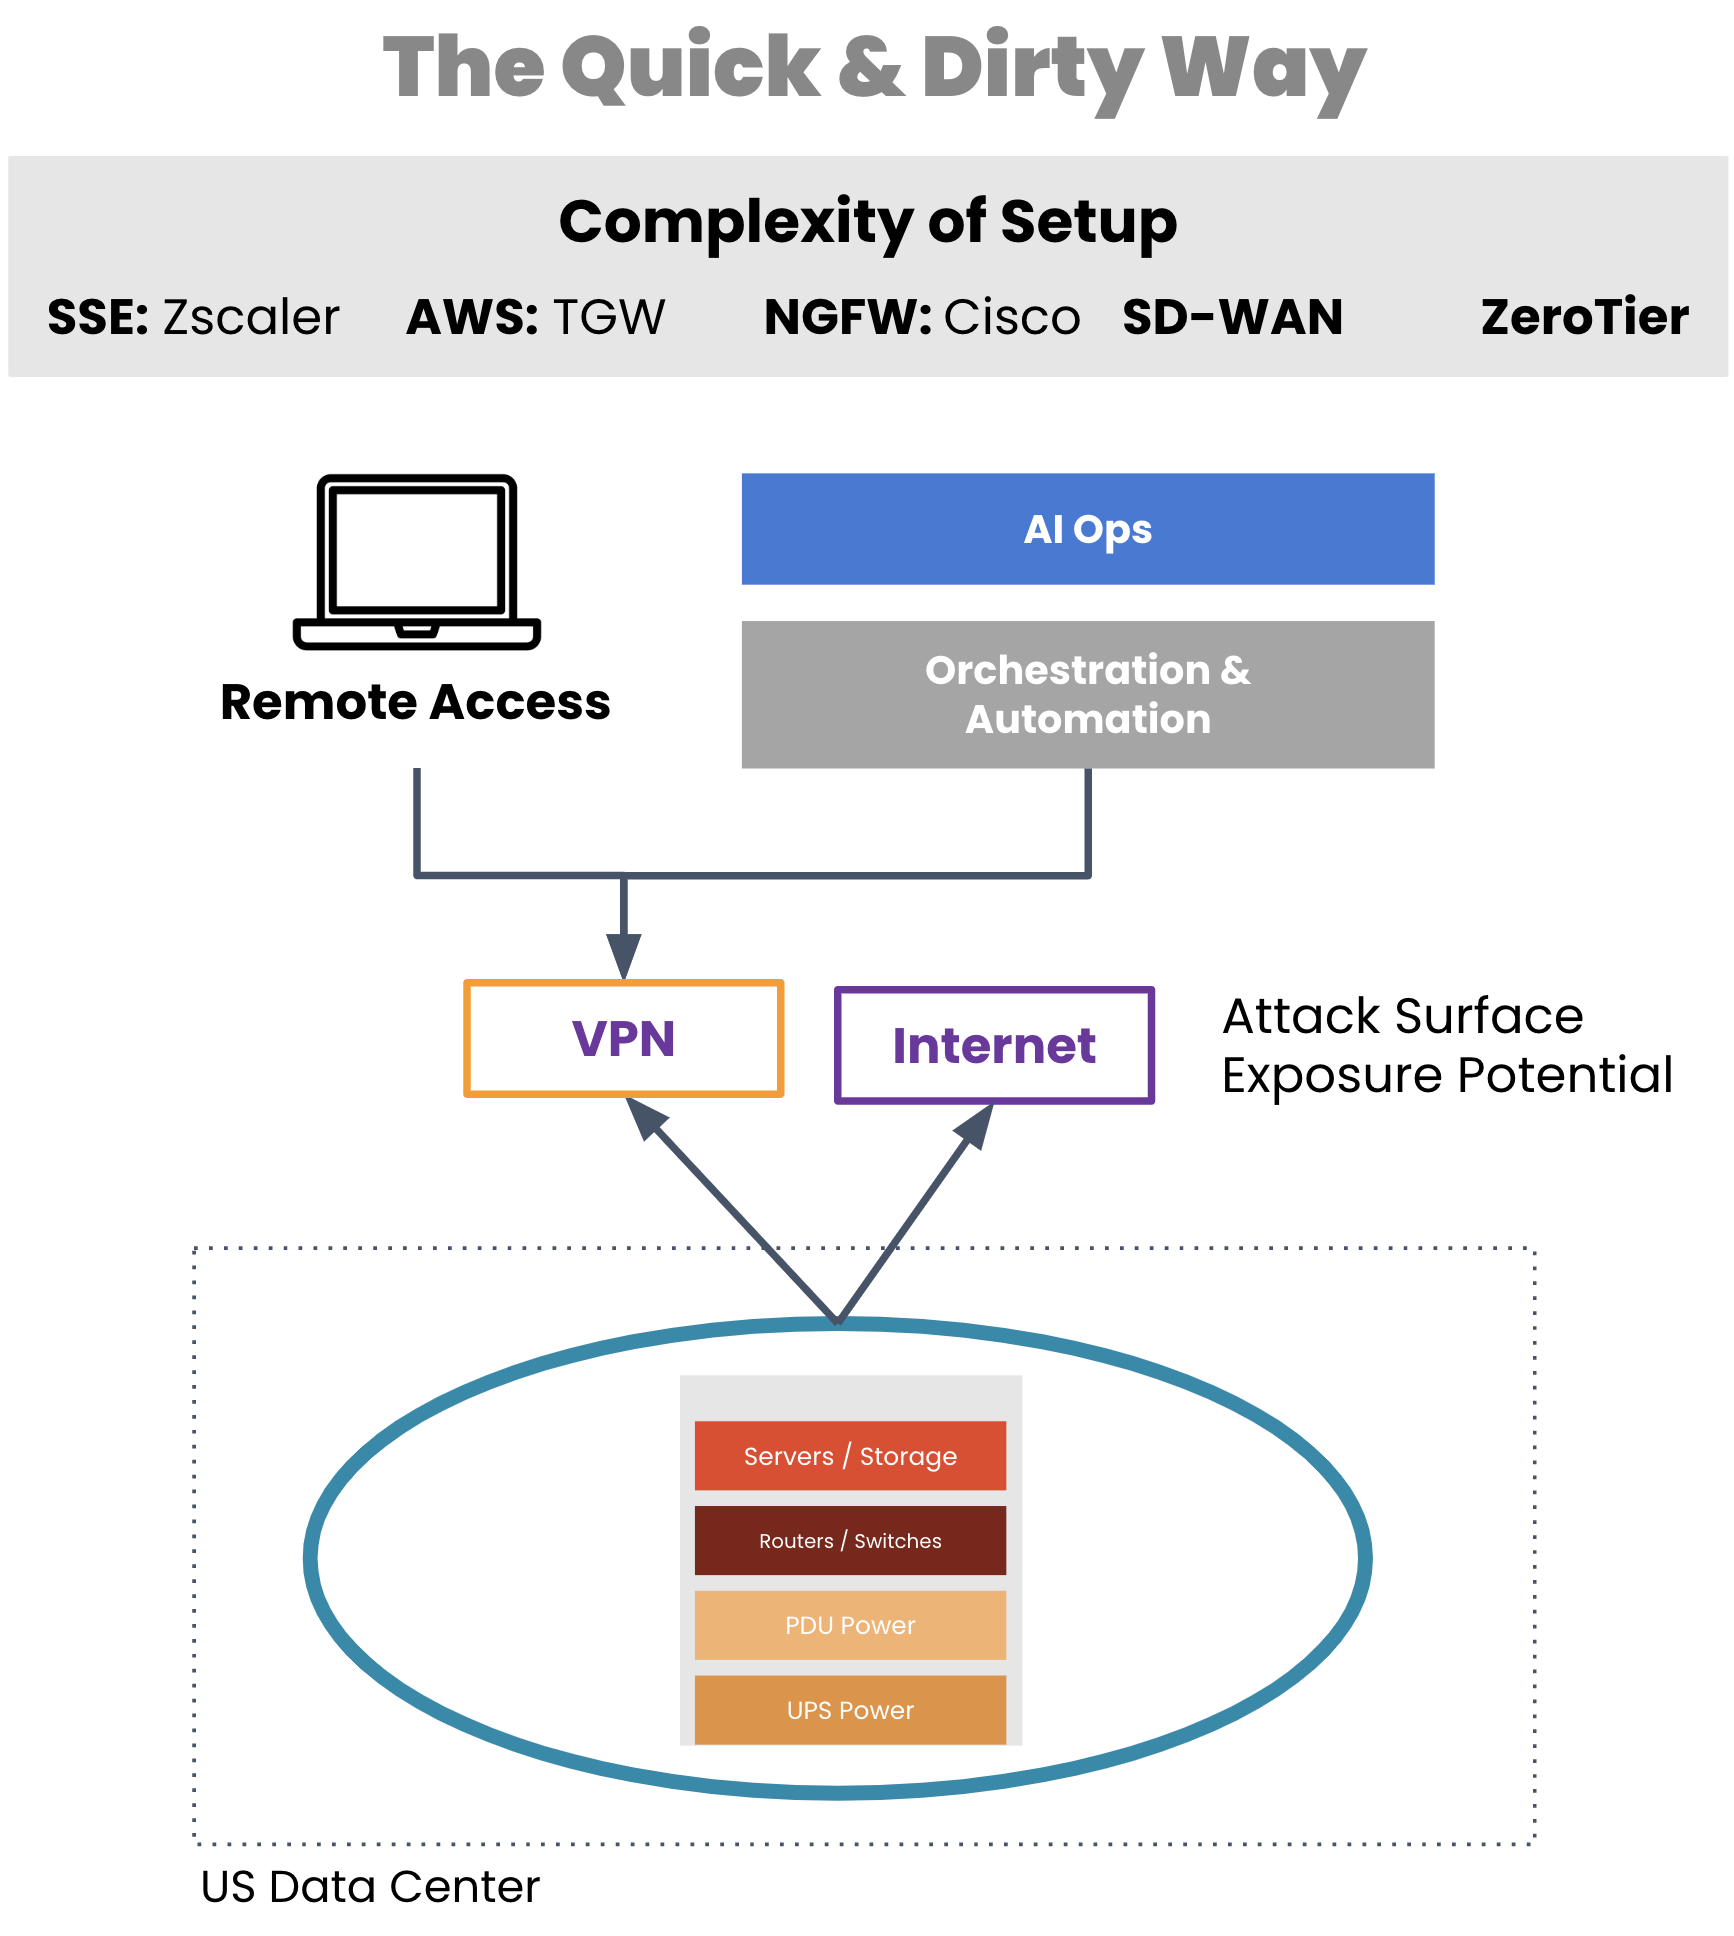
A critical tool for network engineers is out-of-band that enables remote WAN management. But typically, organizations employ a WAN management strategy that also relies on their production infrastructure, such as for creating VPN tunnels for management traffic. If a VPN tunnel becomes broken or the production gear fails, network engineers are suddenly left without remote access to their equipment.

Aside from a lack of availability, traditional OOB access comes with real security risks. Exposing LTE modems to the Internet, leveraging untrusted third-party VPN services, using OOB hardware that’s old and unpatched, and worse — exposing the management port of devices to public Internet. All of these are attack surfaces, any of which can give access to your infrastructure and be used as the pivot point to get to the rest of the infrastructure.

traditional WAN management approach

Image: Management access depends on production equipment to establish VPN tunnels. 

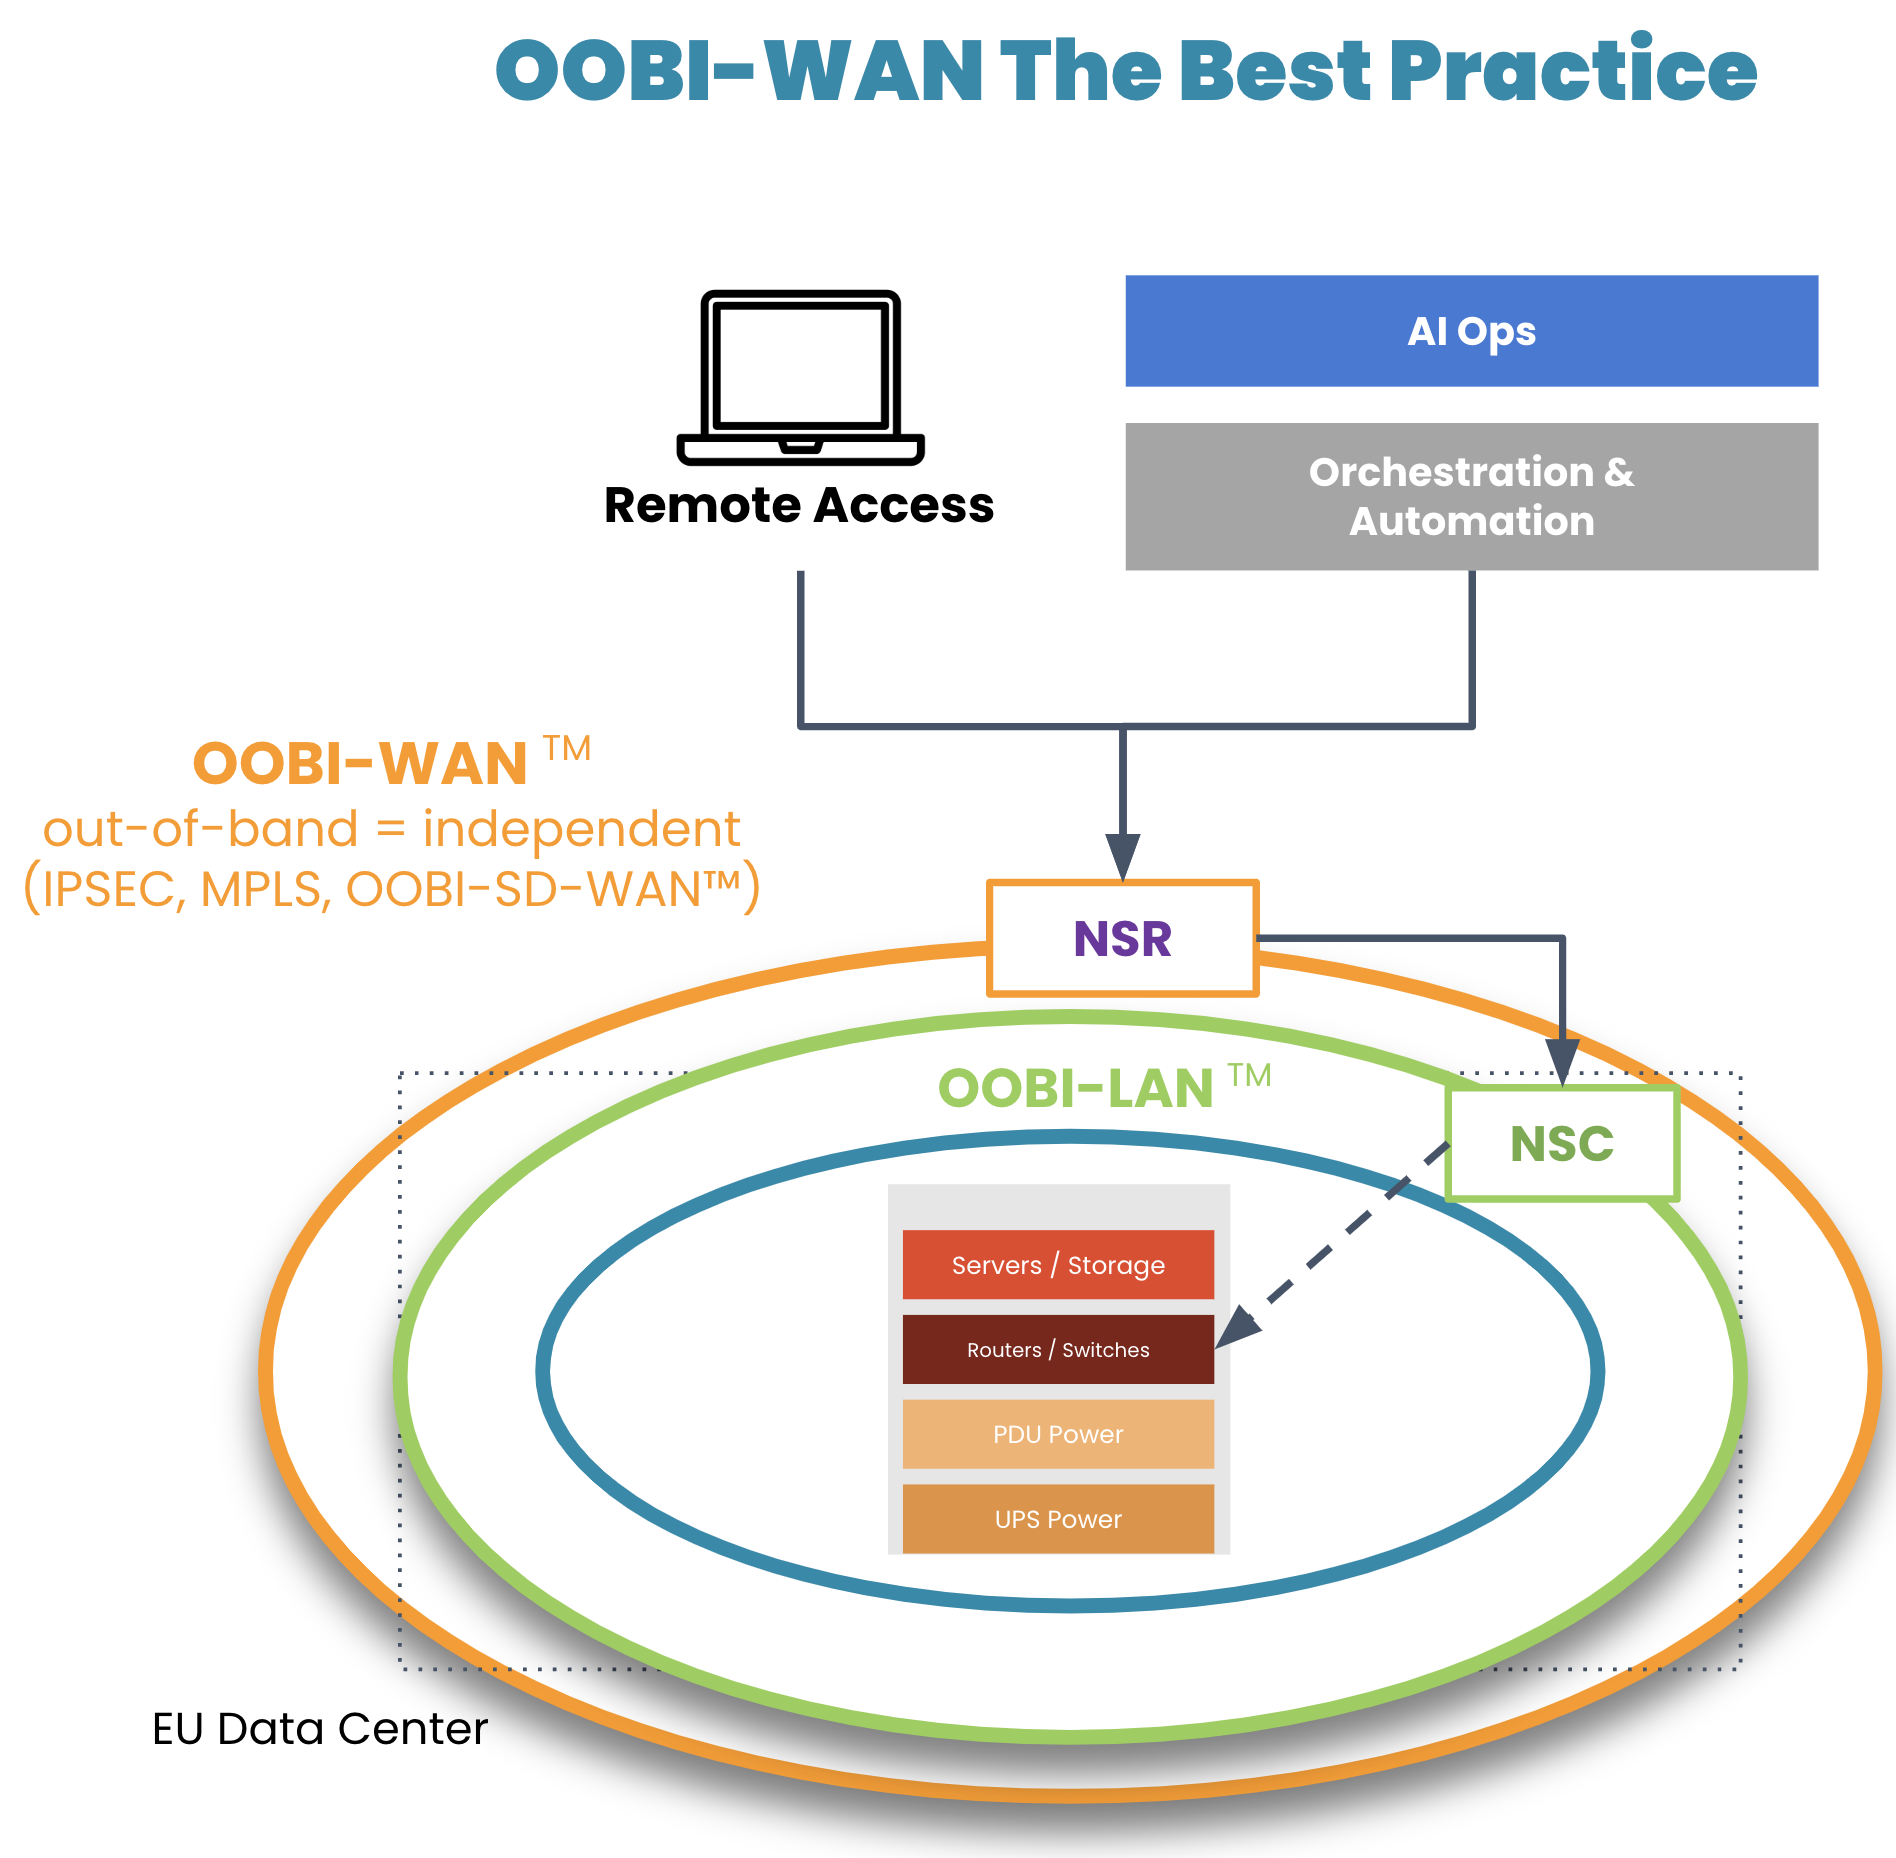
On top of their OOBI-LAN, organizations have built dedicated OOB infrastructure for the WAN (OOBI-WAN – there’s a Star Wars reference somewhere in there) for added resilience against these scenarios.

OOBI-WAN is the WAN best practice

Image: OOBI-WAN and OOBI-LAN create a fully separate out-of-band infrastructure that can be used to completely rebuild production infrastructure. 

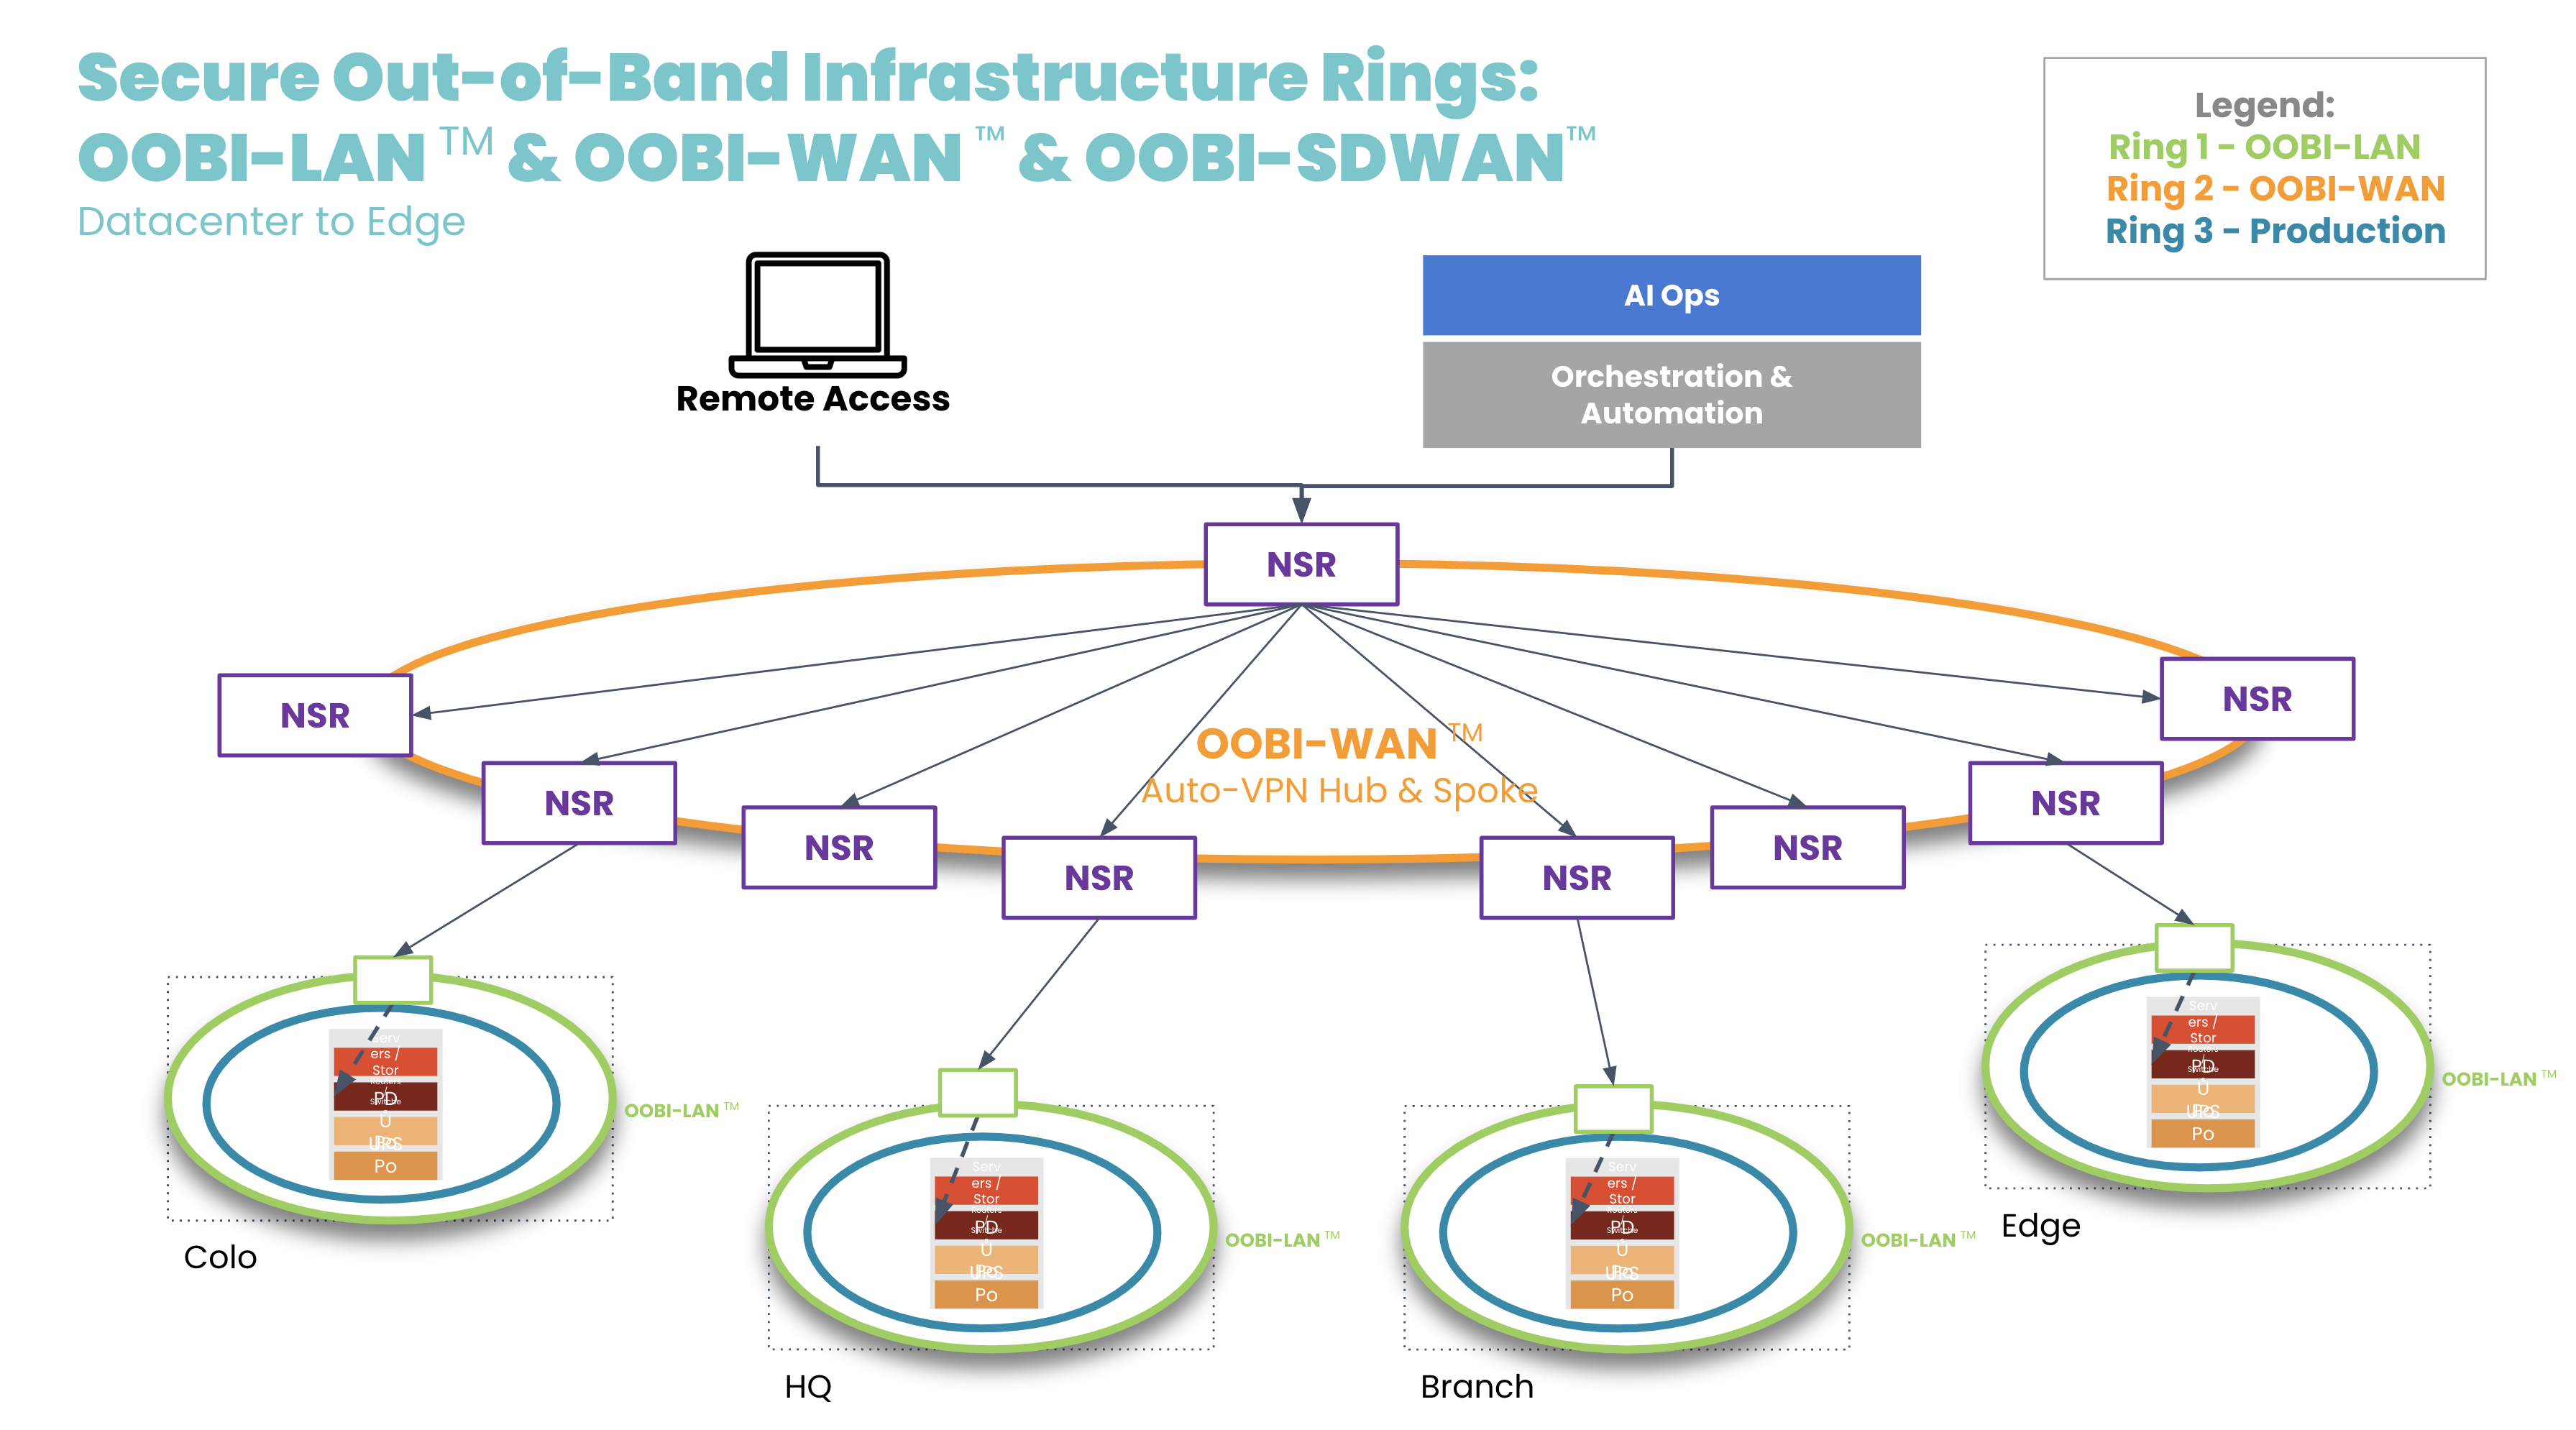
OOBI-WAN uses MPLS, IPsec, or SD-WAN links to create an overlay network dedicated specifically to management traffic. This gives network engineers private access to their infrastructure for management and troubleshooting, essentially creating a completely separate OOB network that does not rely on any part of the production network. OOBI-WAN lets network engineers use their WAN connection to remotely access their OOBI-LAN and fully rebuild their distributed networks, regardless of the state of their production infrastructure.  

A key part of OOBI-WAN is the inherent security that is built at all layers. To build secure OOBI-WAN, the best practice is to use OOBI-SDWAN™ which automates the building of VPN tunnels between all the nodes that need to be managed. OOBI-SDWAN provides the expected auto-VPN feature which means VPN encryption keys remain secure, as they don’t need to be copied/pasted/typed into multiple third-party devices. OOBI-SDWAN also ensures that an SLA is provided on the OOBI network along with observability dashboards of connectivity and the access state of the network. The combination of OOBI-SDWAN with a zero trust security framework is the best way to gain reliability in a way that reduces your risk.

OOBI-WAN hub and spoke

Tool 3. Fully independent automation infrastructure

Another tool that network engineers are becoming familiar with is automation. Network automation codifies repetitive tasks to reduce workloads for configuration management, compliance, and troubleshooting. During a slow economy, being able to scale an IT team’s efforts is especially valuable to business operations and end customers.

There is one major concern, however: having automation that runs loose and begins destroying the network, much like a bull in a China shop. Network engineers typically must learn new automation tools and programming languages, which requires trial and error. And because there is a lack of a best practice reference architecture, teams don’t know any better than to automate directly on the production network. This causes anxiety, as one mistake could bring down the network, cause catastrophic losses, and leave network engineers without an efficient way to recover.

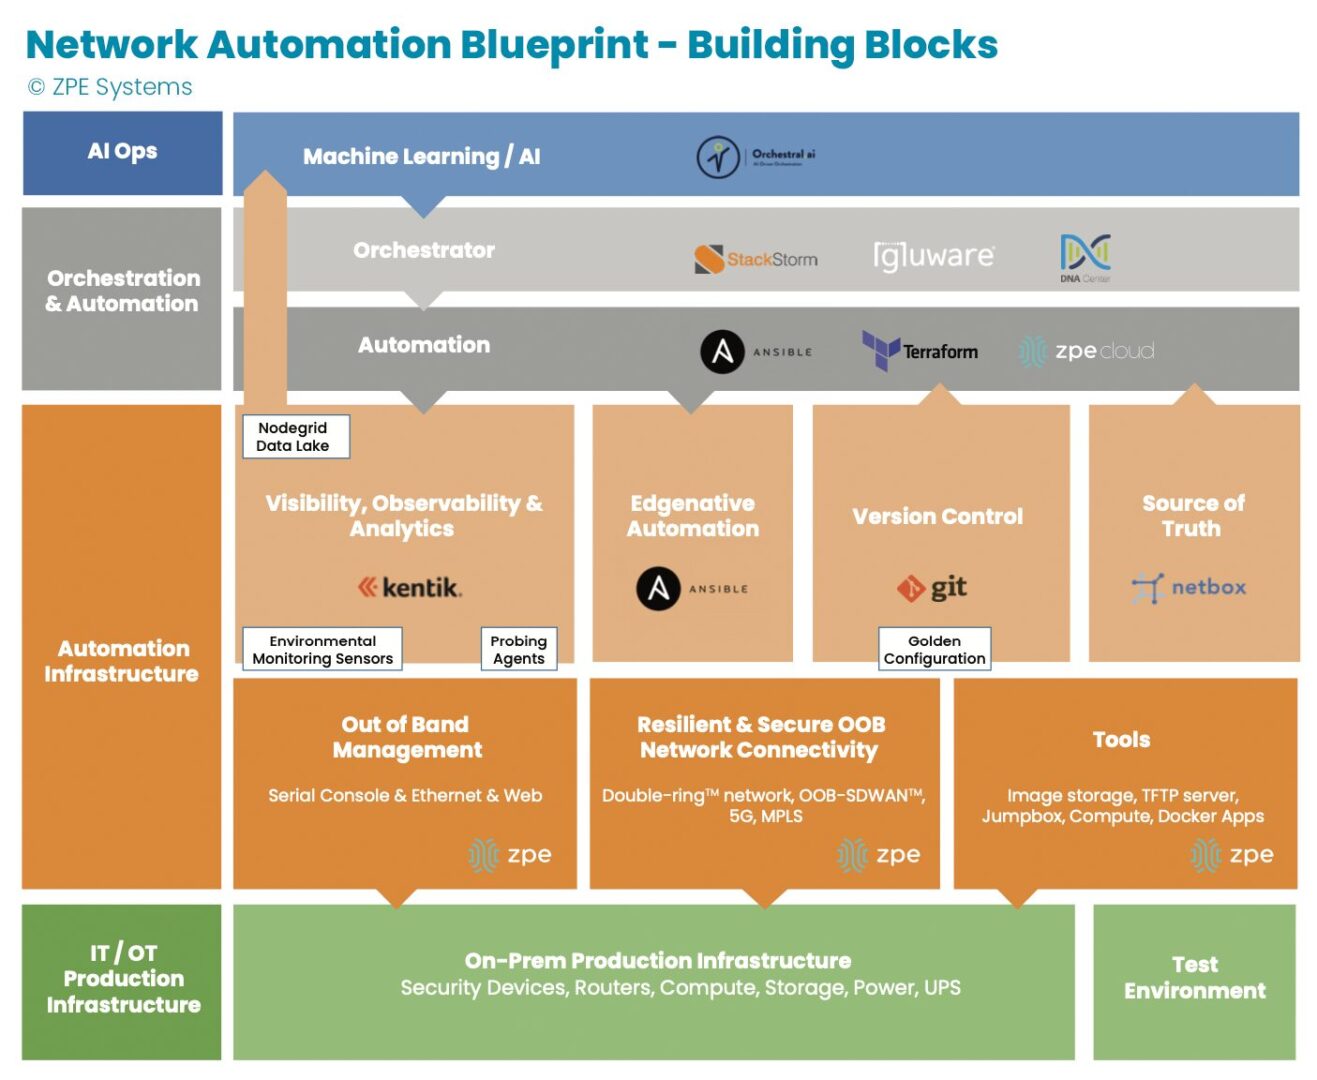
Image: The orange section describes dedicated automation infrastructure used for safely implementing automation.

In recent years, teams have been deploying automation on dedicated infrastructure like their OOB network. This automation infrastructure sits between the production infrastructure and the orchestration infrastructure, and serves as a safe way to build an automation pipeline. Open, Linux-based appliances like the Nodegrid Net SR combine a variety of functions and can host automation tools, like those for observability and analytics, version control, and source of truth. This independent automation infrastructure allows network engineers to ensure the integrity of configuration changes, software updates, and remediation protocols in an out-of-band manner, rather than testing directly on the production network. They can scale their capabilities, and in case of errors, roll back to a golden configuration that keeps services online.

Tool 4. Remote access to local jump box

Network engineers have another tool at their disposal: the jump box (a.k.a. jump server, jump host). A jump box hosts tools for maintaining operations, and these include file servers, image storage, configuration management tools, and troubleshooting commands. The jump box is a valuable asset for normal operations and for restoring services, such as when a device fails and needs its image rebuilt.

The issue with jump boxes is that they are typically a separate device that requires power, cooling, rack space, and maintenance. Some jump boxes also require on-site technicians to physically connect to the equipment needing repair.

Many organizations have adapted by upgrading their OOB infrastructure with appliances that can run full virtual machines (VMs). These can run all the tools mentioned above as well as with Docker containers, while consolidating power consumption, cooling resources, and rack space. The OOB appliance can double as a jump box. Combined with OOBI-LAN and OOBI-WAN, network engineers get remote access to re-image a device, diagnose DNS/routing issues, and perform any other necessary tasks. Key point is that discrete jump boxes – Like the Intel NUC — to be converted to virtual jump boxes running on a secure OOB platform like the Nodegrid Service routers.

Tool 5. Smart hands

A final way that network engineers get help through a slow economy is by outsourcing to so-called ‘smart hands.’ Employing smart hands means involving a third-party expert who can take on some of the IT workload. It’s a viable strategy, especially for teams feeling crushed by corporate belt tightening and the resulting mountain of tasks.

Companies who take this approach must be aware that the skills of smart hands varies greatly, as does the cost. This means it’s essential to strike a balance between which tasks to outsource, and which tasks to keep in house. For example, many organizations use smart hands for simple jobs such as replacing hardware and installing equipment at new sites. For more specialized jobs that require deeper knowledge of the environment, such as fixing a misconfigured IP address or route, teams use in-house personnel. This balance helps organizations get the support they need to keep operations running.

Get a cheat sheet to implement these tools fast

Some companies thrive during economic downturn, because they’ve intelligently placed these tools within their network architecture. Over the past decade, we’ve worked with these companies — including the largest tech giants — to describe in painstaking detail how they set up their infrastructure. We just released all 40+ pages of this validated reference architecture, complete with implementation diagrams and examples.

It’s called the network automation blueprint and it combines all of these tools. Network engineers can confidently answer questions like:

  • How do we meet SLAs with a smaller workforce?
  • How can we keep sites operating without physical access to equipment?
  • How can we perform weekly updates/patching without breaking things?

The blueprint is your cheat sheet to implementing a more resilient network, and fast. Click the button below to download your copy now.

Upgrade Network Infrastructure With Minimal Business Interruption

upgrade network infrastructure

Outdated network infrastructure poses a significant risk to the security and continuity of business operations. According to NTT’s “2020 Global Network Insights Report,” obsolete devices contain nearly twice as many security vulnerabilities as currently supported solutions. Outdated network hardware is also more likely to fail, and the ability to recover from a failure is severely hampered by a lack of vendor support. However, network upgrades can be highly disruptive, so many organizations delay network upgrades to avoid business interruption. They don’t realize that their outdated devices are like ticking time bombs that could bring down their network at any moment. In this post, we’ll provide advice that helps answer the question: How do I upgrade network infrastructure without disrupting business operations?

Why and when to upgrade network infrastructure

Obsolete network infrastructure no longer receives updates and security patches from the vendor. That means any vulnerabilities that exist on the device will remain open, giving cybercriminals time to find and exploit them. In addition, older network solutions often lack the advanced security features like SSO and MFA, which are required for Zero Trust.

Even supported legacy devices suffer from limitations that can prevent a business from achieving its technological goals. For instance, legacy devices may not support automation, making it difficult to achieve NetDevOps transformation. Plus, as enterprise networks grow more distributed, there’s a need for solutions that support SD-WAN and SD-Branch technology.

Sometimes the solutions themselves aren’t terribly outdated, it’s just that business requirements have changed in such a way that the existing infrastructure can’t support. For example, an organization may migrate some applications and systems to the cloud, so they need networking solutions that support hybrid environments. In addition, the mix of old and new devices and cloud and on-premises resources increases management complexity and prevents teams from effectively leveraging network orchestration.

Obsolete devices, outdated security, limited automation support, and changing business requirements are all important reasons to upgrade network infrastructure. However, these upgrades must be approached with a thoughtful strategy to reduce the impact on the performance and availability of business resources.

How to upgrade network infrastructure with minimal business interruption

Vendor agnostic platforms are the key to smooth network infrastructure upgrades. Vendor agnostic (a.k.a. vendor neutral) network management platforms support integrations with all or most viable and established network solutions, including legacy devices.

Vendor-neutral management devices, such as the Nodegrid Serial Console, support both legacy and modern Cisco pinouts. That means Nodegrid provides a single, unified platform from which to manage all the outdated devices you already have as well as any new solutions you add to your infrastructure. This reduces management complexity for network administrators, giving them more time to focus on optimizing performance and planning future network upgrades.

Additionally, a vendor-neutral network orchestration platform can use that management device to extend modern automation and orchestration to legacy hardware. A truly vendor-agnostic platform, such as Nodegrid Manager (for on-premises and private cloud deployments) or ZPE Cloud (for public cloud and hybrid deployments) can run third-party automation playbooks and custom Python scripts. This gives network administrators the unprecedented ability to implement a fully-automated NetOps environment even while still rolling out infrastructure upgrades.

The final piece of the puzzle is vendor-neutral Zero Touch Provisioning (ZTP). ZTP gives you the ability to deploy new devices efficiently and securely in remote data centers, branch offices, and edge compute sites. ZTP devices are provisioned automatically over the network, reducing the need for onsite deployments or pre-staging. A vendor-neutral ZTP solution like Nodegrid can extend ZTP to other vendors’ devices so you can quickly deploy upgraded infrastructure.

Nodegrid delivers vendor-neutral management, orchestration, and ZTP so you can upgrade network infrastructure with minimal business interruption.

Need Help Upgrading Your Network Infrastructure?

Contact ZPE Systems to learn how to upgrade your network infrastructure with Nodegrid.

Contact Us

3 Gaps That Will Leave IT Teams Scrambling This Winter

Winter is Looming – Wolf Howling

Today’s IT teams must maintain a growing infrastructure of on-prem and cloud solutions. These range from physical routers, out-of-band devices, and firewalls, to Zero Trust Security solutions, micro-segmentation tools, and network automation integrations. Despite an abundance of physical and virtual solutions meant to help keep digital services online, many organizations face an overwhelming number of tasks just to sustain everyday operations. 

With the rising risk of recession, organizations will be forced to cut back on resources including staff, training, and tools. This will only worsen the existing challenges teams face in their efforts to maintain their distributed infrastructure. 

In this blog, we’ll explore three gaps that will leave IT teams scrambling this winter, and show you several practical approaches to cope during recession. 

Gap 1: Lack of staff

IT teams have been historically understaffed, and most people can remember at least one significant tech worker hiring campaign from the past decade. Today’s CIOs may in fact be facing the biggest talent gap since 2008. For example, in the cybersecurity sector alone, the 2021 (ISC)2 Cybersecurity Workforce Study reported that despite adding 700,000 cybersecurity professionals to the workforce in 2021, there’s still a gap of more than 2.7 million workers globally, 377,000 of which are needed in the United States. 

Trained staff are a must for managing an organization’s distributed sites, especially as team silos disappear and workers are required to have a breadth of skills. Business leaders increasingly need people who are proficient in networking and programming, so they can maintain normal operations while progressing their digital transformation initiatives such as hyperautomation. It’s a challenge that often comes down to hiring new talent or increasing the skills of existing employees, and both of these approaches require plenty of time and money. 

This issue will only worsen with the coming recession as companies begin to tighten their belts and slash budgets. Major brands have already shed thousands of workers this year, leaving IT teams to make due with existing staff numbers or even reduced headcounts. In the simplest terms, the coming recession will leave companies much less willing or able to invest in staff. 

Gap 2: Lack of tools to reduce workloads

Today’s infrastructure incorporates solutions from many different vendors, but the problem is these often come with their own unique tools that are meant to serve only a specific function. Managing SD-WAN, SASE, ZTNA, orchestration, and out-of-band solutions means jumping between disparate tools, many of which lack integration with one another. This complexity leaves operational teams stuck in a reactionary break/fix posture trying to climb mountains of never-ending support tickets. 

To address this challenge, many Big Tech companies empower their IT teams through digital transformation initiatives, such as using automation to achieve a proactive approach. But this requires additional investments in upskilling staff and acquiring adequate automation infrastructure/tools. For many organizations, a lack of money and resources makes this difficult during normal economic conditions, and will only become exacerbated with the coming recession. IT teams will continue scrambling with their inflated workloads.

Gap 3: Lack of trust in automation

Automation can greatly reduce the risk of human error (and subsequent outages) by handling simple workloads, such as device provisioning and firmware updates. However, companies that do have the resources to implement automation also recognize its limitations. Automation solutions that aren’t optimized leave IT teams with mundane tasks like managing, scheduling, and restarting bots. But to even reach this level of automation requires training staff who typically don’t have a background in programming or development. 

These teams will be unfamiliar with NetOps/DevOps concepts. In order to develop essential automation practices, these employees will need to learn through trial and error. This is a problem because most organizations lack the proper automation infrastructure and tools that allow their IT teams to recover from mistakes. Operational teams in charge of keeping infrastructure running often fear automation for this exact reason — if they make one error, there’s the potential that it will bring down the network, lead to unhappy customers, and cost them their job. 


BlueprintPDF

Close these gaps with the Network Automation Blueprint

You can close these gaps for good using out-of-band, jump boxes, and tools you already have. After years of working directly with tech giants, we’ve created a best practice reference architecture any company can use to automate their network. This Network Automation Blueprint has been proven by global enterprises to increase capabilities and reduce workloads through trustworthy automation.