Providing Out-of-Band Connectivity to Mission-Critical IT Resources

What To Look for In a Cloud Edge Gateway Solution
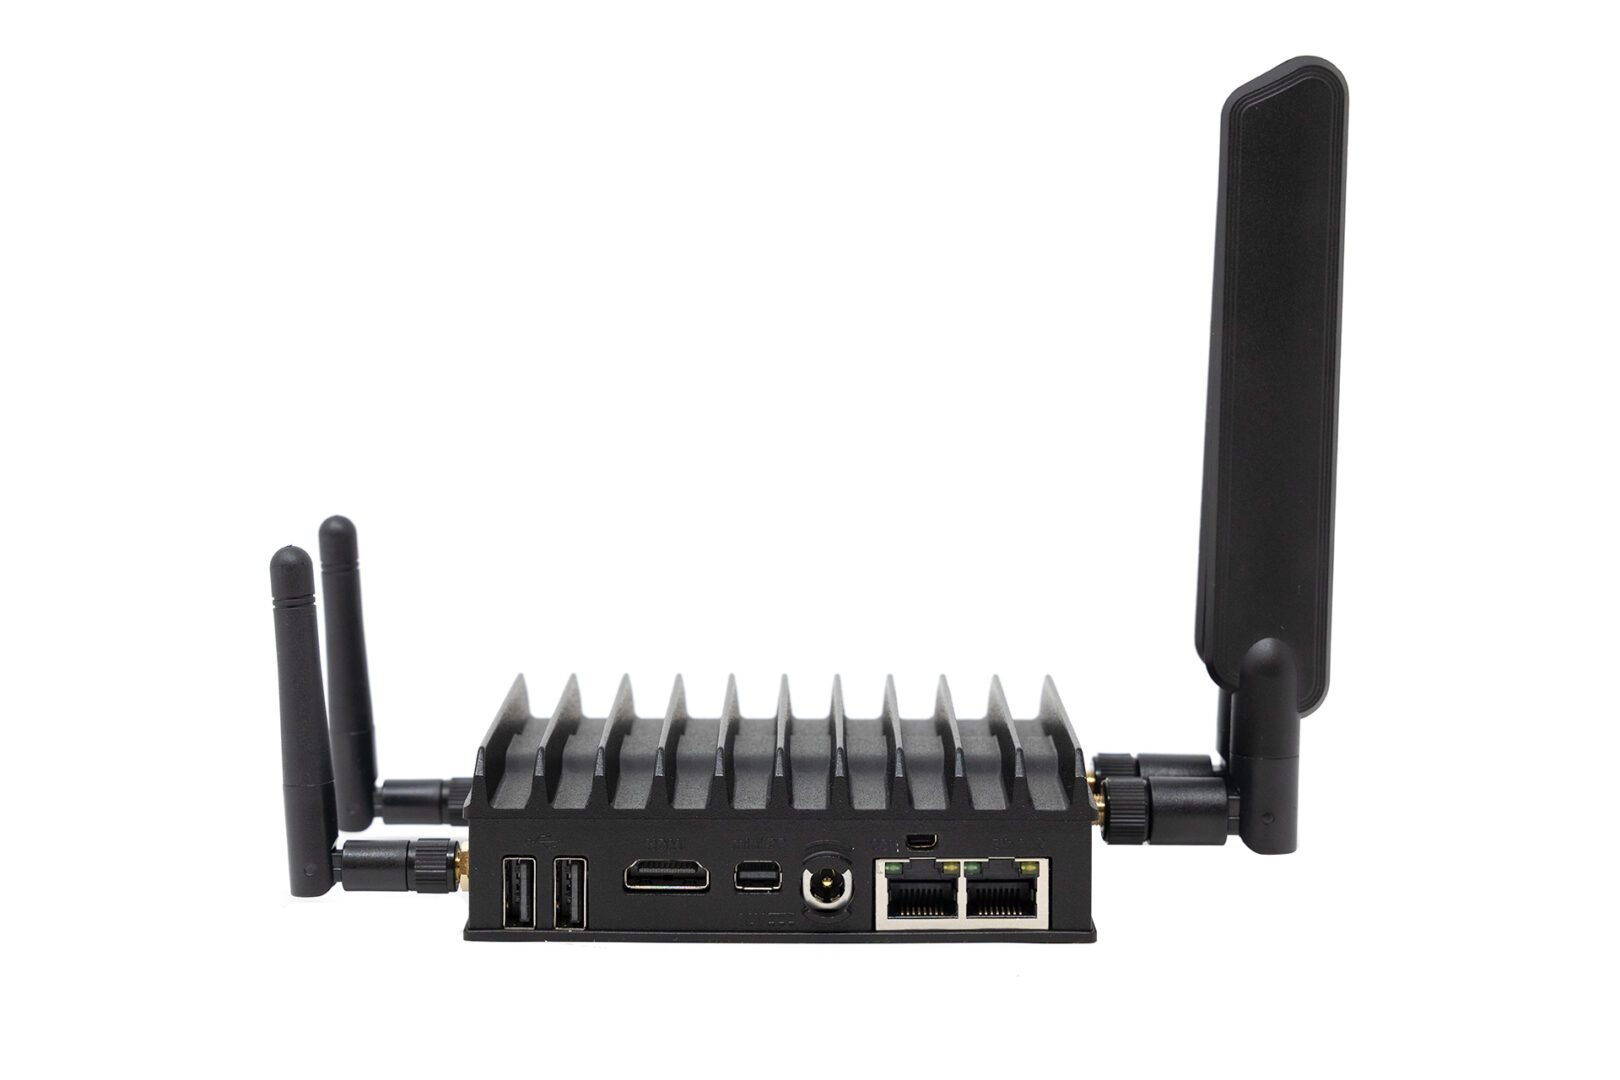
Mini-SR-Rear
Gartner predicts that by 2029 more than 15 billion IoT devices will connect to enterprise infrastructure. Many of these devices will operate outside of the centralized enterprise network, in satellite offices, manufacturing facilities, retail stores, and other remote locations. These remote – or edge – IoT devices need a secure and reliable way to connect to cloud resources and applications.

A cloud edge gateway is a hardware or software solution used to connect edge devices to the cloud. Some edge gateways are also routers that connect the edge location’s network to the WAN (wide area network) or SD-WAN (software-defined wide area network). In addition, many cloud edge gateway solutions also provide management access to connected devices, so administrators can remotely monitor and control edge infrastructure.

Some popular use cases for cloud edge gateways include:

  • Retail stores: Cloud edge gateways give retail stores a fast and secure connection for POS (point of sale) terminals, credit card readers, and security cameras.
  • Remote health facilities: Hospitals and clinics in remote areas use cloud edge gateways to securely and reliably transmit health data from IoT medical devices.
  • Police/emergency response vehicles: Cloud edge gateways enable secure data transmission from police, fire, and EMS vehicles to cloud applications.

In this blog post, we’ll discuss the key characteristics and components of a robust, secure, and reliable cloud edge gateway solution.

What to look for in a cloud edge gateway

Vendor neutrality

In a decentralized network with many remote locations, network solutions like edge gateways are often chosen based on which vendor offered the best deal or had the most compelling sales pitch at the time a new site was opening. This creates a heterogeneous network architecture, with each vendor offering their own platform from which to monitor and manage their solutions. With so many platforms to learn and keep track of, it becomes very challenging for admins to keep networks operating at peak efficiency.

A vendor-neutral cloud edge gateway solution reduces management complexity by seamlessly integrating with the existing edge infrastructure. For example, Nodegrid Services Routers can run other vendors’ software, so admins can keep using the management platform they’re most comfortable with. Or, admins can use the ZPE Cloud network orchestration platform to manage any other vendor solution that’s connected to a Nodegrid device.

Vendor-neutral cloud edge gateways give organizations the freedom to continue expanding to new locations without worrying about integration issues. Vendor neutrality also reduces headaches for network administrators so they can focus on improving efficiency and optimizing performance.

High-speed cellular failover and out-of-band management

Edge IoT devices are used for critical operations, which means they need 24/7 connectivity. Cellular failover provides a secondary internet connection that’s independent of wired network infrastructure. A cloud edge gateway with cellular failover ensures that IoT devices have uninterrupted access to the cloud even if the primary ISP connection goes down. The best solution supports high-speed 4G/5G cellular to reduce the performance impact of failover, as well as providing dual-SIM slots for redundancy.

In addition, admins need management access to edge infrastructure and IoT devices that are independent of both the WAN and the LAN (local area network), so if something like a firmware update causes the local network to go down, they can repair the issue without needing to dispatch an expensive truck roll. Out-of-band (OOB) management uses a secondary network interface (like a 5G cellular SIM) to create an OOB network that’s dedicated to management and troubleshooting. An edge gateway with OOB management ensures that admins have 24/7 high-speed access to remote infrastructure so they can recover from problems faster and reduce downtime.

Secure hardware and software

The security threats to enterprise networks are ceaseless and growing more sophisticated by the day. Many IoT devices and edge locations operate with little-to-no human intervention, which means breaches could go undetected for a long time. In addition, it can be difficult to stay on top of patch schedules or remotely install security updates on so many devices in so many locations, which can leave edge networks vulnerable to attack.

The right cloud edge gateway comes with robust hardware security features like BIOS protection, encrypted disks, and geofencing that prevent malicious actors from using a stolen gateway to hijack edge networks. Its management software should also include Zero Trust security features like SAML 2.0 integration, selectable cryptographic protocols and cipher suite levels, and two-factor authentication (2FA). With a vendor-neutral solution like Nodegrid, admins can even use the cloud edge gateway to push out security updates to connected devices using the ZPE Cloud management platform.

Automation support

It’s growing more difficult for people to simultaneously manage the complex network infrastructures required for modern business operations while ensuring peak performance and 24/7 availability. Network automation solutions help decrease the burden on overworked admins and can improve the performance and reliability of edge networks.

Many edge gateways include some automation features as part of their management software. However, these tend to be limited to baked-in workflows, meaning admins may not be able to use custom scripts or third-party playbooks. The best cloud edge gateway has vendor-neutral automation support so admins can use their choice of automation solutions. For example, Nodegrid edge gateways can directly host automation playbooks from all the major platforms including Ansible and Puppet. Nodegrid also supports custom scripting and third-party integrations for even greater flexibility.

The best cloud edge gateway solution is vendor-neutral, uses high-speed cellular for failover and OOB management, follows Zero Trust best practices to keep the infrastructure secure, and supports all of the major automation tools and scripting languages. With the edge gateway market still being somewhat new, there’s really only one solution that checks all these boxes: the Nodegrid family of cloud edge gateway routers.

Why choose the Nodegrid cloud edge gateway solution?

There are six Nodegrid Services Router models to choose from based on your deployment size, networking requirements, and use case. For example, the Mini SR delivers versatile edge networking capabilities in a device approximately the size of an iPhone, which is perfect for mobile emergency response units or retail branches where space is at a premium.

For larger deployments, such as an edge compute data center or Smart Building system, the Net SR provides a modular solution with options for additional serial console ports, disk space, compute, PoE, and more.

Nodegrid’s vendor-neutral platform is extensible and capable of directly hosting other vendor solutions for automation, security, and other networking functions. Cellular failover and high-speed OOB are delivered via dual- or quad-SIM cellular slots with 5G/4G LTE support. Nodegrid devices are protected by secure hardware features, SAML 2.0 and 2FA support, and advanced authentication, plus the OS is kept up-to-date with frequent patches. Nodegrid is also the only cloud edge gateway with full support for all the top automation and IaC (infrastructure as code) solutions, including Ansible, Chef, and Puppet.

Ready to learn more about the Nodegrid cloud edge gateway solution?

Contact ZPE Systems today to learn more about the Nodegrid cloud edge gateway solution.
Contact Us

Uplogix 5000 Local Manager EOL Best Replacement Options

A businessman considers two different options, such as which model to replace the Uplogix 5000 Local Manager EOL with
The Uplogix 5000 Local Manager line of serial console servers will go end-of-life (EOL) on December 31, 2025, with software support ending on December 31, 2023. Uplogix recommends the LM83X as a replacement model, but there are some concerns and limitations to be aware of before you make this switch. In this blog, we’ll compare the new LM83X to the Uplogix 5000 Local Manager and discuss an alternative replacement option.

About the Uplogix 5000 Local Manager

The 5000 Local Manager is Uplogix’s flagship serial console, providing out-of-band (OOB) management for up to 38 devices. Management access is delivered via two 10/100/1000 Mbps Base-T Ethernet interfaces, with a slot available for an optional v.92 modem, cellular SIM, RS-232 card, or fiber module.

All Uplogix serial console servers use the Local Manager software platform for monitoring and management. This software includes automation capabilities for routine management, maintenance, and recovery tasks. However, the Local Manager platform does not support the use of third-party automation tools or custom scripts. In addition, while the 5000 Local Manager hardware can access and manage devices from other vendors, the management software is not easily extensible by the customer. That means users are locked into the vendor’s feature roadmap and automation capabilities.

Uplogix 5000 Local Manager tech specs:

System
CPU Intel 1.3 GHz Atom
RAM 1 GB
Storage 40 GB 2.5″ SSD
Local interfaces – Up to 38 x RS-232 Serial ports

– Up to 8 x dedicated 10/100/1000 Mbps Ethernet ports

– 1 x RS-232 Power management port

– 1 x RJ-11 Modem port

– 2 x USB ports

Management interfaces – 2 x 10/100/1000 Mbps Base Ethernet interfaces

– 1 x RS-232 Console port

Option slots 1 available for field installable internal modems (v.92, cellular, or RS232) or a fiber module
Expansion slots 2 available for:

– 8 Port Serial card

– 16 Port Serial card

– 8 Port Ethernet card (10/100/1000 Mbps)

Power Dual AC or Dual DC
Features
Vendor-neutral Heterogeneous device access and management
Security – Secure Shell (SSHv2)

– TACACS and Radius authentication

– IP and caller ID filtering

– FIPS 140-2 Level 2

– Automatic session management to prevent unauthorized access

– Enforces RBAC, command-level authorization

– Logging of user access, device changes, and session activity

OOB/Failover – POTS lines

– Cellular modems

– Fiber

– DSL

– Satellite

Device monitoring In-band or out-of-band data collection every 5 to 30 seconds
Environmental monitoring – Temperature

– Humidity

Remote access – SSHv2

– Secure access to web-only management interfaces

Automation Rule-based engine for automation of routine management tasks

– No third-party automation

– cannot be easily expanded by customer

Remote power management Monitors and controls power, can remotely restart a managed device

Uplogix ended the sale of the 5000 Local Manager at the end of 2020, with the EOL date set at 12/31/2022. The EOL Uplogix 5000 product SKUs are listed below.

Uplogix 5000 EOL replacement option: The Uplogix LM83X

Uplogix released a new Local Manager serial console to replace the 5000: the LM83X. This model can manage up to 104 devices through the use of three expansion bays for additional serial and Ethernet ports. In addition to two 10/100/1000 Base-T Ethernet interfaces, the new Local Manager has a 1-Gbps SFP port for faster management access.

The LM83X runs on the same Local Manager software platform as its predecessor, which means it also suffers from vendor lock-in and limited automation capabilities. In addition, the Uplogix platform has some advanced security features like FIPS 140-2 Level 2 certification and support for Radius authentication, but it doesn’t support SAML 2.0 for cross-domain single sign-on. That makes it difficult to extend Zero Trust Security best practices to the out-of-band management network, which can leave the entire enterprise vulnerable to an attack.

Another crucial consideration is that Uplogix was just bought by Lantronix, one of its biggest competitors. It’s still unknown how Uplogix will be integrated, leaving existing customers uncertain about the future of their hardware and software support contracts.

Uplogix 5000 Local Manager vs. LM83X tech specs:

Uplogix 5000 Uplogix LM83X
System
CPU Intel 1.3 GHz Atom Not listed
RAM 1 GB Not listed
Storage 40 GB 2.5″ SSD 256 GB NVMe
Local interfaces – Up to 38 x RS-232 Serial ports

– Up to 8 x dedicated 10/100/1000 Mbps Ethernet ports

– 1 x RS-232 Power management port

– 1 x RJ-11 Modem port

– 2 x USB ports

– Up to 104 x RS-232 Serial ports

– 1 x USB-A port

– 1 x USB-C port

Management interfaces – 2 x 10/100/1000 Mbps BaseT Ethernet interfaces

– 1 x RS-232 Console port

– 2 x 10/100/1000 BaseT Ethernet ports

– 1 x 1-Gbps SFP port

Option slots 1 available for field installable internal modems (v.92, cellular, or RS232) or a fiber module 1 available for field installable internal modems (v.92, cellular, or RS232) or a fiber module
Expansion slots 2 available for:

– 8 Port Serial card

– 16 Port Serial card

– 8 Port Ethernet card (10/100/1000 Mbps)

3 available for:

– 8 Port, 16 Port, or 32 Port Serial cards

– 8 Port Ethernet card (10/100/1000 Mbps)

– LCD keypad

Power Dual AC or Dual DC Redundant internal universal power
Features
Vendor-neutral Heterogeneous device access and management Heterogeneous device access and management
Security – Secure Shell (SSHv2)

– TACACS and Radius authentication

– IP and caller ID filtering

– FIPS 140-2 Level 2

– Automatic session management to prevent unauthorized access

– Enforces RBAC, command-level authorization

– Logging of user access, device changes, and session activity

– Secure Shell (SSHv2)

– TACACS and Radius authentication

– IP and caller ID filtering

– FIPS 140-2 Level 2

– Automatic session management to prevent unauthorized access

– Enforces RBAC, command-level authorization

– Logging of user access, device changes, and session activity

OOB/Failover – POTS lines

– Cellular modems

– Fiber

– DSL

– Satellite

– POTS lines

– Cellular modems

– Fiber

– DSL

– Satellite

Device monitoring In-band or out-of-band data collection every 5 to 30 seconds In-band or out-of-band data collection every 5 to 30 seconds
Environmental monitoring – Temperature

– Humidity

– Temperature

– Humidity

Remote access – SSHv2

– Secure access to web-only management interfaces

– SSHv2

– Secure access to web-only management interfaces

Automation Rule-based engine for automation of routine management tasks

– No third-party automation

– Not easily expandable

Rule-based engine for automation of routine management tasks

– No third-party automation

– Not easily expandable

Remote power management Monitors and controls power, can remotely restart a managed device Monitors and controls power, can remotely restart a managed device

Alternative Uplogix 5000 EOL replacement options from ZPE Systems

The Uplogix Local Manager solutions are what’s known as second generation, or Gen 2, out-of-band serial consoles. That means they provide heterogeneous device management, built-in security features, and some automation capabilities. However, they fall short of true vendor neutrality, which makes it impossible to achieve end-to-end network automation. In addition, without SAML 2.0 support, Uplogix devices are vulnerable to compromise by malicious actors who could use them to gain control over the production network.

To get secure and extensible OOB management access with end-to-end automation capabilities, you need a Gen 3 out-of-band serial console solution like the Nodegrid platform from ZPE Systems.

About the Nodegrid Serial Console Plus (NSCP)

The Nodegrid Serial Console Plus (NSCP) provides Gen 3 OOB management for up to 96 devices, including support for Cisco and legacy pinouts. Management access is delivered via two Gigabit Ethernet ports, two SFP+ ports, or v.92 modem, with out-of-band and network failover to dual SIM 5G/4G LTE cellular, WiFi, or v.92 modem.

All Nodegrid devices can be managed with one of two offerings: the on-premises Nodegrid Manager software or the ZPE Cloud application. Both solutions are easily extensible with your choice of third-party applications for infrastructure automation and orchestration, security, big data analytics, and more. Nodegrid hardware can even directly host other vendors’ software, giving you a convenient platform for Docker containers, Infrastructure as Code (IaC) playbooks, Security Service Edge (SSE) applications, and SD-WAN solutions.

The Gen 3 NSCP protects your infrastructure using Zero Trust best practices like SAML 2.0 support, disk encryption, and secure boot. ZPE Systems is also the only serial console vendor with a FIPS 140-3 pre-certification, making them the most secure OOB solution on the market.

Head-to-head: Uplogix 5000 vs. Uplogix LM83X vs. NSCP tech specs

Uplogix 5000 Uplogix LM83X Nodegrid Serial Console Plus (NSCP)
System
CPU Intel 1.3 GHz Atom Not listed Intel x 86, 64 bit
RAM 1 GB Not listed 4 GB / 8 GB
Storage 40 GB 2.5″ SSD 256 GB NVMe 32 GB FLASH
Local interfaces – Up to 38 x RS-232 Serial ports

– Up to 8 x dedicated 10/100/1000 Mbps Ethernet ports

– 1 x RS-232 Power management port

– 1 x RJ-11 Modem port

– 2 x USB ports

– Up to 104 x RS-232 Serial ports

– 1 x USB-A port

– 1 x USB-C port

– Up to 96 x RS-232 Serial ports

– 2 x 1-GbE Ethernet

– 2 x SFP+

– 2 x USB 3.0 ports

– 1 x HDMI port

– 1 x Console port

– can manage devices RS-232, USB, IPMI, SSH,Telenet, WebUI, RESTAPI

– can manage over 500 devices (mix of serial and IP) on a single appliance

Management interfaces – 2 x 10/100/1000 Mbps BaseT Ethernet interfaces

– 1 x RS-232 Console port

– 2 x 10/100/1000 BaseT Ethernet ports

– 1 x 1-Gbps SFP port

– 2 x 1-GbE Ethernet

– 2 x SFP+

– 1 x v.92 Modem

Option slots 1 available for field installable internal modems (v.92, cellular, or RS232) or a fiber module 1 available for field installable internal modems (v.92, cellular, or RS232) or a fiber module – Wi-Fi

– Dual SIM 5G/4G LTE cellular

– v.92 modem

Expansion slots 2 available for:

– 8 Port Serial card

– 16 Port Serial card

– 8 Port Ethernet card (10/100/1000 Mbps)

3 available for:

– 8 Port, 16 Port, or 32 Port Serial cards

– 8 Port Ethernet card (10/100/1000 Mbps)

– LCD keypad

Power Dual AC or Dual DC Redundant internal universal power Single or Dual AC, Dual DC
Features
Vendor-neutral Heterogeneous device access and management Heterogeneous device access and management – Vendor-neutral device access and management

– Can directly host third-party apps for security, automation, etc.

– Platform integrates with third-party solutions not hosted on Nodegrid hardware

– Can extend Zero Touch Provisioning to other vendor devices

Security – Secure Shell (SSHv2)

– TACACS and Radius authentication

– IP and caller ID filtering

– FIPS 140-2 Level 2

– Automatic session management to prevent unauthorized access

– Enforces RBAC, command-level authorization

– Logging of user access, device changes, and session activity

– Secure Shell (SSHv2)

– TACACS and Radius authentication

– IP and caller ID filtering

– FIPS 140-2 Level 2

– Automatic session management to prevent unauthorized access

– Enforces RBAC, command-level authorization

– Logging of user access, device changes, and session activity

Hardware Security:

– TPM 2.0

– Encrypted solid-state disk

– UEFI BIOS with protection

– Secure boot (signed OS)

– Geofencing

Authentication:

– Local

– RADIUS

– TACACS+

– LDAP/AD

– NIS and Kerberos

– SAML 2.0 (Okta, Duo, PingID, ADFS)

OOB/Failover – POTS lines

– Cellular modems

– Fiber

– DSL

– Satellite

– POTS lines

– Cellular modems

– Fiber

– DSL

– Satellite

– 5G/4G/LTE

– V.92 modem

– Wi-Fi

Device monitoring In-band or out-of-band data collection every 5 to 30 seconds In-band or out-of-band data collection every 5 to 30 seconds – Keystroke logging

– Logging to ZPE Cloud, NFS, Local

– Alert on cable disconnects

Environmental monitoring – Temperature

– Humidity

– Temperature

– Humidity

– Particulate

– Smoke

– Airflow & temperature

– Proximity/door lock

– Temp & humidity

– 7-port USB hub

– 8-port GPIO

– 4-port Relay

Remote access – SSHv2

– Secure access to web-only management interfaces

– SSHv2

– Secure access to web-only management interfaces

– SSH direct to consoles

– ZPE Cloud (web) or Nodegrid Manager (local)

Automation Rule-based engine for automation of routine management tasks

– No third-party automation

– cannot be easily expanded by customer

Rule-based engine for automation of routine management tasks

– No third-party automation

– cannot be easily expanded by customer

– ZPE Cloud

– Chef

– Docker

– KVM Hypervisor

– Puppet

– Python

– RedHat Ansible

– Ruby

– ShellScript

– Node.js JavaScript

Remote power management Monitors and controls power, can remotely restart a managed device Monitors and controls power, can remotely restart a managed device – Support major power strip manufacturers

– Power management integrated with serial session (escape sequence in the serial session or power buttons in web serial session)

– Power control of VMs

– Access rights for users and user groups

The Uplogix LM83X is the direct replacement for the EOL Uplogix 5000 Local Manager, which means it provides the same base capabilities with some upgraded hardware features. However, this also means the LM83X suffers from the same limitations as its predecessor, namely a lack of SAML 2.0 integration and a closed management platform that doesn’t support third-party automation. To achieve end-to-end network automation, you need a Gen 3 OOB serial console solution like the Nodegrid Serial Console Plus.

Uplogix 5000 Local Manager EOL product SKUs

Product SKU Description End of Hardware Support End of Software Support End of Life End of Sale
71-1321-10 FIPS Uplogix 5000 Local manager, 14 Serial, V.92 modem 12/31/2023 12/31/2025 12/31/2025 12/31/2020
61-5001-01 Uplogix 5000 8 Port Serial Expansion Module w/LMS-FIPS 12/31/2023 12/31/2025 12/31/2025 12/31/2020
61-5500-30 Uplogix 5000 Local Manager 12/31/2023 12/31/2025 12/31/2025 12/31/2020
61-5500-33 FIPS Uplogix 5000 Local Manager 12/31/2023 12/31/2025 12/31/2025 12/31/2020

Ready to replace your Uplogix 5000​?

To replace your Uplogix 5000 Local Manager EOL serial console server with the Gen 3 Nodegrid Serial Console Plus, Contact ZPE Systems today!

Request a Demo Today

Implementing a Network Modernization Strategy for Large-Scale Organizations

Two engineers plan a network modernization strategy from a platform overlooking racks of data center infrastructurea
The COVID-19 pandemic forced many large-scale organizations to decentralize their business operations to enable remote work, which shined a spotlight on how outdated their enterprise networks are. As other world events like wars, a recession, and virus resurgences continue to impact business, organizations must modernize their network infrastructure if they want to survive. However, their survival is also contingent on their ability to meet SLAs and maintain 24/7 availability, so it’s crucial to minimize the disruption caused by infrastructure upgrades. This blog provides advice to large-scale organizations on how to implement a network modernization strategy that minimizes disruptions while leaving room for future growth and innovation.

The importance of network modernization

Network infrastructure updates are expensive and can be disruptive, leaving many large companies wondering if the payoff is worth the risks. However, when COVID-19 struck, these organizations were left scrambling to replace their outdated and insecure VPN solutions with more robust remote connectivity technology. Similarly, in the current recession, enterprises that put off network modernization in the past are now finding themselves without the remote management and orchestration capabilities they need to keep their infrastructure running optimally with reduced staff. Even without the looming threat of major world disruptions, outdated network infrastructure poses a risk to large-scale organizations. Obsolete devices are no longer patched by the vendor, which means any vulnerabilities that exist will remain open for hackers to exploit. Older equipment is also more likely to break, and may not be supported by the provider, making it more difficult and expensive to recover from a failure. Plus, outdated infrastructure hampers an enterprise’s ability to innovate with new technologies to stay competitive in the market. Upgrading network infrastructure is expensive, time-consuming, and requires careful planning to prevent business interruption. However, investing in network modernization now will save you from more costly disruptions in the future.

A network modernization strategy for large-scale organizations

Enterprises need to carefully plan their path to network modernization to ensure they can meet their customer SLAs by avoiding outages and performance degradation. Here are some tips for implementing a network modernization strategy that minimizes disruption while leaving room for future growth.

Bridge the gap with a vendor-agnostic platform

To ensure a smooth upgrade process, organizations will gradually upgrade their infrastructure by replacing individual solutions one at a time. There’s typically an extended window of time in which there are both legacy and modern devices that need to be monitored, managed, and supported. This creates additional complexity for administrators who need to learn how to use the new solutions, integrate them with the existing infrastructure, and ensure there’s little-to-no impact on end users. It’s especially challenging when they need to use different management platforms to access and control each solution. That’s why it’s important to implement a vendor-agnostic network management platform that supports legacy and multi-vendor solutions. A vendor-agnostic platform gives administrators a single pane of glass from which to control the entire heterogeneous network architecture, simplifying day-to-day management and allowing them to focus on optimizing performance and implementing future upgrades. Plus, a unified platform makes it possible to extend new technological capabilities (like remote OOB management and automation) to older infrastructure, accelerating network modernization efforts.

Reduce downtime with remote out-of-band management

Any experienced admin knows that installations and updates are risky procedures. Even with the best-laid plan, errors can occur that prevent new systems from coming online, cause integration issues with existing infrastructure, or even take down dependent network services. The risk is even greater when the upgrades occur remotely without any technicians on-site to power cycle devices or reconfigure systems offline. What if there’s an outage or severe disruption, but COVID lockdowns or natural disasters prevent staff from entering these locations? Remote out-of-band (OOB) management creates an alternative path that admins use to access remote infrastructure. It creates an out-of-band network that’s dedicated to infrastructure management and orchestration and that doesn’t rely on the availability of the production network. That means administrators can access and troubleshoot offline devices remotely, reducing the duration and impact of downtime. Remote OOB management makes it safer for large-scale organizations to implement a network modernization strategy and ensures the continued stability and availability of enterprise infrastructure.

Streamline deployments with automation

Even when new infrastructure deployments run smoothly, they take considerable time and effort on the part of network administrators. Large, global organizations have complex and highly distributed network architectures with thousands of moving parts that need to be upgraded or replaced. Just configuring and installing all of these new solutions can add significant delays to the network modernization process. Plus, configuring so many devices is tedious and prone to human error, causing more delays as admins troubleshoot and fix deployment failures. For example, a typo in an IP address on one device could prevent dependent services from deploying correctly, forcing teams to retrace their steps and waste time identifying the error. Automation is the key to streamlining device deployments and reducing configuration errors. For example, Zero Touch Provisioning (ZTP) allows admins to provision new devices automatically over the network using definition files. These files can be reused as many times as needed to deploy many identical solutions across the enterprise network, significantly reducing the time and effort required to modernize infrastructure. Plus, configuration files can be tested pre-deployment to ensure there are no errors or security vulnerabilities. Vendor-agnostic network management platforms, OOB management, and automation are crucial components of a smooth network modernization strategy. Implementing this strategy is easier if you choose a management solution that integrates all these capabilities into a single, unified platform.

Make Nodegrid a part of your network modernization strategy

The Nodegrid platform from ZPE Systems delivers vendor-agnostic control, Gen 3 OOB management, and end-to-end network automation capabilities in a single box. Nodegrid has helped large-scale organizations like the Internet Association of Australia update their network infrastructure without disrupting business. Nodegrid serial consoles support both legacy and modern Cisco pinouts, allowing them to dig their hooks into any device in your network infrastructure. That means you can use the ZPE Cloud solution to extend automation and orchestration to your entire heterogeneous architecture, supercharging your network modernization efforts. Nodegrid uses high-speed OOB interfaces (e.g., 5G/4G cellular) to provide admins with a fast and reliable connection for remote upgrades, management, and orchestration. Nodegrid allows you to power cycle devices, enter BIOS menus, manage power load distribution, and more from anywhere in the world with an internet connection. This makes it easier and safer for large-scale organizations to remotely upgrade their network infrastructure and ensures continuous management availability to prevent downtime in the future. The vendor-agnostic Nodegrid platform also allows you to extend automation features like ZTP to both legacy and modern solutions in your network infrastructure. Nodegrid supports integrations with your choice of third-party automation tools, or you can use Nodegrid hardware to directly host custom scripts and automation apps. This both streamlines the network modernization process and gives you the ability to grow and evolve your network with emerging automation technologies like AIOps. Nodegrid streamlines network modernization strategies by providing vendor-agnostic management, remote OOB management, and end-to-end automation support in a single platform. 

Want to learn more about Nodegrid’s role in enterprise?

To learn more about Nodegrid’s role in an enterprise network modernization strategy, contact ZPE Systems today. Contact Us

Using AIOps and Machine Learning To Manage Automated Network Infrastructure

shutterstock_1825096265(1)

Automation is the key to maintaining optimal network performance and availability during tumultuous times. A resilient, automated network keeps functioning even if administrators can’t physically access the infrastructure or when a recession forces companies to reduce their IT workforce. A network automation framework includes all the tools, technologies, and practices required to build a resilient and fully automated enterprise network infrastructure.

The four building blocks of a resilient network automation framework include:

  1. IT/OT production infrastructure
  2. Automation infrastructure
  3. Orchestration infrastructure
  4. AIOps

In previous blogs, we focused on the building blocks that enable network automation and orchestration. In this blog, we’ll discuss how AIOps and machine learning help teams manage their automation and orchestration—and the massive amounts of data produced by their automated systems—more efficiently.

What is AIOps?

AIOps—artificial intelligence for IT operations—was originally introduced by Gartner in 2017. It uses AI technologies like machine learning (ML) and natural language processing (NLP) to analyze IT operations data. This data is pulled in from many different sources, including monitoring and visibility platforms, environmental monitoring sensors, event logs, and firewalls. AIOps utilizes that data to automate tasks like event correlation, anomaly detection, and root cause analysis (RCA) as well as to predict future outcomes and provide valuable business insights.

What’s the difference between AI and machine learning?

Before we delve any deeper into the specific uses for and benefits of AIOps, it’s important to clarify what we mean when we talk about technologies like AI and machine learning.

AI stands for artificial intelligence, which is defined as a computer’s ability to display human-like intelligence through behaviors like learning from new data, drawing conclusions based on that data, and coming up with solutions to problems.

Machine learning, on the other hand, describes a computer’s ability to process large quantities of data and learn from it. Learning is a major requirement for AI, which means that all machine learning applications could be considered AI. However, not all AI is machine learning—artificial intelligence uses additional technology to make decisions, solve problems, and perform other automated functions.

Essentially, AI describes a broad range of technologies, whereas machine learning is a more specific subset of technologies included in the AI umbrella. In the context of AIOps, however, machine learning is often the only artificial intelligence technology in use.

Using AIOps and machine learning to manage automated network infrastructure

In an automated enterprise network, AIOps and machine learning use advanced algorithms to provide in-depth analysis of all the data collected from production infrastructure, automation components, and orchestration systems. AIOps solutions can even take things a step further by making decisions and solving problems based on the results of that data analysis.

Some examples of how AIOps and machine learning can be used to manage automated network infrastructure include:

Security

Cyberattacks and data breaches are major threats to the reliability and performance of network infrastructure. In addition to the financial losses caused by sensitive data exfiltration and reputation loss, security breaches are also a leading cause of downtime, which directly impacts business revenue. According to the ITIC’s 2022 Global Server Hardware Security survey, 76% of enterprises cited security breaches as the top cause of downtime. That means network security is paramount to the resilience of an automated infrastructure.

For many years, network security relied on signature-based detection for jobs like intrusion prevention, antivirus, and spam filtering. Signature-based detection involves comparing an incoming request to a database of known threats to see if it matches—if not, it’s assumed to be safe and allowed into the network. This approach only works if the database is kept up to date and if all incoming threats have been identified in the past. Signature-based detection often fails to catch zero-day exploits or novel malware that it hasn’t seen before, plus it tends to generate a lot of false positives.

AIOps security solutions overcome this problem by learning from past experiences. Machine learning is able to extract information from past threats and then develop algorithms to recognize, predict, and categorize a new threat that it’s never seen before. This makes AIOps adept at preventing new threats as well as detecting ones already on the network.

You can also use AIOps to analyze data from infrastructure logs and other security solutions to spot the more subtle signs of a breach that’s already happened or that’s currently taking place. For example, AIOps and machine learning may detect an unusually large amount of data leaving the network, which could indicate that a malicious actor is exfiltrating sensitive information. Another security use for AI is called User and Entity Behavior Analytics (UEBA), which inspects account activity on a network and reports anomalous behavior that could indicate an account has been compromised.

AIOps improves upon automated network security solutions by using adaptive learning and predictive analysis to detect new and unusual threats with a greater degree of accuracy. It also takes advantage of the massive amounts of data produced by security appliances and network infrastructure to identify the subtle clues left behind by sophisticated cybercriminals. This makes AIOps a valuable tool for maintaining the security and availability of an automated network infrastructure.

Monitoring

An automated network infrastructure generates a massive quantity of logs that can be used to assess health and performance as well as to identify potential issues before they cause any outages or downtime. However, humans aren’t very good at sifting through large amounts of data to figure out what’s relevant and what isn’t.

Many monitoring solutions use basic automation to help weed out important data, for example by letting admins set performance thresholds that generate automatic alerts when devices fall out of the optimal operating range. However, this kind of automation creates a lot of false positives, which are tedious to sort through and could lead to admin neglect or complacency. It can also only detect specific symptoms and issues that fall within the scope of the monitoring thresholds programmed by a sysadmin, which means it can’t adapt to changing circumstances or predict new problems that weren’t anticipated by the admin in advance.

An AIOps monitoring solution collects all the logs produced by automated infrastructure and analyzes them in real time. Sysadmins can still set performance thresholds and program automatic alerts, but AIOps also uses machine learning to “think outside the box” by recognizing patterns and detecting anomalies it wasn’t programmed to look for. That means issues are identified faster, potentially before they cause any noticeable problems for end-users.

Machine learning also gives AIOps monitoring solutions the ability to track performance over time and predict future outcomes based on historical data. For example, organizations can use AIOps analysis to plan infrastructure upgrade schedules based on when device performance is predicted to start degrading, or in advance of a predicted spike in demand for a particular location. This gives CIOs and IT managers the ability to make smarter decisions about where and when to invest money and how to prioritize new initiatives.

AIOps monitoring solutions work well with data lakes, which are large repositories for unstructured data. Data lakes are an efficient way to process large quantities of data, such as monitoring and security logs. This enables the data to be used by AIOps and other big data tools.

AIOps transforms the flood of logs generated by complex, automated network infrastructures into actionable data. Enterprises can use AIOps and machine learning to catch subtle issues before they turn into major problems, improving the performance and availability of network resources. AIOps also provides valuable business intelligence that organizations can use to make smarter and more cost-effective decisions during recessions and other tumultuous events.

Root cause analysis (RCA)

When there’s an outage or other business interruption, the main priority is fixing whatever is preventing systems from operating normally so that systems can get back online. Often, this means fixing the symptoms of some deeper underlying problem. If that core problem isn’t addressed, it’s likely to cause another outage in the future. That means administrators must perform a root cause analysis (RCA) to discover the source, come up with a fix, and document everything for future reference.

Root cause analysis involves digging through devices, applications, and service logs, which human engineers can’t do as efficiently as AI solutions. AIOps can comb through all the relevant logs to determine the most likely cause of the problem as well as recommend the best solution to fix it. Incidents are automatically generated, prioritized, and assigned to the correct team for resolution, ensuring the core problem is quickly and thoroughly fixed to prevent future outages.

Some AIOps solutions can even automatically resolve some issues without waiting for a human engineer to receive an alert, log in to the system, identify the problem, and implement a solution. This can significantly reduce the mean time to resolution (MTTR) and minimize expensive business interruptions.

Sorting through data is what AIOps does best, which makes it the perfect tool for RCA. AIOps can determine the root cause of automated infrastructure failures much faster than human admins, making it easier to fix these underlying problems before they cause future downtime. AI can even proactively implement fixes while issues are ongoing, allowing businesses to recover faster and reduce the cost of outages.

Implementing AIOps and machine learning in a resilient network automation framework

AIOps is the final layer of the network automation framework because it reduces the management complexity involved in monitoring, troubleshooting, and optimizing automated network infrastructure. Because AIOps needs to collect logs from every single component of the network automation framework, it must be a vendor-neutral solution that has access to your orchestration platform as well as all your management hardware and software. This will be much easier if your orchestration, automation infrastructure, and IT/OT management infrastructure are also vendor-neutral.

For example, the Nodegrid platform from ZPE Systems includes management devices like Gen 3 OOB serial consoles and integrated network edge routers that can bring your entire mixed-vendor environment under a single management umbrella. Nodegrid hardware is truly vendor-neutral, which means it can directly host your AIOps applications to help consolidate devices in your rack. The ZPE Cloud infrastructure orchestration platform also supports integrations with third-party and cloud-based AIOps solutions. Either way, you get network infrastructure management, monitoring, automation, orchestration, and AIOps in a single platform.

ZPE’s Network Automation Blueprint

AIOps works together with IT/OT production infrastructure, automation infrastructure, and orchestration to ensure network resiliency during uncertain times. The Network Automation Blueprint from ZPE Systems provides a reference architecture for achieving Gartner’s definition of hyperautomation as well as meeting the Open Networking User Group (ONUG) Orchestration and Automation recommendations.

Download the Network Automation Blueprint today and see how all these building blocks fit together to ensure network resiliency.

Ready to learn more about implementing AIOps and machine learning?

To learn more about implementing AIOps and machine learning with Nodegrid, contact ZPE Systems today.

Contact Us

A Guide to Infrastructure Orchestration and Automation

infrastructure orchestration and automation
As the recession continues to affect businesses across all industries, enterprise network resilience has never been more critical. The typical outage costs at least $100,000—a price tag that most companies can’t easily absorb in the current economic climate. However, decreasing business revenues have caused many companies, especially in the tech industry, to lay off large portions of their key IT staff. That means there are fewer administrators to monitor and manage network infrastructure and fewer engineers available to respond to issues and recover from outages.

Network automation is the key to ensuring 24/7 availability and optimal performance with less human interaction. A network automation framework provides all the tools and guidance needed to create a fully-automated network infrastructure that’s resilient to failure.

The four building blocks of a resilient network automation framework include:

  1. IT/OT production infrastructure
  2. Automation infrastructure
  3. Orchestration infrastructure
  4. AIOps

In previous blogs we discussed the role of IT/OT production infrastructure in network automation and how an IT/OT convergence strategy accelerates network automation. We also described the automation infrastructure components that enable end-to-end network automation. In this post, we’ll explain how infrastructure orchestration and automation build upon the previous two layers to enable streamlined, hyperautomated network resiliency. Our final blog in the series will conclude with a guide to using AIOps and other machine learning technologies to complete the network automation framework.

What is infrastructure orchestration and automation?

The infrastructure orchestration and automation layer contains the tools and paradigms used to efficiently manage and control that automation. The core components of infrastructure orchestration and automation include:

Version control

The automation infrastructure layer uses infrastructure as code (IaC) to decouple device configurations from the underlying hardware so they can be written as scripts or definition files that automatically provision network resources. In addition, this layer uses software-defined networking (SDN) to create a virtual control plane that overlays the production network infrastructure, allowing network management and optimization tasks to be written as automated scripts.

The goal of IaC and SDN is to reduce human error, speed up device provisioning, and build a more streamlined and resilient network infrastructure. However, IaC and SDN programming can be very complex, and not all sysadmins and network administrators are expert coders. In addition, an automated enterprise network has hundreds or even thousands of these definition files and scripts to store, manage, and deploy.

This is why a network automation framework should include version control in the orchestration and automation layer. Version control is a very familiar concept to programmers, especially in DevOps environments, but not all network and infrastructure teams have used it before. Version control involves storing all code in a centralized repository and then tracking and managing changes to that code.

Let’s say one administrator is responsible for configuring and maintaining the IaC definition file used to provision a particular model of Meraki AP. Here are some examples of how that workflow could break down when that one admin is out of the office for an extended period of time due to COVID-19 or gets laid off due to cutbacks in the organization:

  • Twenty new Meraki APs need to be deployed to a new site with identical configurations.
  • The existing definition needs to be updated and pushed out ASAP to patch a security vulnerability.
  • Someone discovers an error in the current version and they need to roll back to a previous configuration.

A version control system for IaC and SDN acts as the single source of truth for the entire automated infrastructure. All automation scripts and definition files are stored in one centralized location, so anyone with authorization can deploy identical devices with the push of a button. When an admin needs to change the code, those changes are tracked and can be rolled back at any time if a mistake is made. Version control systems even allow admins to leave notes explaining the reasoning or logic behind individual changes, so other team members can pick up where they left off, or in their absence, identify the root cause of issues.

Another key benefit of version control is that it facilitates the use of automated testing. QA and security analysts can run automated scans on code in the version control repository pre-production, so any misconfigurations or security vulnerabilities are identified and fixed before deployment. This reduces the risk of human error and improves the security and resiliency of the automated network infrastructure.

Version control is a core component of infrastructure orchestration and automation because it serves as the single source of truth for the entire automated network architecture.

Orchestrator

Automation is meant to make life easier, but it can be very complicated to manage on a large scale. Modern enterprise network architectures include thousands of moving parts in locations around the world and in the cloud. Automating each of these workflows means writing, testing, deploying, managing, and troubleshooting many different definition files and automation scripts. Doing all of that manually adds more work to overloaded and under-resourced network infrastructure teams, which increases the risk of something going wrong. Simply put, organizations need a way to automate their automation.

An orchestrator is a tool used to control all of the automated workflows on an enterprise network, just like a conductor orchestrates many different instruments and musicians into one cohesive symphony. An orchestrator uses management devices, like Gen 3 OOB serial consoles and SD-WAN gateway routers, to gain control over the physical and virtual network infrastructure. Administrators program the orchestrator to automatically deploy definition files or networking scripts (which it pulls from the version control system) in response to certain triggers. That means admins could potentially automate every step in every workflow, removing the need for human intervention and reducing the chance of errors.

Plus, an orchestrator can react to events much faster than even the best administrator. For example, if a spike in demand is overloading resources at one regional data center, the orchestrator can instantly deploy automated load-balancing workflows to reroute traffic before end-users notice any performance issues. This allows enterprises to maintain 24/7 network availability and performance even with reduced IT staff.

As part of a resilient network automation framework, the orchestrator should be vendor-agnostic (vendor-neutral). It needs to be compatible with all of the automation infrastructure components, as well as the production IT/OT solutions. It also needs to support all of the major third-party automation vendors, such as Ansible and Gluware, to give infrastructure teams the flexibility to use the tools they’re most comfortable with and that work best in their enterprise’s unique environment. Finally, the orchestrator needs to integrate with other tools within the orchestration and automation layer, including the version control system and the monitoring and analytics platform.

The orchestrator is what gives the “orchestration and automation” layer its name. It provides admins with the ability to automatically manage all the automated workflows that make up a resilient network infrastructure. An orchestrator reduces the risk of outages caused by human error and can automatically respond to and prevent potential issues.

Visibility & insights

It’s tempting to think of infrastructure orchestration and automation as a “set it and forget it” solution that can perfectly manage an enterprise network without any human oversight, but the technology isn’t quite there yet. Administrators need a way to monitor all the automated workflows, identify problems the orchestrator may have missed, and analyze the health and performance of the network infrastructure.

A visibility and insights platform collects logs from all the various components of the automated network infrastructure and aggregates the data in one centralized location. It provides visualizations of current device health and network performance, and may even include predictive analysis to power business insights. This gives administrators a big-picture overview of distributed, complex, and automated network architectures so they can ensure continuous availability and optimal performance.

As with the version control system and the orchestrator, the visibility and insights solution needs to be vendor-agnostic so it can dig into every single hardware and software solution in the automated network infrastructure. In a resilient network automation framework, the vendor-neutral version control, orchestrator, and visibility solutions are all combined in a single platform.

Infrastructure orchestration and automation with a single platform

A unified infrastructure orchestration and automation platform like ZPE Cloud simplifies the control and management of a fully-automated enterprise network. ZPE Cloud uses Nodegrid hardware—such as Gen 3 OOB serial consoles and integrated network edge routers—to deliver orchestration and automation to large, distributed, multi-vendor network infrastructures. The ZPE Cloud management app supports integrations with your choice of third-party version control and infrastructure automation solutions, or you can use Nodegrid hardware to directly host your automation software.

With ZPE Cloud, you also get comprehensive monitoring data on all connected infrastructure, plus, you can use Nodegrid environmental monitor sensors to gain insights on conditions in remote data centers and network closets.

ZPE’s Network Automation Blueprint

Infrastructure orchestration and automation works together with IT/OT production infrastructure, automation infrastructure, and AIOps to ensure network resiliency during uncertain times. The Network Automation Blueprint from ZPE Systems provides a reference architecture for achieving Gartner’s definition of hyperautomation as well as meeting the Open Networking User Group (ONUG) Orchestration and Automation recommendations.

In a future blog post, we’ll discuss the remaining building block of the Network Automation Blueprint in depth. In the meantime, you can read about IT/OT production infrastructure and automation infrastructure, or click here to get a sneak peek of the blueprint, which includes a 10-step checklist to get started with automation now.

Ready to learn more about infrastructure orchestration and automation?

To learn more about infrastructure orchestration and automation with ZPE Cloud and Nodegrid, contact ZPE Systems today.

Contact Us