Providing Out-of-Band Connectivity to Mission-Critical IT Resources

Using Isolated Management Infrastructure to Access the Debug Port of Open Compute Project (OCP) Devices in AI Deployments
Data center computers large facility with servers storage. Illustration AI Generative

As artificial intelligence (AI) workloads grow more demanding, data centers are turning to specialized hardware like Open Compute Project (OCP) cards to meet their needs.

OCP cards, known for their open-source architecture and scalability, have become popular in AI-driven infrastructures due to their flexibility and cost-efficiency.

However, managing and troubleshooting these cards — especially in large-scale AI deployments — can pose significant challenges, particularly when it comes to accessing debug ports for diagnostics.

In this post, we’ll explore how isolated management infrastructure (IMI) offers a secure and reliable solution for accessing the debug ports of OCP cards used in AI systems. We’ll also discuss the importance of debugging in AI, the obstacles that come with large-scale deployments, and the role of IMI in overcoming those hurdles.

OCP Cards in AI: A High-Performance Solution

Open Compute Project cards have become central to AI and machine learning (ML) environments due to their powerful compute capabilities, scalability, and open-source design. These cards are often integrated into large data centers tasked with training AI models, running inference operations, and handling massive data streams.

With OCP cards, companies can optimize their data center hardware for specific workloads without being tied to proprietary solutions. This open-source approach allows for flexibility in AI infrastructure, but it also introduces challenges when managing such hardware at scale, especially when components fail or need troubleshooting.

The Importance of Debugging and Monitoring in AI

Debugging and monitoring are critical components of maintaining AI infrastructure. AI model training, in particular, places heavy demands on hardware, making performance consistency a key factor. Any malfunction at the hardware or software level needs to be identified and resolved quickly to avoid costly downtime.

One way to troubleshoot hardware-related problems is by accessing the debug ports of OCP cards. Debug ports provide administrators with direct access to diagnostics, enabling them to monitor system health and perform necessary repairs. However, accessing these ports can be difficult, particularly in AI deployments where hardware is distributed across large data centers.

The Challenges of Accessing Debug Ports in AI Deployments

In a large AI deployment, accessing the debug ports of individual OCP cards can present several obstacles:

  • Physical Access: High-density data centers make it challenging for technicians to reach hardware components physically. In many cases, the OCP cards are housed in remote locations, requiring specialized tools for diagnostics.
  • Security Risks: Allowing unrestricted access to debug ports can introduce security vulnerabilities. If these ports are not properly secured, cyber attackers could exploit them to gain control of critical infrastructure.
  • Network Disruptions: During system failures, it can be difficult to access the network and troubleshoot the issue. When the primary network goes down, relying on that same network to manage hardware can delay recovery efforts and worsen the outage.

These challenges make it essential to adopt a secure, remote solution for managing OCP cards and their debug ports, especially when it comes to AI environments where any downtime can disrupt business-critical operations.

How Isolated Management Infrastructure (IMI) Works

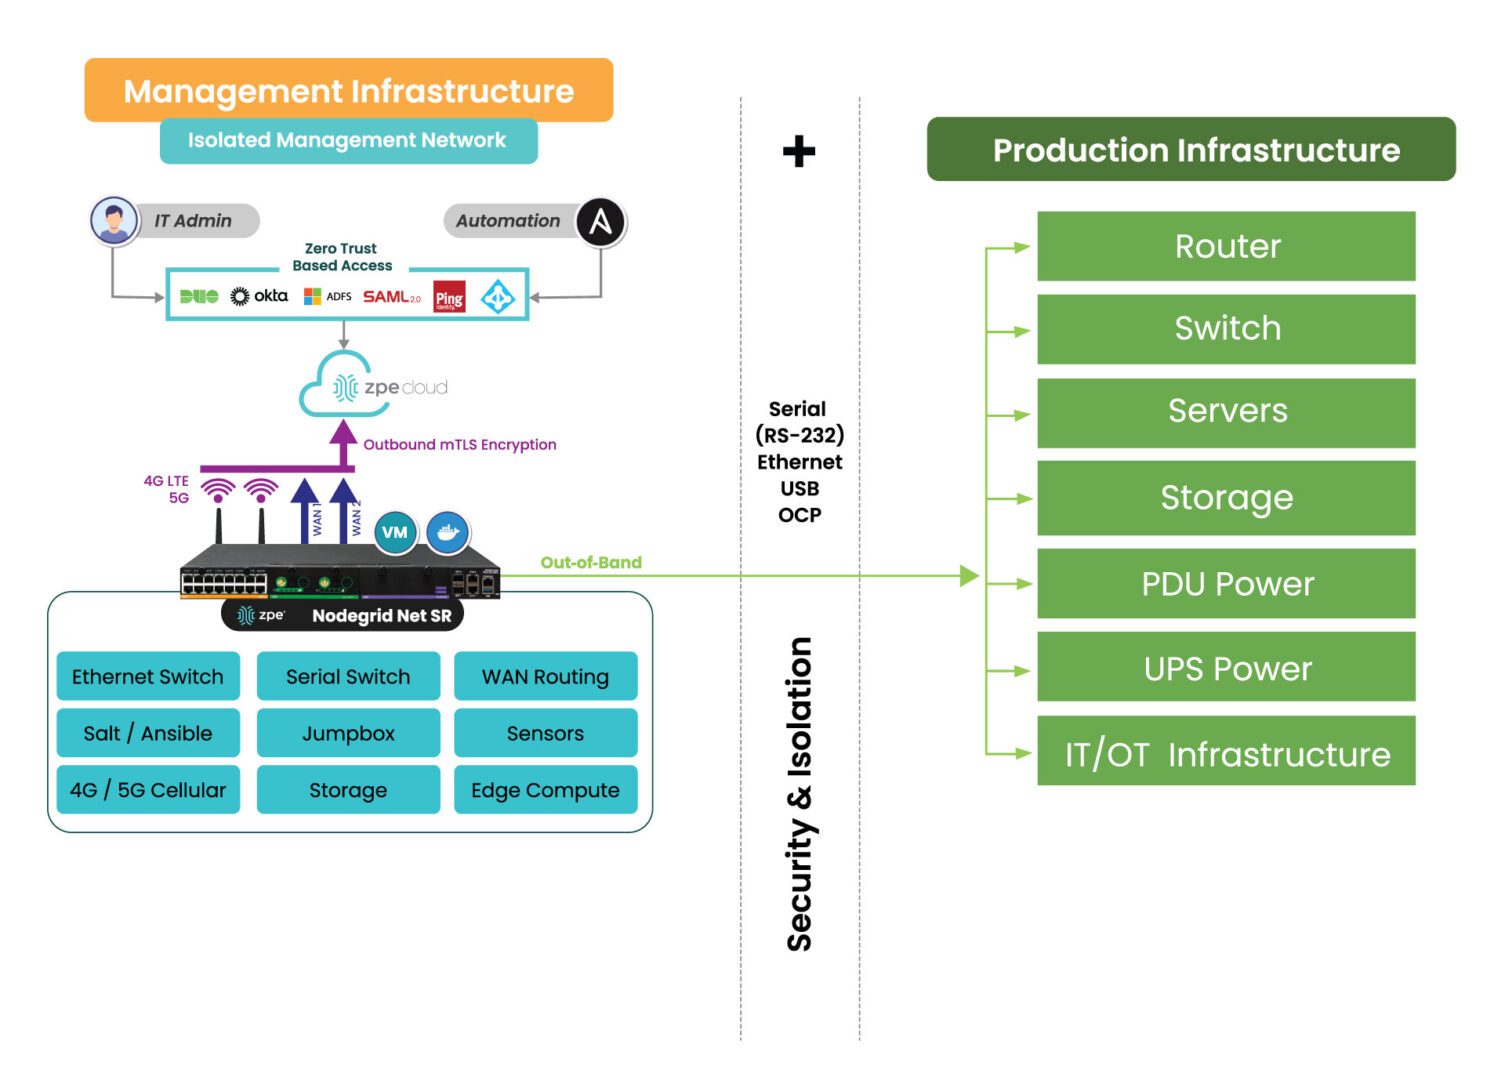
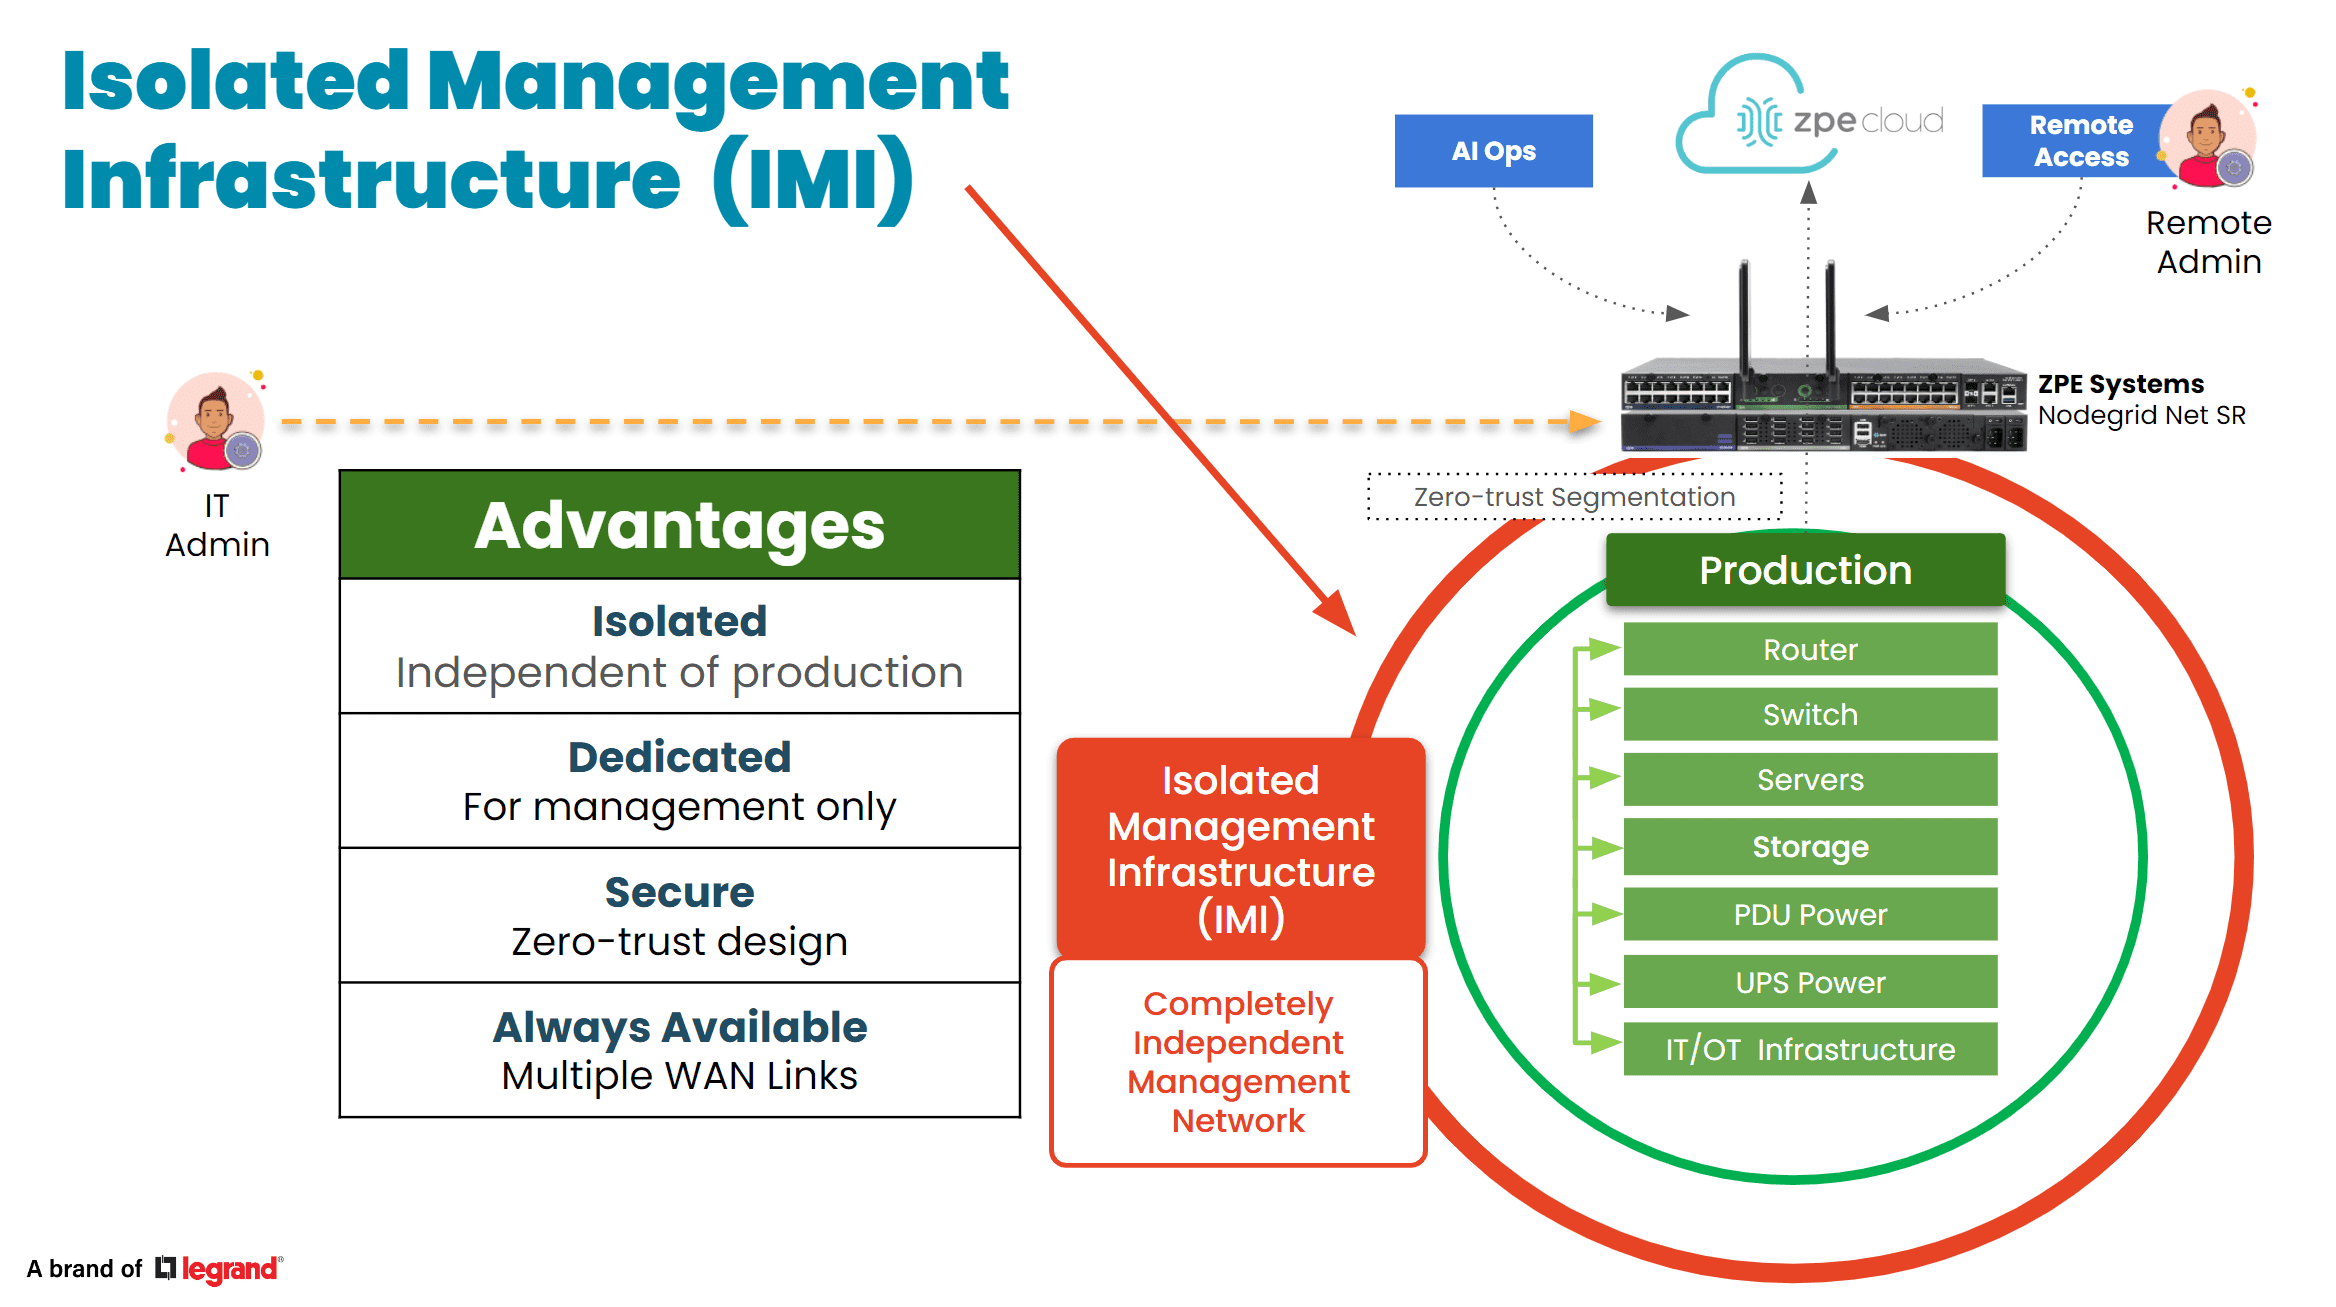
Isolated management infrastructure (IMI) is a dedicated, separate network used exclusively for system management and maintenance. Unlike the primary network that handles day-to-day operations, the management network is isolated to ensure uninterrupted access to critical systems, even during outages or security incidents.
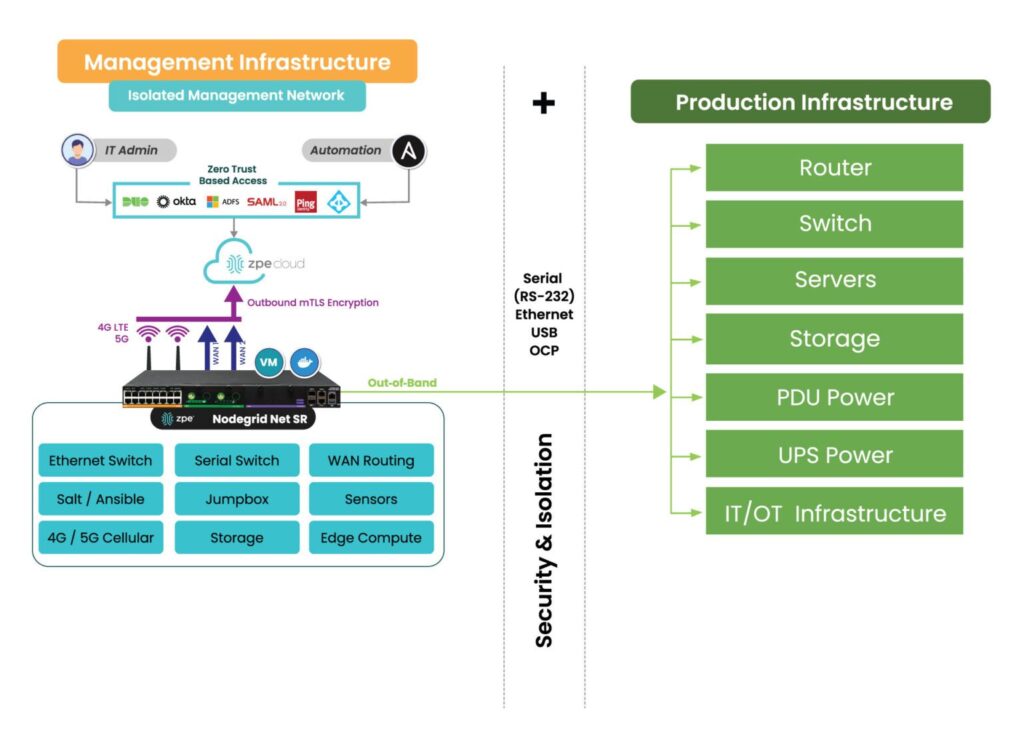
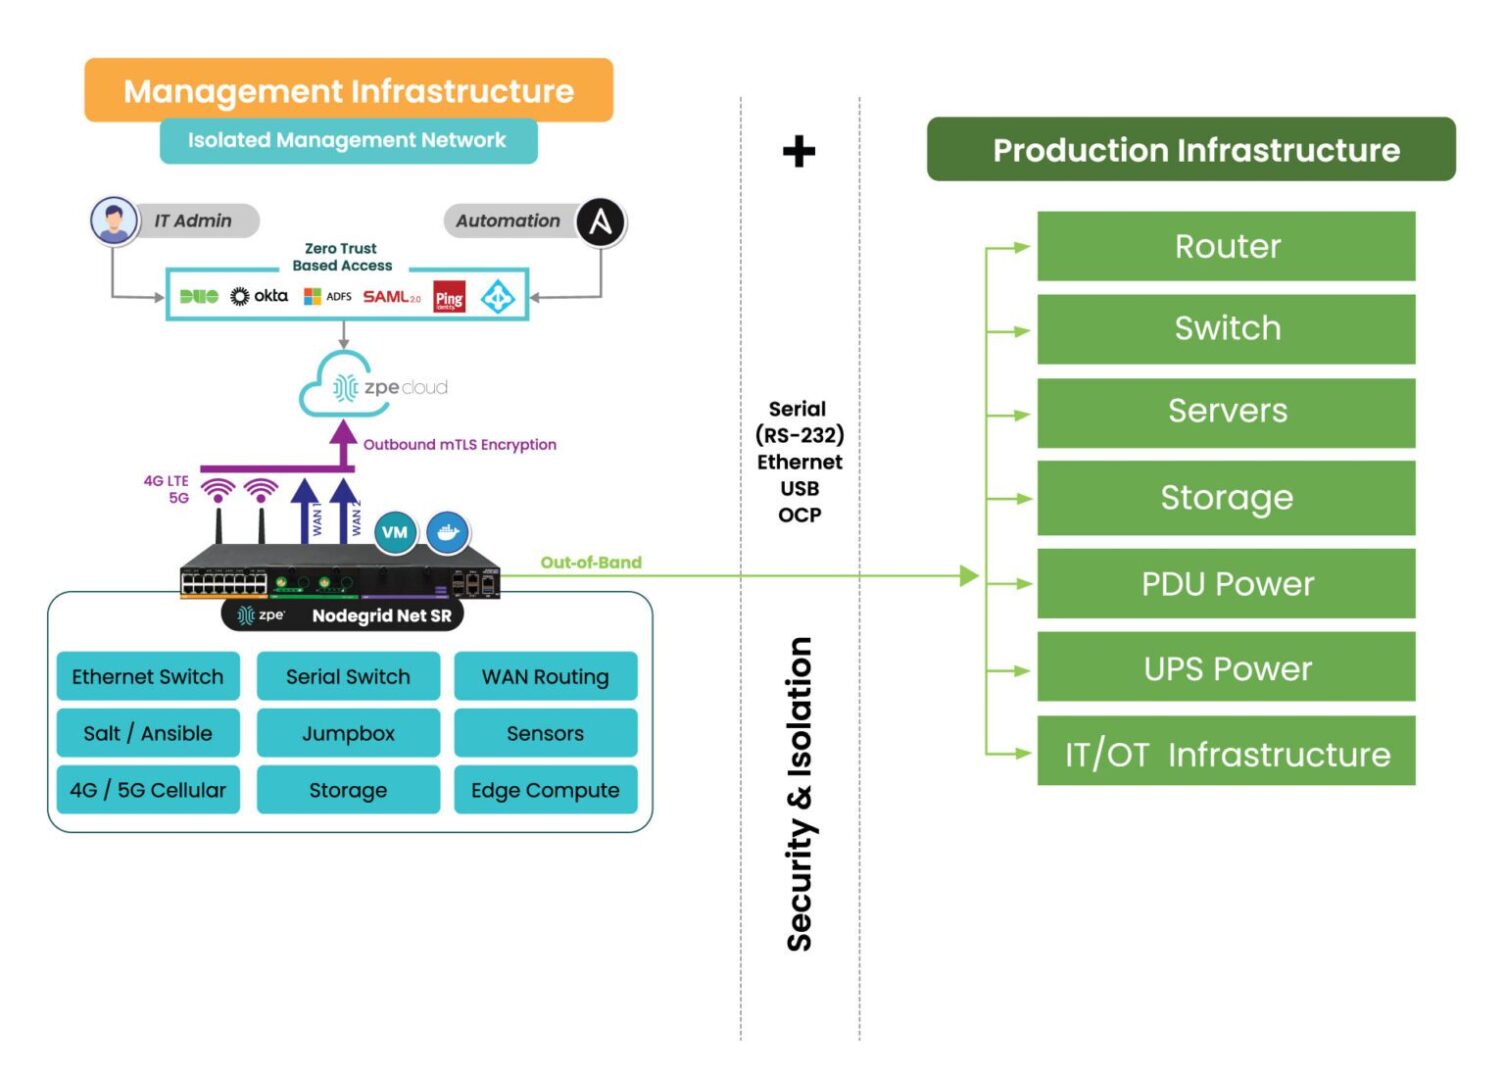
OOB management network isolation with the Nodegrid platform.

Image: Isolated Management Infrastructure physically separates management access from production assets.

By implementing IMI, administrators can remotely access the debug ports of OCP cards without affecting the main production network. This setup not only secures the debug ports but also ensures that troubleshooting can be done in real-time, even if the primary network is down.

Benefits of Using IMI for OCP Debug Ports:

  • Secure, Controlled Access: Since the management network is isolated, it limits access to only authorized personnel. This reduces the chances of an attacker compromising critical hardware through exposed debug ports.
  • Reduced Downtime: IMI enables administrators to access, troubleshoot, and repair systems quickly, minimizing downtime during failures or performance issues. Even during major network outages, IMI ensures out-of-band (OOB) access to the OCP cards’ debug ports.
  • Lower Security Risks: By separating management traffic from regular operations, IMI reduces the attack surface. It becomes more difficult for hackers to use network vulnerabilities to gain unauthorized access to critical infrastructure.
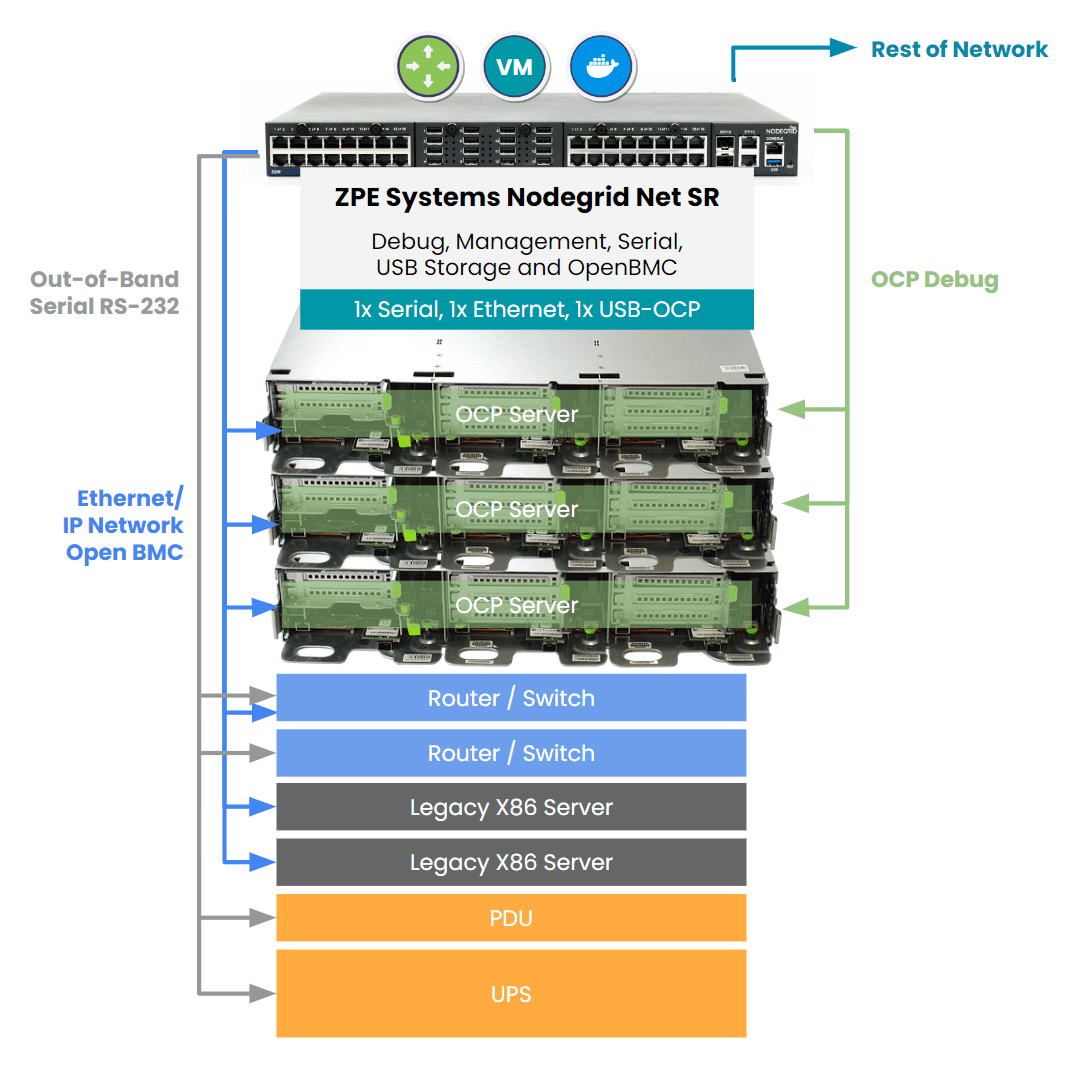
Out-of-band management for OCP servers

Implementing Isolated Management for OCP Debug Access

To implement isolated management infrastructure for accessing the debug ports of OCP cards, follow these steps:

  • Network Segmentation: Physically separate your management network from the production network. Ensure that management traffic is not routed through the same pathways used for regular operations.
  • Use Out-of-Band Management Devices: Deploy dedicated OOB management hardware that allows for remote access and control of the OCP cards, even when the primary network is unavailable. This can include IPMI (Intelligent Platform Management Interface) or SSH (Secure Shell) for secure communication.
  • Integrate with Monitoring Systems: Combine IMI with automated monitoring and alerting systems. This way, any anomaly detected in the AI environment will trigger a response, allowing administrators to quickly access the OCP card’s debug port for diagnostics.

Security Benefits of Isolated Management Infrastructure

In addition to improving accessibility, IMI enhances security across the board in AI environments. Here’s how: 

  • Limited Access Points: Isolating management infrastructure limits the number of entry points for attackers, significantly reducing the attack surface.
  • Controlled User Access: Only authorized users can access the isolated network, meaning that internal threats and insider attacks are also mitigated.
  • Compliance and Auditing: For industries with strict regulatory requirements, IMI provides clear documentation and control over system access, helping organizations meet compliance standards and pass security audits.

Real-World Example

Consider a scenario in a data center where an AI model’s training process experiences sudden instability. The system administrator, located remotely, uses IMI to securely access the OCP card’s debug port through an OOB management interface.

The problem is quickly diagnosed and resolved without needing physical access to the hardware, minimizing downtime and ensuring that the AI model’s training can continue uninterrupted.

Deploy IMI with Nodegrid to Strengthen AI Environments

As AI infrastructures grow, so do the risks and complexities associated with managing them. The October 2024 cyberattack on American Water, which impacted their operational technology and water distribution, highlights the need for robust, secure, and isolated management networks to avoid large-scale disruptions.

By integrating isolated management infrastructure into your AI data center, you can ensure quick access to critical systems like OCP devices, reduce the impact of system failures, and improve security. ZPE Systems’ Nodegrid is a Gen 3 out-of-band management platform that allows you to deploy IMI in your data center environment, and it’s the only out-of-band management built to manage OCP cards. It can integrate or directly host third-party applications for automation, security, and much more, consolidating an entire tech stack into a single, cost-efficient solution.

Schedule a demo to see how Nodegrid gives remote access to OCP cards and strengthens your AI deployments.

Top 5 Data Center Mistakes and How To Avoid Them

Top 5 Data Center Mistakes and How To Avoid Them

Data center deployments require careful planning and execution. The sheer complexity makes it easy to stumble into common pitfalls that can compromise uptime, security, and scalability. After talking with hundreds of customers, we’ve compiled the top five data center mistakes organizations often make during deployments, with tips on how to avoid them.

1. Overlooking Isolated Management Infrastructure

In the data center, the focus is bringing production infrastructure online, including power, cabling, racks, servers, and network gear. But many project managers and architects say they wished they’d given more attention to setting up proper management infrastructure. This oversight usually leads to business challenges down the line, especially when management access relies on the production infrastructure. When a device fails or goes offline, there’s no choice but to go on-site to manually troubleshoot and recover. Many professionals admit to making this data center mistake and wish that they had considered this early in the planning process. Incorporating something called Isolated Management Infrastructure from the start can avoid this challenge, since it provides a dedicated management plane through which teams can access production gear without relying on the production network. 

Tip: Make management infrastructure a priority in your initial planning stages. This proactive approach can prevent complications later.

IMI

2. Neglecting Automation for Configuration and Scaling

Many data center implementors focus heavily on the “rack and stack” initial setup, but fail to automate processes for configuration and scaling operations. This data center mistake often leads to days’ or weeks’ worth of manual, repetitive work, while also exposing the organization to human error. A lot of people we talked to wish they’d invested just a few weeks into automating essential tasks such as switch setup, VLAN configurations, and IP address assignments, which would have saved them lots of time later on and likely helped to prevent errors. Additionally, if rearchitecting is needed, automated systems allow for quick reimplementation, minimizing the time and complexity involved. 

Tip: Dedicate time to automating routine processes. This investment will pay off in enhanced operational efficiency and reduced human error.

3. Inadequate Out-of-Band Management

When people think of out-of-band (OOB) management, a common misconception is that it is solely about Ethernet switches. However, it’s crucial not to overlook the importance of having management access to your entire device stack. Low-level access can be essential for system recovery and management. The recent CrowdStrike outage is a perfect example – when the failed devices needed to be reimaged, typical out-of-band management solutions were inadequate at providing this type of low-level access. Generation three out-of-band serial consoles, like the Nodegrid Net SR, give Ethernet, serial, and USB access, allowing teams to remote-in at the BIOS level to revive failed devices. Using this kind of comprehensive out-of-band – on a fully isolated management plane – helps teams remotely recover and confidently automate processes.

Tip: Ensure that your OOB strategy includes robust serial console access to enhance system reliability and recovery capabilities.

IMI with Nodegrid2

4. Ignoring Security Best Practices

Zero trust security is no longer just advisable, it’s essential. The typical approach is to establish direct connectivity to devices to configure, troubleshoot, upgrade, etc. But this comes with unnecessary risks, often exposing management ports to the Internet and leaving you at risk of attack. Without a fully isolated management plane and zero trust security controls, how would you recover if you were ransomware’d? This is why it’s essential to implement security controls like role-based access and multi-factor authentication, and ensure complete separation of management and production networks. 

Tip: Prioritize security by adopting a zero-trust approach and implementing rigorous access controls to safeguard your data center.

5. Cutting Corners on Out-of-Band Management

In the race for implementing AI, it’s crucial to invest in AI data center infrastructure. But organizations often cut corners on their ability to manage the underlying infrastructure that powers AI. Management access should not stop at ethernet switches; it should extend to encompass serial console access, PDUs, jump boxes, 5G connectivity, routing, WAN links, and a centralized cloud hub with secure tunnels to colocation sites. Using a comprehensive and centralized platform like Nodegrid consolidates many management devices into one while giving remote control to optimize AI’s underlying infrastructure. Aside from enhancing efficiency, this approach minimizes waste and energy consumption, which addresses environmental, social, and governance (ESG) concerns. 

Tip: Avoid the partial out-of-band management deployment. A complete system not only supports resilience and security but also contributes to sustainability goals.


Addressing these common data center mistakes can significantly enhance operational efficiency, security, and scalability. By prioritizing management infrastructure, automating processes, ensuring adequate out-of-band access, implementing robust security measures, and investing wisely in management systems, organizations can build resilient data centers equipped to meet the demands of today and the future.

See ZPE Cloud in action with this video demo

Senior Sales Engineer Marcel van Zwienen gives you a hands-on demo of ZPE Cloud in this video. Watch Marcel take you from signing in to gaining remote access for troubleshooting, to showing how to apply configuration changes automatically across device fleets. Watch now at the link below.

Use Our Blueprint to Avoid Data Center Mistakes

Our blueprint shows how to deploy an isolated management infrastructure, which gives you secure remote access to recover from outages and automate operations. Download now for the complete guide.

Comparing Console Server Hardware

Console servers – also known as serial consoles, console server switches, serial console servers, serial console routers, or terminal servers – are critical for data center infrastructure management. They give administrators a single point of control for devices like servers, switches, and power distribution units (PDUs) so they don’t need to log in to each piece of equipment individually. It also uses multiple network interfaces to provide out-of-band (OOB) management, which creates an isolated network dedicated to infrastructure orchestration and troubleshooting. This OOB network remains accessible during production network outages, offering remote teams a lifeline to recover systems without costly and time-consuming on-site visits. 

Console server hardware can vary significantly across different vendors and use cases. This guide compares console server hardware from the three top vendors and examines four key categories: large data centers, mixed environments, break-fix deployments, and modular solutions.

Console server hardware for large data center deployments

Large and hyperscale data centers can include hundreds or even thousands of individual devices to manage. Teams typically use infrastructure automation, like infrastructure as code (IaC), because managing devices at such a large scale is impossible to do manually. The best console server hardware for high-density data centers will include plenty of managed serial ports, support hundreds of concurrent sessions, and provide support for infrastructure automation.

Click here to compare the hardware specs of the top providers, or read below for more information.

Nodegrid Serial Console Plus (NSCP)

The Nodegrid Serial Console Plus (NSCP) from ZPE Systems is the only console server providing up to 96 RS-232 serial ports in a 1U rack-mounted form factor. Its quad-core Intel processor and robust (as well as upgradable) internal storage and RAM options, as well as its Linux-based Nodegrid OS, support Guest OS and Docker containers for third-party applications. That means the NSCP can directly host infrastructure automation (like Ansible, Puppet, and Chef), security (like Palo Alto’s next-generation firewalls and Secure Access Service Edge), and much more. Plus, it can extend zero-touch provisioning (ZTP) to legacy and mixed-vendor devices that otherwise wouldn’t support automation.

The NSCP also comes packed with hardware security features including BIOS protection, UEFI Secure Boot, self-encrypted disk (SED), Trusted Platform Module (TPM) 2.0, and a multi-site VPN using IPSec, WireGuard, and OpenSSL protocols. Plus, it supports a wide range of USB environmental monitoring sensors to help remote teams control conditions in the data center or colocation facility.

Advantages:

  • Up to 96 managed serial ports in a 1U appliance
  • Intel x86 CPU and 4GB of RAM for 3rd-party Docker and VM apps
  • Extends ZTP and automation to legacy and mixed-vendor infrastructure
  • Robust on-board security features like BIOS protection and TPM 2.0
  • Supports a wide range of USB environmental monitoring sensors
  • Wi-Fi and 5G/4G LTE options available
  • Supports over 1,000 concurrent sessions

Disadvantages:

  • USB ports limited on 96-port model

Opengear CM8100

The Opengear CM8100 comes in two models: the 1G version includes up to 48 managed serial ports, while the 10G version supports up to 96 serial ports in a 2U form factor. Both models have a dual-core ARM Cortex processor and 2GB of RAM, allowing for some automation support with upgraded versions of the Lighthouse management software. They also come with an embedded firewall, IPSec and OpenVPN protocols for a single-site VPN, and TPM 2.0 security.

Advantages:

  • 10G model comes with software-selectable serial ports
  • Supports OpenVPN and IPSec VPNs
  • Fast port speeds

Disadvantages:

  • Automation and ZTP require Lighthouse software upgrade
  • No cellular or Wi-Fi options
  • 96-port model requires 2U of rack space

Perle IOLAN SCG (fixed)

The IOLAN SCG is Perle’s fixed-form-factor console server solution. It supports up to 48 managed serial ports and can extend ZTP to end devices. It comes with onboard security features including an embedded firewall, OpenVPN and IPSec VPN, and AES encryption. However, the IOLAN SCG’s underpowered single-core ARM processor, 1GB of RAM, and 4GB of storage limit its automation capabilities, and it does not integrate with any third-party automation or orchestration solutions. 

Advantages:

  • Supports ZTP for end devices
  • Comprehensive firewall functionality

Disadvantages

  • Very limited CPU, RAM, and flash storage
  • Does not support third-party automation

Comparison Table: Console Server Hardware for Large Data Centers

Nodegrid NSCP Opengear CM8100 Perle IOLAN SCG
Serial Ports 16 / 32 / 48 / 96x RS-232 16 / 32 / 48 / 96x RS-232 16 / 32 / 48x RS-232
Max Port Speed 230,400 bps 230,400 bps 230,000 bps
Network Interfaces

2x SFP+ 

2x ETH

1x Wi-Fi (optional)

2x Dual SIM LTE (optional)

2x ETH 1x ETH
Additional Interfaces

1x RS-232 console

2x USB 3.0 Type A

1x HDMI Output

1x RS-232 console

2x USB 3.0

1x RS-232 console

1x Micro USB w/DB9 Adapter

Environmental Monitoring Any USB sensors
CPU Intel x86_64 Quad-Core ARM Cortex-A9 1.6 GHz Dual-Core ARM 32-bit 500MHz Single-Core
Storage 32GB SSD (upgrades available) 32GB eMMC 4GB Flash
RAM 4GB DDR4 (upgrades available) 2GB DDR4 1GB
Power

Single or Dual AC

Dual DC

Dual AC

Dual DC

Single AC
Form Factor 1U Rack Mounted

1U Rack Mounted (up to 48 ports)

2U Rack Mounted (96 ports)

1U Rack Mounted
Data Sheet Download

CM8100 1G

CM8100 10G

Download

Console server hardware for mixed environments

Data center deployments that include a mix of legacy and modern solutions from multiple vendors benefit from console server hardware that includes software-selectable serial ports. This feature allows administrators to manage devices with straight or rolled RS-232 pinouts from the same console server. 

Click here to compare the hardware specs of the top providers, or read below for more information.

Nodegrid Serial Console S Series

The Nodegrid Serial Console S Series has up to 48 auto-sensing RS-232 serial ports and 14 high-speed managed USB ports, allowing for the control of up to 62 devices. Like the NSCP, the S Series has a quad-core Intel CPU and upgradeable storage and RAM, supporting third-party VMs and containers for automation, orchestration, security, and more. It also comes with the same robust security features to protect the management network.

Advantages:

  • Includes 14 high-speed managed USB ports
  • Intel x86 CPU and 4GBof RAM for 3rd-party Docker and VM apps
  • Supports a wide range of USB environmental monitoring sensors
  • Extends ZTP and automation to legacy and mixed-vendor infrastructure
  • Robust on-board security features like BIOS protection and TPM 2.0
  • Supports 250+ concurrent sessions

Disadvantages

  • Only offers 1Gbps and Ethernet connectivity for OOB

Opengear OM2200

The Opengear OM2200 comes with 16, 32, or 48 software-selectable RS-232 ports, or, with the OM2224-24E model, 24 RS-232 and 24 managed Ethernet ports. It also includes 8 managed USB ports and the option for a V.92 analog modem. It has impressive storage space and 8GB of DDR4 RAM for automated workflows, though, as with all Opengear solutions, the upgraded version of the Lighthouse management software is required for ZTP and NetOps automation support.

Advantages:

  • Optional managed Ethernet ports
  • Optional V.92 analog modem for OOB
  • 64GB of storage and 8GB DDR4 RAM

Disadvantages:

  • Automation and ZTP require Lighthouse software upgrade
  • No cellular or Wi-Fi options

Comparison Table: Console Server Hardware for Mixed Environments

  Nodegrid S Series Opengear OM2200
Serial Ports

16 / 32 / 48x Software Selectable RS-232

14x USB-A serial

16 / 32 / 48x Software Selectable RS-232
8x USB 2.0 serial


(OM2224-24E) 24x Software Selectable RS-232 and 24x Managed Ethernet

Max Port Speed

230,400 bps (RS-232)

921,600 bps (USB)

230,400 bps
Network Interfaces 2x1Gbps or 2x ETH

2x SFP+ or 2x ETH

1x V.92 modem (select models)

Additional Interfaces

1x RS-232 console

1x USB 3.0 Type A

1x HDMI Output

1x RS-232 console

1x Micro USB

2x USB 3.0

Environmental Monitoring Any USB sensors
CPU Intel x86_64 Dual-Core AMD GX-412TC 1.4 GHz Quad-Core
Storage 32GB SSD (upgrades available) 64GB SSD
RAM 4GB DDR4 (upgrades available) 8GB DDR3
Power

Single or Dual AC

Dual DC

Dual AC

Dual DC

Form Factor 1U Rack Mounted 1U Rack Mounted
Data Sheet Download Download

Console server hardware for break-fix deployments

A full-featured console server solution may be too complicated and expensive for certain use cases, especially for organizations just looking for “break-fix” OOB access to remotely troubleshoot and recover from issues. The best console server hardware for this type of deployment provides fast and reliable network access to managed devices without extra features that increase the price and complexity.

Click here to compare the hardware specs of the top providers, or read below for more information.

Nodegrid Serial Console Core Edition (NSCP-CE)

The Nodegrid Serial Console Core Edition (NSCP-CE) provides the same hardware and security features as the NSCP, as well as ZTP, but without the advanced automation capabilities. Its streamlined management and affordable price tag make it ideal for lean, budget-conscious IT departments. And, like all Nodegrid solutions, it comes with the most comprehensive hardware security features in the industry. 

Advantages:

  • Up to 48 managed serial ports in a 1U appliance
  • Extends ZTP and automation to legacy and mixed-vendor infrastructure
  • Robust on-board security features like BIOS protection and TPM
  • Supports a wide range of USB environmental monitoring sensors
  • Analog modem and 5G/4G LTE options available
  • Supports over 100 concurrent sessions

Disadvantages

  •  Supports automation only via ZPE Cloud

Opengear CM7100

The Opengear CM7100 is the previous generation of the CM8100 solution. Its serial and network interface options are the same, but it comes with a weaker, Armada 800 MHz CPU, and there are options for smaller storage and RAM configurations to reduce the price. As with all Opengear console servers, the CM7100 doesn’t support ZTP without paying for an upgraded Lighthouse license, however.

Advantages:

  • Can reduce storage and RAM to save money
  • Supports OpenVPN and IPSec VPNs
  • Fast port speeds

Disadvantages:

  • Automation and ZTP require Lighthouse software upgrade
  • No cellular or Wi-Fi options
  • 96-port model requires 2U of rack space

Comparison Table: Console Server Hardware for Break-Fix Deployments

  Nodegrid NSCP-CE Opengear CM7100
Serial Ports 16 / 32 / 48 / RS-232 16 / 32 / 48 / 96x RS-232
Max Port Speed 230,400 bps 230,400 bps
Network Interfaces

2x SFP ETH

1x Analog modem (optional)

2x 5G/4G LTE (optional)

2x ETH
Additional Interfaces

1x RS-232 console

2x USB 3.0 Type A

1x RS-232 console

2x USB 2.0

Environmental Monitoring Any USB sensors Smoke, water leak, vibration
CPU Intel x86_64 Dual-Core Armada 370 ARMv7 800 MHz
Storage 16GB Flash (upgrades available) 4-64GB storage
RAM 4GB DDR4 (upgrades available) 256MB-2GB DDR3
Power

Dual AC

Dual DC

Single or Dual AC
Form Factor 1U Rack Mounted

1U Rack Mounted (up to 48 ports)

2U Rack Mounted (96 ports)

Data Sheet Download Download

Modular console server hardware for flexible deployments

Modular console servers allow organizations to create customized solutions tailored to their specific deployment and use case. They also support easy scaling by allowing teams to add more managed ports as the network grows, and provide the flexibility to swap-out certain capabilities and customize their hardware and software as the needs of the business change. 

Click here to compare the hardware specs of the top providers, or read below for more information.

Nodegrid Net Services Router (NSR)

The Nodegrid Net Services Router (NSR) has up to five expansion bays that can support any combination of 16 RS-232 or 16 USB serial modules. In addition to managed ports, there are NSR modules for Ethernet (with or without PoE – Power over Ethernet) switch ports, Wi-Fi and dual-SIM cellular, additional SFP ports, extra storage, and compute. 

The NSR comes with an eight-core Intel CPU and 8GB DDR4 RAM, offering the same vendor-neutral Guest OS/Docker support and onboard security features as the NSCP. It can also run virtualized network functions to consolidate an entire networking stack in a single device. This makes the NSR adaptable to nearly any deployment scenario, including hyperscale data centers, edge computing sites, and branch offices.

Advantages:

  • Up to 5 expansion bays provide support for up to 80 managed devices
  • 8GB of DDR4 RAM
  • Robust on-board security features like BIOS protection and TPM 2.0
  • Supports a wide range of USB environmental monitoring sensors
  • Wi-Fi and 5G/4G LTE options available
  • Optional modules for various interfaces, extra storage, and compute

Disadvantages

  • No V.92 modem support

Perle IOLAN SCG L/W/M

The Perle IOLAN SCG modular series is customizable with cellular LTE, Wi-Fi, a V.92 analog modem, or any combination of the three. It also has three expansion bays that support any combination of 16-port RS-232 or 16-port USB modules. Otherwise, this version of the IOLAN SCG comes with the same security features and hardware limitations as the fixed form factor models.

Advantages:

  • Cellular, Wi-Fi, and analog modem options
  • Supports ZTP for end devices
  • Comprehensive firewall functionality

Disadvantages

  • Very limited CPU, RAM, and flash storage
  • Does not support third-party automation

Comparison Table: Modular Console Server Hardware

  Nodegrid NSR Perle IOLAN SCG R/U
Serial Ports

16 / 32 / 48 / 64 / 80x RS-232 with up to 5 serial modules

16 / 32 / 48 / 64 / 80x USB with up to 5 serial modules

Up to 50x RS-232/422/485

Up to 50x USB

Max Port Speed 230,400 bps 230,000 bps
Network Interfaces

1x SFP+ 

1x ETH with PoE in

1x Wi-Fi (optional)

1x Dual SIM LTE (optional)

2x SFP or 2x ETH
Additional Interfaces

1x RS-232 console

2x USB 2.0 Type A

2x GPIO

2x Digital Out

1x VGA

Optional Modules (up to 5):

16x ETH

8x PoE+

16x SFP

8x SFP+

16x USB OCP Debug

1x RS-232 console

1x Micro USB w/DB9 adapter


Environmental Monitoring Any USB sensors
CPU Intel x86_64 Quad- or Eight-Core ARM 32-bit 500MHz Single-Core
Storage 32GB SSD (upgrades available) 4GB Flash
RAM 8GB DDR4 (upgrades available 1GB
Power

Dual AC

Dual DC

Dual AC

Dual DC

Form Factor 1U Rack Mounted 1U Rack Mounted
Data Sheet Download Download

Get the best console server hardware for your deployment with Nodegrid

The vendor-neutral Nodegrid platform provides solutions for any use case, deployment size, and pain points. Schedule a free Nodegrid demo to learn more.

Want to see Nodegrid in action?

Watch a demo of the Nodegrid Gen 3 out-of-band management solution to see how it can improve scalability for your data center architecture.

Watch a demo

Data Center Scalability Tips & Best Practices

Data center scalability is the ability to increase or decrease workloads cost-effectively and without disrupting business operations. Scalable data centers make organizations agile, enabling them to support business growth, meet changing customer needs, and weather downturns without compromising quality. This blog describes various methods for achieving data center scalability before providing tips and best practices to make scalability easier and more cost-effective to implement.

How to achieve data center scalability

There are four primary ways to scale data center infrastructure, each of which has advantages and disadvantages.


4 Data center scaling methods

Method Description Pros and Cons
1. Adding more servers Also known as scaling out or horizontal scaling, this involves adding more physical or virtual machines to the data center architecture. Can support and distribute more workloads

Eliminates hardware constraints

Deployment and replication take time

Requires more rack space

Higher upfront and operational costs

2. Virtualization Dividing physical hardware into multiple virtual machines (VMs) or virtual network functions (VNFs) to support more workloads per device. Supports faster provisioning

Uses resources more efficiently

Reduces scaling costs

Transition can be expensive and disruptive

Not supported by all hardware and software

3. Upgrading existing hardware Also known as scaling up or vertical scaling, this involves adding more processors, memory, or storage to upgrade the capabilities of existing systems. Implementation is usually quick and non-disruptive

More cost-effective than horizontal scaling

Requires less power and rack space

Scalability limited by server hardware constraints

Increases reliance on legacy systems

4. Using cloud services Moving some or all workloads to the cloud, where resources can be added or removed on-demand to meet scaling requirements. Allows on-demand or automatic scaling

Better support for new and emerging technologies

Reduces data center costs

Migration is often extremely disruptive

Auto-scaling can lead to ballooning monthly bills

May not support legacy software

It’s important for companies to analyze their requirements and carefully consider the advantages and disadvantages of each method before choosing a path forward. 

Best practices for data center scalability

The following tips can help organizations ensure their data center infrastructure is flexible enough to support scaling by any of the above methods.

Run workloads on vendor-neutral platforms

Vendor lock-in, or a lack of interoperability with third-party solutions, can severely limit data center scalability. Using vendor-neutral platforms ensures that teams can add, expand, or integrate data center resources and capabilities regardless of provider. These platforms make it easier to adopt new technologies like artificial intelligence (AI) and machine learning (ML) while ensuring compatibility with legacy systems.

Use infrastructure automation and AIOps

Infrastructure automation technologies help teams provision and deploy data center resources quickly so companies can scale up or out with greater efficiency. They also ensure administrators can effectively manage and secure data center infrastructure as it grows in size and complexity. 

For example, zero-touch provisioning (ZTP) automatically configures new devices as soon as they connect to the network, allowing remote teams to deploy new data center resources without on-site visits. Automated configuration management solutions like Ansible and Chef ensure that virtualized system configurations stay consistent and up-to-date while preventing unauthorized changes. AIOps (artificial intelligence for IT operations) uses machine learning algorithms to detect threats and other problems, remediate simple issues, and provide root-cause analysis (RCA) and other post-incident forensics with greater accuracy than traditional automation. 

Isolate the control plane with Gen 3 serial consoles

Serial consoles are devices that allow administrators to remotely manage data center infrastructure without needing to log in to each piece of equipment individually. They use out-of-band (OOB) management to separate the data plane (where production workflows occur) from the control plane (where management workflows occur). OOB serial console technology – especially the third-generation (or Gen 3) – aids data center scalability in several ways:

  1. Gen 3 serial consoles are vendor-neutral and provide a single software platform for administrators to manage all data center devices, significantly reducing management complexity as infrastructure scales out.
  2. Gen 3 OOB can extend automation capabilities like ZTP to mixed-vendor and legacy devices that wouldn’t otherwise support them.
  3. OOB management moves resource-intensive infrastructure automation workflows off the data plane, improving the performance of production applications and workflows.
  4. Serial consoles move the management interfaces for data center infrastructure to an isolated control plane, which prevents malware and cybercriminals from accessing them if the production network is breached. Isolated management infrastructure (IMI) is a security best practice for data center architectures of any size.

How Nodegrid simplifies data center scalability

Nodegrid is a Gen 3 out-of-band management solution that streamlines vertical and horizontal data center scalability. 

The Nodegrid Serial Console Plus (NSCP) offers 96 managed ports in a 1RU rack-mounted form factor, reducing the number of OOB devices needed to control large-scale data center infrastructure. Its open, x86 Linux-based OS can run VMs, VNFs, and Docker containers so teams can run virtualized workloads without deploying additional hardware. Nodegrid can also run automation, AIOps, and security on the same platform to further reduce hardware overhead.

Nodegrid OOB is also available in a modular form factor. The Net Services Router (NSR) allows teams to add or swap modules for additional compute, storage, memory, or serial ports as the data center scales up or down.

Want to see Nodegrid in action?

Watch a demo of the Nodegrid Gen 3 out-of-band management solution to see how it can improve scalability for your data center architecture.

Watch a demo

Edge Computing Use Cases in Banking

financial services

The banking and financial services industry deals with enormous, highly sensitive datasets collected from remote sites like branches, ATMs, and mobile applications. Efficiently leveraging this data while avoiding regulatory, security, and reliability issues is extremely challenging when the hardware and software resources used to analyze that data reside in the cloud or a centralized data center.

Edge computing decentralizes computing resources and distributes them at the network’s “edges,” where most banking operations take place. Running applications and leveraging data at the edge enables real-time analysis and insights, mitigates many security and compliance concerns, and ensures that systems remain operational even if Internet access is disrupted. This blog describes four edge computing use cases in banking, lists the benefits of edge computing for the financial services industry, and provides advice for ensuring the resilience, scalability, and efficiency of edge computing deployments.

4 Edge computing use cases in banking

1. AI-powered video surveillance

PCI DSS requires banks to monitor key locations with video surveillance, review and correlate surveillance data on a regular basis, and retain videos for at least 90 days. Constantly monitoring video surveillance feeds from bank branches and ATMs with maximum vigilance is nearly impossible for humans, but machines excel at it. Financial institutions are beginning to adopt artificial intelligence solutions that can analyze video feeds and detect suspicious activity with far greater vigilance and accuracy than human security personnel.

When these AI-powered surveillance solutions are deployed at the edge, they can analyze video feeds in real time, potentially catching a crime as it occurs. Edge computing also keeps surveillance data on-site, reducing bandwidth costs and network latency while mitigating the security and compliance risks involved with storing videos in the cloud.

2. Branch customer insights

Banks collect a lot of customer data from branches, web and mobile apps, and self-service ATMs. Feeding this data into AI/ML-powered data analytics software can provide insights into how to improve the customer experience and generate more revenue. By running analytics at the edge rather than from the cloud or centralized data center, banks can get these insights in real-time, allowing them to improve customer interactions while they’re happening.

For example, edge-AI/ML software can help banks provide fast, personalized investment advice on the spot by analyzing a customer’s financial history, risk preferences, and retirement goals and recommending the best options. It can also use video surveillance data to analyze traffic patterns in real-time and ensure tellers are in the right places during peak hours to reduce wait times.

3. On-site data processing

Because the financial services industry is so highly regulated, banks must follow strict security and privacy protocols to protect consumer data from malicious third parties. Transmitting sensitive financial data to the cloud or data center for processing increases the risk of interception and makes it more challenging to meet compliance requirements for data access logging and security controls.

Edge computing allows financial institutions to leverage more data on-site, within the network security perimeter. For example, loan applications contain a lot of sensitive and personally identifiable information (PII). Processing these applications on-site significantly reduces the risk of third-party interception and allows banks to maintain strict control over who accesses data and why, which is more difficult in cloud and colocation data center environments.

4. Enhanced AIOps capabilities

Financial institutions use AIOps (artificial intelligence for IT operations) to analyze monitoring data from IT devices, network infrastructure, and security solutions and get automated incident management, root-cause analysis (RCA), and simple issue remediation. Deploying AIOps at the edge provides real-time issue detection and response, significantly shortening the duration of outages and other technology disruptions. It also ensures continuous operation even if an ISP outage or network failure cuts a branch off from the cloud or data center, further helping to reduce disruptions and remote sites.

Additionally, AIOps and other artificial intelligence technology tend to use GPUs (graphics processing units), which are more expensive than CPUs (central processing units), especially in the cloud. Deploying AIOps on small, decentralized, multi-functional edge computing devices can help reduce costs without sacrificing functionality. For example, deploying an array of Nvidia A100 GPUs to handle AIOps workloads costs at least $10k per unit; comparable AWS GPU instances can cost between $2 and $3 per unit per hour. By comparison, a Nodegrid Gate SR costs under $5k and also includes remote serial console management, OOB, cellular failover, gateway routing, and much more.

The benefits of edge computing for banking

Edge computing can help the financial services industry:

  • Reduce losses, theft, and crime by leveraging artificial intelligence to analyze real-time video surveillance data.
  • Increase branch productivity and revenue with real-time insights from security systems, customer experience data, and network infrastructure.
  • Simplify regulatory compliance by keeping sensitive customer and financial data on-site within company-owned infrastructure.
  • Improve resilience with real-time AIOps capabilities like automated incident remediation that continues operating even if the site is cut off from the WAN or Internet
  • Reduce the operating costs of AI and machine learning applications by deploying them on small, multi-function edge computing devices. 
  • Mitigate the risk of interception by leveraging financial and IT data on the local network and distributing the attack surface.

Edge computing best practices

Isolating the management interfaces used to control network infrastructure is the best practice for ensuring the security, resilience, and efficiency of edge computing deployments. CISA and PCI DSS 4.0 recommend implementing isolated management infrastructure (IMI) because it prevents compromised accounts, ransomware, and other threats from laterally moving from production resources to the control plane.

IMI with Nodegrid(2)

Using vendor-neutral platforms to host, connect, and secure edge applications and workloads is the best practice for ensuring the scalability and flexibility of financial edge architectures. Moving away from dedicated device stacks and taking a “platformization” approach allows financial institutions to easily deploy, update, and swap out applications and capabilities on demand. Vendor-neutral platforms help reduce hardware overhead costs to deploy new branches and allow banks to explore different edge software capabilities without costly hardware upgrades.

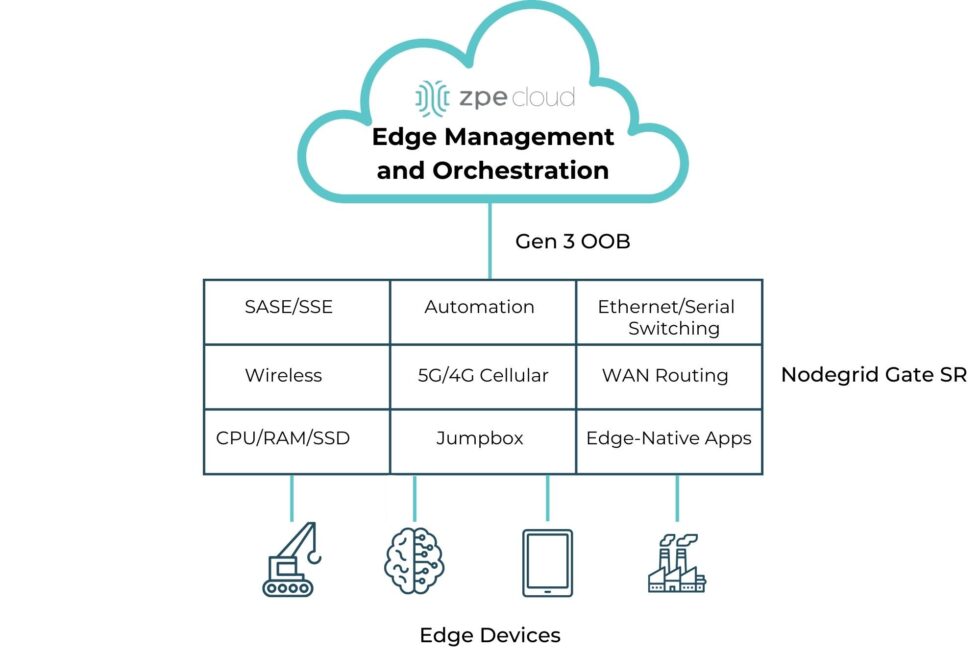
Edge-Management-980×653

Additionally, using a centralized, cloud-based edge management and orchestration (EMO) platform is the best practice for ensuring remote teams have holistic oversight of the distributed edge computing architecture. This platform should be vendor-agnostic to ensure complete coverage over mixed and legacy architectures, and it should use out-of-band (OOB) management to provide continuous remote access to edge infrastructure even during a major service outage.

How Nodegrid streamlines edge computing for the banking industry

Nodegrid is a vendor-neutral edge networking platform that consolidates an entire edge tech stack into a single, cost-effective device. Nodegrid has a Linux-based OS that supports third-party VMs and Docker containers, allowing banks to run edge computing workloads, data analytics software, automation, security, and more. 

The Nodegrid Gate SR is available with an Nvidia Jetson Nano card that’s optimized for artificial intelligence workloads. This allows banks to run AI surveillance software, ML-powered recommendation engines, and AIOps at the edge alongside networking and infrastructure workloads rather than purchasing expensive, dedicated GPU resources. Plus, Nodegrid’s Gen 3 OOB management ensures continuous remote access and IMI for improved branch resilience.

Get Nodegrid for your edge computing use cases in banking

Nodegrid’s flexible, vendor-neutral platform adapts to any use case and deployment environment. Watch a demo to see Nodegrid’s financial network solutions in action.

Watch a demo

AI Data Center Infrastructure

ZPE Systems – AI Data Center Infrastructure
Artificial intelligence is transforming business operations across nearly every industry, with the recent McKinsey global survey finding that 72% of organizations had adopted AI, and 65% regularly use generative AI (GenAI) tools specifically. GenAI and other artificial intelligence technologies are extremely resource-intensive, requiring more computational power, data storage, and energy than traditional workloads. AI data center infrastructure also requires high-speed, low-latency networking connections and unified, scalable management hardware to ensure maximum performance and availability. This post describes the key components of AI data center infrastructure before providing advice for overcoming common pitfalls to improve the efficiency of AI deployments.

AI data center infrastructure components

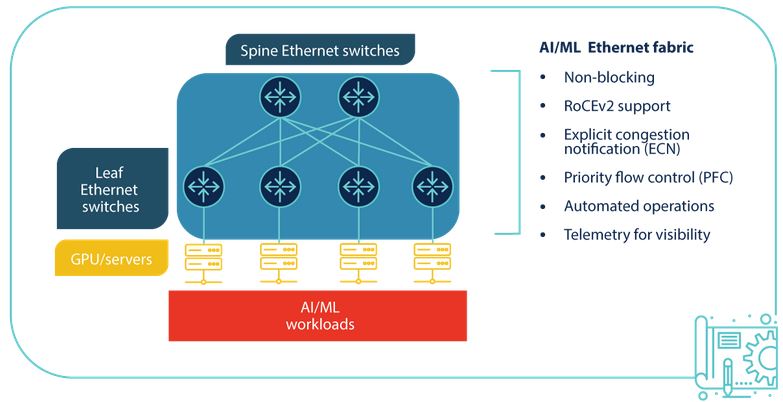
A diagram of AI data center infrastructure.

Computing

Generative AI and other artificial intelligence technologies require significant processing power. AI workloads typically run on graphics processing units (GPUs), which are made up of many smaller cores that perform simple, repetitive computing tasks in parallel. GPUs can be clustered together to process data for AI much faster than CPUs.

Storage

AI requires vast amounts of data for training and inference. On-premises AI data centers typically use object storage systems with solid-state disks (SSDs) composed of multiple sections of flash memory (a.k.a., flash storage). Storage solutions for AI workloads must be modular so additional capacity can be added as data needs grow, through either physical or logical (networking) connections between devices.

Networking

AI workloads are often distributed across multiple computing and storage nodes within the same data center. To prevent packet loss or delays from affecting the accuracy or performance of AI models, nodes must be connected with high-speed, low-latency networking. Additionally, high-throughput WAN connections are needed to accommodate all the data flowing in from end-users, business sites, cloud apps, IoT devices, and other sources across the enterprise.

Power

AI infrastructure uses significantly more power than traditional data center infrastructure, with a rack of three or four AI servers consuming as much energy as 30 to 40 standard servers. To prevent issues, these power demands must be accounted for in the layout design for new AI data center deployments and, if necessary, discussed with the colocation provider to ensure enough power is available.

Management

Data center infrastructure, especially at the scale required for AI, is typically managed with a jump box, terminal server, or serial console that allows admins to control multiple devices at once. The best practice is to use an out-of-band (OOB) management device that separates the control plane from the data plane using alternative network interfaces. An OOB console server provides several important functions:

  1. It provides an alternative path to data center infrastructure that isn’t reliant on the production ISP, WAN, or LAN, ensuring remote administrators have continuous access to troubleshoot and recover systems faster, without an on-site visit.
  2. It isolates management interfaces from the production network, preventing malware or compromised accounts from jumping over from an infected system and hijacking critical data center infrastructure.
  3. It helps create an isolated recovery environment where teams can clean and rebuild systems during a ransomware attack or other breach without risking reinfection.

An OOB serial console helps minimize disruptions to AI infrastructure. For example, teams can use OOB to remotely control PDU outlets to power cycle a hung server. Or, if a networking device failure brings down the LAN, teams can use a 5G cellular OOB connection to troubleshoot and fix the problem. Out-of-band management reduces the need for costly, time-consuming site visits, which significantly improves the resilience of AI infrastructure.

AI data center challenges

Artificial intelligence workloads, and the data center infrastructure needed to support them, are highly complex. Many IT teams struggle to efficiently provision, maintain, and repair AI data center infrastructure at the scale and speed required, especially when workflows are fragmented across legacy and multi-vendor solutions that may not integrate. The best way to ensure data center teams can keep up with the demands of artificial intelligence is with a unified AI orchestration platform. Such a platform should include:

  • Automation for repetitive provisioning and troubleshooting tasks
  • Unification of all AI-related workflows with a single, vendor-neutral platform
  • Resilience with cellular failover and Gen 3 out-of-band management.

To learn more, read AI Orchestration: Solving Challenges to Improve AI Value

Improving operational efficiency with a vendor-neutral platform

Nodegrid is a Gen 3 out-of-band management solution that provides the perfect unification platform for AI data center orchestration. The vendor-neutral Nodegrid platform can integrate with or directly run third-party software, unifying all your networking, management, automation, security, and recovery workflows. A single, 1RU Nodegrid Serial Console Plus (NSCP) can manage up to 96 data center devices, and even extend automation to legacy and mixed-vendor solutions that wouldn’t otherwise support it. Nodegrid Serial Consoles enable the fast and cost-efficient infrastructure scaling required to support GenAI and other artificial intelligence technologies.

Make Nodegrid your AI data center orchestration platform

Request a demo to learn how Nodegrid can improve the efficiency and resilience of your AI data center infrastructure.
 Contact Us