Providing Out-of-Band Connectivity to Mission-Critical IT Resources

How to Use a Cloud Managed Gateway Router to Optimize OT Automation
cloud managed gateway router

The right cloud managed gateway router simplifies edge network management and unlocks remote access to operational technology (OT). In this blog, we’ll explain what OT automation is, how to manage it with a gateway router, and what to look for in an ideal solution.

What is operational technology (OT)?

Operational technology, or OT, controls equipment interacting with the physical world. The term is used to differentiate these systems and devices from information technology (IT), focused on non-physical data computing.

OT manages the physical equipment used for industrial manufacturing, water and energy utilities, medical procedures, building management, and other physical processes.

Some examples of operational technology include:

  • Programmable logic controller (PLC) – Controls assembly lines, industrial machines, robotic devices, and other manufacturing processes.
  • Supervisory control and data acquisition (SCADA) – A control system for high-level supervision of industrial machines and processes, including PLCs.
  • Building management system (BMS) and Building automation system (BAS) – manage a building’s mechanical and electrical equipment such as lighting and HVAC.

OT facilitates industrial automation, by reducing manual intervention required to control and optimize physical technology. OT automation systems are traditionally isolated from IT networks, running on specialized industrial computers. However, modern OT systems are converging with IT to allow operators to manage them via network-connected PC or even from a cloud platform.

Using a cloud managed gateway router to optimize OT automation

Frequently, OT devices operate outside your main headquarters, in remote facilities such as factories, warehouses, data centers, and branch offices. In the past, that meant you needed operational technology installed at each location, with operators on-site to monitor OT automation computers. However, IT/OT convergence enables you to connect operational technology to edge network gateway routers, facilitating remote control via specialized software or a cloud-based application.

Gateway routers connect remote facilities to WAN or SD-WAN architectures, providing seamless and secure access to enterprise network resources. They also provide administrators with access to monitor and manage edge network routing and security. Some gateway routers also function as serial console routers, which means they can be used to directly manage the devices connected to them—including operational technology. A cloud managed gateway router with serial console capabilities gives administrators the ability to control remote networking and OT systems anywhere.

One of the issues with remote OT automation is that it may consist of several different systems and applications. For example, a managed service provider (MSP) may need to control HVAC, power distribution, security systems, and other infrastructure for many different clients using a variety of OT computers. They may even have some old analog gauges in place which they monitor with a cheap IoT camera.

Each of these disparate OT systems has its own application or cloud portal that operators must learn, configure, and manage, which is inefficient and creates risk of human error. A vendor-neutral cloud managed gateway router can solve this problem by bringing all your OT applications together under one unified platform.

What to look for in a cloud managed gateway router

Not all cloud managed gateway routers are optimized for OT automation. Let’s examine what an ideal solution looks like.

★ Hardware

The gateway router itself should use high quality hardware, and it should integrate with high quality operational technology hardware as well. You should secure the router hardware with features like cryptographic modules and geofencing to prevent tampering if the devices are stolen or intercepted in transit. A vendor neutral gateway router also needs to support various hardware connections such as RS-232, RJ-45, USB, and IPMI so you can ensure compatibility with your various OT systems, including analog and IoT solutions.

★ Operating System

The OS that runs on the cloud managed gateway router should be hardened and frequently patched to prevent hackers from exploiting vulnerabilities. The provider will update an ideal solution, so you don’t have to constantly stay abreast of all new security vulnerabilities or keep on top of the vendor’s patch schedule. A vendor neutral gateway router should run on an open, Linux-based OS to allow easy integrations with OT software.

★ Zero touch provisioning

Zero touch provisioning (ZTP) allows you to automatically deploy device configurations over a network connection. A cloud managed gateway router should have ZTP capabilities both for itself and for other connected devices. This eliminates the need for pre-staging so that you won’t risk a configured device falling into the wrong hands during shipping. It also reduces the need for engineers to travel on-site to install and configure new devices, saving time and money.

★ Connectivity

The gateway router’s primary job is to provide remote systems and users with a reliable connection to the enterprise network, ideally using SD-WAN technology. It should also provide a dedicated out-of-band (OOB) management connection, so administrators have reliable access to control and troubleshoot the remote network. An ideal solution includes high-speed failover via 4G/5G to ensure seamless connectivity for both administrators and end-users.

★ OOB provisioning and management

Provisioning and changing device configurations over the production network is risky. There’s always the chance that a configuration mistake could take the whole network offline. That’s another reason why a cloud managed gateway router should provide an OOB network connection, so you can deploy and modify device configurations without affecting the production network.

★ Orchestration

A cloud managed gateway router should provide orchestration so you can coordinate automated tasks and workflows across all your OT systems. This brings all OT applications together behind one pane of glass, facilitating efficient management and powerful optimization. End-to-end OT automation at the edge is only possible with a truly vendor-neutral gateway router that supports integrations with your choice of OT solutions, automation tools, and scripting languages.

A cloud managed gateway router with these features will empower efficient OT automation at the edge.

Why choose the Nodegrid cloud managed gateway router solution?

The Nodegrid line of cloud managed gateway routers delivers powerful edge network management optimized for operational technology automation. Features like secure zero touch provisioning and gen 3 OOB management support efficient and low-risk operational technology deployments while ensuring constant availability. Nodegrid’s vendor-neutral hardware, operating system, and cloud-based management platform can integrate all your OT solutions for true end-to-end orchestration.

Learn more about edge network orchestration:

→  Simplifying Network Edge Orchestration with a Single Platform
→  Edge Computing Trends to Expect in the Post-Covid World
→  Out-of-Band Is a Lifesaver for Critical Edge Networking. Here’s Why…

Learn more about the Nodegrid cloud managed gateway router.

Call 1-844-4ZPE-SYS or  Contact us online!
Contact Us

How to Implement Zero Trust: Technologies to Shield You From Million-Dollar Losses

Staff on laptop with zero trust security in place.

How to implement zero trust security is a growing focus of organizations across the globe. With cyber attacks frequently hitting some of the largest companies and threatening entire economies, it’s no wonder why comprehensive network security is a top priority among public- and private-sector entities.

In this post, we’ll show you what you need to implement zero trust security, from big-picture items to individual technologies.

But first, here’s a recap of zero trust security and why your business won’t be safe without it.

Why you need Zero Trust Security

Imagine bringing in a new hire to your department. Soon after, you notice suspicious computer slowdowns and applications that don’t respond as usual. You dive into your program files and discover an unknown .exe file, and you dive deeper to discover attackers actively exploiting your resources. You quickly pull your team together to lock down your network, sanitize every computer and connection, and send out a company-wide instruction to have every employee reset their password.

It turns out, your newest employee unknowingly clicked a bad link and opened the door for a trojan horse attack. But because of your quick response, no significant damage was done and you can rest easy again.

Months later, you come in for your normal workday only to find all your systems locked and unresponsive. Dave, a senior engineer, retired on the day of the attack and never reset his password. The hackers stole his credentials and have gone unnoticed for months. Now your company and its customers are compromised, and the consumer markets you serve are in a frenzy due to a shortage of goods. You can’t help but feel somewhat responsible for the entire ordeal.

This example mimics recent real-world cyberattacks and highlights the importance of moving away from traditional security approaches.

Traditional architecture uses the castle-and-moat security approach. Once a user gains access (crosses the moat), they become trusted to use your organization’s resources (the castle). Aside from the occasional password reset or other authentication protocol, this approach leaves plenty of opportunities for outsider and insider attacks. Zero trust security, however, places a moat around every node and user. This means that no matter how often a system or user needs to access a resource, they always have to verify their identity and intent.

In other words: never trust, always verify. In our example above, implementing simple two-factor authentication could have alerted Dave to his stolen credentials, which would have prevented the attack.

The need for zero trust is due to the explosion of distributed networking. Communications used to be straightforward and centralized: a trusted user using a trusted device would connect from a trusted office location to the data center. Apps and data were securely transmitted between parties, and sealing out attackers could be as simple as deploying a new point solution or product. But user expectations changed all this; now, they need to connect from anywhere using a variety of devices, which means the modern network includes SaaS, cloud, and third-party platforms. This hybrid infrastructure means there are now more nodes and lines of communication than ever — and each is vulnerable to attack.

If the recent attacks on SolarWinds, Microsoft Exchange, and Colonial Pipeline aren’t convincing enough, consider the latest hack involving Kaseya, an American company that specializes in IT and network management software. By exploiting the virtual systems/server administrator (VSA), attackers were able to compromise up to 1,500 of Kaseya’s customers, shutting down educational services, law firms, and an outpatient surgical center in South Carolina.

Pervasive attacks like these have prompted political action, with the President signing a cybersecurity executive order this past May. Read our breakdown of the legislation and how it aims to improve cybersecurity across public and private sectors.

Now that you know why you need better security, how do you implement zero trust?

How to implement Zero Trust: The big picture

Zero trust is merely a concept, however implementing Zero Trust Network Access (ZTNA) means putting this concept to work. Implementing ZTNA involves two parts:

  • The processes, which we covered in a previous post, and
  • The technologies, which we’ll talk about in this post

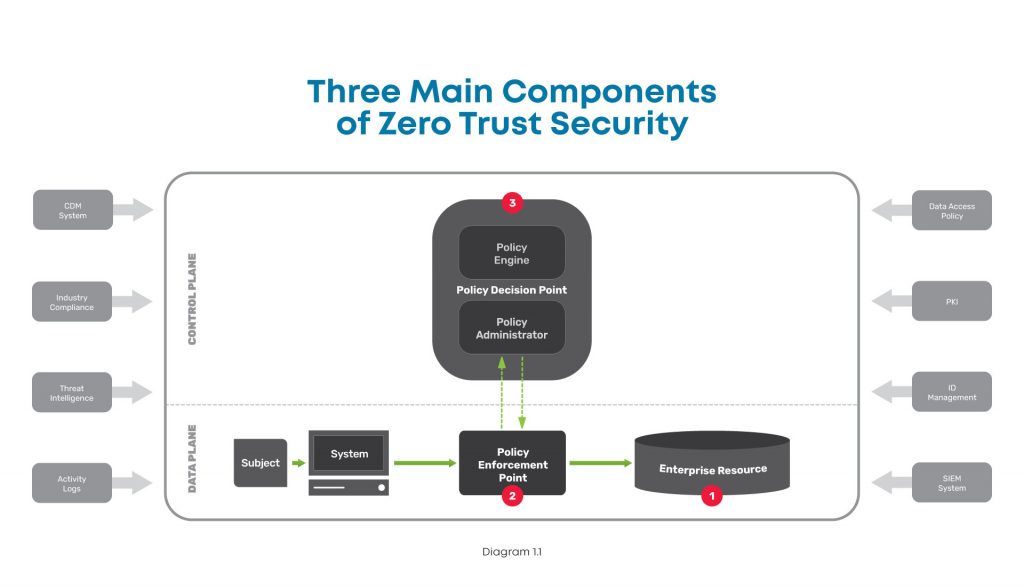
At a high level, this diagram shows the components you need when considering how to implement zero trust.

A high level diagram of the three main components of zero trust security, including the enterprise resource, policy enforcement point, and policy decision point.

There are three major components to look at in the big picture of zero trust security:

  1. Enterprise resource — This includes all the IT stuff you need to protect and that your business relies on, like hardware, software, and network equipment. In simple terms, this is like the gold that you keep carefully guarded in the center of your castle.
  2. Policy enforcement point — This is the datapath element that enables, monitors, and terminates connections between users / devices / applications and enterprise resources. Simply put, this is like the guard that accompanies those wishing to access your gold.
  3. Policy decision point — This is the layer that decides who / what is safe and grants / revokes access accordingly. In other words, this is the gatekeeper who determines who is allowed into your castle.

To better understand these, here’s a closer look at each:

Enterprise resource

This component is pretty straightforward, and consists of elements you need to operate and manage IT environments. These elements can include hardware like computers and data storage devices; software such as web servers, content management systems, and operating systems; and network equipment like servers, routers, firewalls, and out-of-band devices.


Policy enforcement point

This component consists of the datapath elements that enable, monitor, and terminate connections between subjects (users / devices / applications) and your enterprise resources. Though this is represented as one component, it is comprised of two parts that are both typically used in deployments. These parts are:

  • A client-side agent, usually deployed on a laptop or server.
  • A resource-side gateway, which controls access in cases where a client-side agent is not used. Examples where gateways are used include regulated healthcare equipment, ATM machines, and operational technology equipment.


Policy decision point

This component is the management and orchestration layer. This layer essentially checks identities to verify who is safe, and assigns policies to determine who gets access and to what. This is also represented as one component but is comprised of two parts:

  • Policy engine — This is the engine that decides whether a machine or web traffic is safe. To accomplish this, the engine uses a variety of data sources when making its determination, such as PKIs and identity management providers, CDM systems, and activity logs.
  • Policy administrator — This administrator uses the policy engine’s determination to grant or revoke access to a machine or web traffic.

There are many tools available to help you monitor and visualize traffic, so you can create policies and configure your policy decision point to meet your zero trust outcomes.

In order to create your zero trust configuration, you need to deploy several essential technologies.

How to implement Zero Trust: Essential technologies

Zero trust is a complete re-imagining of network security and can be a daunting task. But when you add its fundamental technologies to your toolkit, you can effectively build the three components described above and achieve Zero Trust Network Access (ZTNA). Here are the essential technologies you need to accomplish this.


Identity and access management

Such a big part of zero trust security relies on verifying that a device or user really is who they say they are. For this, you need an identity management solution from a trusted provider and public key infrastructure (PKI). This allows you to essentially create and issue a digital fingerprint for every user, and includes information such as their username, role, and other unique data. Multi-factor authentication is a critical component of identity verification, which requires users to present two or more pieces of identification/verification before granting access.

Additionally, access management is an important piece that determines a user’s authorization level, or in other words, which resources they can access. Identity and access management both feed information into your zero trust model’s policy engine.


Policy management

Another essential technology to have is a policy management solution. This is integrated into your security stack and serves as a single policy creation point. This allows you to define access and authentication policies for your entire organization.

You can specify data access rules for users, devices, and roles, which is vital to achieving micro-segmentation, limiting lateral movement, and enforcing least-privilege access. All of these feed into your policy engine and are used by your policy enforcement point to validate whether a session is allowed to continue.


Zero trust equipment and applications

Tying everything together requires equipment and applications that are able to enforce your policies. These are physical or virtual solutions that sit in front of servers and serve as your enforcement points. For example, this could be your next-gen firewall (NGFW) that initiates the multi-factor authentication protocol, verifies a user’s identity, and uses your defined policies to restrict the user’s access to a specific segment of your network.

Where can you get these essential Zero Trust technologies?

When considering how to implement zero trust, keep in mind that there are many vendors who can provide you with the essential technologies.

  • Obtaining an identity and access management solution is the easiest task when implementing zero trust. Many organizations offer an identity store, such as Azure Active Directory or Google Cloud Identity. You can also use companies dedicated to identity management, such as Duo, Okta, or Ping Identity. Keep in mind that if you need to control third-party access, such as for customers or equipment management contractors, you’ll need a solution that can access multiple identity stores simultaneously.
  • Obtaining a policy management solution requires careful consideration and should be part of your overall security stack. Look for a solution that allows you to create policies and set up datapath enforcement points. An adequate framework enables you to create authentication and post-authentication access rules, with an enforcement point that segments your network and continuously authenticates sessions. This security stack can be an on-prem NGFW, or delivered via the cloud using a Secure Access Service Edge (SASE) model, both of which are available from trusted providers like Palo Alto Networks.
  • Regardless of whether you use an on-prem or SASE model, you need an edge infrastructure platform to sit in front of servers and host the enforcement point. For on-prem, this platform must be able to host an NGFW to secure network segments and VLANs. For SASE, this platform must be able to create VPN tunnels to your SASE platform, which can be used for inline inspection and policy enforcement. Either approach requires powerful computing capabilities and a flexible operating system to accommodate workloads for detecting, analyzing, and automatically responding to threats, which few vendors offer.

Here are examples of what proper zero trust implementations look like, with ZPE Systems’ Nodegrid as the edge infrastructure platform:

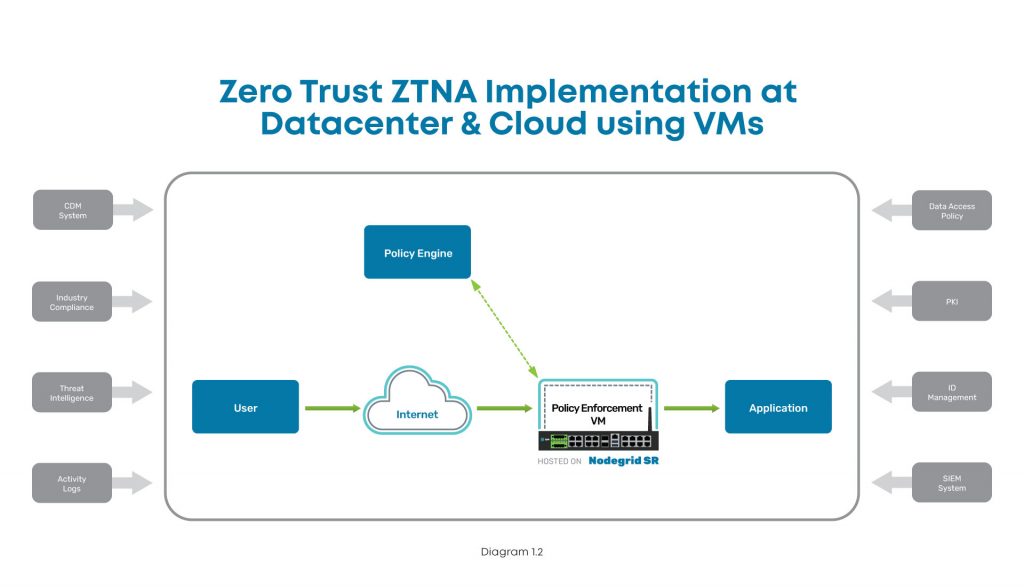
Implementation diagram showing how to implement ZTNA at the data center using Nodegrid.

In this diagram, you can see where ZTNA and Nodegrid fit into the scheme at the data center. The user connects via Internet, and the Nodegrid SR device serves as the Policy Enforcement Point hosting a VM. This VM communicates with the Policy Engine to authenticate the user, and then grants access to the data center application.

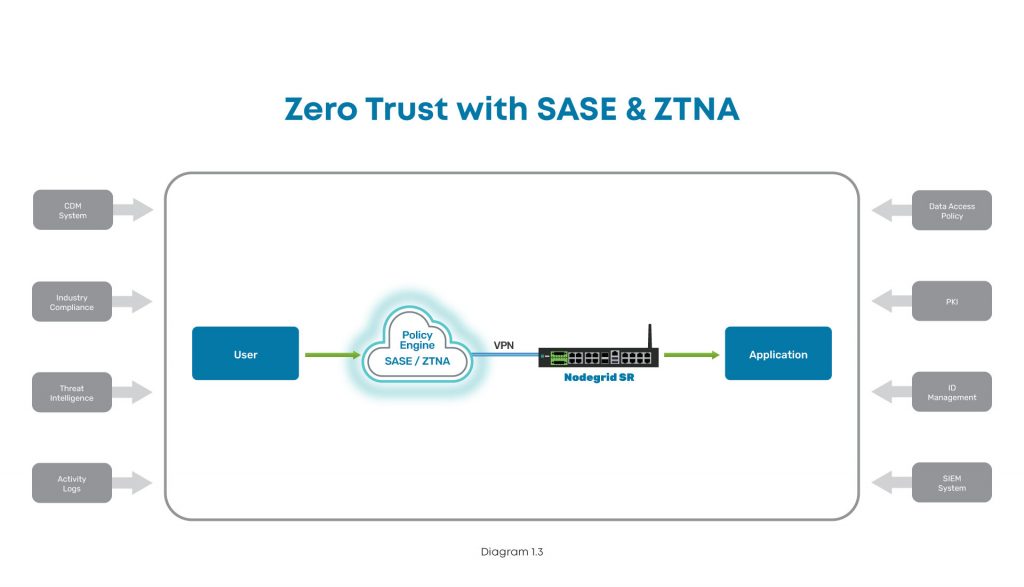
Implementation diagram showing how to implement ZTNA at a branch, edge, or other distributed location.

In this diagram, the user tries to connect to an application at a branch, edge, or other distributed location. The user connects via Internet, where SASE and ZTNA provide secure connectivity. The Nodegrid SR device connects via VPN to the Policy Engine for authentication, and then grants access to the branch application.

How to implement Zero Trust: A recap

To protect your organization, implementing zero trust requires you to build out the main components. With the policy decision point and policy enforcement point in place, you can secure your enterprise resources from outsider and insider attacks. Ensuring these components work like a well-oiled machine means you need the proper identity and access management tools, a complete policy management solution built into your security stack, and equipment and applications that can enforce your zero trust security policies.

Because user expectations have caused infrastructure to become incredibly distributed and complex, the attack surface has increased dramatically. The traditional castle-and-moat approach to security is no longer adequate, and recent newsworthy cyberattacks showcase the network vulnerabilities that even the largest companies still struggle to address. The President’s latest cybersecurity executive order is a step in the right direction to bolster infrastructure protection for public and private sector entities, and you can use this blog as a starting point to begin your zero trust journey.

Don’t get caught without these 5 security must-haves

Watch our webinar, Cyberattacks: 5 Security Must-Haves for Hybrid Infrastructure Gateways, and learn how to lay a solid foundation that makes implementing zero trust easier. Our experts will talk you through how to:

  • Keep edge networks and users fully protected
  • Make smart buying decisions
  • Get complete security and control for years of serviceability

Watch now to protect your business from growing cybercrime.

SASE vs Security Service Edge: What’s the difference?

Employee tapping into cloud services such as security service edge

Security Service Edge. Is it just another fancy networking term? After all, we’ve already got SASE (Secure Access Service Edge), so why throw another buzzword into the mix?

The truth is, there’s a big difference between Security Service Edge (SSE) and SASE. SSE is a foundational element of SASE, but there’s another necessary component you need to be aware of. In this article, we’ll break down the differences between these two acronyms so you can understand how to achieve better security for your distributed users and devices.

But first, let’s quickly recap why networking and security have become decentralized.

Security Service Edge: An evolving need

The modern workforce is increasingly distributed. In fact, Gartner research shows that demand for remote work will increase 30% by 2030, as Gen Z fully enters the workforce. Another factor is the ongoing coronavirus pandemic, which has forced companies worldwide to accommodate off-site staff.

But the need for distributed networking goes back much earlier than the previous 18 months.

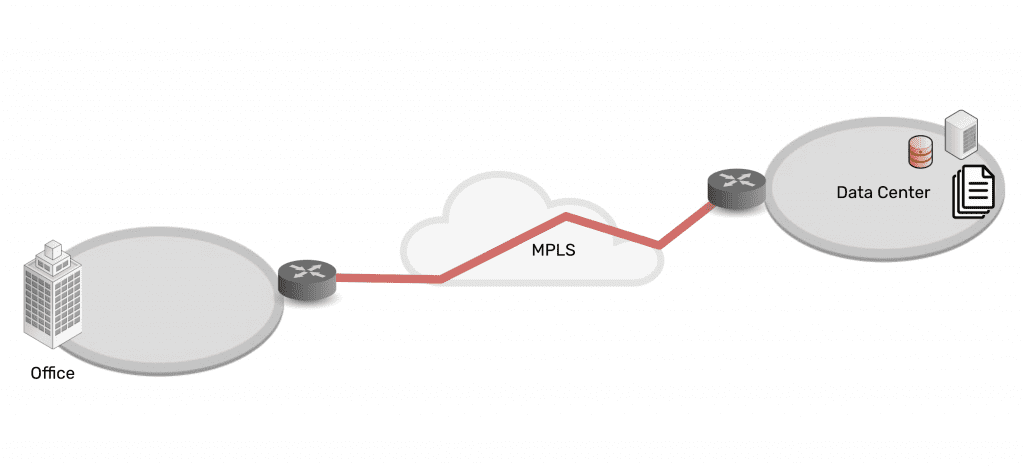
Connectivity and network architectures used to be simple. In the 1990s and 2000s, companies centralized data in the data center, connected branch offices to the data center, and set up simple security measures in between. Most staff worked from the office, which made it easy to provide secure access to and from these enterprise locations and resources.

Network architecture showing simplicity of data center connected via MPLS to branch office

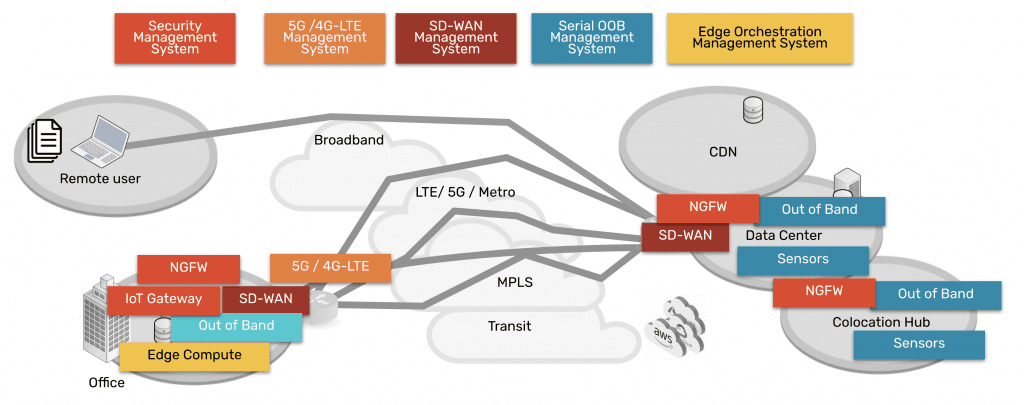
As technologies advanced, companies and their employees discovered that it was becoming easier to work outside of the office. Cloud, SaaS, and edge offerings emerged to create a hybrid infrastructure, as everything moved from being centralized to highly distributed. Now data, security, networking, and computing are everywhere and comprise a complex web of services — owned by enterprises themselves as well as third parties. Securing it all has been an impossible feat for more than a decade.

Network architecture showing complexity of data center, CDN, remote user, branch office, all connected via many paths

Fortunately, Security Service Edge and SASE are models that can address this challenge.

SASE vs Security Service Edge (SSE)

Security Service Edge is a main component of SASE. In the simplest terms, SASE is the architecture that organizations strive to build. It involves delivering networking and security via the cloud, directly to the end user, device, office, etc. instead of having to backhaul through the company’s data center. Aside from SSE, the other main component of SASE is the access portion, which allows the edge services to be deployed and managed. This access portion includes the physical hardware required to connect ‘network’ the edges and services.

Therefore, SASE breaks down into two main components:

  • Security Service Edge, and
  • Access

Keep reading for a detailed explanation of each and why they have been separated out into two pieces now.

Security Service Edge

Security Service Edge (SSE) is the security component of SASE. As Gartner states, SSE ensures secure access to the web, cloud services, and applications. SSE is delivered via the cloud and offers several capabilities, including threat protection, security monitoring, and data security.

Security Service Edge capabilities are available from companies who provide NGFWs (next generation firewalls), SWGs (secure web gateways), and CASBs (cloud access security brokers).

  • NGFWs: Next generation firewalls are implemented to not only secure networking components and services, but also to protect against modern threats that exploit weaknesses in applications.  This type of service secures all the traffic even traffic that’s UDP and also non web based applications including malware exploits.
  • SWGs: Secure web gateways are self explanatory. They are placed between the user and the web, serving as a gateway that provides secure access to the web. Basic functions of SWGs include blocking access to certain websites, preventing unauthorized transfers of data, and inspecting for malicious content.  As its name implies this type of service is limited to web traffic and is used in specific use cases.
  • CASBs: Cloud access security brokers are software that sit between cloud users and cloud applications, to monitor activity and enforce security policies. This software keeps a close eye on data as it moves between cloud environments, SaaS, and users, and enforces security policies to block malware, protect sensitive data, and maintain compliance.  This type of service also has a specific use case of only examining specific cloud applications as its name suggests.

Access for Security Service Edge

In order to use the capabilities of Security Service Edge, you need the physical hardware to deploy services at your locations. This hardware is the access component, and includes SD-WAN capabilities. When deployed, it connects your location to a variety of services (NGFWs, SWGs, CASBs mentioned above) in order to make those services available to your location.

SASE = Security Service Edge + Access

A simple way to think about the SASE concept and its components is to imagine a skyscraper.

Imagine SSE capabilities live in the clouds, and you’d like to bring them down to your enterprise. You’ve got the blueprints to build a skyscraper (SASE) that can connect you to these cloud-based capabilities. But before you can do any of that, you need a sturdy foundation (the access portion) on which to build it all. In other words, your investment in cloud services needs a solid access onramp to those services.

With the right access component, your employees can shuffle in and out of your skyscraper, and easily perform their job functions using SSE capabilities in the cloud. And if you deploy a more robust access solution such as ZPE Systems’ Nodegrid, you’ll be able to maintain your SASE architecture no matter how the clouds change.

How to implement SASE: Focus on Access

When you’re considering implementing SASE architecture, you might be inclined to go to a SASE company to buy everything. But Gartner states that companies that offer the two segments have more mature offerings. 

Therefore, you should focus on purchasing the right solution for the access portion, since it serves as the foundation of your infrastructure at the edge, and then marry this to the right SSE solution for your company. This separation of vendors gives you flexibility to manage several IT systems, and eliminates vendor tie in.

Nodegrid puts the Access in SASE

The Nodegrid SR family of edge routers serves as the access portion in your SASE architecture. A single Nodegrid SR device is a powerful, cost-effective solution to connecting sites to Security Service Edge providers.

The onboard Intel CPU and Linux-based Nodegrid OS offer speed and flexibility. Orchestrate freely across vendors to activate service licenses, spin up VMs, and get your SSE solutions up and running automatically. Additional RAM and storage also help you deploy edge computing for data thinning, de-duplication, monitoring, and other edge workloads.

On top of this, Nodegrid gives you out-of-band management capabilities so you can remotely manage your SASE architecture from anywhere. If you need to optimize bandwidth, investigate data logs for security, or simply power cycle an edge device, you don’t have to get out of your pajamas. Nodegrid gives you secure access to everything via your web browser.

To summarize, the reason SSE has been separated from SASE is that many SD-WAN vendors began to confuse the market by advertising that they offered SASE. This prompted Gartner to point out that there are security-savvy companies that give you more mature security solutions, and to consider such solutions from vendors like zScaler, Netskope, and Acreto, for example. Regarding the Access component, vendors like ZPE Systems provide more capable and robust solutions for connectivity to cloud services, when compared to SD-WAN companies that claim to offer SASE.

Don’t miss out on valuable SSE content. Make sure to sign up for our newsletter using the form below.

If you have questions or would like to speak with an expert, feel free to contact us.


Improving Network Design for a Major Online Retailer

Out-of-band management is a critical component of network design. Instead of using one of your main networks for administrative tasks, out-of-band (OOB) gives you admin access via a completely separate path. In this blog, you’ll learn about how one of the world’s largest online retailers implemented OOB, and how Nodegrid brought a few major surprises to the table.

Why consider out-of-band in network design?

How you approach network design depends on your industry, business goals, customers, and many other factors. However, enterprises across the spectrum implement out-of-band because it’s crucial to keeping networks running.

Out-of-band (OOB) gives you an isolated access path to your network’s assets. When it’s time to make routine updates, implement configuration changes, or address network threats, OOB is your secure line for administration. You don’t have to put your main network at risk or interrupt service. And with modern OOB solutions like Nodegrid, you can give support staff convenient remote access. No more rolling a truck for issues like resetting a password or updating firmware — you can do it all even from half a world away.

Here’s a recap video explaining Out-of-Band Management:

Along with OOB, you should also think about automation and consolidation when considering network design. Together, these three solutions bring you significant benefits like time and cost savings:

  • Out-of-band gives you remote access to your infrastructure. Think about no longer having to roll a truck every time a device needs to be rebooted, a patch installed, or a configuration rolled back. This can save you tremendously on support costs, boost response times, and help you maintain network & business continuity.
  • Network automation lets you automate critical tasks. When it comes to deploying new locations, you can take advantage of zero touch provisioning and get a network that builds itself. This helps you allocate resources more efficiently (i.e. let staff provision remotely instead of having to coordinate expensive travel plans & on-site work). You can also automate ongoing tasks and even non-routine work, saving you even more time & money on support.
  • Consolidation using all-in-one devices helps you save on CAPEX, rack space, and energy. Instead of having to deploy several devices to deliver failover, Wi-FI access, switching, routing, etc., you can use consolidated appliances. This can significantly reduce your stack, deployment costs, and support expenses.

How does Nodegrid improve network design?

ZPE Systems’ Nodegrid is pioneering network design capabilities that weren’t available until just a few years ago. And as you’ll see with this case study, we’re reinventing networking with possibilities that network engineers only dreamed of until recently.

Nodegrid’s advanced out-of-band gives you remote access without slow modems and phone lines. It takes advantage of fast broadband over WAN, and is even supported by cellular failover paths. So even if all your other network connections suffer an outage, Nodegrid’s out-of-band gives you continuous access to your infrastructure.

Nodegrid also supports custom automation via the most popular automation tools. Not only can you use zero touch provisioning and make configuration management a breeze, but you can also deploy your own in-house applications for seamless integration.

On top of all this, Nodegrid features all-in-one devices that let you wield the power of consolidation. In fact, you can replace up to six devices using the Nodegrid Services Router, which is a powerful appliance for converged infrastructure and features capabilities like switching, routing, cellular failover, and more.

But don’t just take our word for it.

Here’s how Nodegrid improved a major retailer’s network design

When a Fortune 500 business needed out-of-band at its distribution centers, they were faced with drawbacks. Traditional thinking meant they would install a network switch and an out-of-band device at each MDF. But Nodegrid came along and completely reimagined their network design.

Instead of wasting rack space, energy, and CAPEX & OPEX by implementing a traditional solution, the Nodegrid Services Router was deployed and helped save across the board. Without expanding their stack, the e-commerce giant got an all-in-one device with serial and networking capabilities that allowed them to gain full control of MDFs and IDF closets.

Out-of-band and consolidation were vital components of the implementation. But a major key would be seamless integration with the company’s automation-heavy environment. Nodegrid’s open, automation-friendly platform fit right into their network, and they deployed their proprietary kick-off application with ease.

Want to get the full story? You’ll get the details about how Nodegrid streamlined network design to deliver savings, convenient management, and customer satisfaction.

Download the case study now!

Retail Cost Savings Using Network Consolidation

When it comes to infrastructure, network consolidation is becoming a must-have. This is especially true in hyper converged architectures, where streamlining operations means the difference between profitability and major losses. Combining systems and reducing the number of disparate solutions helps you achieve an efficient network that supports your business goals — whether it means speeding up the customer experience, decreasing points of failure, saving on support costs, or anything in between.

With legacy infrastructure configurations, you’re forced to deploy purpose-built appliances that add complexity. This complexity is reflected not only by your physical topology, but also by your management practices, system integrations, and end-user experiences. No matter what industry you’re in, you can unwind your tangled enterprise network and reap many benefits using a consolidated solution.

In this entry, you’ll explore network consolidation and why a global retailer could no longer do business without the advantages it offers.

Network consolidation means simpler networking

Network consolidation is a straightforward concept that you can implement on several levels.

If you draw a layout of your hardware configurations, your legacy setups most likely resemble intricate webs. Network traffic must travel along many paths and stop at each hardware node for processing. Heavy user loads can easily bog down your system, especially because your legacy devices don’t come with processors built for performance.

But when you consolidate, you can implement multi-function devices and replace many disparate appliances. Instead of having a complicated stack comprised of switches, routers, firewall boxes, modems, and other devices, you can get a powerful solution that combines all these into one.

Consolidating can also involve taking advantage of virtualization to simplify your infrastructure. You can deploy applications, run VMs or Docker containers, use automation tools, and more. You can cut complexity and further reduce your hardware stack by virtualizing your environments.

For management purposes, you can also consolidate your efforts using software that unifies your different solutions. This involves deploying tools to centralize your control, so you don’t have to juggle unique management UIs and vendor-specific software.

Retail Diagram O

Network consolidation comes with many benefits

When you adopt all-in-one hardware, your deployments become simple, fast, and cost effective. You save on capital expenses and shipping costs, and you don’t have to configure and provision an array of separate devices. If you also use zero touch provisioning, deployments become plug ’n play simple. You only need someone to physically install and boot your boxes, and your sites automatically come online in minutes. On top of this, your user experiences become smoother because your network is streamlined with appliances that are more powerful.

Virtualization also speeds up the customer experience thanks to more efficient integrations and service chaining. You can closely integrate solutions to boost efficiency, without being held back and forced to make changes at the hardware level. You can provide an experience that’s responsive, even during increased traffic flows and heavy workloads.

If you consolidate management with a unified software tool, your IT teams can do away with cumbersome administration protocols and practices. They no longer need to be dispatched to perform on-site maintenance or perform lengthy troubleshooting to find problems. A centralized management suite helps pinpoint issues and offers remote control for instant response times. Use it in conjunction with all-in-one hardware, and you don’t need to waste time connecting to check on non-problematic devices. You know exactly where to focus your efforts, while your software tool gives you unified control of all your integrated solutions — from SD-WAN, to routing, switching, security, and more.

How does a large retailer benefit from network consolidation?

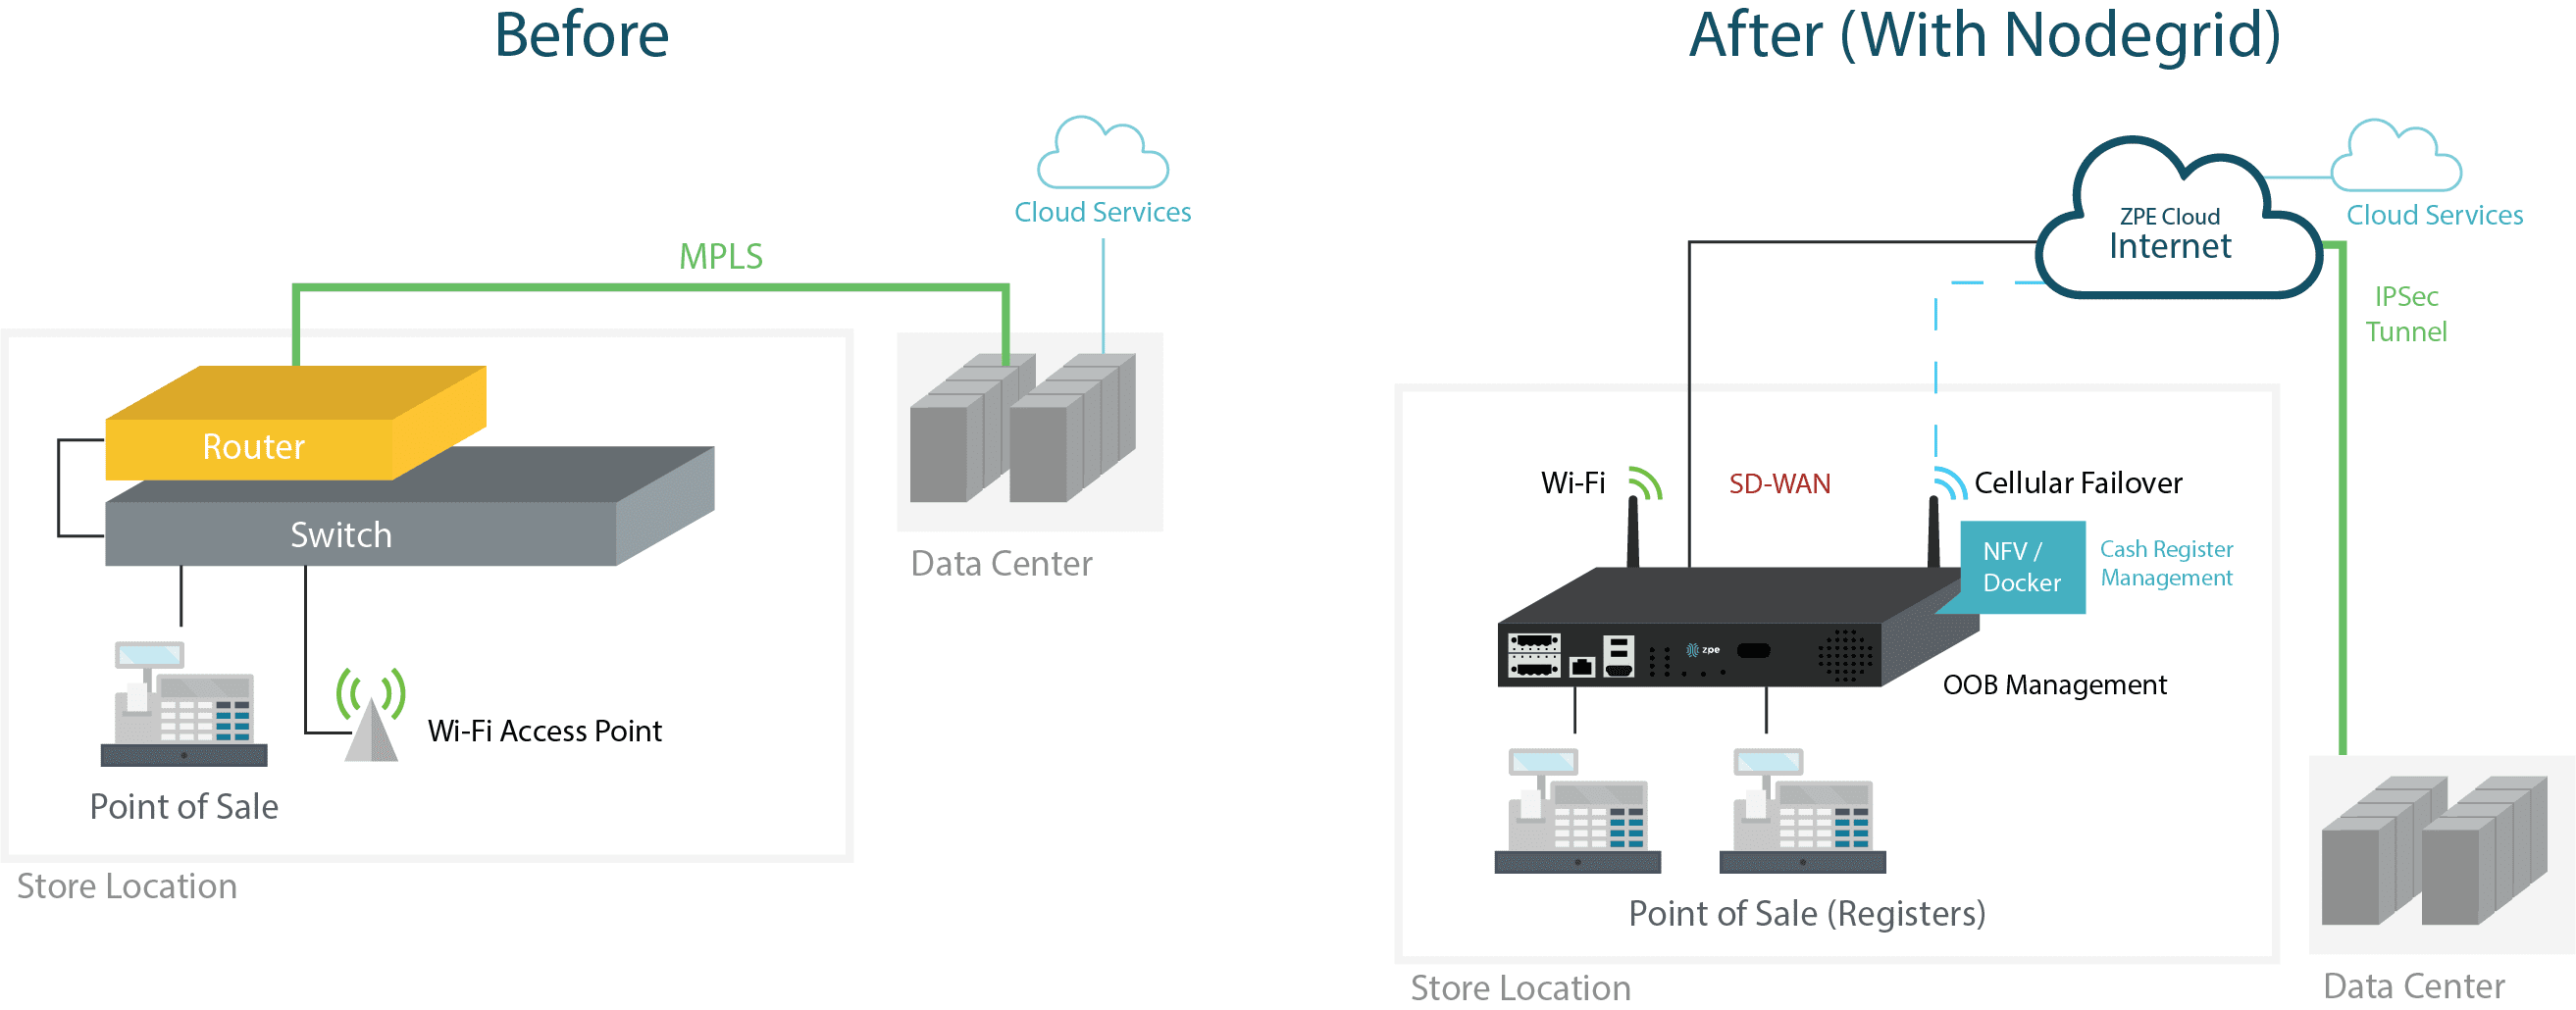
When a global retailer’s costs began to skyrocket, their network was to blame. They knew that in order to maintain profitability, they needed to move away from their legacy infrastructure configuration. This consisted of MPLS lines at each branch location, with separate devices for switching, routing, and security.

Their customer experience was unresponsive, and came with long transaction times and even longer checkout lines. Disruptions exacerbated everyday operations, forcing technicians to be dispatched to set up LTE modems while MPLS connections were restored.

Their network was costing too much money to maintain, and their poor customer experience led to too much lost revenue.

But a single Nodegrid solution allowed them to achieve network consolidation and leave behind all of these problems. They streamlined their hardware stack at each location, and allowed IT teams to support their networks with extreme efficiency.

Virtual Customer Premises Equipment with Palo Alto Networks and Nodegrid

Virtual Customer Premises Equipment

Virtual Customer Premises Equipment, or vCPE, is the epitome of network function virtualization. Enterprises are implementing this form of customer premises equipment because it brings many benefits, such as faster deployments, optimized resource allocation, and unlimited flexibility. Service providers are especially keen to using vCPE to simplify service delivery and dramatically improve customer experiences.

Regardless of what industry you’re in, you can use this virtualization approach to streamline your enterprise networking.

What is Virtual Customer Premises Equipment?

Virtual customer premises equipment makes use of virtualization to deliver network services. This approach essentially uses a virtual environment that consists of software-based functions. These functions can include routing, security/firewalls, VPNs, and much more.

How is Virtual Customer Premises Equipment different?

Networking typically involves deploying stacks of purpose-built devices at each location. These appliances must be configured, provisioned, and maintained by specialized staff, who are usually required to be on site to perform these tasks. This can become expensive — not just to purchase devices (and perpetually replace them every few years), but also to provide support and maintenance. And because branch offices usually have limited physical space, large stacks of equipment can be obtrusive and take up significant real estate.

vCPE vaporizes these large stacks, and instead puts the different network functions into a cloud-based model. These functions are hosted at a separate site or data center. Instead of using many dedicated appliances, branch locations need only one or two devices to run software that can deliver these functions to the site.

Why use Virtual Customer Premises Equipment?

Virtual customer premises equipment helps you gain more business agility. If you look at it from a hardware consolidation standpoint alone, it’s plain to see how much more easily you can deploy and manage your distributed networks.

  • Deploy faster & save money — Fewer pieces of hardware means you no longer need to haul many devices to each location. Once you have your virtualized functions set up at your service delivery site/data center, you can bring branch sites online using a single box. If you also use automation via zero touch provisioning, all you have to do is install & boot each device and watch your network build itself. You can deploy in minutes, while saving on device, shipping, and support costs.
  • Use exactly what you need — Purpose-built hardware can be difficult to optimize — usually, they are over-utilized and cause problems, or under-utilized and lead to wasted resources. Because vCPE allows you to set up a custom & dynamic environment, you can easily optimize resource allocation to eliminate problems and waste, so your network uses exactly what it needs.
  • Get endless flexibility — Software-based solutions are much simpler to deploy, manage, and replace than physical hardware. This gives you the ability to remain flexible as requirements change, especially if you choose a vendor-neutral vCPE platform. Imagine how simple it is to spin up a VM and run a new application, as opposed to purchasing, deploying, and provisioning a new dedicated device to go in each location.

You can get an all-in-one vCPE solution

ZPE Systems and Palo Alto Networks have partnered to bring you an all-in-one joint solution.

Using the Nodegrid Services Router (NSR), you can directly host Palo Alto’s VM-Series next-gen virtual firewalls. These powerful tools allow you to secure all traffic, including out-of-band paths, using a single solution. This makes it easy to deploy sites without hassle and get peace of mind knowing your networks are completely protected.

Here’s a brief video showing how easy it is to deploy your vCPE solution:

On top of this, the NSR allows you to host virtualized network functions (VNFs) from other vendors of your choice. The NSR is also an x86 Intel-powered device that features modular add-ons for compute and storage capabilities. You can deploy powerful vCPE implementations at branch sites, using a single box for routing, switching, computing, security, and other critical functions.

Click the link to read the full joint solutions brief, and contact us to set up a demo.