Providing Out-of-Band Connectivity to Mission-Critical IT Resources

SSE Magic Quadrant: Key Takeaways of the 2023 Report
The SSE Magic Quadrant describes top cloud security service vendors, conceptualized as a cloud with glowing network nodes and a padlock.

Gartner’s SSE Magic Quadrant for 2023 identifies 10 key vendors currently providing secure service edge capabilities for the enterprise market. In this guide, we’ll summarize the common factors shared among leading SSE vendors, discuss what separates them from niche players, and share advice for connecting your edge network to SSE solutions via an SD-WAN on-ramp.

Table of Contents:
  1. What is Security Service Edge (SSE)?
  2. What is the need for SSE?
  3. What is the SSE Magic Quadrant?
  4. What has changed since the 2022 SSE Magic Quadrant?
  5. Key takeaways from the 2023 SSE Magic Quadrant
  6. SD-WAN: An on-ramp for SSE
  7. What to look for in an ideal SSE on-ramp
  8. Why Nodegrid is the ideal SSE on-ramp

What is Security Service Edge (SSE)?

Security service edge (SSE) is a cloud-centric security methodology for protecting edge network traffic. It rolls up technologies like Firewall-as-a-Service (FWaaS), Zero Trust Network Access (ZTNA), and Cloud Access Security Brokers (CASB) into a single service. These technologies offer threat protection, security monitoring, access control, and data governance.

What is the need for SSE?

With the frequency and severity of ransomware attacks and other cybercrimes increasing daily, security is a major priority for any organization. To protect your enterprise from cyber threats, you need to be able to extend your security policies and controls to all the remote and geographically distributed systems at your network edge. Historically, that meant backhauling all remote traffic through your primary firewall, which would inevitably cause performance issues for everyone on the network. This is frustrating and can greatly impact the business when much of your remote traffic is destined for cloud and web resources that aren’t even on your enterprise network.

SSE solves this problem by taking advanced enterprise security technologies and making them available as a cloud-based service. You can use SD-WAN with intelligent routing (more on that later) to send remote and branch office traffic through your SSE stack. This allows you to apply consistent policies and controls to your enterprise and edge traffic while reducing bottlenecks and increasing overall network performance.
.

Learn more about SSE:

Gartner’s 2023 SSE Magic Quadrant Summarized

Challengers

Leaders

Cisco (SIG)

Netskope
Zscaler
Palo Alto Networks (Prisma Access)

Niche Players

Visionaries

Broadcom
iboss
Cloudflare

Skyhigh Security
Forcepoint (Bitglass)
Lookout

There are many reasons why an SSE vendor would be considered a niche player, including that the market hasn’t caught on to them yet due to poor marketing or sales strategies. However, one common caution among niche players is a failure to fully integrate SSE components, which means customers must use multiple dashboards to manage a single SSE solution. Another common issue is poor support during sales, implementation, and operation, leading to frustration among enterprises with less experience in edge networking and security.

On the other hand, the leaders of the SSE Magic Quadrant share a few common characteristics as well. For one, they have strong marketing and sales outreach, a clear vision, and a roadmap for the future. This vision is essential because it allows enterprises to ensure their goals and strategies align with where their SSE vendor is headed.

In addition, these solutions’ components are tightly integrated with a single, unified management platform for more accessible and efficient operation. Magic Quadrant leaders invest in and implement new security features frequently, bug-free, and with adequate documentation and support. That means customers can stay ahead of emerging security threats without worrying about breaking their existing setups.

What has changed since the 2022 SSE Magic Quadrant?

There are three major changes to Magic Quadrant this year.

  • Palo Alto Networks moves from Challenger to Leader: In 2022, Palo Alto extended its Prisma Access SSE solution to better integrate with Prisma SD-WAN, enhance its proxy and ZTNA components, and add SaaS Security Posture Management (SSPM).
  • McAfee splits its cloud business into Skyhigh Security: Early in 2022, McAfee enterprise split into two, with its cloud business now known as Skyhigh Security. This split disrupted Skyhigh’s growth and market share and moved this SSE offering from the Leaders quadrant to the Visionaries quadrant.
  • Versa leaves the SSE Magic Quadrant: Versa no longer ranks in the top 20 organizations in Gartner’s market momentum index (MMI), so it isn’t included in the 2023 Magic Quadrant.

Key takeaways from the 2023 SSE Magic Quadrant

  • Most vendors prioritized improving their core capabilities and better integrating their product, rather than focusing on new features and other innovations.
  • Vendors who fail to fully integrate their SSE offering into a unified platform are quickly losing market share.
  • WFH traffic is less of a concern for enterprises than branch/edge sites, so SD-WAN access and integrations are critical.

Overall, the biggest takeaway from the SSE Magic Quadrant is the importance of a seamlessly-integrated platform. A consolidated platform ensures complete visibility and control over your security service edge solution without needing to learn and operate multiple consoles.

On top of this, to use SSE’s cloud-delivered solution, you need a reliable way to send traffic from your branch and edge locations to the SSE stack. That means part of the architecture needs to include an access solution that can tunnel traffic from these locations to the cloud, such as SD-WAN. The access solution serves as an on-ramp to SSE, and requires a physical appliance for on-premises installations. This framework combining SD-WAN access with SSE is how SASE (secure access service edge) is built.

SD-WAN: An on-ramp to SSE

Security service edge provides the technology to protect your edge-based cloud-destined traffic, but you still need a way to get that traffic to your SSE platform. This is known as an SSE on-ramp, and it’s not included in any of the SSE Magic Quadrant solutions. However, one of Gartner’s selection criteria was the ability to integrate with SD-WAN technology.

An SSE on-ramp uses SD-WAN (software-defined wide area network) technology to route remote and branch office traffic to your SSE stack in the cloud. SD-WAN separates the control and management processes from your underlying WAN hardware and virtualizes them as software, making it possible to centrally control and orchestrate even very complex and distributed WANs. With SD-WAN, you can use intelligent and application-aware routing to connect your edge users directly to the SSE platform, cloud, and web resources.

What to look for in an ideal SSE on-ramp

The ideal on-ramp to SSE will support seamless integration with your SSE platform, and vice-versa. In addition, the right solution will provide additional capabilities like the ones listed below.

Features of an ideal SSE on-ramp include:

Versatile tunneling

Physical hardware that’s easy to provision with a versatile tunnel mechanism to SSE, including IPsec and WireGuard, with simple cloud management. Ideally this tunneling mechanism uses application-aware traffic steering to make it an effective part of an SD-WAN on-ramp.

Integrated L3/L4 firewall

Integrated Layer 3/Layer 4 firewall technology to secure incoming traffic to your remote and branch locations, including VPN support. The ideal on-ramp has local segmentation capabilities and zero-trust, since SSE can’t do local segmentation on its own without help from on-premises equipment, agents, or VMs.

Out-of-band (OOB) management

OOB management for a direct, dedicated network connection to the SD-WAN on-ramp that doesn’t rely on cloud-based in-band connectivity. OOB access and provisioning are ideal to gain greater control over remote networking infrastructure on a dedicated connection.

Multiple WAN interfaces

Flexible and redundant WAN interfaces to ensure 24/7 availability. At least one of these should include a 5G/4G LTE modem with 2 SIM slots for high-speed cellular failover and out-of-band access when the primary WAN link is down.

Terminal server

Terminal server/serial console/”jump box” port management for easy remote management of edge infrastructure. This should include the ability to host third-party troubleshooting tools so admins can easily recover from outages without going on-site.

Computing power

Compute capabilities to run third-party apps and Docker containers right at the network edge. With built-in compute it’s easier to extend the functionality of SSE with additional applications that may not be part of the SSE stack or need an edge Docker footprint, like vulnerability scanning or user experience monitoring agents.

Centralized automation

Unified management of automation like Zero Touch Provisioning (ZTP) to automatically spin-up edge devices and connect them to SSE. Automation can significantly speed up branch deployments while reducing the risk of human error.

Why Nodegrid is the ideal SSE on-ramp

The Nodegrid branch and edge networking solution from ZPE Systems combines all the capabilities of the ideal SSE on-ramp in a single platform. For example, the Nodegrid Net Services Router (NSR) is a customizable, all-in-one device with available modules for storage, compute, serial console management, and more. The vendor-neutral NSR can host your preferred SD-WAN solution and supports easy integrations with SSE Magic Quadrant Leaders like Palo Alto Prisma Access, or you can use ZPE Cloud’s integrated SD-WAN app.

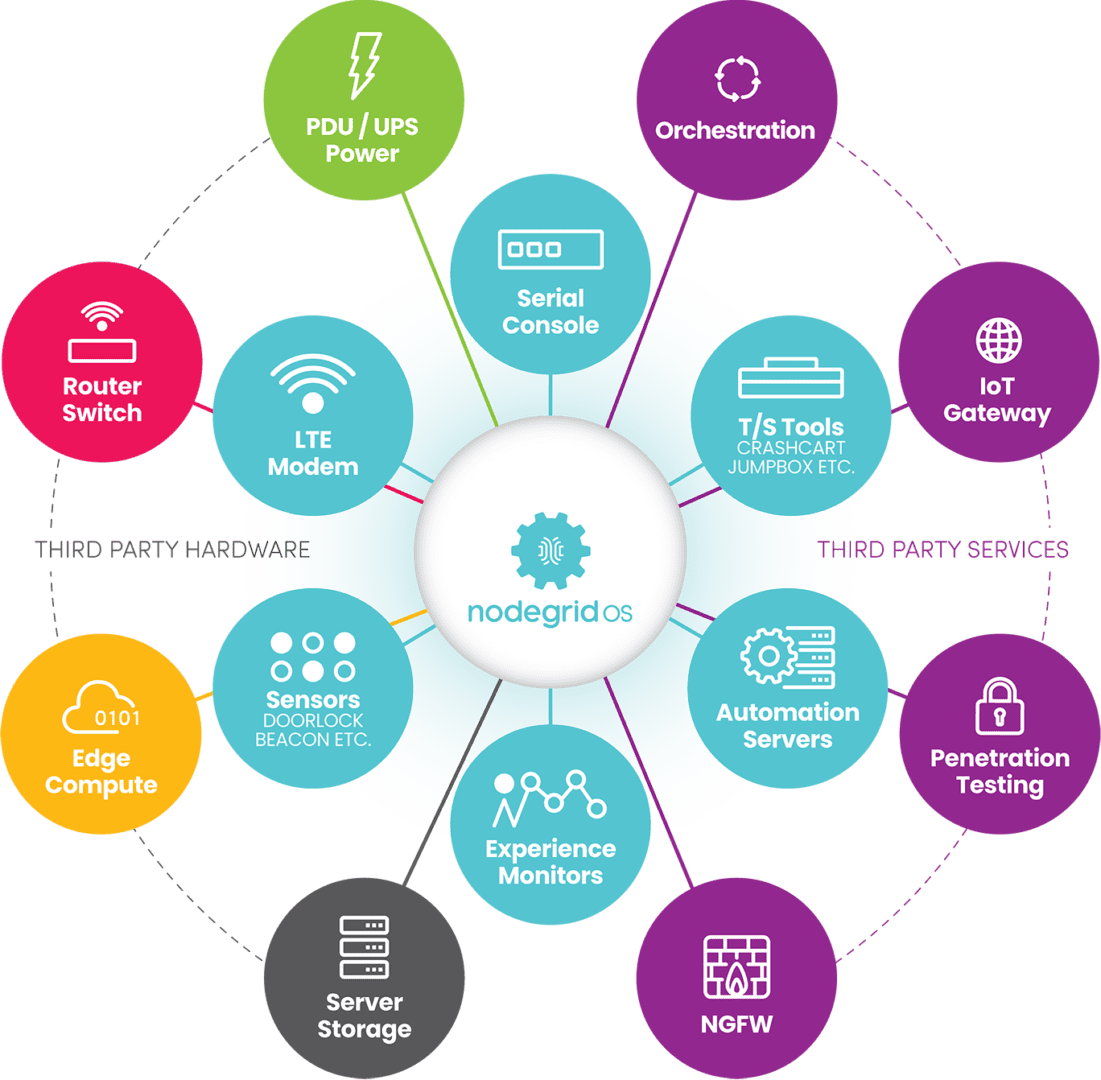
Thanks to the open-architecture, Linux-based Nodegrid OS, you can also extend Nodegrid’s capabilities with your choice of custom and third-party applications for security, monitoring, automation, and more. Plus, every device, application, and integration connected to the Nodegrid platform is brought under a single management umbrella for a unified and efficient orchestration experience. 

The Nodegrid platform from ZPE Systems rolls up everything you need in an SSE on-ramp and delivers it in one powerful, unified edge networking solution.

Learn how Nodegrid easily hosts and integrates Gartner’s picks for the 2023 SSE Magic Quadrant!

Contact ZPE Systems today!
Contact Us

What is an Application Delivery Platform?

An illustration showing a breakout of various software application components to highlight the need for an application delivery platform

Modern software architectures are highly complex and often very difficult to maintain and operate. A single enterprise application comprises hundreds (or even thousands) of individual services, technologies, and toolchains while requiring a lot of underlying infrastructure, such as servers, routing and load balancing rules, and security controls. All of this complexity increases overhead costs and adds to the ever-growing workloads of software, network, and infrastructure teams, especially when you multiply this effort across dozens or hundreds of software deployments.

Platform engineering is a new discipline introduced by Gartner to address these challenges by reducing the complexity of software engineering, network operations, and application delivery. The platforms built by these engineers are known by several names, including internal developer platforms, internal developer portals, and application delivery platforms. This guide defines an application delivery platform, discusses the underlying technology, and highlights a leading platform engineering solution.
.

Table of Contents:
  1. What is an application delivery platform?
  2. What is the importance of an application delivery platform?
  3. What technology makes up an application delivery platform?
  4. Introducing ZPE Systems’ Services Delivery Platform

What is an application delivery platform?

An application delivery platform is a suite of technologies that handles all the services that support an application, including security, traffic management, load balancing, and data management. Platform engineers combine all these services into a common toolset used to deploy applications at customer sites, so there’s no need to build a new architecture every time. This streamlined experience makes application delivery cost-effective by significantly reducing workloads and deployment timelines.

What is the importance of an application delivery platform?

The goal of an application delivery platform is to reduce deployment and management complexity. Deployment complexity leads to a greater risk of human error when configuring things like security controls and access policies, and any mistakes are likely to be found and exploited by cybercriminals. Management complexity makes it harder to stay on top of patch schedules. Unpatched software often contains vulnerabilities that are exploited by cybercriminals; for example, known ransomware groups targeted unpatched IBM software earlier this year.

By reducing complexity, an application delivery platform also reduces the attack surface, improving an organization’s overall security posture.

What technology makes up an application delivery platform?

By its very nature, an application delivery platform is highly customized to fit the needs of the applications being supported. Here are some examples of the services and technologies that are often included.

  • Server storage & compute: The platform needs storage (usually solid-state) and processing units (CPUs or GPUs) to run the applications and store necessary data. Ideally, the OS and computing architecture will support containers (e.g., Docker) for microservices applications.
  •  
  • Automation tools: A key feature of application delivery platforms is the ability to automatically provision and deploy new environments, apps, and network services as well activate services licenses and service chaining. That means the platform should host automation tools for configuration management, code delivery, and software-defined networking (SDN).
  •  
  • Security: The ideal platform makes it possible to deliver applications without configuring security every time. That means it provides unified management and repeatable deployments for security services like firewall traffic inspection, access control lists, and advanced authentication.
  •  
  • Routing & load balancing: A lot of backend networking goes into the typical application deployment to ensure traffic is routed correctly and optimized for performance. An application delivery platform should support network functions virtualization (NFVs) and SDN so standard network configurations can be easily deployed alongside the applications being delivered.
  • Management tools: Engineers need a way to remotely access, manage, and troubleshoot application deployments, even (and especially) during major service disruptions. The ideal platform includes out-of-band serial console management and supports third-party troubleshooting tools so remote teams can quickly recover systems and applications without an expensive on-site visit.

While this list is far from exhaustive, it covers the foundational technology that supports an application delivery platform. Platform engineering is still in its infancy, and many organizations struggle to efficiently execute it because of how many moving pieces need to be considered. The goal is to find a solution that provides the best framework of hardware and software capabilities that platform engineers can build upon, so they can create a fully customized application delivery platform without reinventing the wheel.

Introducing ZPE Systems’ Services Delivery Platform

Zero Pain Ecosysteme

The Services Delivery Platform from ZPE Systems is the perfect foundation for any platform engineering initiative. Nodegrid edge routers serve as the hardware backbone, providing networking and failover capabilities, OOB serial console management, and plenty of memory, storage, and CPU headroom for additional apps and services. You can build a fully customized hardware platform with the modular Net Services Router (NSR), extending your storage or compute capabilities or adding more ports to support your application deployment.

The vendor-neutral, Linux-based Nodegrid OS can run your custom applications as well as third-party automation, security, DevOps, and management tools. Plus, Nodegrid unifies all connected services and applications under a single management umbrella, allowing teams to oversee and orchestrate all of their deployments from one convenient portal.


Ready to Learn More?

The Services Delivery Platform from ZPE Systems simplifies platform engineering with powerful, multipurpose hardware and an open, vendor-neutral OS. Contact us today to learn more about using Nodegrid for your application delivery platform!

Contact Us

The Biggest Ransomware Attack You Haven’t Heard of…Yet

James Cabe CISSP

This article was written by James Cabe, CISSP, whose cybersecurity expertise has helped major companies including Microsoft and Fortinet.

MOVEit over SolarWinds — The largest and most successful ransomware attack ever recorded is happening. Right now. It’s attacking healthcare and financial institutions with high rates of success, and recently stole sensitive data of 4 million more healthcare patients. It uses something called CL0P ransomware, and the threat actor is a well-known criminal group with the name FIN11. Many organizations are finding it difficult to stop the attack because they have no way to access infected devices, take them offline, patch, or even replace them. So, what exactly is going on?

The group responsible for the attack

FIN11 is a cybercriminal group that has been active since 2016 or before, originating from the Commonwealth of Independent States (CIS). While the group has historically been associated with widespread phishing campaigns, their focus has shifted towards other initial access vectors. FIN11 often runs high-volume operations targeting industries in North America and Europe for data theft and ransomware deployment, primarily leveraging CL0P (aka CLOP).

FIN11 is responsible for multiple widespread, high-profile intrusion campaigns leveraging zero-day vulnerabilities, and the group likely has access to the networks of many more organizations than it is able to successfully monetize. Despite this, they’re currently attacking MOVEit, a well-known SaaS provider who relies on a file transfer appliance called Accellion lFile Transfer Appliance (FTA). This legacy product remains unpatched, which has led to the breach of many Fortune 100 companies and state and federal agencies.

FIN11

How did the ransomware attack start?

The ransomware attack began with several Accellion FTA customers, including those in industries like healthcare, legal, finance, retail, and telecom. Companies such as Jones Day Law, Kroger, Singtel, and many others had no idea that they had been attacked, because the initial breach was quiet and headless.

Their only indication came after receiving a threatening email aimed at extortion. 

In this email, the group threatened to publish stolen data on the “CL0P^_- LEAKS” .onion website, according to an investigation from Accellion. The Federal Bureau of Investigation (FBI) and the Cybersecurity and Infrastructure Security Agency (CISA) are releasing this joint CSA to disseminate known CL0P ransomware IOCs and TTPs identified through FBI investigations as recently as June 2023.

According to the investigation, four zero-day security holes were exploited in the attacks:

  • CVE-2021-27101 – SQL injection via a crafted Host header
  • CVE-2021-27102 – OS command execution via a local web service call
  • CVE-2021-27103 – SSRF via a crafted POST request
  • CVE-2021-27104 – OS command execution via a crafted POST request

And, the published victim data appears to have been stolen using a “WEB SHELL”. These web shells give remote administrative access to the web server and create a jumping off point to attack the rest of the internal network. Mandiant, a well-known cyber investigation arm of Google, added, “The exfiltration activity has affected entities in a wide range of sectors and countries” (Threatpost). Exfiltration is the unauthorized removal of important or damaging data from an organization.

However the biggest problem is that these web shells are what researchers call “PERSISTENCE”. This means that an attacker can remain in your network indefinitely to continue damaging and attacking your resources. Researchers call these “APTs,” or Advanced Persistent Threats.

Why is the ransomware attack still going strong?

The ransomware attack is still going strong because there’s no patch available. According to open source information, beginning on May 27, 2023, CL0P Ransomware Gang began exploiting a previously unknown SQL injection vulnerability (CVE-2023-34362) in Accelion’s appliance that is the backbone of a solution known as Progress Software’s MOVEit Transfer service. Internet-facing MOVEit Transfer web applications were infected with a web shell named LEMURLOOT, which was then used to steal data from underlying MOVEit Transfer databases. In similar spates of activity, TA505, which is the group responsible for the Dridex trojan and Locky ransomware, conducted zero-day-exploit-driven campaigns against Accellion FTA devices in 2020 and 2021, and Fortra/Linoma GoAnywhere MFT servers in early 2023.

What most organizations want to know is: How do you quickly respond to issues like these? How can you be properly prepared to respond to an issue you didn’t cause or didn’t expect?

Patching is a good response. However, it takes an average of 205 days to patch a recently known zero-day exploit like the MOVEit vulnerability. While patching alone is typically the ideal response, it isn’t automatic nor can it be done quickly.

Another approach involves removing the offending software or appliance, or cutting off access to the software or appliance. But once you remove this access, how do you continue normal operations, and how can you easily bring the software/appliance back online? Without adequate infrastructure in place, physically deploying to each site is not practical, especially for distributed organizations.

CISA and the FBI encourage organizations to implement the recommendations in the Mitigations section of this CSA to reduce the likelihood and impact of CL0P ransomware and other ransomware incidents. The Mitigations section describes many approaches, including patching, removing software/appliance access, and implementing a recovery plan. But all of these take too much time and too many resources, which leaves organizations vulnerable as they scramble to create an adequate response.

The great news is, organizations can cover all their bases without having to reinvent the wheel. This approach is recommended in one of CISA’s recent directives, and gives organizations somewhat of a silver bullet that allows them to quickly defeat ransomware and remain prepared for any future attack.

What approach does CISA recommend to address ransomware attacks?

CISA’s recent directive (23-02), which addresses the vulnerability of Internet-exposed management interfaces, calls for organizations to create an isolated management infrastructure (IMI) via out-of-band connectivity. This is a drop-in solution that the military, telcos, and hyperscalers/cloud companies use to respond to widespread ransomware and other issues impacting security and resilience. This approach — which ZPE Systems has perfected in the last decade with the help of Big Tech — gives organizations a completely separate control plane through which they can monitor and manage their entire IT infrastructure in a safe and dedicated fashion.

What is isolated management infrastructure?

Isolated management infrastructure consists of the hardware and software that create a management network that’s fully separate from other production and management networks. The key to this is in out-of-band connectivity, which is defined as connectivity other than TCP/IP. Out-of-band can include direct USB, serial, or even non-routed zero-trust connections to crown-jewel assets.

Essentially, the IMI gives an organization complete oversight and control of their widespread IT infrastructure, in a way that is secure and accessible only to their IT teams.

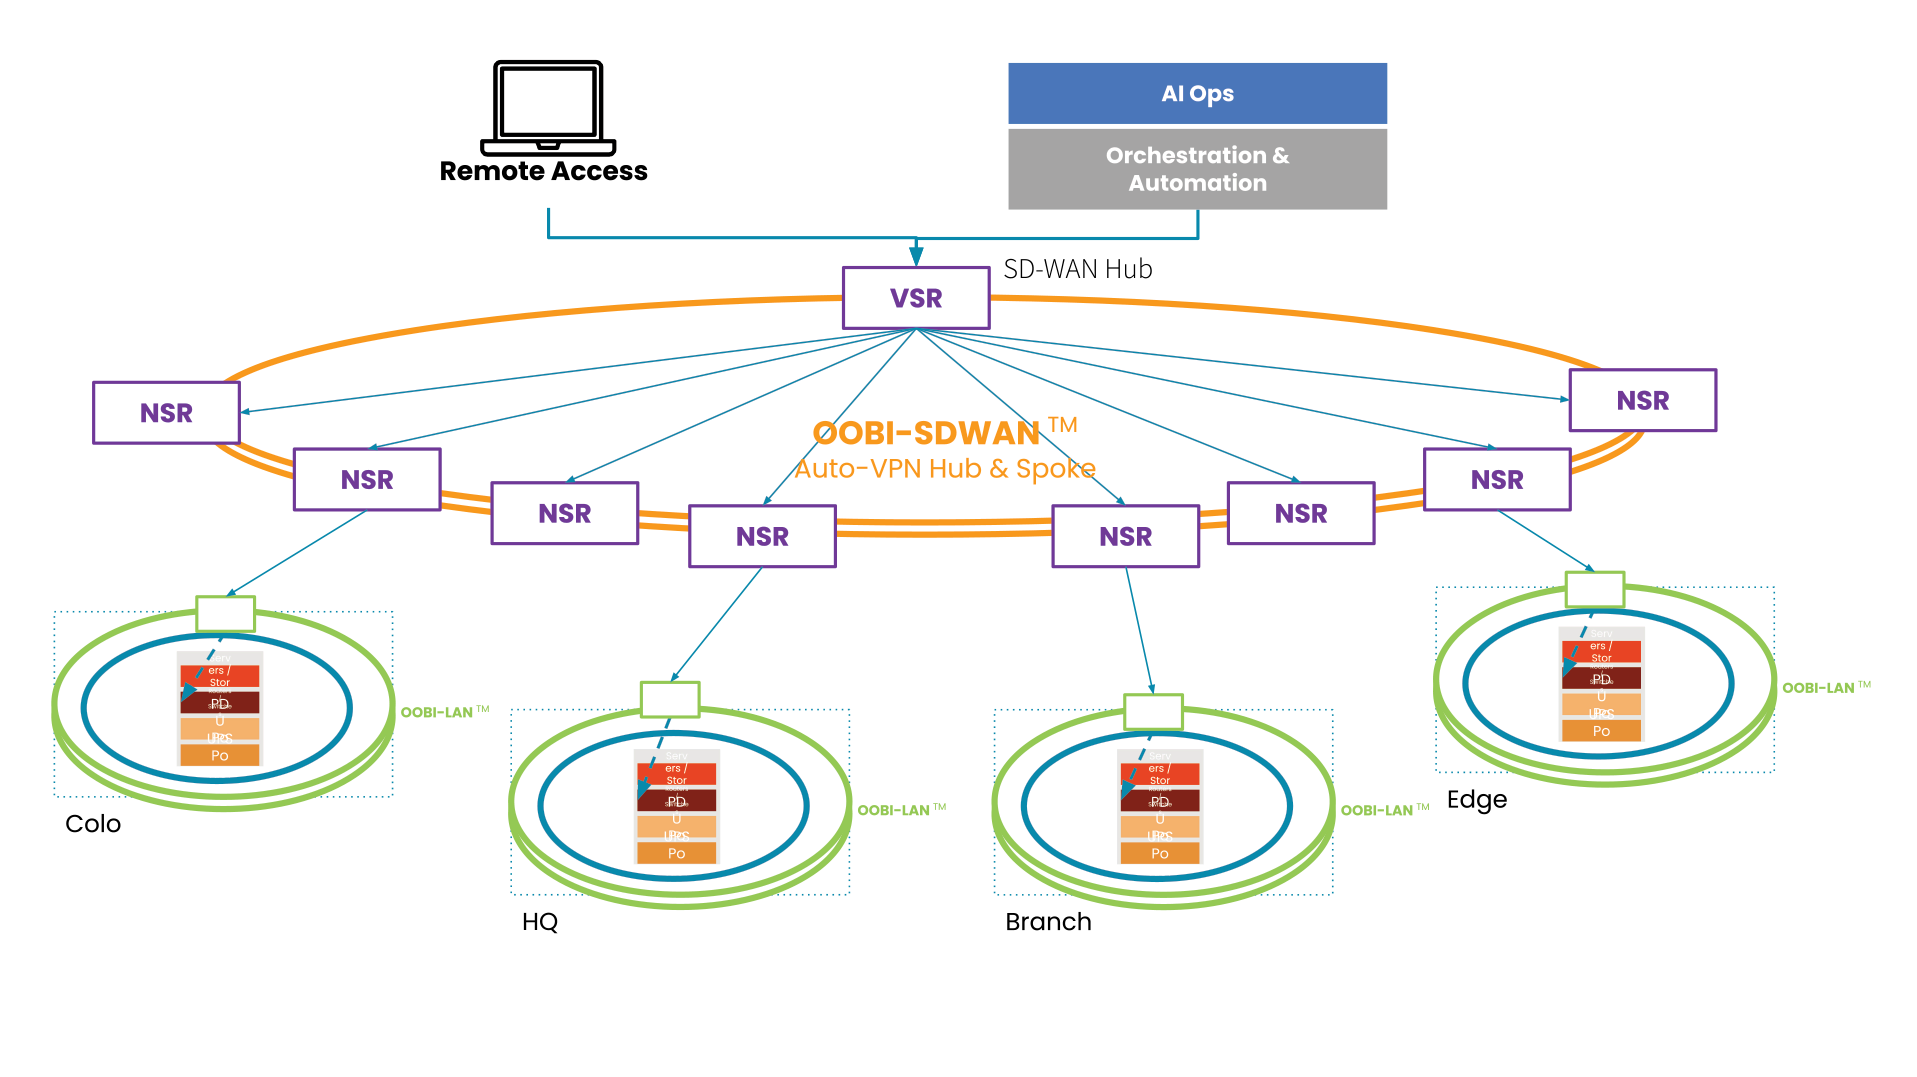
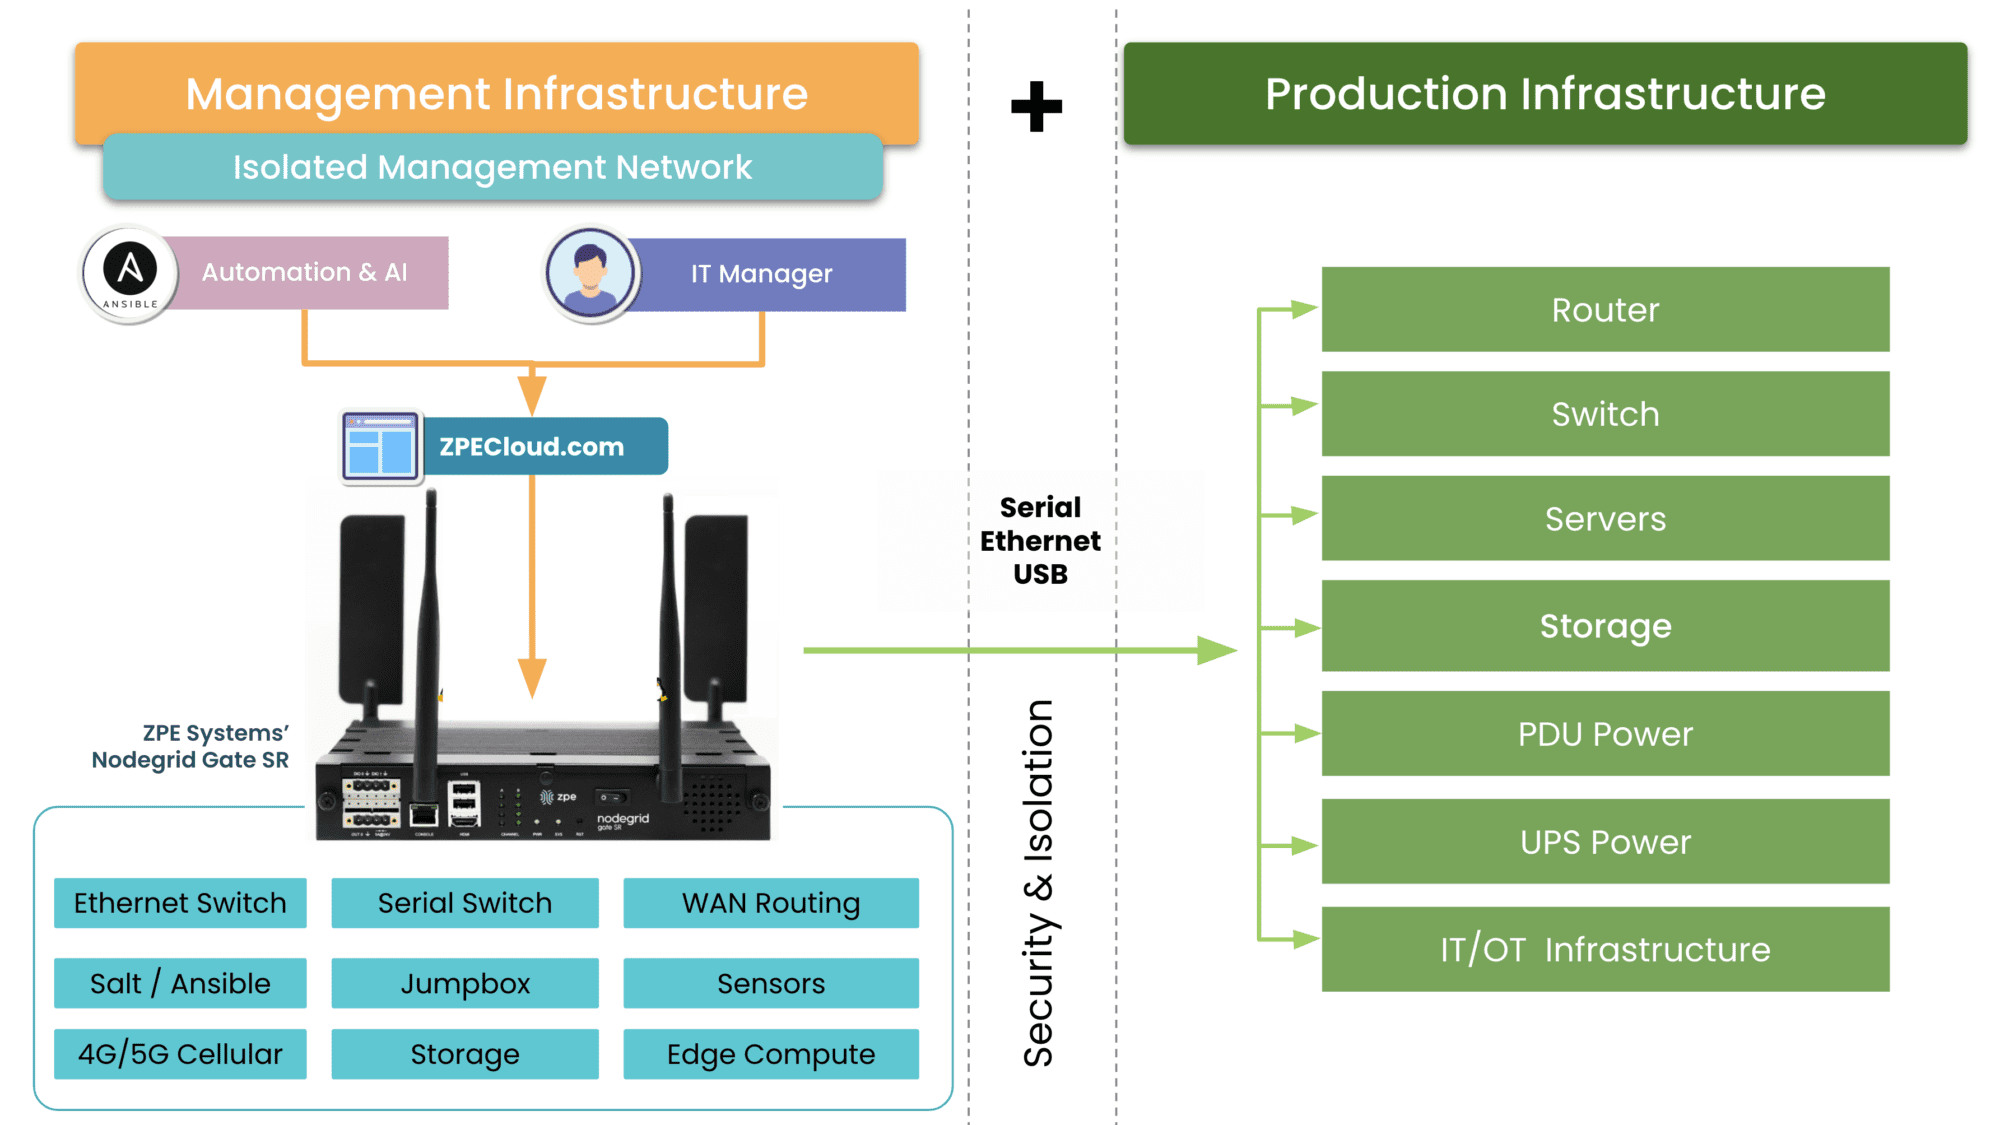
In this diagram, the production infrastructure (blue ring) sits at each distributed location. The out-of-band infrastructure for LAN (OOBI-LAN) is the green ring and surrounds the production infrastructure with one layer of isolated management. The OOBI-WAN (orange ring) is what provides a second layer of isolated management, which teams can access from a central or remote location, to gain access to the OOBI-LAN and ultimately the production infrastructure.

ZPE Automation

Knowing these assets and providing access across the organization can be easy and does not have to disrupt current operations. 

How can IMI stop the FIN11 ransomware attack?

In the ongoing FIN11 ransomware attack, Internet-facing applications are targets of the zero-day exploit. This means that no amount of security solutions can pre-mitigate the attack (i.e., there’s nothing you can do to stop it). This is where IMI shines.

Isolated Management Network diagram sitting beside production infrastructure

Remember the OOBI-LAN/OOBI-WAN diagram? Here’s a zoomed-in view of the isolated management infrastructure sitting beside the production infrastructure. The IMI connects via serial, Ethernet, and USB to production gear, and provides the necessary functions (routing, storing golden images, hosting jumpbox tools, etc.) to recover from attack. But how?

IT teams can use OOBI-WAN to remotely access their OOBI-LAN and production gear. They can pull affected devices offline and bring them in for forensics, which takes place in an Isolated Recovery Environment (IRE). This means these assets and networks are still reachable by analysts and responders, but isolated from other vulnerable assets. This allows an organization to quickly and even automatically deploy tools and resources inside of this environment through devices like ZPE Systems’ Nodegrid.

To combat the FIN11 attack, organizations don’t need to unplug cables or shut their devices off. They can instead deploy their IMI as the framework for closing the attack surface while maintaining access and critical data to aid in recovery.

Get the blueprint for isolated management infrastructure

Don’t wait until the next attack to shore up your defenses. ZPE Systems has worked with Big Tech for ten years developing the isolated management infrastructure. It’s now available inside the Network Automation Blueprint, and walks you through how to implement your own IMI. Download the blueprint now to stay ready for any attack.

Get in touch with me!

True security can only be achieved through resilience, and that’s my mission. If you want help shoring up your defenses, building an IMI, and implementing a Resilience System, get in touch with me. Here are links to my social media accounts:

How to Implement Zero Trust for OT

zero trust for ot
Enterprise security teams traditionally focus on IT networks, but operational technology (OT) security is just as important. OT comprises equipment that interacts with the physical world, such as sensors, temperature gauges, and motors, as well as the systems used to control that technology. Attacks on OT systems have a huge impact on business operations and customers, often causing more devastation than an IT breach. For example, an attack on an oil pipeline’s control systems could shut down production for weeks and affect millions of people in the region.

“Zero trust” is a security methodology designed to reduce the risk of attack through network segmentation, granular access policies, and advanced security technologies. Many organizations use zero trust to protect their IT networks, but it’s just as critical to the safeguarding of operational technology. This post defines zero trust security before explaining how to implement zero trust for OT.

Table of Contents:

What is zero trust for OT?

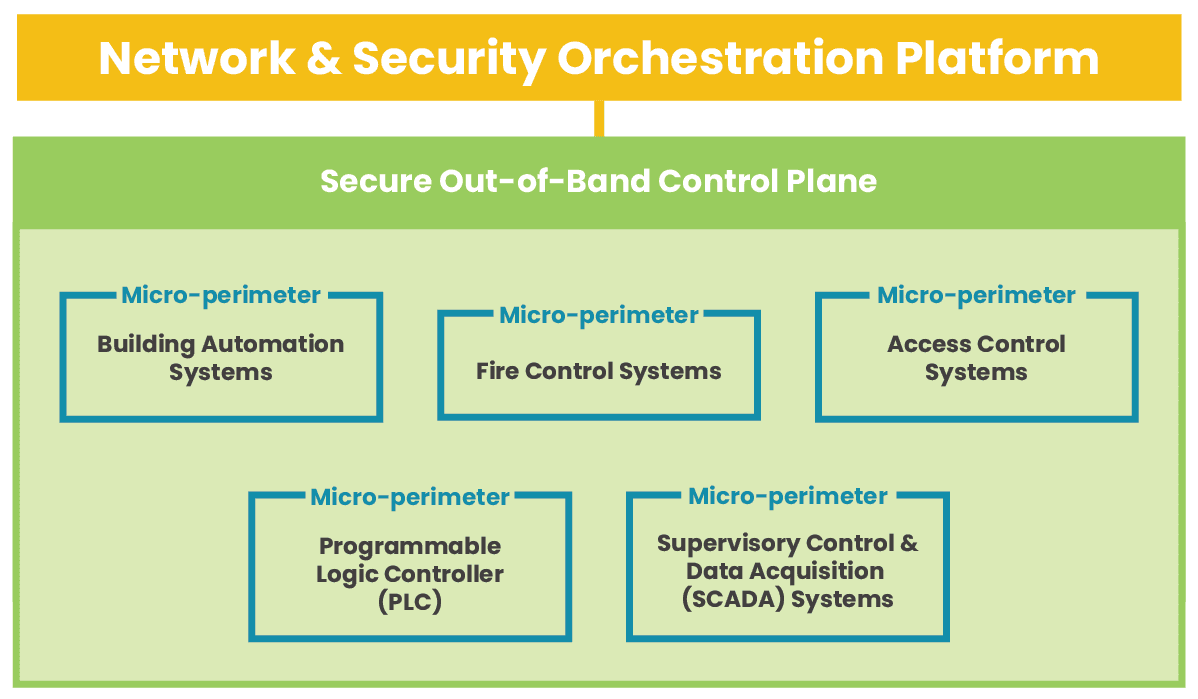
According to recent research by Barracuda Networks, more than 90 percent of manufacturing organizations saw cyberattacks hit their production or energy supply in 2021 alone. OT is a frequent target because of how devastating an attack can be on business operations and because it often lacks the same security policies and controls that protect IT infrastructure. To solve this problem, teams need to apply zero trust security principles, policies, and technology to their OT networks. The zero trust security methodology follows the motto “never trust, always verify.” That means operating under the assumption that no users or devices should be trusted, even if they’re logging in from within the main office. Achieving a zero-trust architecture means segmenting IT and OT networks and creating micro-perimeters of highly specific security policies and controls to protect each segment. Zero trust often uses advanced security technologies like AIOps and machine learning to enforce those policies, identify subtle signs of compromise, and quickly resolve security incidents.

How to implement zero trust for OT

Let’s discuss the requirements and best practices for implementing zero trust for OT.

Isolate critical systems with segmentation

Zero trust requires custom-tailored security policies and controls to protect specific network resources. That means network teams must logically segment the network based on which resources need to be protected by which policies and technologies, a practice known as micro-segmentation.

OT is often grouped together into a single micro-segment under the assumption that all OT needs the same protection. However, not all OT is created equally, especially in the eyes of a would-be attacker. For example, a programmable logic controller (PLC) gives cybercriminals control over manufacturing processes, but compromising an access control system lets them physically infiltrate the building. Some organizations take zero trust even further by using nano-segmentation to isolate individual systems, applications, or containers to create extremely effective micro-perimeters to address specific vulnerabilities.

Micro- and nano-segmentation are the backbone of a zero-trust architecture, enabling the creation of micro-perimeters using granular access policies and security controls customized for the protected resources.

Create and enforce strong security policies

Zero trust security policies determine who can pass through each micro-perimeter and who can access each OT resource. These policies should follow a least-privilege approach, meaning everyone gets the bare minimum privileges required to complete their workflows and nothing more. The best practice is to use role-based access control (RBAC), categorizing individual accounts based on their role (e.g., system administrators or machine operators) and giving each role least-privilege access to the resources required for that job.

The best way to create and enforce zero trust security policies is with an identity and access management (IAM) solution. A zero-trust IAM solution monitors each micro-perimeter to verify the identities of all accounts requesting access and attempts to establish an account’s trustworthiness using methods like two-factor authentication (2FA). Some advanced IAM solutions even use machine learning technology like user and entity behavior analytics (UEBA) to monitor account activity on the network and spot anomalous behavior that could indicate compromise.

  • IAM = Identity and Access Management: Creates and deploys policies, verifies identities, and establishes trustworthiness.
  • 2FA = Two-Factor Authentication: Requires an additional form of identity verification (besides the username and password), such as a code sent to an authorized mobile device.
  • UEBA = User and Entity Behavior Analytics: Uses machine learning to monitor account activity, creates baselines for normal behavior, and identifies anomalies that could mean an account is compromised.

Strong, granular security policies and zero-trust IAM solutions help protect OT by limiting account privileges and preventing compromised accounts from accessing network resources.

Leverage advanced security technologies

There are additional security technologies that support or enhance zero trust for OT. For example, a next-generation firewall (NGFW) makes network segmentation easier and includes advanced features such as application-aware filtering and deep-packet inspection. Secure access service edge (SASE) delivers zero trust security solutions to the network edge, safeguarding OT at remote branch sites with the same policies and controls as the central enterprise network. AIOps uses artificial intelligence for better threat detection and faster incident recovery.

Organizations use advanced security technologies to fortify micro-perimeters, extend zero trust to the edge, and gain enhanced detection and recovery capabilities.

Implement zero trust for OT with Nodegrid

Zero trust security protects operational technology using network segmentation to create micro-perimeters of strong security policies and advanced security technologies custom-tailored to each individual resource’s requirements and vulnerabilities. Achieving zero trust is typically a long and tedious process because of how many solutions and devices you must deploy.

The Nodegrid solution from ZPE Systems alleviates this challenge by providing a vendor neutral platform capable of hosting and deploying all your zero trust security technologies. For example, Nodegrid network edge routers deliver all the networking capabilities required to spin up an OT branch and can directly host your choice of third-party security solutions. Nodegrid reduces hardware expenses by consolidating network functionality onto fewer devices while unifying network and security management under a single umbrella for greater operational efficiency.

In fact, Nodegrid is an entire Services Delivery Platform that you can deploy anywhere in your network architecture to host your critical third-party SaaS (software as a service) solutions. That means you can create a customized branch-in-a-box that combines gateway routing, switching, out-of-band (OOB) management, NGFW, SASE, infrastructure automation, and more in a single device.

Ready to Learn More?

Contact ZPE Systems to learn more about implementing and enhancing zero trust for OT with the Nodegrid Services Delivery Platform.

Contact Us

IoT in Finance Industry and Security Challenges

IoT in Finance Industry and Security Challenges
The Internet of Things (IoT) drives new innovations in the finance industry by empowering organizations to harvest more data, improve operational efficiency, and provide better customer service. However, adding dozens of low-touch devices to the network’s edge creates major security, privacy, and compliance challenges.

This post discusses how to take advantage of IoT in the finance industry by overcoming security challenges with automation, secure platforms, and vendor-neutral orchestration

IoT in the Finance Industry: Security Challenges and Solutions

The challenge: Unpatched, out-of-date IoT devices are easier to compromise for harvesting sensitive data.

The solution: Automated patch management using vendor-neutral management platforms that can dig their hooks into multi-vendor IoT.

The challenge: Unsecured remote management interfaces can be used by cybercriminals to access IoT devices and data.

The solution: Secure management hardware and software protected by robust security features like self-encrypted disk (SED) and two-factor authentication (2FA).

The challenge: It’s difficult to enforce security and privacy policies on remote IoT devices that process regulated financial data at the edge of the network.

The solution: A vendor-neutral security orchestration platform that extends Zero Trust Security policies and controls to multi-vendor IoT at the edge.

The challenge: It’s difficult to troubleshoot and resolve security incidents involving remote IoT devices without expensive, time-consuming truck rolls.

The solution: Secure out-of-band (OOB) management solutions that integrate with (or even directly host) third-party automation and AIOps tools.

The challenge: A lot of complexity is involved in gaining holistic security coverage over a distributed, multi-vendor financial network without leaving any gaps.

The solution: A vendor-neutral platform that unifies security and network management for the entire architecture behind a single pane of glass.


IoT in the finance industry: security challenges and solutions

There were over 10.54 million global IoT cybersecurity attacks in December 2022 alone. In the finance industry, a breach can result in significant consequences, including regulatory fines and irreparable reputational damage, which means IoT security must be a top priority. Let’s discuss the specific security challenges of using IoT in the finance industry.

Challenge #1: Keeping IoT devices up-to-date

IoT typically uses low-touch, set-it-and-forget-it devices, so they’re deployed around the network’s edge and receive little interaction from operators or technical staff. For example, IoT devices collect sensitive financial data from ATMs, self-service payment kiosks, and smartphone applications with little-to-no human oversight. That makes it easy for network teams to forget about operating system (OS) and software updates, especially when dozens or thousands of IoT devices are in use.

In fact, a recent report found that teams wait an average of 205 days to patch their infrastructure. This is a frightening statistic given that out-of-date software is rife with vulnerabilities just waiting to be exploited by cybercriminals looking for valuable financial data.

Solution: Automated patch management

Automating patches is the best way to ensure they’re installed on time. For example, many IoT device management systems provide dashboards where admins can see IoT device versioning information at-a-glance, manually deploy or roll-back updates, or create automated schedules/triggers to deploy those updates without manual intervention. However, most of these platforms only work within specific vendor ecosystems, which limits your capabilities. The best practice is to use a vendor-neutral IoT device management platform that can dig its hooks into multi-vendor IoT devices. This will ensure that critical IoT devices like credit card payment readers are kept secure and up-to-date.


A vendor-neutral IoT device management platform with automated patch management ensures that all devices are kept up-to-date and no vulnerabilities fall between the cracks.

Challenge #2: Securing remote management interfaces

Network admins typically work from a centralized location, which means they remotely access and manage IoT deployments at the branch and edge using jump boxes or serial consoles. If these remote management devices and interfaces aren’t adequately secured, malicious actors could use them to access IoT data and move laterally to other sensitive resources on the network. However, many admins deploy jump boxes without onboarding them with IT, which means they’re not added to security monitoring software and don’t have enterprise policies or controls applied. Serial consoles, on the other hand, often lack the advanced security features and integrations needed to protect them from cybercriminals.

Solution: Secure management hardware and software

The newest generation of serial consoles includes robust hardware security features and supports advanced authentication methods to safeguard remote management interfaces from compromise. A 3rd generation – or Gen 3 – serial console has onboard security features like a self-encrypted disk (SED), secure boot, BIOS protection, and geofencing, so malicious actors can’t access a stolen device. In addition, it supports SAML 2.0 authentication (via integrations with providers like Okta and Ping) and other advanced authentication methods to prevent unauthorized access to its software.


A Gen 3 serial console solution uses robust onboard security features and third-party security integrations to protect management hardware and interfaces.

Challenge #3: Complying with data privacy regulations

In a highly-regulated industry like finance, organizations must keep track of which people and devices can access sensitive data and ensure that permissions are granted on a least-privilege basis. Typically, achieving this level of granular control requires applying strict Zero Trust Security policies to every device and user accessing the network, including IoT devices at the edge. However, extending enterprise security policies and controls to the edge is difficult in a distributed, heterogeneous environment due to vendor lock-in.

For example, some branch networking solutions don’t support integrations with third-party identity management tools, forcing you to use their built-in access management settings. That means admins must manually recreate their Zero Trust data access policies in the router settings at every single branch and ensure they’re kept up-to-date.

Solution: Vendor-neutral Zero Trust Security orchestration

A centralized Zero Trust Security orchestration platform allows admins to deploy and manage security policies and controls across the network from a single place. A vendor-neutral platform can extend policy enforcement and other vital security controls to any device or application on the network. For example, you can apply the same Zero Trust data policies to all branch routers in the entire architecture to ensure consistent enforcement.  Such a platform makes compliance easier because financial organizations gain greater control over data access privileges and monitoring for IoT devices deployed anywhere in the world.


A vendor-neutral Zero Trust Security orchestration platform simplifies IoT data compliance by providing a centralized control panel to deploy and manage security policies across the entire distributed network architecture.

Challenge #4: Quickly resolving IoT security incidents

When malicious actors compromise an IoT device, financial organizations must act quickly to avoid regulatory fees and reputational damage. However, these devices are often deployed in remote, hard-to-reach locations with no technical or security staff nearby, such as in rural or island communities. That means problems require an expensive, time-consuming truck roll to resolve. Even with a team on-site, manual root cause analysis (RCA) and recovery efforts take a lot of time and effort, increasing both the duration and the expense of incidents.

Solution: Secure OOB with automation and AIOps support

The solution to this IoT security challenge involves out-of-band serial consoles and automation.

  • Out-of-band (OOB) serial consoles create a dedicated control plane to manage, troubleshoot, and recover remote devices and infrastructure. Admins access this control plane via alternative network interfaces that don’t rely on the production network at all. This means teams can still reach remote IoT devices even if the ISP goes down or the LAN is compromised by ransomware. The best practice is to use a Gen 3 serial console with advanced security features, as discussed above.
  • Automation and AIOps streamline the incident resolution process by automating RCA and recovery workflows. A Gen 3 OOB serial console solution can integrate or even directly host third-party automation and AIOps tools, ensuring teams always have remote access to their recovery toolkit during an outage or breach.


A secure, Gen 3 OOB serial console ensures 24/7 remote access to edge IoT deployments and supports automation and AIOps for faster security incident resolution.

Challenge #5: Gaining holistic security coverage

A distributed financial services network with many branches, ATMs, edge sites, and IoT devices has a large attack surface, so it requires several different security solutions to cover all potential vulnerabilities. Gaining complete security coverage over every IoT device in every location means deploying many appliances, each of which needs to be installed, patched, and managed, adding a lot of complexity to network and security operations and further increasing the attack surface. The need to orchestrate so many moving pieces increases the risk that security teams will make mistakes and prevent organizations from operating efficiently.

Solution: Unified, vendor-neutral security orchestration

A vendor-neutral security orchestration platform unifies a company’s security solutions and workflows under a single management umbrella. For example, the Nodegrid platform from ZPE Systems can dig its hooks into other vendors’ security appliances and virtual solutions, giving security analysts a holistic overview of the entire architecture from a single centralized portal. Teams can use Nodegrid to orchestrate firewalls, identity and access management (IAM), patches, secure access service edge (SASE), and more.

Nodegrid’s hardware can even directly host third-party security applications for a streamlined, consolidated branch deployment. You can use the Nodegrid platform to build a complete DCIM (data center infrastructure management), network management, and automation orchestration solution, streamlining operations with a truly unified experience.

A vendor-neutral security orchestration platform provides holistic security coverage while reducing complexity, which prevents human error and increases operational efficiency.

IoT in the finance industry and security challenges

Deploying IoT in the finance industry comes with security challenges, including patch management, unsecured management interfaces, policy enforcement, incident resolution, and complexity. The Nodegrid platform provides finance industry solutions to help you overcome each of these challenges, including:

A truly vendor-neutral platform that unifies security, network, and infrastructure management behind a single pane of glass for holistic coverage.

Ready to Learn More?

To learn more about deploying IoT in the finance industry and overcoming security challenges with Nodegrid, contact ZPE Systems.

Contact Us

Atsign: Why Choose ZPE Systems to Host IoT Security?

Colin

A Conversation with Atsign CTO & Co-Founder, Colin Constable

This is a guest post composed by Atsign, creators of zero-attack-surface solutions including atProtocol.

We recently sat down with our CTO and Mariposa Rotary Club extraordinaire, Colin Constable, to discuss our partnership with our friends over at ZPE Systems. Let’s explore the driving force behind this powerful partnership, and how together we’re securing IoT devices and the data shared between them.

Why is this partnership strategically important?

We are a software company that helps people connect beyond the edge of the Internet. And as a software company, we need to have hardware to run our software on. After looking at a number of hardware platforms, ZPE stood out as an organization that provides a strong array of network connectivity options. Our software running on ZPE’s hardware serves as an edge platform that gives customers reliable access to edge-generated data.

What are some of the synergies between Atsign and ZPE?

First and foremost, ZPE’s hardware was designed from scratch to provide the openness and flexibility that we were looking for in a hardware platform. If I were going to design something like this myself, it would look very much like a ZPE box! It is incredibly easy to drop our Docker containers straight onto the platform, and they just simply work, which is quite a joy. To have a Docker container environment on an edge box is really the thing that makes ZPE stand out as a platform. Combine that with the fact that ZPE boxes are running x86, which makes things easy–plus actually having dual SIM cards–we can work with our MVNO partners to provide constant connectivity; even if hardlines go down, there’s cellular backup. The thing we can offer ZPE and their customers is if the box can see the Internet, then you’ll be able to address it, get data to and from it, and actually even log into it, and get hold of the built-in UI on the box.

Tell us about ZPE’s Docker Container support

Our docker containers literally just ran perfectly on the ZPE hardware. I went into the UI, selected my docker container, and it just ran. It doesn’t get much easier than that. Plus, there’s the promise of being able to have the docker container talk to connected devices like V.24 cables to provide connectivity to IoT devices.

Once IoT devices become directly addressable, then it opens up all kinds of opportunities for more efficient delivery or sharing of information that can save customers tons of money by eliminating a lot of the current infrastructure they currently use to do that job.

What are some real-world use cases for Atsign and ZPE Systems?

Because ZPE boxes have lots of connectivity options (e.g. serial ports, 4/5G backhaul, and ethernet–with more coming!) for connecting IoT devices, then you can have always-on devices at the edge, and be able to address and get data to and from them. For example, a radio station that has DSL connectivity, and cellular backup would be able to just automatically move over to cellular backup, notify the radio station that it’s on cellular backup, but use that connectivity until the ADSL line comes back online and at all times be able to get information from the equipment at the radio station. This is critical for radio stations, as it eliminates “dead air,” that moment when the transmitter is not transmitting. Sponsors rely on radio stations to put out notifications for what their businesses are doing, so having constant, uninterrupted connectivity is essential.

Do Atsign & ZPE Systems improve sustainability?

Traditional solutions would have you installing many different boxes. What we really like about the ZPE platform is that although the hardware provides lots of connectivity options–that reduces the footprint for starters–there’s no need to have different modems and firewalls, and any other services can be added via docker containers, so you actually have an environment where you have a single box, and it can do multiple functions at the edge.

What are your final thoughts on the partnership between Atsign and ZPE Systems?

As a software company, we need hardware to deploy on. We especially need hardware that can sit on the edge with all the right connectivity points. Atsign and ZPE Systems is really a perfect combination of great software and great hardware at the edge.

Bonus: What is Colin’s favorite firewall configuration for a ZPE box?

My favorite firewall rule is the one that costs the least money, and is ultimately the most secure firewall ruleset: Deny All. If you’ve got Deny All, that means that you don’t have to deal with the pain and complexities of firewall rules in order to address devices, which is what the real cost of networking is these days; it’s not necessarily the hardware, it’s actually having people to administer firewall rulesets. Having zero network attack surfaces, having a Deny All ruleset, just means you don’t have to have people changing rulesets all the time, which is a good thing.