Providing Out-of-Band Connectivity to Mission-Critical IT Resources

Healthcare Network Design
Edge Computing in Healthcare
In a healthcare organization, IT’s goal is to ensure network and system stability to improve both patient outcomes and ROI. The National Institutes of Health (NIH) provides many recommendations for how to achieve these goals, and they place a heavy focus on resilience engineering (RE). Resilience engineering enables a healthcare organization to resist and recover from unexpected events, such as surges in demand, ransomware attacks, and network failures. Resilient architectures allow the organization to continue operating and serving patients during major disruptions and to recover critical systems rapidly.

This guide to healthcare network design describes the core technologies comprising a resilient network architecture before discussing how to take resilience engineering to the next level with automation, edge computing, and isolated recovery environments.

Core healthcare network resilience technologies

A resilient healthcare network design includes resilience systems that perform critical functions while the primary systems are down. The core technologies and capabilities required for resilience systems include:

  • Full-stack networking – Routing, switching, Wi-Fi, voice over IP (VoIP), virtualization, and the network overlay used in software-defined networking (SDN) and software-defined wide area networking (SD-WAN)
  • Full compute capabilities – The virtual machines (VMs), containers, and/or bare metal servers needed to run applications and deliver services
  • Storage – Enough to recover systems and applications as well as deliver content while primary systems are down

These are the main technologies that allow healthcare IT teams to reduce disruptions and streamline recovery. Once organizations achieve this base level of resilience, they can evolve by adding more automation, edge computing, and isolated recovery infrastructure.

Extending automated control over healthcare networks

Automation is one of the best tools healthcare teams have to reduce human error, improve efficiency, and ensure network resilience. However, automation can be hard to learn, and scripts take a long time to write, so having systems are easily deployable with low technical debt is critical. Tools like ZTP (zero-touch provisioning), and the integration of technology like Infrastructure as Code (IaC), accelerate recovery by automating device provisioning. Healthcare organizations can use automation technologies such as AIOps with resilience systems technologies like out-of-band (OOB) management to monitor, maintain, and troubleshoot critical infrastructure.

Using automation to observe and control healthcare networks helps prevent failures from occuring, but when trouble does actually happen, resilience systems ensure infrastructure and services are quickly returned to health or rerouted when needed.

Improving performance and security with edge computing

The healthcare industry is one of the biggest adopters of IoT (Internet of Things) technology. Remote, networked medical devices like pacemakers, insulin pumps, and heart rate monitors collect a large volume of valuable data that healthcare teams use to improve patient care. Transmitting that data to a software application in a data center or cloud adds latency and increases the chances of interception by malicious actors. Edge computing for healthcare eliminates these problems by relocating applications closer to the source of medical data, at the edges of the healthcare network. Edge computing significantly reduces latency and security risks, creating a more resilient healthcare network design.

Note that teams also need a way to remotely manage and service edge computing technologies. Find out more in our blog Edge Management & Orchestration.

Increasing resilience with isolated recovery environments

Ransomware is one of the biggest threats to network resilience, with attacks occurring so frequently that it’s no longer a question of ‘if’ but ‘when’ a healthcare organization will be hit.

Recovering from ransomware is especially difficult because of how easily malicious code can spread from the production network into backup data and systems. The best way to protect your resilience systems and speed up ransomware recovery is with an isolated recovery environment (IRE) that’s fully separated from the production infrastructure.
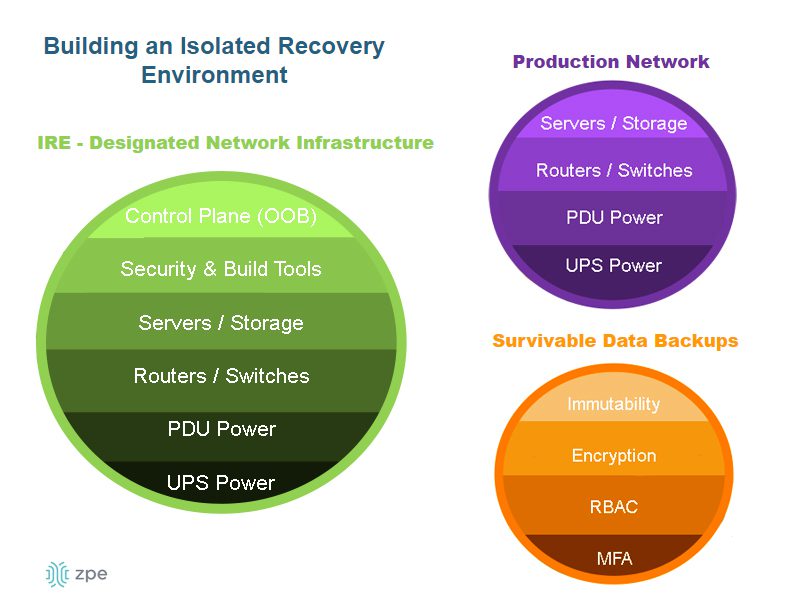
 

A diagram showing the components of an isolated recovery environment.

An IRE ensures that IT teams have a dedicated environment in which to rebuild and restore critical services during a ransomware attack, as well as during other disruptions or disasters. An IRE does not replace a traditional backup solution, but it does provide a safe environment that’s inaccessible to attackers, allowing response teams to conduct remediation efforts without being detected or interrupted by adversaries. Isolating your recovery architecture improves healthcare network resilience by reducing the time it takes to restore critical systems and preventing reinfection.

To learn more about how to recover from ransomware using an isolated recovery environment, download our whitepaper, 3 Steps to Ransomware Recovery.

Resilient healthcare network design with Nodegrid

A resilient healthcare network design is resistant to failures thanks to resilience systems that perform critical functions while the primary systems are down. Healthcare organizations can further improve resilience by implementing additional automation, edge computing, and isolated recovery environments (IREs).

Nodegrid healthcare network solutions from ZPE Systems simplify healthcare resilience engineering by consolidating the technologies and services needed to deploy and evolve your resilience systems. Nodegrid’s serial console servers and integrated branch/edge routers deliver full-stack networking, combining cellular, Wi-Fi, fiber, and copper into software-driven networking that also includes compute capabilities, storage, vendor-neutral application & automation hosting, and cellular failover required for basic resilience. Nodegrid also uses out-of-band (OOB) management to create an isolated management and recovery environment without the cost and hassle of deploying an entire redundant infrastructure.

Ready to see how Nodegrid can improve your network’s resilience?

Nodegrid streamlines resilient healthcare network design with consolidated, vendor-neutral solutions. Request a free demo to see Nodegrid in action.
Request a Demo

Best DevOps Tools

A glowing interface of DevOps tools and concepts hover above a laptop.
DevOps is all about streamlining software development and delivery through automation and collaboration. Many workflows are involved in a DevOps software development lifecycle, but they can be broadly broken down into the following categories: development, resource provisioning and management, integration, testing, deployment, and monitoring. The best DevOps tools streamline and automate these key aspects of the DevOps lifecycle. This blog discusses what role these tools play and highlights the most popular offerings in each category.

The best DevOps tools

Categorizing the Best DevOps Tools

Version Control Tools

Track and manage all the changes made to a code base.

IaC Build Tools

Provision infrastructure automatically with software code.

Configuration Management Tools

Prevent unauthorized changes from compromising security.

CI/CD Tools

Automatically build, test, integrate, and deploy software.

Testing Tools

Automatically test and validate software to streamline delivery.

Container Tools

Create, deploy, and manage containerized resources for microservice applications.

Monitoring & Incident Response Tools

Detect and resolve issues while finding opportunities to optimize.

DevOps version control

In a DevOps environment, a whole team of developers may work on the same code base simultaneously for maximum efficiency. DevOps version control tools like GitHub allow you to track and manage all the changes made to a code base, providing visibility into who’s making what changes at what time. Version control prevents devs from overwriting each other’s work or making unauthorized changes. For example, a developer may come up with a way to improve the performance of a feature by changing the existing code, but doing so inadvertently creates a vulnerability in the software or interferes with other application functions. DevOps version control prevents unauthorized code changes from integrating with the rest of source code and tracks who’s responsible for making the request, improving the stability and security of the software.

  •  Best DevOps version control tool: Github

Infrastructure as Code (IaC)

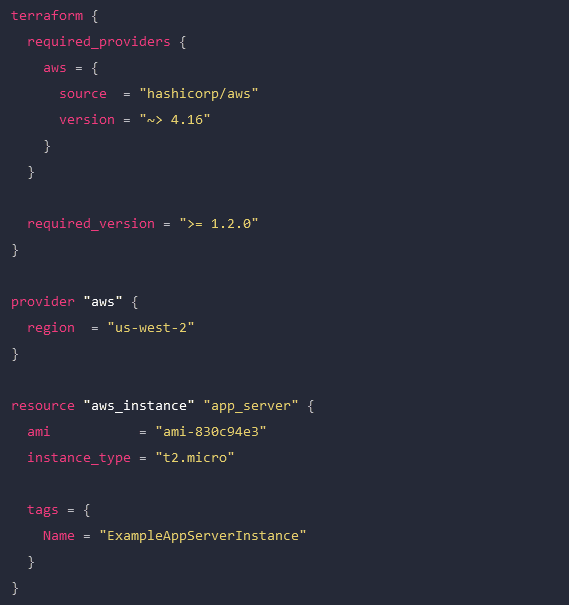
Infrastructure as Code (IaC) streamlines the Operations side of a DevOps environment by abstracting server, VM, and container configurations as software code. IaC build tools like HashiCorp Terraform allow Ops teams to write infrastructure configurations as declarative or imperative code, which is used to provision resources automatically. With IaC, teams can deploy infrastructure at the velocity required by DevOps development cycles. A screenshot of a Terraform configuration for AWS infrastructure.

An example Terraform configuration for IaC.

Configuration management

Configuration management involves monitoring infrastructure and network devices to make sure no unauthorized changes are made while systems are in production. Unmonitored changes could introduce security vulnerabilities that the organization is unaware of, especially in a fast-paced DevOps environment. In addition, as systems are patched and updated over time, configuration drift becomes a concern, leading to additional quality and security issues. DevOps configuration management tools like RedHat Ansible automatically monitor configurations and roll back unauthorized modifications. Some IaC build tools, like Terraform, also include configuration management.

Continuous Integration/Continuous Delivery (CI/CD)

Continuous Integration/Continuous Delivery (CI/CD) is a software development methodology that goes hand-in-hand with DevOps. In CI/CD, software code is continuously updated and integrated with the main code base, allowing a continuous delivery of new features and improvements. CI/CD tools like Jenkins automate every step of the CI/CD process, including software building, testing, integrating, and deployment. This allows DevOps organizations to continuously innovate and optimize their products to stay competitive in the market.

Software testing

Not all DevOps teams utilize CI/CD, and even those that do may have additional software testing needs that aren’t addressed by their CI/CD platform. In DevOps, app development is broken up into short sprints so manageable chunks of code can be tested and integrated as quickly as possible. Manual testing is slow and tedious, introducing delays that prevent teams from achieving the rapid delivery schedules required by DevOps organizations. DevOps software testing tools like Selenium automatically validate software to streamline the process and allow testing to occur early and often in the development cycle. That means high-quality apps and features get out to customers sooner, improving the ROI of software projects.

  •  Best software testing tool: Selenium

Container management

In DevOps, containers are lightweight, virtualized resources used in the development of microservice applications. Microservice applications are extremely agile, breaking up software into individual services that can be developed, deployed, managed, and destroyed without affecting other parts of the app. Docker is the de facto standard for basic container creation and management. Kubernetes takes things a step further by automating the orchestration of large-scale container deployments to enable an extremely efficient and streamlined infrastructure.

Monitoring & incident management

Continuous improvement is a core tenet of the DevOps methodology. Software and infrastructure must be monitored so potential issues can be resolved before they affect software performance or availability. Additionally, monitoring data should be analyzed for opportunities to improve the quality, speed, and usability of applications and systems. DevOps monitoring and incident response tools like Cisco’s AppDynamics provide full-stack visibility, automatic alerts, automated incident response and remediation, and in-depth analysis so DevOps teams can make data-driven decisions to improve their products.

Deploy the best DevOps tools with Nodegrid

DevOps is all about agility, speed, and efficiency. The best DevOps tools use automation to streamline key workflows so teams can deliver high-quality software faster. With so many individual tools to manage, there’s a real risk of DevOps tech sprawl driving costs up and inhibiting efficiency. One of the best ways to reduce tech sprawl (without giving up all the tools you love) is by using vendor-neutral platforms to consolidate your solutions. For example, the Nodegrid Services Delivery Platform from ZPE Systems can host and integrate 3rd-party DevOps tools, reducing the need to deploy additional virtual or hardware resources for each solution. Nodegrid utilizes integrated services routers, such as the Gate SR or Net SR, to provide branch/edge gateway routing, in-band networking, out-of-band (OOB) management, cellular failover, and more. With a Nodegrid SR, you can combine all your network functions and DevOps tools into a single integrated solution, consolidating your tech stack and streamlining operations.

A major benefit of using Nodegrid is that the Linux-based Nodegrid OS is Synopsys secure, meaning every line of source code is checked during our SDLC. This significantly reduces CVEs and other vulnerabilities that are likely present in other vendors’ software.

Learn more about efficient DevOps management with vendor-neutral solutions

With the vendor-neutral Nodegrid Services Delivery Platform, you can deploy the best DevOps tools while reducing tech sprawl. Watch a free Nodegrid demo to learn more.

Request a Demo

Best Network Performance Monitoring Tools

Best Network Performance Monitoring Tools
Network performance monitoring tools provide visibility into the health and efficiency of networks and their underlying infrastructure of devices and software. Some platforms focus entirely on collecting and analyzing logs from various sources on the network, while others provide additional management capabilities that let you control, change, and troubleshoot network infrastructure. Choosing the right solution requires a thoughtful consideration of factors such as the cost, scalability, and interoperability of the software, as well as your team’s experience and abilities. This guide compares three of the best network performance monitoring tools by analyzing these critical factors before providing advice on the most scalable and cost-effective way to deploy your solutions.

Comparing best network performance monitoring tools

Platform

Key Features

SolarWinds Network Performance Monitor (NPM)

  • Network device, performance, and fault monitoring

  • Deep packet inspection and analysis

  • LAN and WAN monitoring

  • Automatic network discovery, mapping, and monitoring

  • Network availability monitoring

  • Network diagnostics

  • Network path analysis

  • Network performance testing

  • SNMP monitoring

  • Wi-Fi analysis

Kentik

  • Network telemetry dashboards

  • Multi-vendor network monitoring

  • Cloud, edge, and hybrid cloud monitoring

  • SaaS application performance & uptime monitoring

  • Intelligent automated alerts

  • SNMP, traffic flow, VPC, host agent, and synthetic monitoring

  • Multi-cloud performance monitoring

  • Kubernetes workload monitoring

  • SD-WAN monitoring

  • Network security monitoring

  • Network map visualizations

  • QoE monitoring

ThousandEyes

  • Network availability and performance testing

  • WAN performance monitoring

  • Cisco SD-WAN monitoring and optimization

  • Browser session monitoring

  • Network path visibility

  • User Wi-Fi connectivity monitoring

  • VPN mapping and monitoring

  • Cross-layer data visualizations

Disclaimer: This comparison was written by a 3rd party in collaboration with ZPE Systems using data gathered from publicly available data sheets and admin guides, as of 10/20/2023. Please email us if you have corrections or edits, or want to review additional attributes: Matrix@zpesystems.com

SolarWinds Network Performance Monitor (NPM)

The Network Performance Monitor (NPM) is part of the SolarWinds Orion platform of integrated products. This mature and richly featured monitoring software is delivered as a cloud-based service and can observe SaaS (software as a service), cloud, hybrid cloud, and on-premises infrastructure. With advanced features like deep packet inspection (DPI), WAN optimization monitoring, automatic network mapping, and automated diagnostic tools, SolarWinds NPM is meant to be a complete, enterprise-grade observability solution. As part of the Orion platform, it’s also extensible with other products from the SolarWinds ecosystem, such as a Network Configuration Manager. As an enterprise solution, SolarWinds NPM comes with a high price tag that grows even larger as additional monitoring agents are added, limiting the scalability. Another important factor to consider is that SolarWinds recently suffered a high-profile hack that compromised thousands of customers, so there are security risks involved in trusting the Orion supply chain. Additionally, despite a large library of integrations, SolarWinds is a closed ecosystem that doesn’t work well with 3rd-party tools or custom scripts.​

Pros

Cons

  • Supports SaaS, cloud, and on-premises networks
  • Includes advanced monitoring features like DPI
  • Part of a large ecosystem of observability and management solutions
  • Pricing is expensive and limits scalability
  • Recently suffered a high-profile breach that impacted thousands of customers
  • Closed ecosystem may not support your 3rd-party tools

Kentik

Kentik is an end-to-end network observability platform for cloud, multi-cloud, hybrid cloud, SaaS, and data center infrastructure. In addition to network performance monitoring, the platform includes monitoring solutions for SaaS application performance and SD-WAN performance. Other observability features include SaaS uptime monitoring, AI-driven insights and alerts, network security monitoring, and QoE (Quality of Experience) monitoring. Kentik also recently launched a Kubernetes network monitoring solution called Kentik Kube that provides end-to-end cluster visibility. Overall, Kentik is a powerful network observability platform that includes many of its most innovative features in its “Essentials” and “Pro” pricing packages, providing a lot of bang for your buck. The downside is that you can’t subscribe to features individually and must purchase a whole package, meaning you could end up paying for features you don’t need. Because Kentik is not a large vendor, its customer service may be slow to respond in some cases. Additionally, although Kentik does have a large library of integrations, it is not a vendor-neutral platform.

Pros

Cons

  • Supports cloud, multi-cloud, hybrid cloud, SaaS, and data center infrastructure
  • Includes many advanced features and solutions at no additional cost
  • Provides AI-driven network insights and intelligent alerts
  • Products aren’t available a la carte
  • Customer service and technical support can be slow to respond
  • Isn’t entirely vendor-neutral

ThousandEyes

ThousandEyes is a digital experience monitoring platform primarily focused on network and application synthetic testing, end-user performance monitoring, and ISP Internet monitoring for SaaS, cloud, and on-premises networks. Additionally, ThousandEyes is part of the Cisco family and can be used to monitor and optimize Cisco SD-WAN architectures. Across its family of observability products, ThousandEyes includes features like wireless network visibility, SaaS performance visualizations, cloud application outage detection, and SD-WAN performance forecasting. The major advantage of the ThousandEyes platform is that it provides true end-to-end visibility of the entire service delivery chain, including end-user device performance and third-party provider availability. One downside is the endpoint agent-based monitoring solution requires on-premises VMs to run, which can be cumbersome to maintain and limits scalability. The pricing is expensive compared to similar solutions, and you may have to combine products to get all the features you need. Additionally, ThousandEyes is not a vendor-neutral platform and has a relatively small library of integrations.

Pros

Cons

  • Supports SaaS, cloud, and on-premises networks
  • Works with Cisco DNA software for SD-WAN monitoring
  • Provides end-to-end visibility of the entire service delivery chain
  • Agent-based monitoring requires on-premises VMs, limiting scalability
  • Pricing is expensive compared to similar solutions
  • Limited integrations, preventing interoperability

Conclusion

Each of the solutions on this list has advantages that make it well-suited to certain environments, as well as limitations to consider. Solarwinds NPM is part of a large ecosystem of observability and management solutions that includes advanced features like DPI, but it’s suffering from a major security incident and has a closed ecosystem. Kentik packs a lot of innovative, AI-driven monitoring capabilities into its platform offerings, but its pricing tiers are inflexible, and it doesn’t have the large, enterprise-grade support team of its larger competitors. ThousandEyes provides end-to-end visibility of the entire service delivery chain and works seamlessly with Cisco DNA software, but it has a steep learning curve and a limited library of integrations.

How to run the best network performance monitoring tools

Most network performance monitoring tools – even cloud-based SaaS offerings – communicate with endpoint agents using software deployed on VMs (virtual machines) running on-premises in each business location. Running these VMs on fully provisioned servers or PCs is expensive, but deploying them on NUCs is highly insecure, especially as organizations scale out with distributed branches and edge computing sites. What’s needed is a consolidated hardware solution that combines critical branch, edge, and data center networking functionality with vendor-neutral VM and application hosting, such as the Nodegrid platform from ZPE Systems. Nodegrid’s serial switches and network edge routers run the open, Linux-based Nodegrid OS, which can host your choice of third-party software – including Docker containers – for network performance monitoring, SD-WAN, security, automation, and more. Nodegrid’s versatile, modular hardware solutions also provide out-of-band (OOB) management access to critical remote infrastructure and monitoring solutions, giving teams a lifeline to recover from outages and ransomware attacks. Nodegrid uses innovative, enterprise-grade security features like Secure Boot, self-encrypted disk, and two-factor authentication (2FA), and its onboard software is frequently patched for vulnerabilities to defend against a breach. Deploying Nodegrid at each business site consolidates your network to reduce hardware overhead, streamlining management and enabling easy scalability.

Deploy the best network performance monitoring tools with Nodegrid

Reach out to ZPE Systems to see a demo of how the best network performance monitoring tools run on the Nodegrid platform.
Contact Us

OOB Network Management Software Tools

ZPE – Comparison-2(1)

Network management software tools enable administrators to provision, monitor, and maintain networks and network infrastructure without manually touching each individual device or service. We’ve previously covered the best network management software for both cloud-based and hardware-based networks. This post dives deeper into the hardware-based network management tools deployed in on-premises or private cloud environments via serial consoles (a.k.a. console servers, serial console servers, serial console routers, or serial switches).

These network management software tools provide out-of-band (OOB) management access to connected network infrastructure in data centers and remote sites. Serial consoles directly interface with network systems and devices, creating an isolated management network that doesn’t depend on the production LAN, WAN, or ISP. OOB management ensures continuous remote access even during major outages, so teams can troubleshoot and recover branch offices, edge computing sites, and other remote environments without costly truck rolls or managed service support. OOB console servers also unify management of all connected infrastructure, giving administrators a single platform to monitor, control, and automate the entire distributed network architecture.

Looking for a new out-of-band network management device? Read our guide: ​

Comparing the Best Out-of-Band Management Devices

We compare offerings from the four best OOB network management software tool providers and discuss the features, advantages, and disadvantages of each to help network teams make the best choice for their environment.

The best OOB network management software tools

Platform

Key Features

ZPE Systems Nodegrid Manager/ZPE Cloud

  • 5G/4G LTE, Wi-Fi, POTS, or fiber OOB and failover support

  • On-premises or cloud-based software options

  • Robust hardware and software security including 2FA and SAML 2.0

  • x86 CPU and Linux-based Nodegrid OS support Guest OS and Docker containers

  • Vendor-neutral software integrates with third-party tools like Ansible, Chef, Python, and Ruby

  • Extends ZTP and other automation to legacy and mixed-vendor infrastructure

  • OOB support over IPMI, ILO, DRAC, CIMC, vSerial, and KVM

  • Device auto-discovery via network scan and custom probes

  • Power management integrated with serial session

  • Supports full range of environmental monitoring sensors

Vertiv Avocent DSView

  • 4G LTE OOB and failover support

  • HTML5 KVM and Serial viewers

  • Telnet/PuTTY serial interfaces

  • Session log, report, and archive

  • Data Center Zone definitions

  • ZTP, SOAP API, Python, Perl, PDU, and UPS automation

  • Schedule and on-demand firmware management

  • Web secure 2048 SSL certificate

  • Two-factor authentication (2FA)

PerleVIEW

  • 4G LTE, Wi-Fi, POTS, or fiber OOB and failover support

  • Health monitoring and event handling

  • Integrates with SNMP NMS

  • Automated device discovery

  • Device CLI scripting

  • Configuration backup, firmware, and change management

  • Single sign-on for in-band connections

  • Device PING tool

  • Audit trail log

Opengear Lighthouse

  • 4G LTE or fiber for OOB and failover

  •  x86 processor can run Guest OSes and automation

  • Supports over 100 power vendors’ equipment

  •  Automatic port discovery

  • Lighthouse playbooks for streamlined automation

  • Integrated SAML and AAA authentication

  • Opengear NetOps modules support Bash, Docker, Pearl, Python, and Ruby

  • SSH direct to consoles

  • Keystroke logging 

Disclaimer: This comparison was written by a 3rd party in collaboration with ZPE Systems using data gathered from publicly available data sheets and admin guides, as of 10/13/2023. Please email us if you have corrections or edits, or want to review additional attributes: Matrix@zpesystems.com

ZPE Systems Nodegrid Manager/ZPE Cloud

ZPE Systems offers two network management software tools based on their Nodegrid line of serial consoles and integrated edge routers. Nodegrid Manager is on-premises software, and ZPE Cloud is a cloud-based tool, but both provide out-of-band management access to on-premises infrastructure in data centers, branches, private clouds, and other remote sites. Nodegrid hardware offers a variety of connectivity options for OOB, failover, and WAN, including Wi-Fi and 5G. Nodegrid also supports a full range of environmental monitoring sensors for greater control over conditions in remote deployments.

Nodegrid solutions are protected by robust hardware and software security features, including UEFI Secure Boot, an embedded firewall with selectable cryptographic protocols, and 2FA and SAML 2.0 authentication. The x86 CPU architecture and Linux-based OS support Guest OSes and Docker containers, so Nodegrid boxes can directly host third-party software for security, automation, orchestration. Both Nodegrid Manager and ZPE Cloud are also completely vendor-neutral, supporting third-party automation scripts and tools including RedHat Ansible, Chef, Python, Ruby, and more. Nodegrid can even extend ZTP and other automation to legacy infrastructure that otherwise wouldn’t support it.

Nodegrid’s open platform essentially makes it a customizable network management multi-tool that’s capable of consolidating many different software solutions and network services. The primary limitation to this vendor-neutrality is that some other providers may require the purchase of additional licenses to run their tools on the Nodegrid platform.

For a real-world example of Nodegrid’s ability to streamline network management, read our case study, Vapor IO: Re-architecting the Internet.
.

Pros

Cons

  • 5G/4G LTE, Wi-Fi, POTS, or fiber OOB and failover support

  • On-premises or cloud-based software options

  • Robust hardware and software security including 2FA and SAML 2.0

  • x86 CPU and Linux-based OS support Guest OS and Docker containers

  • Vendor-neutral software integrates with third-party tools like Ansible, Chef, Python, and Ruby

  • Extends ZTP and other automation to legacy and mixed-vendor infrastructure 

  • Other vendors may require additional licenses to run VNFs and other tools on Nodegrid

Vertiv Avocent DSView

The DSViewTM network management software works with Vertiv Avocent out-of-band serial consoles, the ACS 800 and ACS 8000, which use 4G LTE cellular for out-of-band management and failover. Like the other options on this list, DSView consolidates the management of connected network infrastructure in a single web-based platform. In addition to serial port control, this software also provides keyboard/video/mouse (KVM) and MIB-based (Management Information Base) controls. It also supports environmental monitoring via sensors, but ACS8000 serial console servers only come with one sensor port – and the ACS800 doesn’t have one at all.

DSView management software includes automation support for Zero Touch Provisioning (ZTP), SOAP API, Python, and Perl scripts, and automated PDU (power distribution unit) and UPS (uninterruptible power supply) management. It also provides console event logging and notifications, such as “dying gasp” alarms when systems unexpectedly lose power. However, the software is not extensible with third-party automation or orchestration integrations, and the ACS800 and ACS8000 serial console hardware solutions run on an ARM CPU architecture that can’t support VMs or Docker.
.

Pros

Cons

  • 4G LTE OOB and failover support
  • Environmental monitoring sensor support
  • ZTP, SOAP API, Python, Perl, PDU, and UPS automation
  • Serial, KVM, and MIB-based controls
  • FIPS 410-2 cryptography and 2FA security
  • No support for third-party automation or orchestration
  • Doesn’t run VMs or Docker containers
  • Serial console lacks an embedded firewall

PerleVIEW

PerleVIEW network management software tools are based on Perle’s IOLAN SCG & SCR OOB console servers. The platform includes automated device discovery, automatic event handling, device scripting, ZTP, and collection of device statistics and health statuses. Perle focuses on meeting the FCAPS network management framework created by the International Organization for Standardization (ISO). FCAPS standards for Fault management, Configuration, Administration, Performance management, and Security management, and PerleVIEW’s features target each of these areas. For example, fault management is streamlined through automated event handling with customizable alerts and SNMP probes.

However, the software does not support any third-party integrations, limiting its automation and security capabilities. Aside from automated device discovery and event handling, PerleVIEW doesn’t offer any automation for end devices. It also doesn’t support two-factor authentication (2FA), and only supports single sign-on (SSO) for in-band connections.
.

Pros

Cons

  • 4G LTE, Wi-Fi, POTS, or fiber OOB and failover support
  • Automated device discovery, event handling, health and device log collection, and device scripting
  • Integrates with SNMP NMS (network management station)
  • Single sign-on for in-band connections only
  • Follows FCAPS standards
  • No support for third-party automation or orchestration
  • Doesn’t run VMs or Docker containers
  • Lacks support for environmental monitoring sensors

Opengear Lighthouse

Lighthouse is a network management platform that works with Opengear console servers, such as the OM2200 Operations Manager and the CM8100. The base version of Lighthouse provides out-of-band management access, integrated SAML and AAA authentication, and integrations with third-party notification and alert systems. Lighthouse supports over 100 power vendors’ equipment to streamline PDU and UPS management, and the x86 processor can run Guest OSes and automation.

With additional licenses, Lighthouse software is extensible with Opengear NetOps modules that provide greater automation capabilities with support for Bash, Docker, Pearl, Python, and Ruby. The upgraded Automation edition also includes ZTP for end devices and RESTful APIs. Beyond that, however, automation and orchestration abilities are limited because Lighthouse isn’t vendor-neutral, and Opengear has a limited ecosystem of integrations.
.

Pros

Cons

  • 4G LTE or fiber for OOB and failover
  • Integrated SAML and AAA authentication
  • Supports over 100 power vendors’ equipment
  • x86 processor can run Guest OSes and automation
  • Opengear NetOps modules and ZTP available for automation
  • Only upgraded Automation edition supports ZTP for end devices
  • NetOps modules require additional licenses
  • Limited integration ecosystem

Key takeaways

All four options on this list provide out-of-band (OOB) access to remote network infrastructure, giving teams a lifeline in case of production failures or outages. Vertiv Avocent’s DSView software provides some automation capabilities and environmental monitoring, but doesn’t support third-party automation, VMs, or Docker containers. PerleVIEW focuses on meeting FCAPS network management standards but has very limited automation and security capabilities. Opengear Lighthouse is extensible with NetOps modules and other automation features, but they require additional licenses or fees, and you’re limited to Opengear’s ecosystem of integrations.

ZPE Systems offers Nodegrid Manager as an on-premises application or ZPE Cloud as a cloud-based tool. Both options use vendor-neutral hardware and software to create an open platform you can customize with your favorite third-party apps and integrations. ZPE’s OOB network management software tools enable end-to-end automation over a highly secure and reliable out-of-band control plane for a more resilient network infrastructure.


Deploy the best OOB network management software tools with ZPE Systems

Reach out to ZPE to learn how to build a resilient network with Nodegrid OOB network management software tools. Contact Us

Living Spaces Furniture: Scaling to 50 sites with only 3 network staff

Collapsing the stack and centralizing management helps Living Spaces accelerate scaling across the U.S.

Blake Johnson – Living Spaces Furniture Network Architect

“We’ve quadrupled business, but Nodegrid is actually shrinking our workload, especially as we implement new automation. It’s a gamechanger for network folks. Period.” — Blake Johnson, Network Architect, Living Spaces Furniture

Living Spaces is a prominent furniture retailer in the United States. Their store locations include large showrooms, where customers can view furnishings for indoor and outdoor spaces, and plenty of warehouse space for storing on-hand inventory. These locations must serve customers with responsive shopping experiences, which depend on the network infrastructure.

Increasing demand helped Living Spaces grow out of its home state of California, into states including Arizona, Colorado, Oklahoma, Texas, and others. Their out-of-band infrastructure was crucial to spinning up new locations and maintaining operations. But they faced a significant problem: this infrastructure was incredibly complex and costly, requiring many dedicated cellular and out-of-band devices at each location. See why their three-person network team needed a solution that could:

  • Reduce costs and eliminate the need for $300,000 per year in SIM contracts
  • Reduce workloads and risks, by centralizing management and minimizing entry points
  • Accelerate deployments by allowing automation

ISP Network Architecture

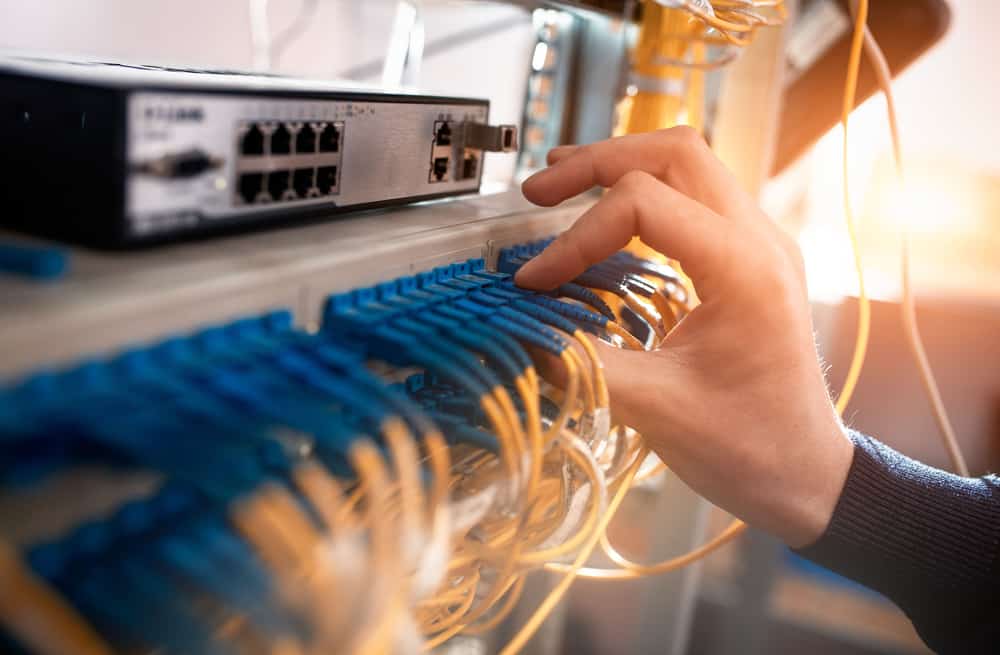
An engineer installs fiber optic patch cables at a customer site that’s part of an ISP network architecture.
Internet service providers (ISPs) are the backbone of modern society, responsible for connecting businesses, services, and people to the Internet and to each other. ISP networks are vast, distributed, and complex, making them challenging to manage effectively. However, failing to do so has major consequences. For example, in July of 2022, Rogers Communications in Canada suffered a network system failure after a maintenance update, causing an outage that lasted more than 15 hours and took down emergency services and other critical infrastructure.

An ISP network architecture must be designed for resilience to prevent major incidents from occurring that affect consumers, communities, and the provider’s reputation. But significant challenges stand in the way, including a reliance on legacy infrastructure, and an inability to troubleshoot and recover failed gear remotely. This post discusses why these challenges exist and what ISPs can do to overcome them.

ISP network architecture challenges

Many ISP networks lack resilience because providers are failing to adapt to a rapidly changing landscape. With networks growing larger and more complex every day, new technologies like AI (artificial intelligence) and software-defined networking are needed to manage infrastructure efficiently and deliver innovative services. Additionally, providers get stuck in a break-fix cycle that leaves teams struggling to maintain service level agreements or focus on innovation. Let’s look at the causes of these challenges and discuss how to build more resilient ISP network architectures.

Legacy infrastructure creates technical debt and hampers growth

The challenge:

The solution:

Reliance on legacy systems creates technical debt and prevents ISPs from implementing new technologies

Vendor-neutral platforms like Gen 3 serial consoles extend automation, software-defined networking, and other advanced technologies to legacy infrastructure until it can be replaced.

Internet service providers often have a network architecture that’s a mix of new and legacy infrastructure. However, engineers with the experience to support older solutions are no longer working in the field, either because they’ve been promoted to leadership positions or retired. When legacy hardware fails, inexperienced engineers need time to overcome this skills gap, and ISPs may even need to bring in consultants. This increases the cost of failures, creating what’s known as “technical debt” – when a solution is more expensive to support than the value it brings to the organization.

In addition, ISPs can improve network resilience and provide better service to customers, by adopting new technologies like AI, 5G, software-defined networking (SDN), and Network as a Service (NaaS). But legacy hardware hampers the ability to adopt these technologies. For example, NaaS abstracts the need for MPLS circuits and customer-premises gear, making architectures more cost-effective and improving the customer experience. NaaS brings SDN concepts like programmable networking and API-based operations to WAN & LAN services, hybrid cloud, Private Network Interconnect, and internet exchange points. It optimizes resource allocation by considering network and computing resources as a unified whole and attempts to automate as much as possible. The trouble is, ISPs struggle to implement NaaS and other beneficial new technologies because their legacy hardware simply can’t support it.

Solution: Legacy modernization with a vendor-neutral platform

The ideal solution is to replace legacy infrastructure with modern hardware and software that supports the latest technologies. But for many ISPs, an overhaul like this is too costly and intensive. The next-best option is to bridge the gap with a vendor-neutral network modernization platform that extends automation, AI, and 5G connectivity to otherwise unsupported systems.

For example, serial consoles (also known as terminal servers, console servers, and serial console switches) provide remote management access to network infrastructure. The newest generation of these devices, known as Gen 3, are vendor-neutral by design so that they can control third-party and legacy hardware. Through a combination of built-in features and integrations, Gen 3 serial consoles can use technology like zero-touch provisioning (ZTP), AIOps, and automated configuration management to control connected hardware that otherwise wouldn’t support it. Some solutions, such as the Nodegrid platform from ZPE Systems, can even directly host SDN and NaaS software from other vendors, so ISPs can start implementing network improvements right away while they gradually replace their outdated infrastructure.

Physical infrastructure is difficult to manage and troubleshoot remotely

The challenge:

The solution:

ISP network admins can’t respond to changing environmental conditions or recover failed hardware remotely

Environmental monitoring connected to an out-of-band (OOB) management solution ensures continuous remote access on a dedicated, isolated network that enables fast and cost-effective recovery.

ISP network architectures involve a great deal of physical infrastructure, which is often deployed in remote edge sites and customer premises. Even with software- or service-based network solutions, hardware is needed to host that software, and the physical environment for that hardware is often less than ideal. Drastic weather changes, power outages, and other unexpected scenarios can happen without notice and rapidly bring down an ISP network. These events often cut off remote management access as well, making troubleshooting and recovery difficult, time-consuming, and expensive. In fact, supporting this physical infrastructure often consumes so much time and effort that it prevents ISPs from focusing on delivering better services and software to their customers.

Solution: Out-of-band management with environmental monitoring

The first part of the solution involves monitoring the environment that houses remote, physical infrastructure. An environmental monitoring system uses sensors to detect changes in airflow, temperature, humidity, and other conditions that affect the operation of network hardware. These sensors give ISPs a virtual presence in edge deployments and customer sites so they can quickly respond to changing conditions before systems overheat or circuitry corrodes.

The second part involves providing management teams with reliable remote access to physical infrastructure that won’t go down if there’s a production network outage. Out-of-band (OOB) management solutions use serial consoles with dedicated network interfaces used just for management access. This creates a parallel, out-of-band network that’s completely isolated from production network services and infrastructure. Additionally, many serial consoles use cellular connectivity via 4G or 5G to OOB access, providing a wireless lifeline to connect, troubleshoot, and restore remote infrastructure. OOB management allows ISPs to troubleshoot and recover failed hardware remotely, even during total network outages, so they can get services back up and running faster and less expensively.

The environmental monitoring system should run on the OOB network so remote admins can continue to monitor conditions while they recover failed hardware. The out-of-band management solution also needs to be vendor-neutral so ISPs can deploy third-party automation, AI, and NaaS on the OOB network. For example, Nodegrid Gen 3 serial consoles provide OOB, environmental monitoring, and a vendor-neutral platform to host third-party software at the edge. Nodegrid even enables fully automated responses to changing environmental conditions in those edge environments before admins are aware of a problem.

To learn more about building a resilient, automated network infrastructure with Nodegrid, download the Network Automation Blueprint.

Download Now

ISP network architecture resilience with Nodegrid

ISP network architectures must be resilient, meaning service providers must find a way to bridge the gap between legacy and modern systems while ensuring continuous remote access to manage, troubleshoot, and recover hardware at the edge. The Nodegrid ISP network infrastructure solution  from ZPE Systems is a vendor-neutral, Gen 3 platform that delivers legacy modernization, environmental monitoring, out-of-band management, and much more.

Nodegrid delivers ISP network architecture resilience in a single platform

Request a free demo to see Nodegrid ISP network architecture solutions in action.

Watch a Demo