Providing Out-of-Band Connectivity to Mission-Critical IT Resources

Edge Management and Orchestration
shutterstock_2264235201(1)

Organizations prioritizing digital transformation by adopting IoT (Internet of Things) technologies generate and process an unprecedented amount of data. Traditionally, the systems used to process that data live in a centralized data center or the cloud. However, IoT devices are often deployed around the edges of the enterprise in remote sites like retail stores, manufacturing plants, and oil rigs. Transferring so much data back and forth creates a lot of latency and uses valuable bandwidth. Edge computing solves this problem by moving processing units closer to the sources that generate the data.

IBM estimates there are over 15 billion edge devices already in use. While edge computing has rapidly become a vital component of digital transformation, many organizations focus on individual use cases and lack a cohesive edge computing strategy. According to a recent Gartner report, the result is what’s known as “edge sprawl”: many individual edge computing solutions deployed all over the enterprise without any centralized control or visibility. Organizations with disjointed edge computing deployments are less efficient and more likely to hit roadblocks that stifle digital transformation.

The report provides guidance on building an edge computing strategy to combat sprawl, and the foundation of that strategy is edge management and orchestration (EMO). Below, this post summarizes the key findings from the Gartner report and discusses some of the biggest edge computing challenges before explaining how to solve them with a centralized EMO platform.

Key findings from the Gartner report

Many organizations already use edge computing technology for specific projects and use cases – they have an individual problem to solve, so they deploy an individual solution. Since the stakeholders in these projects usually aren’t architects, they aren’t building their own edge computing machines or writing software for them. Typically, these customers buy pre-assembled solutions or as-a-service offerings that meet their specific needs.

However, a piecemeal approach to edge computing projects leaves organizations with disjointed technologies and processes, contributing to edge sprawl and shadow IT. Teams can’t efficiently manage or secure all the edge computing projects occurring in the enterprise without centralized control and visibility. Gartner urges I&O (infrastructure & operations) leaders to take a more proactive approach by developing a comprehensive edge computing strategy encompassing all use cases and addressing the most common challenges.

Edge computing challenges

Gartner identifies six major edge computing challenges to focus on when developing an edge computing strategy:

Gartner’s 6 edge computing challenges to overcome

Enabling extensibility so edge computing solutions are adaptable to the changing needs of the business.

Extracting value from edge data with business analytics, AIOps, and machine learning training.

Governing edge data to meet storage constraints without losing valuable data in the process.

Supporting edge-native applications using specialized containers and clustering without increasing the technical debt.

Securing the edge when computing nodes are highly distributed in environments without data center security mechanisms.

Edge management and orchestration that supports business resilience requirements and improves operational efficiency.

Let’s discuss these challenges and their solutions in greater depth.

  • Enabling extensibility – Many organizations deploy purpose-built edge computing solutions for their specific use case and can’t adapt when workloads change or grow.  The goal is to attempt to predict future workloads based on planned initiatives and create an edge computing strategy that leaves room for that growth. However, no one can really predict the future, so the strategy should account for unknowns by utilizing common, vendor-neutral technologies that allow for expansion and integration.
  • Extracting value from edge data – The generation of so much IoT and sensor data gives organizations the opportunity to extract additional value in the form of business insights, predictive analysis, and machine learning training. Quickly extracting that value is challenging when most data analysis and AI applications still live in the cloud. To effectively harness edge data, organizations should look for ways to deploy artificial intelligence training and data analytics solutions alongside edge computing units.
  • Governing edge data – Edge computing deployments often have more significant data storage constraints than central data centers, so quickly distinguishing between valuable data and destroyable junk is critical to edge ROIs. With so much data being generated, it’s often challenging to make this determination on the fly, so it’s important to address data governance during the planning process. There are automated data governance solutions that can help, but these must be carefully configured and managed to avoid data loss.
  • Supporting edge-native applications – Edge applications aren’t just data center apps lifted and shifted to the edge; they’re designed for edge computing from the bottom up. Like cloud-native software, edge apps often use containers, but clustering and cluster management are different beasts outside the cloud data center. The goal is to deploy platforms that support edge-native applications without increasing the technical debt, which means they should use familiar container management technologies (like Docker) and interoperate with existing systems (like OT applications and VMs).
  • Securing the edge – Edge deployments are highly distributed in locations that may lack many physical security features in a traditional data center, such as guarded entries and biometric locks, which adds risk and increases the attack surface. Organizations must protect edge computing nodes with a multi-layered defense that includes hardware security (such as TPM), frequent patches, zero-trust policies, strong authentication (e.g., RADIUS and 2FA), and network micro-segmentation.
  • Edge management and orchestration – Moving computing out of the climate-controlled data center creates environmental and power challenges that are difficult to mitigate without an on-site technical staff to monitor and respond. When equipment failure, configuration errors, or breaches take down the network, remote teams struggle to meet resilience requirements to keep business operations running 24/7. The sheer number and distribution area of edge computing units make them challenging to manage efficiently, increasing the likelihood of mistakes, issues, or threat indicators slipping between the cracks. Addressing this challenge requires centralized edge management and orchestration (EMO) with environmental monitoring and out-of-band (OOB) connectivity.

    A centralized EMO platform gives administrators a single-pane-of-glass view of all edge deployments and the supporting infrastructure, streamlining management workflows and serving as the control panel for automation, security, data governance, cluster management, and more. The EMO must integrate with the technologies used to automate edge management workflows, such as zero-touch provisioning (ZTP) and configuration management (e.g., Ansible or Chef), to help improve efficiency while reducing the risk of human error. Integrating environmental sensors will help remote technicians monitor heat, humidity, airflow, and other conditions affecting critical edge equipment’s performance and lifespan. Finally, remote teams need OOB access to edge infrastructure and computing nodes, so the EMO should use out-of-band serial console technology that provides a dedicated network path that doesn’t rely on production resources.

Gartner recommends focusing your edge computing strategy on overcoming the most significant risks, challenges, and roadblocks. An edge management and orchestration (EMO) platform is the backbone of a comprehensive edge computing strategy because it serves as the hub for all the processes, workflows, and solutions used to solve those problems.

Edge management and orchestration (EMO) with Nodegrid

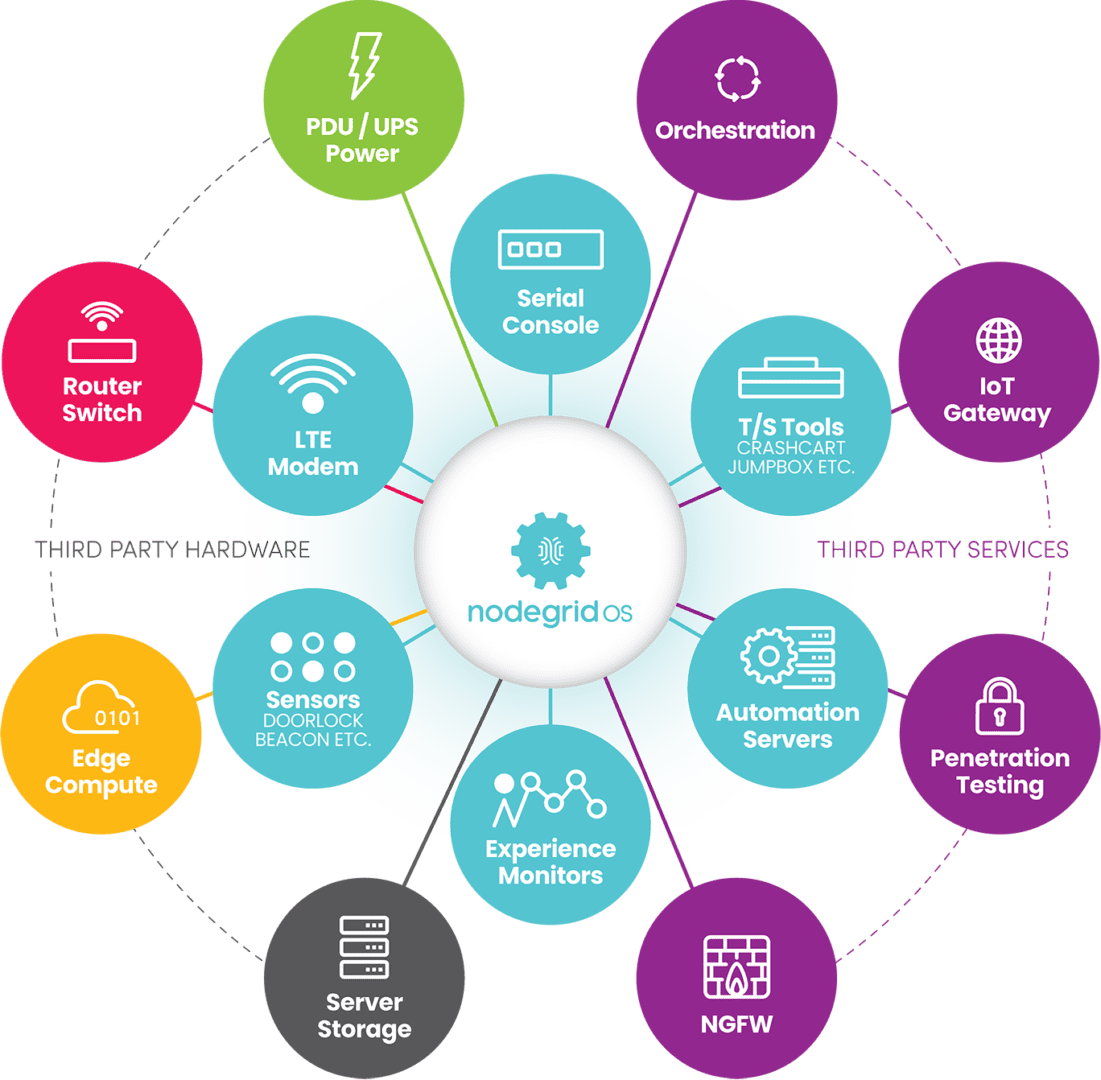
Nodegrid is a vendor-neutral edge management and orchestration (EMO) platform from ZPE Systems. Nodegrid uses Gen 3 out-of-band technology that provides 24/7 remote management access to edge deployments while freely interoperating with third-party applications for automation, security, container management, and more. Nodegrid environmental sensors give teams a complete view of temperature, humidity, airflow, and other factors from anywhere in the world and provide robust logging to support data-driven analytics.

The open, Linux-based Nodegrid OS supports direct hosting of containers and edge-native applications, reducing the hardware overhead at each edge deployment. You can also run your ML training, AIOps, data governance, or data analytics applications from the same box to extract more value from your edge data without contributing to sprawl.

In addition to hardware security features like TPM and geofencing, Nodegrid supports strong authentication like 2FA, integrates with leading zero-trust providers like Okta and PING, and can run third-party next-generation firewall (NGFW) software to streamline deployments further.

The Nodegrid platform brings all the components of your edge computing strategy under one management umbrella and rolls it up with additional core networking and infrastructure management features. Nodegrid consolidates edge deployments and streamlines edge management and orchestration, providing a foundation for a Gartner-approved edge computing strategy.

Want to learn more about how Nodegrid can help you overcome your biggest edge computing challenges?

Contact ZPE Systems for a free demo of the Nodegrid edge management and orchestration platform.
Contact Us

Intel NUC Use Cases

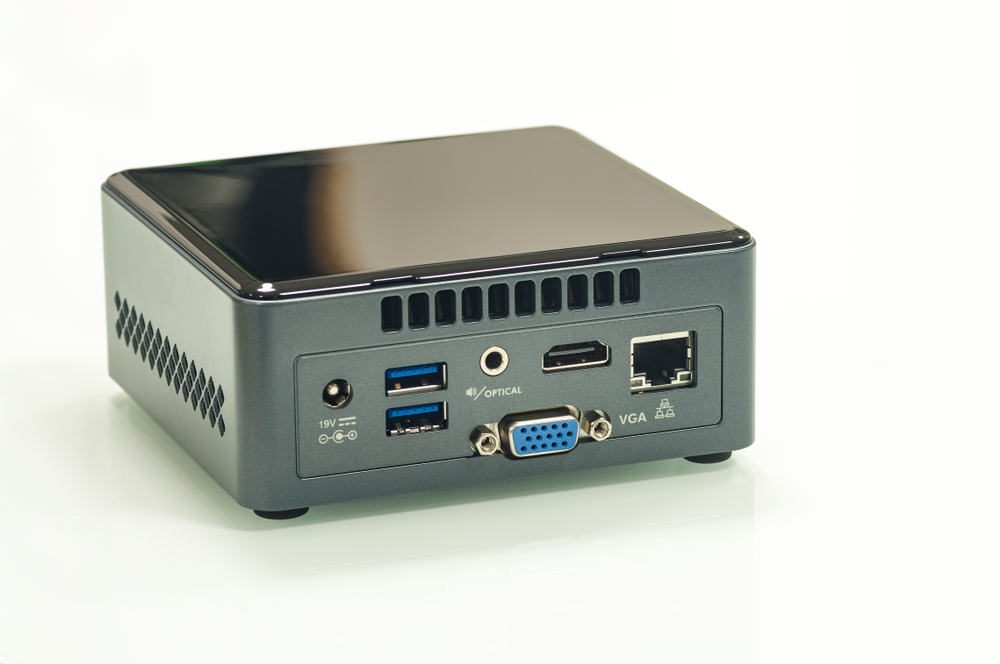
A mini-PC similar to an Intel NUC.

The Intel NUC, or “Next Unit of Computing,” is a small, appliance-like minicomputer that’s widely used across a variety of industries and applications. They’re tiny and relatively inexpensive, so you’ll often find them inside IoT devices and ruggedized cases. They’re also frequently deployed as jump boxes or service delivery appliances. However, Intel NUCs create added security risks, technical debt, and management headaches. Plus, Intel recently announced the discontinuation of all NUC product lines. This post describes some of the most common Intel NUC use cases, explains the security and management issues that caused its discontinuation, and provides superior replacement options.

Table of Contents

  1. Intel NUC use cases
  2. Intel NUC EOL products
  3. Why is Intel EOL-ing the NUC?
  4. Intel NUC replacement options from ZPE Systems
  5. Nodegrid product comparison
  6. Intel NUC replacement SKUs

Intel NUC use cases

While Intel NUCs have a dedicated fanbase among home enthusiasts, they’re primarily used by professional IT teams. Some popular Intel NUC use cases include:

  • Reducing carbon footprints: As investors place more importance on an organization’s environmental, social, and governance (ESG) practices, it becomes necessary to improve sustainability and reduce greenhouse gas emissions. Replacing inefficient PC towers with Intel NUCs can help reduce carbon footprints and improve ESG ratings.
  • Security and surveillance systems: An Intel NUC can run a wide range of security applications for things like entry control and surveillance cameras, eliminating the need for dedicated servers. Some IoT (Internet of Things) security devices have embedded Intel NUCs for greater mobility and efficiency.
  • Application delivery: Some service providers use Intel NUCs as platforms to deploy their software on-site to reduce hardware overhead costs. For example, a provider can install a NUC in their customer’s server room to deliver artificial intelligence (AI) or Software-as-a-Service (SaaS) applications.
  • Jump boxes: Managed Service Providers (MSPs) and Managed Security Service Providers (MSSPs) often deploy Intel NUCs at customer sites to act as “jump boxes” used to remotely access client infrastructure without taking up rack space.
  • Rugged computing: When services are needed out in the field, such as in military or construction applications, a traditional laptop may not be heavy-duty enough to withstand operating conditions. Some organizations solve this problem by running their services on Intel NUCs installed inside rugged cases designed for the environment.
  • Customized appliance computing: For specialized applications requiring a high degree of physical customization, such as law enforcement surveillance systems, an Intel NUC is often used because it’s small enough to fit nearly any case.

Intel NUC EOL products

Intel recently announced it’s discontinuing all NUC products, with specific dates for end-of-sale, end-of-support, and end-of-security-support varying by product. ASUS agreed to take over manufacturing and support of NUC product lines, but it’s unclear what the transition will look like or how ASUS will develop the NUC in the future.

Click here to view a list of all Intel NUC end-of-life SKUs as well as direct replacement options.

Why is Intel EOL-ing the NUC?

Despite all the exciting enterprise use cases listed above, the Intel NUC was never intended to be used as an appliance. It has numerous security and management limitations that make it challenging for Intel (and ASUS, in the future) to support the NUC for enterprise applications, including:

  • There’s no dedicated platform to deploy or secure NUC applications
  • Each Intel NUC is managed and accessed individually with no centralized management
  • Intel NUCs create a lot of technical debt because they require a lot of coding, API knowledge, and other specialized skills to work with
  • NUC operating systems are usually left out of patch schedules, leaving vulnerabilities critically exposed
  • There is usually no ability to recover a non-responsive NUC remotely, requiring expensive on-site visits any time there’s a network hiccup or OS crash
  • NUCs often don’t have the onboard hardware Roots of Trust (e.g., TPM) needed to secure them properly
  • The hardware NUCs are embedded in often have unclear or undocumented supply chains
  • There’s no ability for bidirectional authentication to the cloud with unique certificates
  • The production data and applications are on the same plane as management processes, leaving management ports exposed

Intel NUCs are a quick and inexpensive way to deploy applications, jump boxes, and digital services, which is what makes them so popular in enterprises. However, due to a lack of security features and centralized management, NUCs are also popular with cybercriminals looking for an easy target to exploit. With Intel discontinuing all NUC product lines, it’s the perfect opportunity to look for a replacement option that delivers the same cost-efficient flexibility but with enterprise-grade security and management features built in.

Intel NUC replacement options from ZPE Systems

Nodegrid is a family of all-in-one networking, application delivery, and infrastructure management devices from ZPE Systems. Nodegrid was built with security in mind, taking a three-pronged approach that includes:

  1. Hardware security – Onboard security features like TPM 2.0 and self-encrypted disk (SED) protect your device even if it falls into the wrong hands.
  2. Software security – Nodegrid protects its software using features such as BIOS protection and Signed OS, and it can host third-party security applications for an even stronger defense.
  3. Management security – Nodegrid keeps the management plane isolated from the data plane and uses strong zero-trust authentication methods to protect your management interfaces.

Nodegrid reduces management headaches without reducing security or functionality. ZPE provides enterprise-level support for all Nodegrid products with a responsive engineering team and 24-hour CVE (common vulnerabilities and exposures) patching. Nodegrid also lowers the technical debt and can meet teams at their skill level. You can deploy Nodegrid and use it to manage solutions that are already in place without any specialized programming or API knowledge.

Plus, Nodegrid uses out-of-band (OOB) management and serial connectivity to ensure continuous remote access to the control plane, making it a superior choice to an Intel NUC jump box for MSPs and MSSPs. With OOB connection options like 5G/4G LTE, teams can remotely troubleshoot and recover systems, services, and applications, even during major network outages. Management of all Nodegrid-connected infrastructure is unified by a single platform for streamlined control at any scale.

Due to its size, cost, and open, Linux-based operating system, Nodegrid is just as flexible and efficient as an Intel NUC while delivering the centralized management, robust security, and responsive support needed in enterprise deployments.

Learn more about replacing mini-computers with enterprise solutions:

Nodegrid product comparison

The entire family of Nodegrid edge solutions provides reliable OOB management and flexible service delivery capabilities protected by enterprise-grade security features. The Nodegrid Mini SR, Bold SR, and Gate SR are direct replacements for EOL Intel NUC models but offer so much more. Nodegrid is an entire Services Delivery Platform designed to streamline operations at any scale.


Mini SR

Bold SR

Hive SR

Gate SR

CPU

X86-64bit Intel 

X86-64bit Intel


X86-64bit Intel 

Cores

4

4 or 8

4 or 8

2, 4 or 8

Guest VM

1

1

1-3

1-3

Guest Docker

2+

2+

2+

2+

Storage

14GB SED

32GB – 128GB

32GB – 128GB

32GB – 128GB

Additional Storage

–

Up to 4TB

512GB

Up to 4TB

Wi-Fi

Yes

Yes

Yes

Yes

Cellular modem

1

1-2

1-2

1-2

5G

–

Yes

Dual 5G

Dual 5G

Sim slots

1

4

4

4

Serial Console Switch

Via USB

8

Via USB

8

Network

2x 1Gb ETH

5x Gb ETH

2x WAN (ETH/SFP)
2x SFP

4x 2.5Gb ETH

2x SFP
5x Gb ETH

4x 1Gb ETH PoE+

Data Sheet

Download

Download

Download

Download

To see first-hand why Nodegrid edge solutions are a superior choice for Intel NUC use cases, request a demo from ZPE Systems today.

Schedule a Demo

Intel NUC replacement SKUs

Intel NUC EOL SKU

In scope features

ZPE replacement product

Intel® NUC 11 Performance Kit NUC11PAHI70900

(Lenovo)

Multi-core Intel processor, expandable memory & SSD storage, Wi-Fi

ZPE-MSR24-W5

ZPE-MSR24-4G-W5

ZPE-MSR24-W5-EXT

ZPE-MSR24-4G-W5-EXT

ZPE-BSR-24a-W5

ZPE-BSR-24-4G-W5

ZPE-BSR-24-4G-W5-D128G

ZPE-BSR-48-W5

ZPE-BSR-48-4G-W5

ZPE-BSR-48-4G-W5-D128G

ZPE-GSR-48-W5

ZPE-GSR-48-4G-W5

ZPE-GSR-48-4G-W5-D128G

ZPE-GSR-816-W5

ZPE-GSR-816-4G-W5

ZPE-GSR-816-4G-W5-D128G

Intel® NUC 11 Pro Kit NUC11TNKv5

Intel® NUC 11 Pro Board NUC11TNBv5

Intel® NUC 11 Pro Board NUC11TNBv7

Intel® NUC 11 Pro Kit NUC11TNHv50L

Intel® NUC 11 Pro Kit NUC11TNKv7

Intel® NUC 11 Pro Kit NUC11TNHv7

Intel® NUC 11 Pro Kit NUC11TNHv70L

Intel® NUC 11 Pro Board NUC11TNBi3

Intel® NUC 11 Pro Board NUC11TNBi5

Intel® NUC 11 Pro Board NUC11TNBi7

Intel® NUC 11 Pro Kit NUC11TNKi3

Intel® NUC 11 Pro Kit NUC11TNKi5

Intel® NUC 11 Pro Kit NUC11TNKi7

Intel® NUC 11 Pro Kit NUC11TNHi30L

Intel® NUC 11 Pro Kit NUC11TNHi50L

Intel® NUC 11 Pro Kit NUC11TNHi70L

Intel® NUC 11 Pro Kit NUC11TNHi3

Intel® NUC 11 Pro Kit NUC11TNHi5

Intel® NUC 11 Pro Kit NUC11TNHi7

Intel® NUC 11 Pro Kit NUC11TNHi30P

Intel® NUC 11 Pro Kit NUC11TNHi50W

Intel® NUC 11 Pro Kit NUC11TNHi70Q

Intel® NUC 11 Pro Board NUC11TNBi30Z

Intel® NUC 11 Pro Board NUC11TNBi50Z

Intel® NUC 11 Pro Board NUC11TNBi70Z

Intel® NUC 11 Pro Kit NUC11TNKi30Z

Intel® NUC 11 Pro Kit NUC11TNKi50Z

Intel® NUC 11 Pro Kit NUC11TNKi70Z

Intel® NUC 11 Pro Kit NUC11TNKv50Z

Intel® NUC Kit, NUC11PAHi30Z

Intel® NUC Kit, NUC11PAHi50Z

Intel® NUC Kit, NUC11PAHi70Z

Intel® NUC 11 Enterprise Edge Compute NUC11TNHv50L

Intel® NUC 11 Enterprise Edge Compute NUC11TNHv70L

Intel® NUC 11 Pro Kit NUC11TNHi50Z

Multi-core Intel processor, expandable memory & SSD storage, Wi-Fi

ZPE-MSR24-W5

ZPE-MSR24-4G-W5

ZPE-MSR24-W5-EXT

ZPE-MSR24-4G-W5-EXT

ZPE-BSR-24a-W5

ZPE-BSR-24-4G-W5

ZPE-BSR-24-4G-W5-D128G

ZPE-BSR-48-W5

ZPE-BSR-48-4G-W5

ZPE-BSR-48-4G-W5-D128G

ZPE-GSR-48-W5

ZPE-GSR-48-4G-W5

ZPE-GSR-48-4G-W5-D128G

ZPE-GSR-816-W5

ZPE-GSR-816-4G-W5

ZPE-GSR-816-4G-W5-D128G

Intel® NUC Kit, NUC10i5FNHN

     (no cord, US cord, EU cord, AU cord, IN cord)

Intel® NUC Kit, NUC10i5FNKN

     (no cord, US cord, EU cord, AU cord, IN cord)

Intel® NUC Kit, NUC10i3FNHN

     (no cord, US cord, EU cord, AU cord, IN cord)

Multi-core Intel processor, expandable memory & SSD storage, Wi-Fi

ZPE-MSR24-W5

ZPE-MSR24-4G-W5

ZPE-MSR24-W5-EXT

ZPE-MSR24-4G-W5-EXT

ZPE-BSR-24a-W5

ZPE-BSR-24-4G-W5

ZPE-BSR-24-4G-W5-D128G

ZPE-BSR-48-W5

ZPE-BSR-48-4G-W5

ZPE-BSR-48-4G-W5-D128G

ZPE-GSR-48-W5

ZPE-GSR-48-4G-W5

ZPE-GSR-48-4G-W5-D128G

ZPE-GSR-816-W5

ZPE-GSR-816-4G-W5

ZPE-GSR-816-4G-W5-D128G

Intel® NUC11 Enthusiast Kit, NUC11PHKi7C, with Core™ i7, RTX 2060

     (no cord, US cord, EU cord, UK cord, AU cord, CN cord)

Multi-core Intel processor, expandable memory & SSD storage, Wi-Fi

ZPE-MSR24-W5

ZPE-MSR24-4G-W5

ZPE-MSR24-W5-EXT

ZPE-MSR24-4G-W5-EXT

ZPE-BSR-24a-W5

ZPE-BSR-24-4G-W5

ZPE-BSR-24-4G-W5-D128G

ZPE-BSR-48-W5

ZPE-BSR-48-4G-W5

ZPE-BSR-48-4G-W5-D128G

ZPE-GSR-48-W5

ZPE-GSR-48-4G-W5

ZPE-GSR-48-4G-W5-D128G

ZPE-GSR-816-W5

ZPE-GSR-816-4G-W5

ZPE-GSR-816-4G-W5-D128G

Intel® NUC Kit, NUC10i5FNHN

Intel® NUC Kit, NUC10i3FNHN

Multi-core Intel processor, expandable memory & SSD storage, Wi-Fi

ZPE-MSR24-W5

ZPE-MSR24-4G-W5

ZPE-MSR24-W5-EXT

ZPE-MSR24-4G-W5-EXT

ZPE-BSR-24a-W5

ZPE-BSR-24-4G-W5

ZPE-BSR-24-4G-W5-D128G

ZPE-BSR-48-W5

ZPE-BSR-48-4G-W5

ZPE-BSR-48-4G-W5-D128G

ZPE-GSR-48-W5

ZPE-GSR-48-4G-W5

ZPE-GSR-48-4G-W5-D128G

ZPE-GSR-816-W5

ZPE-GSR-816-4G-W5

ZPE-GSR-816-4G-W5-D128G

Intel® NUC Board NUC7PJYBN

Multi-core Intel processor, expandable memory & SSD storage, Wi-Fi

ZPE-MSR24-W5

ZPE-MSR24-4G-W5

ZPE-MSR24-W5-EXT

ZPE-MSR24-4G-W5-EXT

ZPE-BSR-24a-W5

ZPE-BSR-24-4G-W5

ZPE-BSR-24-4G-W5-D128G

ZPE-BSR-48-W5

ZPE-BSR-48-4G-W5

ZPE-BSR-48-4G-W5-D128G

ZPE-GSR-48-W5

ZPE-GSR-48-4G-W5

ZPE-GSR-48-4G-W5-D128G

ZPE-GSR-816-W5

ZPE-GSR-816-4G-W5

ZPE-GSR-816-4G-W5-D128G

Intel® NUC 11 Enthusiast Mini PC, w/ Core™

i7, RTX 2060, Optane™ Mem H10 

(32GB+512GB) Solid State Storage, 16G 

RAM, Windows® 10

     (No cord, US Cord, EU Cord, CN cord)

Multi-core Intel processor, expandable memory & SSD storage, Wi-Fi

ZPE-MSR24-W5

ZPE-MSR24-4G-W5

ZPE-MSR24-W5-EXT

ZPE-MSR24-4G-W5-EXT

ZPE-BSR-24a-W5

ZPE-BSR-24-4G-W5

ZPE-BSR-24-4G-W5-D128G

ZPE-BSR-48-W5

ZPE-BSR-48-4G-W5

ZPE-BSR-48-4G-W5-D128G

ZPE-GSR-48-W5

ZPE-GSR-48-4G-W5

ZPE-GSR-48-4G-W5-D128G

ZPE-GSR-816-W5

ZPE-GSR-816-4G-W5

ZPE-GSR-816-4G-W5-D128G

Intel® NUC 8 Rugged Kit NUC8CCHKRN (All SKUs)

Intel® NUC 8 Rugged Board NUC8CCHBN (All SKUs)

Multi-core Intel processor, expandable memory & SSD storage, Wi-Fi

ZPE-MSR24-W5

ZPE-MSR24-4G-W5

ZPE-MSR24-W5-EXT

ZPE-MSR24-4G-W5-EXT

ZPE-BSR-24a-W5

ZPE-BSR-24-4G-W5

ZPE-BSR-24-4G-W5-D128G

ZPE-BSR-48-W5

ZPE-BSR-48-4G-W5

ZPE-BSR-48-4G-W5-D128G

ZPE-GSR-48-W5

ZPE-GSR-48-4G-W5

ZPE-GSR-48-4G-W5-D128G

ZPE-GSR-816-W5

ZPE-GSR-816-4G-W5

ZPE-GSR-816-4G-W5-D128G

Intel® NUC Kit – NUC10i7FNHN

Intel® NUC Kit – NUC10i7FNKN

Multi-core Intel processor, expandable memory & SSD storage, Wi-Fi

ZPE-MSR24-W5

ZPE-MSR24-4G-W5

ZPE-MSR24-W5-EXT

ZPE-MSR24-4G-W5-EXT

ZPE-BSR-24a-W5

ZPE-BSR-24-4G-W5

ZPE-BSR-24-4G-W5-D128G

ZPE-BSR-48-W5

ZPE-BSR-48-4G-W5

ZPE-BSR-48-4G-W5-D128G

ZPE-GSR-48-W5

ZPE-GSR-48-4G-W5

ZPE-GSR-48-4G-W5-D128G

ZPE-GSR-816-W5

ZPE-GSR-816-4G-W5

ZPE-GSR-816-4G-W5-D128G

Intel® NUC Kit – NUC7CJYHN (All SKUs)

Intel® NUC Kit – NUC7PJYHN (All SKUs)

Multi-core Intel processor, expandable memory & SSD storage, Wi-Fi

ZPE-MSR24-W5

ZPE-MSR24-4G-W5

ZPE-MSR24-W5-EXT

ZPE-MSR24-4G-W5-EXT

ZPE-BSR-24a-W5

ZPE-BSR-24-4G-W5

ZPE-BSR-24-4G-W5-D128G

ZPE-BSR-48-W5

ZPE-BSR-48-4G-W5

ZPE-BSR-48-4G-W5-D128G

ZPE-GSR-48-W5

ZPE-GSR-48-4G-W5

ZPE-GSR-48-4G-W5-D128G

ZPE-GSR-816-W5

ZPE-GSR-816-4G-W5

ZPE-GSR-816-4G-W5-D128G

Intel® NUC 9 Pro Kit – NUC9VXQNX

Intel® NUC 9 Pro Compute Element – NUC9VXQNB

Intel® NUC 9 Pro Compute Element – NUC9V7QNB

Multi-core Intel processor, expandable memory & SSD storage, Wi-Fi

ZPE-MSR24-W5

ZPE-MSR24-4G-W5

ZPE-MSR24-W5-EXT

ZPE-MSR24-4G-W5-EXT

ZPE-BSR-24a-W5

ZPE-BSR-24-4G-W5

ZPE-BSR-24-4G-W5-D128G

ZPE-BSR-48-W5

ZPE-BSR-48-4G-W5

ZPE-BSR-48-4G-W5-D128G

ZPE-GSR-48-W5

ZPE-GSR-48-4G-W5

ZPE-GSR-48-4G-W5-D128G

ZPE-GSR-816-W5

ZPE-GSR-816-4G-W5

ZPE-GSR-816-4G-W5-D128G

Intel® NUC 12 Pro Kit NUC12WSKi50Z

Intel® NUC 12 Pro Kit NUC12WSHi50Z

Intel® NUC 12 Pro Kit NUC12WSKi70Z

Intel® NUC 12 Pro Kit NUC12WSHi70Z

Multi-core Intel processor, expandable memory & SSD storage, Wi-Fi

ZPE-MSR24-W5

ZPE-MSR24-4G-W5

ZPE-MSR24-W5-EXT

ZPE-MSR24-4G-W5-EXT

ZPE-BSR-24a-W5

ZPE-BSR-24-4G-W5

ZPE-BSR-24-4G-W5-D128G

ZPE-BSR-48-W5

ZPE-BSR-48-4G-W5

ZPE-BSR-48-4G-W5-D128G

ZPE-GSR-48-W5

ZPE-GSR-48-4G-W5

ZPE-GSR-48-4G-W5-D128G

ZPE-GSR-816-W5

ZPE-GSR-816-4G-W5

ZPE-GSR-816-4G-W5-D128G

Intel® NUC 9 Extreme Kit – NUC9i5QNX

Intel® NUC 9 Extreme Kit – NUC9i7QNX

Intel® NUC 9 Extreme Kit – NUC9i9QNX

Multi-core Intel processor, expandable memory & SSD storage, Wi-Fi

ZPE-MSR24-W5

ZPE-MSR24-4G-W5

ZPE-MSR24-W5-EXT

ZPE-MSR24-4G-W5-EXT

ZPE-BSR-24a-W5

ZPE-BSR-24-4G-W5

ZPE-BSR-24-4G-W5-D128G

ZPE-BSR-48-W5

ZPE-BSR-48-4G-W5

ZPE-BSR-48-4G-W5-D128G

ZPE-GSR-48-W5

ZPE-GSR-48-4G-W5

ZPE-GSR-48-4G-W5-D128G

ZPE-GSR-816-W5

ZPE-GSR-816-4G-W5

ZPE-GSR-816-4G-W5-D128G

Want to learn more about replacing your Intel NUC with Nodegrid?

Ready to replace your Intel NUC with a Nodegrid alternative? Call ZPE Systems today at 1-844-4ZPE-SYS or contact us online.

Contact Us

IT Infrastructure Management Challenges

Stop,Falling.,Save,Falling,Economy,Business,Vector,Illustration.

Modern IT infrastructure management is defined by the struggle to keep an increasingly complex architecture of critical business services running 24/7 without interruption. According to a recent report from Siemens, a single hour of unplanned downtime could cost businesses anywhere from $39,000 to $2 million. The ability to maintain continuous business operations and recover from outages with minimal disruption is known as network resilience, and it should be the top priority for any organization. Infrastructure teams face numerous challenges on their path to creating resilience, including management complexity, cybersecurity threats, vendor lock-in, bloated tech stacks, and poorly supported legacy devices. This post analyzes the top 5 IT infrastructure management challenges while providing potential solutions and additional resources.

Table of Contents

The top 5 IT infrastructure management challenges & solutions:

1. Challenge: Increasing complexity

As organizations evolve their capabilities and service offerings with advanced technology like artificial intelligence (AI), the supporting infrastructure grows more complex. For example, microservice applications are extremely agile and allow software teams to deliver advanced, high-performance products very quickly and efficiently. Building and maintaining the containerized environments, network logic, and security architecture to host and support those applications is difficult and prone to human error. A lot of human error occurs during tedious, repetitive tasks like device security configurations. These mistakes are the cause of up to 35% of cybersecurity incidents, so minimizing human error is critical to network resilience.

Solution: Network automation

Tedious IT infrastructure and network management workflows are perfect candidates for automation. For example, zero touch provisioning (ZTP) turns network device configurations into software code, allowing admins to pre-write configuration files that can be tested and verified before deployment. Teams can ship factory-condition devices to remote data centers and branches, where a non-expert plugs the device into power and networking. As soon as the device connects to DHCP, it downloads its ZTP configuration file and automatically configures itself. ZTP significantly reduces human intervention in the deployment process, which minimizes the risk of errors. Devices with accurate security configurations are less likely to contain vulnerabilities. In addition, automating tasks like patch management will further reduce vulnerabilities, improving network resilience.

Back to Top

To learn how ZTP and automated deployments can shrink deployment times, download this Vapor IO case study.

Download Now

2. Challenge: Ransomware

Ransomware attacks on businesses are so frequent that many organizations consider them inevitable, and Gartner calls ransomware the modern disaster. Standard ransomware takes over the network and encrypts all of an organization’s data until the ransom is paid, bringing operations to a screeching halt. Newer attacks, such as the Cl0p MOVEit breach currently affecting Shell and other major energy companies, use randomware tactics to harvest sensitive data for ransom. Ransomware attacks often start with social engineering tactics that are difficult to prevent with security technology alone. Once the network is infected, ransomware is nearly impossible to stop and difficult to recover from without reinfecting backup data and systems. While there are many other types of cybersecurity threats, ransomware’s frequency and business impact make it one of the biggest IT infrastructure management challenges.

Solution: Isolated management infrastructure

Network micro-segmentation, Zero Trust security policies, advanced authentication methods, and other security controls help prevent some attacks and can limit the blast radius of others. However, there’s no way to ensure 100% protection, so organizations should focus instead on building a comprehensive recovery architecture to decrease downtime and reduce the risk of reinfection. This can be done using something called Isolated Management Infrastructure (IMI). An isolated management infrastructure using out-of-band (OOB) serial consoles gives teams a dedicated control plane that’s separate from the production network. This creates an isolated recovery environment where they can rebuild systems, restore data, and perform security validation without the risk of reinfection undoing their efforts. It also takes management interfaces off the production network as mandated by a recent CISA binding directive. An IMI improves resilience by speeding up recovery times so business can resume faster.

Back to Top

For more help building ransomware resilience, download our 3 Steps to Ransomware Recovery whitepaper.

Download Now

3. Challenge: Lack of integration & vendor freedom

Most IT infrastructure is a mix of features and services provided by different vendors, each with its own software and interface used to manage them. Some IT infrastructure management teams compromise on features, security, redundancy, etc., to stay in their vendor’s ecosystem, which makes it difficult to build a custom-fit network. Many teams opt instead to manage each vendor solution separately with little interoperability. This lack of integration makes centralized orchestration especially challenging. A fragmented view of networks and infrastructure makes it difficult to spot systemic issues or signs of compromise. Managing solutions individually is inefficient and tedious, which increases the risk of human error. In fact, organizations wait an average of 205 days to patch systems because they’re afraid an update will break their operations. Vendor lock-in is a significant hurdle on the path to network resilience.

Solution: Vendor-neutral platforms

Flexibility and agility are key here; enterprises need to adopt a network infrastructure that can accommodate their exact needs and adapt when those needs change. Teams also need centralized orchestration of the entire multi-vendor architecture. This requires a vendor-neutral infrastructure management platform that can dig its hooks into any solution on your network. For example, OOB serial consoles running open, Linux-based operating systems offer unified management of mixed-vendor infrastructure. Some solutions can even host third-party software for SASE, NGFWs, and other network and security services. Administrators get a single centralized management platform that provides 360-degree visibility and control, improving security coverage and reducing human error. This OOB platform also creates the isolated management infrastructure described above. The IMI itself is a vendor-neutral platform that allows for safe management, including applying patches and deploying automation. This platform also provides an “undo button” in case mistakes are made. That way, teams don’t need to be afraid of breaking their own systems while applying necessary updates.

Back to Top

4. Challenge: Overwhelming tech stacks

IT managers working with an enterprise network have a massive variety of equipment and software to work with to make their networks function efficiently. These solutions often include, but are not limited to,

  • Servers, switches, and routers
  • Out-of-band management hardware
  • Firewalls and other security solutions
  • Data backup and configuration devices
  • Cellular failover boxes

Each new solution added to the network must be secured, monitored, maintained, and patched. Keeping track of vulnerabilities and patch schedules for so many devices and applications is challenging, but unpatched infrastructure is risky to network security and resilience. All these moving parts are potential points of failure, so keeping them functioning and optimally performing is critical. Still, it’s difficult to be proactive about maintenance with so many disparate solutions to keep track of.

Solution: Consolidated infrastructure

There are three ways to overcome this IT infrastructure management challenge. In the previous section, we discussed how a vendor-neutral platform streamlines the management of multi-vendor devices, which also helps infrastructure teams stay on top of patch schedules and maintenance. Before that, we mentioned automation as a way to reduce complexity, but it also helps reduce maintenance workloads. For example, automated infrastructure monitoring solutions keep track of software versioning information and alert teams when vendors announce vulnerabilities or release patches. Some solutions also employ machine learning and artificial intelligence to analyze monitoring data, predict potential issues, and suggest optimal maintenance schedules. The third method uses converged infrastructure solutions that combine many different functions in a single device or platform. For example, you can deploy an integrated branch router that rolls up network functions, out-of-band management, security, and cellular failover in a single box. Some vendor-neutral solutions let you host third-party software as well, so you can add application delivery, SASE, configuration management, and more.

A 3-pronged approach to simplifying tech stacks
  1. Vendor-neutral management platforms
  2. Automated infrastructure monitoring & maintenance
  3. Converged infrastructure solutions

This three-pronged approach to infrastructure management helps streamline the tech stack to improve network performance and resilience.

Back to Top

5. Challenge: Legacy infrastructure

As providers modernize and upgrade their service offerings, older devices fall out of support. These “legacy devices” are outdated and incapable of integrating with modern software by themselves. As a result, they slow down workflows and inhibit automation efforts. Legacy devices pose significant security risks since the vendor no longer patches new vulnerabilities. Despite their inherent flaws, enterprises insist on using legacy systems, citing staff familiarity, high replacement costs, and potential service disruptions as reasons for keeping them around. For example, 53% of healthcare devices still operate on Windows 7, which Microsoft no longer supports. Unless those devices are updated, they cannot be properly secured.

Solution: Legacy modernization platforms

When replacing legacy devices is impossible, the next best option is to bring them on board your modern IT management platform. For example, some serial consoles use auto-sensing ports to automatically detect legacy devices and integrate them under the same management umbrella as newer systems. A vendor-neutral legacy modernization platform like Nodegrid can even push automation to older devices that otherwise wouldn’t be supported. This reduces the friction created by older infrastructure, so administrators can incorporate them into their automated workflows. Nodegrid also extends security coverage – including modern Zero Trust solutions and automated security monitoring – to legacy devices to ensure there are no gaps. Legacy modernization with the Nodegrid platform improves network resilience without the disruption of an infrastructure upgrade.

Back to Top

Solving IT infrastructure management challenges with ZPE Systems

All the biggest IT infrastructure management challenges revolve around network resilience. Automation, security solutions, vendor-neutral platforms, and legacy modernization help reduce the frequency of outages, but for true resilience, organizations must be able to recover from the outages that do occur and get services up and running as quickly and possible to minimize the impact of downtime on revenue and reputation. An isolated management infrastructure using Gen 3 out-of-band serial consoles provides a dedicated control plane for troubleshooting and recovery operations. For example, using Nodegrid OOB management solutions from ZPE Systems, teams get 24/7 access to remote infrastructure even during network outages and ransomware attacks. This OOB network provides a safe environment to restore and rebuild systems, applications, and data without the risk of reinfection. Nodegrid is a vendor-neutral infrastructure orchestration platform that brings all your mixed-vendor and legacy systems together under a single management umbrella. Nodegrid’s Linux-based OS extends automation and security coverage to outdated equipment to streamline workflows and provide a 360-degree view of the entire architecture.

Need more help to overcome Solving IT infrastructure?

To learn more about how the Nodegrid platform solves your IT infrastructure management challenges, contact ZPE Systems today. Contact Us

What is a radio access network (RAN)?

This post provides an introduction to radio access networks (RAN) before discussing 5G RAN challenges, solutions, and use cases.
5G cellular technology is used for internet of things (IoT) deployments and operational technology (OT) automation across many different kinds of organizations, including city governments, global logistics companies, and healthcare providers. 5G access is provided by a radio access network (RAN) using mobile towers and small cells, but deploying these networks is challenging due to numerous factors, including poor public opinion. This post provides an introduction to radio access networks before discussing 5G RAN challenges, solutions, and use cases.

Table of Contents:

What is a Radio Access Network (RAN)?

A radio access network (RAN) is the portion of a cellular network that connects smartphones and other end-user devices to the internet. Information is communicated back and forth between smartphones and the RAN’s transceivers via radio waves. Those wireless signals are translated into digital form, passed to the core network, and then to the global internet.

What is 5G RAN?

Every cellular generation has its own associated RAN technology. 4G RAN was the first generation based entirely on the internet protocol (IP) rather than older circuit-based technology. The newest generation, 5G, supports faster speeds, great capacity, and lower latency than previous generations. However, there are significant challenges in the way of 5G implementation.

5G Radio Access Network (RAN) challenges

There are three major hurdles to 5G implementation:

  1. Public opinion – Thanks in part to misinformation and conspiracy theories, there has been a lot of resistance to 5G implementations. While many people already use smartphones with 5G technology, they tend to balk at the idea of giant cell towers and masts going up in their town or city.
  2. mmWave limitations – Wireless frequencies in the mmWave (millimeter wave) spectrum provide the speed and capacity required for 5G, but they have a shorter range and difficulty penetrating walls. That makes 5G tricky in industrial settings and office buildings.
  3. Remote recovery – A 5G RAN typically operates in cramped spaces without a continuous human presence, and administrators monitor and manage the equipment remotely over the cellular network. However, if that cell link goes down due to equipment failure or natural disaster, teams are cut off, and a truck must be rolled to fix the issue, adding significant costs and downtime.

Addressing these hurdles is complicated, as the solutions often create additional challenges. For example, the first two points can be addressed with 5G small cell technology. Small cells are typically compact enough to deploy on top of buildings or street furniture to extend 5G coverage into densely populated areas without a full-size mobile mast. This makes 5G small cell networks more palatable to city officials and the general public alike. However, small cells are still subject to planning restrictions, and the absence of a common 5G small cell framework makes the application process difficult and time-consuming.

In addition, some small cells are tiny enough to deploy indoors, improving 5G propagation and coverage in buildings. However, operators would need to deploy dozens or hundreds of small cells to achieve the speed and reliability needed for industrial IoT and high-tech use cases. Each one requires significant power resources as well as a fiber or wireless backhaul, and due to a lack of standardization, operators may even have to submit many individual planning applications. Plus, a small cell network of that size is complex to monitor and manage, requiring additional hardware and software solutions that add even more costs and complexity.

Addressing the third point requires an out-of-band network connection to 5G RAN deployments. For example, a 4G/LTE serial console provides an alternative internet connection so teams can remotely access RAN equipment during 5G outages. A serial console directly connects to radio access network infrastructure so remote administrators can do things like reboot a hung device or refresh DHCP even if the local network is down.

However, many serial consoles suffer from vendor lock-in, meaning they don’t connect to all devices or support third-party management, troubleshooting, and recovery tools. This either limits an administrator’s ability to remotely recover from outages or forces them to deploy additional hardware and software solutions to gain all the remote functionality required, adding to the expense and complexity of 5G RAN deployments.

A new approach to 5G deployments

The upgrade from 4G to 5G is proving to be more fraught than previous transitions between generations, so it’s clear that a new approach is needed. Small cell technology is a good start, but a lack of standardization severely hampers its adoption. Help is on the way, though – a group called the Small Cell Forum (SCF), which is made up of wireless leaders like AT&T, Cisco, Qualcomm, and Samsung, is working to establish a set of common definitions and recommendations to help the industry standardize 5G small cell networks.

In their definitional report, the SCF highlights the need for vendor-neutral hardware that’s customizable and swappable for various 5G use cases. Architectural design and planning applications are simpler when all of a small cell network’s equipment supports the same common 5G interface. Multi-functional devices combining networking, out-of-band access, and third-party application hosting significantly reduce expenses and management complexity.

Let’s examine some potential 5G use cases that could benefit from this new approach.

Smart cities

A smart city is the ideal use case for a 5G small cell network. Since wireless clients are packed into densely populated areas, an array of 5G small cells should provide sufficient coverage without the need for a full-sized mast. Deploying a small, vendor-neutral, multi-functional device like the Nodegrid Mini Services Router alongside small cells provides flexible backhaul options, out-of-band remote management, and application hosting. Installing small cells and Mini SRs on streetlamps, parking structures, and other public infrastructure gives teams everything they need to remotely monitor, operate, and recover 5G smart city infrastructure without adding more complexity to the network.

Global asset tracking and logistics

The internet of things (IoT) makes it possible for large, global enterprises to streamline asset tracking and supply chain logistics. Organizations use IoT-enabled devices to handle inventory management, fulfillment, shipment tracking, quality control, and more. 5G small cell technology provides the necessary speed, coverage, and bandwidth, but the sheer number of devices – and their global distribution – creates a lot of management complexity.

All-in-one solutions like Nodegrid reduce the tech stack by combining networking, management, and application hosting in a single box. Plus, Nodegrid provides a centralized management platform that can unify all connected devices, apps, and services in a single place. Administrators get a single pane of glass to monitor, control, troubleshoot, and automate the entire global architecture, reducing costs and streamlining operations.

Building automation

Many large property management companies rely on building automation systems that use operational technology (OT) to control door locks, lighting, HVAC, and more with very little human intervention. 5G’s improved speed and lower latency open up even greater automation capabilities, especially in warehouses and manufacturing plants.

Nodegrid’s compact, vendor-neutral solutions give remote operators a reliable, out-of-band connection to automated building systems to keep businesses running 24/7, even during 5G outages or LAN failures. You can deploy the Mini SR in cramped or semi-outdoor spaces to extend monitoring, security, and management coverage to every part of the 5G deployment. Nodegrid enables end-to-end building automation and makes 5G networks more resilient to failure.

Simplifying 5G with Nodegrid

A 5G radio access network (RAN) provides internet access to 5G-enabled systems, such as smartphones and IoT devices. While 5G deployments are proving complicated and fraught with issues, these challenges are overcome using small cell technology and vendor-neutral, multi-function devices like Nodegrid. Nodegrid’s integrated services routers deliver all-in-one networking, out-of-band management, backhauling, and application hosting capabilities to simplify 5G deployments without compromise.

Learn how Nodegrid can help deliver simplified 5G with out-of-band management!

Request a free Nodegrid demo to see how vendor-neutral solutions simplify 5G radio access network (RAN) deployments.

Contact Us

SSE Magic Quadrant: Key Takeaways of the 2023 Report

The SSE Magic Quadrant describes top cloud security service vendors, conceptualized as a cloud with glowing network nodes and a padlock.

Gartner’s SSE Magic Quadrant for 2023 identifies 10 key vendors currently providing secure service edge capabilities for the enterprise market. In this guide, we’ll summarize the common factors shared among leading SSE vendors, discuss what separates them from niche players, and share advice for connecting your edge network to SSE solutions via an SD-WAN on-ramp.

Table of Contents:
  1. What is Security Service Edge (SSE)?
  2. What is the need for SSE?
  3. What is the SSE Magic Quadrant?
  4. What has changed since the 2022 SSE Magic Quadrant?
  5. Key takeaways from the 2023 SSE Magic Quadrant
  6. SD-WAN: An on-ramp for SSE
  7. What to look for in an ideal SSE on-ramp
  8. Why Nodegrid is the ideal SSE on-ramp

What is Security Service Edge (SSE)?

Security service edge (SSE) is a cloud-centric security methodology for protecting edge network traffic. It rolls up technologies like Firewall-as-a-Service (FWaaS), Zero Trust Network Access (ZTNA), and Cloud Access Security Brokers (CASB) into a single service. These technologies offer threat protection, security monitoring, access control, and data governance.

What is the need for SSE?

With the frequency and severity of ransomware attacks and other cybercrimes increasing daily, security is a major priority for any organization. To protect your enterprise from cyber threats, you need to be able to extend your security policies and controls to all the remote and geographically distributed systems at your network edge. Historically, that meant backhauling all remote traffic through your primary firewall, which would inevitably cause performance issues for everyone on the network. This is frustrating and can greatly impact the business when much of your remote traffic is destined for cloud and web resources that aren’t even on your enterprise network.

SSE solves this problem by taking advanced enterprise security technologies and making them available as a cloud-based service. You can use SD-WAN with intelligent routing (more on that later) to send remote and branch office traffic through your SSE stack. This allows you to apply consistent policies and controls to your enterprise and edge traffic while reducing bottlenecks and increasing overall network performance.
.

Learn more about SSE:

Gartner’s 2023 SSE Magic Quadrant Summarized

Challengers

Leaders

Cisco (SIG)

Netskope
Zscaler
Palo Alto Networks (Prisma Access)

Niche Players

Visionaries

Broadcom
iboss
Cloudflare

Skyhigh Security
Forcepoint (Bitglass)
Lookout

There are many reasons why an SSE vendor would be considered a niche player, including that the market hasn’t caught on to them yet due to poor marketing or sales strategies. However, one common caution among niche players is a failure to fully integrate SSE components, which means customers must use multiple dashboards to manage a single SSE solution. Another common issue is poor support during sales, implementation, and operation, leading to frustration among enterprises with less experience in edge networking and security.

On the other hand, the leaders of the SSE Magic Quadrant share a few common characteristics as well. For one, they have strong marketing and sales outreach, a clear vision, and a roadmap for the future. This vision is essential because it allows enterprises to ensure their goals and strategies align with where their SSE vendor is headed.

In addition, these solutions’ components are tightly integrated with a single, unified management platform for more accessible and efficient operation. Magic Quadrant leaders invest in and implement new security features frequently, bug-free, and with adequate documentation and support. That means customers can stay ahead of emerging security threats without worrying about breaking their existing setups.

What has changed since the 2022 SSE Magic Quadrant?

There are three major changes to Magic Quadrant this year.

  • Palo Alto Networks moves from Challenger to Leader: In 2022, Palo Alto extended its Prisma Access SSE solution to better integrate with Prisma SD-WAN, enhance its proxy and ZTNA components, and add SaaS Security Posture Management (SSPM).
  • McAfee splits its cloud business into Skyhigh Security: Early in 2022, McAfee enterprise split into two, with its cloud business now known as Skyhigh Security. This split disrupted Skyhigh’s growth and market share and moved this SSE offering from the Leaders quadrant to the Visionaries quadrant.
  • Versa leaves the SSE Magic Quadrant: Versa no longer ranks in the top 20 organizations in Gartner’s market momentum index (MMI), so it isn’t included in the 2023 Magic Quadrant.

Key takeaways from the 2023 SSE Magic Quadrant

  • Most vendors prioritized improving their core capabilities and better integrating their product, rather than focusing on new features and other innovations.
  • Vendors who fail to fully integrate their SSE offering into a unified platform are quickly losing market share.
  • WFH traffic is less of a concern for enterprises than branch/edge sites, so SD-WAN access and integrations are critical.

Overall, the biggest takeaway from the SSE Magic Quadrant is the importance of a seamlessly-integrated platform. A consolidated platform ensures complete visibility and control over your security service edge solution without needing to learn and operate multiple consoles.

On top of this, to use SSE’s cloud-delivered solution, you need a reliable way to send traffic from your branch and edge locations to the SSE stack. That means part of the architecture needs to include an access solution that can tunnel traffic from these locations to the cloud, such as SD-WAN. The access solution serves as an on-ramp to SSE, and requires a physical appliance for on-premises installations. This framework combining SD-WAN access with SSE is how SASE (secure access service edge) is built.

SD-WAN: An on-ramp to SSE

Security service edge provides the technology to protect your edge-based cloud-destined traffic, but you still need a way to get that traffic to your SSE platform. This is known as an SSE on-ramp, and it’s not included in any of the SSE Magic Quadrant solutions. However, one of Gartner’s selection criteria was the ability to integrate with SD-WAN technology.

An SSE on-ramp uses SD-WAN (software-defined wide area network) technology to route remote and branch office traffic to your SSE stack in the cloud. SD-WAN separates the control and management processes from your underlying WAN hardware and virtualizes them as software, making it possible to centrally control and orchestrate even very complex and distributed WANs. With SD-WAN, you can use intelligent and application-aware routing to connect your edge users directly to the SSE platform, cloud, and web resources.

What to look for in an ideal SSE on-ramp

The ideal on-ramp to SSE will support seamless integration with your SSE platform, and vice-versa. In addition, the right solution will provide additional capabilities like the ones listed below.

Features of an ideal SSE on-ramp include:

Versatile tunneling

Physical hardware that’s easy to provision with a versatile tunnel mechanism to SSE, including IPsec and WireGuard, with simple cloud management. Ideally this tunneling mechanism uses application-aware traffic steering to make it an effective part of an SD-WAN on-ramp.

Integrated L3/L4 firewall

Integrated Layer 3/Layer 4 firewall technology to secure incoming traffic to your remote and branch locations, including VPN support. The ideal on-ramp has local segmentation capabilities and zero-trust, since SSE can’t do local segmentation on its own without help from on-premises equipment, agents, or VMs.

Out-of-band (OOB) management

OOB management for a direct, dedicated network connection to the SD-WAN on-ramp that doesn’t rely on cloud-based in-band connectivity. OOB access and provisioning are ideal to gain greater control over remote networking infrastructure on a dedicated connection.

Multiple WAN interfaces

Flexible and redundant WAN interfaces to ensure 24/7 availability. At least one of these should include a 5G/4G LTE modem with 2 SIM slots for high-speed cellular failover and out-of-band access when the primary WAN link is down.

Terminal server

Terminal server/serial console/”jump box” port management for easy remote management of edge infrastructure. This should include the ability to host third-party troubleshooting tools so admins can easily recover from outages without going on-site.

Computing power

Compute capabilities to run third-party apps and Docker containers right at the network edge. With built-in compute it’s easier to extend the functionality of SSE with additional applications that may not be part of the SSE stack or need an edge Docker footprint, like vulnerability scanning or user experience monitoring agents.

Centralized automation

Unified management of automation like Zero Touch Provisioning (ZTP) to automatically spin-up edge devices and connect them to SSE. Automation can significantly speed up branch deployments while reducing the risk of human error.

Why Nodegrid is the ideal SSE on-ramp

The Nodegrid branch and edge networking solution from ZPE Systems combines all the capabilities of the ideal SSE on-ramp in a single platform. For example, the Nodegrid Net Services Router (NSR) is a customizable, all-in-one device with available modules for storage, compute, serial console management, and more. The vendor-neutral NSR can host your preferred SD-WAN solution and supports easy integrations with SSE Magic Quadrant Leaders like Palo Alto Prisma Access, or you can use ZPE Cloud’s integrated SD-WAN app.

Thanks to the open-architecture, Linux-based Nodegrid OS, you can also extend Nodegrid’s capabilities with your choice of custom and third-party applications for security, monitoring, automation, and more. Plus, every device, application, and integration connected to the Nodegrid platform is brought under a single management umbrella for a unified and efficient orchestration experience. 

The Nodegrid platform from ZPE Systems rolls up everything you need in an SSE on-ramp and delivers it in one powerful, unified edge networking solution.

Learn how Nodegrid easily hosts and integrates Gartner’s picks for the 2023 SSE Magic Quadrant!

Contact ZPE Systems today!

Contact Us

What is an Application Delivery Platform?

An illustration showing a breakout of various software application components to highlight the need for an application delivery platform

Modern software architectures are highly complex and often very difficult to maintain and operate. A single enterprise application comprises hundreds (or even thousands) of individual services, technologies, and toolchains while requiring a lot of underlying infrastructure, such as servers, routing and load balancing rules, and security controls. All of this complexity increases overhead costs and adds to the ever-growing workloads of software, network, and infrastructure teams, especially when you multiply this effort across dozens or hundreds of software deployments.

Platform engineering is a new discipline introduced by Gartner to address these challenges by reducing the complexity of software engineering, network operations, and application delivery. The platforms built by these engineers are known by several names, including internal developer platforms, internal developer portals, and application delivery platforms. This guide defines an application delivery platform, discusses the underlying technology, and highlights a leading platform engineering solution.
.

Table of Contents:
  1. What is an application delivery platform?
  2. What is the importance of an application delivery platform?
  3. What technology makes up an application delivery platform?
  4. Introducing ZPE Systems’ Services Delivery Platform

What is an application delivery platform?

An application delivery platform is a suite of technologies that handles all the services that support an application, including security, traffic management, load balancing, and data management. Platform engineers combine all these services into a common toolset used to deploy applications at customer sites, so there’s no need to build a new architecture every time. This streamlined experience makes application delivery cost-effective by significantly reducing workloads and deployment timelines.

What is the importance of an application delivery platform?

The goal of an application delivery platform is to reduce deployment and management complexity. Deployment complexity leads to a greater risk of human error when configuring things like security controls and access policies, and any mistakes are likely to be found and exploited by cybercriminals. Management complexity makes it harder to stay on top of patch schedules. Unpatched software often contains vulnerabilities that are exploited by cybercriminals; for example, known ransomware groups targeted unpatched IBM software earlier this year.

By reducing complexity, an application delivery platform also reduces the attack surface, improving an organization’s overall security posture.

What technology makes up an application delivery platform?

By its very nature, an application delivery platform is highly customized to fit the needs of the applications being supported. Here are some examples of the services and technologies that are often included.

  • Server storage & compute: The platform needs storage (usually solid-state) and processing units (CPUs or GPUs) to run the applications and store necessary data. Ideally, the OS and computing architecture will support containers (e.g., Docker) for microservices applications.
  •  
  • Automation tools: A key feature of application delivery platforms is the ability to automatically provision and deploy new environments, apps, and network services as well activate services licenses and service chaining. That means the platform should host automation tools for configuration management, code delivery, and software-defined networking (SDN).
  •  
  • Security: The ideal platform makes it possible to deliver applications without configuring security every time. That means it provides unified management and repeatable deployments for security services like firewall traffic inspection, access control lists, and advanced authentication.
  •  
  • Routing & load balancing: A lot of backend networking goes into the typical application deployment to ensure traffic is routed correctly and optimized for performance. An application delivery platform should support network functions virtualization (NFVs) and SDN so standard network configurations can be easily deployed alongside the applications being delivered.
  • Management tools: Engineers need a way to remotely access, manage, and troubleshoot application deployments, even (and especially) during major service disruptions. The ideal platform includes out-of-band serial console management and supports third-party troubleshooting tools so remote teams can quickly recover systems and applications without an expensive on-site visit.

While this list is far from exhaustive, it covers the foundational technology that supports an application delivery platform. Platform engineering is still in its infancy, and many organizations struggle to efficiently execute it because of how many moving pieces need to be considered. The goal is to find a solution that provides the best framework of hardware and software capabilities that platform engineers can build upon, so they can create a fully customized application delivery platform without reinventing the wheel.

Introducing ZPE Systems’ Services Delivery Platform

Zero Pain Ecosysteme

The Services Delivery Platform from ZPE Systems is the perfect foundation for any platform engineering initiative. Nodegrid edge routers serve as the hardware backbone, providing networking and failover capabilities, OOB serial console management, and plenty of memory, storage, and CPU headroom for additional apps and services. You can build a fully customized hardware platform with the modular Net Services Router (NSR), extending your storage or compute capabilities or adding more ports to support your application deployment.

The vendor-neutral, Linux-based Nodegrid OS can run your custom applications as well as third-party automation, security, DevOps, and management tools. Plus, Nodegrid unifies all connected services and applications under a single management umbrella, allowing teams to oversee and orchestrate all of their deployments from one convenient portal.


Ready to Learn More?

The Services Delivery Platform from ZPE Systems simplifies platform engineering with powerful, multipurpose hardware and an open, vendor-neutral OS. Contact us today to learn more about using Nodegrid for your application delivery platform!

Contact Us