Today’s IT teams must maintain a growing infrastructure of on-prem and cloud solutions. These range from physical routers, out-of-band devices, and firewalls, to Zero Trust Security solutions, micro-segmentation tools, and network automation integrations. Despite an abundance of physical and virtual solutions meant to help keep digital services online, many organizations face an overwhelming number of tasks just to sustain everyday operations.
With the rising risk of recession, organizations will be forced to cut back on resources including staff, training, and tools. This will only worsen the existing challenges teams face in their efforts to maintain their distributed infrastructure.
In this blog, we’ll explore three gaps that will leave IT teams scrambling and show you several practical approaches to cope during recession.
Gap 1: Lack of staff
IT teams have been historically understaffed, and most people can remember at least one significant tech worker hiring campaign from the past decade. Today’s CIOs may in fact be facing the biggest talent gap since 2008. For example, in the cybersecurity sector alone, the 2021 (ISC)2 Cybersecurity Workforce Study reported that despite adding 700,000 cybersecurity professionals to the workforce in 2021, there’s still a gap of more than 2.7 million workers globally, 377,000 of which are needed in the United States.
Trained staff are a must for managing an organization’s distributed sites, especially as team silos disappear and workers are required to have a breadth of skills. Business leaders increasingly need people who are proficient in networking and programming, so they can maintain normal operations while progressing their digital transformation initiatives such as hyperautomation. It’s a challenge that often comes down to hiring new talent or increasing the skills of existing employees, and both of these approaches require plenty of time and money.
This issue will only worsen with the coming recession as companies begin to tighten their belts and slash budgets. Major brands have already shed thousands of workers this year, leaving IT teams to make due with existing staff numbers or even reduced headcounts. In the simplest terms, the coming recession will leave companies much less willing or able to invest in staff.
Gap 2: Lack of tools to reduce workloads
Today’s infrastructure incorporates solutions from many different vendors, but the problem is these often come with their own unique tools that are meant to serve only a specific function. Managing SD-WAN, SASE, ZTNA, orchestration, and out-of-band solutions means jumping between disparate tools, many of which lack integration with one another. This complexity leaves operational teams stuck in a reactionary break/fix posture trying to climb mountains of never-ending support tickets.
To address this challenge, many Big Tech companies empower their IT teams through digital transformation initiatives, such as using automation to achieve a proactive approach. But this requires additional investments in upskilling staff and acquiring adequate automation infrastructure/tools. For many organizations, a lack of money and resources makes this difficult during normal economic conditions, and will only become exacerbated with the coming recession. IT teams will continue scrambling with their inflated workloads.
Gap 3: Lack of trust in automation
Automation can greatly reduce the risk of human error (and subsequent outages) by handling simple workloads, such as device provisioning and firmware updates. However, companies that do have the resources to implement automation also recognize its limitations. Automation solutions that aren’t optimized leave IT teams with mundane tasks like managing, scheduling, and restarting bots. But to even reach this level of automation requires training staff who typically don’t have a background in programming or development.
These teams will be unfamiliar with NetOps/DevOps concepts. In order to develop essential automation practices, these employees will need to learn through trial and error. This is a problem because most organizations lack the proper automation infrastructure and tools that allow their IT teams to recover from mistakes. Operational teams in charge of keeping infrastructure running often fear automation for this exact reason — if they make one error, there’s the potential that it will bring down the network, lead to unhappy customers, and cost them their job.
Close these gaps with the Network Automation Blueprint
You can close these gaps for good using out-of-band, jump boxes, and tools you already have. After years of working directly with tech giants, we’ve created a best practice reference architecture any company can use to automate their network. This Network Automation Blueprint has been proven by global enterprises to increase capabilities and reduce workloads through trustworthy automation.
Network engineers need powerful tools to keep digital services online and customers happy. This is especially true during economic downturn, when organizations must freeze hiring and put more strain on existing staff. Revenue relies on network availability, and with experts predicting a recession this winter, significant operational challenges are inevitable for most organizations.
The burden of overcoming these challenges falls on network engineers. Success means maintaining reliable services and reaping any professional benefits (salary increases, promotions, etc.). Failure, on the other hand, means the very realistic possibility of major business losses and job cuts, including yours.
In order to make sure you don’t fall into the latter scenario, here are five must-have tools and techniques to help network engineers overcome these challenges.
Tool 1. OOBI-LAN™
Out-of-band (OOB) management is an essential part of a network engineer’s toolkit. At the conceptual level, out-of-band is meant to provide management access to production equipment, even if the production equipment is offline.
One major problem is that many organizations invest a lot of time and money into their production infrastructure, but not into any dedicated OOB infrastructure. In other words, they deploy OOB solutions that rely in part on their production equipment, such as OOB VLANs connected to in-band switches. All it takes is a mistake, misconfiguration, or attack to bring down the production and management networks, leaving network engineers to rebuild the entire system from scratch while their services remain offline to customers. This is simply not acceptable in a slow economy, where the business’ resources and revenue are already too thin.
From the pandemic lockdowns, organizations have learned that they need a way to more quickly recover their network locations. According to the Uptime Institute’s 2022 Outage Analysis, outages lasting longer than 24 hours increased to nearly 30% in 2021. This has led many to build dedicated OOB infrastructure for the LAN (OOBI-LAN). They deploy a serial console locally to establish connectivity to the management ports of their sensitive equipment. Network engineers must use this serial console to access their production infrastructure. This serial console minimizes the attack surface since it’s the only device connected to the Internet, and allows network engineers to restore services even if production equipment is down.
Tool 2. OOBI-WAN™
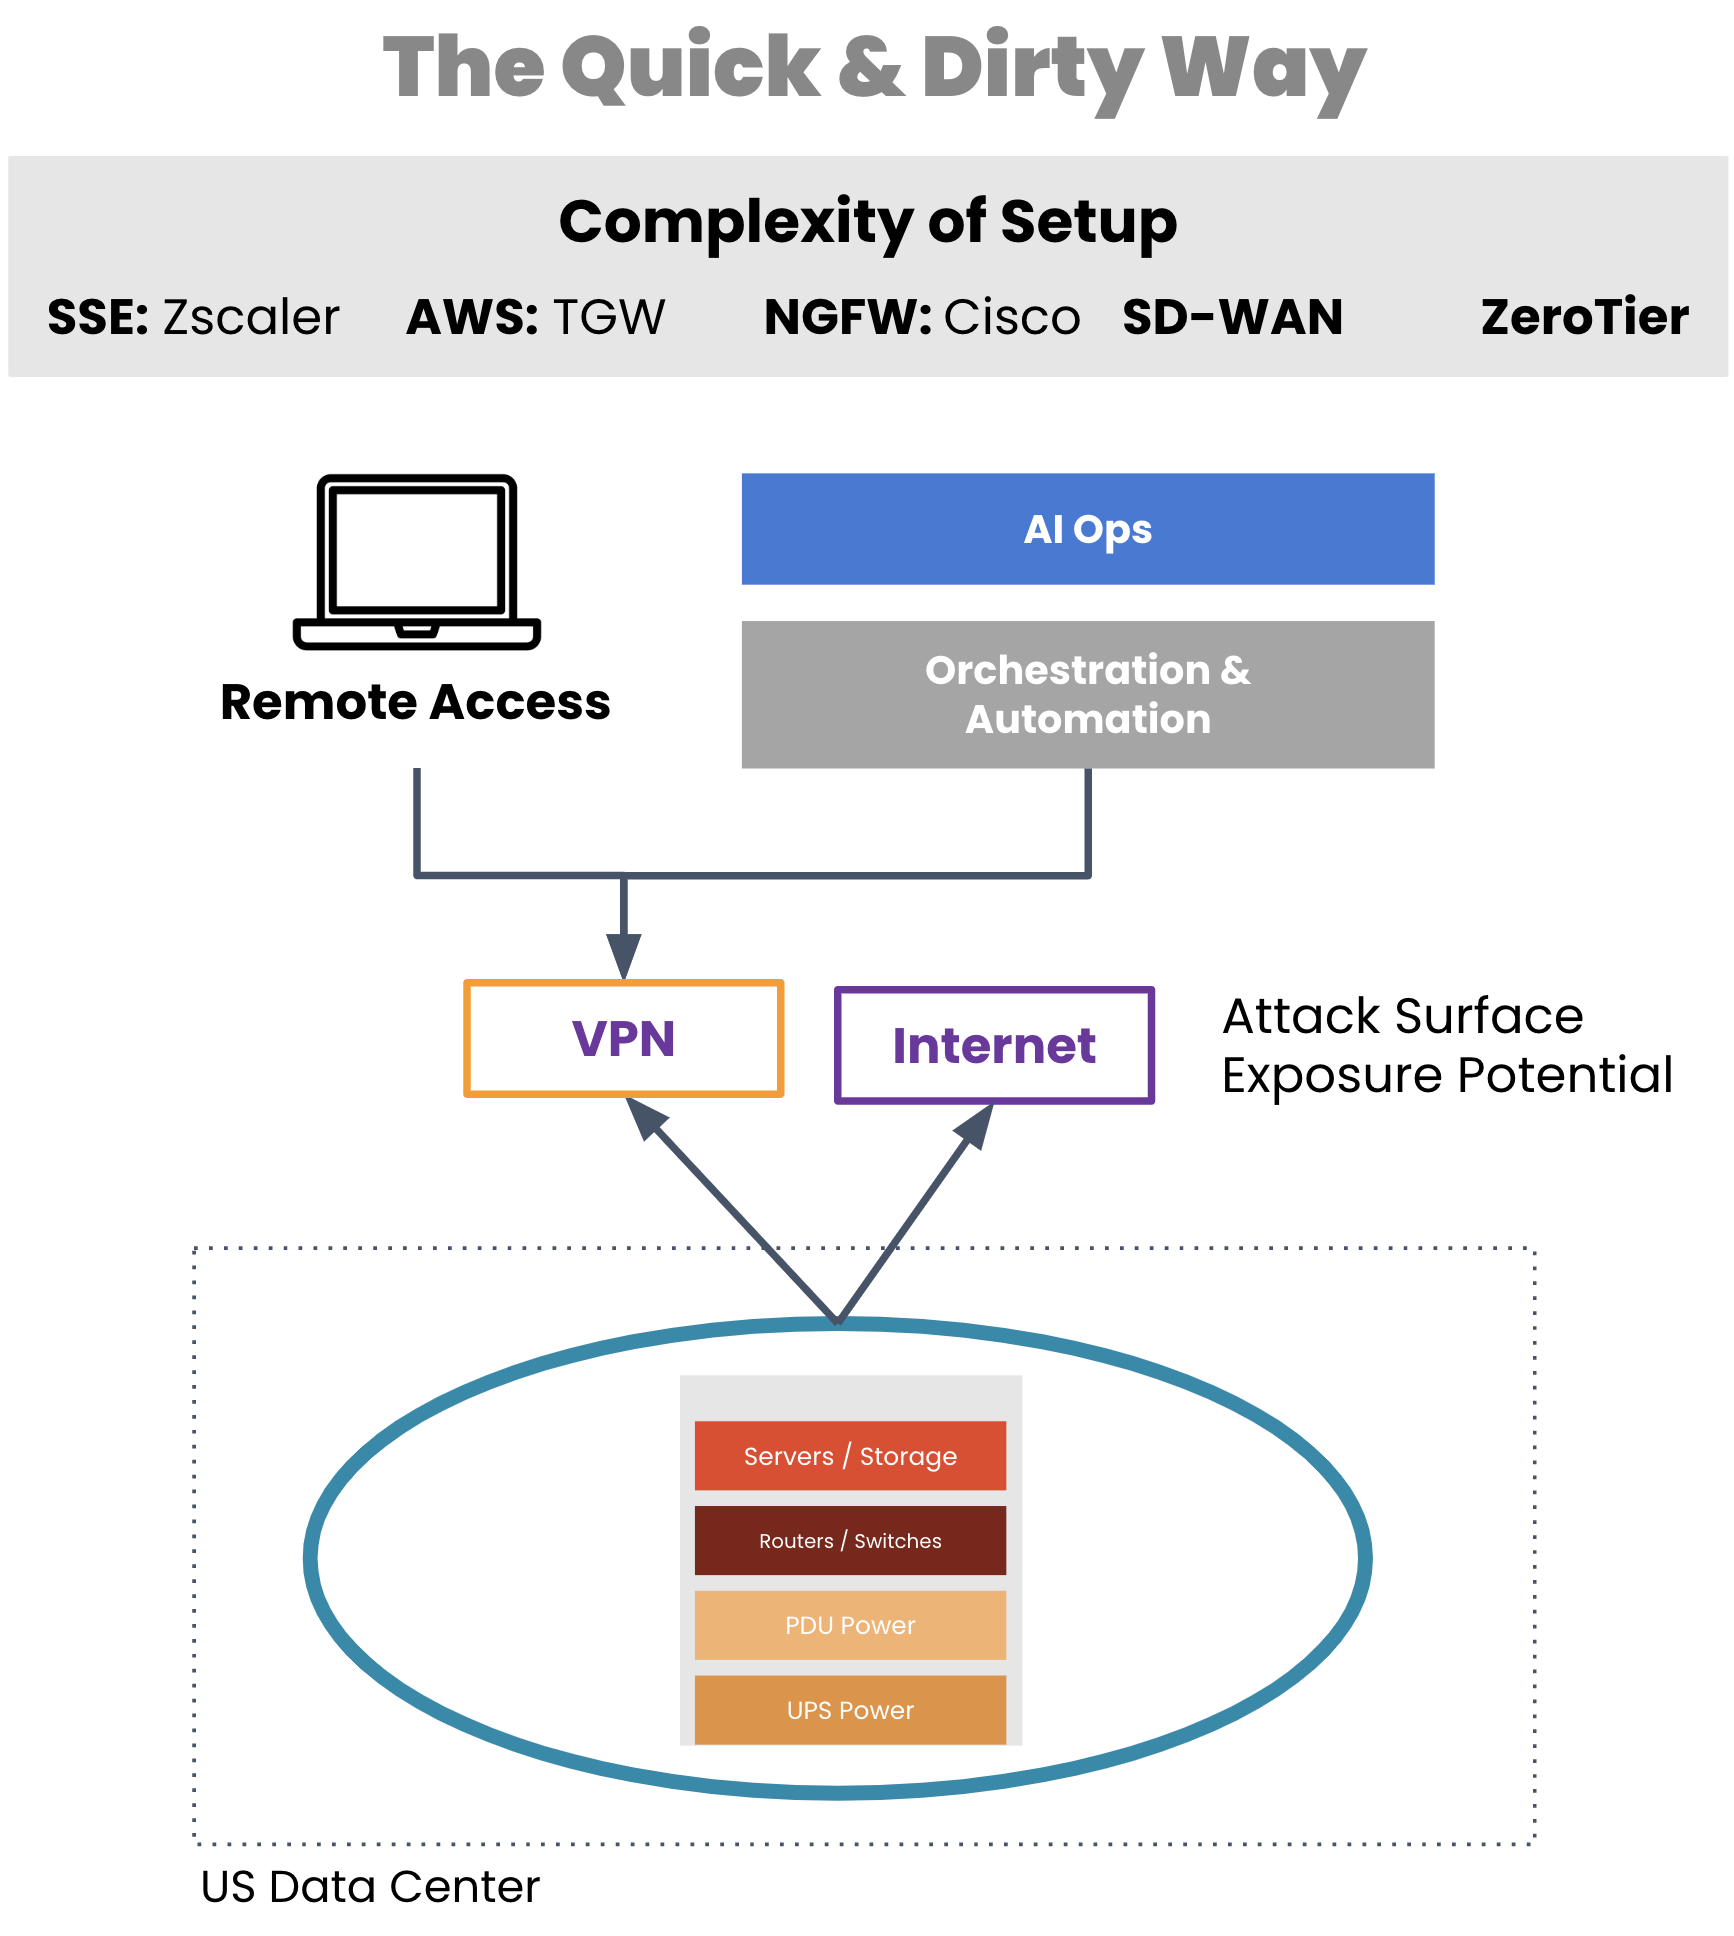
A critical tool for network engineers is out-of-band that enables remote WAN management. But typically, organizations employ a WAN management strategy that also relies on their production infrastructure, such as for creating VPN tunnels for management traffic. If a VPN tunnel becomes broken or the production gear fails, network engineers are suddenly left without remote access to their equipment.
Aside from a lack of availability, traditional OOB access comes with real security risks. Exposing LTE modems to the Internet, leveraging untrusted third-party VPN services, using OOB hardware that’s old and unpatched, and worse — exposing the management port of devices to public Internet. All of these are attack surfaces, any of which can give access to your infrastructure and be used as the pivot point to get to the rest of the infrastructure.
Image: Management access depends on production equipment to establish VPN tunnels.
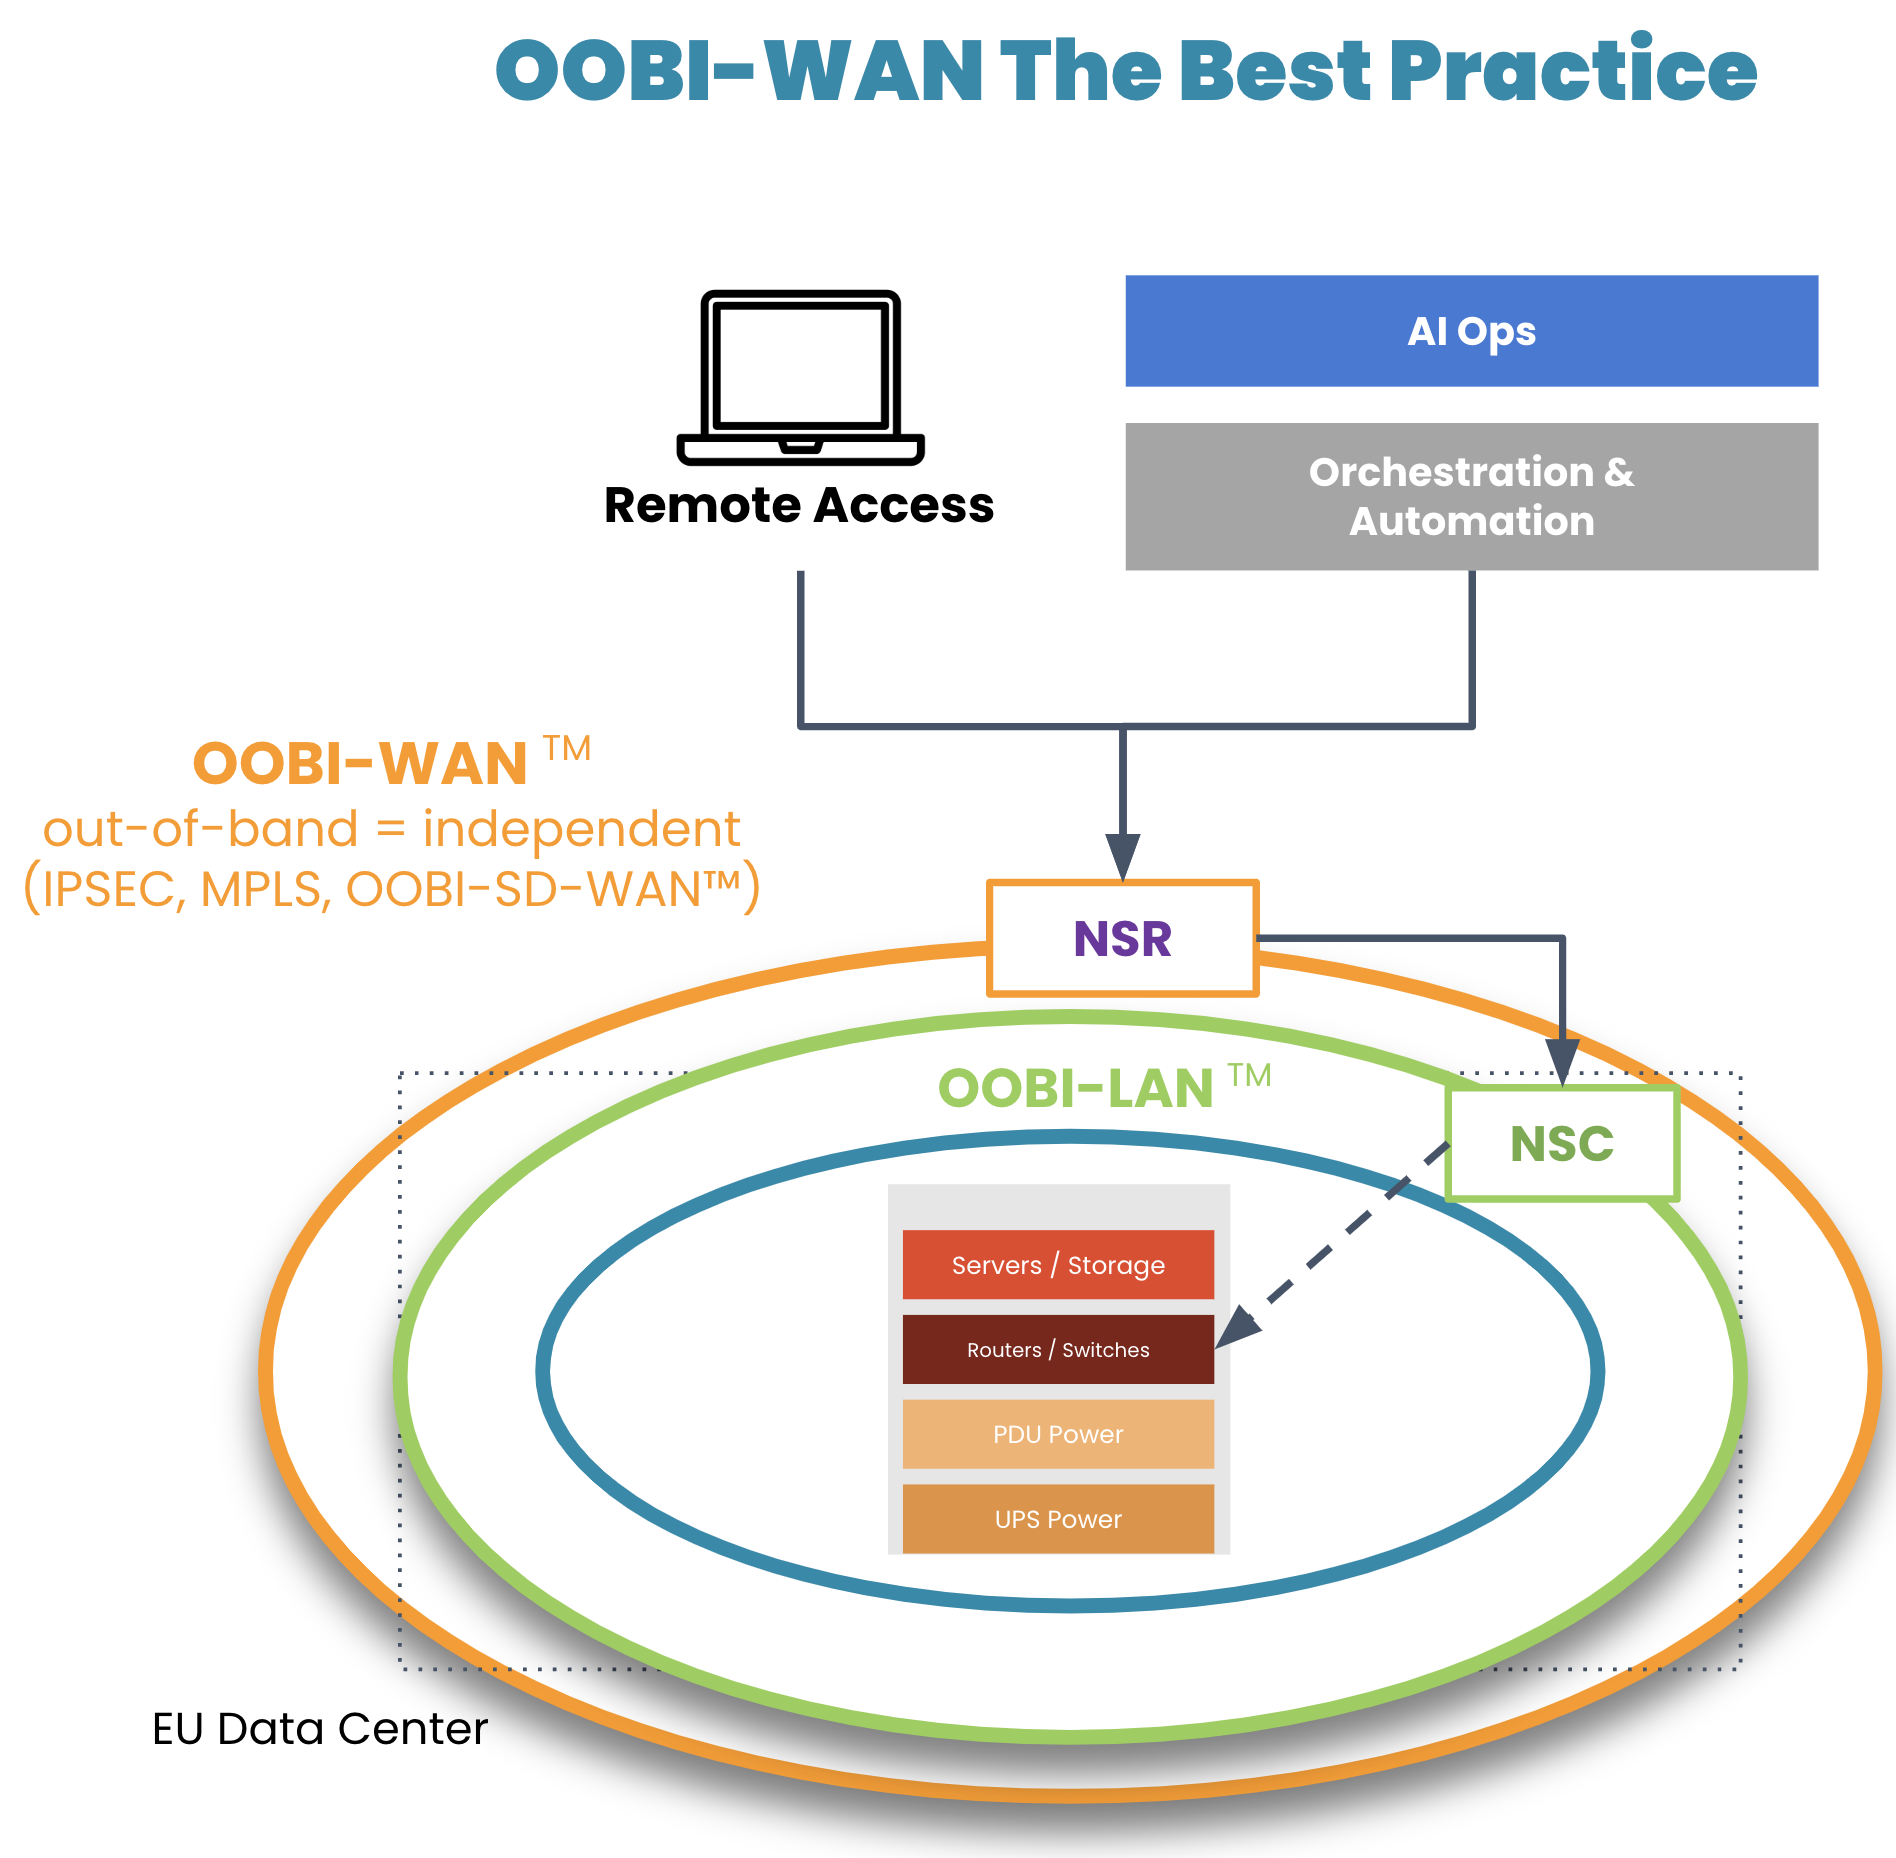
On top of their OOBI-LAN, organizations have built dedicated OOB infrastructure for the WAN (OOBI-WAN – there’s a Star Wars reference somewhere in there) for added resilience against these scenarios.
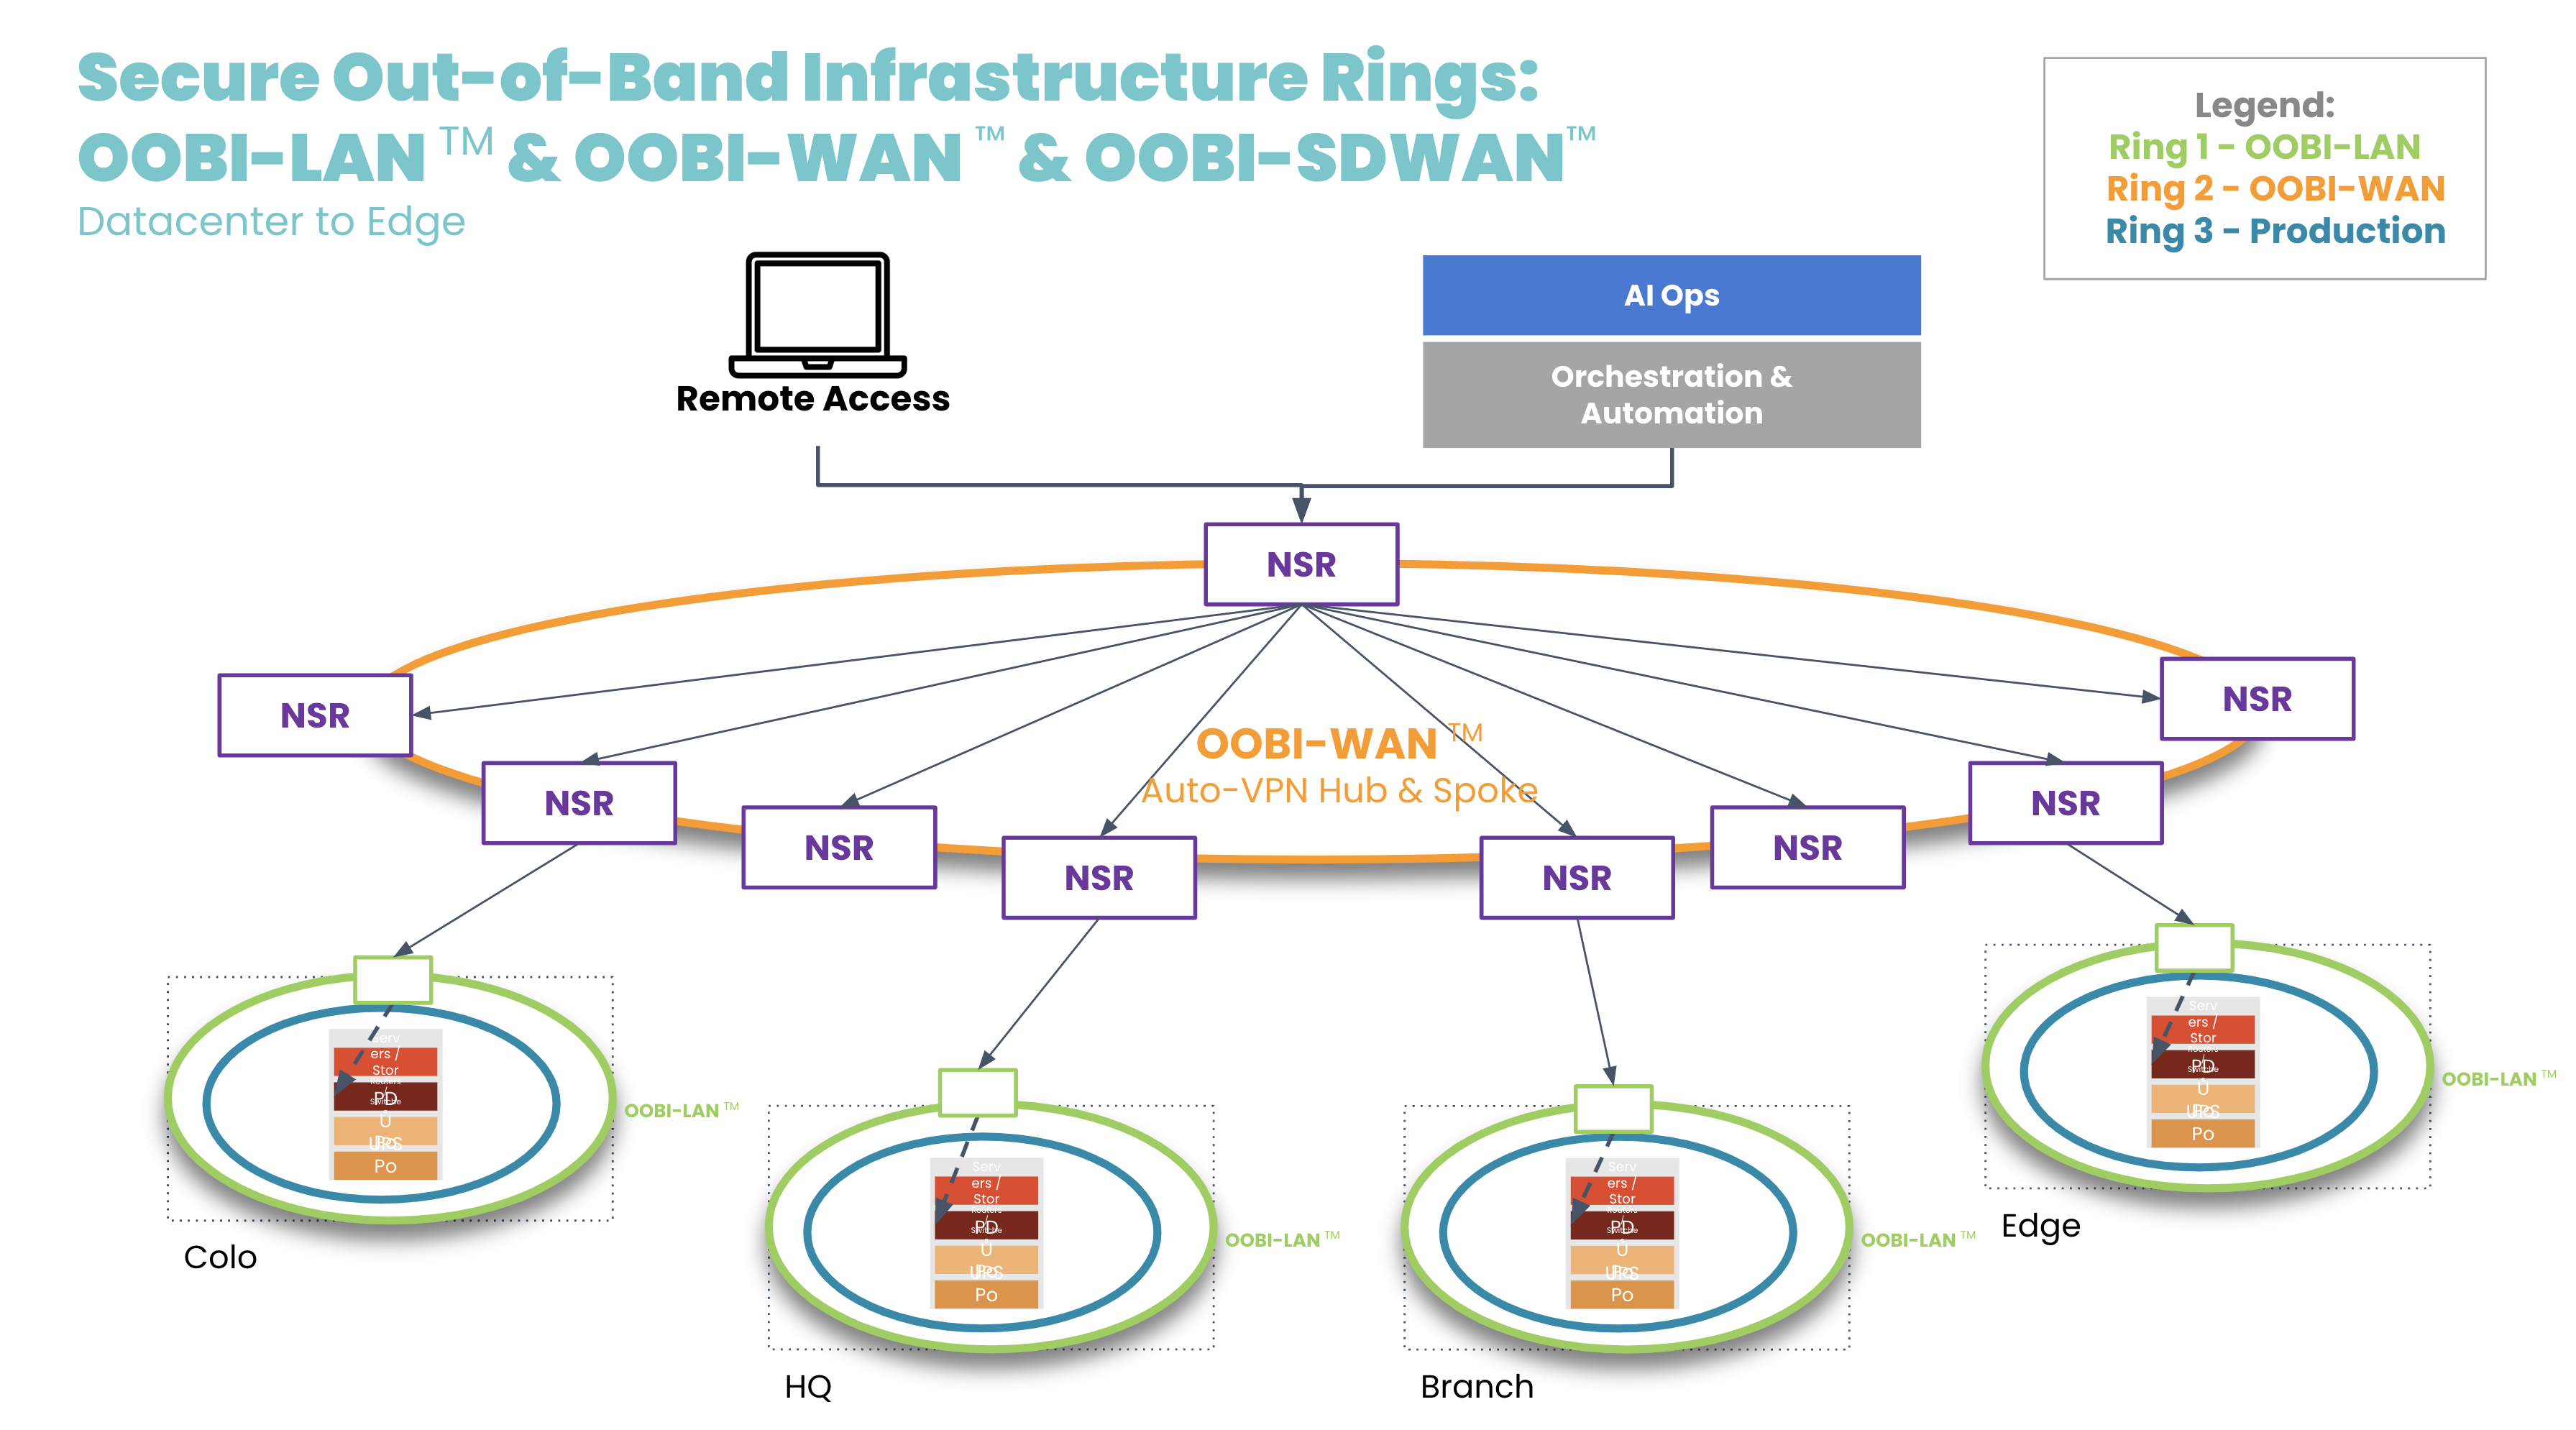
Image: OOBI-WAN and OOBI-LAN create a fully separate out-of-band infrastructure that can be used to completely rebuild production infrastructure.
OOBI-WAN uses MPLS, IPsec, or SD-WAN links to create an overlay network dedicated specifically to management traffic. This gives network engineers private access to their infrastructure for management and troubleshooting, essentially creating a completely separate OOB network that does not rely on any part of the production network. OOBI-WAN lets network engineers use their WAN connection to remotely access their OOBI-LAN and fully rebuild their distributed networks, regardless of the state of their production infrastructure.
A key part of OOBI-WAN is the inherent security that is built at all layers. To build secure OOBI-WAN, the best practice is to use OOBI-SDWAN™ which automates the building of VPN tunnels between all the nodes that need to be managed. OOBI-SDWAN provides the expected auto-VPN feature which means VPN encryption keys remain secure, as they don’t need to be copied/pasted/typed into multiple third-party devices. OOBI-SDWAN also ensures that an SLA is provided on the OOBI network along with observability dashboards of connectivity and the access state of the network. The combination of OOBI-SDWAN with a zero trust security framework is the best way to gain reliability in a way that reduces your risk.
Another tool that network engineers are becoming familiar with is automation. Network automation codifies repetitive tasks to reduce workloads for configuration management, compliance, and troubleshooting. During a slow economy, being able to scale an IT team’s efforts is especially valuable to business operations and end customers.
There is one major concern, however: having automation that runs loose and begins destroying the network, much like a bull in a China shop. Network engineers typically must learn new automation tools and programming languages, which requires trial and error. And because there is a lack of a best practice reference architecture, teams don’t know any better than to automate directly on the production network. This causes anxiety, as one mistake could bring down the network, cause catastrophic losses, and leave network engineers without an efficient way to recover.
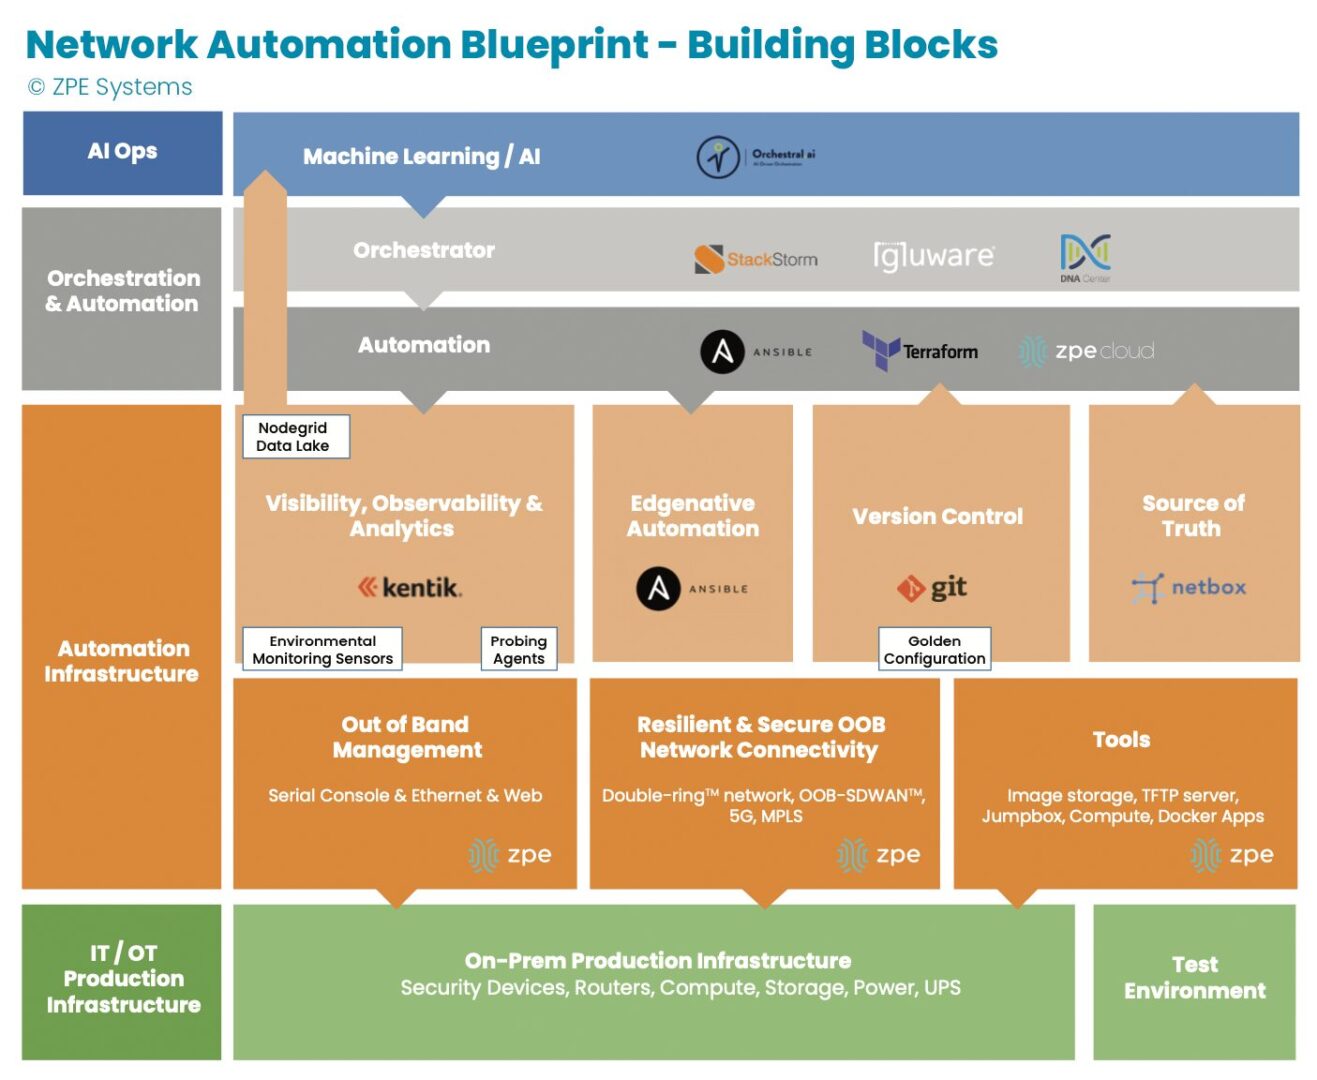
Image: The orange section describes dedicated automation infrastructure used for safely implementing automation.
In recent years, teams have been deploying automation on dedicated infrastructure like their OOB network. This automation infrastructure sits between the production infrastructure and the orchestration infrastructure, and serves as a safe way to build an automation pipeline. Open, Linux-based appliances like the Nodegrid Net SR combine a variety of functions and can host automation tools, like those for observability and analytics, version control, and source of truth. This independent automation infrastructure allows network engineers to ensure the integrity of configuration changes, software updates, and remediation protocols in an out-of-band manner, rather than testing directly on the production network. They can scale their capabilities, and in case of errors, roll back to a golden configuration that keeps services online.
Tool 4. Remote access to local jump box
Network engineers have another tool at their disposal: the jump box (a.k.a. jump server, jump host). A jump box hosts tools for maintaining operations, and these include file servers, image storage, configuration management tools, and troubleshooting commands. The jump box is a valuable asset for normal operations and for restoring services, such as when a device fails and needs its image rebuilt.
The issue with jump boxes is that they are typically a separate device that requires power, cooling, rack space, and maintenance. Some jump boxes also require on-site technicians to physically connect to the equipment needing repair.
Many organizations have adapted by upgrading their OOB infrastructure with appliances that can run full virtual machines (VMs). These can run all the tools mentioned above as well as with Docker containers, while consolidating power consumption, cooling resources, and rack space. The OOB appliance can double as a jump box. Combined with OOBI-LAN and OOBI-WAN, network engineers get remote access to re-image a device, diagnose DNS/routing issues, and perform any other necessary tasks. Key point is that discrete jump boxes – Like the Intel NUC — to be converted to virtual jump boxes running on a secure OOB platform like the Nodegrid Service routers.
Tool 5. Smart hands
A final way that network engineers get help through a slow economy is by outsourcing to so-called ‘smart hands.’ Employing smart hands means involving a third-party expert who can take on some of the IT workload. It’s a viable strategy, especially for teams feeling crushed by corporate belt tightening and the resulting mountain of tasks.
Companies who take this approach must be aware that the skills of smart hands varies greatly, as does the cost. This means it’s essential to strike a balance between which tasks to outsource, and which tasks to keep in house. For example, many organizations use smart hands for simple jobs such as replacing hardware and installing equipment at new sites. For more specialized jobs that require deeper knowledge of the environment, such as fixing a misconfigured IP address or route, teams use in-house personnel. This balance helps organizations get the support they need to keep operations running.
Get a cheat sheet to implement these tools fast
Some companies thrive during economic downturn, because they’ve intelligently placed these tools within their network architecture. Over the past decade, we’ve worked with these companies — including the largest tech giants — to describe in painstaking detail how they set up their infrastructure. We just released all 40+ pages of this validated reference architecture, complete with implementation diagrams and examples.
It’s called the network automation blueprint and it combines all of these tools. Network engineers can confidently answer questions like:
How do we meet SLAs with a smaller workforce?
How can we keep sites operating without physical access to equipment?
How can we perform weekly updates/patching without breaking things?
The blueprint is your cheat sheet to implementing a more resilient network, and fast. Click the button below to download your copy now.
Software-defined wide area networking, or SD-WAN, has made it possible to efficiently control highly distributed WAN architectures using software abstraction and automation. SD-WAN adoption is increasing, partially due to the rise in remote work during the pandemic, with experts predicting a compound annual growth rate (CAGR) of 26.2% between 2022 and 2028. However, while SD-WAN solves a lot of remote, edge, and branch networking problems, it also introduces security concerns that must be addressed. This definitive SD-WAN security checklist highlights the most important challenges and provides solutions for overcoming them.
The definitive SD-WAN security checklist
Keeping an SD-WAN architecture secure requires several features to be successful. It’s vital to consider this comprehensive list.
1. Frequent security patching
Outdated operating systems create a significant security risk. According to a 2016 Voke Media survey, about 80% of breaches or failed audits could have been prevented by patching outdated software or updating device configurations. An SD-WAN router with an outdated OS is more likely to have vulnerabilities, and the longer it goes unpatched, the more likely a hacker is to find and exploit those vulnerabilities.
However, SD-WAN architectures are often multi-vendor and highly distributed, making it challenging for administrators to monitor for vulnerabilities and stay on top of patch schedules. There are two primary ways to overcome this difficulty:
Centralized SD-WAN management platforms provide a single pane of glass from which to monitor and update device software. The right platform is vendor-agnostic, so administrators can easily patch any and all vendor devices from one common interface.
Automated patch management software helps keep OSes up to date by automatically applying new updates based on a predetermined schedule. Some solutions even perform automatic vulnerability scans or can monitor environments for missing patches and apply new updates that fall outside of the usual patch schedule.
Your ability to keep SD-WAN device software secure ultimately depends on the vendor’s patch schedule. Some providers are sluggish to patch known vulnerabilities in their software, either because they think they can keep said vulnerabilities a secret or because they don’t want to dedicate the time and resources needed to keep the OS up to date. That’s why you should look for SD-WAN hardware and software vendors who are transparent about vulnerabilities and who work diligently to release frequent patches and updates.
2. Zero Trust Provisioning
SD-WAN platforms are software-based, but they still require underlying networking hardware at each remote site for connecting to the enterprise network. Deploying this hardware can be difficult, especially when SD-WAN sites are in hard-to-reach locations such as offshore oil rigs, remote weather stations, or nations experiencing disasters or active conflicts. Often, organizations opt to pre-stage devices in their home office and then ship them to remote sites so they can avoid costly or dangerous travel.
Pre-staging creates a security risk because a pre-configured device could be intercepted by hackers and used to access the enterprise network. Zero Touch Provisioning (ZTP) reduces the need for pre-staging by deploying new device configurations over the network. ZTP-enabled devices provision themselves by using DHCP or TFTP to find and download configuration files, which means administrators can ship factory-default hardware that doesn’t contain any exploitable information about the enterprise network.
However, ZTP also introduces some additional security challenges. Once they’ve created the configuration file, administrators generally don’t monitor the entire automatic provisioning process, so there’s a chance that a mistake in the configuration file could create a security vulnerability that goes unnoticed. And, since one ZTP configuration file is usually applied to multiple devices, a potential security vulnerability could affect several systems or locations without anyone knowing. In addition, hackers could intercept the transmission of the configuration file over the network if the connection isn’t strongly encrypted.
These challenges are overcome with a secure ZTP solution that follows zero trust security principles. This type of solution is often referred to as “Zero Trust Provisioning,” and it includes hardware-based security like TPM, BIOS protection, encryption modules, and an onboard firewall which protects the software layer (secure boot) and management layer (two-factor authentication). In addition, the ideal Zero Trust Provisioning solution supports integrations with automated configuration management tools like Chef and Ansible which can be set up to test and monitor ZTP configurations for mistakes and security vulnerabilities.
Zero Trust Provisioning is a key part of the SD-WAN security checklist because it prevents branch networking hardware from being intercepted and used in a cyberattack. It also ensures that automatic provisioning occurs over a secure, encrypted network connection, and allows integration with configuration management tools to prevent errors from introducing additional vulnerabilities.
3. Secure out-of-band access
Many organizations use out-of-band (OOB) management to configure, control, and troubleshoot remote network infrastructure. OOB management uses a separate management plane, so resource-intensive network management and orchestration workflows don’t affect the performance or reliability of the production network. This may involve using a jump box to access an OOB network, which is an entirely separate management network architecture that runs parallel to the production network. However, a simpler solution is to use an OOB console server to achieve the same goal without the hassle of deploying a separate architecture.
OOB management improves the performance and reliability of production networks, and provides an alternative path to remote infrastructure (typically via cellular modem) in the event of an ISP outage or a network device failure. The issue with OOB management is that jump boxes and console servers are attractive targets to hackers. If a malicious actor manages to compromise the OOB network, they’ll gain complete control over the remote infrastructure.
To keep SD-WAN devices and other remote infrastructure secure, it’s best to use an OOB console server with advanced encryption for both the hardware and the management connections. In addition, the OOB solution should include Zero Trust features like MFA (multi-factor authentication) and RBAC (role-based access control). Just like the SD-WAN hardware, the OOB device(s) should run a fully patched OS and support Zero Trust Provisioning. For even greater protection, choose an OOB solution that supports integrations with third-party security solutions like next-generation firewalls (NGFW).
A secure out-of-band management solution gives network administrators 24/7 access to remote infrastructure on a dedicated, encrypted network connection using hardened OOB console server devices. This ensures that hackers can’t use the OOB network to hijack production infrastructure while also giving administrators the ability to quickly recover from outages, hardware failures, and cyberattacks.
4. Cloud-based security technology
As we’ve discussed above, it’s possible to run SD-WAN solutions on hardware with onboard firewall features. However, these basic firewalls often lack the advanced functionality needed to protect enterprise networks from sophisticated cyberattacks, which is why most organizations also use some form of stateful firewall or NGFW that resides in a central data center. This works well for a single, centralized enterprise network, but the addition of remote sites can create performance issues.
For the centralized firewall to inspect and protect SD-WAN traffic, that traffic must be backhauled through the central data center, even if the request is ultimately destined for the web. This inefficient routing causes bottlenecks, performance issues, and even dropped connections for on-premises and remote users alike. The obvious solution to this problem would be installing physical or virtual firewalls in each remote location, but this is expensive and disruptive and creates more management complexity for network administrators.
A better way to protect remote traffic while improving performance is through the use of cloud-based security solutions, such as Security Service Edge (SSE). SSE relies on SD-WAN’s intelligent routing capabilities to separate remote traffic that’s destined for web, cloud, and SaaS resources. This traffic bypasses the firewall and is instead routed through a cloud-based security stack, reducing the load on the enterprise network.
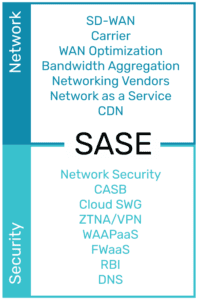
Ideally, the SD-WAN solution will tightly integrate with the SSE platform. This combination of SSE security with an SD-WAN on-ramp creates what’s known as SASE, or Secure Access Service Edge. This is most easily achieved using vendor-neutral branch networking platforms which can host or integrate with a wide variety of SD-WAN and SSE solutions. An integrated SASE architecture ensures comprehensive security while providing remote users and systems with fast, reliable access to cloud resources.
Nodegrid checks every box on your SD-WAN security checklist
Only one remote network management solution provides everything you need to keep your SD-WAN architecture secure: the Nodegrid platform from ZPE Systems. Nodegrid’s vendor-neutral routers, such as the 5-in-1 Hive SR branch gateway, can directly host or integrate with your chosen SD-WAN solution. Whether you enable SD-WAN with a Nodegrid device or by using ZPE Cloud’s SD-WAN application, you’ll get seamless access, centralized management, and state-of-the-art security.
1. Secure, up-to-date SD-WAN device OS
Nodegrid’s branch gateway routers run on the vendor-neutral, x86 Linux-based Nodegrid OS, which is constantly monitored for vulnerabilities and frequently patched to ensure security. Plus, with the ZPE Cloud orchestration platform, you can monitor and update all your SD-WAN devices from one convenient management portal—even if that hardware comes from another vendor.
2. Zero Trust Provisioning for branch networks
All Nodegrid devices support Zero Trust Provisioning, and they can extend this capability to any third-party devices managed by Nodegrid. That means administrators can securely configure all the multi-vendor devices in a remote branch network without the need for travel or pre-staging. Nodegrid ZTP is considered Zero Trust because it protects the hardware, software, and management layers with advanced security features like:
Password-protected BIOS
Current cryptographic modules
SSO with SAML (Duo, Okta, Ping, and ADFS), MFA, and remote authentication
Geofence perimeter crossing detection
Onboard firewall, IPSec, and Fail2Ban intrusion protection
Fine grain RBAC with strong password enforcement
Nodegrid also supports integrations with automated configuration management solutions like Ansible, Chef, and Puppet, so you can ensure every device is provisioned correctly.
3. Gen 3 secure out-of-band management
Nodegrid services routers provide reliable, Gen 3 OOB management access to any connected devices, including those from other vendors. This access is protected by a patched OS, onboard hardware security features, and current encryption modules. Plus, Nodegrid’s hardware and software can host or integrate with third-party security solutions like NGFWs for comprehensive OOB security.
4. An SD-WAN onramp to SSE
The Nodegrid branch networking solution provides the ideal SD-WAN on-ramp to leading Security Service Edge providers. That’s because Nodegrid is a completely open platform that can host or integrate with any SSE and SD-WAN offering to provide a single, unified SASE solution. This gives administrators complete control over every aspect of branch network management and SD-WAN security from one convenient portal, reducing complexity and improving your security posture at the same time.
Wondering how ZPE’s Nodegrid solution checks all the boxes on your SD-WAN security checklist?
Today’s IT teams must maintain a growing infrastructure of on-prem and cloud solutions. These range from physical routers, out-of-band devices, and firewalls, to Zero Trust Security solutions, micro-segmentation tools, and network automation integrations. Despite an abundance of physical and virtual solutions meant to help keep digital services online, many organizations face an overwhelming number of tasks just to sustain everyday operations.
With the rising risk of recession, organizations will be forced to cut back on resources including staff, training, and tools. This will only worsen the existing challenges teams face in their efforts to maintain their distributed infrastructure.
In this blog, we’ll explore three gaps that will leave IT teams scrambling this winter, and show you several practical approaches to cope during recession.
Gap 1: Lack of staff
IT teams have been historically understaffed, and most people can remember at least one significant tech worker hiring campaign from the past decade. Today’s CIOs may in fact be facing the biggest talent gap since 2008. For example, in the cybersecurity sector alone, the 2021 (ISC)2 Cybersecurity Workforce Study reported that despite adding 700,000 cybersecurity professionals to the workforce in 2021, there’s still a gap of more than 2.7 million workers globally, 377,000 of which are needed in the United States.
Trained staff are a must for managing an organization’s distributed sites, especially as team silos disappear and workers are required to have a breadth of skills. Business leaders increasingly need people who are proficient in networking and programming, so they can maintain normal operations while progressing their digital transformation initiatives such as hyperautomation. It’s a challenge that often comes down to hiring new talent or increasing the skills of existing employees, and both of these approaches require plenty of time and money.
This issue will only worsen with the coming recession as companies begin to tighten their belts and slash budgets. Major brands have already shed thousands of workers this year, leaving IT teams to make due with existing staff numbers or even reduced headcounts. In the simplest terms, the coming recession will leave companies much less willing or able to invest in staff.
Gap 2: Lack of tools to reduce workloads
Today’s infrastructure incorporates solutions from many different vendors, but the problem is these often come with their own unique tools that are meant to serve only a specific function. Managing SD-WAN, SASE, ZTNA, orchestration, and out-of-band solutions means jumping between disparate tools, many of which lack integration with one another. This complexity leaves operational teams stuck in a reactionary break/fix posture trying to climb mountains of never-ending support tickets.
To address this challenge, many Big Tech companies empower their IT teams through digital transformation initiatives, such as using automation to achieve a proactive approach. But this requires additional investments in upskilling staff and acquiring adequate automation infrastructure/tools. For many organizations, a lack of money and resources makes this difficult during normal economic conditions, and will only become exacerbated with the coming recession. IT teams will continue scrambling with their inflated workloads.
Gap 3: Lack of trust in automation
Automation can greatly reduce the risk of human error (and subsequent outages) by handling simple workloads, such as device provisioning and firmware updates. However, companies that do have the resources to implement automation also recognize its limitations. Automation solutions that aren’t optimized leave IT teams with mundane tasks like managing, scheduling, and restarting bots. But to even reach this level of automation requires training staff who typically don’t have a background in programming or development.
These teams will be unfamiliar with NetOps/DevOps concepts. In order to develop essential automation practices, these employees will need to learn through trial and error. This is a problem because most organizations lack the proper automation infrastructure and tools that allow their IT teams to recover from mistakes. Operational teams in charge of keeping infrastructure running often fear automation for this exact reason — if they make one error, there’s the potential that it will bring down the network, lead to unhappy customers, and cost them their job.
Close these gaps with the Network Automation Blueprint
You can close these gaps for good using out-of-band, jump boxes, and tools you already have. After years of working directly with tech giants, we’ve created a best practice reference architecture any company can use to automate their network. This Network Automation Blueprint has been proven by global enterprises to increase capabilities and reduce workloads through trustworthy automation.
A cybersecurity platform provides a unified interface from which to manage multiple security tools and controls. Traditionally, these platforms only work within a single vendor’s ecosystem of products. However, a new type of solution, called Cybersecurity-as-a-Platform (or CaaP), allows you to integrate your choice of third-party, multi-vendor solutions. In this blog, we’ll discuss the challenge of managing a complex cybersecurity environment and explain how CaaP can help.
Why Cybersecurity-a-a-Platform (CaaP) is the future of holistic security
Modern network security is rapidly evolving and expanding to deal with the increasing sophistication and frequency of cyberattacks. According to the Oracle and KPMG Cloud Threat Report from 2020, the average organization uses over 100 discrete cybersecurity controls. Often these tools come from many different vendors and perform many different functions, requiring specialized training to use each one effectively. This creates a highly complex cybersecurity environment that’s prone to human error.
In addition, there’s a lack of interoperability between products, meaning tools are often disjointed and working independently of each other rather than as a cohesive system. There’s also no centralized control or visibility over these independent solutions, which means administrators need to log in to each one to configure, monitor, and manage their functionality.
This leaves teams without a big-picture overview of their cybersecurity environment, making it impossible to achieve a complete security posture. This need for centralized management and monitoring of discrete security products led to the development of unified cybersecurity platforms.
What is a cybersecurity platform?
A cybersecurity platform is a software solution—typically, but not always, cloud-based—which unifies an ecosystem of security tools and controls behind one management interface. In the past, this has usually been vendor-specific (e.g., Trend Micro providing a single platform from which to manage their own security products). However, this type of platform leaves you locked in to whatever features and functionality are included by the cybersecurity vendor, or their chosen integration partners.
That leaves organizations with one of two choices:
1. Stay within that ecosystem and accept that they may have gaps in their coverage due to a lack of needed functionality. In this case, this means sacrificing the security of their network and systems for the convenience of using a single management system.
2. Add on additional products that must be managed outside of that platform, creating more management complexity for security administrators. In this case, this means sacrificing efficiency and interoperability in the hopes of improving overall security.
In either scenario, the organization is hurting its security posture by making compromises. A better solution is to choose a platform that gives you the freedom to combine the best security products and tools for your unique environment under one convenient management umbrella.
What is Cybersecurity-as-a-Platform (CaaP)?
Cybersecurity-as-a-Platform (CaaP) provides a vendor-agnostic interface from which to control a vast and complicated cybersecurity ecosystem. CaaP doesn’t care who you bought your security tools from or how you plan to use them—it provides the platform from which to integrate, manage, and monitor every component of your cybersecurity toolkit. This includes creating unified dashboards and visualizations that combine data from all your different security monitoring and analytics solutions, so you can get a complete picture of your cybersecurity environment.
How CaaP enables holistic cybersecurity
A unified Cybersecurity-as-a-Platform solution benefits businesses by:
→ Reducing data overload – Security analysts must monitor and act on data from a wide variety of sources, including intrusion detection systems (IDS), firewalls, and security information and event management (SIEM) solutions. With so much data to sort through to filter out the false positives from the real threats, analysts can easily become overwhelmed and allow issues to fall through the cracks.
CaaP unifies the data from these individual sources and gives teams a single dashboard from which to view and analyze events. Plus, CaaP supports integrations with tools that can automatically analyze, filter, and remediate security incidents, reducing the risk of human error and freeing up security teams to work on high-priority issues.
→ Simplifying security management – It’s very difficult (if not impossible) for a single security analyst to become an expert in 100+ different products, each of which has its own interface, nomenclature, compatibility issues, etc. Plus, simply logging into every one of these tools on a regular basis takes a significant amount of time, making it far too easy for analysts to neglect or forget critical security systems.
With the right Cybersecurity-as-a-Platform, analysts can integrate all their security tools into one common platform, reducing the number of discrete solutions they need to learn, maintain, and support. This both reduces the risk of human error and reduces the workload on overwhelmed security teams.
→ Improving security posture – The more complex a system is, the more prone it is to failure. A cybersecurity strategy that relies on the continued operation and effectiveness of over 100 individual moving parts is more likely to fail because an issue with even one of those tools could lead to a breach. Plus, without a centralized view of how these parts work together, there’s no way to get a complete picture of an organization’s security posture.
CaaP gives analysts the ability to monitor and maintain all their security tools in one place, so they can see alerts about new vulnerabilities, apply patches, and more. They can also ensure all these tools are working together as expected so there are no gaps in coverage, and see data and visualizations about the security of the organization as a whole.
Adopt the CaaP approach to security with ZPE Systems
Cybersecurity-as-a-Platform is a unified, tightly integrated solution that rolls up a vast ecosystem of security tools behind one pane of glass. CaaP is the future of holistic security because it empowers efficient security monitoring and management while providing a complete overview of an organization’s security posture. True CaaP, like the Nodegrid solution from ZPE Systems, is completely vendor-neutral. This gives you the freedom to bring in your choice of cybersecurity solutions and automation tools, so you get the best features, functionality, and performance for your unique environment.
Want to learn more about cybersecurity platforms with Nodegrid?
Organizations are starting to recognize the benefits of edge computing, which moves data processing resources closer to the sources of data generation and away from the central data center. In addition, businesses are becoming more geographically dispersed, with branch offices, manufacturing facilities, and other remote sites around the world.
While larger remote sites are typically connected to the enterprise network via WAN or SD-WAN, this may not be feasible for smaller branches with fewer staff. Traditionally, VPNs (virtual private networks) are used to create a private connection for remote systems and users. However, a new technology called Zero Trust Network Access improves upon VPNs by providing faster and more secure remote connections.
What is a VPN?
A VPN, or virtual private network, is a service that creates an encrypted connection between a device and a network. In this particular use case, VPNs are used to extend the enterprise network to branch and edge locations. Often, organizations use VPNs as an alternative to installing expensive WAN solutions in very small remote sites. They’re also used to connect sites that are unreachable by traditional network infrastructure, such as offshore oil rigs.
Though VPN traffic is encrypted, there are still security risks. Many VPNs still use single-factor authentication, meaning all you need is a username and password to connect. If a remote user’s account information is stolen, a hacker could easily gain access because they don’t need to provide a second form of identity verification.
In addition, VPNs grant complete access to the enterprise network, trusting remote users and devices just like they were in the main office. That means a malicious actor could use a compromised account or stolen laptop to move laterally around your enterprise network, stealing whatever data they can find.
What is Zero Trust Network Access (ZTNA)?
Zero trust network access, or ZTNA, is another product or service that connects remote users and devices to enterprise network resources. However, instead of creating a tunnel to the enterprise network itself, ZTNA directly connects users to the applications and services they need. Users then need to re-verify their identity and re-establish trust before they access another application.
ZTNA follows the “dark cloud” concept, which prevents remote users from seeing or interacting with any of the data, systems, or applications they aren’t explicitly authenticated to. Microsegmentation is used to create perimeters around each resource with granular, context-based access control policies.
For example, if a branch office employee uses ZTNA to access the shipping system, they can’t see or touch the payroll application unless they authenticate to that specific resource. If the account is behaving suspiciously (logging in at unusual times, accessing resources it doesn’t typically need, etc.) then the account is locked until trust can be re-established. The dark cloud principle prevents malicious actors from discovering valuable resources and moving laterally on the enterprise network.
Comparing zero trust network access vs. VPN for branch and edge networking
Trust
Zero trust network access is more secure than VPNs because it follows the zero trust security model of “never trust, always verify.” Branch and edge accounts are assumed to be untrustworthy until they prove otherwise through repeated identity verification and trustworthy behavior. Remote accounts never have full access to the enterprise network and can only see and interact with the specific resources they’re presently authenticated to.
Authentication
While newer VPNs may allow integrations with third-party MFA (multi-factor authentication) providers like Okta, many organizations are still using single-factor authentication for VPN clients. That makes it much easier for a hacker to use a single set of stolen credentials to gain unrestricted access to the enterprise network. In addition, if a branch employee leaves their VPN session active and their laptop is stolen (for example, because it was in an unsecured building that’s open to the public), the thief can use that session to jump around the network without ever needing to re-verify or re-authenticate.
Performance
VPN connections are notoriously slow. All VPN traffic needs to be backhauled through a centralized concentrator, which creates massive bottlenecks and network latency. ZTNA, on the other hand, connects branch and edge devices directly to the resources they need. If that resource lives on the web or in the cloud, the traffic bypasses the enterprise network entirely, reducing the load and improving performance for everyone.
Scalability
Finally, VPNs are meant to be deployed to individual users on a case-by-case basis. Scaling up is difficult and expensive because you need to purchase licenses and install software for each machine that connects. Also, the more VPN connections, the greater the impact on network performance, and the more VPN concentrator solutions you’ll need to deploy to distribute the load. Gartner predicts that by 2025, 75% of enterprise-generated data will be processed at the edge, so individual VPN solutions won’t be able to keep up.
ZTNA is often delivered on the “as-a-service” model, which means it’s hosted in the cloud and doesn’t require any customer premises equipment (CPE). Licenses are scaled up or down at the click of a button, and there’s no software to install on remote machines. This makes ZTNA the ideal choice for enterprises hoping to expand their global reach or scale up their edge computing capabilities.
Deploying ZTNA for branch and edge networks
Zero trust network access is available as a standalone service, but you can also find it among the cloud-oriented security stack in a Security Service Edge (SSE) solution. SSE combines ZTNA with security technology such as Cloud Access Security Broker (CASB), Secure Web Gateway (SWG), and Firewall-as-a-Service (FWaaS). This suite of cloud security features delivers comprehensive protection for branch and edge networks while reducing the need for remote traffic to pass through the central data center.
ZPE Systems delivers innovative solutions to simplify infrastructure managment at the datacenter, branch, and edge.
Learn how our Zero Pain Ecosystem can solve your biggest network orchestration pain points.