Providing Out-of-Band Connectivity to Mission-Critical IT Resources

Operational Technology Security
An engineer using a tablet to control robotic machinery illustrates a use case for operational technology security

Managing and securing operational technology (OT) is notoriously challenging because of stakeholder focus on continuity and safety. This is only becoming more difficult as OT systems and networks grow more complex and distributed. Operational technology is a rare but valuable target of cyberattacks due to the severe impact on business operations and a relative lack of cybersecurity monitoring due to physical security requirements and GRC. It is simply harder to blend cybersecurity into operational security when the stakes are high and availability and continuity are the prime focus.

Early attempts to apply IT-specific security controls to OT had mixed success. A particular tool may work well in one scenario, but fail in another project. Some solutions meant to simplify OT management, such as NMAP (or Network Mapper), could even turn into weapons in the wrong hands. For example, the AvosLocker ransomware variant uses NMAP NSE (NMAP Scripting Engine) to scan endpoints for the Log4shell vulnerability and select targets to exploit.

This guide defines OT, explains how to overcome some of the biggest operational technology security challenges, and discusses the importance of recovery in building resilience in OT.

Table of Contents:

What is operational technology (OT)?

Operational technology (OT) includes any equipment interacting with the real world, as well as the systems that control such equipment. Some examples of OT equipment include HVAC systems, door controls, industrial machinery, fluid system sensors, and medical robotics. Examples of OT control systems include programmable logic controllers (PLC), supervisory control and data acquisition systems (SCADA), building management systems (BMS), and building automation systems (BAS). These control systems enable a high degree of automation in fields like industrial manufacturing, water and energy utilities, building management, and medicine.
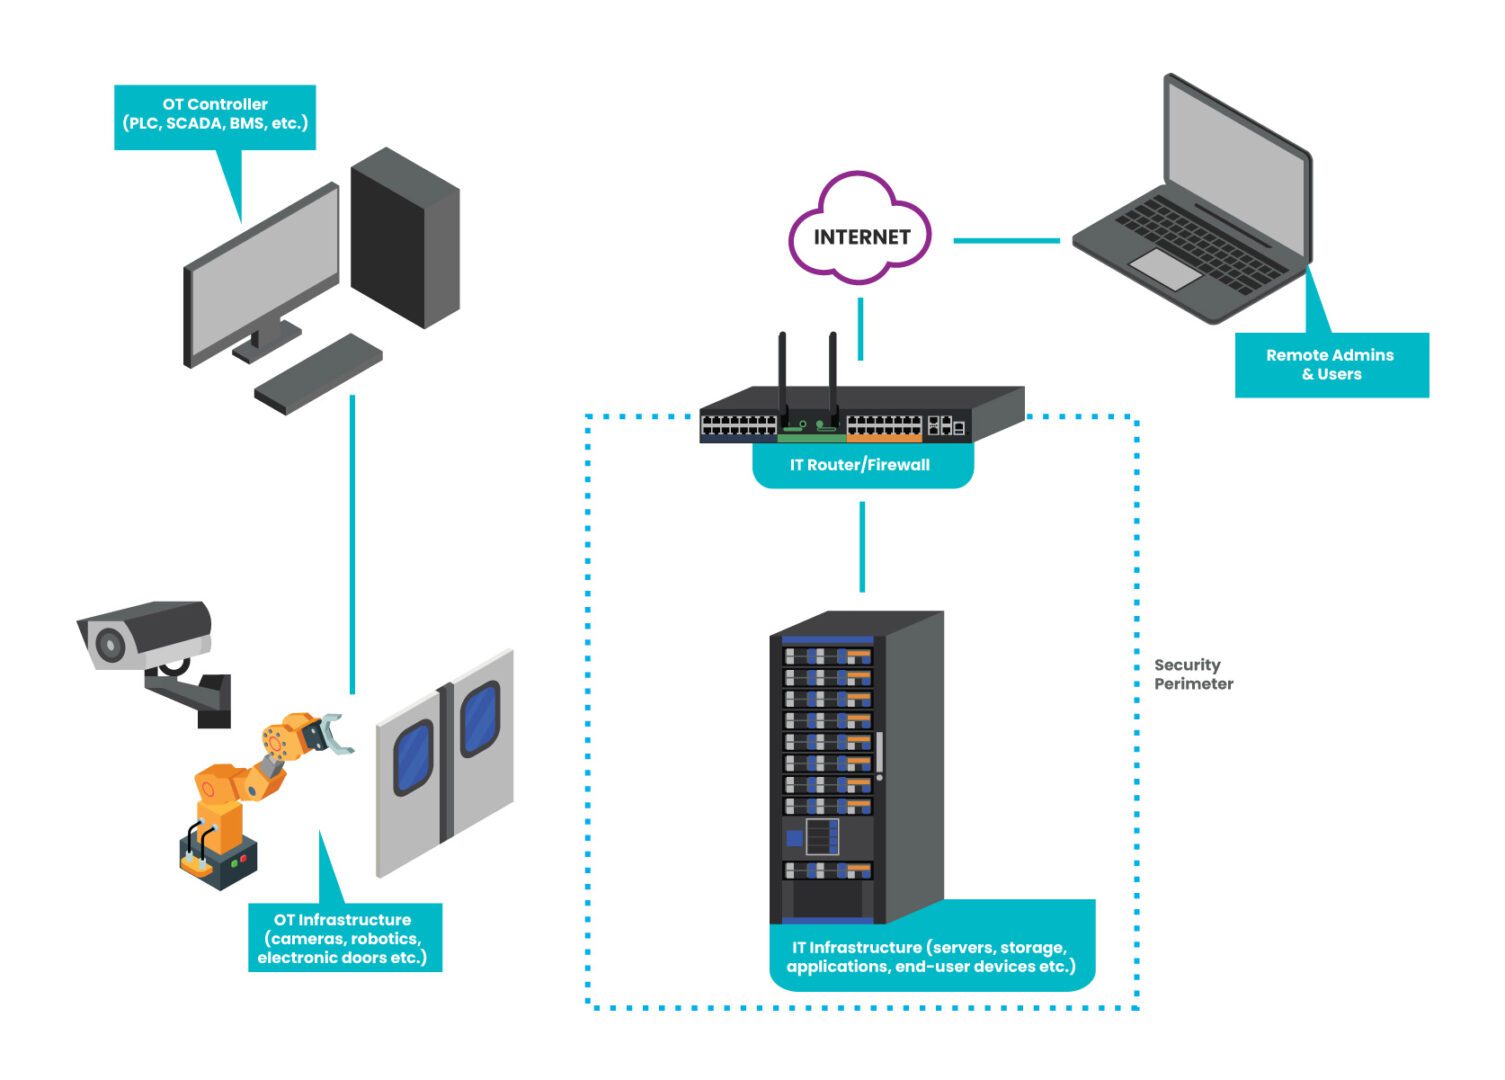
 
OT-Security-Mockup(2)

Figure: An example of how a typical OT network is isolated from the IT network & security infrastructure.

Operational technology security challenges & solutions

It’s tempting to believe that operational technology is safe from cyberattacks because it’s often isolated from the IT network—the “security through obscurity” approach. However, OT is a very tempting target for malicious actors because it’s so critical to business operations. Recent research from Barracuda Networks found that over 90 percent of manufacturing organizations experienced cyber attacks on their production or energy supply in 2021. An OT attack can completely halt manufacturing lines, interrupt oil and gas supplies, or prevent life-saving procedures from taking place.

Operational technology security is a crucial focal point, but significant challenges exist.

Challenge: OT security tools are a double-edged sword

Network Mapper, or NMAP, is a widely-used network management tool. NMAP started as a simple scanner in 1997 but evolved over the years into a solid open-source tool for OS detection, software version detection, and other network discovery features. NMAP aids in OT security by mapping exposed operational technology controls for teams to patch and secure. However, in the wrong hands, this tool could be used in intelligence gathering to attack vulnerable, out-of-date systems.

The problem with tools like NMAP is that they only discover information about systems with open ports on the same network as the tool – usually the production network. If an authorized network admin can find OS versioning information on the production network, so can an unauthorized user with stolen credentials.

Security teams need an efficient way to discover, patch, and manage operational technology without exposing these systems to cybercriminals.

Solution: Out-of-band (OOB) OT management

An out-of-band (OOB) network uses dedicated network infrastructure to create a control plane that’s completely isolated from the production network. An out-of-band serial console is the most efficient way to create an OOB network. This device directly connects to OT equipment and control systems via management ports (e.g., RS232 Serial), allowing administrators to monitor and patch vulnerabilities without exposing OS/versioning information to production.

An OOB serial console also uses alternative network interfaces—such as LTE cellular or dial-up—to ensure this management network is always remotely accessible by administrators, even when the production ISP, WAN, or LAN goes down from a failure or breach. With this added redundancy, teams can recover and restore critical OT operations much faster, even when the outage occurs in a remote or hard-to-reach location.

An out-of-band OT management solution provides efficient patch management without exposing vulnerable systems to cybercriminals. OOB also streamlines OT recovery efforts to minimize the impact of successful attacks and other failures.

Challenge: OT isolation hinders disaster recovery and Zero Trust

Since operational technology is often isolated from the IT network on its own LAN, there usually isn’t any way to access the control systems remotely. Operators must be on-site to use SCADA or PLC systems to monitor and control industrial processes. If on-site access is impossible, for example, due to a global pandemic or natural disaster, OT operations completely shut down. For example, increased tornadoes, floods, and other natural disasters in the midwest have forced major companies like General Motors and Amazon to close regional plants and logistics centers. When workers are sent home, operations grind to a halt unless operators have a way to access their OT control system remotely.

In addition, this separation makes it difficult to extend Zero Trust to operational technology. Without strong authentication, granular security policies, and targeted protection, there’s a significant risk of breaches. Plus, a lack of Zero Trust makes it difficult to contain the lateral movement of a malicious actor who’s using stolen credentials, which increases the blast radius and business impact of cyber incidents. 

Organizations need a way to minimize operational disruptions from natural disasters and apply Zero Trust to OT networks if they want to improve their resilience.

Solution: IT/OT convergence with vendor-neutral platforms

IT/OT convergence involves bringing information technology and operational technology together under one management umbrella and securely bridging the gap between the two networks. 

An IT/OT convergence strategy improves business resilience in two ways:

  1. It brings OT onto the same enterprise network as IT systems which facilitates the use of remote tools (like VPNs or ZTNA), giving operators access to OT control systems from off-site
  2. It brings OT within the purview of Zero Trust security controls like multi-factor authentication (MFA), identity and access management (IAM), and deep packet inspection (DPI)

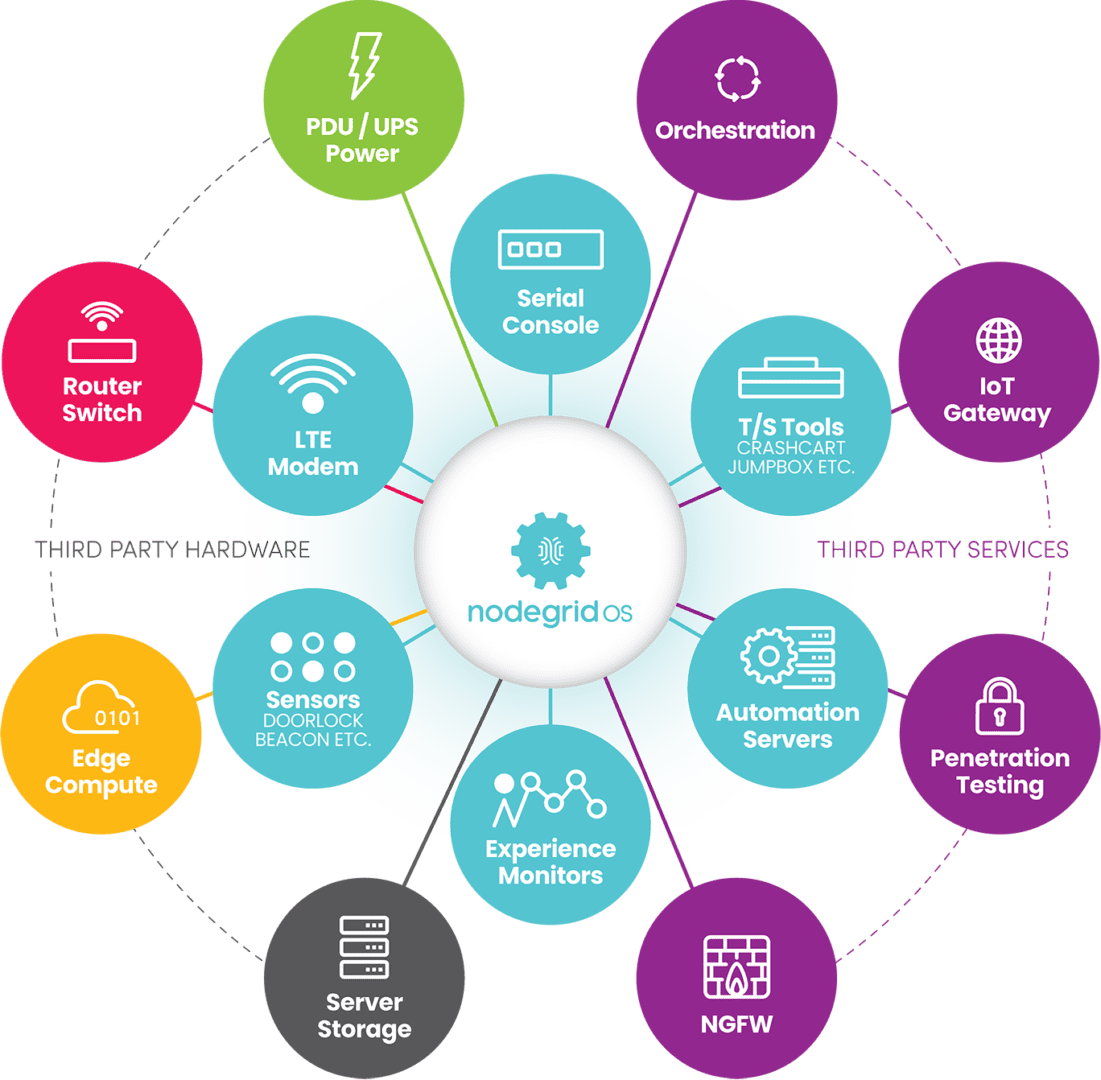
The easiest way to achieve IT/OT convergence without gaps is to use a vendor-neutral management and orchestration platform. For example, an OOB serial console with an open OS architecture that can dig its hooks into multi-vendor OT systems will give administrators a single-pane-of-glass view of the converged IT/OT infrastructure. A platform that can host or integrate 3rd party Zero Trust solutions will also enable unified orchestration of IT and OT security. 

By converging IT and OT, organizations can keep business running during natural disasters and limit the blast radius of breaches. A vendor-neutral platform also provides unified security orchestration for greater coverage and improved efficiency.

Operational technology security & resilience

A comprehensive operational technology security strategy will help improve resilience by preventing some cybersecurity incidents and reducing the impact of the rest. However, it’s impossible to ensure 100% protection, especially with ransomware attacks on the rise. That’s why it’s important to distinguish between security and resilience; security provides preventative measures, but resilience is your ability to withstand adversity and keep business flowing. 

One of the best measures of resilience is how quickly you can recover from outages caused by failures and attacks. And the best way to ensure a speedy recovery, according to the experts at Gartner and the CISA, is by using isolated management infrastructure such as OOB serial consoles to create an isolated recovery environment (IRE). This gives teams a dedicated environment, insulated from ransomware and production failures, where they can rebuild and restore critical services. 

Download our whitepaper 3 Steps to Ransomware Recovery for more guidance on streamlining IT/OT recovery and improving business resilience.


Building OT security & resilience with Nodegrid

The Nodegrid platform from ZPE Systems is a complete resilience solution that delivers OOB operational technology management and vendor-neutral IT/OT convergence. Using Nodegrid out-of-band solutions as your isolated management infrastructure ensures teams will have 24/7 remote access to monitor, patch, troubleshoot, and recover operational technology. The open, Linux-based Nodegrid OS supports VM and container hosting and easy integrations so you can deploy and control 3rd party applications for Zero Trust, OT management, and more from a single platform. Nodegrid can also host all the tools your team needs to recover and rebuild critical services — including to fully destroy and rebuild production networks — making it the perfect solution for building an isolated recovery environment.

Nodegrid can also run 3rd-party automation solutions such as software-defined networking (SDN)/software-defined wide area networking (SD-WAN), infrastructure as code (IaC), and artificial intelligence for IT operations (AIOps). Automating workloads helps reduce the risk of human error, while automating root-cause analysis (RCA) and security event analysis can significantly speed up recovery efforts, creating a more resilient network.

Learn how Nodegrid delivers unified orchestration and out-of-band management!

Nodegrid delivers unified orchestration and out-of-band management to help you build your zero trust security architecture. Contact ZPE Systems today to learn more.
Contact Us

Medical Devices Cybersecurity Risk

A hacker’s laptop connects to a stethoscope to represent medical devices cybersecurity risk

The healthcare industry is one of the largest adopters of “Internet of Things” (IoT) technology, using internet-enabled devices to monitor patient health, dispense lifesaving medication, perform medical procedures, and more. Some examples of IoT devices used in healthcare include insulin pumps, pacemakers, heart rate monitors, and intracardiac defibrillators. These devices allow healthcare teams to provide advanced care in bustling urban centers as well as remote or rural areas where frequent in-person visits are impossible.

However, these devices often run outdated software due to the difficulty of patch management and the time-intensive nature of updates, which end up getting bumped from the schedules of busy metropolitan teams. In addition, healthcare organizations and patients alike often sacrifice security hygiene for convenience, increasing the likelihood of stolen credentials and compromised devices. Plus, since these devices often operate in patient homes and other locations outside the organization’s network, security teams may not even know if an IoT device is stolen or compromised until it’s too late.

Many cybercriminals target IoT medical devices to harvest sensitive health data, but in the process could cause a pacemaker to crash and severely injure the patient. To address the growing threat of ransomware and other cyberattacks on patient health devices, the FDA recently issued a set of guidelines for securing medical devices. In this post, we’ll discuss the factors that make medical devices a cybersecurity risk before providing mitigation strategies to help healthcare organizations meet FDA requirements.

Table of Contents:

What makes medical devices a cybersecurity risk?

Every internet-enabled device expands an organization’s attack surface, giving cybercriminals something new to compromise and gain access to data and other resources. Medical devices are particularly risky for three reasons.

  • Outdated software – It’s difficult to update software on remote, wearable, or implanted medical devices without causing a (potentially dangerous) disruption to the patient. A recent FBI report showed that 53% of IoT medical devices had known, unpatched vulnerabilities in their software, making them more susceptible to cyberattacks.
  • Poor security hygiene – Teams often deploy medical devices with easy, insecure passwords for ease of use. While this may make operating and troubleshooting these devices easier for busy healthcare practitioners, it also significantly increases the cybersecurity risk.
  • Inadequate monitoring – Once medical devices leave the central network, it can be difficult for admins to monitor software versioning, account activity, device location, and other critical security metrics. That means they may not be aware of breaches or failures that put patient health at risk.

Medical device cybersecurity risk mitigation strategies

Due to the increased frequency of attacks and the potential to cause patient harm, the FDA released guidance earlier this year to address medical device cybersecurity risks. For the FDA to consider a medical device “secure,” there must be plans and processes in place to monitor, identify, and patch vulnerabilities, both on a routine schedule and as soon as possible in response to specific threats. There are also additional requirements to demonstrate that reasonable security measures are in place, including strong authentication.

This guidance is intentionally broad, giving general rules without detailing exactly how to achieve compliance. Let’s discuss three specific risk mitigation strategies that address the above mentioned risk factors and meet FDA guidelines.

Automated patch management

Medical device manufacturers and service providers must continuously monitor for vulnerabilities and release software patches on a regular schedule to comply with the FDA’s ruling. Automated monitoring, configuration management, and software delivery tools can all help teams stay on top of demanding patch schedules. On the consumer side, healthcare teams can use automated patch management solutions to ensure updates are installed as soon as they’re available, reducing manual workloads and improving device security.

Zero trust security

Zero trust security is a methodology that involves applying highly specific security policies and building checkpoints of security controls around individual network resources. Zero trust requires strong passwords and uses technology like multi-factor authentication (MFA) to prevent compromised accounts from accessing devices or data. Zero trust is difficult to achieve, and it can be challenging to get overworked healthcare providers or elderly patients to follow stricter password guidelines, but it’s quickly becoming standard practice for new medical devices and cloud services. Teams can help smooth the transition by providing additional training and support when deploying new healthcare technology.

Vendor-neutral monitoring

Administrators need to track device metrics to ensure the equipment functions correctly and identify any signs of compromise. Often, devices come with software monitoring solutions that are specific to a particular vendor, but most healthcare teams deploy a wide variety of equipment from multiple vendors. As a result, admins must log in to several different dashboards, all of which provide varying degrees of coverage and granularity. A vendor-neutral monitoring platform can unify all these disparate systems, making it easier to track device health and spot potential problems.

Medical device security, recovery, and resilience

Medical devices pose a significant cybersecurity risk, and the consequences of successful breaches could be deadly. The FDA urges medical device providers to follow guidelines for vulnerability monitoring, patch management, and overall cybersecurity. In addition, healthcare organizations can use automated patch management, zero trust security, and vendor-neutral monitoring platforms to improve their security posture.

It’s also vital that organizations have a plan for how to recover remote medical devices that are compromised by ransomware or other cyberattacks. The faster teams can restore, rebuild, or replace the device, the better the patient’s health outcomes. This combination of security and recovery planning makes healthcare networks more resilient to cyberattacks and failures.

For example, the Nodegrid platform from ZPE Systems allows healthcare teams to deploy automation, zero trust security, monitoring, recovery tools, and more from one unified system. Nodegrid’s out-of-band management solutions can also be used to build an isolated recovery environment where teams can rebuild and restore compromised systems with the risk of reinfection.

To learn more about recovering from ransomware and other medical device cybersecurity risks, download our whitepaper, 3 Steps to Ransomware Recovery.

Download the Whitepaper

Learn more about recovering from ransomware and other medical device cybersecurity risks!

Nodegrid allows healthcare teams to deploy automation, zero trust security, monitoring, recovery tools, and more from one unified system. 

Contact Us

Zero Trust Security Architecture

The words zero trust in a circle with simulated computer architecture as the background.

In today’s economy, businesses can’t afford to neglect their cybersecurity architecture. According to a recent report, cybercrime damages are expected to reach $10.5 trillion annually by 2025. Attacks are more frequent and damaging, thanks partly to the difficulty in establishing a solid security perimeter around a modern enterprise network. With Internet of Things (IoT) device usage on the rise and networks expanding to include remote branch offices and edge data centers, it can be impossible to clearly define the boundaries of a network, let alone effectively defend those boundaries. For example, many organizations use tools like Citrix to enable secure remote access to enterprise resources, but recently, high-risk vulnerabilities were discovered in several Citrix gateway products. The very tools we rely on to defend our expanding perimeter may leave us the most exposed to attacks.

The zero trust security methodology was created to address the challenges involved in traditional, perimeter-based defense strategies. This post defines a zero trust security architecture, discusses some of the gaps typically left in such an architecture and provides tips for avoiding these pitfalls.

Table of Contents:

What is a zero trust security architecture?

A zero trust security architecture is designed around the principle of “never trust, always verify.” Traditional security architectures assume that every user and device should be implicitly trusted as long as they’re inside the organization’s network perimeter. That assumption leaves compromised accounts and malicious insiders free to move laterally around the network, accessing and exfiltrating data or executing ransomware in the process.

On the other hand, a zero trust security architecture assumes that every account and device is already compromised unless trust is continuously established. The zero trust methodology was founded by Forrester analyst John Kindervag in 2009; the same year, Google’s BeyondCorp project launched with the sole purpose of defining and developing a zero trust security architecture.

Zero trust uses network micro-segmentation, advanced authentication, Layer 7 (application-level) threat monitoring, and highly-granular security policies to verify trust and prevent lateral movement. Risk is calculated for each resource on the network, and then micro-perimeters of specific security controls are built around the resource micro-segment. Users and devices must establish trust each time they hit a micro-perimeter no matter how elevated their accounts are or where they’re accessing the network from, making it easier to spot and disable a compromised account. This is how a zero trust architecture limits the blast radius and duration – and thus the cost – of cyberattacks.
.

Tips for implementing zero trust without gaps

Zero trust is not a single solution to purchase and deploy in your enterprise – it’s a combination of tools, policies, and proccesses that contribute to a more resilient network. The complexity of a zero trust architecture makes it prone to gaps. For example, manually configuring and managing so many moving parts increases the risk of human error. Additionally, zero trust doesn’t prevent 100% of attacks, but many organizations lack a comprehensive recovery plan. Plus, you can’t have a zero trust environment unless you isolate all administrative interfaces for infrastructure.

During the planning stage of your zero trust security implementation, you should keep the following three questions in mind:

  1. How will you manage so many different policies and solutions?
  2. Do you have tools to aid you in recovering from a successful attack?
  3. How will you protect your control plane from malicious actors on your network?

Addressing these challenges with the following best practices will help you build a successful zero trust security architecture.

Reduce human error with centralized orchestration

A zero trust security architecture includes hundreds or thousands of individual security policies and solutions. Configuring and managing this architecture is a monumental task prone to human error, leading to potential vulnerabilities. According to Microsoft, configuration errors cause 80% of ransomware attacks, making human error a major threat to network resilience. The best way to reduce complexity and prevent mistakes is to be able to see and manage all your solutions from one place, with the ability to automate regardless of skill level.

A centralized security orchestration platform allows administrators to configure, monitor, deploy, and automation all their zero trust solutions from a single place. The best practice is to use a vendor-neutral platform that integrates with third-party zero trust vendors for identity and access management (IAM), next-generation firewalls (NGFWs), and more. Such a platform allows organizations to build bespoke micro-perimeters using the preferred solutions, regardless of vendor, and still manage the entire architecture from a single pane of glass. Plus, with a holistic view of the security architecture, organizations gain a more accurate perspective on their overall security posture and have the context needed to spot systemic issues or subtle indicators of a breach.

Prioritize incident response and recovery planning

According to a recent report from Check Point Research, the global volume of cyberattacks reached an average of 1168 per week per organization in Q4 of 2022. That means there’s no question of “if” a breach will occur, only “when” it will happen. It’s essential to consider incident response and recovery when you build your zero trust security architecture to reduce the cost of an attack.

Research from Sophos found that 70% of organizations hit by ransomware took longer than two weeks to recover, implying they didn’t have the right recovery architecture in place. Downtime gets more expensive the longer it goes on, so organizations must improve their recovery capabilities. For example, data backups are critical to recovery efforts, so they must be protected by zero trust authentication and policies to prevent compromise or corruption. In addition, backup data, systems, and infrastructure must be validated with security scans before they’re restored to ensure they don’t reinfect the network with malware. Getting business back up and running as soon as possible will decrease the cost of cyberattacks, which means a recovery toolkit is an essential component of a zero trust architecture.

Secure the control plane on a dedicated OOB network

The management interfaces used by administrators to control network infrastructure are often excluded from cybersecurity planning because because end users don’t access them. Only admins have usernames and passwords, and they trust their own security hygiene, so they (incorrectly) assume these interfaces are safe. If zero trust policies aren’t applied to the control plane, a compromised administrator account could completely wipe out your infrastructure and gain unfettered access to sensitive data and backups. The blast radius of such an attack would be devastating and severely hamper recovery efforts.

A recent CISA directive provides guidance for reducing the risk of open management ports. The best practice for a zero trust security architecture is to keep the control plane on a separate, out-of-band (OOB) network. An OOB network uses dedicated infrastructure that’s isolated from the production LAN, preventing lateral movement by attackers. This also allows administrators to perform recovery operations even when ransomware or hardware compromises bring down the production network. In addition, zero trust policies and controls must be applied to the OOB control plane to prevent a compromised administrator account from gaining too much access.

Tips for building a zero trust security architecture
  • A vendor-neutral security orchestration platform reduces management complexity and mitigates the risk of human error
  • Integrating a recovery toolkit in the architecture will help limit the cost and business disruption of successful attacks
  • Keeping the control plane on an OOB network and applying zero trust policies and controls will limit the blast radius of a breach

The zero trust methodology asks us to assume that devices and accounts are already compromised, and attackers have breached the network, requiring everyone to continuously prove trustworthiness before accessing enterprise resources. A successful zero trust architecture is unified by a vendor-neutral orchestration platform, prioritizes business resilience and recovery, and secures management interfaces with the same strict policies and controls as the production network.

Build your zero trust security architecture with Nodegrid

Building such an architecture is easier with the Nodegrid solution from ZPE Systems. Nodegrid is a vendor-neutral security orchestration platform that delivers unified control of the entire architecture of zero-trust policies and controls to reduce complexity and mitigate the risk of human error. Nodegrid branch gateway routers and serial console servers provide secure OOB management, so you get an isolated control plane without deploying an entire secondary network. You can even use Nodegrid to build an isolated recovery environment (IRE) to streamline ransomware recovery and reduce the business impact of attacks.

Learn how Nodegrid delivers unified orchestration and out-of-band management!

Nodegrid delivers unified orchestration and out-of-band management to help you build your zero trust security architecture. Contact ZPE Systems today to learn more.
Contact Us

SSE Magic Quadrant: Key Takeaways of the 2023 Report

The SSE Magic Quadrant describes top cloud security service vendors, conceptualized as a cloud with glowing network nodes and a padlock.

Gartner’s SSE Magic Quadrant for 2023 identifies 10 key vendors currently providing secure service edge capabilities for the enterprise market. In this guide, we’ll summarize the common factors shared among leading SSE vendors, discuss what separates them from niche players, and share advice for connecting your edge network to SSE solutions via an SD-WAN on-ramp.

Table of Contents:
  1. What is Security Service Edge (SSE)?
  2. What is the need for SSE?
  3. What is the SSE Magic Quadrant?
  4. What has changed since the 2022 SSE Magic Quadrant?
  5. Key takeaways from the 2023 SSE Magic Quadrant
  6. SD-WAN: An on-ramp for SSE
  7. What to look for in an ideal SSE on-ramp
  8. Why Nodegrid is the ideal SSE on-ramp

What is Security Service Edge (SSE)?

Security service edge (SSE) is a cloud-centric security methodology for protecting edge network traffic. It rolls up technologies like Firewall-as-a-Service (FWaaS), Zero Trust Network Access (ZTNA), and Cloud Access Security Brokers (CASB) into a single service. These technologies offer threat protection, security monitoring, access control, and data governance.

What is the need for SSE?

With the frequency and severity of ransomware attacks and other cybercrimes increasing daily, security is a major priority for any organization. To protect your enterprise from cyber threats, you need to be able to extend your security policies and controls to all the remote and geographically distributed systems at your network edge. Historically, that meant backhauling all remote traffic through your primary firewall, which would inevitably cause performance issues for everyone on the network. This is frustrating and can greatly impact the business when much of your remote traffic is destined for cloud and web resources that aren’t even on your enterprise network.

SSE solves this problem by taking advanced enterprise security technologies and making them available as a cloud-based service. You can use SD-WAN with intelligent routing (more on that later) to send remote and branch office traffic through your SSE stack. This allows you to apply consistent policies and controls to your enterprise and edge traffic while reducing bottlenecks and increasing overall network performance.
.

Learn more about SSE:

Gartner’s 2023 SSE Magic Quadrant Summarized

Challengers

Leaders

Cisco (SIG)

Netskope
Zscaler
Palo Alto Networks (Prisma Access)

Niche Players

Visionaries

Broadcom
iboss
Cloudflare

Skyhigh Security
Forcepoint (Bitglass)
Lookout

There are many reasons why an SSE vendor would be considered a niche player, including that the market hasn’t caught on to them yet due to poor marketing or sales strategies. However, one common caution among niche players is a failure to fully integrate SSE components, which means customers must use multiple dashboards to manage a single SSE solution. Another common issue is poor support during sales, implementation, and operation, leading to frustration among enterprises with less experience in edge networking and security.

On the other hand, the leaders of the SSE Magic Quadrant share a few common characteristics as well. For one, they have strong marketing and sales outreach, a clear vision, and a roadmap for the future. This vision is essential because it allows enterprises to ensure their goals and strategies align with where their SSE vendor is headed.

In addition, these solutions’ components are tightly integrated with a single, unified management platform for more accessible and efficient operation. Magic Quadrant leaders invest in and implement new security features frequently, bug-free, and with adequate documentation and support. That means customers can stay ahead of emerging security threats without worrying about breaking their existing setups.

What has changed since the 2022 SSE Magic Quadrant?

There are three major changes to Magic Quadrant this year.

  • Palo Alto Networks moves from Challenger to Leader: In 2022, Palo Alto extended its Prisma Access SSE solution to better integrate with Prisma SD-WAN, enhance its proxy and ZTNA components, and add SaaS Security Posture Management (SSPM).
  • McAfee splits its cloud business into Skyhigh Security: Early in 2022, McAfee enterprise split into two, with its cloud business now known as Skyhigh Security. This split disrupted Skyhigh’s growth and market share and moved this SSE offering from the Leaders quadrant to the Visionaries quadrant.
  • Versa leaves the SSE Magic Quadrant: Versa no longer ranks in the top 20 organizations in Gartner’s market momentum index (MMI), so it isn’t included in the 2023 Magic Quadrant.

Key takeaways from the 2023 SSE Magic Quadrant

  • Most vendors prioritized improving their core capabilities and better integrating their product, rather than focusing on new features and other innovations.
  • Vendors who fail to fully integrate their SSE offering into a unified platform are quickly losing market share.
  • WFH traffic is less of a concern for enterprises than branch/edge sites, so SD-WAN access and integrations are critical.

Overall, the biggest takeaway from the SSE Magic Quadrant is the importance of a seamlessly-integrated platform. A consolidated platform ensures complete visibility and control over your security service edge solution without needing to learn and operate multiple consoles.

On top of this, to use SSE’s cloud-delivered solution, you need a reliable way to send traffic from your branch and edge locations to the SSE stack. That means part of the architecture needs to include an access solution that can tunnel traffic from these locations to the cloud, such as SD-WAN. The access solution serves as an on-ramp to SSE, and requires a physical appliance for on-premises installations. This framework combining SD-WAN access with SSE is how SASE (secure access service edge) is built.

SD-WAN: An on-ramp to SSE

Security service edge provides the technology to protect your edge-based cloud-destined traffic, but you still need a way to get that traffic to your SSE platform. This is known as an SSE on-ramp, and it’s not included in any of the SSE Magic Quadrant solutions. However, one of Gartner’s selection criteria was the ability to integrate with SD-WAN technology.

An SSE on-ramp uses SD-WAN (software-defined wide area network) technology to route remote and branch office traffic to your SSE stack in the cloud. SD-WAN separates the control and management processes from your underlying WAN hardware and virtualizes them as software, making it possible to centrally control and orchestrate even very complex and distributed WANs. With SD-WAN, you can use intelligent and application-aware routing to connect your edge users directly to the SSE platform, cloud, and web resources.

What to look for in an ideal SSE on-ramp

The ideal on-ramp to SSE will support seamless integration with your SSE platform, and vice-versa. In addition, the right solution will provide additional capabilities like the ones listed below.

Features of an ideal SSE on-ramp include:

Versatile tunneling

Physical hardware that’s easy to provision with a versatile tunnel mechanism to SSE, including IPsec and WireGuard, with simple cloud management. Ideally this tunneling mechanism uses application-aware traffic steering to make it an effective part of an SD-WAN on-ramp.

Integrated L3/L4 firewall

Integrated Layer 3/Layer 4 firewall technology to secure incoming traffic to your remote and branch locations, including VPN support. The ideal on-ramp has local segmentation capabilities and zero-trust, since SSE can’t do local segmentation on its own without help from on-premises equipment, agents, or VMs.

Out-of-band (OOB) management

OOB management for a direct, dedicated network connection to the SD-WAN on-ramp that doesn’t rely on cloud-based in-band connectivity. OOB access and provisioning are ideal to gain greater control over remote networking infrastructure on a dedicated connection.

Multiple WAN interfaces

Flexible and redundant WAN interfaces to ensure 24/7 availability. At least one of these should include a 5G/4G LTE modem with 2 SIM slots for high-speed cellular failover and out-of-band access when the primary WAN link is down.

Terminal server

Terminal server/serial console/”jump box” port management for easy remote management of edge infrastructure. This should include the ability to host third-party troubleshooting tools so admins can easily recover from outages without going on-site.

Computing power

Compute capabilities to run third-party apps and Docker containers right at the network edge. With built-in compute it’s easier to extend the functionality of SSE with additional applications that may not be part of the SSE stack or need an edge Docker footprint, like vulnerability scanning or user experience monitoring agents.

Centralized automation

Unified management of automation like Zero Touch Provisioning (ZTP) to automatically spin-up edge devices and connect them to SSE. Automation can significantly speed up branch deployments while reducing the risk of human error.

Why Nodegrid is the ideal SSE on-ramp

The Nodegrid branch and edge networking solution from ZPE Systems combines all the capabilities of the ideal SSE on-ramp in a single platform. For example, the Nodegrid Net Services Router (NSR) is a customizable, all-in-one device with available modules for storage, compute, serial console management, and more. The vendor-neutral NSR can host your preferred SD-WAN solution and supports easy integrations with SSE Magic Quadrant Leaders like Palo Alto Prisma Access, or you can use ZPE Cloud’s integrated SD-WAN app.

Thanks to the open-architecture, Linux-based Nodegrid OS, you can also extend Nodegrid’s capabilities with your choice of custom and third-party applications for security, monitoring, automation, and more. Plus, every device, application, and integration connected to the Nodegrid platform is brought under a single management umbrella for a unified and efficient orchestration experience. 

The Nodegrid platform from ZPE Systems rolls up everything you need in an SSE on-ramp and delivers it in one powerful, unified edge networking solution.

Learn how Nodegrid easily hosts and integrates Gartner’s picks for the 2023 SSE Magic Quadrant!

Contact ZPE Systems today!

Contact Us

What is an Application Delivery Platform?

An illustration showing a breakout of various software application components to highlight the need for an application delivery platform

Modern software architectures are highly complex and often very difficult to maintain and operate. A single enterprise application comprises hundreds (or even thousands) of individual services, technologies, and toolchains while requiring a lot of underlying infrastructure, such as servers, routing and load balancing rules, and security controls. All of this complexity increases overhead costs and adds to the ever-growing workloads of software, network, and infrastructure teams, especially when you multiply this effort across dozens or hundreds of software deployments.

Platform engineering is a new discipline introduced by Gartner to address these challenges by reducing the complexity of software engineering, network operations, and application delivery. The platforms built by these engineers are known by several names, including internal developer platforms, internal developer portals, and application delivery platforms. This guide defines an application delivery platform, discusses the underlying technology, and highlights a leading platform engineering solution.
.

Table of Contents:
  1. What is an application delivery platform?
  2. What is the importance of an application delivery platform?
  3. What technology makes up an application delivery platform?
  4. Introducing ZPE Systems’ Services Delivery Platform

What is an application delivery platform?

An application delivery platform is a suite of technologies that handles all the services that support an application, including security, traffic management, load balancing, and data management. Platform engineers combine all these services into a common toolset used to deploy applications at customer sites, so there’s no need to build a new architecture every time. This streamlined experience makes application delivery cost-effective by significantly reducing workloads and deployment timelines.

What is the importance of an application delivery platform?

The goal of an application delivery platform is to reduce deployment and management complexity. Deployment complexity leads to a greater risk of human error when configuring things like security controls and access policies, and any mistakes are likely to be found and exploited by cybercriminals. Management complexity makes it harder to stay on top of patch schedules. Unpatched software often contains vulnerabilities that are exploited by cybercriminals; for example, known ransomware groups targeted unpatched IBM software earlier this year.

By reducing complexity, an application delivery platform also reduces the attack surface, improving an organization’s overall security posture.

What technology makes up an application delivery platform?

By its very nature, an application delivery platform is highly customized to fit the needs of the applications being supported. Here are some examples of the services and technologies that are often included.

  • Server storage & compute: The platform needs storage (usually solid-state) and processing units (CPUs or GPUs) to run the applications and store necessary data. Ideally, the OS and computing architecture will support containers (e.g., Docker) for microservices applications.
  •  
  • Automation tools: A key feature of application delivery platforms is the ability to automatically provision and deploy new environments, apps, and network services as well activate services licenses and service chaining. That means the platform should host automation tools for configuration management, code delivery, and software-defined networking (SDN).
  •  
  • Security: The ideal platform makes it possible to deliver applications without configuring security every time. That means it provides unified management and repeatable deployments for security services like firewall traffic inspection, access control lists, and advanced authentication.
  •  
  • Routing & load balancing: A lot of backend networking goes into the typical application deployment to ensure traffic is routed correctly and optimized for performance. An application delivery platform should support network functions virtualization (NFVs) and SDN so standard network configurations can be easily deployed alongside the applications being delivered.
  • Management tools: Engineers need a way to remotely access, manage, and troubleshoot application deployments, even (and especially) during major service disruptions. The ideal platform includes out-of-band serial console management and supports third-party troubleshooting tools so remote teams can quickly recover systems and applications without an expensive on-site visit.

While this list is far from exhaustive, it covers the foundational technology that supports an application delivery platform. Platform engineering is still in its infancy, and many organizations struggle to efficiently execute it because of how many moving pieces need to be considered. The goal is to find a solution that provides the best framework of hardware and software capabilities that platform engineers can build upon, so they can create a fully customized application delivery platform without reinventing the wheel.

Introducing ZPE Systems’ Services Delivery Platform

Zero Pain Ecosysteme

The Services Delivery Platform from ZPE Systems is the perfect foundation for any platform engineering initiative. Nodegrid edge routers serve as the hardware backbone, providing networking and failover capabilities, OOB serial console management, and plenty of memory, storage, and CPU headroom for additional apps and services. You can build a fully customized hardware platform with the modular Net Services Router (NSR), extending your storage or compute capabilities or adding more ports to support your application deployment.

The vendor-neutral, Linux-based Nodegrid OS can run your custom applications as well as third-party automation, security, DevOps, and management tools. Plus, Nodegrid unifies all connected services and applications under a single management umbrella, allowing teams to oversee and orchestrate all of their deployments from one convenient portal.


Ready to Learn More?

The Services Delivery Platform from ZPE Systems simplifies platform engineering with powerful, multipurpose hardware and an open, vendor-neutral OS. Contact us today to learn more about using Nodegrid for your application delivery platform!

Contact Us