Providing Out-of-Band Connectivity to Mission-Critical IT Resources

SD-WAN ROI Calculator & Cost Reduction Strategies
sd-wan roi calculator

As an organization expands by adding new branches, its WAN also expands. The larger the WAN grows, the more network traffic needs to flow through MPLS (multi-protocol label switching) circuits, which have much more expensive bandwidth fees than traditional circuits. Some organizations improve their network performance by deploying security appliances at regional data centers, so they don’t need to backhaul traffic through the central firewall, but this only increases MPLS expenses and operating costs. Plus, spinning up each branch takes time, partly because of how long it takes to install a new MPLS circuit, which reduces agility and increases overhead costs.

SD-WAN, or software-defined wide area networking, abstracts WAN management to a separate control plane, streamlining workflows and allowing for a high degree of automation. SD-WAN makes it possible to leverage 5G and other networking technologies to reduce the reliance on MPLS circuits while still applying security policies and controls. With SD-WAN, you can lower your MPLS bandwidth costs, reduce the number of security appliances deployed around the enterprise, and deploy new branches faster.

In this post, we describe how SD-WAN decreases branch networking costs. We also explore strategies to reduce your expenses, providing an SD-WAN ROI calculator for a more personalized estimate of your potential savings.

How SD-WAN reduces branch networking costs


Reducing branch networking costs with SD-WAN

SD-WAN decreases MPLS bandwidth expenses by leveraging 5G and other available networks when possible.
An SD-WAN on-ramp to SASE means fewer security appliances deployed around the enterprise.
SD-WAN results in faster branch deployments by decreasing the reliance on new MPLS circuit installations.


Implementing SD-WAN can result in the following cost reduction benefits.

Decreased MPLS bandwidth expenses

In a traditional WAN architecture, MPLS circuits are installed at each branch to create a semi-private connection back to the primary enterprise network; this traffic isn’t encrypted, but it is partitioned from the public internet and other MPLS customers. MPLS networks are very reliable, but the bandwidth is significantly more expensive than public internet bandwidth. Finding ways to reduce the amount of traffic over MPLS circuits can reduce the ongoing operational costs of each branch.

SD-WAN leverages whatever networks are at its disposal—including MPLS, public ISPs, and 5G/4G cellular—to find the best and most efficient path for branch traffic. An organization can use SD-WAN software to prioritize specific kinds of traffic based on parameters such as the apps or resources being requested, so precious MPLS bandwidth is only used when needed. Many organizations are able to move away from MPLS completely by using SD-WAN. Providers are also required to build their SD-WAN fabric from encrypted tunnels, allowing SD-WAN to direct traffic over the public internet with less risk.

Cost reduction strategy: secure access service edge (SASE)

Even with SD-WAN’s encryption, branch traffic still needs to pass through a security appliance in the central data center so enterprise security policies and controls can be applied, which likely means using the MPLS anyway. Secure access service edge, or SASE, rolls up multiple enterprise security technologies (such as next-generation firewalls (NGFWs) and data loss prevention) into a single solution delivered as a service, which means organizations can deploy it to regional data centers or even the branches themselves. SD-WAN’s intelligent routing feature can determine when branch traffic is destined for cloud or web resources, then direct this traffic through the SASE stack instead of using the MPLS to reach the central firewall. SASE can help eliminate MPLS usage completely while reducing bottlenecks for greater cost savings.

With SD-WAN and SASE, your organization can reduce the ongoing monthly expense of MPLS bandwidth at each branch without sacrificing reliability or security.


Fewer security appliances

To ensure that branch traffic is as secure as the primary enterprise network, teams usually backhaul that traffic through the same central firewall for inspection and policy application. This creates a massive bottleneck that can slow the entire enterprise down, so some organizations choose to deploy security appliances at smaller regional data centers near their branch locations to distribute the load. However, that usually means additional MPLS circuits are provisioned at each data center, increasing startup and bandwidth costs. Plus, there are the hardware, software, and licensing costs for all the additional security appliances.

We’ve already mentioned how SD-WAN leverages alternative networks (as well as encrypted tunnels) to reduce MPLS bandwidth usage and how SASE applies enterprise security controls to branch traffic while bypassing firewalls entirely. These two benefits also result in cost savings from needing to purchase and license fewer security appliances. Since vendors deliver SASE as a service, it doesn’t necessarily require special hardware to run, and some providers even offer it as a managed cloud service, eliminating the hardware cost altogether.

Cost reduction strategy: vendor-neutral solutions

On-premises versions of SASE usually don’t need vendor-specific hardware so you can deploy the software on any available server as a VM. However, many branches lack the extra server storage or computer headroom needed for this kind of deployment. To ensure you can deploy SASE without buying additional resources, consider vendor-neutral branch networking solutions that can directly host and run third-party VMs. That means you can get gateway routing, switching, out-of-band serial console management, and SASE in a single device, consolidating the branch networking stack to reduce hardware expenses and management complexity.

With SD-WAN, SASE, and vendor-neutral solutions, you can streamline your branch deployments to reduce costs and increase efficiency.


Faster branch deployments

Generally speaking, the faster a company can deploy a new branch, the faster it will see a return on investment (ROI). However, getting a new MPLS circuit provisioned can take a long time—several months is typical—which can delay deployment timelines and increase overhead expenses while an organization sits on a non-productive branch.

SD-WAN makes it possible to leverage alternative network technologies to get a branch up and running before the MPLS circuit is ready. For example, SD-WAN can direct branch traffic across a 5G network even before the main fiber or cable connection is installed. When all of the branch circuits are provisioned, SD-WAN can seamlessly incorporate them into its routing policies based on preconfigured policies and automation triggers for a smooth deployment. In short, SD-WAN eliminates the organization’s reliance on MPLS for revenue generation, with branches that can be fully operational as soon as LTE or ISP links are set up.

Cost reduction strategy: zero touch provisioning (ZTP)

Another way to reduce branch spin-up times is with zero touch provisioning, or ZTP. ZTP uses software scripts to execute new device configurations over the network, reducing the need for pre-staging or manual, on-site programming. Typical branch deployments involve sending engineers on-site to manually copy and paste configuration files, which is time consuming and increases the risk of human error. With ZTP, unskilled on-site staff simply plug in new device cables and the configuration scripts are automatically retrieved and executed to fully build the environment without human touch. Plus, ZTP scripts are reusable, so you can use the same ones to deploy many different branches.

With SD-WAN and ZTP, your organization can reduce branch deployment delays and see a faster ROI from new branches.


SD-WAN ROI calculator

ZPE Systems provides vendor-neutral branch networking solutions that can directly host or integrate your choice of SD-WAN and SASE applications. ZPE’s platform also allows you to extend ZTP and other automation to every device in every branch on your network. Check out our SD-WAN ROI calculator for a customized estimate of how much money you can save by deploying SD-WAN on ZPE’s platform.

ZPE System’s Nodegrid solution combines branch networking, out-of-band management, and vendor-neutral orchestration into a single platform.

To learn more about using Nodegrid as your on-ramp to SD-WAN, or for help with the SD-WAN ROI calculator, contact ZPE Systems today
Contact Us

Atsign: Why Choose ZPE Systems to Host IoT Security?

Colin

A Conversation with Atsign CTO & Co-Founder, Colin Constable

This is a guest post composed by Atsign, creators of zero-attack-surface solutions including atProtocol.

We recently sat down with our CTO and Mariposa Rotary Club extraordinaire, Colin Constable, to discuss our partnership with our friends over at ZPE Systems. Let’s explore the driving force behind this powerful partnership, and how together we’re securing IoT devices and the data shared between them.

Why is this partnership strategically important?

We are a software company that helps people connect beyond the edge of the Internet. And as a software company, we need to have hardware to run our software on. After looking at a number of hardware platforms, ZPE stood out as an organization that provides a strong array of network connectivity options. Our software running on ZPE’s hardware serves as an edge platform that gives customers reliable access to edge-generated data.

What are some of the synergies between Atsign and ZPE?

First and foremost, ZPE’s hardware was designed from scratch to provide the openness and flexibility that we were looking for in a hardware platform. If I were going to design something like this myself, it would look very much like a ZPE box! It is incredibly easy to drop our Docker containers straight onto the platform, and they just simply work, which is quite a joy. To have a Docker container environment on an edge box is really the thing that makes ZPE stand out as a platform. Combine that with the fact that ZPE boxes are running x86, which makes things easy–plus actually having dual SIM cards–we can work with our MVNO partners to provide constant connectivity; even if hardlines go down, there’s cellular backup. The thing we can offer ZPE and their customers is if the box can see the Internet, then you’ll be able to address it, get data to and from it, and actually even log into it, and get hold of the built-in UI on the box.

Tell us about ZPE’s Docker Container support

Our docker containers literally just ran perfectly on the ZPE hardware. I went into the UI, selected my docker container, and it just ran. It doesn’t get much easier than that. Plus, there’s the promise of being able to have the docker container talk to connected devices like V.24 cables to provide connectivity to IoT devices.

Once IoT devices become directly addressable, then it opens up all kinds of opportunities for more efficient delivery or sharing of information that can save customers tons of money by eliminating a lot of the current infrastructure they currently use to do that job.

What are some real-world use cases for Atsign and ZPE Systems?

Because ZPE boxes have lots of connectivity options (e.g. serial ports, 4/5G backhaul, and ethernet–with more coming!) for connecting IoT devices, then you can have always-on devices at the edge, and be able to address and get data to and from them. For example, a radio station that has DSL connectivity, and cellular backup would be able to just automatically move over to cellular backup, notify the radio station that it’s on cellular backup, but use that connectivity until the ADSL line comes back online and at all times be able to get information from the equipment at the radio station. This is critical for radio stations, as it eliminates “dead air,” that moment when the transmitter is not transmitting. Sponsors rely on radio stations to put out notifications for what their businesses are doing, so having constant, uninterrupted connectivity is essential.

Do Atsign & ZPE Systems improve sustainability?

Traditional solutions would have you installing many different boxes. What we really like about the ZPE platform is that although the hardware provides lots of connectivity options–that reduces the footprint for starters–there’s no need to have different modems and firewalls, and any other services can be added via docker containers, so you actually have an environment where you have a single box, and it can do multiple functions at the edge.

What are your final thoughts on the partnership between Atsign and ZPE Systems?

As a software company, we need hardware to deploy on. We especially need hardware that can sit on the edge with all the right connectivity points. Atsign and ZPE Systems is really a perfect combination of great software and great hardware at the edge.

Bonus: What is Colin’s favorite firewall configuration for a ZPE box?

My favorite firewall rule is the one that costs the least money, and is ultimately the most secure firewall ruleset: Deny All. If you’ve got Deny All, that means that you don’t have to deal with the pain and complexities of firewall rules in order to address devices, which is what the real cost of networking is these days; it’s not necessarily the hardware, it’s actually having people to administer firewall rulesets. Having zero network attack surfaces, having a Deny All ruleset, just means you don’t have to have people changing rulesets all the time, which is a good thing.

99.999% Uptime for a Top-10 Engineering School

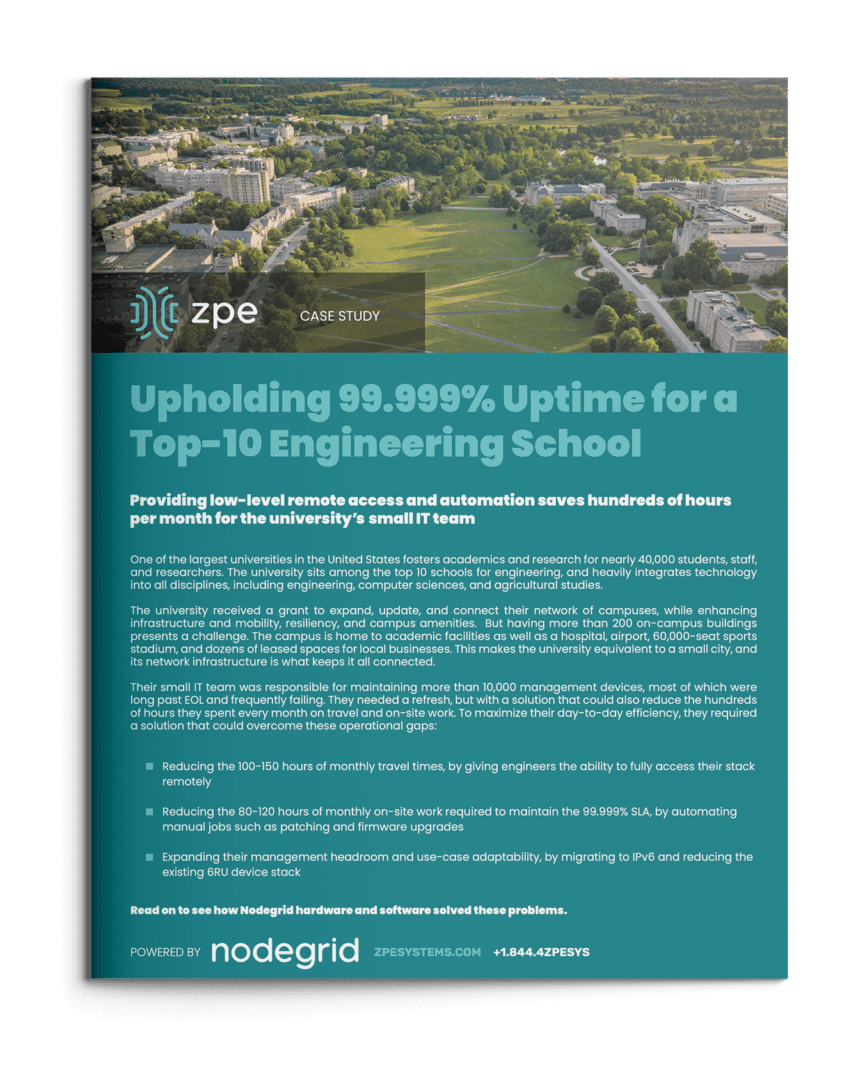
Providing low-level remote access and automation saves hundreds of hours per month for the university’s small IT team

One of the largest universities in the United States fosters academics and research for nearly 40,000 students, staff, and researchers. The university sits among the top 10 schools for engineering, and heavily integrates technology into all disciplines, including engineering, computer sciences, and agricultural studies.

The university received a grant to expand, update, and connect their network of campuses, while enhancing infrastructure and mobility, resiliency, and campus amenities.  But having more than 200 on-campus buildings presents a challenge. The campus is home to academic facilities as well as a hospital, airport, 60,000-seat sports stadium, and dozens of leased spaces for local businesses. This makes the university equivalent to a small city, and its network infrastructure is what keeps it all connected.

Their small IT team was responsible for maintaining more than 10,000 management devices, most of which were long past EOL and frequently failing. They needed a refresh, but with a solution that could also reduce the hundreds of hours they spent every month on travel and on-site work. To maximize their day-to-day efficiency, they required a solution that could overcome these operational gaps:

  • Reducing the 100-150 hours of monthly travel times, by giving engineers the ability to fully access their stack remotely
  • Reducing the 80-120 hours of monthly on-site work required to maintain the 99.999% SLA, by automating manual jobs such as patching and firmware upgrades
  • Expanding their management headroom and use-case adaptability, by migrating to IPv6 and reducing the existing 6RU device stack

Download the full case study to see how ZPE’s Nodegrid hardware and software solved these problems.

EngineeringSchoolCover

Download the full case study

Problems and Gaps

The university is one of the largest in the United States. It sits among the nation’s top 50 schools for research expenditures, and heavily integrates technology into all disciplines, including engineering. Its main campus is home to more than 200 buildings that sit on over 2,500 acres of land. The campus is essentially a small city, and the university’s network infrastructure keeps it all connected.

This network infrastructure, however, was well beyond EOL and in disrepair. But rather than simply upgrade to newer devices, the university’s small IT team wanted to improve the overall quality of life well into the future. This meant addressing three gaps:

  • Inefficient management at scale — Each engineer spent an average of ten hours per month on travel alone, just to traverse the campus’ wide footprint and get to each MDF/IDF closet.
  • Too much focus on ops — The aging infrastructure was on the brink of collapse and required each engineer to spend eight hours per month in on-site work, just to keep devices running.
  • Too many devices — The infrastructure includes roughly 10,000 devices to manage, which was exhausting IP on their limited IPv4 network and too rigid to fit in tight spaces, like their remote farm closets and research labs.

Solution

The university deployed the full lineup of Nodegrid devices, including the Nodegrid Serial Console, Nodegrid Services Routers, and Nodegrid Manager. These allowed them to overcome all three gaps using remote management, automation, and consolidated functionality, to save engineers hundreds of hours every month. Download the full case study to see the complete solution and benefits.

Need Help Replacing End-of-Life Gear?

Check out our complete products and services package to make your EOL transition seamless. Choose from a variety of Synopsys-validated devices, get a generous trade-in discount, and let our engineers install and configure into your environment. Click below to explore this offer and more customer case studies.

Best Intel NUC Alternatives

Intel NUC Alternatives

Service providers often struggle with the hybrid nature of their business. Even as they transition more towards a consumable service-based model that’s decoupled from traditional hardware solutions, there’s still a need for some sort of box to be deployed physically at a customer’s premises. Providers frequently rely on COTS (Common Off The Shelf) hardware to reduce costs and simplify the deployment process.

One commonly used COTS device is the Intel NUC, or “Next Unit of Computing,” which is a small appliance-like mini computer. Some service providers utilize Intel NUC devices as jump boxes, while others use them as a platform to deploy their services on-site. While these mini-computers are relatively inexpensive and easy to install, they create added security risks and management headaches that service providers need to be aware of.

This post highlights the challenges and security risks involved in relying on Intel NUC devices before discussing enterprise-grade Intel NUC alternatives that solve these problems.

Table of contents:


Why is Intel NUC so popular in IT infrastructure?

Managed Service Providers (MSPs) and Managed Security Service Providers (MSSPs) often use Intel NUC jump boxes to remotely access the control plane of critical client infrastructure. These mini PCs typically run bare bones software to reduce licensing costs, which means they are unpatched, unmonitored, and unsecured. This lack of oversight and management makes Intel NUCs popular access points for hackers to breach client networks.

Why consider Intel NUC alternatives?

Service providers like to use Intel NUC boxes because they’re cheaper, faster to install, and take up less space than a full PC or server. NUCs are often deployed without antivirus, monitoring agents, or other security software installed, which excludes them from the service provider’s security coverage. Plus, clients are frequently unaware that these devices are in their racks accessing their infrastructure, so they don’t access them in security and compliance audits. Other Intel NUC challenges include:

  • Lack of centralized management – Each Intel NUC is an island that’s managed and accessed individually, which makes it impossible to efficiently deploy updates, install new tools, or monitor for problems.
  • Insecure, unpatched OS – Operating systems and software contain thousands of potential vulnerabilities that hackers can exploit, so a lack of monitoring and patch management creates a huge security risk.
  • No hardware security – Intel NUC boxes lack any hardware security, which means someone could steal the device and use it to deploy malware or access client resources – or even just pawn the hardware.
  • Regulatory issues – When providers use unmanaged jump boxes to access client infrastructure, they expose their customers to potential noncompliance with privacy laws like HIPAA that require strict data access controls.
  • Affects insurance eligibility – Using an unsecured Intel NUC may also disqualify customers from receiving cybersecurity insurance benefits in the event of a successful breach.

While Intel NUCs are a quick and inexpensive way for MSPs, MSSPs, and other service providers to remotely access client infrastructure, they also make it easier for cybercriminals to breach enterprise networks. To reduce the attack surface without increasing the cost, hassle, or footprint of deploying jump boxes, you need an enterprise-grade solution that combines networking functions, security, and remote out-of-band access to the control plane to eliminate the need for a separate device.

Intel NUC alternatives from ZPE Systems

The Nodegrid product line from ZPE Systems simplifies the tech stack in data centers and network closets with all-in-one infrastructure management solutions. Nodegrid devices roll up gateway routing, switching, Wi-Fi, and 5G/4G/LTE out-of-band management to cut down on the number of boxes in the rack. They’re also enterprise solutions, which means they can be onboarded with your security team and covered by your monitoring, intrusion detection, antivirus, and other security controls.

In addition, all Nodegrid boxes are protected by hardware security features such as BIOS protection, self-encrypted disk (SED), UEFI Secure Boot, and Signed OS. Plus, Nodegrid’s hardware and software are completely vendor-neutral, allowing easy integrations with third-party security solutions and SAML 2.0 authentication. Nodegrid can even directly host other vendors’ security software to further reduce your tech stack.

Key Nodegrid features


All Nodegrid Devices Include:

Key features

Strong Out-of-band management integration

Extensible applications with virtualization and containers

Zero Touch Provisioning (ZTP) over the WAN

Vendor-neutral, unified management via ZPE Cloud/Nodegrid Manager

Modern x86-64bit Linux Kernel

Extended automation based on actionable data

Failover to 4G/5G/LTE & Wi-Fi

Power control and monitoring

Orchestration support via Puppet, Chef, Ansible, RESTful

Security

BIOS protection

TPM 2.0

UEFI Secure Boot

Signed OS

Self-Encrypted Disk (SED)

Geofencing

X.509 SSH certificate support, 4096-bit encryption keys

Selectable cryptographic protocols for SSH and HTTPS (TLSv1.3)

Selectable cypher suite levels: high, medium, low, custom

SSL VPN (Client and Server)

IPSec, Wireguard, and Strongswan with support for multi-sites

Local, AD/LDAP, RADIUS, TACACS+, Kerberos, authentication

SAML support via DUO, OKTA, Ping Identity

Local, backup-user authentication support

User-access lists per port

Group/role-based authorization: AD/LDAP, RADIUS, TACACS+

Fine grain and role-based access control

Firewall – IP packet and security filtering, IP forwarding support

MD5 / SHA System Configuration Checksum™

System event syslog

Custom security settings

Strong password enforcement

Two-Factor Authentication with RSA and DUO

Networking

IPv4 / IPv6 Support

Embedded Layer 2 switching

VLAN

Layer 3 Routing

BGP

OSFP

RIP

QoS

DHCP (Client and Server)

RIPv1, RIPv2

VXLAN

DDNS

NTP

To learn more about the benefits of Nodegrid’s Intel NUC alternatives, contact ZPE Systems.

Nodegrid product comparison

The Nodegrid family of network edge routers delivers secure, Gen 3 OOB management for reliable remote access to distributed customer sites like branch offices or manufacturing centers.

Nodegrid Service Delivery Platform Family


Link SR

Bold SR

Hive SR

Gate SR

Net SR

Mini SR

CPU

X86-64bit Intel 

X86-64bit Intel

X86-64bit Intel 

X86-64bit Intel 

X86-64bit Intel 

X86-64bit Intel 

Cores

2

4 or 8

4 or 8

2, 4 or 8

2, 4, 8 or 16

4

Guest VM

1

1

1-2

1-3

1-6

1

Guest Docker

2+

2+

2+

2+

2+

2+

Storage

16GB – 128GB

32GB – 128GB

16GB – 128GB

32GB – 128GB

32GB – 128GB

14GB SED

Additional Storage

Up to 4TB

Up to 4TB

Up to 4TB

Up to 4TB

Up to 4TB

–

Wi-Fi

Yes

Yes

Yes

Yes

Yes

Yes

Cellular modem

1

1-2

1-2

1-2

1-6

1

5G

–

Yes

Dual 5G

Dual 5G

6x 5G

–

Sim slots

2

4

4

4

12

1

Serial Console Switch

1

8

Via USB

8

16-80

Via USB

Network

1x Gb ETH 1x SFP

5x Gb ETH

2x GbE ETH 2x 10 Gbps

4x 10/100/1000/2.5 Gbps RJ-45

2x SFP 5x Gb ETH

4x 1Gb ETH PoE+

2x 1Gb ETH 2x SFP+ Multiple expansion cards

2x 1Gb ETH

Data Sheet

Download

Download

Download

Download

Download

Download

The Nodegrid family of Intel NUC alternatives from ZPE Systems can help MSPs and MSSPs ensure secure, reliable remote management access to customer infrastructure without increasing costs.

Ready for a Demo?

To see one of ZPE’s Intel NUC alternatives in action, request a free Nodegrid demo! Request a Demo

Cisco 2900 EOL: Replacement Options

cisco 2900 eol

The Cisco ISR 2900 series of branch routers went EOS (end-of-sale) on the 9th of December 2017, and Cisco concluded support on the 31st of December 2022. In this guide, we’ll compare migration options for the Cisco ISR 2900 EOL models to help you select a solution that supports your business use case, deployment size, and future growth.

Disclaimer: This comparison was written by a third party in collaboration with ZPE Systems using data gathered from publicly available data sheets and admin guides, as of 5/12/2023. Please email us if you have corrections or edits, or want to review additional attributes: Matrix@zpesystems.com


Table of Contents

Cisco ISR 2900 overview

The Cisco ISR 2900 is a line of enterprise gateway routers designed for branch and edge networking. It’s a modular solution that can be expanded with optional Network Interface Modules (NIMs) and Service Modules (SMs) for more functionality. There are two primary use cases for the 2900:

Converged branch networking – The ISR 2900 easily integrates with Cisco’s SD-WAN, SD-Branch, cloud security, and DNA network management software, can be extended with optional modules for added hardware capabilities, and supports NFV (network functions virtualization) for all-in-one branch networking.

Out-of-band (OOB) management – Using serial port modules, the ISR 2900 turns into an out-of-band (OOB) serial console solution that provides remote management access to the control plane of branch infrastructure.

The ISR 2900 is officially EOL as of the 31st of December 2022. The EOL models include all 2901, 2911, 2921, and 2951 ISR product SKUs.

Looking for replacement options for your other Cisco ISR EOL products? Read our guide to Cisco ISR EOL Replacement Options.


Cisco 2900 EOL replacement options

The discontinuation of the Cisco 2900 has left many organizations looking for migration options. Let’s compare two direct replacements from Cisco before discussing alternative options that deliver better branch management capabilities and greater opportunities for automation.

Cisco ISR 1100

Cisco ISR 1100 is a series of enterprise branch routers, though in this comparison we’re only looking at the models that support SD-WAN and thus serve as direct replacements for the discontinued 2900 models. The capabilities of the 1100 series vary, mostly because only some of the models are modular. For example, the fixed form-factor 1100-4G/4G LTE models have cellular functionality but offer fewer networking and security features. Conversely, the 1161X-8P and 112x-8P models are modular and can be extended with optional modules (like cellular for the 1161X or terminal server ports for the 112x-8P).

Even with these expansions, the compact ISR 1100s are best suited for smaller deployments in branch offices or small, provider-managed edge data centers. If your organization uses the ISR 2900 for converged branch networking, the 1100s are the closest Cisco replacement, though it supports OOB serial modules as well.

Cisco Catalyst C8300

The Cisco Catalyst C8300 series is a modular branch and edge networking solution, though due to its large size, it’s sometimes used as a primary on-premises gateway router. There are four models to choose from – two 2RU units with 2 SM and 2 NIM slots, and two 1RU units with 1 SM and 1 NIM slot. Each chassis comes with 6 embedded Layer3 Ethernet ports (1 Gbps and/or 10 Gbps) as well as a console port and USB port. All other port configurations and capabilities come via Cisco expansion modules, including options for 5G/4G cellular.

The Catalyst C8300 is a big, robust solution that’s designed for medium to large deployments such as campuses, colocation sites, and AI/machine learning data centers. The C8300 is primarily a converged branch networking solution like the ISR 1100 series, but it provides OOB management with optional serial cards.

Cisco 2900 replacement option comparison table


Cisco ISR 2900 (EOL)

Cisco ISR 1100

Cisco Catalyst 8300

Nodegrid Net SR

Nodegrid Serial Console Plus

Form Factor

1-2 RU

Desktop-1RU

1-2 RU

1 RU

1 RU

Max IPsec Throughput

Not defined

Up to 18.8 Gbps

Up to 18.8 Gbps

600 Mbps – 1.2 Gbps

600Mbps

Total Onboard WAN or LAN 10/100/1000 Ports

2-3

4-6

4-6

2

2

Total Onboard WAN or LAN 10Gbps Ports

0

0

0-2

2

2

WAN Ports

2-3

0-6

2-6

1+, configurable

0-4

LAN Ports

2-3

0-6

2-6

4-84

0-4

Slots

2-3

0-1

2-4

5

0

Default Memory

512 MB

4 GB

8 GB

8 GB

4 GB

Max Memory

2 GB

8 GB

32 GB

64 GB

16 GB

Compute

–

–

UCS-E Card

On-board, Compute card

On-board

OOB Capabilities

Requires Serial Card

Requires Serial Card

Requires Serial Card

Included

Included

Environmental Monitoring

N/A

N/A

N/A

Included

Included

For users looking for a Cisco solution to replace their EOL ISR 2900, the ISR 1100 series and Catalyst C8300 are the closest direct replacements. However, both product lines suffer from a major limitation – they aren’t vendor-neutral.

While Cisco routers integrate with some third-party partners, they do not support custom or third-party applications for automation and orchestration, which limits you to the automation offered by Cisco’s software. This lack of open integrations increases the chances that a Cisco solution won’t be able to hook into all the hardware and software components of a distributed and multi-vendor network architecture.

For example, if you utilize different SD-WAN and next-generation firewall (NGFW) vendors at some of your remote sites, Cisco’s automation may not extend to these devices. That means you’ll need to send out technicians to all remote sites (which could number in the dozens or hundreds) just to set up these services when you otherwise could have deployed them automatically.

Want to learn more about breaking free of locked ecosystems? Read The Benefits of Vendor Agnostic Platforms in Network Management

When network solutions like the Cisco 2900 go EOL, it’s the perfect opportunity to look for alternative options that provide the functionality you need without locking you into an ecosystem or limiting your automation capabilities.

Cisco 2900 direct replacement options from ZPE Systems

ZPE Systems provides a line of vendor-neutral solutions for branch and edge networking called Nodegrid. The Nodegrid Net Services Router (NSR) and Nodegrid Serial Console Plus (NSCP) serve as direct replacements for Cisco 2900 EOL products.

Nodegrid Net Services Router (NSR)

The Nodegrid NSR is a modular branch networking solution that you can customize to increase your terminal server ports, storage space, processing power, or switch ports. The NSR delivers converged branch networking capabilities like SD-WAN, SD-Branch, and NFVs, plus it can host your choice of custom and third-party applications for automation, security, and more.

While the NSR is the perfect converged branch solution to replace the Cisco ISR 2900, it also provides 3rd generation (or Gen 3) OOB management. That means Nodegrid’s OOB network is completely vendor-neutral and can extend automation capabilities to all your legacy and mixed-vendor infrastructure for efficient deployments, management, and orchestration.

Want to see the Nodegrid converged branch networking solution in action? Watch a Demo

Nodegrid Serial Console Plus (NSCP)

The NSCP is a robust, scalable branch networking and out-of-band serial console solution. The NSCP comes in 16-, 32-, 48-, and 96-port models, so you can choose the solution that’s right-sized to your deployment and use case. Plus, you can get built-in 5G/4G LTE and Wi-Fi options for failover and out-of-band.

Like the NSR, the NSCP is also an open platform that can run your choice of software to expand your capabilities and reduce your tech stack. Like the NSR, the NSCP delivers Gen 3 OOB management of all connected infrastructure, enabling true end-to-end automation in data centers, branches, and other remote sites. The NSCP is the perfect replacement for enterprises utilizing the Cisco 2900 for out-of-band management, though it also provides converged branch networking capabilities at any scale.

All Nodegrid devices run the open, Linux-based Nodegrid OS which can host your choice of third-party or custom applications, freeing you from vendor lock-in. You can even integrate infrastructure orchestration tools like Puppet, Chef, and Ansible to extend automation to end devices, regardless of vendor. This is what makes Nodegrid the world’s first Gen 3 branch networking solution.

Want to see how Nodegrid stacks up against Cisco’s replacement options? Click here to download the services routers comparative matrix.

Global support and supply chain

Leaving a trusted ecosystem behind to adopt alternative options can be risky, so it’s important to find a vendor that offers the support you need to make the transition and keep your operations running smoothly. ZPE Systems offers global product support using the “follow the sun” model, which means you get support when you need it, regardless of your timezone. You also won’t have to worry about supply chain issues causing stock shortages – ZPE supplies hyperscalers in 10K+ units per quarter and has great, consistent supply chain control.

Need to replace your Cisco 2900 EOL?

To learn more about replacing your Cisco 2900 EOL solution with the vendor-neutral Nodegrid platform and our shipping in as little as two weeks, contact ZPE Systems today. Contact Us

Cisco 2900 EOL product tables with migration SKUs

Cisco 2900 EOL Model

In Scope Features

Replacement Product (modular form factor)

Cisco ISR 2901

Cisco ISR 2911

Cisco ISR 2921

Cisco ISR 2951

Serial Console Module, Routing, 16 serial ports

ZPE-NSR-816-DAC with 1 x 16 port serial module 1 x ZPE-NSR-16SRL-EXPN

Cisco ISR 2901

Cisco ISR 2911

Cisco ISR 2921

Cisco ISR 2951

Serial Console Module, Routing, 32 serial ports

ZPE-NSR-816-DAC with 2×16 port serial module 2x ZPE-NSR-16SRL-EXPN

Cisco ISR 2901

Cisco ISR 2911

Cisco ISR 2921

Cisco ISR 2951

Serial Console Module, Routing, 48 serial ports

ZPE-NSR-816-DAC with 3×16 port serial module 3x ZPE-NSR-16SRL-EXPN

Cisco ISR 2901

Cisco ISR 2911

Cisco ISR 2921

Cisco ISR 2951

Serial Console Module, Routing, 60 serial ports

ZPE-NSR-816-DAC with 4×16 port serial module 4x ZPE-NSR-16SRL-EXPN

80 serial port option – no Cisco equivalent

Serial Console Module, Routing, 80 serial ports

ZPE-NSR-816-DAC with 5×16 port serial module 5x ZPE-NSR-16SRL-EXPN


Cisco 2900 EOL Model

In Scope Features

Replacement Product (fixed form factor)

Cisco ISR 2901

Cisco ISR 2911

Cisco ISR 2921

Cisco ISR 2951

Serial Console Module, Routing, 16 serial ports

ZPE-NSCP-T16R-STND-DAC

Cisco ISR 2901

Cisco ISR 2911

Cisco ISR 2921

Cisco ISR 2951

Serial Console Module, Routing, 32 serial ports

ZPE-NSCP-T32R-STND-DAC

Cisco ISR 2901

Cisco ISR 2911

Cisco ISR 2921

Cisco ISR 2951

Serial Console Module, Routing, 48 serial ports

ZPE-NSCP-T48R-STND-DAC

96 serial port option – no Cisco equivalent

Serial Console Module, Routing, 96 serial ports

ZPE-NSCP-T96R-STND-DAC

Want to see how Nodegrid compares to other serial console solutions?

Raspberry Pi Alternatives for Business

Raspberry Pi alternatives
Many businesses use Raspberry Pi devices as jump boxes to remotely access the control plane of critical infrastructure. By their very nature, these devices usually aren’t correctly managed or vetted by the security team. This creates a security challenge known as Shadow IT. Shadow IT is a situation that arises when an organization has devices in use that are not known to, or securely managed by, the IT or Information Security department. These unmanaged devices are vulnerable to attack, and Raspberry Pi jump boxes are particularly tempting targets to cybercriminals because they provide access to important remote infrastructure. This blog discusses the security risks of using Raspberry Pi jump boxes and provides solutions in the form of secure, enterprise-grade Raspberry Pi alternatives.

Why consider Raspberry Pi alternatives?

Unmanaged Raspberry Pi devices don’t receive patches, aren’t visible to change management systems, and are excluded from security audits. These unsecured devices are used to access critical remote infrastructure, which creates a number of security risks.

Raspberry Pi security risks

  • Malware vulnerability – Deploying Raspberry Pi devices without onboarding them with IT means they’re not protected by enterprise antimalware solutions, leaving them exposed to viruses and ransomware attacks.
  • Undetected misconfigurations – Since unmanaged Raspberry Pi devices aren’t monitored by security or change management systems, it’s more likely that misconfigurations and vulnerabilities will remain undetected, leaving a potential backdoor open for cybercriminals.
  • Lack of IAM – A Raspberry Pi jump box that isn’t covered by enterprise IAM (Identity and Access Management) is susceptible to attack because security teams can’t extend Zero Trust security policies or controls to protect it (e.g., multi-factor authentication, role-based access control, and single sign-on).
  • Non-compliance – For organizations in regulated industries, a Raspberry Pi jump box could expose them to potential liability, because the org can’t monitor who’s using that device to access what data, resulting in non-compliance with privacy laws like HIPAA.
  • Lack of centralized Fleet Management – Organizations who have hundreds or thousands of these jump boxes have no way to centrally manage them, which makes upgrades, app deployments, licensing, patch management, and other tasks more time-consuming.
  • Lack of secure OS – Operating systems and software contain thousands of common  vulnerabilities, and there’s no way to automatically apply security patches or OS upgrades to unmanaged Raspberry Pi devices.
  • Lack of secure HW – Raspberry Pi storage disks often aren’t encrypted and lack any sort of secure boot sequence or other onboard security features, which means a stolen device could be used to breach the network or introduce malware.

Ultimately, Raspberry Pi devices expand a company’s attack surface because they fall outside of enterprise security policies, controls, solutions, and monitoring. However, many organizations use a Raspberry Pi to avoid the expense of deploying another fully managed device as a jump box in every site that houses critical infrastructure. Overcoming this challenge requires an enterprise-grade networking solution that includes remote out-of-band access to the control plane to eliminate the need for a jump box altogether.

Looking for alternative options for your Intel NUC jump boxes? Read Best Intel NUC Alternatives

Raspberry Pi alternatives from ZPE Systems

The Nodegrid product line from ZPE Systems helps organizations avoid Shadow IT by simplifying the tech stack with all-in-one network management solutions. In addition to data center and branch networking functionality like gateway routing, switching, and Wi-Fi, all Nodegrid devices provide out-of-band (OOB) management access over 5G/4G LTE.

Nodegrid is more secure than a Raspberry Pi jump box because it’s an enterprise solution that’s onboarded with IT and covered by all your security policies, controls, and solutions. In addition, Nodegrid boxes themselves are protected by enterprise security features such as BIOS protection, Signed OS, UEFI Secure Boot, and self-encrypted disk (SED).

Plus, all Nodegrid devices are completely vendor-neutral, which means they easily integrate with third-party Zero Trust security solutions and can even directly host other vendors’ security software to further reduce your tech stack.

Key Nodegrid features

All Nodegrid Devices Include:

Key features

Strong Out-of-band management integration

Extensible applications with virtualization and containers

Zero Touch Provisioning (ZTP) over the WAN

Vendor-neutral, unified management via ZPE Cloud/Nodegrid Manager

Modern x86-64bit Linux Kernel

Extended automation based on actionable data

Failover to 4G/5G/LTE & Wi-Fi

Power control and monitoring

Orchestration support via Puppet, Chef, Ansible, RESTful

Security

BIOS protection

TPM 2.0

UEFI Secure Boot

Signed OS

Self-Encrypted Disk (SED)

Geofencing

X.509 SSH certificate support, 4096-bit encryption keys

Selectable cryptographic protocols for SSH and HTTPS (TLSv1.3)

Selectable cypher suite levels: high, medium, low, custom

SSL VPN (Client and Server)

IPSec, Wireguard, and Strongswan with support for multi-sites

Local, AD/LDAP, RADIUS, TACACS+, Kerberos, authentication

SAML support via DUO, OKTA, Ping Identity

Local, backup-user authentication support

User-access lists per port

Group/role-based authorization: AD/LDAP, RADIUS, TACACS+

Fine grain and role-based access control

Firewall – IP packet and security filtering, IP forwarding support

MD5 / SHA System Configuration Checksum™

System event syslog

Custom security settings

Strong password enforcement

Two-Factor Authentication with RSA and DUO

Networking

IPv4 / IPv6 Support

Embedded Layer 2 switching

VLAN

Layer 3 Routing

BGP

OSFP

RIP

QoS

DHCP (Client and Server)

RIPv1, RIPv2

VXLAN

DDNS

NTP

To learn more about the security benefits of Nodegrid’s Raspberry Pi alternatives, contact ZPE Systems.

Nodegrid product comparison

The Nodegrid product line includes serial console servers (also known as RS232 serial switches) for data center deployments, as well as network edge routers for distributed branch and campus sites. Each solution delivers Gen 3 OOB management and all-in-one networking in a variety of sizes and configurations to suit any use case.

Nodegrid Serial Consoles

Nodegrid Serial Console Plus

Nodegrid Serial Console S Series

CPU

X86-64bit Intel 

X86-64bit Intel

Guest Docker

1-2

1-2

Storage

32GB

32GB

Wi-Fi

Yes

Yes

Cellular (Dual-SIM)

2

None

Serial

16 – 96

Auto-sensing

Network

2x Gb ETH 2x SFP+

2x SFP

Data Sheet

Download

Download


Nodegrid Network Edge Routers

Link SR

Bold SR

Hive SR

Gate SR

Net SR

Mini SR

CPU

X86-64bit Intel 

X86-64bit Intel

X86-64bit Intel 

X86-64bit Intel 

X86-64bit Intel 

X86-64bit Intel 

Cores

2

4 or 8

4 or 8

2, 4 or 8

2, 4, 8 or 16

4

Guest VM

1

1

1-2

1-3

1-6

1

Guest Docker

2+

2+

2+

2+

2+

2+

Storage

16GB – 128GB

32GB – 128GB

16GB – 128GB

32GB – 128GB

32GB – 128GB

14GB SED

Additional Storage

Up to 4TB

Up to 4TB

Up to 4TB

Up to 4TB

Up to 4TB

–

Wi-Fi

Yes

Yes

Yes

Yes

Yes

Yes

Cellular modem

1

1-2

1-2

1-2

1-6

1

5G

–

Yes

Dual 5G

Dual 5G

6x 5G

–

Sim slots

2

4

4

4

12

1

Serial Console Switch

1

8

Via USB

8

16-80

Via USB

Network

1x Gb ETH 1x SFP

5x Gb ETH

2x GbE ETH 2x 10 Gbps

4x 10/100/1000/2.5 Gbps RJ-45

2x SFP 5x Gb ETH

4x 1Gb ETH PoE+

2x 1Gb ETH 2x SFP+ Multiple expansion cards

2x 1Gb ETH

Data Sheet

Download

Download

Download

Download

Download

Download

The Nodegrid line of Raspberry Pi alternatives from ZPE Systems can help your organization prevent Shadow IT to reduce your attack surface and improve your security posture without increasing costs.

Ready for a Raspberry Pi alternative?

Want to see one of ZPE’s Raspberry Pi alternatives in action? Request a free Nodegrid demo! Request a Demo