Providing Out-of-Band Connectivity to Mission-Critical IT Resources

Cyberthreats are Soaring: ZPE Systems Urges Immediate Action with Gen 3 Console Servers to Thwart Breaches
Press Release Complete EOL replacement solution

Organizations using end-of-life console servers must reduce their vulnerability exposure and secure their infrastructure comprehensively by using ZPE’s console servers, installation services and configuration engineering. 

Fremont, CA, May 2, 2024 — As cyberattacks continue to rise, ZPE Systems, a leader in network management infrastructure, recently acquired by Legrand, is urging organizations to  transition to Generation 3 console servers as part of their security strategies. With other well-known infrastructure providers discontinuing support for serial consoles already in use within data centers, communication networks and other commercial and industrial environments, the need to upgrade is paramount.    

Console servers are the backbone of remote IT management, providing essential access to network devices and servers. However, using discontinued console servers poses significant security risks. Outdated firmware may contain known vulnerabilities that enable cyber attackers to infiltrate critical systems, causing costly data breaches and operational disruptions. 

Despite these substantial risks, many organizations hesitate to replace their outdated infrastructure, citing budget constraints, labor costs and concerns about infrastructure disruption. Arnaldo Zimmermann, cofounder of ZPE Systems, highlights this dilemma, saying, “Organizations face financial constraints when considering hardware upgrades, especially when existing infrastructure seems to be working fine. When you consider the capex, labor costs and time it takes to physically install and configure new equipment, it’s easy to see why organizations say, ‘if it’s not broken, don’t fix it.’”  

To address these challenges, ZPE Systems now offers a comprehensive solution designed to alleviate budgetary concerns and streamline the replacement process:

1. New Cost-Effective Replacement Options

ZPE’s Nodegrid devices enable organizations to secure their management infrastructure with new budget-friendly, Gen 3 console servers. These range in cost from premium options to small yet powerful, budget-friendly units.

2. New Professional Installation & Recycling Services

As needed, ZPE Systems offers solutions for physical installation process and recycling of old equipment, minimizing downtime and ensuring environmental responsibility. ZPE connects organizations to a network of trusted partners including ByteBridge, Mirapath, Trace3, and others.

3. New Tailored Configuration Services

ZPE’s engineers provide customized configuration services to transfer the old configuration to new systems and optimize the performance and security of the new console servers. 

“There’s a lot of friction in upgrading,” adds Koroush Saraf, VP of Products and Marketing at ZPE Systems. “We’ve heard of customers using outdated devices for years, who won’t replace because they just don’t have the time, money or manpower. Our goal is to remove that friction, streamlining the transition process and empowering organizations to enhance their security posture without the added burden.”  

By utilizing Gen 3 console servers from ZPE, customers benefit from 3rd party security validated firmware that addresses Common Vulnerabilities and Exposures (CVEs) as well as hardware security features designed to mitigate cybersecurity threats. Organizations can safeguard their assets, protect sensitive data, and maintain operational continuity in an increasingly volatile digital landscape. 


Explore this comprehensive solution using the link below

Explore the hardware options, trusted partner network, and configuration services by clicking the link. You can also get hands-on with this solution at RSA Conference next week. Click the link for details and to get ZPE’s special code that unlocks your free pass.
Cisco ISR 4431 EOL Replacement Guide

NSR with ZPE Logo

The Cisco ISR 4431 is an enterprise branch services router from Cisco’s Integrated Services Router product line. The ISR 4431 integrates with the Cisco DNA infrastructure management platform and the Catalyst SD-WAN (software-defined wide area networking) solution. Its modular design also makes the ISR 4431 extensible with Cisco’s Network Interface Modules (NIMs) to add storage, Ethernet switching, out-of-band (OOB) console server management, and other capabilities.

Cisco announced end-of-sale and end-of-life (EOL) dates for select ISR 4400-series models, including the ISR 4431. Its Cisco-recommended replacement option is the Catalyst C8300, which offers some improvements over the ISR but still suffers from some management, automation, and scaling limitations. However, there are other options on the market that fill these gaps with secure, vendor-neutral, all-in-one branch networking solutions. This guide compares Cisco ISR 4431 EOL replacement options and discusses the advanced features and capabilities offered by Cisco alternatives.

Click here for a list of ISR 4431 EOL products and replacement SKUs.
.

Upcoming Cisco ISR 4431 EOL dates

  • November 6, 2024 – End of routine failure analysis, end of new service attachment
  • August 31, 2025 – End of software maintenance releases and bug fixes
  • February 5, 2028 – End of service contract renewal
  • November 30, 2028 – Last date of support

Looking to replace a different Cisco EOL model? Read our guides Cisco ISR EOL Replacement Options and Cisco 4351 EOL Replacement Guide.

Cisco ISR 4431 EOL replacement options

Cisco ISR 4431 (EOL)

Cisco Catalyst C8300

Nodegrid NSR

Out-of-band (OOB) management

Gen 1 OOB

Gen 2 OOB

Gen 3 OOB

Extensibility

Integrates with Cisco partners only

Integrates with Cisco partners only

Supports virtualization, containers, and integrations

Automation

• Policy-based automation

• Cloud-based automated device provisioning (ZTP)

• Automated deployment of network services (Cisco DNA)

• Policy-based automation

• Cloud-based automated device provisioning (ZTP)

• Automated deployment of network services (Cisco DNA)

• Zero Touch Provisioning (ZTP) via LAN/DHCP, WAN/ZPE Cloud, USB

• Auto-discovery via network scan and custom probes

• Integrated orchestration and automation:

  ◦ Puppet

  ◦ Chef

  ◦ Ansible

  ◦ RESTful

  ◦ ZPE Cloud

  ◦ Nodegrid Manager

Security

• Intrusion prevention

• Cisco Umbrella Branch

• Encrypted traffic analytics

• IPSec tunnels

• DMVPN

• FlexVPN

• GETVPN

• Content filtering

• NAT

• Zone-based firewall

• Intrusion prevention

• Cisco Umbrella Branch

• Encrypted traffic analytics

• IPSec tunnels

• DMVPN

• FlexVPN

• GETVPN

• Content filtering

• NAT

• Zone-based firewall

• Edgified, hardened device with BIOS protection, TPM 2.0, UEFI Secure Boot, Signed OS, Self-Encrypted Disk (SED), Geofencing

• X.509 SSH certificate support, 4096-bit encryption keys

• Selectable cryptographic protocols for SSH and HTTPS (TLSv1.3)

• SSL VPN (Client and Server)

• IPSec, Wireguard, support for multi-sites

• Local, AD/LDAP, RADIUS, TACACS+, and Kerberos authentication

• SAML support via Duo, OKTA, Ping Identity

• Local, backup-user authentication support

• User-access lists per port

• Fine grain and role-based access control (RBAC)

• Firewall - IP packet and security filtering, IP forwarding support

• Two-factor authentication (2FA) with RSA and Duo

Hardware Services

• Serial console ports

• USB console ports

• IP management ports

• Voice functionality

• Compute module

• Serial console ports

• USB console ports

• Voice functionality

• Serial console ports

• USB console ports

• IP management ports

• PDU management

• IPMI device management

• (Optional) Compute module

• (Optional) Storage module

Network services

• Cisco SD-WAN software

• WAN optimization

• AppNAV

• Application visibility and control

• Multicast

• Overlay Transport Virtualization (OTV)

• Ethernet VPN (EVPNoMPLS)

• IPv6 support

• Cisco SD-WAN software

• WAN optimization

• AppNAV

• Application visibility and control

• Multicast

• Overlay Transport Virtualization (OTV)

• Ethernet VPN (EVPNoMPLS)

• IPv6 support

• IPv4 / IPv6 Support

• Embedded Layer 2 Switching

• VLAN

• Layer 3 Routing

• BGP

• OSFP

• RIP

• QoS

• DHCP (Client and Server)

Operating System

Cisco IOS

Cisco IOS

Nodegrid OS

CPU

Multi-Core processor

Multi-Core processor

Intel x86-64 Multi-Core

Storage

4GB-8GB Flash memory

16GB M.2 SSD storage

32GB FLASH (mSATA SSD) (Upgradeable) Self-Encrypted Drive (SED)

RAM

4GB-8GB DRAM

8GB DRAM

8GB DDR DRAM (Upgradeable)

Size

2RU

2RU

1RU

The Cisco Catalyst C8300

The Cisco ISR 4431 suffers from numerous limitations, such as its large physical size and closed ecosystem. Cisco’s recommended replacement option, the Catalyst C8300, has the same problems.

Both devices are 2RU, making them too large to easily install in cramped branches and edge computing sites that may not have a dedicated IT space. Both the ISR 4431 and the Catalyst C8300 are closed platforms, only supporting integrations with Cisco’s third-party partners like ThousandEyes. This prevents teams from utilizing all the security, automation, and monitoring solutions they’re most familiar with (or that work best for their specific use case), increasing the difficulty and complexity of branch network operations. Cisco’s OOB management modules and DNA software are also mostly limited to controlling other Cisco devices, leaving administrators with critical coverage gaps or multiple management solutions to deal with. Overall, these limitations reduce the efficiency, resilience, and scalability of branch network operations.

The Nodegrid Net SR (NSR)

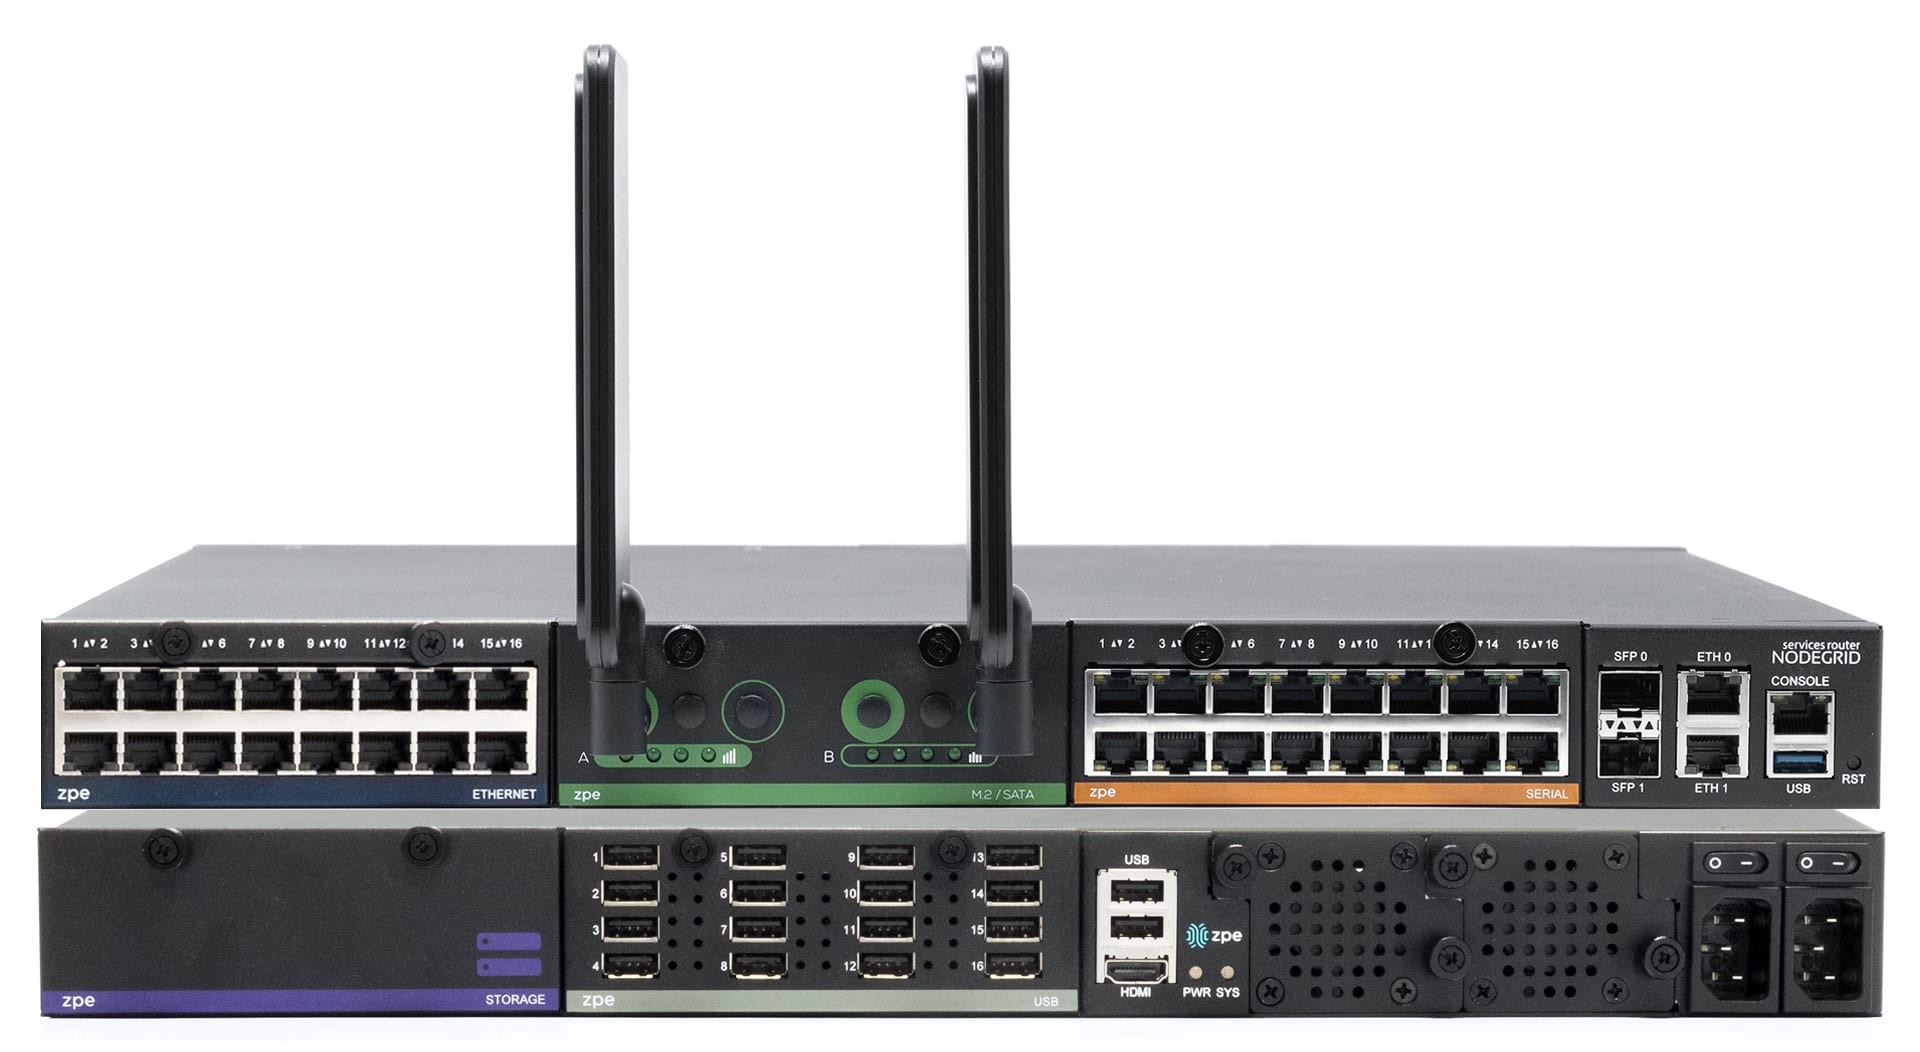
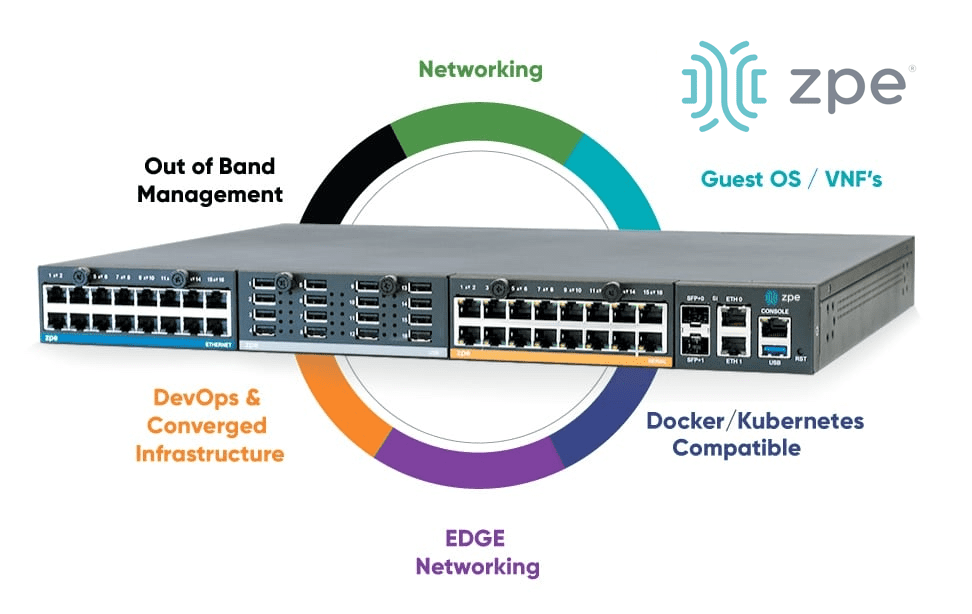
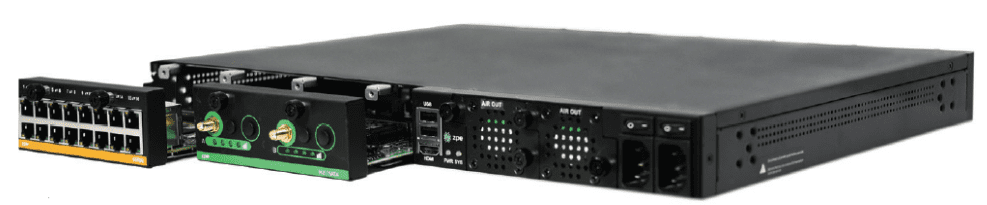
The Nodegrid platform from ZPE Systems addresses many of Cisco’s limitations with vendor-neutral branch services routers (SRs). The Nodegrid Net Services Router (NSR) is a 1RU replacement for Cisco ISR 4431 EOL devices and features advanced branch networking capabilities.

Want to see how Nodegrid stacks up against Cisco’s ISR 4431 EOL replacement options? Click here to download the services routers comparative matrix.

The NSR provides branch gateway routing and switching, vendor-neutral VNF (virtual network function) hosting, and out-of-band management in a single, 1RU device. The NSR’s expansion modules add capabilities like PoE+, cellular/Wi-Fi, edge compute, and additional serial console management ports.

Nodegrid solutions are vendor-neutral, supporting Guest OS and Docker containers for third-party software. Teams can use their favorite tools for monitoring, automation, and security, and even extend these capabilities to legacy and mixed-vendor infrastructure. Organizations can use Nodegrid to create a custom-tailored, all-in-one branch networking solution with all the apps and services needed to deploy, manage, troubleshoot, and recover branch operations. Plus, Nodegrid creates an isolated management plane where teams can recover from ransomware, deploy resource-intensive automated workflows, and ensure 24/7 branch operations, improving resilience and supporting efficient scaling.

Ready to replace your Cisco ISR 4431 EOL products?

The Nodegrid platform delivers vendor-neutral branch network management for improved efficiency, resilience, and scalability. See our Cisco ISR 4431 EOL replacement SKUs below or contact ZPE Systems for help choosing the right Nodegrid solution for your business.

Explore our full products and services package to replace your Cisco ISR 4431

We know that replacing EOL devices takes a lot of effort. That’s why ZPE now offers a complete package of budget-friendly products and engineering services. Visit our page to see how we make it easy to replace discontinued devices like the Cisco ISR 4431.

Cisco ISR 4431 replacement SKUs

Cisco ISR 4431 EOL Product SKUs

In-Scope Features

Nodegrid Replacement Product SKUs

ISR4431-AX/K9

ISR4431-AXV/K9

ISR4431-DNA

ISR4431-PM20

ISR4431-SEC/K0

ISR4431-V/K9

ISR4431-VSEC/K9

ISR4431/K9

Serial Console Module, Routing, 16 serial ports

ZPE-NSR-816-DAC with 1 x 16 port serial module 1 x ZPE-NSR-16SRL-EXPN


ISR4431-AX/K9

ISR4431-AXV/K9

ISR4431-DNA

ISR4431-PM20

ISR4431-SEC/K0

ISR4431-V/K9

ISR4431-VSEC/K9

ISR4431/K9

Serial Console Module, Routing, 32 serial ports

ZPE-NSR-816-DAC with 2 x 16 port serial module 2 x ZPE-NSR-16SRL-EXPN

ISR4431-AX/K9

ISR4431-AXV/K9

ISR4431-DNA

ISR4431-PM20

ISR4431-SEC/K0

ISR4431-V/K9

ISR4431-VSEC/K9

ISR4431/K9

Serial Console Module, Routing, 48 serial ports

ZPE-NSR-816-DAC with 3 x 16 port serial module 3 x ZPE-NSR-16SRL-EXPN

ISR4431-AX/K9

ISR4431-AXV/K9

ISR4431-DNA

ISR4431-PM20

ISR4431-SEC/K0

ISR4431-V/K9

ISR4431-VSEC/K9

ISR4431/K9

Serial Console Module, Routing, 60 serial ports

ZPE-NSR-816-DAC with 4 x 16 port serial module 4 x ZPE-NSR-16SRL-EXPN

80 serial port option – no Cisco equivalent

Serial Console Module, Routing, 80 serial ports

ZPE-NSR-816-DAC with 5 x 16 port serial module 5 x ZPE-NSR-16SRL-EXPN

Opengear Alternatives for the OM2200 and OM1200

NSRSTACK2-1
The Opengear Operations Manager is a series of NetOps console servers providing out-of-band remote access to manage remote network infrastructure in data center, edge, and branch deployments. There are a few reasons to consider alternative options, including a lack of 3rd-party integrations, 5G support, and gateway routing capabilities. This blog goes over the pros and cons of the Operations Manager solutions before discussing Opengear alternatives that provide greater automation, orchestration, and security features as well as all-in-one branch networking capabilities.

Executive summary

  • Opengear’s Operations Manager (OM) appliances are NetOps console servers providing out-of-band (OOB) management for remote network infrastructure.
  • While OM appliances provide some automation capabilities, especially with the upgraded Automation Edition, they offer limited third-party integrations and end-device automation features.
  • The OM2200 and OM1200 both lack integrated branch gateway functionality and have limited security features overall.
  • The Nodegrid platform from ZPE Systems overcomes these limitations with vendor-neutral OOB serial consoles and branch services routers.
  • Nodegrid enables end-to-end automation through end-device ZTP and unlimited third-party integrations with leading tools like Ansible and Chef.
  • Nodegrid also consolidates data center and branch networking functionality like gateway routing, 5G cellular failover, and security to provide all-in-one solutions.

Reviewing the Opengear Operations Manager platform

Operations Manager (or OM) is Opengear’s line of NetOps console servers. OM appliances come with Smart OOBTM for out-of-band management, including automated port discovery and VLAN support. Opengear’s x86 Lighthouse platform supports Python scripts and Docker container deployments for NetOps automation. Lighthouse also supports over 100 power vendors’ equipment, allowing it to monitor and control UPS batteries, PDU outlets, and power load balancing. It’s important to note that, while the standard (Enterprise) edition of Lighthouse supports Python and Docker, customers must upgrade to the Automation edition for zero-touch provisioning (ZTP) or other third-party automation integrations. Additionally, OM solutions do not support 2FA or SAML authentication.

Opengear OM2200

The Opengear OM2200 Operations Manager model is designed for data center and high-density use cases. It features 16, 32, 48 serial and 24 serial/Ethernet mixed port configuration options, with an optional global LTE-A Pro cellular module. The OM2200 provides five regional options for dual AC power as well as a dual DC power cord model.

Click here to see a complete Opengear OM2200 Operations Manager product SKUs list.

OM2200 Pros:

  • Plenty of RAM and storage space
  • Many options for power and serial port configurations
  • Uniquely broad support for 3rd-party power equipment
  • Some NetOps automation capabilities

OM2200 Cons:

  • Requires upgraded software licenses for ZTP and most 3rd-party automation
  • No 2FA or SAML 2.0 support
  • No managed USB serial ports
  • No 5G support

Opengear OM1200

The Opengear OM1200 Operations Manager model is meant for small edge deployments. The compact chassis supports 4 serial, 8 serial, and 8 serial/8 Ethernet port combinations. It provides OOB and failover access via dual Ethernet (SFP Fiber is available on the 4E and 8E models) as well as an optional global LTE-A Pro cellular module.

Click here to see a full list of Opengear OM1200 Operations Manager product SKUs.

OM1200 Pros:

  • Compact size
  • Cost-effective range of port configurations
  • Supports 3rd-party power equipment, Docker, and Python

OM1200 Cons:

  • Requires upgraded software licenses for ZTP and most 3rd-party automation
  • No 2FA or SAML 2.0 support
  • It doesn’t have gateway routing/SD-WAN capabilities
  • No 5G support

Opengear Operations Manager limitations

Both the OM2200 and OM1200 models suffer from similar limitations regarding automation, especially with the base version of the Lighthouse software. Even the upgraded Automation Edition, which unlocks ZTP and RESTful APIs, doesn’t provide much automation for end devices beyond running Python playbooks. This limits operational efficiency, slows down new deployments, and impedes the team’s ability to quickly rebuild core infrastructure after a failure or ransomware attack. Another issue with the OM1200, in particular, is that while its compact size will save space in your edge data center and branch office rack, it’s still a single-purpose device. That means you still need to purchase separate solutions for gateway routing, switching, and/or edge compute. These additional devices take up space, cost extra money, and require time to configure and manage.

Opengear alternatives from ZPE Systems

ZPE Systems provides an alternative option for NetOps-enabled OOB console servers called the Nodegrid solution. All Nodegrid devices run on the open, Linux-based, x86 Nodegrid OS which supports VMs and Docker containers to run your choice of third-party automation, software-defined networking/SD-WAN, and security applications. Nodegrid’s robust, onboard security protects lost or stolen devices with features like TPM 2.0, encrypted SSD, UEFI BIOS, secure boot, and geofencing. Nodegrid can also extend ZTP and other automation to legacy and mixed-vendor end devices for end-to-end network infrastructure automation. Try ZPE’s product selector to see which of Nodegrid’s serial consoles or integrated branch routers is right for your deployment. Below, we review the two models that serve as direct replacements for the Opengear OM1200 and OM2200 solutions.

Nodegrid Serial Console Plus (NSCP)

The Nodegrid Serial Console Plus (NSCP) is an alternative to the OM2200 for data center and high-density deployments. The NSCP connects 16, 32, 48, or 96 (Patent No. 9,905,980) serial devices, all in a standard 1U rackmount chassis. Dual SFP+, dual Gigabit Ethernet, and optional Wi-FI and 4G/5G LTE modules provide secure Gen 3 OOB management access and failover, ensuring blazing fast speeds and high performance. Plus, the NSCP comes with two managed USB 3.0 ports for additional flexibility.

Click here to see a complete list of Nodegrid NSCP product SKUs.

Nodegrid Net Services Router (NSR)

The Nodegrid Net Services Router (NSR) is an alternative to the OM1200 for edge data center and branch office use cases. The NSR is a modular, compact device that can deliver gateway routing, switching, serial console, and compute capabilities all in a single appliance. Gen 3 OOB and network failover are provided out of the box via dual SFP+ and dual Gigabit Ethernet ports, with optional modules for WiFi and dual-SIM 5G/4G LTE. Additional NSR modules include:

  • 16-port GbE Ethernet
  • Storage
  • 16-port Serial (for console server capabilities)
  • 16-port USB serial
  • Compute
  • 8-port PoE+
  • M.2 Cellular/Wi-Fi/SATA
  • 16-port GbE Ethernet SFP
  • 8-port Ethernet SFP+

Click here to see a complete list of Nodegrid NSCP product SKUs.

Key takeaways:

While the OM1200 and OM2200 provide OOB management with some automation, they have serious limitations that negatively impact operational efficiency. Nodegrid is an Opengear alternative providing a vendor-neutral OOB management platform that delivers unlimited automation, enhanced security, and all-in-one networking for ultimate operational efficiency.

Trade in to get a discount on Opengear alternatives

If you’re ready to replace end-of-life devices from Opengear or other vendors, now’s your chance to get a discount. Visit our trade-in page to get your trade-in offer.
Get Trade-In Offer

See Nodegrid’s Opengear Alternatives in action

Reach out today to view a demo of Nodegrid’s Opengear alternatives in action.
Request a Demo

Opengear OM2200 – Product SKU’s:

OM2216

16 x Serial, 8GB RAM, 64GB SSD, 8 x USB 2.0, 2 x GbE/SFP Fiber

OM2216-AU

Dual AC – Australian power cord

OM2216-EU

Dual AC – European Union power cord

OM2216-JP

Dual AC – Japanese power cord

OM2216-UK

Dual AC – United Kingdom power cord

OM2216-US

Dual AC – United States power cord

OM2216-DDC

Dual DC power

OM2216-L-AU

Global 4G LTE-A Pro cellular module, Dual AC – AU power cord

OM2216-L-EU

Global 4G LTE-A Pro cellular module, Dual AC – EU power cord

OM2216-L-JP

Global 4G LTE-A Pro cellular module, Dual AC – JP power cord

OM2216-L-UK

Global 4G LTE-A Pro cellular module, Dual AC – UK power cord

OM2216-L-US

Global 4G LTE-A Pro cellular module, Dual AC – US power cord

OM-2216-DDC-L

Global 4G LTE-A Pro cellular module, Dual DC power


OM2224-24E

24 x Serial, 24 x GbE, 8GB RAM, 64GB Flash

OM2224-24E-AU

1 x GbE/SFP, Dual AC – Australian power cord

OM2224-24E-EU

1 x GbE/SFP, Dual AC – European Union power cord

OM2224-24E-JP

1 x GbE/SFP, Dual AC – Japanese power cord

OM2224-24E-UK

1 x GbE/SFP, Dual AC – United Kingdom power cord

OM2224-24E-US

1 x GbE/SFP, Dual AC – United States power cord

OM2224-24E-DDC

1 x GbE/SFP, Dual DC power

OM2224-24E-L-AU

1 x GbE/SFP, Global 4G LTE-A Pro cellular module, Dual AC – AU power cord

OM2224-24E-L-EU

1 x GbE/SFP, Global 4G LTE-A Pro cellular module, Dual AC – EU power cord

OM2224-24E-L-JP

1 x GbE/SFP, Global 4G LTE-A Pro cellular module, Dual AC – JP power cord

OM2224-24E-L-UK

1 x GbE/SFP, Global 4G LTE-A Pro cellular module, Dual AC – UK power cord

OM2224-24E-L-US

1 x GbE/SFP, Global 4G LTE-A Pro cellular module, Dual AC – US power cord

OM2224-24E-DDC-L

1 x GbE/SFP, Global 4G LTE-A Pro cellular module, Dual DC power

OM2224-24E-10G-AU

10 x GbE/SFP, Dual AC – AU power cord

OM2224-24E-10G-EU

10 x GbE/SFP, Dual AC – EU power cord

OM2224-24E-10G-JP

10 x GbE/SFP, Dual AC – JP power cord

OM2224-24E-10G-UK

10 x GbE/SFP, Dual AC – UK power cord

OM2224-24E-10G-US

10 x GbE/SFP, Dual AC – US power cord

OM2224-24E-10G-DDC

10 x GbE/SFP, Dual DC power

OM2224-24E-10G-L-AU

10 x GbE/SFP, Global 4G LTE-A Pro cellular module, Dual AC – AU power cord

OM2224-24E-10G-L-EU

10 x GbE/SFP, Global 4G LTE-A Pro cellular module, Dual AC – EU power cord

OM2224-24E-10G-L-JP

10 x GbE/SFP, Global 4G LTE-A Pro cellular module, Dual AC – JP power cord

OM2224-24E-10G-L-UK

10 x GbE/SFP, Global 4G LTE-A Pro cellular module, Dual AC – UK power cord

OM2224-24E-10G-L-US

10 x GbE/SFP, Global 4G LTE-A Pro cellular module, Dual AC – US power cord

OM2224-24E-10G-DDC-L

10 x GbE/SFP, Global 4G LTE-A Pro cellular module, Dual DC power


OM2232

32 x Serial, 8GB RAM, 64GB SSD, 2 x GbE/SFP Fiber

OM2232-AU

Dual AC – Australian power cord

OM2232-EU

Dual AC – European Union power cord

OM2232-JP

Dual AC – Japanese power cord

OM2232-UK

Dual AC – United Kingdom power cord

OM2232-US

Dual AC – United States power cord

OM2232-DDC

Dual DC power

OM2232-L-AU

Global 4G LTE-A Pro cellular module, Dual AC – AU power cord

OM2232-L-EU

Global 4G LTE-A Pro cellular module, Dual AC – EU power cord

OM2232-L-JP

Global 4G LTE-A Pro cellular module, Dual AC – JP power cord

OM2232-L-UK

Global 4G LTE-A Pro cellular module, Dual AC – UK power cord

OM2232-L-US

Global 4G LTE-A Pro cellular module, Dual AC – US power cord

OM2232-DDC-L

Global 4G LTE-A Pro cellular module, Dual DC power


OM2248

48 x Serial, 8GB RAM, 64GB SSD

OM2248-AU

2 x GbE/SFP, Dual AC – Australian power cord

OM2248-EU

2 x GbE/SFP, Dual AC – European Union power cord

OM2248-JP

2 x GbE/SFP, Dual AC – Japanese power cord

OM2248-UK

2 x GbE/SFP, Dual AC – United Kingdom power cord

OM2248-US

2 x GbE/SFP, Dual AC – United States power cord

OM2248-DDC

2 x GbE/SFP, Dual DC power

OM2248-L-AU

2 x GbE/SFP, Global 4G LTE-A Pro cellular module, Dual AC – AU power cord

OM2248-L-EU

2 x GbE/SFP, Global 4G LTE-A Pro cellular module, Dual AC – EU power cord

OM2248-L-JP

2 x GbE/SFP, Global 4G LTE-A Pro cellular module, Dual AC – JP power cord

OM2248-L-UK

2 x GbE/SFP, Global 4G LTE-A Pro cellular module, Dual AC – UK power cord

OM2248-L-US

2 x GbE/SFP, Global 4G LTE-A Pro cellular module, Dual AC – US power cord

OM2248-DDC-L

2 x GbE/SFP, Global 4G LTE-A Pro cellular module, Dual DC power

OM2248-10G-AU

10 x GbE/SFP, Dual AC – AU power cord

OM2248-10G-EU

10 x GbE/SFP, Dual AC – EU power cord

OM2248-10G-JP

10 x GbE/SFP, Dual AC – JP power cord

OM2248-10G-UK

10 x GbE/SFP, Dual AC – UK power cord

OM2248-10G-US

10 x GbE/SFP, Dual AC – US power cord

OM2248-10G-DDC

10 x GbE/SFP, Dual DC power

OM2248-10G-L-AU

10 x GbE/SFP, Global 4G LTE-A Pro cellular module, Dual AC – AU power cord

OM2248-10G-L-EU

10 x GbE/SFP, Global 4G LTE-A Pro cellular module, Dual AC – EU power cord

OM2248-10G-L-JP

10 x GbE/SFP, Global 4G LTE-A Pro cellular module, Dual AC – JP power cord

OM2248-10G-L-UK

10 x GbE/SFP, Global 4G LTE-A Pro cellular module, Dual AC – UK power cord

OM2248-10G-L-US

10 x GbE/SFP, Global 4G LTE-A Pro cellular module, Dual AC – US power cord

OM2248-10G-DDC-L

10 x GbE/SFP, Global 4G LTE-A Pro cellular module, Dual DC power

Opengear OM1200 – Product SKU’s

OM1204

4 x Serial, 2GB RAM, 16GB Flash, 1 x GbE

OM1204-L

4 x Serial, 2GB RAM, 16GB Flash, 1 x GbE, Global 4G LTE

OM1204-4E

4 x Serial, 4 x GbE, 4GB RAM, 16GB Flash, 1 x GbE SFP 

OM1204-4E-L

4 x Serial, 4 x GbE, 4GB RAM, 16GB Flash, 1 x GbE SFP, Global 4G LTE 

OM1208

8 x Serial, 2GB RAM, 16GB Flash, 1 x GbE

OM1208-L

8 x Serial, 2GB RAM, 16GB Flash, 1 x GbE, Global 4G LTE

OM1208-8E

8 x Serial straight X2 pinout, 8 x GbE switch, 4GB RAM, 16GB SSD, 2 x USB 2.0, 2 x GbE/SFP Fiber

OM1208-8E-L

8 x Serial straight X2 pinout, 8 x GbE switch, 4GB RAM, 16GB SSD, 2 x USB 2.0, 2 x GbE/SFP Fiber, Global 4G LTE

Nodegrid Serial Console Plus – Product SKU’s

Nodegrid Serial Console Plus (NSCP)

4-Core Intel CPU, 4GB DDR4 RAM, 32GB SSD, 2 x SFP+, 2 x GbE, 2 x USB 3.0, 1 x HDMI, 1 x Console

NSCP-T16R-STND-SAC

16 x Cisco Rolled Serial, Single AC power

NSCP-T16R-STND-DAC

16 x Cisco Rolled Serial, Dual AC power

NSCP-T16R-STND-DDC

16 x Cisco Rolled Serial, Dual AC power

NSCP-T32R-STND-SAC

32 x Cisco Rolled Serial, Single AC power

NSCP-T32R-STND-DAC

32 x Cisco Rolled Serial, Dual AC power

NSCP-T32R-STND-DDC

32 x Cisco Rolled Serial, Dual DC power

NSCP-T48R-STND-SAC

48 x Cisco Rolled Serial, Single AC power

NSCP-T48R-STND-DAC

48 x Cisco Rolled Serial, Dual AC power

NSCP-T48R-STND-DDC

48 x Cisco Rolled Serial, Dual DC power

NSCP-T96R-STND-SAC

96 x Cisco Rolled Serial, Single AC power

NSCP-T96R-STND-DAC

96 x Cisco Rolled Serial, Dual AC power

NSCP-T96R-STND-DDC

96 x Cisco Rolled Serial, Dual DC power

Nodegrid Net SR – Product SKU’s

Nodegrid Net Services Router (NSR)

Multi-Core Intel CPU, On-board Switch, 8GB DDR4 RAM, 32GB MSATA, Hot-Swappable Fans, 2 x SFP+, 2 x GbE

NSR-TOP1-DAC

Dual AC power, 5 Slots support

NSR-BASE-DAC

Dual AC power, 3 Slots support

NSR-TOP1-SAC

Single AC power, 5 Slots support

NSR-BASE-SAC

Single AC power, 3 Slots support

NSR-TOP1-SAC-POE

Single AC and PoE, 5 Slots support

NSR-BASE-SAC-POE

Single AC and PoE, 3 Slots support

Expansion Cards

NSR-16ETH-EXPN

16 x GbE Ethernet expansion card

NSR-8ETH-POE-EXPN

8 x GbE Ethernet with PoE+ expansion card

NSR-16SRL-EXPN

16 x RJ45 Serial Rolled expansion card

NSR-16USB-EXPN

16 x USB Type A expansion card

NSR-8SFP-EXPN

8 x 10GbE SFP expansion card

NSR-DISK-EXPN

Storage expansion card

NSR-COMP-EXPN

Compute 4-core, 8GB DDR4, 32GB SATA expansion card

NSR-M2-EXPN

M.2/SATA Expansion Card

The Future of Edge Computing

The Future of Edge Computing
Edge computing moves computing resources and data processing applications out of the centralized data center or cloud, deploying them at the edges of the network and allowing companies to use their edge data in real-time. An explosion in edge data generated by Internet of Things (IoT) sensors, automated operational technology (OT), and other remote devices has created a high demand for edge computing solutions. A recent report from Grand View Research valued the edge computing market size at $16.45 billion in 2023 and predicted it to grow at a compound annual growth rate (CAGR) of 37.9% by 2030.

The current edge computing landscape comprises solutions focused on individual use cases,  lacking interoperability and central orchestration. The future of edge computing, as described by leading analysts at Gartner, depends on unifying the edge computing ecosystem with comprehensive strategies and centralized, vendor-neutral management and orchestration. This future relies on edge-native applications that integrate seamlessly with upstream resources, remote management, and orchestration while still being able to operate independently.

Where is edge computing now?

Many organizations already use edge computing technology to solve individual problems or handle specific workloads. For example, a manufacturing department may deploy an edge computing application to analyze log data and provide predictive maintenance recommendations for a single type of machine or assembly line. A single company may have a dozen or more disjointed edge computing solutions in use throughout the network, creating visibility and management headaches for IT teams. This piecemeal approach to edge computing results in what Gartner calls “edge sprawl”: many disparate solutions deployed without centralized control, security, or visibility. Edge sprawl increases management complexity and risk while decreasing operational efficiency, creating significant roadblocks for digital transformation initiatives.

Additionally, many organizations misunderstand edge computing by thinking it’s just about moving computing resources as close to the edge as possible to collect data. In reality, the true potential of the edge involves using edge data in real-time, gaining “cloud-in-a-box” capability that works in concert with the network’s upstream resources.

Anticipating the future of edge computing

At Gartner’s 2023 IT Infrastructure Operations & Cloud Strategies Conference, edge technology experts predicted that, by 2025, enterprises will create and process more than 50% of their data outside the centralized data center or cloud. Surging edge data volume will accelerate the challenges caused by a lack of strategy or orchestration.

Gartner’s 6 Edge Computing Challenges

Lack of extensibility

Many purpose-built edge computing solutions can’t adapt as use cases change or expand as the business scales, limiting agility and preventing efficient growth.

Inability to extract value from edge data

Much of the valuable data generated by edge sensors and devices gets left on the table, so to speak, because companies lack the resources needed to run all their data analytics and AI apps at the edge and are stuck simply collecting data rather than being able to do much with it.

Data storage constraints

Edge computing deployments are often smaller and have more data storage constraints than large data centers and cloud deployments, but quickly distinguishing between valuable data and destroyable junk is difficult with edge resources.

Knowledge debt from edge-native apps

Edge-native applications are designed for edge computing architectures from the ground up. Edge containers are similar to cloud-native apps, but clustering and cluster management work much differently, creating what’s known as “knowledge debt” and straining IT teams.

Lack of security controls, policies, & visibility

Edge deployments often lack many of the security features used in data centers, and sometimes other departments install edge computing solutions without onboarding them with IT for the application of security policies and monitoring agents, adding risk and increasing the attack surface.

Inability to remotely orchestrate, monitor, & troubleshoot

When equipment failures, configuration errors, or breaches take down edge networks, remote teams are often cut-off and unable to troubleshoot or recover without traveling on-site or paying for managed services, increasing the duration and cost of the outage. Current edge solutions are novel and don’t connect to or integrate with the full networking stack.

At the Gartner conference, analyst Thomas Bittman gave multiple presentations echoing his advice from the Building an Edge Computing Strategy report published earlier in the year. In preparing for the future of edge computing, Bittman urges companies to proactively develop a comprehensive edge computing strategy encompassing all potential use cases and addressing the challenges described above. His recommendations include:

  • Enabling extensibility by utilizing vendor-neutral platforms that allow for expansion and integration, which supports growth and agility at the edge.
  • Looking for opportunities to deploy artificial intelligence, data analytics, and machine learning alongside edge computing units, for example, with system-on-chip technology or all-in-one edge networking and computing devices.
  • Anticipating data storage and governance challenges at the edge by defining clear policies and deploying AI/ML data management solutions that dynamically determine data value.
  • Reducing knowledge debt by utilizing vendor-neutral platforms that support familiar container and cluster management technologies (like Docker and Kubernetes).
  • Securing the edge with a multi-layered defense, including hardware security, frequent patches, zero-trust policies, strong authentication, network micro-segmentation, and comprehensive security monitoring.
  • Centralizing edge management and orchestration (EMO) with a vendor-neutral platform that unifies control, supports environmental monitoring, and uses out-of-band (OOB) management while interoperating with automated edge management workflows (such as zero-touch provisioning and infrastructure configuration management).

Bittman’s recommended edge computing strategy uses the central EMO as a hub for all the technologies, processes, and workflows involved in operating and supporting the edge. This strategy will prepare companies for the future of edge computing and support efficient, agile growth and innovation.

Enter the future of edge computing with Nodegrid

Nodegrid is a vendor-neutral edge management and orchestration platform from ZPE Systems. Nodegrid easily interoperates with your choice of edge solutions and can directly run third-party AI, ML, data analytics, and data governance applications to help you extract more value from your edge data. The open, Linux-based Nodegrid OS can also host Docker containers and edge-native applications to reduce hardware overhead and knowledge debt.

Nodegrid devices protect your edge management interfaces with hardware security features like TPM and geofencing, support for strong authentication like 2FA, and integrations with leading zero-trust providers like Okta and PING. The Nodegrid OS and ZPE Cloud are Synopsys-validated to address security at every stage of the SDLC. Plus, you can run third-party security solutions for SASE, next-generation firewalls, and more.

Nodegrid edge networking solutions use out-of-band technology to give teams 24/7 remote visibility, management, and troubleshooting access to edge deployments. It freely interoperates with third-party solutions for infrastructure automation, monitoring, and recovery to support network resilience and operational efficiency. Nodegrid is like a cloud-in-a-box solution, incorporating edge computing and the full networking stack. Nodegrid’s edge management and orchestration platform provides single-pane-of-glass visibility, control, and resilience while supporting future edge growth.

Use Nodegrid for your Gartner-approved edge computing strategy

The Nodegrid EMO platform helps you anticipate the future of edge computing with vendor-neutral, single-pane-of-glass visibility and control. Watch a free Nodegrid demo to learn more.

Request a Demo

DORA Act: 5 Takeaways For The Financial Sector

Thumbnail – DORA Act 5 Takeaways for the Financial Sector

The Digital Operational Resilience Act (DORA) is a regulatory initiative within the European Union that aims to enhance the operational resilience of the financial sector. Its main goal is to prevent and mitigate cyber threats and operational disruptions. The DORA Act outlines regulatory requirements for the security of network and information systems “whereby all firms need to make sure they can withstand, respond to and recover from all types of ICT-related disruptions and threats” (DORA Act website).

Who and What Are Covered Under the DORA Act?

The DORA Act is a regulation that covers all financial entities within the European Union (EU). It recognizes the critical role of information and communication technology (ICT) systems in financial services. DORA applies to financial services including payments, securities, credit rating, algorithmic trading, lending, insurance, and back-office operations. It establishes a framework for ICT risk management through technical standards, which are being released in two phases, the first of which was published on January 17, 2024. The DORA Act will go into effect in its entirety on January 17, 2025.

With cyberattacks constantly in the news cycle, it’s no surprise that governing bodies are putting forth standards for operational resilience. But without combing through this lengthy piece of legislation, what should IT teams start thinking about from a practical standpoint? Here are 5 takeaways on what the DORA Act means for the financial sector.

DORA Act: 5 Takeaways for the Financial Sector

1. Shore-up your cybersecurity measures

The DORA Act emphasizes strengthening cybersecurity measures within the financial sector. It requires financial institutions, such as banks, stock exchanges, and financial infrastructure providers, to implement robust cybersecurity controls and protocols. These include adopting advanced authentication mechanisms, encryption standards, and network segmentation to protect sensitive financial data and critical infrastructure from cyber threats. Part of this will also require organizations to apply system patches and updates in a timely manner, which means automated patching will become necessary to every organization’s security posture.

2. Implement resilience systems

Operational resilience is a key focus area of the DORA Act, aiming to ensure the continuity of essential financial services in the face of cyber threats, natural disasters, and other operational disruptions. Financial institutions are required to develop comprehensive business continuity plans, establish redundant systems and backup facilities, and conduct regular stress tests to assess their ability to withstand and recover from various scenarios. Implementing a resilience system helps with this, as it provides all the infrastructure, tools, and services necessary to continue operating during major incidents.

3. Conduct regular scans for vulnerabilities

The DORA Act mandates financial institutions to implement robust risk management practices to identify, assess, and mitigate cyber risks and operational vulnerabilities. This includes conducting regular assessments, vulnerability scans, and penetration tests, and developing incident response procedures to quickly address threats. This is all part of taking a proactive approach to identify and mitigate cyber incidents, and reduce the impact that adverse events have on financial stability and consumer confidence.

4. Collaborate and share information with industry peers

The DORA Act encourages financial institutions to share cybersecurity threat intelligence, incident data, and best practices with industry peers, regulators, and law enforcement agencies. The ability to monitor systems and collect data will be crucial to this approach, and will require systems that can rapidly (and securely) deploy apps/services during ongoing incidents. This will help financial institutions to better understand emerging threats, coordinate responses to cyber incidents, and strengthen collective defenses against threats and operational disruptions.

5. Segment physical and logical systems to pass regular audits

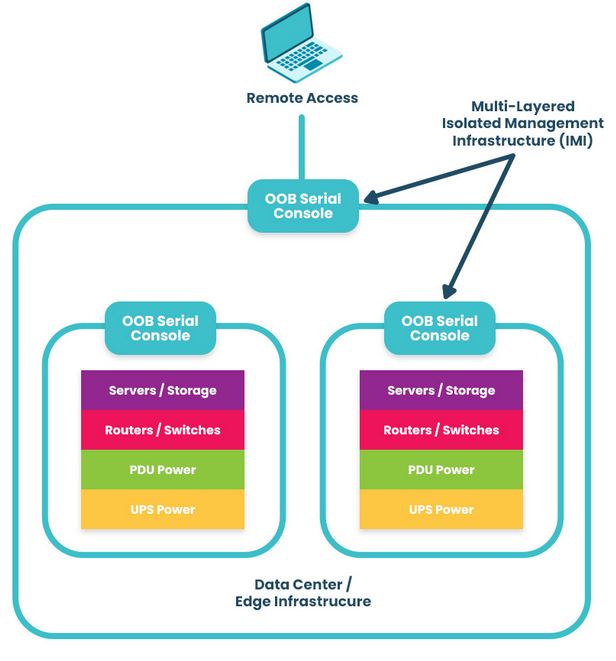
Through the DORA Act, regulators are empowered to conduct regular assessments, audits, and inspections of systems. This will ensure that financial institutions are implementing adequate controls and safeguards to protect against cyber threats and operational disruptions. A crucial part to this will involve physical and logical separation of systems, such as through Isolated Management Infrastructure, as well as implementing zero trust architecture across the organization. These will help bolster resilience by eliminating control dependencies between management and production networks, which will also help to streamline audits.

Get the blueprint to help you comply with the DORA Act

DORA’s requirements are meant to help IT teams better protect sensitive data and the integrity of financial systems as a whole. But without a proper network management infrastructure, their production networks are too sensitive to errors and vulnerable to attacks. ZPE has created the blueprint that covers these 5 crucial takeaways outlined in the DORA Act. The architecture outlined in this blueprint has been trusted by Big Tech for more than a decade, as it allows them to deploy modern cybersecurity measures, physically and logically separated systems, and rapid recovery processes. Download the blueprint now.

What to do if You’re Ransomware’d: A Healthcare Example

What to do if youre ransomwared

This article was written by James Cabe, CISSP, a 30-year cybersecurity expert who’s helped major companies including Microsoft and Fortinet.

Ransomware gangs target the innocent and vulnerable. They hit a Chicago hospital in December 2023, a London hospital in October the same year, and schools and hospitals in New Jersey as recently as January 2024. This is one of the biggest reasons I’m committed to stopping these criminals by educating organizations on how to re-think and re-architect their approach to cybersecurity.

In previous articles, I discussed IMI (Isolated Management Infrastructure) and IRE (Isolated Recovery Environments), and how they could have quickly altered outcomes for MGM, Ragnar Locker victims, and organizations affected by the MOVEit vulnerability. Using IMI and IRE, organizations find that the key to not only speedy recovery, but also to limiting the blast radius and attack persistence, is isolation.

Why is isolation (not segmentation) key to ransomware recovery?

The NIST framework for incident response has five steps: Identify, Protect, Detect, Respond, and Recover. It’s missing a crucial step, however: Isolate. Stay tuned for a full breakdown of this in my next article. But the reason this is so critical is because attacks move at machine speed, and are very pervasive and persistent. If your management network is not fully isolated from production assets, the infection spreads to everything. Suddenly, you’re locked out completely and looking at months of tedious recovery. For healthcare providers, this jeopardizes everything from patient care to regulatory compliance.

Isolation is integral to building a resilience system, or in other words, a system that gives you more than basic serial console/out-of-band access and instead provides an entire infrastructure dedicated to keeping you in control of your systems — be it during a ransomware attack, ISP outage, natural disaster, etc. Because this infrastructure is physically and virtually isolated from production (no dependencies on production switches/routers, no open management ports, etc.), it’s nearly impossible for attackers to lock you out.

So, what really should you do if you’re ransomware’d? Let’s walk through an example attack on a healthcare system, and compare the traditional DR (Disaster Recovery) response to the IMI/IRE approach.

Ransomware in Healthcare: Disaster Recovery vs Isolated Recovery

Suppose you’re in charge of a hospital’s network. MDIoT, patient databases, and DICOM storage are the crown jewels of your infrastructure. Suddenly, you discover ransomware has encrypted patient records and is likely spreading quickly to other crown jewel assets. The risks and potential fallout can’t be understated. Millions of people are depending on you to protect their sensitive info, while the hospital is depending on you to help them avoid regulatory/legal penalties and ensure they can continue operating.

The problem with Disaster Recovery

Though the word ‘recovery’ is in the name, the DR approach is limited in its capacity to recover systems during an attack. Disaster Recovery typically employs a couple things:

  • Backups, which are copies of data, configurations, and code that are used to restore a production system when it fails.
  • Redundancy, which involves duplicating critical systems, services, and applications as a failsafe in the event that primaries go down (think cellular failover devices, secondary firewalls, etc.).

What happens when you activate your DR processes? It’s highly likely that you won’t be able to, and that’s because the typical DR setup relies on the production network. There’s no isolation.

Think about it this way: your backup servers need direct access to the data they’re backing up. If your file servers get pwned, your backup servers will, too. If your primary firewall gets hacked, your secondary will, too. The problem with backup and redundancy systems — and any system, for that matter — is that when they depend on the underlying infrastructure to remain operational, they’re just as susceptible to outages and attacks. It’s like having a reserve parachute that depends on the main parachute.

And what about the rest of your systems? You just discovered the attack has encrypted your servers and is quickly bringing operations to a crawl. How are you going to get in and fight back? What if you try to log into your management network, only to find that you’re locked out? All of your tools, configurations, and capabilities have been compromised.

This is why CISA, the FBI, US Navy, and other agencies recommend implementing Isolated Management Infrastructure.

IMI and IRE guarantee you can fight back against ransomware

You discover that the ransomware has spread. Not only has it encrypted data and stopped operations, but it has also locked you out of your own management network and is affecting the software configurations throughout the hospital. This is where IMI (Isolated Management Infrastructure) and IRE (Isolated Recovery Environment) come in.

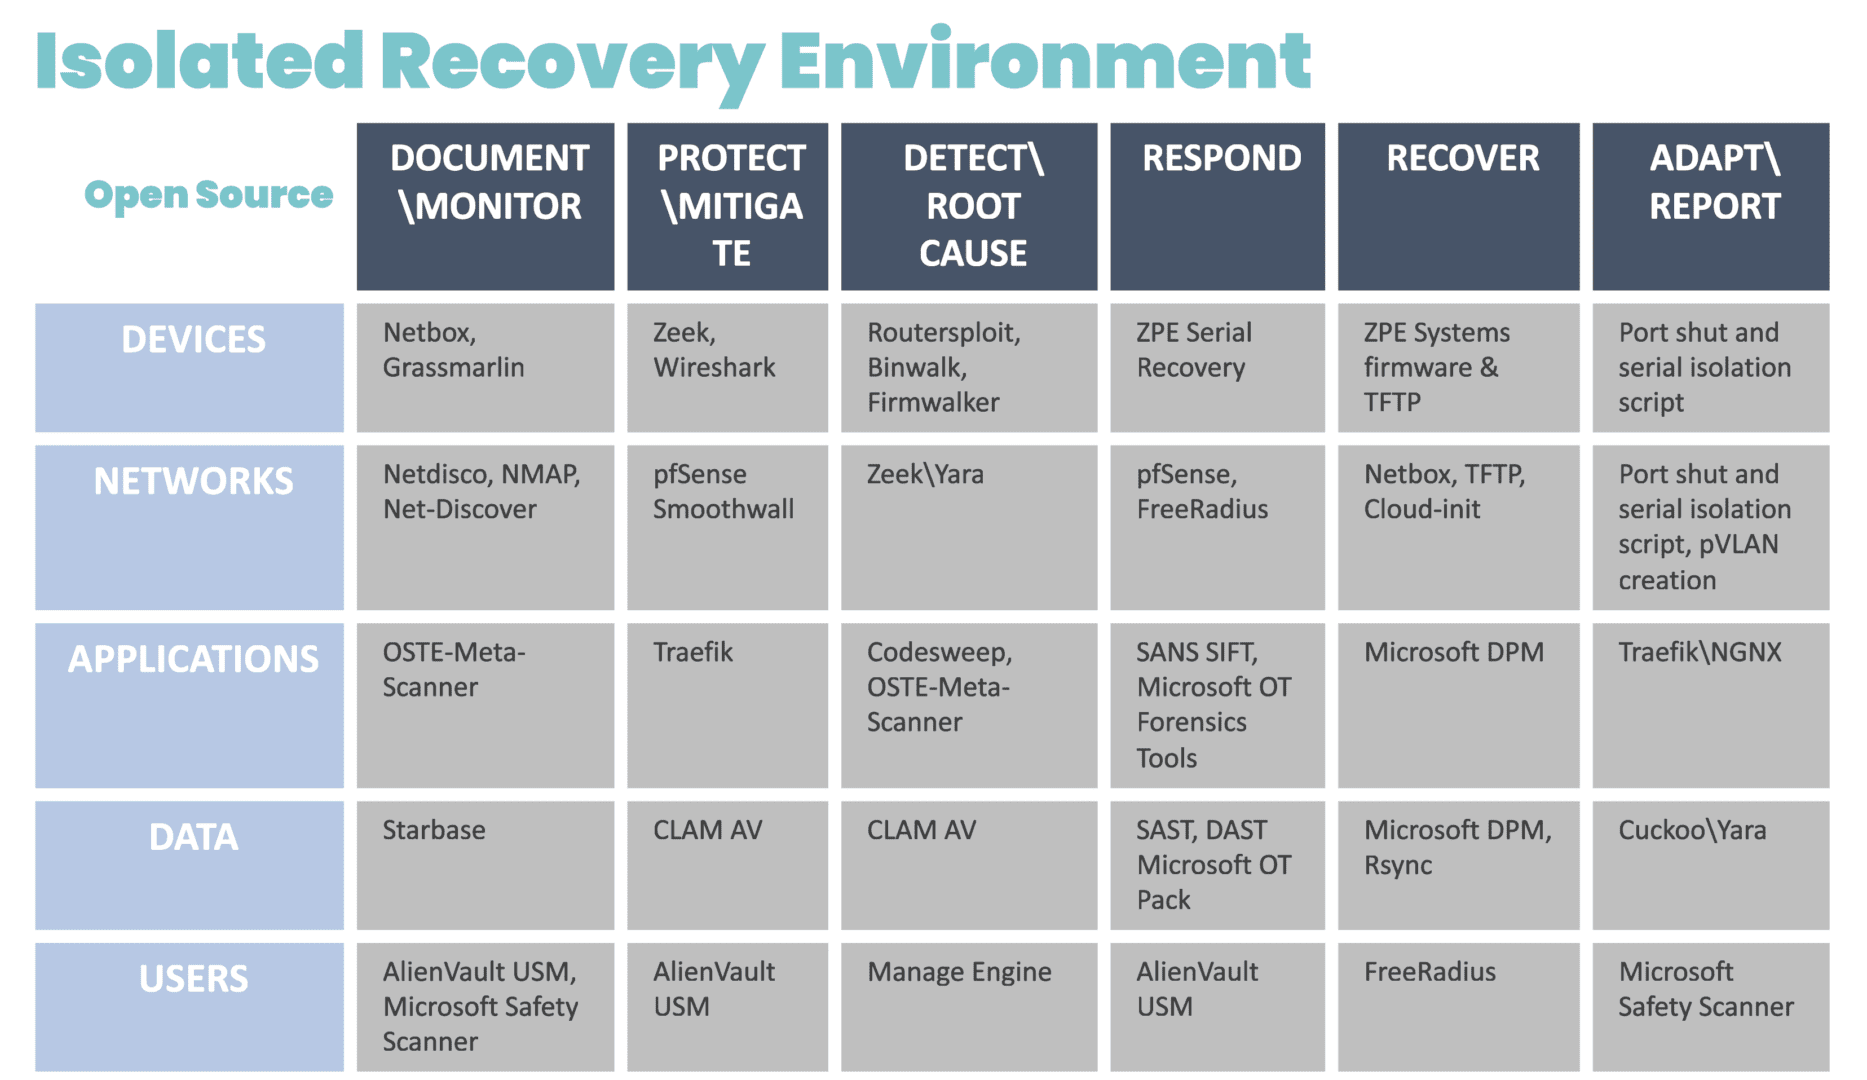
Because IMI is physically separate from affected systems, it guarantees management access so teams can set up communication and a temporary ‘war room’ for incident response. The IRE can then be created using a combination of cellular, compute, connectivity, and power control (see diagram for design and steps). Docker containers should be used to bring up each step.

Diagram showing a chart containing the systems and open-source tools that can be deployed for an Isolated Recovery Environment

Image: The infrastructure and incident response protocol involved in the Isolated Recovery Environment. These products were chosen from free or open source projects that have proven to be very useful in each of these stages of recovery. These can be automated in pieces for each phase, and then be brought down via Docker container to eliminate the risk of leakage or risk during each phase.

Without diving too far into the technicalities, the IRE enables you to recover survivable data, restore software configurations, and prevent reinfection. Here are some things you can do (and should do) in this scenario, courtesy of the IRE:

Establish your war room

You can’t fight ransomware if you can’t securely communicate with your team. Use the IRE to create offline, break-the-glass accounts that are not attached to email. This allows you to communicate and set up ticketing for forensics purposes.

Isolate affected systems

There’s no use running antivirus if reinfection can occur. Use the IRE to take offline the switch that connects the backup and file servers. Isolate these servers from each other and shut down direct backup ports. Then, you can remote-in (KVM, iKVM, iDRAC) to run antivirus and EDR (Endpoint Detection and Response).

Restore data and device images

The key is to have backup data at its most current, both for patient data and device/software configurations. Because the IRE provides an isolated environment, and you’ve already pulled your backups offline, you can gradually restore data, re-image devices, and restore configurations without risking reinfection. The IRE ensures devices “keep away” from each other until they can be cleansed and recovered.

Things You’ll Need To Build The IMI and IRE

Network Automation Blueprint

We’ve created a comprehensive blueprint that shows how to implement the architecture for IMI and IRE. Don’t let the name fool you. The Network Automation Blueprint covers everything from establishing a dedicated management network, to automating deployment of services for ransomware recovery. Get your PDF copy now at the link below.

Gen 3 Console Servers To Replace End-of-Life Gear

It’s nearly impossible to build the IMI or deploy the IRE using older console servers. That’s because these only give you basic remote access and a hint of automation capabilities. You’ll still need the ability to run VMs and containers. Gen 3 console servers let you do all of the things for IMI and IRE, like full control plane/data plane separation, hosting apps, and deploying VMs/containers on-demand. They’ve also been validated by Synopsys and have built-in security features I’ve been talking about for years. Check out the link below for resources about Gen 3 and how we’ll help you upgrade.

Get in touch with me!

I’d love to talk with you about IMI, IRE, and resilience systems. These are becoming more crucial to operational resilience and ransomware recovery, and countries are passing new regulations that will require these approaches. Get in touch with me via social media to talk about this!